Category: Low-Code/No-Code

  • Low-Code/No-Code and Simple APIs

    Low-Code/No-Code and Simple APIs

    In recent years, implementing AI and IoT technologies has been top priority for many organizations as their leading-edge capabilities have become a requisite for digital transformation – but the speed of their adoption is greatly influenced by the flexibility of supporting software. Enter low-code, no-code programming and truly open APIs.

    Low-code/no-code platforms are a promising alternative to traditional software platforms for non-technical business users; a more democratic approach to software development, built on either no or minimal code. The approach begins by minimizing external expenses and time required by outside developers or programmers as business analysts and line managers can now structure new process flows and functionalities.

    This is coming into sharp focus, as the increasing need to get new applications to market quickly is coupled with a growing demand for digital transformation from the C-suite. But to access the benefits, organizations must ensure that their underlying software can integrate well with external systems—introducing application programming interfaces (APIs).

    Low-Code/No-Code – The New Focus

    Analyst predictions have revealed an industrywide trend geared towards these platforms, as 60% of CIOs are set to employ low-code/no-code tools by 2025, with plans to bolster their output capacity. Other analysts expect to see 65% of all application development taking place in low-code/no-code environments by 2024. But, it is the openness of APIs that will determine the success of this software.

    APIs have reached new heights since the early days of component-based architecture, but today’s APIs are still inspired by Roy Fielding’s Representational State Transfer (RESTful) API.

    APIs – Providing Essential Internal and External Openness

    Some vendors will talk about how they have open APIs, but these are often limited and designed for specific, pre-determined integration scenarios. The application, in the meantime, internally communicates in a proprietary fashion that cannot be leveraged by external systems. To maximize the agility delivered by low-code/no-code tools, the entire application should be built on open APIs.

    Enterprise applications can go a step further by relying on the ISO/ICE–approved OASIS Open Data Protocol (OData), making things even more interoperable with more choice, flexibility and capabilities for customers. When the application is built on the same set of RESTful APIs it exposes to other systems, it is even easier to access the precise spot in a value flow with which organizations need to integrate.

    With the support of open APIs, there is an opportunity for companies to leverage low-code/ no-code tools and achieve crucial business returns in three ways:

    1. Undisrupted Connectivity

    A robust architecture built on RESTful Data APIs, documented according to the Open API Initiative specifications, gives organizations the ability to extend enterprise software on the outside to create task specific apps or connect to other systems.
    This may simply be used for automating steps around onboarding a new employee; for instance, filling in a desk number in an office floor plan, initiating payroll activities and creating an Outlook account. It could also populate a serialized part structure from a machinery manufacturing process into the software that will be used to annually service that piece of equipment. Any data, action or event should be accessible in a clear and thorough API library.

    With enough of these RESTful APIs, any number of low-code/no-code tools can be used to create targeted apps that interact with enterprise software and other systems running in a business. Commercial software offerings can be used to build an experience and drive processes in enterprise software.

    2. Digital Transformation Accelerated and Uninterrupted

    The main benefit of using RESTful APIs is that an organization’s external and internal systems can automate processes, expand access to data, and create extensions to their enterprise software on the outside. Regardless of whether an internal process automation (IPA) tool or external low-code/no-code process orchestration software is used, their ERP system should offer transparent access to the part of the system supporting any given integration or process automation.

    Here’s where a low-code/no-code approach helps to develop new solutions and industry specific functionalities that can be built faster, cheaper and with higher quality. Integrating a low-code domain-specific language (DSL) into solutions not only helps create value faster, but also insulates organizations from future technology changes. The DSL describes the intent of what a component in the application (for example, an API) should do, rather than how it is technically done.

    3. Increased Software Governance

    Low-code/no-code tools are also more commonly used to tailor how enterprise software works internally, giving organizations more control over their software. Software providers might currently offer the ability to extend the data model or to tailor the user interface and user navigation flow through a process to an organization’s specific needs, using no-code tooling. But this is not enough.

    Low-Code/No-Code: Go the Extra Mile

    Enterprise software platforms should offer intuitive low-code/no-code tools that will not only automate process steps or actions, but add machine learning capabilities for intelligent process automation. This democratizes the creation of intelligent systems by putting it within reach of business analysts and line managers—a simple what-you-see-is-what-you-get.

    Logical, Automated Processes

    With the IPA capability embedded into software, any additional input needed from users can be captured automatically. These capabilities can then be further enhanced with intelligent parts, such as AI and machine learning models, to make choices inside the automation about what to do next (branching decisions), or predicting values to be filled in.

    As the need to digitally transform continues to surge, enterprise solutions based on open APIs, strengthened by low-code/no-code programming, will become fundamental business tools—speeding up deployment times and delivering business value when it matters most.

  • Is Low-Code Development a Security Risk?

    Is Low-Code Development a Security Risk?

    According to Gartner, the worldwide low-code development market is projected to be $13.8 billion in 2021, a whopping increase of 22.6% from 2020. Gartner also predicts that the surge in remote development during COVID-19  will continue to boost low-code adoption, despite budget cuts and efforts to optimize cost.

    Low-Code’s Popularity Among Professional and Citizen Developers

    Low-code is no longer the new kid on the block. From simple dashboards to complex applications, low-code applications are becoming more and more diverse, with mainstream adoption in the enterprise world. In essence, low-code is a visual paradigm of application development that involves drag-and-drop of pre-built components and integrations resulting in fast, easy and less-error-prone development.

    The advantage of low-code is that it enables users from a non-traditional development background to participate in the app development process, thus democratizing development and accelerating project timelines. It also narrows the demand-supply gap that arose as organizations catered to ever-rising digitization needs with limited resources and developer scarcity. Many low-code platforms make it easy for citizen developers (business analysts, line-of-business users, junior developers, for instance) to build applications while drastically reducing delivery time compared to traditional coding methods.

    But citizen developer productivity and speed are not the only benefits of low-code development. Today, low-code platforms also come with capabilities purpose-built for professional developers from enterprise IT teams to ISVs. These platforms are hardened for enterprise use, are able to leverage the scalability and security needs of a complex application and have integration capabilities mature enough to seamlessly fit in with existing tools and technologies. During the COVID-19 pandemic, many businesses reinvented themselves through adoption of low-code platforms and applications that helped them adapt to the sudden shift to a remote work scenario and enable the necessary modern application needs that came with it.

    Security Challenges with Low-Code and Remote Work

    Compared to traditional development, low-code involves a variety of personas working together to build applications while dealing with automatically generated code, ready-made components and built-in default configurations. This shift in environment revealed some unique challenges that need to be addressed. There are a few common security challenges with remote teams building on low-code.

    Application Development and Remote Team Collaboration

    • Lack of security awareness: Low-code users come from both business and tech backgrounds. Some practitioners aren’t familiar with application security best practices and lack awareness and understanding of potential vulnerabilities and security holes.
    • Platform access and admin controls: Low-code is deployed centrally and available for users across an enterprise via browser access. This introduces a risk of network intrusion; providing access to unauthorized developers and opening up greater permissions to users that do not need it when accessing the platform remotely.
    • Code repository and team collaboration: Low-code platforms must ensure that the automatically generated code can committed to enterprise-sanctioned repositories. This code access shouldn’t be misused, and ought to have sufficient protocols in place for code control and upgrades.

    Code Generation and DevSecOps Best Practices

    • Securing custom code: Low-code tools allow for writing custom code to extend and enforce platform coding guidelines and design patterns to protect sensitive data from unauthorized access.
    • Adhering to secure release practices: Integration with the existing enterprise CI/CD pipeline is important so that dev teams can extend the same release governance protocol to the auto-generated code before going to production.

    End User Application Access and Data Protection

    • Preventing malicious attacks: Today, both web and mobile apps are becoming constant targets for security breaches. Automatically generated code, and citizen developers working remotely, can make low-code applications more prone to vulnerabilities. Platforms should generate apps that are fully protected against phishing attacks, SQL injections, brute force attacks and DOS attacks.
    • Secure data and application access: Low-code platforms should provide a comprehensive access control mechanism preventing unauthorized access to data and app functionality. With remote teams accessing apps from anywhere, at any time and from any device, data breaches can be prevented with the right controls in place.

    Low-Code and Security – The Future of Development

    As enterprises and ISVs turn to low-code for more serious use cases, the larger question still remains. Can low-code platforms enable modern development teams to deliver applications faster, while still enabling a secure and tightly governed environment?
    The answer is, yes, they can! However, development teams must consider the following security checklist when considering low-code platforms:

    1. The chosen low-code platform must be set up within an enterprise secure DMZ or secure private cloud, and must effortlessly pass cybersecurity clearances.
    2. The platform must enforce best practices in programming (coding conventions, design patterns and data encryption) for automatically generated code as well as custom code written by the developer, facilitating easier integration with existing CI/CD processes and tools.
    3. The platform must offer full protection against the top 10 OWASP vulnerabilities for web and mobile apps, and have third-party certifications to guarantee code quality and security. Also, organizations should ensure that there are no vulnerabilities in their chosen platform’s binaries, as well as all third-party dependencies (including open source libraries) as listed in the CVE library.
    4. The solution must support multiple authentication providers (database, LDAP, AD, SSO, SAML, Open-ID, multifactor, biometric) to build applications with strong user security. For user authorization, ensure support for both coarse-grained as well as fine-grained access control policies to protect various aspects of the application based on RBAC.

    Development teams can embrace low-code technology while ensuring security best practices are in place. Low-code is here to stay, and with the right platform, enterprises and ISVs can make sure security is shifted left and addressed by developers much earlier in the development process. The result is a highly productive, remote workforce churning out applications that are modern, scalable and secure.

  • How Low-CodeOps Can Transform DevOps

    How Low-CodeOps Can Transform DevOps

    Over the past year, enterprise adoption of low-code software development platforms surged across the world economy as COVID-19’s economic consequences drove an unprecedented number of digital initiatives. Enterprises are turning to low-code platforms to rapidly build new apps that empower customers, remote workers and external end users conducting business operations or pivoting to new opportunities.

    Accelerating software development, however, only solves half the puzzle of a digital-first approach. Quickly getting solutions into users’ hands requires careful planning to determine how these new applications will function within the organization’s overall software operations strategy. This is often conducted across multiple cloud deployments.

    But the real prize comes when low-code’s underlying principles of automation and abstraction are extended into the DevOps domain of software maintenance and management. The ability to push out a continuous pipeline of software updates with the click of mouse, with streamlined testing and quality assurance, requires a platform that automates myriad, time-consuming tasks associated with building, testing, releasing and maintaining applications in an enterprise-grade production environment. This inevitably leads to the concept of “low-code operations;” or, to coin a phrase, “Low-CodeOps.”

    Indeed, unless the benefits of abstraction and automation — in this case, primarily speed — extend to operations and deployment, the real benefits of low-code development are elusive. A platform that lets you build an app in six days but requires six months to deploy is no solution at all.

    Harnessing the Cloud for Game-Changing Results

    To witness the vital role seamless cloud operations played in business innovation, look no further than biotech giant Moderna and its success in Operation Warp Speed. Moderna used the public cloud to pull together geographically dispersed collaborators, integrate scientific insights and refine its production cycle, enabling the company to deliver its first batch of mRNA vaccine samples a mere 42 days after the COVID-19 virus genome was sequenced. The time-to-value for this solution was definitely warp speed.

    And, it’s safe to assume, expensive. Cloud engineers and DevOps system administrators are highly skilled specialists who roll up their sleeves at 2 a.m. to fix unexpected glitches buried deep in the connected ecosystem of software operations. They figure out how to make the software actually run. Enterprises, no doubt, wish they could hire more of them.

    But the same shortage of skilled IT professionals that fueled today’s demand for low-code software development also impacts DevOps. In this case, the same low-code platform is the solution, empowering a wider cross-functional, collaborative team to reduce operational burdens — in a word, Low-CodeOps.

    Essential Features of Low-CodeOps

    To achieve a frictionless handoff when moving applications and data to the cloud, a production environment leveraging low-code principles will deliver on these key principles of low-code operations:

    Performance monitoring: Daily monitoring and log checks of platform infrastructure are the backbone of modern DevOps operations, ensuring that complex interdependencies are running smoothly. Automated dashboard monitoring can transform hours spent on these repetitive tasks into opportunities for engineering teams to focus on innovation, while still ensuring the health and performance of enterprise software portfolios. The tooling needs to enable automated end-to-end visibility into application workloads and performance characteristics of upstream and downstream services.

    Compliance: Every economic sector is subject to specific government regulations. Software platforms and DevOp teams must keep track of every requirement when integrating new functionality into software upgrades. Banking customers must deploy digital solutions on infrastructure that’s earned ISO/IEC 27001 certification. Healthcare solutions must conform to federally mandated HIPAA requirements. Defense contractors must be FedRAMP certified. Data—the lynchpin of any digital solution—is subject to privacy laws that differ across nations and borders. Imagine having to manually recheck every iteration of your application deployments for compliance. Luckily, low-code operations mean having an automated, system-wide compliance framework in place. This makes short work of service organization (SOC) audits and reporting.

    Security: Cyberattacks that lead to system outages and disruptions are a growing concern in our digitally connected world. Well-resourced cloud giants are not exempt from damaging cyberattacks, such as last year’s SolarWinds hack. Resilience is key. Ongoing security scanning can halt automatic software deployments when suspicious changes are detected. Prevention is always best. Monitoring tools identify vulnerabilities, enabling systems to quickly come back online and help prevent outages that can last for hours or days.

    Infrastructure independence: Widespread enterprise adoption of multi-cloud and hybrid cloud for operational efficiencies has made flexible infrastructure the new standard. Organizations are bypassing single-vendor lock-in to spread workloads across multiple cloud partners. That means DevOps needs streamlined configuration and management tools that can track relationships between resources and keep track of compliance issues. Geopolitical considerations may enter the equation when cloud providers turn out to have close ties with governments antagonistic to other global trading partners. Monitoring instruments that provide observability across the range of vendors consuming enterprise data and applications is mission-critical.

    Resilience: Snafus happen. Platforms can automate continuous domain-level metrics to correlate performance from different sources (including logs, metrics, application tracing and outside penetration testing), speeding up detection and response time. Fast auditing and debugging tools, combined with real-time dashboard monitoring and system-wide alerts, plus an ounce of detection, equals a pound of cure. For agile DevOps teams, reactive firefighting is transformed into resilient firepower.

    Adopting an All-in-One Low-CodeOps Approach

    Low-code’s power to enable frequent iterations of software ideation, creation and deployment may seem contrary to the DevOps mission to minimize risks. However, the same radical abstraction and automation that has made software development faster, higher quality and more accessible to a larger cohort of developers can also reduce the operational burden of landscape management. Every low-code vendor touts the governance features in its platform. But the nuts and bolts of governance require some assembly, including system-wide actionable monitoring, testing alerts and compliance safeguards. Low-CodeOps combines the most efficient, agile, flexible development platform and powerful, streamlined operations tools, infusing both domains with solid guardrails for operational control and predictability. Adopting this approach will greatly increase time-to-value for enterprises, putting innovative digital solutions directly into the hands of end-users with the click of a mouse.

  • Low-Code and DevOps: Friends or Foes?

    Low-Code and DevOps: Friends or Foes?

    What does low-code mean, and who is it really for?

    Over the last few years, I’ve seen many articles associating “low-code” with “citizen developers” or with people who don’t have deep development skills. Users can arrange visual elements, or fill in forms with key information and publish the result as an application.

    But tools for citizen developers are only one part of the low-code story. There is also a growing number of tools for professional developers, and I want to talk about those, too.

    Both citizen developers and professional developers have a role to play in application development and automation projects, and low-code has something to offer both of them.

    Low-code is Not a Market, it’s an Approach

    Low-code does mean providing visual and graphical tools and simple frameworks that mask more complex coded operations, so the application designer does not have to directly touch the code that performs desired operations. These apps are naturally limited, as the resulting application can’t be highly customized if you can’t touch the code.

    With these kinds of visual tools, anyone can create a simple application within the limits of the tool. But when we pull back and look at what is needed to create larger, more complex applications – ones that need to communicate with other enterprise systems, or need extensive customization, or cross organizational boundaries, or need to pay attention to governance requirements, for example – the visual-only approach is frequently insufficient. In complex cases, developer expertise is often needed, and developers have to get “under the hood” to tinker with code.

    There is no “low-code market.” We are bringing tools to people who need them to develop specific projects. A comprehensive low-code approach to application development and automation means offering both visual programming and coding capability. For usability reasons, these tools are clearly separated and presented to the development team in a way that allows citizen developers to work on certain elements and developers to work on others, all on the same platform.

    We know that it’s possible to serve professional developers with low-code, too. A low-code approach also includes drag-and-drop tools that developers can use – for example, to develop APIs, or to integrate the application with other systems, or to customize front-end interfaces. Of course, when code is required, developers should be able to use their own tools and frameworks and not be limited by low-code tools. Platforms that offer a hybrid approach are likely to be most useful to mixed-skills development teams.

    The Hybrid Approach

    Strictly low-code tools can serve simple automation use cases. More broadly, automation platforms offer a hybrid of low-code and coding capabilities for more complex automation use cases.

    For critical enterprise applications, both business and developer inputs are usually needed. Having tools for both of them means not leaving anyone out.

    Low-code tools will continue to become more mainstream. Low-code is not a fad or a passing trend, but a quiet revolution that will see greater incorporation into more business tools.

    Here Come the Digital Natives!

    More vendors are offering low-code tools for digital process automation, business intelligence, robotic process automation, identity management and data integration, to name just a few.

    As automation platforms and other low-code tools mature, a greater number of people are getting used to working with them. Developers are less hesitant about incorporating non-developers into their teams, as everyone gains a better understanding of the benefits of these platforms.

    The younger generations entering the workplace today are digital natives. They are fearless about diving into technology and working hands-on. So, these low-code tools are ready for them, and they are ready to put them to work.

    Low-code is breaking down technical barriers to work in the automation space, making smooth collaboration between business and development easier.

    Low-Code Can Be a Double-Edged Sword

    Automation and development teams are also becoming more aware of vulnerabilities and compliance issues as citizen developers roll up their sleeves and join the technical team.

    Low-code tools are a double-edged sword. They facilitate teamwork, but issues with security and data governance may not be top-of-mind for non-developers. If you have a big team working on automation and/or application development and delivery, the need to build in governance becomes even more important.

    Using a shared platform will help manage and mitigate these issues with security and governance. This will become even easier as the platform tools evolve and mature, so DevOps teams can use them to help mitigate some of these issues.

    Does Low-Code Have a Place in DevOps?

    We are definitely seeing the impact of low-code on development environments and DevOps. Remember, low-code started with small applications, and while DevOps-style teamwork and workflows may not be needed there, as the use of low-code platforms becomes the norm for critical enterprise projects, DevOps will be a necessary part of the mix. This is where low-code is having a more obvious impact; Agile methodologies using low code platforms for iteration, for continuous improvement and for continuous delivery. These applications aren’t one-and-done. They need to be maintained, improved and delivered, again and again.

    Low code isn’t going away. On the contrary – it’s going everywhere.

  • Low-Code Makes API Testing More Accessible

    Low-Code Makes API Testing More Accessible

    APIs are rising both in quantity and business value. But with that growth comes an increasing number of vulnerabilities, which could affect cloud service dependencies and internal APIs. Functionality and uptime could also suffer as cloud services evolve their APIs with new versions. Thus, API endpoint testing is critical to ensure a reliable back end. With growing interest across the organization to stabilize these integrations, how do we test APIs in a reproducible way that non-developers can grasp?

    Low-code platforms — tools that enable workflows with visual programming models — are opening doors for citizen developers to construct applications in a visual mode. Similarly, the low-code concept could aid API testing by providing an easier method to create API tests to verify functionality and uptime. This could arm quality assurance, DevOps and site reliability professionals with an easier means to test high-value integrations and their UI representations.

    Amid a growing headless movement, APIs are now powering many end-user experiences. However, during a developer drought, it may be challenging to find talent with integration know-how.

    I recently met with Dan Belcher from Mabl to discuss combining low-code and API testing. Here, we’ll uncover why it’s difficult for non-engineers to conduct API testing and consider what API testing must address to ensure today’s software meets tomorrow’s digital innovation demands.

    A Low-Code Approach to API Testing

    The software landscape has evolved rapidly in recent years. “Many forces have combined to create an incredible amount of change,” said Belcher, citing DevOps, CI/CD, the API economy and agile enterprises as examples. In this era, applications are becoming more dynamic, disrupting the way teams conduct end-to-end quality testing.

    API-based cloud services are part of this new frontier, becoming popular building blocks within modern applications. Yet, integrations require upkeep as cloud services evolve and version. Without continuous testing of API-based cloud services, organizations could easily suffer from breaking change and poor usability.

    Unfortunately, as it stands, typical QA teams aren’t well-equipped to handle ongoing regression testing for APIs. Instead, “developers, historically, have been the only ones that understood API testing,” explained Belcher. For years, API testing has been relegated to the realm of developers, who use tools like Postman to perform unit-level testing. But why is API testing so difficult for others?

    What Makes API Testing Difficult?

    Well, to start, non-engineers are typically more accustomed to UI-based testing. These environments use a structure designed for anyone to consume, making it easy to locate fields and confirm values, Belcher explained. When it comes to API testing, you often must handle massive chunks of JSON responses to match fields and surface issues. Testing API responses typically requires writing code, parsing JSON and writing it to variables, Belcher explained, which may be difficult for non-developers to implement.

    Or, difficulties could arise when testing asynchronous endpoints, Belcher added. Asynchronous APIs often involve background server processes that take a while to respond. This comes at a moment when event-driven architecture (EDA) is a growing trend. Take AsyncAPI, a standard API specification for EDA APIs, which recently joined the Linux Foundation. A recent report found AsyncAPI production usage tripled from 5% in 2019 to 19% in 2020. According to Belcher, testing such asynchronous services requires an infrastructure for continuous testing to anticipate these emerging scenarios.

    Four Crucial Areas For API Testing

    So what should API tests be focusing on? Belcher highlighted four areas that warrant close examination throughout the API testing process:

    • Functionality: This is the core functionality. Does the API do what it promises? Does it return the correct data?
    • Uptime: What is the API’s availability? Are all endpoints available in production?
    • Speed: This ensures cloud dependencies meet SLAs. What is the latency? Is there drift in API performance over time? Though API monitors like Api.expert help aggregate industry performances, they might not always reflect your specific customer-level realities. Belcher recommends not placing faith in supposed performance and instead, clocking your own.
    • End-to-End: Belcher stresses the role APIs now play across customer-facing presences. An end-to-end workflow should involve API endpoints, how they interact with one another, and the resulting visual representations. “Just like we have end-to-end testing for UIs, we should have end-to-end testing for APIs,” he said.

    API testing isn’t always combined with other parts of the user experience, but Belcher believes, going forward, end-to-end testing will be critical to ensure all workflows function in concert. For example, if a user profile is created within a browser, teams should verify the user profile has been created at an API level, as well.

    Low-Code API Testing and Shift Left

    APIs are beneficial to avoid reinventing the wheel. However, 100% operational uptime is impossible. Applications will inevitably encounter API problems, including outages, technical failures and functional misrepresentation. Developers also often come to rely upon production behaviors that may not be officially documented, an effect known as Hyrum’s Law. This can cause unstable integrations as APIs version over time.

    Thus, for these reasons and more, it’s a good practice to adopt continuous API testing. With the surging interest in site reliability engineering, spotting API errors early on will become an important aspect in reducing mean time to recovery (MTTR). Testing third-party APIs could also expose production latencies to inform cloud investments.

    “As the pace of change is going up, how do we deliver great quality to our customers?” Belcher asked. API testing is one answer to address this rapid change, and is growing in importance for the software delivery life cycle. It especially rings true for headless frontend experiences, where the API-driven backend isn’t transparent to QA testers.

    Low-code capabilities for API testing could help tear down silos inherent in the development process, enabling more people to participate in testing integrations. Belcher also stresses the importance of improving the usability of API testing for developers and non-developers alike. “We need to integrate with tools developers are already using for verification,” he added.

  • Manufacturing Workers Eager to Digitally Upskill

    Manufacturing Workers Eager to Digitally Upskill

    Anyone who has worked in machining within the past 70 years knew that the future of machining was automation. In the 1940s, computer pioneer John T. Parsons and engineer Frank L. Stulen invented, via a contract with the U.S. Air Force, numerical control milling machines. The machines were designed to help the Air Force produce geometrically complex parts more economically and accurately.

    Those machines were the precursor to today’s computer numerical control (CNC) machining tools that use programming to automatically process some material, such as metal or wood, to specification. By the late 1980s, such machines were standard within tool and die, machine shops and manufacturing floors. Today, such digitization of manufacturing is accelerating.

    Workers, for the most part, embrace the change and would do more to meet the technical skills demands needed for their jobs – if only their employers supported them. That’s the primary finding from a survey, Digital Illiteracy in the Factory: Providing Workers with Low-Code Tools, commissioned by low-code platform provider Mendix.

    Interestingly, today, low-code development tools are finding a home in manufacturing. According to the survey, nearly 9 out of 10 said they want to learn low-code software development, while only 3% currently use low-code in their jobs. More than two-thirds (67%) say they want to create a software app that would solve work issues. According to this survey and a parallel survey conducted in Europe, U.S. workers are more willing to welcome and contribute to workplace digitalization than their counterparts in Germany (78% versus 61%) — a surprising result, given that German manufacturing workers enjoy a reputation as some of the most skilled in the world.

    “Incorporating digital applications is vital to the ongoing competitiveness of manufacturing in the U.S., and it is heartening to see such a large percentage of the manufacturing workforce ready to contribute to this effort,” Gardner Carrick, vice president of strategic initiatives at The Manufacturing Institute said in a statement. “Low-code applications provide our workforce with the tools to contribute to this digital transformation, and we should prioritize training in these skills.”

    The survey found that 87% of U.S. workers want to learn low-code development, and within those respondents, 88% of women who responded indicated being very interested in learning low-code, while 51% of men responded in kind. Perhaps not surprisingly, younger workers are more interested in learning low-code than those nearing retirement.

    That may be so, but U.S. manufacturing employers aren’t getting the memo. The survey found that U.S. manufacturers are giving their workers little help in developing their digital skills, and only 18% of workers are happy with their digital skills. “That only 18% are happy with their digital skills is just one sign that more training is required. At a time when the country’s manufacturing industry remains mired in a decades-long slump and when managers clamor for more useful software applications, news reports indicate that the nation’s workforce is ill-equipped to deal with writing code,” Mendix said in a statement.

    “The United States needs to move now to get their workers into the digital game,” said Derek Roos, Mendix CEO. “If the country wants ‘Made in the USA’ to mean something again, and if it wants to reduce unemployment and keep its economy vital and thriving, manufacturing and industry should provide low-code and other tools that help bridge the digital divide.”

    The survey was conducted from Jan. 29 through Feb. 11, among 250 full-time manufacturing workers in the U.S. and 250 within Germany. The survey’s objectives included learning workers’ attitudes and motivations, as well as obstacles that prevent them from acquiring low-code and other digital skills.

  • Citizen Development Program: Establishing Guardrails

    Citizen Development Program: Establishing Guardrails

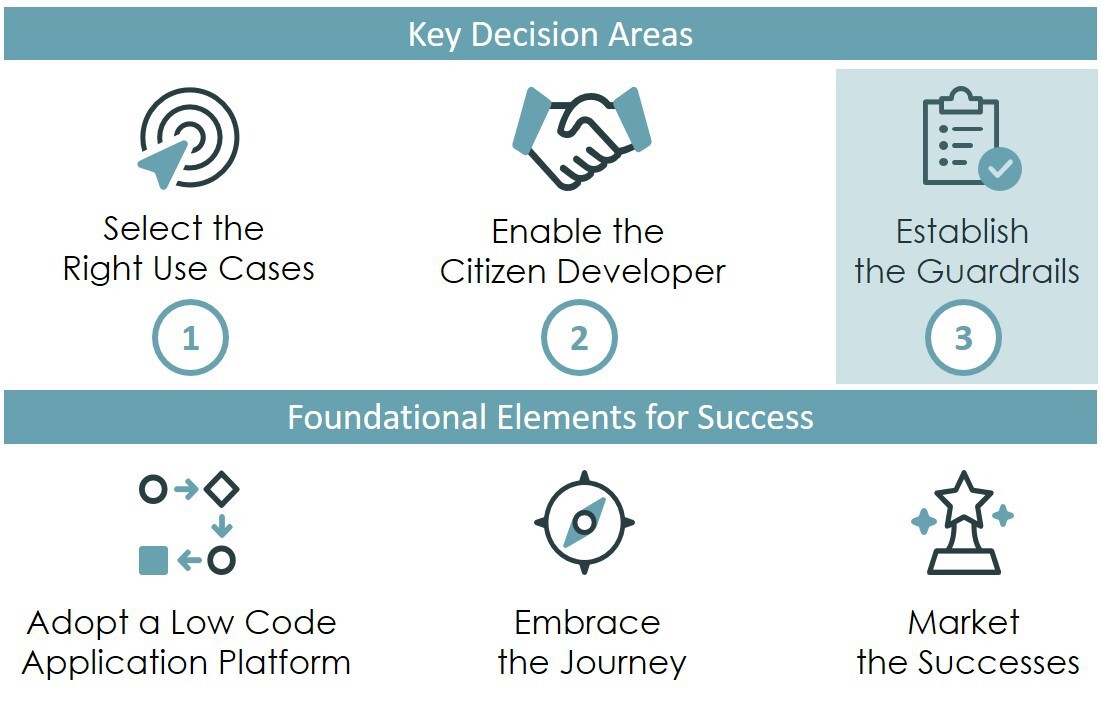
    Citizen development is as easy as one, two, three.

    1. Select the right use cases
    2. Enable the citizen developer(s)
    3. And establish the guardrails, which I will cover here.

    Of course, there is a little more to it than this. Success requires focus, planning and patience. We previously discussed, in parts one and two of the series, the discipline required around use cases and citizen developers (CDs). This third and final post covers how to establish the appropriate technical and process guardrails to ensure the wider enterprise, platform and developers are protected.

    Establishing the Guardrails

    Guardrails exist for two primary purposes: alignment and independence. Clear and concise guardrails ensure alignment across organizational objectives, company policies and disparate teams. Those same guardrails provide CDs with a degree of independence – a safe operating space where they will not be micromanaged or unnecessarily burdened by processes.
    Effective guardrails define and enforce a range of acceptable behaviors, as well as reduce risk and speed application delivery.

    While low-code application platforms (LCAPs) each have their unique capabilities and technical implementations, relevant features can be viewed in three broad categories: platform foundation security, app dev access control and development tools & processes.

    Within the context of your specific LCAP and development methodology, you need to consider and answer the following questions:

    Platform Foundation Security

    • How will you provide your CDs a “safe” environment to build and test their applications? Does your platform support separate and secure development, test and production environments? Will you put your citizen developers in their own discrete development environment?
    • Will your developers be working with data that requires encryption and/or localization? If so, does your platform support data encryption and compliance with relevant data residency laws?
    • Does your LCAP support anti-virus scanning and/or HTML sanitization, and if not, how will you prevent a CD from inadvertently putting your organization at risk?
    • What logging and auditing is required for your CD activities? Who reviews logs? How long is the information kept?
    • Does your platform support enhanced security mechanisms like two-factor authentication (2FA) or virtual private networks (VPNs)? Will citizen developers be working in areas or with applications that require enhanced security?
    • Are there other risk, compliance and security standards that your organization mandates? If so, how will you incorporate them?

    App Dev Access Control

    • How will you provision or deprovision developer and tester accounts? How will you handle developer login and authentication into the development environment?
    • Will CDs have development access to downstream environments across testing, staging and production?
    • Will you use groups to control access to applications in development, and if so, who will manage these groups?
    • Will you use roles to grant access to distinct development capabilities like tables, workflows, UIs, mobile, reporting, analytics, etc.? What determines which role(s) a citizen developer is granted?
    • Will you provide a library of pre-built application components (e.g., workflows, dashboards, virtual agents, etc.)? How will you control access to and usage of the pre-built components?
    • Will you allow citizen developers to access pre-built integrations? How will you control access to and monitor usage of those pre-built integrations?
    • Does the developer identity and access management process need to be driven by an enterprise identity provider, such as Azure Active Directory?
    • Will citizen developed applications be able to access other citizen developed applications? How will app-to-app access be controlled?

    Development Tools and Processes

    • How will you manage your demand intake process? How will you ensure that new applications do not duplicate existing application functionality? What criteria will you use to determine if an application is a good fit for a citizen developer?
    • Will you require your CDs to adhere to all, some or none of your existing development methodology? Can you explain the methodology in terms the citizen developer will understand and accept?
    • Will you require CDs to create requirements or agile stories before building an application?
    • Will you require tests be developed for CDs’ applications, and if so, can these be automated? Who will develop those tests?
    • Will you require code or application reviews of citizen developed applications? What best practices and standards will be used during those reviews? Can those reviews be automated?
    • What level of documentation, if any, will you require developers to produce?
    • How will you promote applications through the development pipeline (i.e., dev to test to prod)? Can the app promotion process be automated?
    • How will you track and manage CDs’ applications through the development pipeline and their life cycle?

    Reflections on Citizen Development Programs

    The exercise of writing this series and your feedback has encouraged me to reflect on parts one (selecting the right use cases) and two (enabling citizen developers). Here are a few final thoughts to consider:

    • Do you care that a CD builds just one app or do you want them to build more?
      Ideally, a CD continues to deliver app after app. But attrition can be high in a CD program. Therefore, if your CD built a single application that delivers business value and then returned to their “day job,” you should still celebrate that success.
    • Is citizen development better suited for creating new apps or maintaining existing apps?
      In my view, the answer is both. LCAPs provide great opportunity for CDs to prototype or even produce an MVP of an application. At the same time, LCAPs allow professional developers to build more complex applications and turn the maintenance of those applications over to CDs.
    • How many LCAPs can you reasonably expect a citizen developer to understand?
      Realistically, perhaps one, or maybe two. Keep in mind that app development is important, but having CDs focus their technology choices on a single LCAP vastly improves their chances of success.
    • Do citizen developers make good professional developers?
      Consider this – some of the best developers I have worked with do not have computer science or software engineering degrees. It’s more important that a developer has a passion for technology and, more importantly, for understanding how technology solves business problems.
    • Finally, explore and embrace citizen development before your competitors do, as the value proposition is real in this new world of work we have found ourselves in. After 30 years in enterprise IT, I can confidently say we’ve reached an inflection point in technology and business, truly democratizing application development.

    This post is the third of a three-part series from Mark Tognetti that provides real-world insights on delivering business value from citizen development initiatives.

  • How to Mitigate Low-Code Security Risks

    How to Mitigate Low-Code Security Risks

    Gartner predicts that by the end of 2025, over 65% of development projects will use low-code builders. The field of low-code continues to expand. But what security implications does low-code introduce?

    Low-code refers to tools that enable application construction using visual programming models. Adopting drag-and-drop components instead of traditional code, no-code and low-code platforms enables non-technical folks to construct their own workflows without as much help from IT. Yet, handing power to citizen developers with less security training can be risky. Plus, low-code platforms may hold compromised propriety libraries or leverage APIs that may unknowingly expose sensitive data to the outside world. There’s also the possibility that low-code could increase shadow IT if not governed well.

    Low-code opens the door to more producers. But, does it open the backdoor, too? I recently met with Chris Wysopal, CTO and cofounder of Veracode, to discuss the growing security risk posed by low-code applications. According to Chris, hardening low-code environments involves a combination of compartmentalization, dynamic and runtime techniques, and adopting the “least privilege as possible” rule across the board. Below, we’ll expand on potential low-code risks and see what other methods Wysopal recommends organizations employ to secure the emerging low-code paradigm.

    Low-Code Security Concerns

    Verizon’s 2020 Data Breach Investigations Report (DBIR) found 43% of all breaches are connected to a vulnerability at the application layer. Thus, securing these applications, or in the case of low-code, the layer that generates them, is essential for business to function smoothly.

    When it comes to low-code, Wysopal notices a few key risk areas:

    Proprietary libraries with hidden vulnerabilities. By their nature, low-code platforms typically use a good deal of proprietary software, making securing them a bit opaque. These systems could involve a proprietary language, proprietary libraries and proprietary frameworks. If you trust a low-code platform, you place a lot of faith in the low-code vendor to have a strong security process in place.

    Some platforms do generate traditional code, which organizations can export to run on a Node.JS or Java server. Yet, this often involves a mix of code and proprietary libraries, says Wysopal. While you could run traditional static analysis on the generated code, you may miss some context.

    Lack of citizen developer security training. Citizen developers have little technical knowledge, let alone DevSecOps training. If runtime applications present vulnerabilities, expecting no-code users to mitigate them is unrealistic.

    API integrations. If low-code platforms expose an API or generate a web application via an API, the platform could be exposing sensitive data.

    Ways to Harden Low-Code Environments

    To respond to these areas, Wysopal offers some advice for securing low-code environments:

    • Perform static code analysis: Perform your own static analysis on any generated code and test for common errors. “Look at the code, and understand where it interacts with the outside,” Wysopal recommended.
    • Audit proprietary libraries: Whenever possible, Wysopal said he recommends pushing back on the vendor to question them on their application security standards and examine proprietary libraries for potential risks.
    • Verify partners: Similarly, take precautions when working with third-party partners around low-code tools. Partner tools should be carefully vetted and hold some sort of application security certification from the low-code platform.
    • Secure the API layer: Understand what APIs the application interacts with. These connections should be tested dynamically and automatically with an API scanner. Along your journey, consider these API security testing best practices.
    • Compartmentalize: Wysopal also recommends traditional isolation techniques. Consider more than just the application layer; Wysopal recommended isolating the app and running it in a virtual machine or a container.
    • Security training for citizen developers: Since citizen developers are typically not trained on appsec practices, hold security exercises to train them on fundamentals. A helpful demonstration could involve directly attacking an app to find flaws.
    • Apply the least-privilege-as-possible rule: When assigning user capabilities, whenever possible, use secure-by-default settings and allow access only to those that need it.

    By applying dynamic and runtime techniques, you may catch vulnerabilities, such as a cross-site scripting error. However, if you’re working with proprietary low-code systems, you may not be able to fix it immediately! You may have to send a request to the vendor and wait for the bug to be patched. Thankfully, most technology providers take more immediate action in response to bugs than to feature requests, Wysopal noted.

    Change the Attitude Toward Security

    On the low-code spectrum, there is the attitude that “people aren’t really doing mission-critical applications — they’re mainly doing prototyping, or back office automations,” Wysopal said. Or, since low-code applications often do not publicly expose an application, they are deemed low-risk and fall to the bottom of the security team’s inbox and list of to-dos. “We’re still in a world where people don’t secure all applications,” he said.

    However, these attitudes are a bit short-sighted, since “applications aren’t islands,” Wysopal said. Even if applications are intended for internal use only, phishing attempts could expose credentials and gain access to the network. Here, attackers could leverage sensitive resources or steal infrastructure for compute power.

    Thus, all low-code users should be aware of potential threats and change habits to address these risks accordingly. However, the onus is also on low-code vendors to sufficiently arm their systems. Having a vulnerability disclosure, bounty program and an easy means to accept bug reports from white hat security researchers will be necessary to continually patch issues.

    No-Code ≠ No-Bug

    Low-code continues to permeate more and more digital operations, opening up novel potential for citizen developers. While the low-code movement promises impressive returns, it also brings potential risk.

    To mitigate these concerns, we must level up our security understanding and evolve our approaches, Wysopal said. “Any application can have flaws and security bugs in them.” Just because you’re not writing a function in C and are relying on a visual programming model doesn’t mean you’re not introducing flaws.

    Disseminating the real risk of resources and dependencies, along with helpful consumer-facing documentation, will set the superior low-code platforms apart from the rest. Otherwise, putting faith in proprietary libraries will be a tough pill to swallow.

  • ServiceNow Acquires Intellibot to Gain RPA Capabilities

    ServiceNow Acquires Intellibot to Gain RPA Capabilities

    ServiceNow’s acquisition of Intellibot, a provider of a robotic process automation (RPA) platform, this week is part of a larger effort to automate the development of applications that are driving digital business transformation within enterprise IT environments.

    Earlier this month, ServiceNow unfurled a set of revamped low-code tools that both professional and so-called citizen developers could employ to build applications to modernize various business processes. However, many existing business processes are either manual or paper-based. An RPA platform enables organizations to create bots that mimic, within an application environment, the way those processes are currently managed.

    Josh Kahn, senior vice president for Creator Workflow Products at ServiceNow, said ServiceNow envisions the Intelligent RPA platform as a mechanism to automate rote processes that, for one reason or another, don’t manifest themselves via a set of application programming interfaces (APIs) that application developers can easily invoke.

    Each IT team, of course, will need to decide when it makes more sense to employ bots to digitize an existing workflow versus reengineering it using a set of custom applications infused with machine learning algorithms and natural language processing (NLP) capabilities. As digital business transformation initiatives become more urgent, the application development backlog within many enterprise IT organizations that require those capabilities is steadily increasing.

    However, in some cases, an RPA platform can reduce that backlog by surfacing a set of visual tools to automate a process that doesn’t require a lot of developer expertise to effectively digitize.

    In general, Kahn said ServiceNow is making a case for building a wide range of applications on top of the same software-as-a-service (SaaS) platform many internal IT teams already employ for IT service management (ITSM). That approach enables IT teams to streamline processes as the number of custom applications that need to be both developed and, ultimately, managed, steadily increases over time, Kahn said.

    The developers of those applications might be professionals using a low-code tool instead of writing additional code to quickly build an application, or it might be a “power user” that has enough understanding of software development best practices to build an application. Regardless of who builds the application, the rate at which applications are built using low-code tools is clearly about to accelerate.

    Kahn said the next step for ServiceNow will be to embed the Intellibot RPA capabilities in the ServiceNow platform sometime after the deal closes in the second quarter. In fact, one of the reasons ServiceNow opted to acquire Intellibot is because, as a smaller startup vendor, it is easier to incorporate their RPA platform than it would be to reengineer a much larger RPA platform. However, ServiceNow remains committed to integrating with other third-party RPA platforms that are already being employed by its customers, Kahn noted.

    Regardless of how or at what rate applications are developed, the number of core technologies required to build them continues to expand. The issue IT organizations will need to come to terms with is the degree to which they want to stitch all those tools together themselves, or rely on a platform to do it for them.

  • Why a Low-Code Platform Should Have Pro-Code Capabilities

    Why a Low-Code Platform Should Have Pro-Code Capabilities

    If you want to build a house, you could get a lot done yourself. You could sketch out a simple design, start assembling materials, maybe even nail down some floorboards and install drywall. But to make it truly functional, and to respond to all the unknown fixes — big and small — that would surely arise, you want professional support to enhance and reinforce the job you’re doing. Plus, not everyone is an expert in plumbing and electric.

    The same is true of app development.

    Low-code platforms are available for both professional and less-experienced developers to build apps more quickly than ever. The speed and practicality of low-code has injected a newfound approachability to the coding process, yet can’t account for the full range of user experiences at work within the modern enterprise company of today.

    If this sounds like a takedown of low-code, it’s far from it. As an approach, low-code is transformative. And here to stay. By empowering non-coders (citizen developers), you enable development of responsive web apps using visual tools and pre-built components and save precious development and IT resources.

    Low-code can free IT departments from a constant onslaught of demands and requests for support and create new ways to digitally advance products and services. Plus, IT leadership can be freed up to focus on the strategic needs of the business and maintaining momentum within major digital transformation initiatives. Therefore, it’s worth understanding why not all low-code platforms are the same, and how they’re viewed through the lens of the professional developer and enterprise architect.

    Using Only Low-Code Means You Can Fall Short

    The simple, unvarnished truth is that, when it comes to coding, there is no one-size-fits-all solution. Things are never that simple, or easy.

    There are many crucial components to the app development process that require time, attention and expertise to succeed. The best low-code platforms support the specification of automated workflows and — this is very important — can integrate with various enterprise systems, applications and sources of data. Enterprise systems can be incredibly complex and manage multiple data sets and processes, and some can be outdated. To build enterprise apps with a low-code platform, you need to be able to connect to these systems and customize with the same nuance and security that a pro-code platform provides.

    Take, for example, the Facebook app. While it’s simple and easy to use even on a mobile phone, just imagine all the complexity that makes up the backend: data, algorithms, ad networks, moderation, reporting, etc. — all updating in real-time for billions of users. The same goes for other apps with complex backends but simple front ends, such as those used to manage health insurance companies, retailers, government agency portals, wayfinding apps for big box stores … These are just a few examples that customers of ours offer solutions for built using HCL Volt MX. HCL Volt MX allows organizations to build applications for any audience — consumers, partners and employees, across any device — native mobile, web and wearables. It also provides improved efficiency and higher developer productivity. The platform has robust services for identity, integration, orchestration, business-process automation and rules management. Paired with its low-code design environment, you can create consumer-grade apps across multiple touchpoints — fast.

    Learn more about HCL Volt MX

    Giving developers — and thus, the full enterprise app dev operation — a connected arsenal of front- and back-end tools to design and maintain a dynamic framework includes combining low-code accessibility with power tools that pro-coders expect. Hence, companies can ensure they’re not sacrificing customization, scalability and sustainability, even with the need for design velocity and speed-to-market.

    Bridge Front-End and Back-End Capabilities

    When you are deciding on your approach for delivering your next digital experience, you should have the best of low-code with a pro-code foundation that manages the complete software development life cycle on the terms that a full-stack developer expects. Meaning, you expect the platform to increase your velocity, offer rock-solid security and give you integrated DevOps and automated testing, simplified backend integration and the ability to use advanced technologies such as blockchain, augmented reality (AR) and conversational apps and more, with ease.

    Also, what happens when the application needs features or functionality not included in the pre-built building blocks? How do teams fill in the gaps that inevitably occur when connecting to existing enterprise systems? How will low-code provide the highest level of security over a full range of unique workflows and handle enterprise systems of dizzying complexity?

    In our experience, there is always a time when a full-stack developer experience can get the very most out of the low-code platform, especially when the app demands complexity in the integration and orchestration, needs to scale to millions of users and have a sticky, “pixel perfect” user experience.

    As Simple As You Want, As Expert As You Need

    Professional developers are looking for software that can boost productivity without sacrificing features that allow them to poke around and see what adjustments a given app needs to deliver a full-native mobile, web or wearable app experience. A low-code platform with pro-code support, such as HCL Volt MX, bridges gaps in the entire software development life cycle and brings the business stakeholders, digital innovators, designers and professional developers together to achieve their digital vision.

    You Get the Best of Both Development Options

    • Lightning-fast capabilities for implementing front-end experience, workflows and functions that enable the business to see how their vision comes alive.
    • A professional-grade infrastructure that can respond to the needs of the front-end features and handle the more complex integration and coding demanded by any enterprise business requirements.

    If you’re solely investing in a low-code platform to build web apps, your operation can quickly run out of steam. Being pro-developer grade means you can respond immediately to the intention of the app’s development concept, no matter the complexity and scale required — native mobile, web and wearables. After all, creating apps is never a “one-and-done” pastime; we all know it’s an iterative approach that wins the day. Make sure your low-code platform choice is pro-developer grade.

    Learn how HCL’s Volt MX provides a low-code approach that includes back-end support.