Category: Infrastructure/Networking

  • HPE Acquires Silver Peak to Gain SD-WAN

    HPE Acquires Silver Peak to Gain SD-WAN

    Hewlett Packard Enterprise (HPE) announced its intent to acquire Silver Peak, a software-defined wide area network (SD-WAN) platform provider, which will be incorporated into its Aruba Networks subsidiary.

    Keerti Melkote, president of Intelligent Edge for HPE, told industry analysts the $925 million acquisition will eventually lead to edge computing devices all being managed via the same cloud framework regardless of physical location.

    Aruba Networks has been making a case for unifying the management of wired and wireless networking in branch offices via a cloud management platform. The acquisition of Silver Peak will extend the reach of that framework to SD-WANs, which are becoming more widely employed to connect both remote offices and end users working at home to applications running both in the cloud and in the local data center.

    In the wake of the COVID-19 pandemic, the number of employees working from home and needing direct access to applications has exploded. Rather than employing virtual private networks (VPNs) to connect all those home offices to a local branch office, it’s more efficient and secure to connect those working at home to applications residing in both the cloud and on-premises IT environments via SD-WANs.

    HPE claims the total addressable market for networking services aimed at various edge computing use cases is north of $32 billion, which includes both SD-WANs and wireless and wired networks deployed in the branch office.

    Silver Peak currently has more than 1,500 customers and in its last fiscal year generated $132 million in revenue. The challenge HPE and its Aruba Networks subsidiary will face is most SD-WANs that have been deployed thus far use appliances that were acquired by internal IT teams. Increasingly, however, SD-WANs are being consumed as a managed service. Aruba provides customers access to a cloud console to manage networks deployed in remote offices. It’s not clear how many internal IT organizations moving forward will want to manage remote networks versus relying on a managed service provider (MSP).

    Of course, HPE and Aruba can opt to provide a managed service. However, they will need to build out the points of presence (PoPs) to deliver a managed SD-WAN service—something many MSPs, especially telecommunications providers, and cloud service providers have already done.

    Longer-term, it’s also not clear to what degree wireless 5G services will eliminate the need for not just wired networks, but also wireless local area networks (LANs) in branch offices. Some IT organizations may conclude the cost of a 5G cellular service is less than the total cost of managing a LAN.

    There is, of course, no absolute when it comes to networking. However, if more employees are working from home for the foreseeable future, the dynamics of networking at the edge will never be the same. Developers especially will need to take into account a whole different level of network latency dynamics when deploying applications. The irony is that as applications become more distributed, the management of the networks on which they depend is becoming more centralized.

  • Bringing NetOps Up to Speed With DevOps

    Bringing NetOps Up to Speed With DevOps

    Automation can be an unwieldy topic for network operations and DevOps teams who have enough challenges working together cohesively. Networks have been traditionally viewed as the long pole in the tent for emerging DevOps practices.

    But for DevOps practitioners and business leaders alike, there’s good news: NetOps are more prepared than ever to embrace automation and programmability—increasing the likelihood of on-time service delivery, with far less friction between IT teams.

    According to Enterprise Management Associates (EMA), a strong majority (77%) of organizations deem network automation a high priority, and 58% have already implemented or are planning to implement, approved solutions. This is an important and promising shift.

    Traditionally, network leaders have favored an operating model that emphasizes stability and resiliency over agility. Understandably so, as any network interruption can have a cascading impact on the business’ operations and profitability.

    While ensuring five 9s of availability remains a top priority for NetOps, the growing need to support DevOps, containerized infrastructure for applications and cutting-edge digital services—among other initiatives—continues to highlight some of the glaring inefficiencies of traditional network management tools that are too error-prone and bound by scalability issues.

    With the right automation framework, NetOps can play an equal part in enabling DevOps practices by becoming more adaptable to evolving business and application requirements in the cloud and locally.

    Centralizing Management With Cloud-Based Service Delivery

    For decades, improving agility has been a dyed-in-the-wool practice for network teams. Organizations worldwide have now realized enormous benefits by implementing new software-defined management tactics that allow the network to become more centralized, programmatic and dynamic in nature. By disaggregating software from hardware, networking teams now can manage many more services and devices with less effort and resources.

    Among NetOps’ new arsenal of tools and best practices, centralized management has become one of the key ingredients driving toward greater efficiencies. Utilizing a cloud-based approach for provisioning, deploying and managing network services closely mirrors the way IT has spun up cloud storage and compute over the last decade. Now, DevOps teams no longer have to wait days or weeks for the NetOps team to provision the right networking resources so that they can begin designing, testing and deploying new applications.

    Along with the added efficiencies, NetOps teams have greater and more uniform control over device configurations and policies, where security vulnerabilities lie in wait if these do not establish a zero-trust environment. Orchestrating these elements centrally, rather than device by device, places far less burden on individual network operators for protecting high-value corporate assets. Rock-solid network access control also reduces the risk of security or performance degradation that commonly arise from using an ad hoc patchwork of scripts, templates and CLI commands.

    Advancing Network Automation Frameworks

    Because creating a cloud-native network infrastructure does not all happen with the press of a button, network operations won’t become fully automated overnight. Other factors come into play that inhibit broader adoption of automation frameworks, including budget constraints, difficult technology implementations that lack integration with legacy systems and skill gaps for existing staff.

    It’s essential that NetOps teams embrace a network automation framework that aligns to current and future operating models. Through proactive collaboration, NetOps folks can extend the value of automation platforms already used by their DevOps or application counterparts.

    Fortunately for NetOps teams, myriad networking vendors today readily offer pre-built, certified solutions for DevOps platforms, making it easier to get started on a cloud-native journey by automating activities such as device onboarding and configuration changes. This way, network administrators can leverage existing vendor partnerships, in-house knowledge and technology that is already proven within the larger IT environment.

    Additionally, network engineers shouldn’t need—and won’t have the extra time—to become top-notch developers to take advantage of programmability during their cloud-native journey. Developing basic programming skills is advantageous, but network management systems that offer Python scripting, a consistent set of APIs and webhooks can perform the “heavy lifting” when it comes to enabling extensibility with third-party IT platforms.

    Today, this level of extensibility includes being able to integrate with third-party IT service management tools. A common use case that can realize significant time savings and greater network and application availability is to auto-trigger and assign an incident ticket when a performance SLA is breached. It’s very easy to collect and use machine learning-based tools to correlate all of the relevant diagnostics data in order for a network operator to immediately begin a root cause analysis and quickly resolve the issue.

    On the Horizon: AI-Driven Operations

    Another core aspect of DevOps is continuous improvement—both in terms of elevating service levels, as well as enhancing user experiences. But faster rates of change resulting from continuous improvement processes can negatively impact application performance, and the network is often the first to be blamed.

    But there is a huge silver lining within this cloud created by faster rates of change, which also highlights another growth area for NetOps teams to learn and master. That is, the use of AIOps.

    Today’s networks are bound by human scale. When things break, it takes a human to realize it broke, research the issue and then apply the fix. While traditional management and monitoring tools can alleviate some of the burden, alert fatigue often becomes a huge problem—in other words, too many false alarms, false positives or, worse yet, drawing attention away from more critical issues.

    AIOps tools and technologies mitigate these issues and limitations by combining artificial intelligence, machine learning, and advanced network analytics to automate many aspects of traditional monitoring and troubleshooting. Once deployed, IT organizations have the ability to predict and preempt failures,\ or quickly recover from issues when they do occur. This includes being able to:

    • Leverage ML-trained data sets to continuously monitor network performance and detect anomalies.
    • Eliminate guesswork by prioritizing fixes or improvement efforts and validating that those efforts have the desired business impact.
    • Continuously optimize network performance based on benchmarks.

    Put another way, AIOps systems are worth their weight in gold by helping networks move toward a self-healing, self-securing and self-optimizing model. Even in the interim, during the early phases of deployment, such AI-assisted operations can help IT identify and resolve network- or user-impacting issues faster and easier. The results are that dramatic.

    Next Steps: Bring a DevOps Mentality to NetOps

    Contrary to popular belief, the goals of NetOps are not diametrically opposed to DevOps. Both groups want to deliver more value and help the business innovate.

    Equipping NetOps teams to build on existing DevOps-based automation frameworks, paired with AI-driven insights and modern management tools, will go a long way in ensuring frictionless delivery of new services.

    Now is the time for network operations teams to get to know your DevOps team, learn how they operate and come together to create new methods for advancing the organization’s IT mission. The investment in time and effort should be a creative win-win for both groups and produce a big payoff in IT’s strategic position and importance to the organization.

  • Can NetOps and SecOps Finally Get Along?

    Can NetOps and SecOps Finally Get Along?

    For years, the very definition of NetOps and SecOps has involved friction and even contentious relationships that make their respective jobs more difficult and lessen their efficiency and effectiveness. Much of this conflict originates from having charters that are seemingly in opposition to each other. At the surface, NetOps stands for connectivity, openness, speed and capacity. In contrast, SecOps comes across as binary opponents, posting for far too many regulations with segmented connectivity and a more or less closed or impaired environment.

    The truth is, however, both groups have the same goals:

    • Ensuring business operations and agility.
    • Protecting resources.

    The network is only important in its ability to connect users, systems, applications, information or data and other resources, ensuring effective business operations and agility. The network is means to an end, and not necessarily an end to itself. In a somewhat similar way, security is also not an end, but, rather, the means to an end. Security exists to protect these same users and resources. It’s all about the users and resources being able to run business operations effectively and with the agility and flexibility necessary to give it strategic advantages. Reflecting on this perspective may help NetOps and SecOps realize that they are not so far apart from each other.

    Both NetOps and SecOps struggle with many of the same issues. Both are usually overworked and understaffed, responsible for critical components or aspects of business, face constantly changing environments and challenges and slowed by cumbersome processes and a lack of agility. Because of these things, NetOps and SecOps are largely in the same boat, sharing the same storm.

    netops secopsThe lack of agility is a particularly important issue, as new technologies and techniques are constantly being developed that enable security teams to stay ahead of—or at least keep pace with—attackers. Motivated attackers tend to be far more innovative that defenders and can use anything at their disposal to accomplish their goals. Entire cybercriminal supply chains exist to provide attackers with applications, utilities, routines and even services to conduct their campaigns. These things can and will be used against defenders.

    On the other hand, deploying a new security solution on the network is generally a long, involved, cumbersome process. Even changing solutions involves considerable effort. Sometimes the rules or process gets invented along the way, compounding the difficulties. Additions or changes to the network involve tedious review processes mostly dictated by NetOps. The NetOps team also faces some of these same difficulties in adding or changing network management or monitoring solutions.

    While a careful review is warranted, current processes are too time-consuming and involved. One significant improvement can come from NetOps and SecOps coming together with an established and codified approach for network changes or additions. Getting issues out on the table for discussion is a great start. This means more collaboration and a joint learning cycle on short- and long-term organizational objectives. Both groups need to understand and appreciate the concerns of the other and realize their common ground. Prioritizing issues and agreeing on a fundamental set will ease the overall process, reduce unwarranted fear and antagonism, and eliminate much of the inventing the process on the fly.

    An emerging approach seeks to establish a centralized deployment point for both networking and security solutions with pre-established rules agreed upon by both teams. Ideally, many of the concerns can be addressed or mitigated by hardware and software designed to enforce policies or rules, provide failover as necessary, prevent performance degradation or add to the attack surface. These can allow solutions to drop into the network while offering guarantees of performance or availability.

    Streamlining deployment of shared management will result in much-needed agility and also boost efficiency and overall effectiveness. It will also lessen the typical tensions or outright opposition.

    NetOps and SecOps are much closer to each other than either realizes. Their shared guardianship of users and resources can benefit from joint discussions, plans, tools and policies. Not only can they better accomplish their own charters of connecting and protecting while providing agility and flexibility, but they also can become far more efficient with their operations. They need each other, and their organizations need the vital contributions from both. As typically said in security jargon, “A chain is only as strong as its weakest link.” The new paradigm of security-driven networking is about preventing weak links through the collaboration and synergy between NetOps and SecOps.

  • Fastly Facilitates Observability at the Edge

    Fastly Facilitates Observability at the Edge

    Fastly this week announced it is adding the ability to collect tracing, customizable logging data and both real-time and historical metrics from a serverless computing framework designed to be deployed on edge computing platforms.

    Company CTO Tyler McMullen said the goal is to make it easier for IT to bring observability within the context of a DevOps to an edge computing platform.

    The Compute@Edge serverless compute platform enables IT teams to employ functions to execute code on an edge computing platform versus having to install virtual machines or containers. Those edge computing platforms are connected to a content delivery network (CDN) managed by Fastly.

    McMullen said that approach provides a way to deploy microsecond applications at the edge while still attaining observability in keeping with best DevOps practices. Otherwise, edge computing platforms become yet another black box that provides IT teams with no visibility.

    DevOps teams can send real-time logs to 27 and counting supported endpoints. Default log fields are automatically exposed to better determine the root cause of any issue. DevOps teams can also capture custom event details.

    Metrics such as CPU and RAM utilization can also be surfaced either in real-time or on a historical basis. The Compute@Edge service also honors request tracing parameters by maintaining them when they enter and leave the Fastly platform. Developers can tag individual end user requests with unique identifiers that can be shared with third-party platforms such as Datadog.

    Currently available in beta, Compute@Edge makes it easier for IT teams to employ a serverless computing framework to drive event-driven applications at the edge, McMullen said. Latency issues that arise when applications attempt to access cloud services are pushing more organizations to deploy real-time applications at the network edge. Functions running on a local serverless computing platform enable IT teams to achieve that goal in a way that consumes the smallest amount of IT infrastructure possible, he added.

    With the rise of 5G networking services, it’s now only a matter of time before the number of platforms on which a DevOps team needs to deploy code expands significantly. Most DevOps teams are already challenged by all the unique platforms to which need to deliver code. Edge computing could potentially exacerbate those issues because each edge computing platform tends to have unique attributes. A common serverless computing framework running on each of those edge computing platforms could help streamline continuous delivery.

    Of course, it’s too early to say what impact the downturn on the economy will have on edge computing projects. In theory, at least, organizations are gearing up to deploy these applications in anticipation of wireless 5G connectivity services being widely available and affordable. Chances are high, however, with more organizations not willing to send people to install applications on those endpoints manually, reliance on DevOps processes and CDNs to automate application delivery at the edge will become a requirement.

  • Report: SD-WAN Shift to the Cloud Accelerates

    Report: SD-WAN Shift to the Cloud Accelerates

    The rate at which software-defined wide area networks (SD-WANs) are being consumed as a cloud service appears to be accelerating in the wake of the COVID-19 pandemic.

    A global survey of 750 IT professionals conducted by the market research firm Vanson Bourne on behalf of Barracuda Networks finds over half of respondents (52%) are looking to acquire an SD-WAN solution via a cloud provider, with Microsoft Azure being cited as the most preferred option.

    Only 16% said they prefer an SD-WAN from an independent vendor, while 15% would opt for a telecommunications provider. Another 12% said they would rely on a reseller.

    Klaus Gheri, vice president of network security for Barracuda Networks, said the survey suggests that as application workloads move into the cloud, more IT organizations want to centralize acquisition of networking services alongside compute and storage. As such, he said, providers of SD-WAN appliances such as Barracuda Networks will need to evolve to extend the basic SD-WAN capabilities provided by cloud service providers.

    At the same time, Gheri noted that way applications are being accessed is also evolving as more employees are working from home. Rather than directly accessing applications running in a local data center or office, many organizations are routing access requests to those applications through their cloud service provider. That approach reduces costs by using a public internet connection to access to cloud service, which then routes that request over a virtual private network (VPN) to a local data center.

    Given the egress charges a cloud service provider requires, that approach may not reduce costs in the case of every workload. However, it may reduce costs by reducing the amount of network traffic moving across a leased MPLS line, he noted.

    Gheri said the rise of the cloud as a networking conduit illustrates how varied SD-WAN implementations have become. Organizations increasingly need some capability at the client level to automatically determine which network path makes the most sense for any request based on cost and latency requirements.

    In the meantime, frustrations with VPN clients continue to mount. Most VPN implementations were designed to support a small percentage of employees for occasional access. With more employees working from home more frequently, many organizations are reconsidering their SD-WAN strategies. In addition to being able to scale services more easily, Gheri noted SD-WANs also afford organizations the opportunity to implement zero-trust networking services to better isolate application environments in the event of a security breach.

    Over the last few years, SD-WANs have been one of the fastest-growing categories in IT. The Barracuda survey found 23% of respondents have already deployed SD-WAN, with another 51% either in the process of deploying or expecting to deploy one within the next 12 months.

    Clearly, competition between cloud service providers, telecommunication carriers and independent providers of SD-WAN services will intensify in the months ahead. The challenge facing IT teams now is determining to what degree they want to be directly involved in managing SD-WAN networks versus simply consuming SD-WAN services on an as-needed basis.

  • Why the Success of Edge Computing Relies on a Linux Legacy

    Why the Success of Edge Computing Relies on a Linux Legacy

    At this point you’ve certainly heard rumblings of the promises of edge computing and may wonder if it’s right for your organization and how to assess its viability. The way we think about edge is as a decentralized extension, or evolution, of cloud computing, enabling many of the same technologies and applications to be leveraged in areas/locations that weren’t possible before.

    I believe that the promise of edge computing and the opportunity it unlocks is valuable enough to be a major driver in our industry over the next decade. Here’s how to think about implementing edge computing in your organization. 

    Getting Started

    Since edge is an evolving space, the exploration of edge computing should start as soon as possible, and we’d recommend a phased implementation approach to help deal with change as it comes. 

    Many of the companies we work with who delayed their cloud initiatives found that it contributed to their falling behind from a technology standpoint. Given the choice, it’s better to deal with some sharp edges — no pun intended — than to fall behind your competitors in reaping the benefits.

    Edge requires careful life cycle analysis at the beginning of the journey, rather than an afterthought. The decentralized nature of edge computing raises the stakes and amplifies any potential problems you would have in other computing scenarios. So as you begin, keep in mind issues such as adaptable infrastructure, security and life cycling between hardware and software.

    The Value of Adaptability, Linux and Open Source

    Twenty-five years ago, innovation was a slow, laborious, bug-filled crawl — with any advances crippled by proprietary technology. The breakthrough that paved the way for the continuous, rapid pace of innovation possible today was Linux.

    We need to heed the lessons from the early days around private cloud adoption and, more recently, Linux containers with regards to adaptability. Many man-hours were lost in slash-and-burn style rebuilding of infrastructures. The logistics at the edge make it impractical to have the same learn-as-we-go freedom we had inside the datacenter. 

    As we’re likely to see edge computing evolving quickly, the only adaptable architectures will be the ones that can avoid a total tear-down. Adaptable architectures will also be well-positioned to take advantage of the newer capabilities as they become available. 

    Remember, Linux has a strong history in the embedded world and is well adept at tackling a number of the historic challenges in this space. The more immediate impact is being felt at the distribution level. Our distributions, for example, have objectives around minimization and we expect to see more low-level enablement work on the security side for edge happening in the near future.

    For edge computing to reach its full potential, we need to be completely driven by open source and open standards. What we’ve learned from previous technology waves is that while most proprietary technologies have their merits, they miss out on the multipliers that can come from a thriving community.

    Final Considerations

    Security is a longer topic on it’s own, but given that we’re giving up many of the security barriers that are easy to take for granted in the datacenter and cloud (physical access, networking perimeter, security groups/policy, etc.), we are going to rely more and more on lower-level hardware and operating system security.

    No company wants to risk a common vulnerability across a hundred thousand nodes. This makes it our job to keep enterprise deployments from following the pattern of some consumer-grade devices that are long out of software maintenance.

    For edge computing innovation, we need to be thinking more about how we create sustainable solutions and technologies given how many deployments will require a longer life cycle and are more tightly bound to hardware and equipment refreshes. The path of innovation leads from Linux to and through the network edge. Companies that follow this approach will be better positioned to leverage the promise and power of the edge while avoiding fragmentation and lock-in.

  • Making SD-WAN More Secure and Flexible

    Making SD-WAN More Secure and Flexible

    Cloud and managed services enable companies to focus scarce IT resources on business outcomes. According to Gartner, the “market size for cloud is growing exponentially, and cloud is projected to be a $317 billion industry by 2022.”

    Managed service providers (MSPs) leverage the power of software-defined wide area networks (SD-WAN) to offer higher quality services and reduce branch network costs. SD-WAN offers compelling advantages for distributed organizations with critical branch operations, including the benefits of business agility, improved application performance and lower bandwidth costs.

    MSPs invest considerable time and energy in ensuring that their servers, applications, data centers and people are always available. The same amount of attention needs to be paid to managing customer connectivity, as connectivity issues will result in customer support and retention issues, together with increases in cost and decreases in monthly recurring revenue.

    While bringing connectivity to the data center is viewed as a customer-driven activity —  meaning that MSPs are relying on end-users and carrier networks to deliver their customer experience — managing that connectivity is primarily, but not always, the responsibility of the MSP.

    However, the quality, performance and security of carrier networks can be outside of the MSP’s control, creating vulnerability in the MSP’s service delivery and revenue process. Many MSPs are, therefore, rightly concerned about the safety of end-user data as it passes over the carrier networks. Outsourcing security measures and data assurance for end-users’ critical data can sometimes be undesirable and, thus, should be considered as part of a risk mitigation strategy.

    Making SD-WAN More Secure and Flexible

    A challenge that most MSPs face is ensuring that their customers’ data is encrypted safely in an SD-WAN environment and the integrity and confidentiality of that data is assured.

    An on-premise, scalable encryption management solution that can integrate into an SD-WAN without disrupting an MSP’s environment provides the flexibility MSPs are seeking. In addition, the utilization of micro-segmentation using cryptography to prevent lateral movement of threats between segments can protect the confidentiality and integrity of the end-user’s data providing the security both parties need.

    A viable encryption solution that makes the SD-WAN environment more secure and flexible provides the data assurance MSPs and their end-users are seeking, while mitigating risk and reducing the attack surface for everyone.

    Data Assurance with Separation of Duties

    Layer 4 encryption provides data assurance and eliminates risk for both the MSP and the end-user with the separation of duties, allowing the end-user to encrypt and protect their data prior to sending it over the MSP/carrier networks. Through crypto-segmentation, fine-grained policies are defined and enforced to protect the confidentiality and integrity of the end-user’s data.

    In practice, this means that MSPs do not take on the risk of having to manage and protect the confidentiality and integrity of their customers’ data, nor do they have to accept risk to protect end-user data when it’s on their network — it remains the responsibility of the end-user.

    Similarly, the end-user can eliminate risk to their data from both the MSP and whatever carriers they, or the MSP, may be using for the connectivity; they do not have to trust the carrier team or network to be secure.

    Ensuring Fine-Grained Regulatory Policies with Crypto-Segmentation

    Most MSPs will have enterprise, government and high assurance customers, all of whom are under varying data protection regulations. The end-user can now use crypto-segmentation to create separate policies and data flows, thus eliminating risk by defining fine-grained policies that are difficult to infiltrate.

    Crypto-segmentation enables MSPs with customers who must adhere to different or multiple industry and/or government regulations — for example, to generate these fine-grained policies by each customer and regulation (GDPR, PCI, CJIS, NERC CIP) etc. 

    Scalable Implementation Into Any Network or Transport

    Lastly, a scalable, network agnostic overlay which integrates easily and sits on top of SD-WAN can make the SD environment more secure for MSPs and their customers without disrupting the current network architecture and with zero impact to performance. This solution should be fully interoperable with the SD-WAN, scale to support the breadth and depth of the customer’s environment and operate without impacting the SD-WAN core functionality. 

    Conclusion

    MSPs and their end-users need to mitigate the risks and vulnerabilities associated with multiple carrier networks. In order to achieve this, it is essential that MSPs investigate flexible and secure data assurance solutions that help both carriers and end-users to take advantage of the management services provided by MSPs and provide critical separation of duties to mitigate risk for both parties.

  • SonicWall Adds Multi-Gigabit Switches to SD-Branch Portfolio

    SonicWall Adds Multi-Gigabit Switches to SD-Branch Portfolio

    SonicWall has added a line of multi-gigabit switches to its software-defined (SD)-branch offering that unifies the management of wireless access points and firewalls that include software-defined wide area network (SD-WAN) capabilities.

    Dmitriy Ayrapetov, vice president of platform architecture for SonicWall, said the switches will replace a series of switches that SonicWall had been reselling from Dell Technologies. SonicWall spun out of Dell at the end of 2018 after being acquired in 2012.

    SonicWall has been making a case for unifying the management of remote office networking via a central management console dubbed Capture Security Center. To achieve that goal, the company embedded SD-WAN capabilities in its firewalls while expanding its portfolio to include wireless access points and switches.

    Ayrapetov said in the wake of the COVID-19 pandemic, interest in centralizing the management of remote offices has increased for two reasons: First, IT teams are no longer inclined to travel to remote offices unless there is an absolute requirement; and second, following the economic downturn brought on by the pandemic, there’s more interest in reducing costs—an issue SonicWall addresses by consolidating the management of networking and security.

    As part of its SD-Branch offering, SonicWall also makes available client software in multiple forms, providing IT teams with capabilities such as URL filtering to block access to malicious websites that can be applied to any device on the network, including systems that employees are using to work from home. That capability makes it possible for IT organizations to enforce cybersecurity policies regardless of where employees are located or what network they are using to access IT resources in a branch office, said Ayrapetov.

    Longer-term, Ayrapetov said it’s clear organizations are moving toward zero-trust networking architecture to better ensure cybersecurity using SD-WANs and other technologies to access cloud applications. However, in the short-term, most organizations will continue to rely on virtual private networks (VPNs) to access IT resources located in a branch office, on-premises data center or public cloud.

    SonicWall has been making a case for its Boundless Cybersecurity platform, which can be broadly applied across a distributed computing environment. At the core of that platform is its Capture Advanced Threat Protection (ATP) cloud sandbox service that relies on deep memory inspection in real-time, machine learning and cyber threat intelligence to identify malware and other potential threats.

    As part of that architecture, SonicWall also provides zero-touch deployment capabilities, which eliminate the need for extensive cybersecurity expertise to deploy its appliances and services.

    It’s not clear to what degree organizations will be consolidating the management of networking and cybersecurity. However, the smaller the organization, the more likely one team is managing both networking and security. As the number of cybersecurity threats organizations face continues to rise at a time when IT budgets are under massive pressure, chances are high many larger IT organizations soon also will be consolidating the management of networking and security.
  • Aruba Injects AIOps Into Network Management

    Aruba Injects AIOps Into Network Management

    Aruba, a Hewlett Packard Enterprise (HPE) company, this week launched a platform that leverages artificial intelligence (AI) to identify and remediate networking issues before they have an impact on end users.

    Patrick LaPorte, senior director of cloud and software solutions marketing, said the Aruba Edge Services Platform (ESP) applies algorithms to data collected for customer networks and aggregated by Aruba in the cloud. That approach enables the company to apply AIOps to automate the management of both software-defined wide area networks (SD-WANs) and Wi-Fi access points.

    Aruba has been making a case for converging the management of SD-WANs and Wi-Fi access points in remote offices for a couple of years now. With the downturn in the economy brought on by the COVID-19 pandemic, the need to reduce the total cost of networking is even more pressing, LaPorte said.

    The Aruba ESP platform further reduces the total cost of networking by augmenting network administrators with AIOps capabilities that will enable a smaller team to centrally manage via the cloud a much larger number of network services being delivered to remote offices, he said.

    At the same time, Aruba enables IT organizations to implement zero-trust network security by providing built-in support for role-based access, dynamic segmentation of network services and identity-based intrusion detection to authenticate, authorize and control every user and device connected to the network, said LaPorte.

    The Aruba approach to AIOps revolves around Aruba Central, a cloud service based on Kubernetes the company relies on to manage networking equipment that runs ArubaOS services. Aruba claims to have more than 65,000 customers using Aruba Central to manage network services.

    Aruba Central has been enhanced to include AI Search, a data discovery service based on a natural language processing (NLP) engine that enables IT teams to employ English-language queries to extract user and device information from the data lake created by Aruba ESP. The company has also added user-centric analytics to better identify client, application and network performance issues.

    Aruba has also added a faster Aruba CX 6200 Switch Series that includes built-in analytics and automation capabilities.

    Finally, Aruba has launched Developer Hub, which provides access to its application programming interfaces (APIs) and documentation to applications that leverage the Aruba ESP platform.

    The way network services are being managed and delivered to remote offices is dramatically changing as applications become more distributed. At the same time, the entire definition of what constitutes a remote office in the age of COVID-19 is being transformed as more employees work from home. Aruba is addressing that challenge by making it easier to set up network tunnels between home offices and remote offices managed by Aruba Central, said LaPorte.

    As networking continues to evolve there is no doubt IT organizations will be relying more on automation and AI to deliver network services as scale. Less clear is the degree to which IT organizations will be willing to standardize on networking equipment from a single vendor to achieve that goal. In theory, IT organizations can reduce their total cost by standardizing on a single vendor. In practice, however, many IT environments are comprised of a dizzying array of networking equipment from multiple vendors.

    Regardless of what path forward is chosen, it’s already apparent the current networking status quo will not hold for much longer.

  • A10 Networks Allies with Dell for ADC Infrastructure

    A10 Networks Allies with Dell for ADC Infrastructure

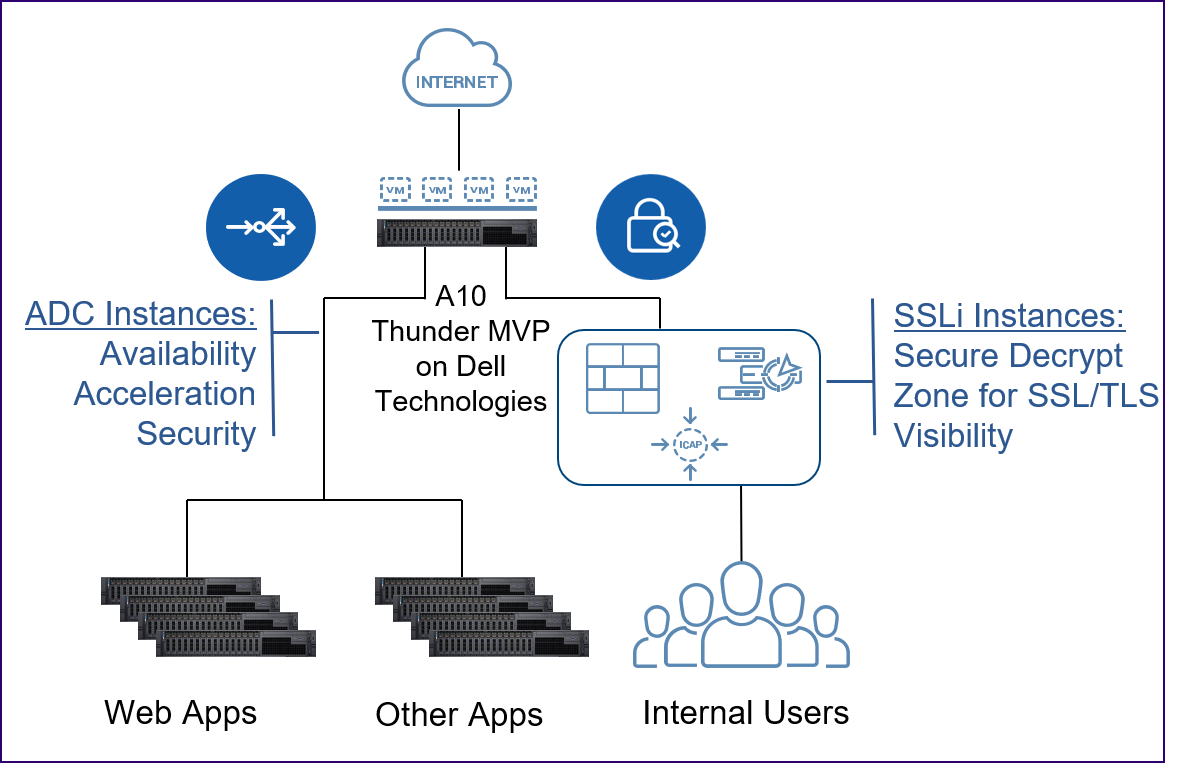
    A10 Networks announced today it has partnered with Dell Technologies to make its application delivery controller (ADC) and A10 Thunder Multi-tenant Virtual Platform (MVP) available on Dell servers.

    Gunter Reiss, vice president of worldwide marketing for A10 Networks, said this alliance reduces the cost of deploying ADCs in on-premises IT environments by taking advantage of industry-standard hardware platforms based on x86 processors beginning in the third quarter. Those servers, however, will only be available in the Americas market.

    Specifically, the A10 Thunder ADCs are designed to run on Dell EMC PowerEdge R640XL and R740XL servers, as well as Dell EMC Virtual Edge Platform 4600. The A10 Thunder MVP is designed to run on Dell EMC PowerEdge R640XL and R740XL servers. IT teams can move A10 ADC licenses across these platforms as they best see fit, said Reiss.

    In the wake of the economic downturn brought on by the COVID-19 pandemic, A10 Networks expects more IT organizations will look to rationalize their server portfolio, he said, noting as a major supplier of those servers, partnering with Dell affords A10 Networks an opportunity to expand the base of potential customers.

    Standardizing on a single server platform also affords some organizations the opportunity to reduce their carbon footprint in the data center, he added.

    It’s too early to say how aggressively IT organizations will be consolidating IT infrastructure. However, the total cost of IT increases whenever an organization adds a new platform or vendor. Many IT organizations have already standardized on a single server vendor as part of an effort to reduce management costs. In fact, Reiss said A10 is betting rival ADC vendors will be shut out of IT environments if they require IT organizations to acquire dedicated hardware.

    In the meantime, the number of ADCs required by IT organizations is increasing as the application environment becomes more complex. The rise of microservices-based applications is requiring IT teams to focus more on application latency issues that occur when more modules of code are sharing access to the same IT infrastructure.

    A10 Networks helps address that issue by embedding analytics into that A10 Harmony Controller that is employed to centrally manage all A10 ADCs deployed in a distributed computing environment. That capability makes it simpler for IT organizations to embrace best DevOps practices, Reiss noted.

    ADCs are also playing a larger role in security by first offloading encrypted SSL/TLS traffic and then providing visibility into that traffic to prevent data leakage.

    In general, Reiss said DevOps teams are exercising more ownership of ADC platforms. Network and security operating teams still play a major role; however, it’s clear IT functions are starting to converge, he said.

    It remains to be seen to what degree those roles will ultimately converge. Each IT organization is likely to pursue a slightly different path toward converging network operations and DevOps. The challenge and the opportunity will be overcoming the inherent cultural challenges associated with bringing together IT teams that historically have not had much cause to interact with one another.