Category: DevOps Practice

  • Five Great DevOps Job Opportunities

    Five Great DevOps Job Opportunities

    devopsy.kinsta.cloud is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted to better serve our audience.

    Our goal in these challenging economic times is to make it easier for DevOps professionals to advance their careers.

    Of course, the pool of available DevOps talent is still relatively constrained, so when one DevOps professional takes on a new role it tends to create an opportunity for others.

    The five job postings shared this week are selected based on the company looking to hire, the vertical industry segment and, naturally, the pay scale being offered.

    We’re also committed to providing additional insights into the state of the DevOps job market. In the meantime, for your consideration:

    SimplyHired.com

    D2 Consulting
    Springfield, Virginia
    DevOps Engineer
    $150,000 to $180,000

    Indeed.com

    Mariner Finance
    Remote
    DevOps Engineer
    $120,000 to $150,000

    ZipRecruiter

    Cogility Software
    Irvine, California
    DevOps Engineer
    $110,000 to $140,000

    CareerBuilder.com

    BAE Systems
    Manassas, Virginia
    DevOps Engineer
    $92,290 to $156,860

    Dice.com

    Rackner
    Falls Church, Virginia
    Software DevOps Engineer
    $90,000 to $140,000

  • 5 Serverless Challenges of DevOps Teams and How to Overcome Them

    5 Serverless Challenges of DevOps Teams and How to Overcome Them

    Serverless is a cloud computing execution model where the cloud provider dynamically manages the allocation of machine resources. The term ‘serverless’ might be somewhat misleading as it doesn’t mean servers are not involved. Instead, it means that developers no longer have to think about servers, even though they’re running on them.

    The idea is to abstract the infrastructure away so that developers can focus solely on the code. Functions, the units of code, are triggered by a variety of events, including HTTP requests, database events, queuing services, monitoring alerts, file uploads, scheduled events (cron jobs), and user sign-ups or in-app activities.

    The Importance of Serverless for DevOps Teams

    Serverless computing brings a paradigm shift in how applications are built, deployed and managed, directly impacting DevOps teams. The core advantage of serverless for these teams is the significant reduction in operational overhead. With serverless, the cloud provider takes responsibility for running the server, ensuring its reliability, and scaling the infrastructure. This frees DevOps teams from the routine tasks of server provisioning, maintenance, and patching, allowing them to focus more on optimizing the application’s code and business logic.

    However, this shift also demands a change in mindset and approach. DevOps teams must adapt to a more granular, event-driven architecture that serverless promotes. They need to design systems thinking about individual functions and how they interact, instead of traditional monolithic applications or even microservices. This requires a deeper understanding of the cloud environment and its services, as serverless functions are often tightly integrated with other cloud services like databases, message queues, and API gateways.

    Moreover, serverless computing introduces new challenges in areas like security, monitoring, and cost management. For instance, the ephemeral nature of serverless functions can make traditional monitoring approaches less effective, and the dynamic scaling can lead to unpredictable costs. DevOps teams need to develop new strategies and adopt specialized tools to address these challenges. Despite these issues, the benefits of serverless – in terms of agility, scalability, and potential cost savings – make it an increasingly essential tool in the DevOps arsenal, particularly for organizations looking to innovate and deploy rapidly in a cloud-centric world.

    5 Serverless Challenges of DevOps Teams and How to Overcome Them

    1. Complexity of Monitoring in Serverless

    A main challenge in the serverless world is the complexity of monitoring. Unlike traditional architectures where you can monitor physical or virtual servers, in serverless, you need to monitor individual functions. This can be tricky as you may have hundreds or even thousands of functions running simultaneously.

    To effectively monitor serverless architectures, you need to go beyond traditional methods. You need tools that can provide insights at the function level, such as AWS CloudWatch or Azure Monitor. These tools allow you to monitor metrics like execution time, error rates, and invocation counts for each of your functions.

    But monitoring is not just about gathering metrics. It’s also about understanding the relationships between your functions and other components of your system. For this, you need distributed tracing tools like AWS X-Ray or OpenTelemetry, which can provide a detailed view of how requests flow through your system.

    2. Managing Lambda Cold Starts

    One of the most common serverless challenges that DevOps teams face is cold starts. A “cold start” refers to the delay that occurs when a function is invoked after being idle for a while. This delay can significantly impact the performance of your applications, especially those that rely on real-time processing.

    The first step to managing Lambda cold starts is understanding what triggers them. Typically, a cold start happens when a new instance of your function is created, which can be due to several reasons, such as an increase in traffic, the deployment of a new version of your function or after a function has been idle for too long.

    To overcome this challenge, there are several strategies you can employ. First, you can use provisioned concurrency, a feature offered by AWS Lambda that allows you to keep a specified number of function instances warm and ready to respond to invocations. Another strategy is to design your applications to be resilient to cold starts by implementing retry logic or using asynchronous invocation when possible.

    3. Security Concerns in Serverless Architectures

    Security is a top concern for any DevOps team. In serverless architectures, you have less control over the underlying infrastructure, making it more difficult to ensure the security of your applications.

    The first step to securing your serverless applications is understanding the shared responsibility model. In a serverless environment, the cloud provider is responsible for securing the infrastructure, while you are responsible for securing your code and configurations. This means you need to pay extra attention to things like input validation, error handling and secure configuration practices.

    Another key aspect of serverless security is managing permissions. Each of your functions should have the least privileges necessary to perform its task. This can be achieved by using identity and access management (IAM) services provided by your cloud provider.

    4. Managing Third-Party Dependencies

    Managing third-party dependencies is another challenge that DevOps teams often face in serverless architectures. These dependencies can introduce vulnerabilities into your applications, affect the performance of your functions, and even increase the cost of your serverless deployments.

    The key to managing third-party dependencies is to minimize their use. Only use dependencies that are necessary for your application and regularly review them to ensure they are still needed. You should also keep your dependencies up-to-date to benefit from the latest security patches and improvements.

    When using third-party dependencies, it’s also important to understand their impact on your functions. You can use tools like AWS X-Ray or Google Cloud Trace to monitor how these dependencies affect the performance of your functions.

    5. Cost Management and Optimization

    While serverless can be cost-effective, it’s easy to rack up high bills if you’re not careful. This is because in serverless, you pay for every invocation of your functions, even if they result in errors.

    To manage costs in serverless, you need to monitor your usage closely. Tools like AWS Cost Explorer or Google Cloud Billing can provide insights into your spending and help you identify areas for optimization.

    You can also optimize costs by designing efficient functions. This means writing code that executes quickly and efficiently, minimizing the use of third-party dependencies, and managing the concurrency of your functions.

    In conclusion, while serverless technologies offer many benefits, they also present unique challenges for DevOps teams. By understanding these challenges and employing the right strategies, you can effectively manage and overcome them, ensuring the successful delivery of your serverless applications.

  • SmartBear Acquires Reflect to Gain Generative AI-Based Testing Tool

    SmartBear Acquires Reflect to Gain Generative AI-Based Testing Tool

    SmartBear this week revealed it has acquired Reflect, a provider of a no-code testing platform for web applications that leverages generative artificial intelligence to create and execute tests.

    Madhup Mishra, senior vice president of product marketing at SmartBear, said the platform Reflect created will initially be incorporated into the company’s existing Test Hub platform before Reflect’s generative AI capabilities are added to other platforms.

    Reflect provides access to a natural language interface to create tests using multiple large language models (LLMs) that it is designed to invoke. It can also understand the intent of a test to understand what elements to test regardless of whether, for example, a button has been moved from one part of a user interface to another, said Mishra. Test step definitions, once approved, can also be automatically executed using scripts generated by the platform.

    SmartBear has no plans to build its own LLMs, said Mishra. Rather, the company is focusing its efforts on providing the tools and prompt engineering techniques needed to effectively operationalize them, he added.

    Reflect is the tenth acquisition SmartBear has made as part of an effort to provide lightweight hubs to address testing, the building of application programming interfaces (APIs) and analysis of application performance and user experience. Last year, the company acquired Stoplight to gain API governance capabilities.

    Rather than building a single integrated platform, the company is focused on providing access to lightweight hubs that are simpler to invoke, deploy and maintain, said Mishra. The overall goal is to meet IT teams where they are versus requiring them to adopt any entirely new monolithic platform that requires organizations to rip and replace every tool they already have in place, he said.

    There is little doubt at this point that generative AI will have a profound impact on application testing in a way that should ultimately improve the quality of the applications. As the time required to create tests drops, more tests will be run. Today, it’s all too common for tests not to be conducted as thoroughly as they should be simply because either a developer lacked the expertise to create one or, with a delivery deadline looming, they simply ran out of time.

    Naturally, the rise of generative AI will also change how testing processes are managed. It’s not clear how far left generative AI will push responsibility for testing applications, but as more tests are created and run, they will need to be integrated into DevOps workflows.

    Of course, testing is only one element of a DevOps workflow that is about to be transformed by generative AI. DevOps teams should already be identifying manual tasks that can be automated using generative AI as part of an effort to further automate workflows that, despite commitments to automation, still require too much time to execute and manage. Once identified, DevOps teams can then get a head start on redefining roles and responsibilities as generative AI is increasingly operationalized across those workflows.

  • Diffblue Integrates Generative AI-Based Testing Platform With GitLab

    Diffblue Integrates Generative AI-Based Testing Platform With GitLab

    Diffblue this week generally made available an integration between its automated unit testing platform for Java and the DevSecOps platform from GitLab.

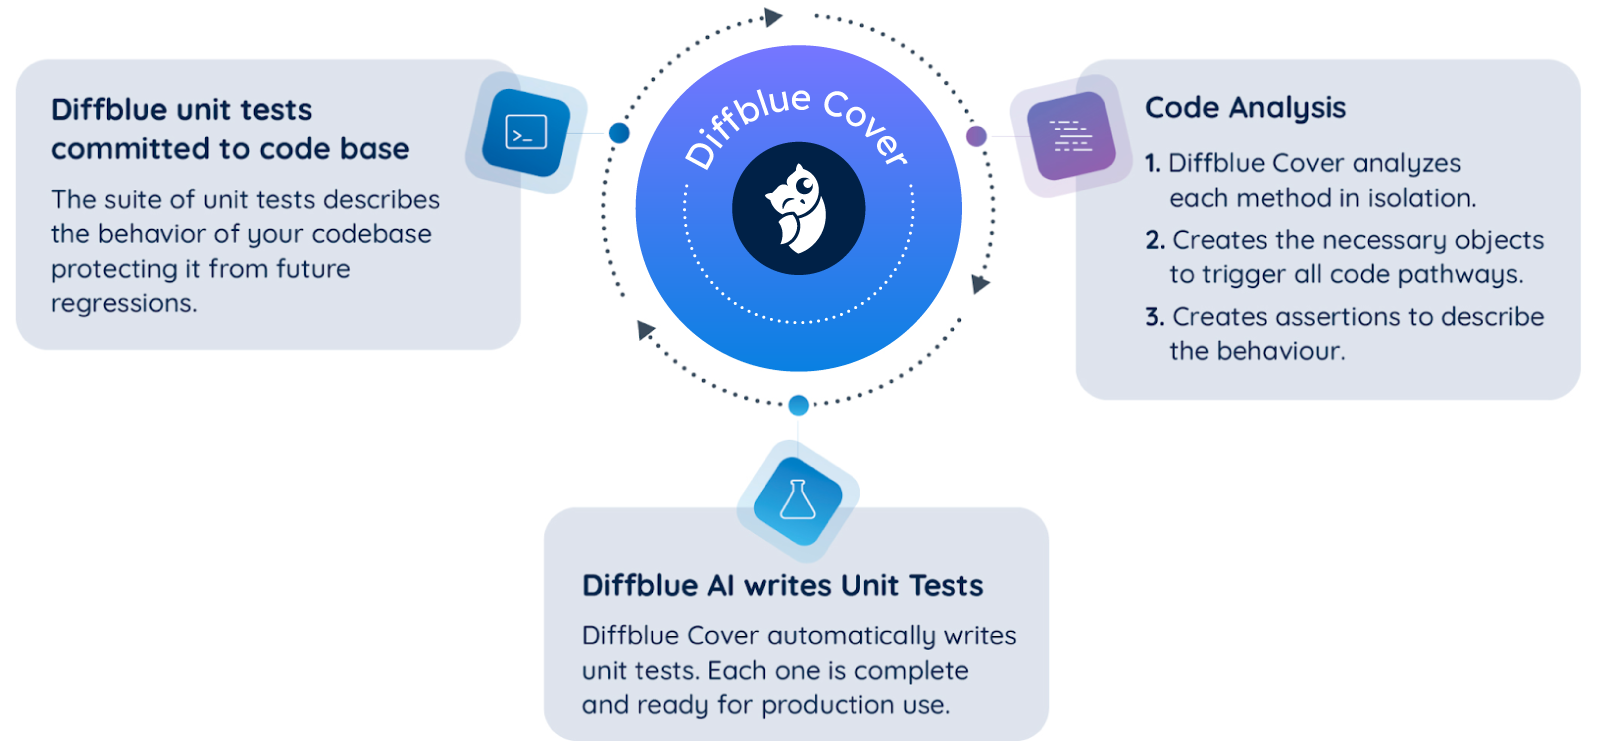
    The Diffblue Cover platform makes use of generative artificial intelligence (AI) to automatically create unit tests based on reinforcement learning technologies that don’t rely on LLMs—avoiding their drawbacks of sometimes introducing hallucinations and also requiring human review.

    Diffblue CEO Mathew Lodge said the integration with the continuous integration capabilities found in the premium and ultimate editions of the GitLab platform would, for example, streamline regression testing in a way that should ultimately improve both application quality and security. Diffblue Cover, for example, can update tests as much as 250 times faster than a human developer can write them manually without developer review.

    That approach also serves to reduce the level of friction many DevSecOps teams encounter when bottlenecks involving testing processes emerge, noted Lodge. The overall goal is to make it simpler for developers to test as much of their own code as possible before integrating it into a build, he added. Otherwise, developers will get fed up because testing is continuously breaking the build, noted Lodge.

    Ultimately, instead of having to write unit tests, developers become supervisors of a platform that automatically generates them on their behalf, said Lodge. The job of a developer doesn’t go away, but it does fundamentally change, he added.

    To achieve that goal, developers need to be able to access a platform that writes the tests and can then also execute them automatically. If it takes too long to create the test, chances are high that most developers won’t run it. On average, writing and evaluating a single unit test can take a developer 10 minutes. Over the course of any project, thousands of tests need to be written, so the amount of time testing takes away from coding is often much greater than most IT leaders fully appreciate.

    Automating those tests should improve developer productivity as more time is available to focus on writing code rather than testing. That doesn’t necessarily eliminate the need for a dedicated testing team, but it does mean that more tests will be run without slowing down the overall pace of application development.

    Developers naturally want to be able to test code at the very instant they create it. AI platforms can make that happen by, for example, employing reinforcement learning to write unit regression tests.

    Most developers are not going to resist assuming more responsibility for testing if the tools to automate that task are more accessible. Instead of merely shifting responsibility for testing left toward developers, DevOps teams need to find ways to streamline the process. Otherwise, testing just becomes one in a series of tasks that are being shifted to developers in ways that many of them are coming to resent.

    It may take some time before AI is fully integrated into software engineering but it’s clear with each passing day more previously manual tasks are being automated. Among the lowest hanging fruit for applying AI to software engineering are clearly testing processes that, if truth be told, few indeed enjoy conducting.

  • New Relic Adds Ability to Correlate IT Events to Business Processes

    New Relic Adds Ability to Correlate IT Events to Business Processes

    New Relic this week added an ability to enable DevOps teams to better understand the potential business impact any change to an IT environment might have.

    Manav Khurana, chief product officer for New Relic, said New Relic Pathpoint adds a dashboard to the company’s observability platform through which business metrics can be collected alongside telemetry data. That data is collected either via connectors provided by New Relic or via a metrics application programming interface (API) that IT teams can invoke.

    IT teams can use that API to connect to custom applications or an end-to-end business process, noted Khurana.

    All that data is then modeled alongside DevOps telemetry data to provide insights into the impact any change might have on the business in real-time, he added. That approach provides the added benefit of making it easier to strategically align the management of applications, services and infrastructure by business function, noted Khurana.

    In the near future, New Relic will also extend the natural language capabilities it is currently previewing to New Relic Pathpoint, he said.

    Longer term, New Relic is working toward making it possible to model how proposed changes to business processes will impact IT environments, added Khurana.

    Business and IT leaders intuitively understand that every business event creates a corresponding IT event, but most organizations manage those processes in isolation. New Relic Pathpoint presents an opportunity to close a divide between IT teams and the rest of the business that has plagued organizations for decades.

    It may be a while before advances in data analytics and AI eliminate that divide completely, but creating a common set of metrics for managing business and IT processes is a crucial first step.

    In the meantime, DevOps teams, in addition to accelerating the pace at which applications can be built and deployed, are being asked to employ observability platforms such as New Relic One to minimize disruption to the business. Observability has always been a core DevOps tenet, but achieving and maintaining it is challenging. Most DevOps teams today aspire to be able to maintain some level of continuous monitoring. However, as it becomes easier and less costly to instrument applications using open source agent software, interest is rising in observability platforms that simplify the investigation of anomalies indicative of an issue that could disrupt an application environment. As that shift occurs, more organizations will seek to correlate IT and business events.

    It’s still early days as far as the adoption of observability platforms is concerned, but it’s apparent that as application environments become more complex, the plethora of monitoring tools that DevOps teams rely on will need to be streamlined. It’s not uncommon for DevOps teams to have multiple monitoring tools that surface a set of predefined but often conflicting metrics. Observability platforms, however, unify logs, metrics and traces in a way that makes it simpler to launch queries to identify the root cause of an issue, hopefully before any catastrophic disruption can occur.

  • 5 Security Threats DevOps Teams Should Know

    5 Security Threats DevOps Teams Should Know

    DevOps security, also known as DevSecOps, is a philosophy in which security practices are integrated into the DevOps process. DevOps security involves creating a ‘security-as-code’ culture with ongoing, flexible collaboration between release engineers and security teams. The DevSecOps movement, much like DevOps itself, is focused on creating new solutions for complex software development processes within an agile framework.

    DevOps security is about breaking down silos and promoting open collaboration across teams. It’s about making everyone accountable for security with the ultimate aim of improving the quality and speed of code releases. The adoption of a DevOps security model necessitates a cultural shift across the organization. It requires the integration of security into every aspect of the development and operations processes.

    DevOps Security is not just about implementing tools and technologies; it’s about changing the way we look at security. Rather than being an afterthought, security should be a key part of the ongoing conversation from the start of the project to the end.

    5 Security Threats DevOps Teams Must Know About

    As a DevOps professional, it’s crucial to be aware of the potential threats that could compromise your systems, applications, and data. Let’s take a look at the top five security threats that DevOps teams must be aware of.

    Phishing Attacks

    Phishing attacks are a common security threat that can lead to data breaches. These attacks involve cybercriminals impersonating legitimate organizations to trick individuals into revealing sensitive information, such as passwords and credit card numbers.

    Phishing attacks can be particularly damaging for DevOps teams. They can lead to unauthorized access to development systems and data, which can lead to devastating supply chain attacks. For example, an attacker could trick a team member into revealing their login credentials for a critical system, allowing the attacker to gain access and inject malware into a CI/CD pipeline.

    Code Injection

    Code injection is another common security threat that DevOps teams must be aware of. This involves the exploitation of an application by injecting malicious code. The attacker can then execute the malicious code to compromise the system or steal sensitive data.

    For DevOps teams, code injection attacks can be particularly harmful. These attacks can lead to compromised systems and applications, resulting in data breaches and significant downtime.

    Man-in-the-Middle Attacks

    Man-in-the-middle attacks are a type of security threat where the attacker intercepts and potentially alters the communication between two parties without their knowledge. This can lead to a range of damaging outcomes, including data theft, session hijacking, and even identity theft.

    For DevOps teams, man-in-the-middle attacks can be particularly problematic. These attacks can lead to compromised systems and data, and even the unauthorized alteration of code.

    Container Vulnerabilities

    Container vulnerabilities are a significant security threat for DevOps teams. Containers are a key technology in the DevOps world, allowing for the rapid and reliable deployment of applications. However, like any technology, they come with their own set of security risks.

    These vulnerabilities can range from use of insecure images, to misconfigurations and software bugs, to more serious issues like kernel exploits. If an attacker is able to exploit a container vulnerability, they could potentially gain control over the entire system.

    DDoS Attacks

    Last but not least, distributed denial-of-service (DDoS) attacks are a significant security threat that DevOps teams must be aware of. These attacks involve overwhelming a production environment with traffic, causing it to become unavailable to users.

    For DevOps teams, DDoS attacks can be particularly damaging. Not only can they lead to significant downtime, but they can also result in lost revenue and damage to the organization’s reputation.

    How to Mitigate These DevOps Security Threats

    While these security threats are concerning, there are effective strategies and techniques that can be used to mitigate them.

    Implement Email Security Practices and Tools

    To combat phishing attacks, it’s crucial to implement email security tools that can detect and block phishing attempts. These tools can help to filter out phishing emails, reducing the likelihood that team members will fall victim to these attacks.

    In addition to implementing email security, it’s also important to provide security awareness training for team members. This training should cover the basics of cybersecurity, including how to recognize and respond to phishing attempts.

    Use Input Validation and Sanitization in Applications

    To protect against code injection attacks, it’s important to use input validation and sanitization in applications. Input validation involves checking that the data provided by a user meets certain criteria before it’s processed by the application.

    Input sanitization, on the other hand, involves cleaning up the data to remove any potentially harmful elements. This can help to prevent malicious code from being executed within the application.

    Employ HTTPS and SSL/TLS Encryption for Data in Transit

    To guard against man-in-the-middle attacks, it’s important to employ HTTPS and SSL/TLS encryption for data in transit. This ensures that any data being sent between the user and the application is encrypted, making it much more difficult for an attacker to intercept and read the data.

    Regularly Scan Containers for Vulnerabilities

    To protect against container vulnerabilities, it’s crucial to regularly scan containers for vulnerabilities. This involves using tools that can analyze the containers and identify any potential security risks.

    By regularly scanning containers, DevOps teams can identify and address vulnerabilities before they can be exploited by an attacker.

    Implement Rate Limiting and Network Filtering

    Finally, to mitigate the risk of DDoS attacks, it’s important to implement rate limiting and network filtering. Rate limiting involves restricting the number of requests that a user can make to the application within a certain period of time.

    Network filtering, on the other hand, involves blocking traffic from certain IP addresses or ranges that are known to be associated with DDoS attacks. This can help to reduce the impact of a DDoS attack and protect the availability of the application.

    In conclusion, DevOps security is a crucial aspect of the DevOps process. By being aware of potential security threats and taking steps to mitigate them, DevOps teams can significantly reduce the risk of a security breach and ensure the ongoing success of their projects.

  • Survey: Widespread Inability to Remediate App Vulnerabilities

    Survey: Widespread Inability to Remediate App Vulnerabilities

    A survey of 621 IT and security professionals published this week found only 20% are confident in their ability to detect a vulnerability before an application is released.

    Conducted by the Ponemon Institute on behalf of Security Journey, a provider of cybersecurity training services for developers, the survey finds 61% struggling to remediate vulnerabilities effectively, with 55% blaming misalignment between development, security and compliance teams for delays.

    A third of respondents (33%) said teams lacked a common view of applications and assets, with 38% acknowledging they lack the ability to hold departments accountable for patching applications. Only 11% of organizations believed they patch vulnerabilities effectively in a timely manner, the survey finds.

    In the 12 months prior to the study, 54% of respondents suffered a security incident due to an unpatched vulnerability, with 51% experiencing more than eight incidents.

    Overall, half (50%) admitted they fail to test the security of their applications after they have been released. Only 36% specifically teach developers to write secure code. Just one-fifth (21%) educated developers on vulnerability remediation. Less than half (43%) have invested in training provided by a third party.

    When training is provided, 68% of respondents also admitted immediate feedback is not provided and less than half (47%) said secure coding training is customized to meet developer needs. Half (50%) of those who provided training have no formal assessment to measure knowledge gain, the survey found.

    Amy Baker, chief marketing officer and security education evangelist for Security Journey, said the survey makes it clear much work still needs to be done in terms of teaching developers how to write secure code.

    In addition, too many software development teams are overly optimistic about their ability to remediate known vulnerabilities the next time they plan to update an application, said Baker. Many developers move on to the next application simply because either the pressure to meet delivery deadlines is too intense or there is some other emerging technology, such as large language models (LLMs), that needs to be learned, she added. In fact, too many organizations are far too focused on the rate at which applications are built and deployed at the expense of cybersecurity, Baker noted.

    That’s especially problematic because cybercriminals have become much more adept at monitoring application deployments and updates, she added.

    The amount of time between when code is deployed and when cybercriminals begin scanning it for vulnerabilities is now measured in hours rather than days. Developers, unfortunately, are deploying more insecure code than ever. In fact, much of that code is insecure by design, noted Baker.

    Overall, nearly half of respondents (48%) only train developers annually, bi-annually or when an incident occurs. More than two-thirds (68%) only train developers on how to implement secure coding practices to meet compliance requirements. In effect, because developers are not taught security in school, what training they do receive is on the job, said Baker.

    Clearly, there is still much work to be done when it comes to implementing DevSecOps best practices to improve application security. In the meantime, the amount of code that needs to be patched has already reached proportions that most application development teams are never going to be able to effectively address.

  • Venafi Adds Ability to Prevent Unauthorized Code From Running

    Venafi Adds Ability to Prevent Unauthorized Code From Running

    Venafi added an ability to prevent unauthorized code from running in IT environments that make use of its machine identity management platform.

    Shivajee Samdarshi, chief product officer at Venafi, said the Stop Unauthorized Code Solution leverages the company’s CodeSign Protect offering to ensure that only authorized code can run on any given platform.

    The overall goal is to enable organizations to better secure their software supply chains using a zero-trust approach to software based on identity management and code signing to verify software comes from an approved source and complies with policy controls, he added.

    All code is signed using private digital certificates or those issued by trusted certificate authorities, said Samdarshi. Before code can execute, the security platforms an organization has in place can be configured to check that digital signature against trusted code signing certificates, he noted.

    Interest in securing software supply chains has risen sharply since the Biden administration issued an executive order requiring federal agencies to implement a range of measures, including code signing, to achieve that goal. However, securing software chains is often more challenging than organizations initially appreciate.

    In fact, a recent Venafi survey found that 70% of security and IT leaders believe that software supply chain attacks are their biggest security blind spot. Additionally, 85% believe that continuous security validation of the CI/CD pipeline is vital to reduce the risk of vulnerabilities going undetected during the software development lifecycle. A full 88% said they believe machine identity management is essential to the success of zero-trust models that are being more widely adopted across enterprise IT environments.

    Arguably, the most important thing organizations need to focus on is making sure application developers and cybersecurity professionals develop a working relationship. The biggest barrier to the adoption of DevSecOps best practices required to secure software supply chains remains largely cultural. For more years than anyone cares to admit, many developers have viewed cybersecurity more as a hindrance to application development that needs to be overcome or circumvented rather than being a core aspect of a quality assurance process. The total number of vulnerabilities that exist in applications running in production environments could likely be measured in the billions.

    Remediating all those vulnerabilities may never be practical, but at the very least, DevSecOps teams could make sure that no new code containing vulnerabilities is allowed to execute. Cybercriminals have become especially adept at inserting malware into code that they hope will find its way into any number of downstream applications before they activate it. That capability alone should help mollify cybersecurity teams that are increasingly being tasked with improving software supply chain security. The challenge is those cybersecurity teams don’t always appreciate the impact new policies can have on the pace at which applications are developed and deployed.

    Like it or not, software supply chains will generally be more secure in 2024. The only thing that remains to be determined is how much friction will be injected into DevSecOps workflows to achieve that goal.