Category: DevOps Practice

  • OpenText Extends Tool for Auditing Source Code Using Machine Learning

    OpenText Extends Tool for Auditing Source Code Using Machine Learning

    OpenText this week updated a static analysis tool it provides to audit code using machine learning algorithms to provide deeper insights into on-premises IT environments.

    Announced at the OpenText Security Summit 2024 conference, the latest generation of Fortify Audit provides additional artificial intelligence (AI) models capable of learning the unique attributes of custom source code.

    The latest version of Fortify Audit Assistant also adds the ability to detect drift in a model and, if necessary, automatically refresh it. OpenText is now committing to refreshing those models every quarter.

    The discriminant AI model from OpenText enables machine learning algorithms to learn how humans conducted an application audit to then run similar tests on other applications. Previously, Fortify Audit relied on the same core model to audit both on-premises and software-as-a-service (SaaS) applications based on data collected by OpenText. Fortify Audit Assistant now provides support for more than 30 language-specific models to improve testing performance.

    Dylan Thomas, senior director for Fortify engineering and product for OpenText Cybersecurity, said this capability ensures that any sensitive data never leaves an on-premises IT environment.

    The overall goal is to streamline the number of alerts that would otherwise overwhelm a DevSecOps team trying to identify the root cause of an issue, he added. For example, Fortify Audit Assistant will identify test code that is not vulnerable because it was never deployed in an actual production environment. That approach makes it easier for DevOps teams to prioritize which vulnerabilities to fix first in their source code using a lightweight AI model that still enables them to deeply scan source code, noted Thomas.

    Historically, DevSecOps teams need to make a trade-off between lightweight approaches and deep scans of source code that is no longer required, he added.

    As regulations pertaining to software supply chain security become more stringent the number of development teams that will be subject to some type of audit is only going to increase. The cost of failing an audit will also inevitably increase as regulatory bodies look to make examples of organizations that are not properly securing their software supply chains.

    It’s not clear how aggressively organizations are embracing best DevSecOps practices to address myriad software supply chain security issues that were highlighted in an executive order issued by the Biden administration to Federal agencies. However, with the rise of AI and other forms of automation, it should become simpler to identify more vulnerabilities before they wind up being exploited in a production environment.

    There will always, of course, be a need to secure production environments because there’s always a probability mistakes will be made. However, given the lax practices many organizations have employed to build and deploy applications, it’s probable the number of vulnerabilities that exist in production environments today is beyond counting. In many cases, the better part of valor might be to replace many of those applications entirely with ones built using DevSecOps best practices.

    Regardless of the path to better application security chose the one thing that is certain is cybercriminals are only going to become even more adept at discovering those vulnerabilities.

  • 10 Key Features of AI Code Assistants

    10 Key Features of AI Code Assistants

    One of the most potent tools that have emerged to streamline the coding process is code assistants. Code assistants are software tools designed to assist programmers by providing suggestions and automated features that help in writing code more efficiently and accurately. They act as virtual aides, making the coding process faster, more intuitive and less prone to errors.

    Code assistants can be categorized into two types: Rule-based and AI-based. Rule-based assistants follow predefined rules and perform according to set guidelines. They are mainly used for syntax highlighting, code formatting and basic error detection. AI-based code assistants can learn from past coding patterns, predict what a programmer is trying to achieve and suggest appropriate code snippets. They are capable of understanding the context of the code and providing accurate suggestions, as well as generating entire blocks of code based on natural language instructions. Read this blog post for examples of popular AI coding assistants.

    Whether you are an experienced software developer handling complex projects or a beginner, coding assistants can automate the tedious aspects of coding, allowing you to focus more on problem-solving and innovation.

    The Growing Importance of AI in Software Development

    As software development becomes more complex and time-sensitive, the role of AI in this field has grown significantly. AI-driven code assistants represent a major shift in how software is developed. They bridge the gap between human expertise and the efficiency of automated processes. 

    AI in software development not only speeds up the coding process but also enhances the quality of the code. These tools can analyze vast amounts of code, learn from it and apply that learning to assist developers in real-time. They can adapt to different coding styles and requirements, making them versatile tools for a wide range of programming tasks. Furthermore, as software projects increase in size and complexity, AI code assistants become crucial in managing and navigating these complexities. They offer intelligent insights, detect potential issues before they become problematic, and assist in keeping large codebases clean and manageable.

    In addition to increasing efficiency, AI code assistants are instrumental in reducing the barrier to entry in software development. They make coding more accessible to people with varying levels of expertise, including those who are new to programming. This accessibility is essential in an era where the demand for software development skills is continuously rising. By providing real-time assistance and learning resources, AI code assistants are not just tools for current developers but also learning aids for future generations of programmers.

    10 Key Features to Expect from Code Assistants in 2024

    With the rapid advances in large language models (LLMs), the following features are becoming standard in coding assistants as we enter 2024.

    Advanced Contextual Understanding

    Modern code assistants are evolving to understand the context of code more intricately. Unlike simple autocomplete tools, these AI systems can analyze the broader scope of a project, recognizing patterns and offering suggestions that align with the overall architecture and design patterns. This advanced understanding not only streamlines coding but also aids in maintaining consistency throughout the codebase.

    Real-Time Code Optimization Suggestions

    AI tools can proactively recommend changes to improve performance and efficiency. For instance, a code assistant might suggest a more efficient algorithm or highlight redundant code blocks that can be simplified. This feature not only enhances code quality but also serves as a learning tool for developers, exposing them to best practices and alternative approaches.

    Enhanced Debugging Assistance

    Debugging is often a time-consuming aspect of development. In 2024, expect code assistants to revolutionize this process by offering enhanced debugging assistance. Through deep analysis, these tools automatically detect errors and anomalies, suggesting potential fixes. They can pinpoint the exact location of a bug and provide context, significantly reducing the time developers spend in the debugging phase.

    Automated Refactoring

    Refactoring is crucial for maintaining clean code, and AI-driven assistants now offer sophisticated automated refactoring capabilities. They intelligently suggest changes that improve code readability and maintainability, such as restructuring code or renaming variables for clarity. These suggestions will be particularly beneficial for managing and updating legacy code, ensuring it adheres to modern coding standards.

    Code Documentation Generation and Update

    Keeping documentation updated is a challenge. Code assistants can now automate this task by generating and updating documentation in real-time. As code changes, the documentation will reflect these updates, ensuring that it always stays in sync with the codebase. This feature will be invaluable in large teams where keeping track of changes can be daunting.

    Predictive Coding Assistance

    Moving beyond reactive suggestions, code assistants will offer predictive assistance. By analyzing coding patterns and project structures, these tools will predict a developer’s next steps and offer relevant suggestions even before they are explicitly requested. This proactive approach will speed up the development process, reducing the cognitive load on developers.

    Understanding and Responding to Developer Queries in Natural Language

    Developers can pose queries or express coding requirements in plain English, and the assistant will interpret and execute these requests. Chat-based interfaces offered by leading AI coding assistants take this one step further. This advancement will make coding more intuitive and accessible, especially for beginners or non-expert users.

    Real-Time Suggestions and Conflict Resolution in Team Projects

    Collaboration in coding projects can lead to conflicts and inconsistencies. Code assistants now offer real-time suggestions and automated conflict resolution for team projects. These tools will identify potential conflicts in merge requests and suggest optimal resolutions, enhancing team collaboration and maintaining code integrity.

    Personalized Coding Assistance Based on Past Interactions

    Personalization is becoming a significant feature of code assistants. By learning from past interactions with a developer, these tools will tailor their suggestions and support to align with individual coding styles and preferences. This adaptive learning approach ensures that the assistance provided is most relevant and efficient for each developer.

    Enhancing Accessibility of Coding for Non-Expert Users

    One of the most impactful features of code assistants is their role in democratizing coding. By simplifying complex coding concepts and automating mundane tasks, these tools will make software development more accessible to non-experts. Beginners and those learning new programming languages will find these assistants particularly useful, as they provide guidance and learning aids.

    Conclusion

    Code assistants powered by AI are becoming an integral part of the software development process. They not only make coding faster and more efficient but also reduce the chances of errors, making the resultant software more reliable. The role of code assistants is only expected to grow, bringing in more advanced and intuitive features. Whether you are a seasoned programmer or a newbie, embracing code assistants can be a game-changer for your coding journey.

  • Salesforce Adds Ability to Apply Custom Security Policies to APIs

    Salesforce Adds Ability to Apply Custom Security Policies to APIs

    Salesforce today added the ability to customize security policies for application programming interfaces (APIs) to the Mulesoft Anypoint API management platform.

    Gerry Egan, vice president of product management for Mulesoft at Salesforce, said this capability makes it possible for organizations to use an Anypoint Flex Gateway Policy Development Kit to streamline development of custom API security policies that can be implemented as code.

    In addition to providing integrations with integrated development environments (IDEs), the Anypoint Flex Gateway Policy Development Kit also provides test policies that can be employed to ensure API security.

    That approach makes it simpler to ensure APIs are secure as they are being built and deployed within the context of an automated DevOps workflow versus having to rely entirely on a separate API security platform, he noted.

    The Mulesoft Anypoint Gateway already comes with security policies that DevSecOps teams can readily implement. Salesforce is now adding the ability to apply custom policies that DevOps teams can apply as it becomes apparent cyberattacks against APIs are becoming more sophisticated, noted Egan. Those policies can, for example, be used to remove sensitive data or replace it with a token, he added.

    Responsibility for API security is often not well established in many organizations, but as more accountability for API security shifts left toward DevSecOps teams, there is growing interest in addressing the issue as code when APIs are developed and deployed. While cybersecurity teams are responsible for maintaining cybersecurity after APIs are deployed, few of them have any insight into how an API is crafted. That’s a significant issue because cybercriminals have become more adept at both exfiltrating data via external facing APIs in addition to manipulating the underlying business logic to compromise a digital process, noted Egan.

    The Mulesoft Anypoint Gateway automates the process of building and applying security policies to APIs as part of the software development life cycle (SDLC) in a way that minimizes any impact on developer productivity, he added. That approach provides the added benefit of reducing the level of cognitive load developers would otherwise experience if they had to manually create software policies, said Egan.

    In general, most APIs are internally facing, but it’s not uncommon for them to suddenly be exposed to the internet as application use cases evolve. The best way to ensure API security is at the point of creation. Providing developers with API security tools gives them an opportunity to address security issues at the beginning of the application development process.

    There have already been several cybersecurity breaches involving APIs in the past year. It may only be a matter of time before there are additional breaches that could prove catastrophic. Regardless of the size of the API breach, the application development team that created and deployed the API in the first place is ultimately going to be held accountable for fixing it. The challenge is to find the simplest way to eliminate the issue in the first place at a time when the number of APIs being built and deployed only continues to explode.

  • IBM Adds Lower-Cost Linux Mainframe to Portfolio

    IBM Adds Lower-Cost Linux Mainframe to Portfolio

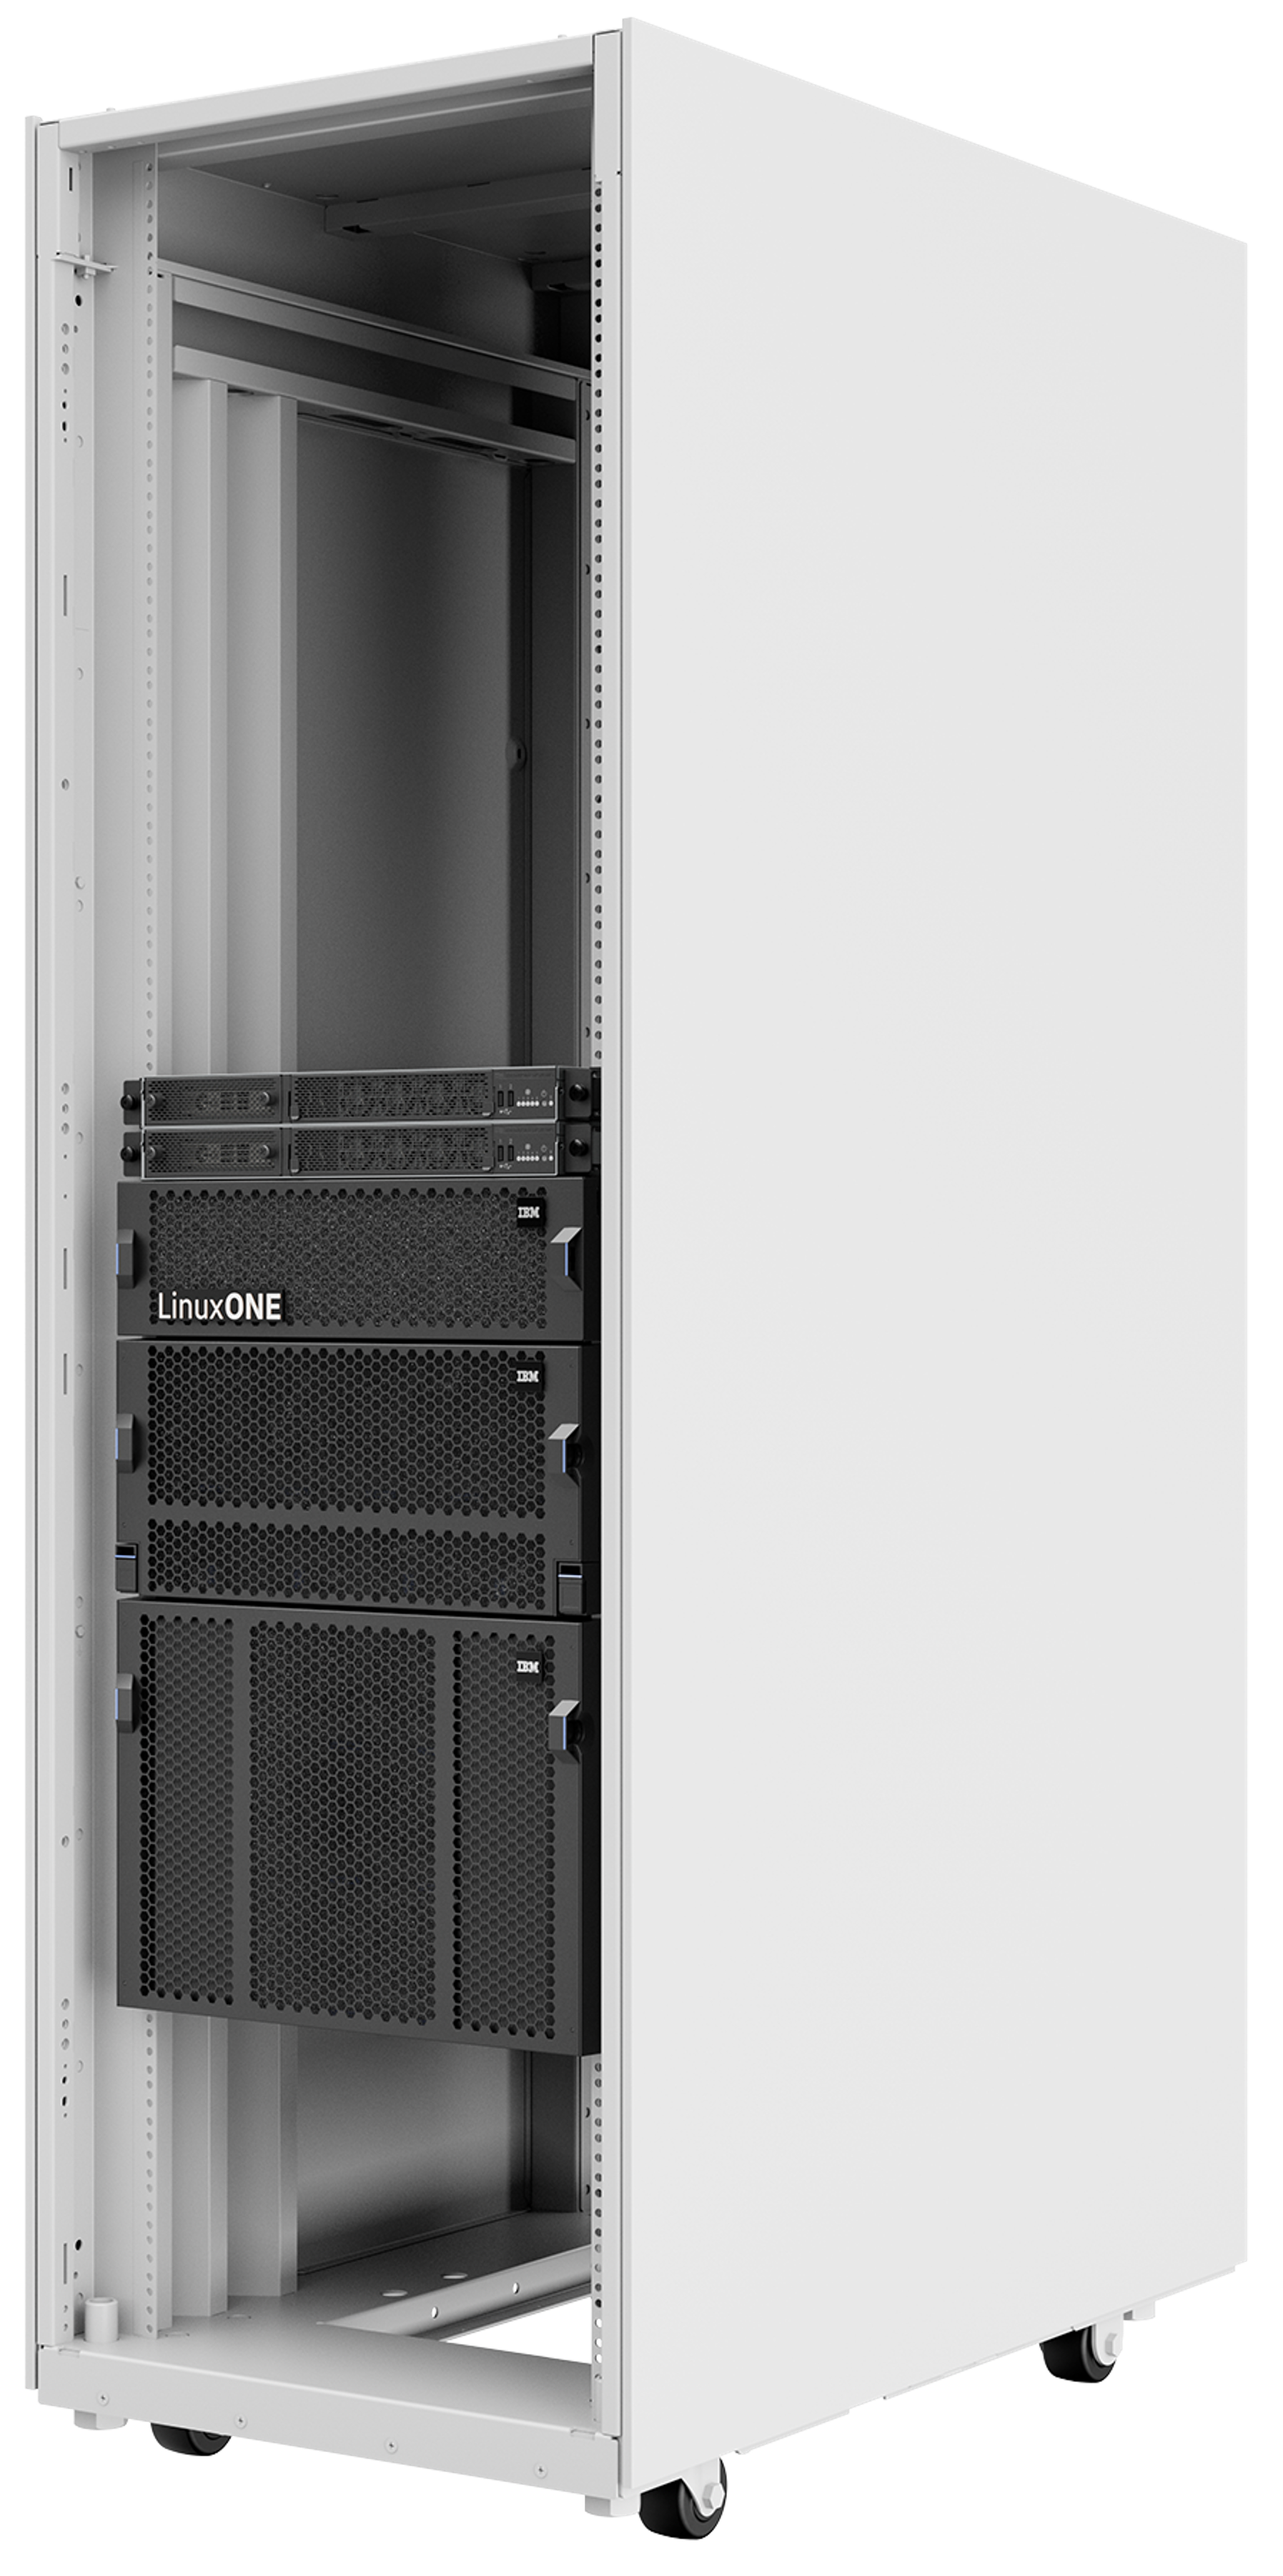
    IBM today made its most aggressive move yet in its quest to make mainframes running Linux more affordable, launching an entry-level platform starting at $135,000.

    The IBM LinuxONE 4 Express is a pre-configured rack system that is based on the same 5.2Ghz IBM Telum processor that IBM uses in its Z16 series of mainframes.

    In addition, the platform supports IBM Secure Execution, which is designed to thwart any attempt to decrypt data in the future using quantum computers.

    IBM claims organizations that move Linux workloads from x86 servers to an IBM LinuxONE 4 Express can save over 52% on their total cost of ownership over five years.

    The overall goal is to make it simpler for organizations to consolidate workloads that otherwise would need to be deployed across a distributed computing environment, she added. That approach ensures higher levels of availability for workloads that are increasingly processing massive amounts of data using two levels of physical and two levels of virtual cache in a way that consumes less energy, noted Tina Tarquinio, vice president of product Management for IBM Z and LinuxONE.

    The IBM LinuxONE 4 Express also includes an integrated accelerator for running artificial intelligence (AI) inference engines using more than 6 TFLOPs compute capacity per chip.

    IBM expects that as more organizations process sensitive data to drive AI applications, there will be increased interest in deploying applications in more secure on-premises IT environments, said Tarquinio. Mainframes provide a more cost-effective way to achieve that goal at a time when DevOps teams are embracing methodologies such as platform engineering to centralize the management of workloads, she added.

    At the same time, increased reliance on automation is making it simpler for IT teams to rely on multiple types of platforms to optimally process workloads. That capability enables IT teams to make platform decisions that are based on fit-for-purpose best principles more easily, noted Tarquinio.

    It’s not clear how many organizations will now be able to afford a mainframe when the initial cost of an x86 server is still much lower. But in the face of ongoing economic uncertainty, it seems more organizations are willing to consider all their options. The issue is that adding additional X86 servers is often viewed as the path of least resistance to increasing compute capacity.

    Naturally, each IT team will need to decide what path forward makes the most sense for them, but as workloads continue to become more data-intensive, it’s clear that infrastructure requirements are changing. The more data that needs to be processed, the more challenging it becomes to maintain service level agreements that are based on maintaining specific levels of application performance, noted Tarquinio.

    The challenge now is determining where best to run those workloads across an increasingly hybrid cloud computing environment that continues to offer more options as IT platforms evolve and expand.

  • Five Great DevOps Job Opportunities

    Five Great DevOps Job Opportunities

    devopsy.kinsta.cloud is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted to better serve our audience.

    Our goal in these challenging economic times is to make it easier for DevOps professionals to advance their careers.

    Of course, the pool of available DevOps talent is still relatively constrained, so when one DevOps professional takes on a new role it tends to create an opportunity for others.

    The five job postings shared this week are selected based on the company looking to hire, the vertical industry segment and, naturally, the pay scale being offered.

    We’re also committed to providing additional insights into the state of the DevOps job market. In the meantime, for your consideration:

    Dice.com

    Travelers
    Hartford, Connecticut
    DevOps Tech Lead
    $133,500 to $220,300

    Indeed.com

    Lawrence Berkeley National Laboratory
    San Francisco, California
    Identity and Access Management DevOps Engineer
    $126,900 to $214,140

    SimplyHired.com

    Workday
    Pleasanton, California
    Software Development Engineer
    $112,500 to $204,000

    LinkedIn

    IBM
    Denver, Colorado
    DevOps Engineer
    $110,100 to $161,100

    CareerBuilder.com

    Cognizant Technology Solutions
    Oakdale, New Jersey
    DevOps Manager – Technology Modernization
    $95,500 to $212,600

  • Graylog Makes Free API Security Tool Available to Developers

    Graylog Makes Free API Security Tool Available to Developers

    Graylog this week made available a free version of its platform for securing application programming interfaces (APIs), intended to encourage developers to adopt best practices to secure them.

    The free version of Graylog API Security has all the capabilities of the paid version but is limited to 16GB of local rolling storage on a single node with a one-year renewable license.

    Graylog CEO Andy Grolnick said the goal is to make it simple for developers to use this edition of the platform as they are building APIs. As applications are deployed in a production environment, the expectation is organizations will then need to access the version of the platform that is designed to scale, he added.

    Based on technology Graylog gained with the acquisition of an API security platform originally developed by Resurface.io, this free version of Graylog’s API security platform is trying to help bridge the divide between the application development teams that create APIs and the cybersecurity teams tasked with protecting them, said Grolnick.

    Capabilities of the platform include API classification, discovery, risk scoring, an ability to capture API request and response payloads and continuous monitoring of API and threat signatures in real-time. Collectively, these capabilities enable Graylog API Security to provide high-fidelity alerts using a data lake that is embedded in the platform, noted Grolnick.

    That approach enables Graylog API Security to capture all API requests and response details to distinguish valid API traffic from malicious activity involving, for example, data exfiltration hiding under valid response codes.

    In addition, Graylog API Security automatically surfaces remediation guidance for developers who typically lack cybersecurity expertise.

    API security has become a major DevSecOps issue because cybercriminals are increasingly targeting APIs to steal data. As more externally facing APIs are deployed, the overall size of the attack surface that needs to be defended increases exponentially.

    A recent survey conducted by Enterprise Strategy Group (ESG) on behalf of Graylog found more than three-quarters of respondents (76%) have an average of 26 APIs per application. Most respondents are using open APIs for public consumption (67%) or are connecting applications with partners (64%).

    In general, most of those APIs are internally facing, but it’s not uncommon for those APIs to suddenly be exposed to the internet as use cases for applications evolve. The challenge is that few cybersecurity teams have visibility into APIs that, when manipulated by malicious actors, can expose code or provide a mechanism through which business processes can be compromised. This issue often exists because, in many organizations, it’s still not clear who is actually responsible for API security.

    Arguably, the best way to ensure API security is at the point of creation. Providing developers with API security tools gives them a chance to do the right thing from the beginning of the application development process, said Grolnick.

    There have already been several cybersecurity breaches involving APIs in the past year. It may only be a matter of time before there are additional breaches that could prove catastrophic. Regardless of the size of the API breach, the application development team that created and deployed the API in the first place is ultimately going to be held accountable for fixing it.

  • Why Startups are Betting Big on Low-Code/No-Code

    Why Startups are Betting Big on Low-Code/No-Code

    It is exhaustive — from infrastructure to app delivery, from data to applications — to modernize your practices, processes and providers to ensure you have the underlying foundation to take advantage of whatever comes next.

    Two or three years ago, apps created through low-code/no-code platforms were not usually as detailed under the surface as software developed from scratch, yet they sufficed for certain purposes. There was even a clear distinction between software developers and everyone else out of necessity because software development was incredibly difficult to master.

    But now, as we head towards more advanced AI, the SaaS-based low-code/no-code (LCNC) platforms empower businesses to create software exponentially faster and cheaper than a code-based approach.

    The future, therefore, of startups in this changing business landscape becomes even more competitive, taking into account the increasing importance of customer-centric UI modeling, data product development and cutting-edge technologies like machine learning and deep learning.

    High-Value Acceleration

    Applications built through traditional software development can take months or even years to launch. If you create a code-based solution, it’s also easy to blame others and there’s a lack of understanding if it’s not well-documented. “Low-code no-code functionalities can change this dynamic,” says Dr. Ingo Mierswa, an industry-veteran computer scientist and founder of Altair RapidMiner. “The visual workflow describes what it’s doing, so people can understand it, buy into it and take ownership of the results.”

    Visual workflows can be understood and created by more people. “They make it easier to maintain and explain why anything, such as a model’s decision or a bug, has happened because the workflows are documenting themselves,” Mierswa articulates. “It would be hard to create such an explanation if you had to sift through 100,000 lines of code, especially if the code had been changed 17 times in the past two weeks.”

    You need to iterate, you will make mistakes, and you don’t want to waste time with coding non-critical things. “My big advice for all starters is to always think about what’s critical for your product. What’s your IP? What do you need to own and customize? And if coding is not that important for your product, I think going low-code/no-code is always the better way,” Mierswa shares. “It’s more important for startups because you have less resources, less time, more competitive pressure and markets are moving very quickly.”

    Everyone is a Citizen Developer

    In the early 1960s and 1970s, there was a clear distinction between software developers and everyone else out of necessity. Software development was incredibly difficult and time-consuming to learn and master. But now with the onset of low-code/no-code solutions, everyone from custodial teams to C-level executives can create and customize applications that make their jobs more efficient.

    Because no-code/low-code platforms are built on the fundamental premise. “People closer to the problem are better equipped to find simpler and effective solutions,” says Kissflow CEO Suresh Sambandam. “It’s a team sport, and accountability, the most important benefit of LCNC solutions, accelerates development and empowers even more people to collaborate the right way.”A big advantage,” Sambandam says, “is that CIOs of large enterprises can solve the IT talent shortage plaguing the industry today by leveraging expert business users who are ‘citizen developers.’ Many companies can’t avoid struggling to recruit and retain tech talent in a highly competitive market, but low-code/no-code solutions exceedingly help bridge that talent gap by freeing up the bandwidth of existing resources.”

    At the highest level, you always need people who understand the business problems that need to be solved. LCNC functionalities also empower adjacent team members — designers, product managers, data scientists and others — to take part in the different stages of development as the product takes shape.

    Reducing Technical Debt to Overcome Friction

    In an enterprise scenario, most of the core systems like ERP, CRM, SCM in the front end, as well as in the back end, are bought from standard vendors. There is NO differentiation, as all the top enterprises buy from the same vendor. On the other hand, the bulk of differentiation comes from middle-office processes that are unique to an enterprise. Sambandam points out, “Often these are business processes that require heavy domain knowledge that frequently change to adapt to the evolving business conditions and hence business users are better equipped to build these workflow automations.” He highlights that conventional software development models don’t do justice to the agility required by business users and are too complex for them to use. While business users have the domain knowledge, the system would also require integration touch points with other enterprise systems. These integrations often require deeper technical expertise.

    It is essential to create a cultural change within your organization, where it is not just about having the right tools, but also about investing in your employees and skilling them up, commented DevRev Head of Engineering Ahmed Bashir.
    It still is hard work, and there will be friction. “Overcoming friction requires creating a tighter loop across departments and managers, closing the gap between developers and customers,” he underscores. “And LCNC platforms are designed to act as a system of action, surfacing real-time information that connects work with developers, customers and product.”

    This is exactly where platforms like Kissflow, Blaze and Bubble, which support both no-code and low-code use cases come in and let business users handle the domain portion of the application (90%) and IT teams configure the integration points (10%). This greatly reduces friction between IT and business users, especially when it comes to solutions for long-tail internal workflows.

    Long-tail applications include things like approval management, creative requests, incident management, customer onboarding and IT helpdesk. “We looked at the space and decided to tackle this,” Sambandam shares.

    Long-tail apps and processes are often viewed by IT as a drain on time/resources they don’t have, yet it’s a lack of internal workflow processes automation that gum up digital transformation. “We found as we scaled the company that when you empower business users to quickly build and augment workflows that directly impact their day-to-day by giving them the tools to do so without advanced technical knowledge, they are motivated to make it happen,” he affirmed.

    Security is a Business Enabler

    The main objective of security is to protect organizations and people. Organizations prepare for potential security threats by implementing policies and ensuring they have the tools to mitigate and quickly respond to outside threats.

    However many low-code/no-code adopters do not have security expertise on their team so they rely on the LCNC platform to offer security features readily available for the apps they build. Because creating applications with custom code can lead to a variety of security issues. And such applications are difficult to secure, with the majority of tested applications containing one or more session management vulnerabilities, and others with input validation errors.

    Getting a firm handle on security means considering what to do. That sounds simple enough, but it’s surprising how many startups make blunders because of poor planning and shoddy strategies. “We’ve been looking at a trend. Companies want enterprise-level security like audit logs, SSO and other data security requirements for their apps,” commented Nanxi Liu, Co-CEO of Blaze. “Seeing this strong trend, we worked to design our platform with enterprise security and scalability in mind, since most early-stage companies do not have security expertise on their team and rely on platforms to offer advanced security features for the applications they build.”

    Make, however, no mistake — there is no best security but the best practices. “That’s part of why,” Liu says, “compliance-driven businesses like financial services and healthcare companies that require the highest level of security to build their customer portals, consider enterprise-grade no-code and low-code platforms that provide the required level of security.”

    With low-code/no-code platforms, your applications are secure with industry-standard protocols, data protection practices, and features to block unauthorized access.

    To underscore: LCNC allows non-technical people to build complex apps without needing to be familiar with traditional software logic. You don’t need computational thinking because visual components in low-code/no-code platforms automatically have the logic built-in. “And now with the mind-bending AI breakthroughs,” Liu remarks, “users can tell AI in natural language the workflow or feature they need and see it instantly created.”