Tag: perforce

  • What Is DISA STIG?

    What Is DISA STIG?

    You need to ensure that your software is secure and safeguarded from security vulnerabilities. DISA STIGs help you ensure the security of your software. Read on to learn how.

    What You Need to Know About DISA STIG

    Defense Information Systems Agency (DISA) provides technical guides referred to as Security Technical Implementation Guides (STIGs). DISA is a part of the Department of Defense and it was created to provide guidance for the IT and technological aspects of organizing, delivering and managing defense-related information. The most prominent of these are the STIG guidelines which outline how an organization should handle and manage security software and systems.

    What’s Included in the Complete STIG Security List

    Each STIG provides you with technical guidance to secure information systems and software that might otherwise be vulnerable to security issues.

    The DoD regularly updates STIGs to ensure that you are able to complete the following three actions:

    1. Configure hardware and software properly.
    2. Implement security protocols.
    3. Organize training processes.

    By using a STIG, you are able to identify potential security vulnerabilities in your code. DISA STIG Compliance Levels While each STIG is unique, every DISA STIG has three compliance levels, which are referred to as “categories.” The categories indicate the severity of the risk of failing to address a particular security vulnerability and weakness. From the most to least severe, the categories are:

    Category I: Category I refers to any vulnerability that will directly and immediately result in loss of confidentiality, availability, or integrity. In addition, these vulnerabilities can enable cybercriminals unauthorized access to classified data or facilities, which can lead to DoS attack. Category I risks are the most severe as they can result in loss of life, damage to facilities or mission familiar.

    Category II: Category II vulnerabilities are any vulnerabilities that can result in the loss of confidentiality, availability or integrity.

    Category III: Category III vulnerabilities are any vulnerabilities that degrades measures to protect against the loss of confidentiality, availability, or integrity.

    To read more, please visit: https://www.perforce.com/blog/kw/what-is-DISA-STIG

  • Guide for Software Development & Software Security

    Guide for Software Development & Software Security

    In order to ensure an efficient, secure and successful software development project, there are many factors that you and your team must consider when starting a new project. The most common and pertinent considerations for many include defining the requirements of the project, selecting the correct processes for each stage of the software development project, selecting the right software development tools and ensuring the proper practices are implemented for software security.

    As meeting each of those considerations for an effective software development project can be a daunting and time-consuming challenge, we recommend you follow this step-by-step guide that will help walk you through how to organize a secure and successful project.

    Understand Your Software Development Project Requirements

    As you begin your software development project, there are several details that you must complete to help you better understand your software development project requirements.

    • Outline the project
    • Define the project vision
    • Identify compliance requirements
    • Select a flexible programming language
    • Develop a code design
    • Establish code architecture

    By completing the above tasks, you are able to create a reliable and secure framework for your software development project.

    How to Define Your Software Development Process

    As your development process will be unique to the needs and requirements of your software development project, we recommend that you consider including the following details into your process:

    • Identify what software security best practices will need to be enforced
    • Align on a development methodology
    • Organize your environment setup
    • Use repository tools
    • Enforce software security with secure coding practices
    • Incorporate checks into your development pipeline
    • Have a definition of “done” for your software development project tasks and features
    • Encourage feedback and communication

    Including the above details into your software development process helps to ensure software security as well as increase the success of your software development project.

    How to Choose the Right Software Security Tools for your Software Development Project

    One of the most important parts of your software development project is to choose the right tools. With the right tools, you are able to standardize your project and enable your entire team to work together more efficiently and effectively. Regardless of what the specifics of your software development may be, we recommend that your toolset includes:

    • Version control system
    • Static code analyzer
    • Application lifecycle management tool

    These tools help to ensure that your project is well-organized; your software reliable, compliant and high quality; and that software security is enforced.

    How to Set Up DevSecOps for Your Software Development Project

    DevSecOps is essential for efficient and secure software development, as it can help your team:

    To read more, please visit: https://www.perforce.com/blog/kw/software-development-and-software-security

  • 5 Ways to Improve Developer Output With Static Analysis

    5 Ways to Improve Developer Output With Static Analysis

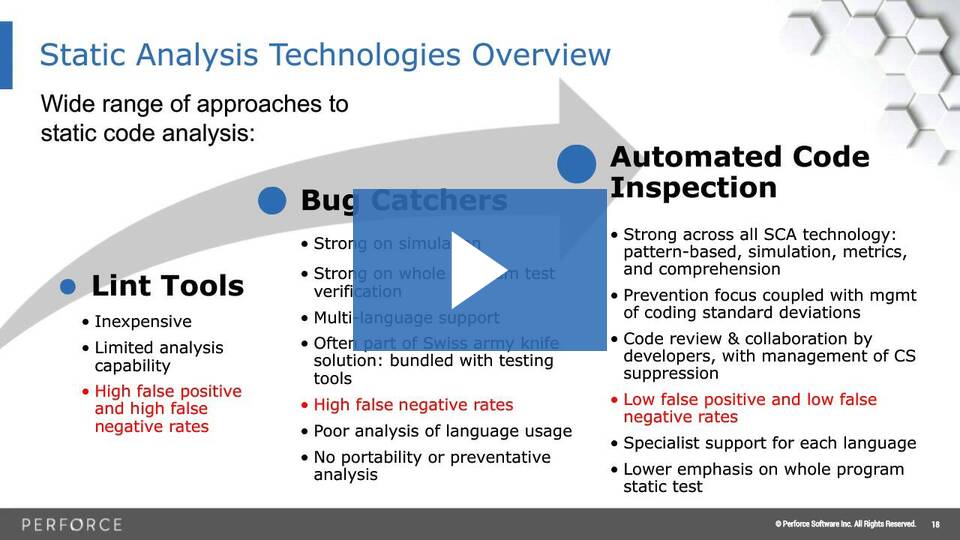
    Developers often have to produce efficient, effective code under tight deadlines. Without the proper software development tools to support this work, coding errors and vulnerabilities could occur. For that reason, it is important to use a static code analysis tool, which verifies the security, quality and compliance of your code as it is being written.

    In this webinar, we will outline three best practices for effective use of a static code analysis tool to improve your output, including:
    1. How to effectively achieve thorough coverage with a static code analysis tool.
    2. How to best use a static code analysis tool with mission-critical systems.
    3. How to achieve gains through effective, automated code analysis.


    To read more, please visit: https://www.perforce.com/webinars/kw/5-ways-improve-developer-output-static-analysis

  • How to Prevent Cybersecurity Threats With Secure Code

    How to Prevent Cybersecurity Threats With Secure Code

    Unfortunately, cybersecurity attacks are an ever-present threat for organizations of all sizes and industries. In fact, a cybersecurity threat is estimated to occur every 39 seconds. For that reason, it is important to understand the how, what and why of cybersecurity threats.

    The How, What and Why of Cybersecurity Threats

    Any malicious attack that threatens to damage software applications is considered to be a cybersecurity threat.

    In order to ensure that your software is safeguarded against any and all cybersecurity threats, you must take the appropriate steps, which includes:

    • Having an understanding of what the most common types of cybersecurity threats that you’ll most likely encounter.
    • Adopting effective secure coding practices.
    • Providing your team with software security training.
    • Using secure software tools — like static code analysis and SAST tools.

    By following these steps, you can more effectively safeguard your software.

    How to Prevent Cybersecurity Threats

    In order to prevent cybersecurity threats, you should use the following secure software development best practices:

    Establish Software Design Requirements

    You should establish software design requirements specifically to prevent and/or mitigate cybersecurity threats. By doing this, you can better address and eliminate potential threats.

    Enforce Secure Coding Standards for Cybersecurity Threats

    Software that is developed with secure coding standards—such as CERT and CWE—helps to prevent, detect and eliminate cybersecurity threats.

    Test Early for Cybersecurity Threats

    You should test your code early and often to identify potential vulnerabilities in your code that could lead to a cybersecurity attack.

    How SAST Tools Help to Prevent Cybersecurity Threats

    With the appropriate tools — such as static code analysis and SAST tools — you can better ensure the security and quality of your software. The reason for this is that both a static code analysis and SAST tool are able to automate vulnerability detection, test all of your code as it is being written, and easily integrates into your DevSecOps processes.

    To read more, please visit: https://www.perforce.com/blog/kw/best-practices-to-prevent-cybersecurity-threats

  • Continuous Integration Overview

    Continuous Integration Overview

    To improve the efficiency of your software development workflow, you should use continuous integration. We’ll explain what continuous integration is, why it’s important and how it can help you.

    Continuous Integration in DevOps

    Continuous integration is the automation of building and testing code each time a change is made in the codebase, and then committing the code back to your central code repository. For each new code commit that is made, an automated build and test process — which is also called a “pipeline”— is triggered. This trigger then generates a report on any defects found during code compilation and/or testing.

    The Benefits of Continuous Integration

    The benefits of using continuous integration include the following:

    • Easier to fix software vulnerabilities, errors and bugs.
    • Minimizing the amount of potential risk to your software development project.
    • Increasing the quality of your software.
    • Increasing the productivity of your team members.

    While the above list is not comprehensive, it does represent the most common benefits for software development teams.

    The Difference Between Continuous Integration and Continuous Delivery

    While both continuous integration and continuous delivery are software development processes, there is quite a bit of differences between them. To put it simply, continuous integration is used during the build and test phase, while continuous delivery is used once changes have been committed. Essentially, the aim of continuous delivery is to always have validated and verified code in your code repository, also known as a version control system.

    Why Continuous Integration Is Important

    Continuous integration is important because it enables you and your team to avoid common development pitfalls. In addition, a continuous integration pipeline ensures that every change is integrated, tested and verified.

    How Static Code Analysis Complements Continuous Integration

    One of the most effective practices you can adopt to improve your continuous integration development process is to use a static code analysis tool. The tool provides you with fast, reliable feedback on submitted code changes — enabling you to identify vulnerabilities and errors earlier in your development process. In addition, you are able to use quality gates with  static analysis tool to prevent those issues from entering your main code stream.

    To read more, please visit: https://www.perforce.com/blog/kw/what-is-continuous-integration

  • CI/CD Best Practices for Software Development

    CI/CD Best Practices for Software Development

    Continuous integration (CI) and continuous delivery (CD) are popular software development practices for automation and shortening feedback times. However, set up improperly, your CI/CD pipelines could instead cause delays in development. For that reason, review  CI/CD best practices to ensure that your pipelines are effective and efficient.

    What You Need to Know About Continuous Integration

    Continuous integration is the practice of automating the build and testing of code every time a change is made and committing that code back to a central repository. One of the fundamental cornerstones of continuous integration is that it encourages breaking up development tasks into small bite-sized pieces that can be performed frequently by every developer on the team.

    The Benefits of Continuous Integration

    There are four key benefits of continuous integration:

    • Easier Bug Fixes
    • Reduced Project Risk
    • Improved Software Quality
    • Higher Productivity

    What You Need to Know About Continuous Delivery

    Continuous delivery is a software development practice that enables continuous process and software improvement through automation. Without continuous delivery, you would have to manually develop, test, and deploy code—which can often take months. That is why continuous delivery is important as it can save you and your team a great deal of time.

    The Benefits of Continuous Delivery There are four key benefits of continuous delivery:

    1. Streamlining Workflows
    2. Lowering Staffing Costs
    3. Improving Operational Confidence
    4. Enhancing Teamwork

    Static Code Analysis Complements Continuous Integration and Continuous Deployment

    Static code analysis is a natural addition to any continuous integration development process. Done correctly, static code analysis adds the possibility for almost immediate feedback of new coding issues, specific to the branch or commit containing them.

    In addition, a static code analysis tool can provide your CI/CD pipeline with the following benefits:

    1. Detection of common security vulnerabilities, potential runtime errors, and other general coding errors.
    2. Compliance with safety-related coding standards, which includes MISRA and AUTOSAR.
    3. Enforce your coding guidelines or naming conventions along with your maintainability requirements.

    To read more, please visit: https://www.perforce.com/resources/kw/ci-cd-best-practices-software-development

  • What Is a CI/CD Pipeline? How to Improve CI/CD

    What Is a CI/CD Pipeline? How to Improve CI/CD

    The most effective way to ensure that your CI/CD pipeline is efficient is to use the right tool, like a static code analyzer. Here we explain what is a CI/CD pipeline and how a static analysis tool can help.

    What You Need to Know About CI/CD Pipelines

    The easiest way to understand a CI/CD pipeline is by understanding its individual components. Continuous integration (CI) is the practice of merging all of the working copies of code together into a shared mainline, while continuous delivery (CD) is the regular delivery of software functionalities.

    With a CI/CD pipeline, you can expect the following benefits:

    • Identifying software issues, errors, and bugs earlier in the software development process. This enables you and your team to fix these issues before they become too damaging and costly.
    • Reducing the amount of potential risk to your development process and your software.
    • Improving the quality and reliability of your software.

    Without having to run the program, a static analysis tool inspects your source code to identify defects, vulnerabilities, and compliance issues.

    This makes it invaluable to any CI/CD pipeline, as it helps with:

    • Detecting security vulnerabilities, runtime errors, and other software issues.
    • Enforcing compliance with safety-related coding standards as well as with company- or project-wide coding guidelines.

    How You Can Improve Your CI/CD Pipeline With a Static Analysis Tool

    With a static analysis tool, you are able to:

    • Ensure that your software is secure, reliable, and high quality.
    • Reduce the cost of identifying and fixing software defects and vulnerabilities earlier in your development process.
    • Enforce software coding standards to help you more easily prove compliance.
    • Improve the productivity, testing efforts, and pace of your software delivery efforts.
    • Report on the quality of your software over time and across multiple product versions.

    To read more, please visit: https://www.perforce.com/blog/kw/static-analysis-ci-cd-pipelines

  • What is CERT? Overview of CERT Secure Coding

    What is CERT? Overview of CERT Secure Coding

    As you write code, you must ensure it is secure and safeguarded from potential security threats. That’s why CERT is essential.

    Read on to learn more about CERT.

    What You Need to Know About CERT Secure Coding

    CERT is a secure coding standard that supports commonly used programming languages, like C, C++ and Java. The CERT Secure Coding standard was developed, and is maintained, by the Software Engineering Institute at Carnegie Mellon University.  The rules and recommendations outlined in CERT target insecure coding practices and undefined behaviors that lead to security risks. Each rule and recommendation is developed by members of the software development and software security communities.

    Why CERT Secure Coding Is Important

    CERT helps to ensure that software developed with coding languages — such as C, C++ and Java — is secure and reliable. The aim of secure coding standards like CERT is to not only detect security risks, but to provide guidance on improving the security and quality of that code. By using CERT, you ensure that your software is safeguarded from potential vulnerabilities.

    What Is a CERT Risk Assessment?

    For each CERT guideline, there is an associated risk assessment to help determine the potential security consequences of violating that specific rule or recommendation. There are three sections of the CERT risk assessment: severity, likelihood and remediation cost. Each risk assessment section is assigned a value between 1 and 3, based upon the results of the assessment. This helps determine the severity of the violation.

    Why You Should Use a SAST Tool to Complement CERT Secure Coding

    The most effective way to ensure your code is secure and safeguarded from security vulnerabilities is to use a static application security testing (SAST) tool. A SAST tool identifies and eliminates security vulnerabilities and software defects early in the software development process. This helps ensure that your software is secure, reliable and compliant.

    To read more, please visit: https://www.perforce.com/blog/kw/what-is-cert

  • How to Improve Code Quality, Efficiently, with Static Analysis

    How to Improve Code Quality, Efficiently, with Static Analysis

    As hard as they try, no programmer is perfect. Testing and manual code reviews cannot find every problem in their code, so software vulnerabilities and bugs persist.

    Unfortunately, the amount of software errors will only continue to grow as your systems get larger and more complex. Which begs the question: How can you find all of the critical problems present in your code while still releasing a quality product on time? Simple: Use a static code analysis tool.

    In this webinar, we will discuss the following topics:
    1. Why bug-free software is difficult to achieve.
    2. Why automated software tools are the most effective solution.
    3. How safe, secure and reliable software can be achieved at lower costs.
    4. How static code analysis and manual code reviews can work together.

    In addition, we will also provide examples of software vulnerabilities that are easily missed by manual code reviews.


    To read more, please visit: https://www.perforce.com/webinars/qac/how-improve-quality-static-code-analysis