Category: News

  • LogicMonitor Expands Reach and Scope of Observability Platform

    LogicMonitor Expands Reach and Scope of Observability Platform

    At its LM Elevate user conference, LogicMonitor today formally launched LM Envision, an observability platform that incorporates artificial intelligence (AI) to both discover and then remediate issues.

    LogicMonitor CEO Christina Kosmowski said LM Envision is the only observability platform available via a software-as-a-service (SaaS) model that can be applied to both on-premises and cloud applications. In total, there are already more than 2,000 integrations for the platform as part of the open LM Envision ecosystem, she noted.

    Over the last year, additional capabilities have been developed and added to the observability platform. These include application performance monitoring (APM) tools to identify bottlenecks and optimize performance, expanded support for public clouds and Kubernetes environments, integration with the StackStorm automation platform, integration with Terraform infrastructure-as-code tools and more advanced tools for searching logs.

    The company has also extended its AI operations tools to provide more context when troubleshooting issues by aggregating logs and including topology tools and graphs.

    Finally, LogicMonitor has added a push metrics application programming interface (API) to make it simpler to ingest data, pre-integrated dashboards and support for open source OpenTelemetry agent software.

    Kosmowski said it’s only a matter of time before observability and AIOps converge to the point where IT teams will finally be able to spend less time managing platforms. One of the major challenges IT teams face is that each platform they use requires its own framework to monitor and manage it. As observability and management frameworks converge, the overall overhead associated with managing modern IT environments should steadily decline as machine learning algorithms make it easier to surface issues before they create a major disruption, she noted.

    The overall goal is to close the loop between the discovery of an IT issue and its remediation, Kosmowski added.

    Observability, of course, is one of the core tenets of any set of DevOps best practices. Achieving it, however, has always been a challenge. The goal now is to eventually replace the hodgepodge of monitoring tools that track a limited set of pre-defined metrics with an observability platform that not only aggregates metrics but enables DevOps teams to launch queries and surface IT issues. In some instances, the rationalization of monitoring tools will help justify the acquisition of an observability platform. The paradox is that, as IT environments become more complex, it may actually become easier to manage those environments as more applications become instrumented and the various silos that isolate IT teams from one another start to collapse.

    In the meantime, there is no shortage of observability platform options. The primary difference between each of them is the degree of integration they provide and their ability to employ AIOps to automatically resolve issues, said Kosmowski. Each minute DevOps teams don’t spend on managing IT platforms is a minute that can be applied to spurring innovation, she added.

    One way or another, DevOps teams will soon have more access to information about their IT environments than ever. Less clear is how much of the data being collected by observability platforms will actually constitute actionable intelligence. But as observability continues to evolve, it’s now more a question of the degree to which that goal will be achieved versus if or when.

  • Catchpoint Enables Experimentation by Automating Web App Testing

    Catchpoint Enables Experimentation by Automating Web App Testing

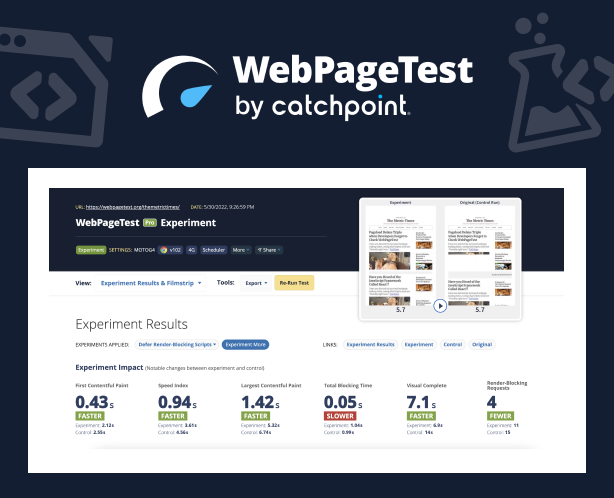
    Catchpoint this week expanded its open source WebPageTest performance testing suite of tools to enable IT teams to run instant tests that surface suggestions for improving overall web application and site performance.

    In addition, Catchpoint is now providing support for private tests, bulk tests and priority testing capabilities within the WebPageTest tool suite.

    Tim Kadlec, director of engineering for WebPageTest, said the goal is to make it easier for both developers and DevOps teams to experiment with how changes to applications and websites could improve performance using a capability that has now been added to the core suite.

    Identifying opportunities to improve performance typically requires tediously constructing manual tests over a period of weeks, noted Kadlec. Much of that effort is experimental in the sense that no one knows for sure if the tests being constructed will have a material impact on performance.

    The Opportunities and Experiments capability provides teams with a low-code tool for building tests based on a set of best practices that Catchpoint has defined. That approach makes it simpler to automatically generate and test tweaks that, for example, eliminate blocking scripts, optimize image rendering and minimize layout shifts. The result is optimization tests that show how their applications and websites could benefit from specific, actionable improvements without having to change any of the code that has already been deployed, said Kadlec.

    That’s a critical capability because it will encourage a level of experimentation that previously IT teams shied away from, simply because the amount of effort required to achieve an uncertain outcome was too high.

    It’s not precisely clear who is conducting these types of tests, as more responsibility for testing applications continues to shift left toward developers. The latest additions to WebPageTest make it easier for developers to conduct those tests without necessarily requiring help from a DevOps team, noted Kadlec.

    While there has always been a tremendous amount of focus on web application and site performance, the attention level has risen across organizations in the digital business transformation era. Many of the processes being implemented via web applications are extremely latency-sensitive. As more of those applications become routinely tested, the overall level of application performance should steadily improve.

    At the same time, the number of web applications and websites that most organizations are supporting also continues to expand. Most of those organizations are looking for ways to test applications without necessarily having to expand the size of the testing team or significantly increase the amount of time spent on testing.

    Regardless of the approach, it is apparent that testing is becoming more automated. The goal is not so much to eliminate the need for dedicated testing teams, but reduce the number of rote tasks that contribute to test avoidance in the interest of saving time. In theory, the more tests run—and the earlier they are run—the fewer issues that DevOps teams will need to deal with later.

  • 3xFAIL: IPv6 Fails | Fintech Fails | Firefox Fails

    3xFAIL: IPv6 Fails | Fintech Fails | Firefox Fails

    Welcome to The Long View—where we peruse the news of the week and strip it to the essentials. Let’s work out what really matters.

    This week: IPv6 gets stabbed in the back, Fintech firms’ valuations are falling, and the latest browser war seems to be over—Firefox lost. (more…)

  • Broadcom’s Software Strategy: Milk the Cash Cow, Exploit ‘Synergies’

    Broadcom’s Software Strategy: Milk the Cash Cow, Exploit ‘Synergies’

    The week began with rumors that Broadcom would acquire VMware and ended with the news that the deal is all but done. The VMware board, along with Michael Dell (who still owns about 41% of VMware’s stock), have a 40-day “go-shop” option; however, I don’t believe there will be other suitors.

    On Tuesday, I published an article about Broadcom’s desperation to gain cloud relevance and transform itself into a software company. I detailed the fact that VMware’s profitable business model and its nearly $4 billion of free cash flow makes it an attractive acquisition target. Finally, I said that Broadcom needed to find innovative DNA to make this acquisition work. 

    After thinking further about this proposed acquisition and talking to a number of VMware customers, as well as customers of CA Technology, which was acquired by Broadcom in July 2018, my outlook on the acquisition has become decidedly more cynical and likely more realistic.

    Milk Profits, Minimize Expenses

    We have seen this scenario play out before. Several former CA Technology customers and employees I spoke to was quick to say, “CA—where software goes to die.” That phrase has become so synonymous with CA that even the Wikipedia page for the company has a section on the phrase! Joking aside, most CA customers I spoke with over the last week agreed that since their acquisition, the company has “gone dark.” CA Technologies was a profitable company with important software that enterprise clients relied on and couldn’t easily transition away from. Sound familiar? VMware is in the exact same spot.

    Soon after the CA acquisition, Broadcom slashed about 40% of the CA workforce. On an analyst call to discuss the acquisition, Tom Krause, president, Broadcom Software Group (the Software Group will be renamed VMware) said that the company will increase VMware earnings from $4.7 billion to $8.5 billion within the next three years. How will the company nearly double earnings? “Synergies,” of course. The drivers of growth will be savings generated by eliminating duplicate functions in the combined company along with projections of more workloads running on the VMware platform.

    Do I expect Broadcom to change its corporate DNA to become an innovator? Will VMware innovators change Broadcom? Based on Broadcom’s past behavior, sadly, I think the answer is clear—No.

    I expect VMware to quickly cut costs across the board. Everything from headcount to R&D will see an immediate slash.

    This is Not Dell 2.0 For VMware

    You might argue that VMware has gone through this before when they were acquired by Dell and later set free by Dell Technologies in a 2021 spinoff. Why is this acquisition different? The Dell deal was, at its core, financial maneuvering to finance a deal and enrich investors with the goal of selling or taking the businesses public at a much higher market valuation. There was little cross-pollination between the Dell Technologies companies, and in this deal, Dell acted more like a private equity firm than an acquiring company.

    Broadcom is different. VMware is going to be milked as a cash cow as Broadcom tries to leverage VMware’s importance in the data center. VMware has huge cloud computing customers (AWS, for one) that are reliant on the company’s technology. If you are a VMware customer, get ready for higher prices as the company shifts to more of a subscription model. I also suspect that we will see large layoffs and the diminution of VMware as an entity. This is the end—VMware is not going to have another opportunity to go public on its own or go private in the future.

    I also don’t expect huge technology advancements from VMware over the next decade; but the company won’t die. The company will continue to exist because of the mere fact that enterprise software never dies.

    What Should Partners and Customers Do?

    This isn’t the end of technology acquisitions; nor is it a one-off event. Within the current market conditions, software vendor valuations have come crashing down to a more realistic level. I suspect that many large businesses with cash on hand will be looking to buy profitable software businesses that are viewed as essential. So, what should technology and business leaders do?

    • Understand vendor roadmaps and business. If you choose to go with an independent vendor, especially a smaller company, you need to understand their product roadmap along with their overall business strategy. 
    • Don’t become overly reliant on a single vendor. This isn’t the first time VMware has forced customers to rethink their relationship with the company. Years ago, VMware attempted to drastically increase licensing costs. Customers revolted and the company reversed course; however, it was a wake-up call and many businesses began to look at alternatives like OpenStack. You also need to ask technology leaders within your business what happens if a vendor changes their pricing, becomes a competitor or goes out of business. These “what if” scenarios are critical to reducing your risk.
    • Explore open source options. Open source isn’t a cure-all, but many businesses have adopted open source in part to reduce the risk of vendors changing strategies, increasing prices or no longer supporting your software. With open source technology, even if a project’s community is no longer active, a business that uses the technology can continue to contribute code and maintain the project.


  • Eclipse Foundation Opens Marketplace for OpenJDK Binaries

    Eclipse Foundation Opens Marketplace for OpenJDK Binaries

    The Eclipse Foundation this week opened an Adoptium Marketplace through which DevOps teams can access Java binaries based on the OpenJDK specification. OpenJDK was created based on the Java standard edition (SE) of the programming language and virtual machine.

    Mike Milinkovich, executive director of the Eclipse Foundation, said the goal is to make it easier for IT teams to access open source binaries via a vendor-neutral marketplace that complies with the Java SE Technology Compatibility Kit (TCK) that was created to make sure runtimes based on OpenJDK conform to the original Java specification.

    The marketplace has been set up in collaboration with the Adoptium Working Group that was set up by the Eclipse Foundation to govern OpenJDK, an open source implementation of the Java SE originally created at Sun Microsystems and later acquired by Oracle.

    Members of The Adoptium Working Group include Alibaba Cloud, Azul, Huawei, IBM, iJUG, Karakun AG, Microsoft, New Relic and Red Hat. That group created an Eclipse AQAvit project to test binaries for compliance with the Java SE TCK specification.

    OpenJDK is a reference implementation used by multiple vendors to create their own binaries, which are only guaranteed to be compatible with the standard until the next update arrives; updates are released approximately every six months. The Eclipse Adoptium project will make it simpler for developer teams to identify which binaries are compatible with specific implementations of OpenJDK. Ultimately, the goal is to encourage developers to build applications using frameworks that make use of new OpenJDK features as they are added to the platform versus continuing to rely on older binaries.

    Java remains the dominant language for developers working in enterprise IT organizations. Over the last few years, however, OpenJDK has gained traction as organizations adopted an open source implementation of the specification that enabled providers of application development frameworks to reduce licensing costs.

    It’s not clear at what rate enterprise IT organizations are replacing proprietary editions of Java with OpenJDK. However, during an economic downturn, more organizations tend to rely on open source software. Many organizations are also now looking to build microservices-based applications using Java frameworks based on OpenJDK runtimes.

    It’s obviously taken quite a bit of time for the OpenJDK community to put together a vendor-neutral marketplace. In the meantime, a wide range of other programming languages gained traction in the enterprise. There is still a lot of dependency on Java for building backend applications and services, but it’s more common than ever to see frontends that access those backend applications and services being built using, for example, a framework based on JavaScript.

    Java, of course, isn’t going away any time soon. The sheer number of enterprise developers that rely on it to build applications will ensure its continued longevity. The important thing to note, however, is that as more open source platforms are employed, the pace at which the overall community will innovate should continue to accelerate.

  • JFrog Aims to Push DevOps to the Edge

    JFrog Aims to Push DevOps to the Edge

    At its swampUP event, JFrog launched a JFrog Connect platform for updating, managing, monitoring and securing remote Linux and internet of things (IoT) devices.

    The JFrog Connect platform is based on a lightweight agent JFrog gained last year with the acquisition of Upswift and that has now been integrated with the JFrog Artifactory repository. DevOps teams can now use a low-code tool to build flow logic that is integrated with a Git repository in addition to triggering a rollback to ensure a device returns to its previous known software state when necessary.

    DevOps teams will also be able to connect to a wide range of Linux-based IoT devices from anywhere in the world and then manage and monitor them in real-time by name, description or tags.

    JFrog CTO Yoav Landman said in the near future, DevOps teams will find themselves building and deploying applications that will not only be deployed on fleets of endpoints at the network edge, but also will be continuously updated.

    Historically, those endpoints have been managed mainly by operations technology (OT) teams, but it will soon be up to DevOps teams to automate the management of those platforms down to an individual container using the lightweight agent created by Upswift, he said.

    The number of application workloads being deployed on edge computing platforms is rising sharply as organizations seek to process and analyze data closer to the point where it is being created and consumed. In fact, that shift is at the core of digital business transformation initiatives that depend on edge computing platforms and devices running, for example, IoT applications that process data in near-real-time.

    The challenge today is in many cases organizations lack the ability to consistently deploy software on edge computing platforms, which results in the creation of a hodgepodge of homegrown tools to manually deploy software on edge computing platforms. There is a clear need to raise the DevOps bar to address edge computing requirements, said Landman.

    It’s too early to say just how much software will be deployed on the edge, but there may come a day when there is more software at the edge than there is in the cloud. In the meantime, the line between edge computing and cloud computing continues to blur. Many more DevOps teams will soon find themselves managing thousands of distributed endpoints from a central cloud.

    In the meantime, DevOps teams should expect to find themselves working more closely with OT teams that generally have a significantly different culture. Many of those OT teams are just now coming to terms with the implications of connecting endpoints to the internet. The need to continuously update the software on those platforms is not typically the first issue that comes to mind for them. Today much of the software running on edge computing platforms is rarely updated. In the future, however, that software is likely to be updated at a rate that many OT teams are not ready to envision much less manage.

  • Go Language is Popular? | VMware Sells to Broadcom? | Unlimited PTO?

    Go Language is Popular? | VMware Sells to Broadcom? | Unlimited PTO?

    Welcome to The Long View—where we peruse the news of the week and strip it to the essentials. Let’s work out what really matters.

    This week: Golang goes from zero to hero, will Broadcom buy VMware? And limitless vacation is still a Thing. (more…)

  • JFrog Launches Blockchain Project to Secure Open Source Software

    JFrog Launches Blockchain Project to Secure Open Source Software

    At its swampUP event, JFrog today launched Project Pyrsia, an open source project that uses a blockchain platform and Sigstore Cosign and Notary V2 cryptographic signature software to secure software packages. In addition to JFrog, other contributors to the project include Docker, Inc., DeployHub, Futureway and Oracle.

    Stephen Chin, vice president of developer relations for JFrog, said Project Pyrsia will enable organizations to establish a chain of provenance for open source software components stored in a secure network of repositories.

    In effect, Project Pyrsia is making use of decentralized Web3 technologies to secure the open source supply chain, noted Chin. That approach to validating the integrity of software components using a blockchain platform will ensure that any software component being employed by developers has not been compromised, he added.

    Ultimately, the goal is to contribute Project Pyrsia to the Open Source Security Foundation (OpenSSF), an arm of the Linux Foundation that, as a consortium, is looking to coordinate efforts to better secure open source software. JFrog’s own research efforts identified more than 20 different open source software supply chain attacks, with two of those involving zero-day threats for which there was no immediate software patch available. Cybercriminals are targeting open source projects because any malware that gets included will later show up in any number of downstream applications. Their ultimate goal is to activate that malware at a time of their choosing.

    Securing open source software became a more urgent issue following the discovery last year of the zero-day Log4Shell vulnerability that impacted Java applications. Many developers routinely reuse open source software, but many of those projects are maintained by a small number of programmers that voluntarily contribute their time and effort to build components that others are free to use. Like any other developer, the amount of security expertise those individuals have is limited; the onus for making sure that software is secure falls on the organizations that decide to deploy it. The trouble is, many developers assume that software is more secure than it really is. Initiatives like Project Pyrsia are part of a larger effort to make it simpler for maintainers to secure open source software.

    It’s not clear whether security concerns are prompting organizations to review the amount of open source software they consume. Most organizations are more dependent on open source software than they realize, because most packaged applications will include open source components. Whenever a zero-day vulnerability is discovered, organizations can spend months looking for all the instances of an open source component that might be vulnerable.

    In theory, increased focus on open source software should lead to greater adoption of DevSecOps best practices that reduce the number of vulnerabilities in production environments. In the meantime, more scrutiny of open source software components is necessary, considering that they are employed by almost every organization.

  • Could Buying VMware Bring Broadcom Hybrid Cloud Bona Fides?

    Could Buying VMware Bring Broadcom Hybrid Cloud Bona Fides?

    Rumors are swirling that Broadcom wants to buy its way into the growing hybrid cloud market by acquiring VMware. The deal won’t come cheap—after news of the potential deal surfaced, VMware’s market cap soared to around $50 billion. Yes, billion with a ‘B’.

    As interest rates increase and investors reevaluate many of the lofty software company valuations, I expect to hear many more acquisition rumors. During this time of uncertainty, cash-flush vendors are going to be on the hunt for software vendors that can provide a technology platform, have large partner ecosystems and that also produce reliable revenue.

    Why the Acquisition Makes Sense for Broadcom

    Broadcom has a nice, solid business producing semiconductors for smartphone makers as well as storage and networking devices used in large data centers. However, like many hardware companies, the business has been desperately trying to break into the software industry. Why? There’s a semiconductor shortage and the company is in the right market at the right time. However, the company’s leadership knows that market conditions change. Software margins are significantly higher than hardware deals, and R&D and manufacturing costs for semiconductors are notoriously high.

    VMware has grown to become a large cloud technology platform, not just a virtualization offering. If Broadcom is able to successfully close on this deal, it will instantly own one of the largest cloud software platforms in the industry. In addition to acquiring large enterprise customers, the VMware partner ecosystem is important. For example, I believe that the NVIDIA partnership will be a profitable one for VMware. The two companies have been working together to create a platform to support AI-based applications for the data center, cloud and at the edge.

    In a time when some cloud businesses are experiencing wild fluctuations because of their lack of profitability, the VMware business model is solid. However, these fundamentals are also why the company is ripe for acquisition. In its fiscal year 2022, the company reported $12.85 billion in revenue and $6.33 billion in subscription and SaaS licensing revenue. Free cash flow for fiscal year 2022 was nearly $4 billion.

    Let’s quickly contrast VMware to the cloud data warehouse Snowflake (NYSE: SNOW). Snowflake’s market capitalization is around $40 billion and within the last year was well over $120 billion. Meanwhile, the company’s revenue is around $1.2 billion and it is struggling to find a path to profitability. If you were hunting to acquire a software business during a time when financial indicators are flashing red, which business model would you prefer?

    Broadcom’s Strategy: Become a Software Company

    I mentioned that Broadcom is desperate to gain relevance in the software industry. Why do I say this? The company’s recent acquisitions showed a clear pattern emerging—Broadcom has been trying to acquire its way into software.

    In 2018 the company acquired CA Technologies for nearly $19 billion. The following year, Broadcom acquired Symantec’s enterprise cybersecurity business for $10.7 billion. In addition, there were rumors that Broadcom was planning to acquire SAS Institute, the privately held analytics vendor, for somewhere around $15 billion to $20 billion. Those talks fell through when the SAS Institute’s aging co-founders and majority stakeholders announced a plan to go public in 2024.

    This M&A strategy might seem strange to many, but Broadcom originally tried growing through the acquisition of companies similar to itself. In 2018, the company made an offer of $117 billion to acquire chip producer Qualcomm. Broadcom later withdrew the bid when it became clear that the Trump administration pushed hard to prevent the deal, citing national security concerns.

    Although this latest deal would face governmental review and the Biden administration previously voiced concerns over tech mega-mergers and monopolies, we have not seen the administration prevent similar deals.

    The Path Won’t be Easy: Three Strategies for Success

    The market is full of cautionary tales of software vendors that were acquired only to be slowly destroyed. A successful acquisition would require Broadcom to tread lightly and maintain the elements that have made VMware the company that it is today. Below are three priorities that Broadcom should focus on if the deal is completed.

    Keep VMware independent: It is critical that VMware does not show favoritism toward one chip maker. VMware’s largest customers use chips from Intel as well as other manufacturers. If Broadcom tries to steer VMware toward its own chips exclusively, the backlash could quickly undercut the value of the acquisition. In addition, it’s my belief that the hybrid and multi-cloud models are here to stay (rather than a single cloud approach). Customers expect vendors to work with each other and are reluctant to accept single stack proprietary approaches. 

    Find innovative DNA and facilitate business unit collaboration opportunities: Hock Tan, Broadcom’s CEO, is very well respected in the industry; however, the company is not known for software innovation. Although I expect VMware to remain a standalone business unit (similar to CA’s current position within Broadcom’s ecosystem), it will be important to foster innovation. Broadcom should accelerate VMware investments, like Project Monterey and the NVIDIA partnership, while looking for new investment opportunities. Perhaps Broadcom could provide VMware with custom chips to help accelerate Project Monterey, but this sort of line-of-business collaborative innovation hasn’t been the model for Broadcom’s other software acquisitions. It should be.

    Nurture the partnership network: The next phase for the VMware partner ecosystem will require partners to understand the company’s vision for the future. What will the acquisition mean for partners? Will they have access to more solution selling that combines VMware and Broadcom technologies? How can existing Broadcom partners join the VMware partnership ecosystem? That will be another big question.

    It will be extremely interesting to see how this plays out. We’ll definitely be keeping an eye on this potential merger of two heavyweights!

  • Survey Surfaces Challenges Ahead on National DevOps Day

    Survey Surfaces Challenges Ahead on National DevOps Day

    A survey published today for National DevOps Day found nearly two-thirds (63%) have seen an increase in the frequency of service incidents that have affected their customers over the course of the last 14 months.

    The survey polled 1,046 engineering, IT operations, DevOps and site reliability engineering (SRE) professionals at organizations with more than 300 employees. The research was conducted by Transposit, a provider of a platform for connecting DevOps workflows, and found well over half (58%) of respondents reported the cost of downtime for their organization could be, on average, up to $499,999 per hour, with 40% of respondents noting that the cost of downtime has increased in the last year.

    Respondents said the top contributing factors to the increase in service incidents were digital transformation (61%), new product rollouts or product updates (55%) and methods and tools for collaboration that do not adequately support their team working remotely (49%). A full 90% of respondents reported there has been an increased focus on digital transformation during the last year with 73% having expanded the technology stack they support. More than half (55%) have increased the size of their DevOps teams.

    Overall, 46% of organizations reported they have experienced between six and 19 major incidents over the course of the last 12 months. More than half (53%) also reported an increase in the amount of time it takes to resolve incidents over the course of the last year, even though three-quarters of respondents (75%) said their organization increased their adoption of SRE practices in the last 12 months. Additionally, 65.1% of those organizations planned to hire site reliability engineers in the next 12 months. However, only just over a third of those respondents said their organization planned to expand their SRE efforts in 2022.

    A full 83% said up to 50% of their engineering operations processes are automated, but over half of the respondents that use SRE practices noted they still manually enter data into an IT service management (ITSM) application or other system-of-record to keep track of actions that were taken by humans during the resolution of an incident. Nearly two-thirds said their approach to automation was incremental, in which they begin by codifying processes and worked up to more advanced, fully automated scenarios.

    The top three tasks respondents would like to automate were service requests (53%), change requests (43%) and user provisioning (40%).The top barriers to implementing automation were cited as inadequate documentation of institutional knowledge and existing processes (56%), lack of clarity about what to automate (55%) and an inability to share knowledge (52%).

    Investments to improve their incident management processes over the next 12 months are focused on automation tools or applications (48%), communications/collaboration tools or applications (42%) and integration tools or applications (41%). Only a quarter (25%) said their tools are integrated through one tool or platform.

    Lack of unified communication with teammates (45%), processes that have changed or are harder to follow while working remotely (42%) and lack of visibility into dependencies and what teams or people are responsible for the code or infrastructure (38%) are all cited as reasons why serviced requests are now more complex.

    Transposit CEO Divanny Lamas said despite all the challenges facing DevOps teams, it’s fortunate that advances in low-code automation are making it simpler to more widely implement DevOps best practices. The challenge is finding a way to implement those best practices faster at a time when IT environments are becoming more complex.