Category: News

  • ServiceNow Adds Lightstep Notebooks to Visualize Observability Data

    ServiceNow Adds Lightstep Notebooks to Visualize Observability Data

    ServiceNow today added a visualization tool to its Lightstep observability platform that will make it simpler for DevOps teams to correlate metrics, logs and traces.

    Ben Sigelman, general manager for Lightstep at ServiceNow, said Lightstep Notebooks will make it easier for DevOps teams to make sense of the massive amounts of data collected by the observability platform.

    Lightstep Notebooks is an extension of the Change Intelligence analysis engine that ServiceNow already makes available within an observability platform it acquired in 2021.

    Included with Lightstep Notebooks are a set of ad hoc charts that include access to heat maps and time-series data with trace exemplars using the database at the core of the Lightstep observability platform.

    An instantly generated investigative path also makes it simpler to identify the root cause of any issue, and each instance of Lightstep Notebooks can be shared with other members of the IT organization via an embedded link. Finally, 100% of trace data can be retained for up to three days.

    Sigelman said the ability to share Notebooks via embedded links will also help bridge the divide between DevOps and IT service management (ITSM) teams that often need to collaborate to resolve an IT issue.

    Naturally, the level of collaboration between those teams tends to vary widely by organization. However, as DevOps best practices are more widely embraced, the number of organizations that are trying to achieve that goal continues to steadily increase. Earlier this year, ServiceNow added an incident response offering to orchestrate on-call escalation, group alerts and provide analytics in further pursuit of that goal.

    Observability platforms aggregate the collection of logs, metrics and traces in a way that makes it possible for DevOps teams to query that data. The goal is to make it easier for DevOps teams to both identify the root cause of an IT issue and pinpoint any anomalies that might disrupt an application environment. The goal is to eliminate the need to convene a “war room” meeting that requires IT teams to suffer through the painstaking process of elimination to identify the root cause of an issue.

    Of course, before an IT environment can be observed, it needs to be instrumented. Thanks to advances in the form of open source agent software being advanced via the OpenTelemetry project managed under the auspices of the Cloud Native Computing Foundation (CNCF), it’s becoming less costly to instrument IT environments. That’s especially critical at a time when more DevOps teams are deploying microservices-based applications that are more complex to manage than legacy monolithic applications. While generally more resilient, the dependencies that exist between the microservices that make up an application can be difficult to identify without the aid of an observability platform.

    As a core DevOps tenet, the need for observability and instrumentation has always been apparent. The challenge has been finding the best way to achieve that at an acceptable cost, Fortunately, there is now no shortage of observability platforms. The only remaining issue is to determine which one best fits within the construct of the organization’s defined DevOps workflow.

  • TechStrong Con: Open Source Software Community Needs Security Help

    TechStrong Con: Open Source Software Community Needs Security Help

    The only way to make significant improvements in the state of open source security is if more organizations that benefit from open source projects commit to making more resources available to achieve that goal.

    At the virtual TechStong Con event, executives on an Open Source and DevOps panel called for more contributions from enterprise IT organizations to ensure the integrity of open source software.

    Organizations of all sizes now benefit from open source software whether directly or indirectly. Those organizations have a responsibility to participate in the development of that software in any way they can, said Jeffrey Barnes, senior software engineer for Remote Operations, a provider of medical transcription services. “We need to give back to the community,” he said.

    Those efforts don’t necessarily have to involve contributing actual code, added Barnes. Many open source projects are in need of documentation and testing help because the number of actual maintainers of the project is relatively small, he noted.

    The challenge is that many enterprise IT organizations don’t understand how to participate in open source software development processes, noted Tom Sweet, CIO for Industrial Refrigeration Pros. An organization might download a piece of open source software and then extend it. Rather than continuing to maintain that branch on their own, organizations should contribute that code back to the project to reduce maintainers’ overall IT burden, Sweet said.

    “Many organizations are struggling to contribute back,” said Sweet. “It’s an evolution.”

    Organizations clearly need to make contributing code back to open source software projects a natural extension of their DevOps workflows. In the meantime, the Open Source Security Foundation (OpenSSF), an arm of the Linux Foundation, is focusing on 10 streams of investment that, in total, would require more than $150 million in funding to drive greater adoption of DevSecOps best practices among maintainers of open source software projects.

    The core issue is that many of those projects are maintained by a small number of programmers that voluntarily contribute their time and effort to build components that others are free to use. Like any other developer, the amount of security expertise those individuals have is limited. The onus for making sure the projects and software are secure is on the organizations that decide to deploy that software.

    Unfortunately, many IT vendors and large enterprise IT organizations reuse that code without contributing anything meaningful back to the project—whether that be in terms of financing or helping open source maintainers find and remediate vulnerabilities.

    It’s not clear to what degree business and IT leaders realize how dependent their organizations actually are on open source software. Many of them assume that open source projects are supported by IT vendors when, in reality, there are many projects that are dependent on the efforts of a small handful of developers volunteering their time and skills.

    Many organizations, of course, may soon decide not to employ open source software if it doesn’t have a critical mass of developers working on it. However, in an era where DevOps teams and developers routinely download software, enforcing those policies is going to be problematic. The best thing enterprise IT organizations can do is engage with the open source software community more rather than less.

  • Cloudflare Outage Outrage | Yet More FAA 5G Stupidity

    Cloudflare Outage Outrage | Yet More FAA 5G Stupidity

    Welcome to The Long View—where we peruse the news of the week and strip it to the essentials. Let’s work out what really matters.

    This week: Cloudflare suffers another huge outage while the FAA and FCC still disagree over 5G/NR near airports. (more…)

  • ShiftLeft Report Reveals State of Application Security

    ShiftLeft Report Reveals State of Application Security

    A report published today by automated application security testing platform ShiftLeft found only one in three applications has an attackable vulnerability. The report also found organizations that prioritized their remediation efforts based on the level of actual threat are fixing 76% of those vulnerabilities within two sprints lasting 12 days, on average.

    Based on millions of scans performed in the last year using the ShiftLeft platform to identify vulnerabilities, organizations have reduced the number of vulnerabilities they need to address by 97% on a year-over-year basis, the report found.

    In addition, the report noted that the average median scan time is only 90 seconds, which helped drive an overall 68% increase in daily scans year-over-year. Overall mean-time-to-remediate (MTTR) has dropped by 37%, the report also found.

    ShiftLeft CEO Manish Gupta said given the increased number of vulnerabilities, it’s more critical than ever for organizations to focus their remediation efforts on those that can be exploited within their IT environment. For example, the report found that only 4% of all Log4j instances discovered in the IT environments analyzed were vulnerable. Rather than spending weeks looking for every instance, Gupta said IT teams would be much better off focusing their efforts on the instances that might actually be exploited.

    The challenge is that not enough organizations have a way to score vulnerabilities based on the risk they represent to the business, Gupta added.

    While there is a lot more focus on adopting DevSecOps best practices in the wake of a series of high-profile breaches of software supply chains, the ShiftLeft report made it clear that presenting developers with a long list of potential vulnerabilities is counterproductive. The bulk of vulnerabilities that are being discovered are not actually attackable, noted Gupta.

    That doesn’t mean application security doesn’t need to improve, but it is clear that a lot of time and effort is being wasted, added Gupta.

    In theory, at least, as the cultural divide been application development teams and cybersecurity teams continues to narrow, the overall ability to prioritize remediation efforts should improve. The first step toward achieving that goal is making it easier to identify what percentage of the application attack surface is really vulnerable. Otherwise, developers presented with a long list of theoretical vulnerabilities will continue to prioritize developing new features and capabilities versus remediating vulnerabilities.

    One way or another, vulnerability remediation issues will soon come to a head. In the wake of an executive order from the Biden administration to improve overall application security within federal IT environments, many organizations will adopt similar policies and processes. Developers, naturally, will inevitably either push back or do an end-run around processes they deem too onerous. Rather than allowing a stalemate to occur, Gupta said savvy DevOps teams will invest more time in identifying the critical vulnerabilities that need to be addressed before cybercriminals exploit them.

    The issue, of course, is that cybercriminals are getting more adept at discovering and exploiting those very same vulnerabilities.

  • Survey Sees Alternative Cloud Service Providers Gaining Ground

    Survey Sees Alternative Cloud Service Providers Gaining Ground

    A survey of 458 development professionals, managers and senior leaders conducted by Techstrong Research, a sister entity of DevOps.com, found 43% are considering adding additional cloud service providers in the next 12 months. In total, nearly two-thirds said they are at least considering, evaluating or are ready to buy from a trusted alternative cloud vendor, with 20% reporting they have already contracted one.

    The survey, conducted on behalf of Linode, an arm of Akamai Technologies that provides cloud services, found a full 93% of survey respondents are already using either Amazon Web Services (AWS), Microsoft Azure or Google Cloud Compute Platform (GCP). Nearly two-thirds (65%) reported they already used more than one cloud service provider. More than a quarter (28%) said they are using alternative providers to augment services they consume from either AWS, Microsoft, Google, Oracle, IBM Rackspace or Alibaba. And 19% said they are using a hyperscaler and an alternative cloud service provider.

    The biggest drivers respondents cited for using alternative providers are reducing reliance on a single provider (55%), improved price/performance (38%) and recent cloud outages (31%).

    Respondents also said they are concerned that large providers might one day compete with them as they expand their reach into other industry segments (24%) or may engage in business practices that would create a moral conflict (19%). A quarter (25%) said they already viewed their cloud service provider as a competitor.

    Dan Kirsch, principal analyst for Techstrong Research, said as cloud computing continues to mature, it is becoming apparent that more organizations are considering their options when it comes to consuming commodity compute, storage and networking services. Many organizations simply don’t need to access complex cloud services, he noted. A total of 42% of respondents said a cloud service provider offering core infrastructure primatives could handle 90% of their typical workloads. In many cases, alternative cloud service providers are being used to augment rather than replace a hyperscale cloud service provider, noted Kirsch.

    Overall, nearly three-quarters of respondents (74%) said they expect their infrastructure will be cloud-based by the end of this year. Nearly three-quarters of respondents buy cloud services directly from an infrastructure provider, with the rest employing a managed services provider or some other type of third-party cloud services reseller.

    More than one-third of respondents also reported using a payment mechanism other than a contract or request for proposal (RFP), according to the study. Among customers of alternative cloud providers, more than two-thirds (67%) are using some other payment mechanism, with one-quarter using cryptocurrencies to pay. That option is becoming increasingly important because more organizations are looking for ways to reduce costs by employing alternative payments, said Kirsch.

    In other cases, IT professionals are looking for an end-run around cumbersome purchasing processes or simply opt to use alternative payment methods as a matter of personal preference, he added. Alternative providers, as a general rule, are more open to processing these types of payments, noted Kirsch.

    The shift to the cloud has clearly been accelerating since the start of the COVID-19 pandemic. But as the landscape continues to evolve, there are now more options than ever for IT organizations to consider as the cloud becomes the preferred platform on which to deploy applications.

  • Survey Shows Correlation Between Open Source, DevOps Skills Demand

    Survey Shows Correlation Between Open Source, DevOps Skills Demand

    A survey published this week by the Linux Foundation suggested enterprise IT organizations now prefer to hire IT professionals that have both open source software and DevOps experience.

    Conducted in collaboration with edX, a leading global online learning platform from 2U, Inc., the survey polled 1,672 open source professionals and 559 respondents with responsibility for hiring open source professionals. The results revealed there is also a high correlation between demand for that expertise and familiarity with DevOps.

    In terms of skills most sought, 69% of employers said they are looking for IT professionals that have cloud and container technology expertise followed by Linux (61%) and DevOps/GitOps/DevSecOps expertise (57%). Another 40% are looking for individuals with cybersecurity skills.

    More than three-quarters of the IT professionals (76%) surveyed currently work with Linux (76%), while 60% have worked with cloud/container technologies and 53% have DevOps/GitOps/DevSecOps experience. Well over three-quarters (79%) said it was either very important (44%) or extremely important (35%) to be familiar with DevOps.

    Clyde Seepersad, senior vice president and general manager for training and certifications at the Linux Foundation, said with all things being equal in terms of salary and benefits, more IT professionals preferred to work for organizations that are clearly viewed as open source software leaders. Organizations that want to recruit the best talent should make an effort to be seen as significant contributors to open source software projects to attract the best IT talent.

    Roughly half the respondents currently work for IT vendors, but the rest represented some type of end-user organization that typically consumes open source software. That distribution showed that demand for open source software expertise has now moved well beyond IT vendors that build commercial applications and IT platforms, he noted.

    Overall, the survey found 93% of employers struggling to find enough skilled talent, with nearly half of respondents (46%) planning to hire additional IT professionals with open source software expertise in the next six months. A full 86% said hiring IT professionals with open source software expertise was a priority. Well over two-thirds of employers (69%) said they are more likely to hire an open source professional with a certification. A total of 90% of employers said they will pay for employees to obtain certifications, with 58% reporting that open source IT professionals typically have higher salaries.

    A total of 81% of the open source software professionals surveyed also said they planned to add certifications this year. Nearly three-quarters of them (73%) also noted it would be easy for them to find a new job. About a third of those respondents either left or changed jobs in the last year, the survey revealed. Two-thirds of open source software professionals said a higher salary would deter them from leaving a job.

    More than three-quarters of IT professionals (77%) also noted they would benefit from additional cybersecurity training.

    However, only 43% of employers identified training as a means to close their current skills gaps. Another 41% said they hired consultants to fill these gaps. Only 16% of those respondents said they were willing to delay projects because of a skills gap.

    It’s clear that IT vendors and enterprise IT organizations are, in many ways, competing for the same talent. The challenge enterprise organizations face is making sure they have a high enough profile to be perceived as a place where IT professionals can make a meaningful open source software contribution.

  • TechStrong Con: Downturn Brings Additional Sense of DevOps Urgency

    TechStrong Con: Downturn Brings Additional Sense of DevOps Urgency

    Regardless of whether the overall economy is experiencing a correction or is on the cusp of a recession, organizations are going to prioritize some projects over others as resources become more constrained.

    During the “DevOps: Has the Bubble Burst?” panel made up of DevOps executives and investors from venture capital firms that kicked off the virtual TechStrong Con event today, panelists said organizations will need to continue to invest in DevOps automation and cybersecurity to ensure their long-term survival.

    However, the number of IT projects that organizations will be able to simultaneously invest in is likely to decline, said Chenxi Wang, general partner for Rain Capital. “We are starting to see a slowdown of projects, for sure,” she said.

    Fundamentally, organizations will need to decide not so much whether they will modernize legacy monolithic applications but rather at what rate. More than 70% of organizations’ codebases are still based on legacy monolithic architectures, noted Wang.

    No one knows for sure how long the current economic contraction might last, but, as in any downturn, organizations will seek to conserve cash, said JFrog CEO Shlomi Ben Haim. DevOps initiatives will continue to be prioritized because otherwise, organizations risk falling far enough behind that they may not be able to ever recover, he added. “DevOps is in a good place,” said Ben Haim.

    In fact, thus far many DevOps companies have yet to see a decline in demand because organizations are investing in automation to reduce their technical debt costs, noted Thomas Krane, managing director for Insight Partners. “It’s a matter of life or death,” he said.

    At the same time, Krane said organizations might want to take a hard look at the profitability of the vendors they are counting on to drive that innovation. Vendors that have been counting on venture capital funding to maintain operations may soon find that money much harder to come by as capital becomes scarce, he noted.

    The core issue will become how quickly returns on investment (ROI) are generated, added Incredibuild CEO Tami Mazel Shachar. “There is going to be a lot more focus on ROI,” she said.

    In the meantime, the debate over what constitutes DevOps continues. Some narrowly define DevOps as a set of development activities that revolve around continuous integration/continuous delivery (CI/CD) platforms. Others definitions of DevOps include everything from application testing to observability and application security. No matter how big the proverbial DevOps tent is defined to be, however, the number of organizations that are embracing DevOps—and now DevSecOps—workflows more deeply only continues to increase.

    The challenge is focusing those efforts on the projects that deliver the most value for the business in the face of executive uncertainty about the future. Of course, nothing quite focuses the mind like an impending crisis; for better or worse, it will require more organizations to honestly assess their current capabilities.

  • Open Source Coder Tool Helps Devs Build Cloud Spaces

    Open Source Coder Tool Helps Devs Build Cloud Spaces

    Coder today launched an open source project that gives developers and data scientists a way to create cloud workspaces in a matter of minutes to make it easier to build applications and models faster.

    Currently, Coder provides a cloud application development platform that enables developers to build applications using any editor or integrated development environment (IDE) as an alternative to their local desktop. That capability is made possible by using the open source Terraform infrastructure provisioning tool to spin up a developer workspace. That approach provides developers with access to cloud resources that scale up and down as required versus, for example, being limited to the memory and storage resources that they can access on a laptop or desktop system.

    Ketan Gangatirkar, vice president of engineering for Coder, said that while individual cloud service providers offer ways of achieving that goal, those offerings lock organizations into a specific cloud service. The Coder approach allows developers to use their preferred tool across multiple cloud services, he added.

    Most developers are already building applications that run on multiple cloud platforms. As such, they require access to a set of tools that eliminate the overhead created when developers need to deploy and master a diverse range of tools to build those applications, said Gangatirkar.

    In contrast, with the Coder tool, developers can open a web browser, choose a workspace template and then start coding, he noted. That capability eliminates all the manual, error-prone processes typically required to get a developer workspace set up, said Gangatirkar.

    That approach also provides organizations with a more secure means of building applications compared to the time and effort that would otherwise be required to secure every local system used by a development team, he added.

    In general, there’s a lot more focus on developer productivity as organizations increase the number of applications they are simultaneously building and deploying. Hiring and retaining developers remains a major challenge as competition for talent intensifies in the race to accelerate digital transformation efforts. All things considered, many developers will prefer to work for organizations that allow them to use the tools they already know and prefer. That approach also makes it easier to onboard developers to a development project, noted Gangatirkar.

    It’s not clear how many application development initiatives are never begun simply because it takes too much time and effort to spin up a development environment whenever inspiration strikes. However, it’s clear that developers are wasting a lot of time maintaining multiple local development environments. Much of that time could be better spent writing actual application code.

    One way or another, open source tools—such as the one provided by Coder—should remove a lot of the friction that exists in application development today. The only issue that remains is whether those tools will be adopted by developers themselves versus the DevOps teams dedicated to serving them.

  • Codenotary Adds SLSA Framework Support to Advance App Security

    Codenotary Adds SLSA Framework Support to Advance App Security

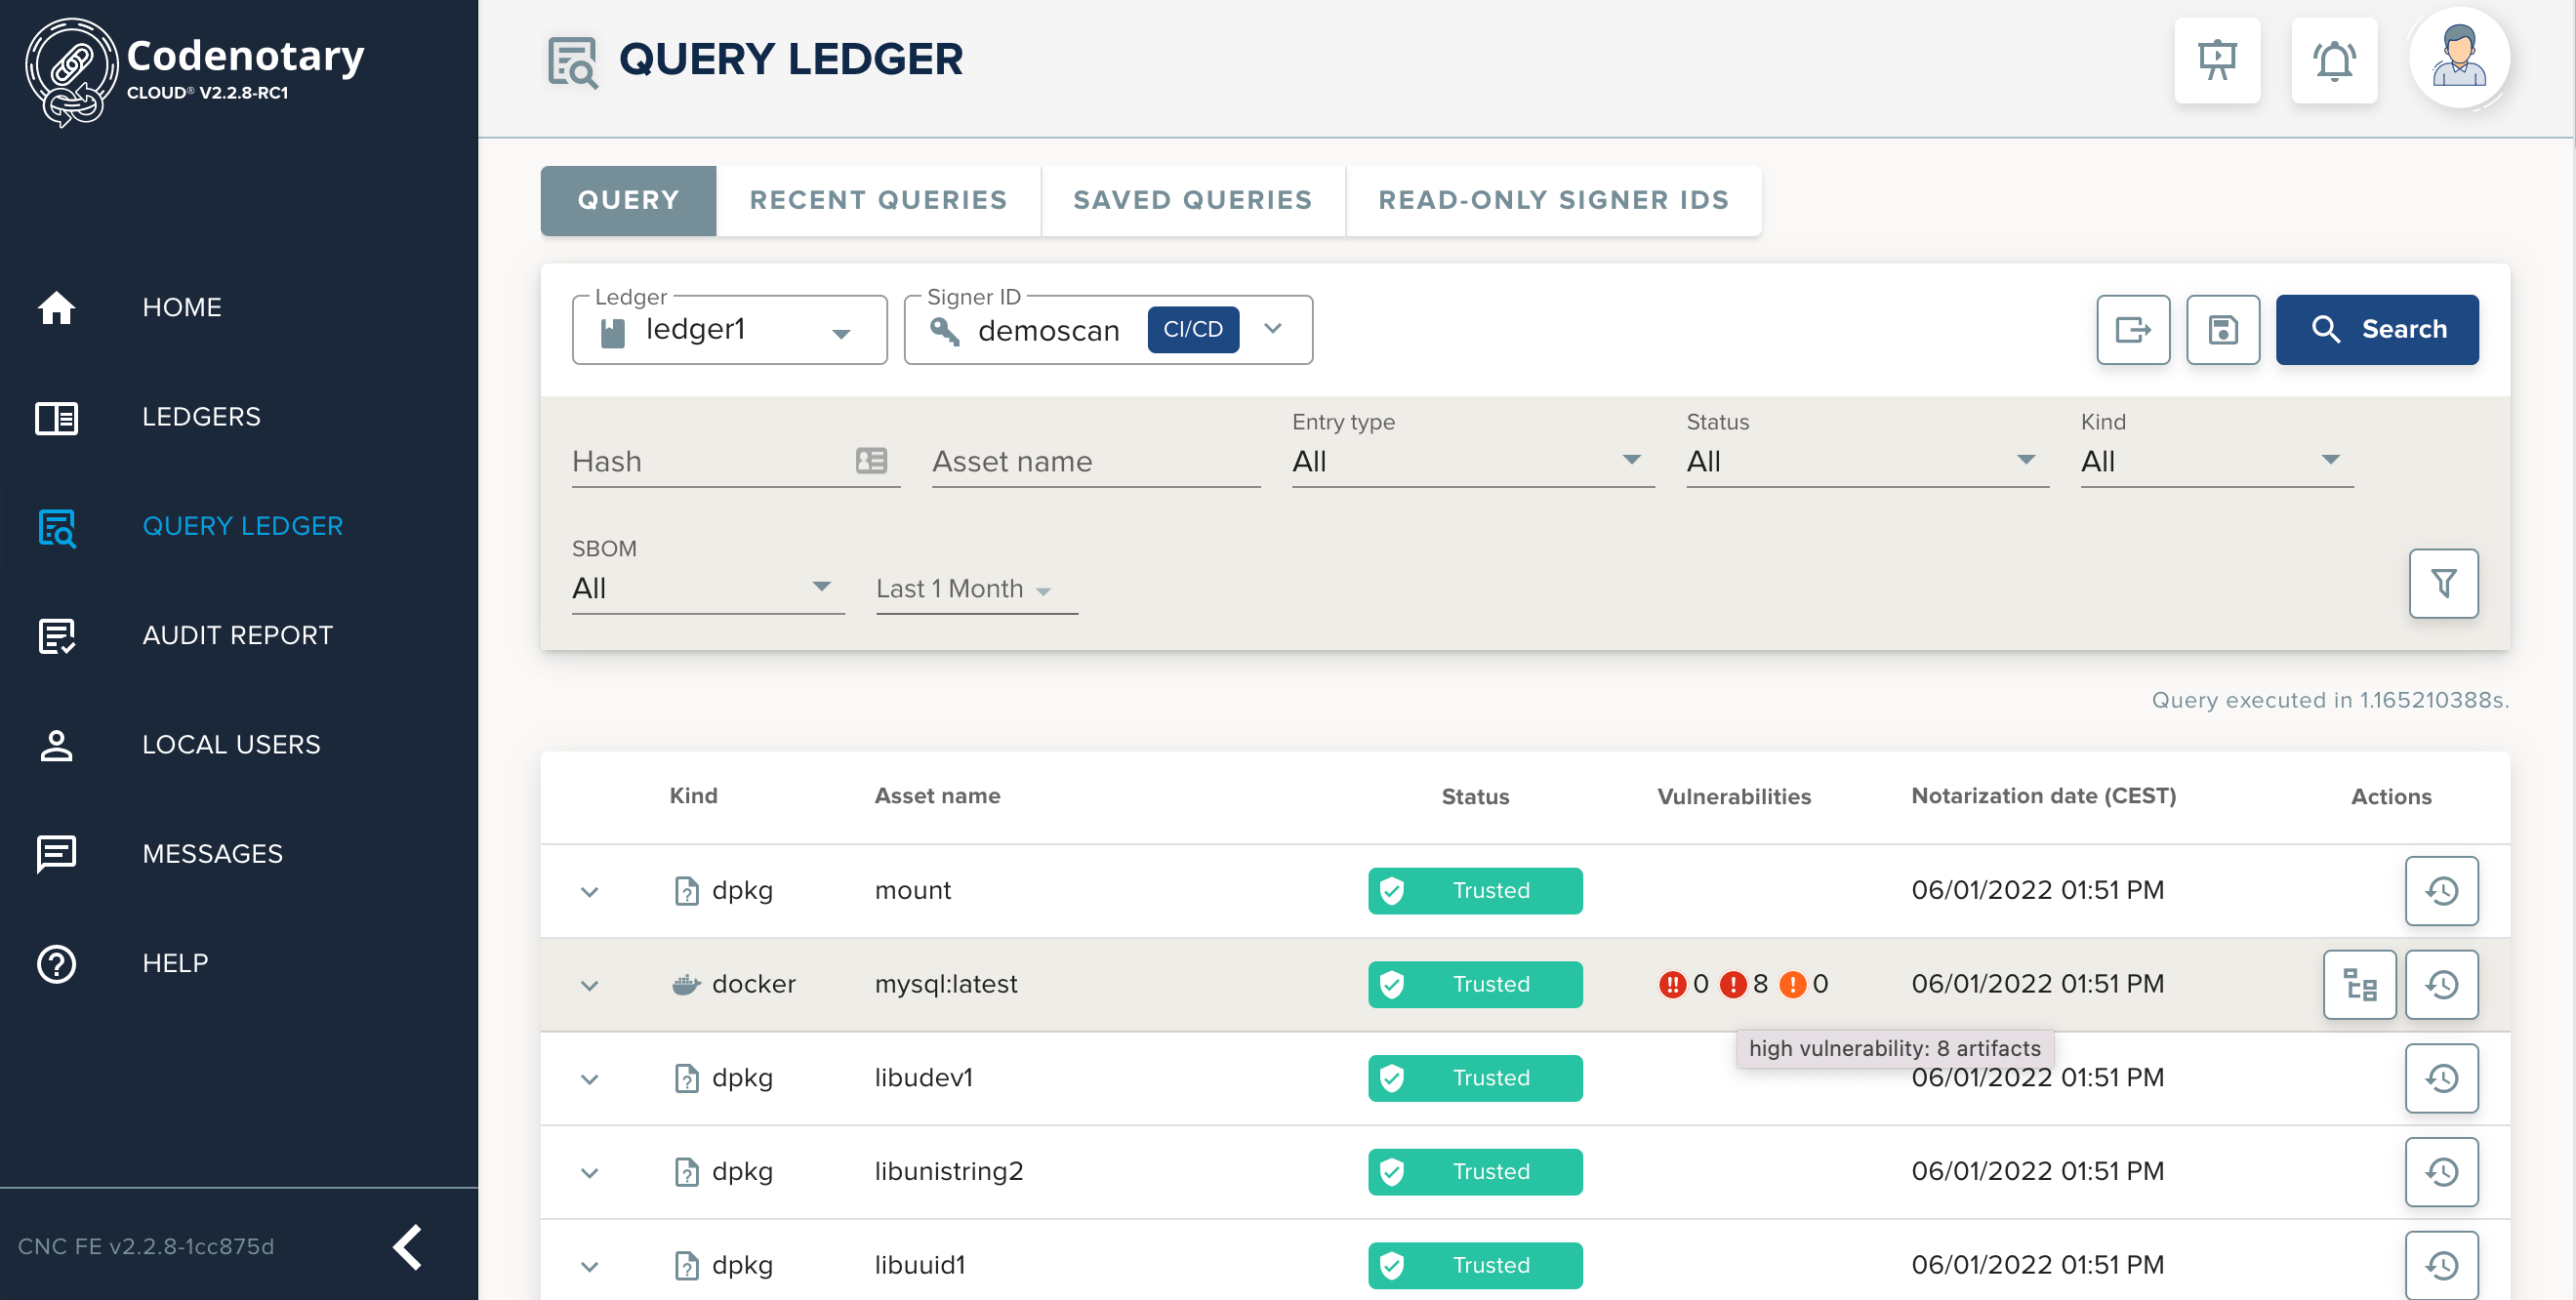
    Codenotary this week announced it has integrated support for the Supply-Chain Levels for Software Artifacts (SLSA) framework in its free notarization and verification service for ensuring the integrity of code.

    Moshe Bar, Code Notary CEO, said as the first application security platform to attain SLSA compliance, the company is making it easier for organizations to secure their software supply chains.

    SLSA is a framework defined by Google that it uses to attach binary authorization to code. In its current form, SLSA is a set of guidelines that identify how to attain four different levels of application security. The long-term goal is to create a framework that will automatically generate auditable metadata that can be fed into policy engines to create a SLSA certification.

    Codenotary provides tools for cataloging and verifying the authenticity of components used with a software development life cycle. At the core of that platform is an immutable open source immudb database that cryptographically attaches an identity to each software artifact. That capability can also be used to dynamically generate a software bill of materials (SBOM).

    The Codenotary Attestation Service can also be integrated with the continuous integration/continuous delivery (CI/CD) platform that DevOps teams use to build and deploy applications using those artifacts. Ideally, DevOps teams should construct a security pipeline that runs alongside their existing DevOps pipelines, noted Bar.

    In the wake of recent high-profile software supply chain breaches, the level of scrutiny being applied to how software is constructed has increased significantly. In theory, at least, developers have assumed more responsibility for application security as part of an overall shift left that provided them with more programmatic control over IT environments. Cybercriminals, however, are now becoming more adept at compromising developers’ credentials and insert malware as an app is developed.

    DevSecOps best practices are, of course, being adopted to teach developers how to better secure their application environments. The issue is that not enough developers are learning how to secure applications fast enough. The volume of attacks against the software supply chain continues to grow at a rate that is now much faster than organizations can thwart simply by educating developers.

    There is a now clear need to embed more cybersecurity guardrails within DevOps workflows, noted Bar. Rather than attempting to achieve that goal in a piecemeal fashion, Bar said Codenotary is making a case for an integrated platform that can be invoked as a natural extension of a DevOps workflow.

    In general, Bar said there’s now a greater sense of urgency when it comes to software supply chain security. Many of the reviews of those processes are, arguably, long overdue. One way or another, there will be a lot more questions asked about how software is actually developed. The organizations that consume this software are starting to appreciate how vulnerable they are as the overall dependency on software continues to increase. The only real question now, unfortunately, is how many more breaches there might be before those software security issues are thoroughly addressed.

  • Armory Aims to Turn Continuous Delivery Into a Service

    Armory Aims to Turn Continuous Delivery Into a Service

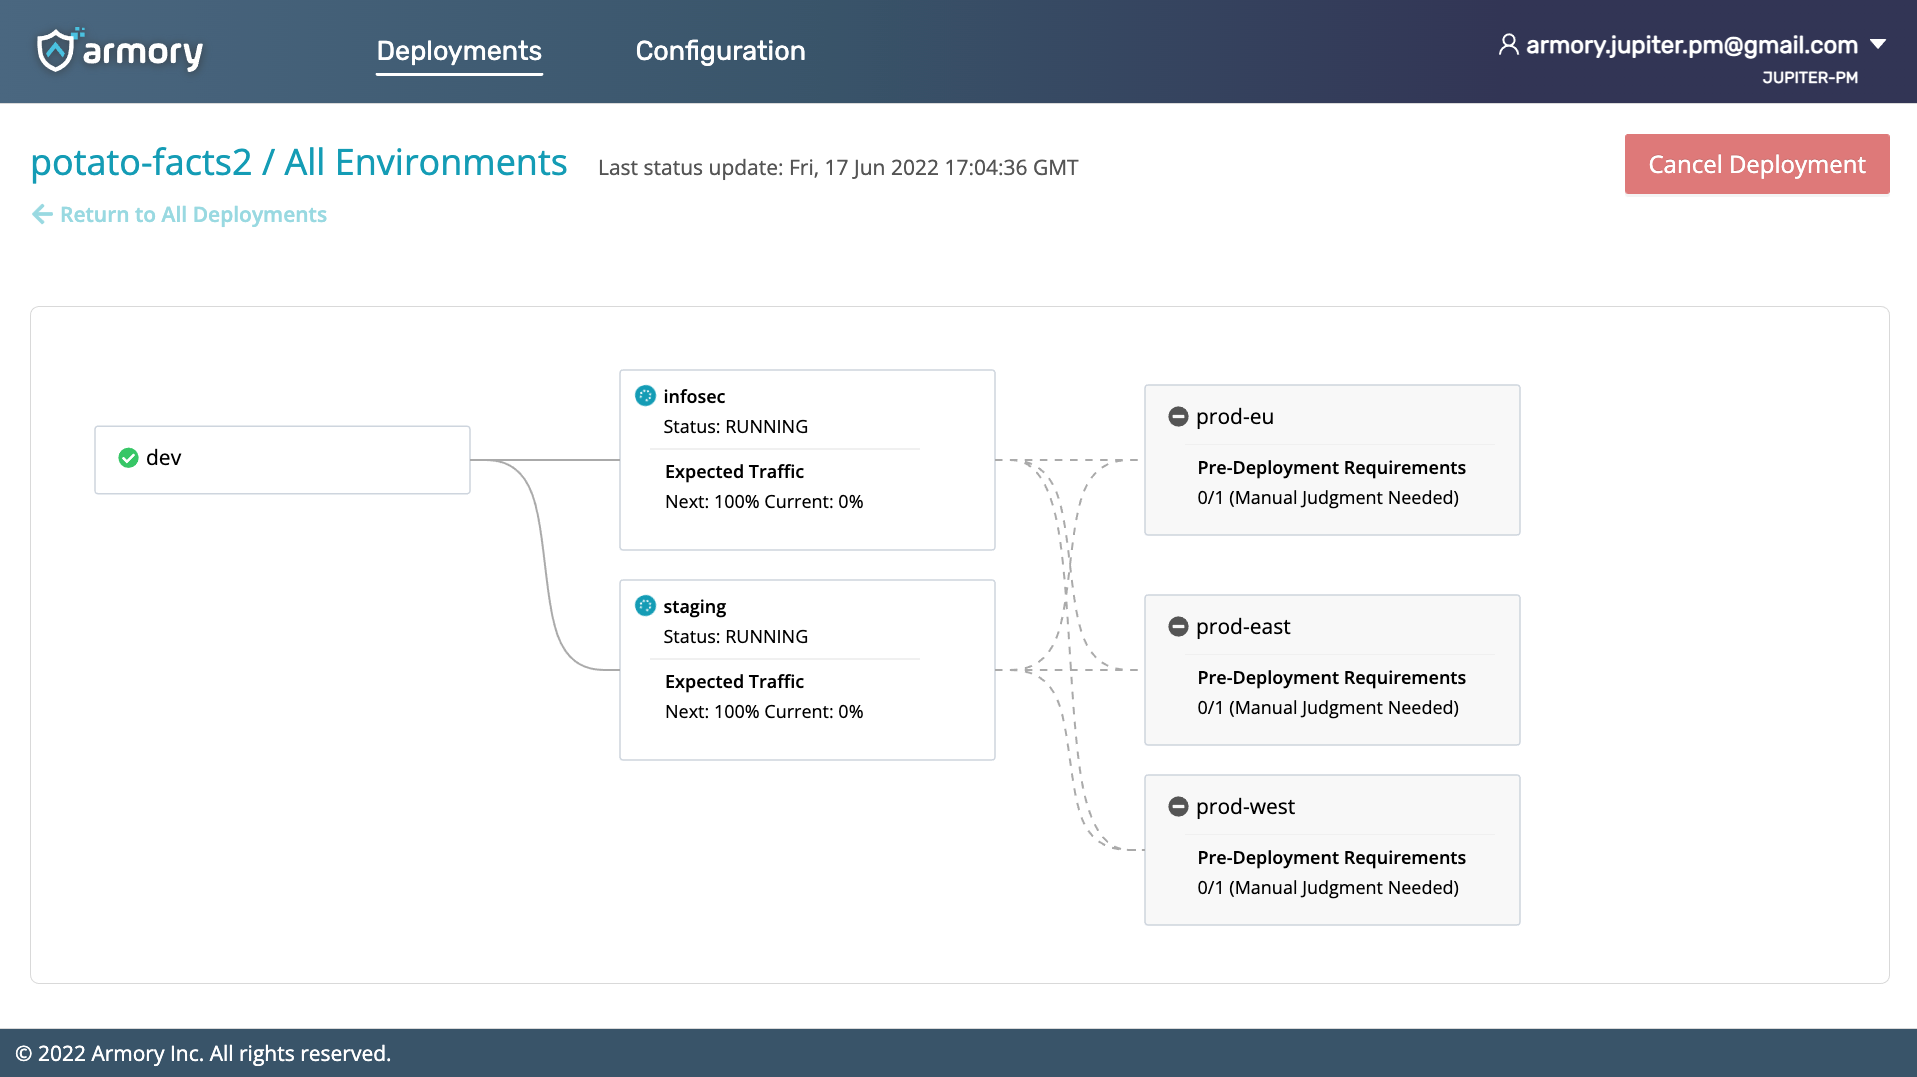
    Armory this week made generally available a continuous delivery-as-a-service (CDaaS) offering that promises to make it simpler for a much wider range of organizations to programmatically deploy applications.

    The Armory Continuous Deployment-as-a-Service platform has been available in beta since March. It differs from Armory’s existing open source Spinnaker continuous delivery (CD) platform in that it is based on a proprietary declarative platform that is designed to integrate with third-party continuous integration platforms.

    Armory CEO Jim Douglas said the goal is to meet organizations that have invested in CI where they are versus requiring them to rip and replace their entire DevOps platform. The company is still committed to providing a curated instance of Spinnaker, but it’s become apparent there are many organizations that want to experience the benefits of a more opinionated CD platform that is more accessible via a cloud service, he added.

    The Armory Continuous Deployment-as-a-Service offering applies many of the best practices that have emerged for the Spinnaker CD platform without requiring organizations to have a dedicated team in place to just manage the CD platform, noted Douglas. IT teams can start using the service to deploy applications in less than 30 minutes, he noted.

    The first edition of Armory Continuous Deployment-as-a-Service is optimized for deploying microservices-based applications on Kubernetes clusters, but Armory will soon extend the reach of the service to platforms running monolithic applications, said Douglas. The company also plans to make available an on-premises edition, he added.

    In either scenario, IT teams will be able to engage in everything from canary testing of deployments to automatic rollbacks in the event an application fails, said Douglas.

    The number of organizations that routinely make use of a CD platform is still relatively small. Historically, each platform used to run applications has been unique, so automating delivery has been problematic. CI platforms, in some cases, have been extended using custom scripts to automate application delivery, but those efforts don’t typically scale across an extended enterprise.

    Douglas said that as more IT teams start to build and deploy microservices-based applications, it’s only a matter of time before CD becomes a more distinct IT discipline. The challenge is enabling IT organizations to achieve that goal without necessarily having to hire a small army of site reliability engineers (SREs). There will still be plenty of DevOps teams that will prefer to deploy Spinnaker, but Douglas said there will also be plenty of instances where a less complex approach to CD will suffice.

    It’s hard to say whether there might soon be varying levels of DevOps platform services that organizations might invoke depending on the complexity of the project and their own internal cultural preferences. However, as the pace of application development continues to accelerate, the need to automate CD will become a more pressing issue. There may be many ways to achieve that goal, but if history is any indication, the path of least resistance is likely to be via the cloud.