Category: Features

  • Zero-Trust Network Access Platforms Slash DevOps Bottlenecks

    Zero-Trust Network Access Platforms Slash DevOps Bottlenecks

    In a prior article, I indicated why a new remote zero-trust platform is needed to support DevOps teams.

    Traditional remote access configurations are not well-suited for DevOps given a shifting user population comprised of employees, contractors and other third parties often using their own devices; the large number of tools and systems to which access must be provided and the hybrid nature of the infrastructure itself (on-premises, hybrid and multi-cloud).

    DevOps Pain Points

    Three pain points are associated with traditional approaches when used with DevOps.

    1. DevOps user experience is poor in traditional remote access configurations. Each DevOps service must be accessed as separate secured sessions, which is confusing and tedious.
    2. System management requires IP whitelisting rules in VPN, static SSH keys in Bastion, firewall rules controlled by different teams and application-specific authentication. The coordination and execution of so many touchpoints for common actions—including the onboarding of new team members, changing roles or adding a new service—invites mistakes that cause productivity issues and introduces unforeseen security holes.
    3. Security is complex and error-prone. DevOps users must be granted restricted access to the individual services they need to be productive. Administering restricted access for individuals and groups is time-consuming. Security policies typically require monitoring detailed audit logs of user access.

    How a Zero-Trust Remote Access Platform Works with DevOps

    In my whitepaper, Zero-Trust-Remote Access-For-DevOps, I explain how a zero-trust remote access platform can resolve the requirements for improved DevOps user experience, consistent and manageable administration and simplified, less error-prone security.

    Improved DevOps User Experience

    By replacing the need for the user to tediously set up separate sessions for each DevOps service they need to use, a client-side DevOps service catalog enables all DevOps services to be accessed with a single click. This service catalog approach is more convenient for DevOps users and provides a form of DevOps governance. It does this by encouraging DevOps teams to select choices that are available in the catalog instead of creating new choices that result in expensive DevOps tool sprawl.

    Simplified DevOps Management

    Management of remote DevOps users is simplified by consolidating access for all DevOps users and services under a single unified service manager and connector. The need to manage each user and service with different teams, each with their own processes, is unified and streamlined when the management requirements for DevOps users and services are consolidated under a common zero-trust remote access platform.

    In addition, this approach makes it much easier to implement more adaptive policies across the breadth of users and services.

    With a zero-trust remote access platform, onboarding new DevOps users and groups is accomplished within a single session—not separate sessions for each onboarding requirement.

    Simplified and Less Error-Prone Security

    Consolidating access to DevOps services under a common zero-trust remote access platform with unified services and services connectors enables simplified and less error-prone security controls, improved security monitoring and policy management. Audit logs of access are reported consistently for all services. Monitoring and changing access rules can be supported for individuals or groups when adjusting a policy. Trust-based access controls can be implemented consistently. Granular policies ensure access is predicated on appropriate device trust score thresholds being met. Rather than a single check prior to granting access, these production services policies continuously assess the security of the users and devices accessing the services.

    Transforming to a Zero-Trust Remote Access platform for DevOps

    Transformations of all types, and especially those for DevOps, are made more certain by following a
    seven-step transformation process, described in my book Engineering DevOps. This process serves as a framework for implementing the zero-trust remote access platform.

    The first two steps, vision and team alignment, involve getting the leaders, key influencers and implementers of an organization to recognize and establish actionable goals for the implementation of the zero-trust remote access platform.

    The third step, assessment, requires taking inventory of the current state of DevOps users, DevOps services and policies that need to be supported by the new platform.

    The fourth step, road map, requires determining the plan for implementation. Typically, it makes sense to start with one application. Start with a set of DevOps users and DevOps services needed for a single application or pipeline which can serve as a model to drive adoption to other applications as the solution is proved and accepted.

    The fifth step, realize, is the step in which the zero-trust remote access platform is installed and set up for the initial model application or pipeline. Banyan Security explains how an example tool vendor helps to simplify this step.

    Capabilities to look in for in zero-trust remote access tools include:

    • Deploys in minutes, with no integration requirements on any existing DevOps services or infrastructure.
    • No need to set up VPNs, open inbound firewall ports or manage DNS.
    • Use existing DevOps user devices without diminishing security.
    • DevOps service catalog provides users visibility and one-click access to DevOps services.
    • Support for bundled services, favorites, and autorun capabilities.

    In step six, operationalize, the procedures for commissioning and using the zero-trust remote access platform are proven, benefits are measured and playbooks are hardened for the organization.

    In step seven, expansion, the zero-trust remote access platform deployment is expanded to other DevOps applications pipelines, DevOps users and DevOps services across the enterprise.

    What This Means

    Traditional remote access configurations are not well suited for DevOps administrators or users given the dynamic nature of services, team members, and environments. A zero-trust remote access platform addresses the need for an improved DevOps admin and user experience, simplified access management to DevOps services and simpler, less error-prone security practices and monitoring.


    I want to express my appreciation for the time spent with the Banyan Security team, who has pioneered many of the concepts outlined in this blog and contributed valuable insight.

  • Google DORA Report Shows Modest DevOps Gains

    Google DORA Report Shows Modest DevOps Gains

    Google today published the annual Accelerate State of DevOps Report created by its DevOps Research and Assessment (DORA) team that finds 26% of DevOps teams surveyed can now be classified as elite performers. That compares to 20% the last time the study was conducted in 2019.

    DevOps teams, made up of a total of 32,000 IT professionals from around the globe, were evaluated based on their ability to frequently deploy, code, lead time for changes, time to restore service, change failure rates and operational performance. An elite team is expected to be able to restore service in the event of an outage in less than an hour.

    Dr. Dustin Smith, a user experience researcher for Google, said the increased rate suggests steady gains in DevOps maturity continue to be made despite all the challenges the COVID-19 pandemic presented. A full 96% of respondents said that prior to the pandemic they had not worked from home on a regular basis.

    The DORA report finds high and elite performers make up two-thirds of respondents. Elite performers were able to collectively decrease their lead time for changes when compared to previous studies. It’s also worth noting only elite performers have minimized their change failure rate. In previous years, medium and high performers were able to do the same.

    Overall, more than half of respondents (52%) report they have adopted site reliability engineering (SRE) best practices to some degree.

    Elite performers deploy code 973 times more frequently than low performers, who reported deploying less than once every six months. The normalized annual deployment numbers range from 1,460 deploys per year for the highest performers to 1.5 deploys per year for low performers. Not surprisingly, for elite performers, the lead times from commit to deploy are 6,570 times faster than low performers.

    Security practices have also improved with 60% conducting security reviews, with 58% reporting that the reviews include testing. Nearly two-thirds (63%) said they work closely with information security teams. The report finds teams with high-quality documentation were 3.8 times more likely to integrate security throughout their development process.

    Reliance on cloud platforms has also increased, with 56% of respondents indicating they employ a public cloud, a 5% increase from 2019. Only 21% of respondents reported deploying to multiple public clouds. Over a quarter (26%) of respondents did so to leverage the unique benefits of each cloud provider, followed closely by 22% that cited availability.

    Just over a third (34%) report they are using a hybrid cloud, while 29% have a private cloud. A total of 21% still don’t use a public cloud.

    The report also finds elite performers were 3.5 times more likely to have met all essential cloud characteristics defined by the National Institute for Standards and Technology (NIST). Those characteristics are defined as on-demand self-service, broad network access, resource pooling, rapid elasticity or expansion and measured service. Only 32% of respondents who said they were using cloud infrastructure agreed or strongly agreed that they met all five of the essential characteristics of cloud computing defined by NIST, an increase of 3% from 2019. Overall, usage of those characteristics of cloud computing have increased by 14% to 19%, with rapid elasticity showing the largest gain.

    The DORA report makes it clear there is still a long way to go before DevOps nirvana is more widely achieved. On the plus side, however, the number of organizations that have embraced DevOps to some degree continues to steadily increase.

  • OpsRamp Extends AI Reach to Incident Management

    OpsRamp Extends AI Reach to Incident Management

    OpsRamp today extended its IT operations platform infused with machine learning algorithms, also known as AIOps, into the realm of incident management.

    The Summer 2021 release of the company’s namesake platform adds alert predictions for preventing outages and incidents, alert enrichment policies for faster incident troubleshooting and enhancements for automatically ingesting metrics data collected from the Alibaba Cloud environment and open source Prometheus monitoring software as well as Hitachi, Poly, VMware and Dell EMC platforms.

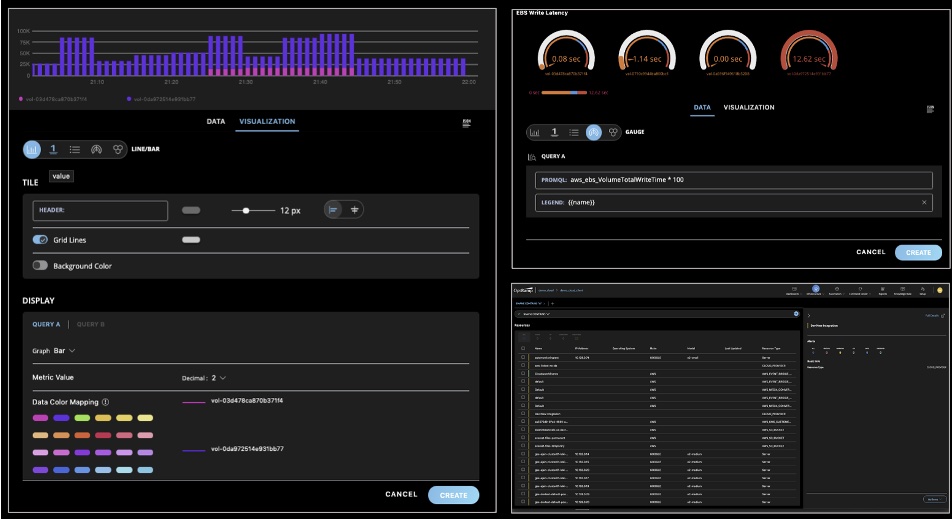
    IT operations teams can now also visualize metric values that can increase or decrease within a fixed range using Gauge charts. IT teams can also now add alert context details to provide more relevant information. There’s also now a mobile app for both Apple iOS and Google Android devices through which IT teams can now respond to alerts and incidents.

    Finally, OpsRamp is also making available a beta release of dynamic Workflows, which enable IT team to maintain a single decision table to address specific operational scenarios.

    Sheen Khoury, chief revenue officer at OpsRamp, said the goal is to leverage artificial intelligence (AI) to increase application availability by enabling IT teams to better predict when there are indicators of an incident caused by, for example, higher volumes of seasonal traffic that could lead to an outage.

    At the same time, IT operations teams can improve overall time-to-value by leveraging the automatic monitoring tools that are embedded in the platform, he added.

    OpsRamp is betting that rather than waiting for incumbent providers of IT operations platforms to add AI capabilities, many IT teams will opt to deploy a new IT management framework altogether. Many of the manual tasks IT operations teams regularly perform today can then be automated faster, noted Khoury.

    Naturally, it takes time for machine learning algorithms to be trained, so the benefits of AIOps are not instantaneous. However, those algorithms will continuously learn the unique attributes of an IT environment in a way that makes it easier for IT teams to manage an IT environment more proactively. The algorithms provide the added benefit of making it easier for new members to join an IT operations team without having to spend months learning all the nuances that are unique to that environment.

    Each IT team will need to decide for itself the degree to which they want to rely on an AIOps platform to manage their IT environment. Initially, most IT teams will need to evaluate the recommendations made by an AI platform. However, as they gain confidence in the recommendations, they will trust the platform to automate more processes in response to events occurring in the IT environment in real-time.

    Regardless of how much faith IT teams put in AI, it has become apparent that enterprise IT environments are only going to become more complex. Many IT teams will not be able to manage some environments without the aid of an AI platform. Many IT professionals may not want to work for organizations that don’t provide some way to augment their skills using AI—the stress level would simply be too high.

    One way or another, DevOps teams that are highly committed to ruthlessly applying automation will be at the forefront of AI adoption in the enterprise.

  • Is AI Taking Over DevOps Functions?

    Is AI Taking Over DevOps Functions?

    Artificial intelligence has taken the tech world to a new level of automation. Today, almost every specialization demands the intervention of machine learning to develop AI technologies that help businesses do more with less time and resources. Still, some organizations question whether leading with AI is a good investment. 

    For DevOps, the answer is a resounding yes. AI can enhance DevOps practices to accelerate the pace of software releases, helping businesses achieve continuous delivery. This enables programmers to release software about 10 times faster and allows programs to be reviewed before they are released. 

    AI also has improved DevOps culture, from enabling more efficient decision-making processes to code quality enhancements and automated operations. So, let’s take a deeper dive into how AI impacts DevOps.

    Recent Changes in DevOps

    Monitoring and managing all the data generated in DevOps environments involves a high degree of complexity, making it difficult for teams to collect and use data effectively. In addition, the volume of data any given team may receive can reach well into exabytes, so AI tools provide much-needed assistance. After all, analyzing massive data sets manually would take too much time for a human and won’t meet the demands of modern businesses.  

    What’s more, surveys show that 57% of developers in the United States have less than five years of experience. For this reason, software testing must be an ongoing and in-depth process to check and double-check that no vulnerabilities impact the security of the code. AI can supplement manual review to increase speed and accuracy in finding bugs. 

    That being said, integrating AI into DevOps functions doesn’t mean developers aren’t necessary, even though their roles have evolved considerably. Backend developers are involved in the development and operations sides as they take on ops tasks and tests, especially around cloud-based infrastructure and cybersecurity. And frontend developers will always be needed for the technical support of creative design—which no one can do better than humans. 

    In today’s dynamic and fast-paced world, developers need to release code faster than they used to while the operations teams ensure that the existing systems function with minimal disruption. This partnership is easier when integrating AI, as it makes the collaboration between development and operations teams more efficient. AI-powered systems provide a unified view into systems and glitches in the complex chain of DevOps. 

    Is AI Taking Over DevOps?

    Short answer: No. AI is supplementing human activity in DevOps to make things more efficient and secure. 

    Due to the complexity of DevOps requirements, people have been looking for a more automated solution that could assist humans in performance and accelerate the processes. What’s more, you can expect to pay around $60 an hour for an experienced backend developer in the U.S. This means using AI to automate the grunt work can be a big cost saver as well.

    Here are a few ways AI transforms DevOps functions:

    Enhanced Security

    Distributed denial of service (DDoS) and related attacks have become a widespread threat to the security of websites and online services these days. AI-powered tools have the ability to identify and mitigate these threats. In addition, AI can help in the pivot to DevSecOps in teams still using traditional DevOps.

    AI security tools detect anomalies and threats based on real-time data and by analyzing past behavior. In this way, AI has played a vital role in protecting many organizations, including schools and colleges, from cyberattacks by supplementing human security experts.

    Improved Data Access

    The massive amount of data that needs to be collected, organized and analyzed in DevOps is beyond human capabilities. However, AI has resolved this issue by compiling data from multiple sources and organizing it for analysis. This drastically improves and accelerates the process of DevOps.

    Rapid Software Testing

    Software development and software testing has accelerated with the integration of AI. As a result, various testing types used by DevOps, such as user acceptance testing, regression testing, and functional testing, are more efficient and accurate than ever.

    These tests produce a large amount of data that would take humans ages to identify and collect manually. With the help of AI, identifying patterns and coding practices that lead to errors and vulnerabilities has become convenient and fast. This data can then be used later by the DevOps team to increase their efficiency and improve development practices. 

    Timely Alerts

    DevOps teams sometimes struggle to react and respond to the alerts during incident response. With no priority tags attached, it becomes challenging for the team to prioritize incidents effectively. A more efficient, comprehensive alert system should be capable of spotting flaws instantly and marking the more severe ones as higher priority. That way, the team can tackle the issues more systematically and resolve them without failure.

    AI can assist in prioritizing the responses to alerts based on certain factors, including the intensity of the alert, the source of the alerts and past behavior. This leads to efficient management in situations where systems get flooded with massive amounts of data and have to respond immediately. AI-powered alerts are particularly important in DevOps security, so this is a critical benefit of AI in the discipline. 

    Superior Implementation Efficiency

    DevOps teams are often burdened by the managerial tasks of a rule-based environment which decreases their time spent in more innovative and creative areas. When AI takes over, these tasks become self-governed, increasing efficiency and reducing human intervention. AI systems can work on their own, sparing humans from these tasks to focus more on innovation and creativity.

    This way, AI has turned the DevOps into self-governed systems that no longer require the rule-based, human management of analysis. This should resolve the complexity of research that DevOps teams were struggling to achieve and enable faster adaptation.

    Feedback Loops

    The primary function of DevOps is to use monitoring tools to gather feedback from every stage of operations and then use that to improve software development and delivery processes. Performance monitoring tools use machine learning to gather information such as performance matrices, log files, datasheets, etc. The feedback collected is then used to track potential issues in advance and make suggestions to resolve them accordingly. The application is then altered by applying these suggestions to make it more efficient.

    Artificial intelligence is driving increased efficiency in DevOps functions. However, it would be a stretch to say that it is taking over, as there are still many areas that require human intervention. The idea behind AI integration is not to change the players but to change the game.

    Even though AI is assisting humans in accelerating software development, developers still lead many aspects of the craft. But it also seems impossible to perform DevOps functions at the required pace without the integration of AI. So, if you wish to release software at a pace that keeps up with modern tech trends, you need to incorporate AI in your DevOps functions.

  • EP 18: Does Standardization Disrupt Innovation?

    EP 18: Does Standardization Disrupt Innovation?

    Although everyone has their own definition of DevOps, it all comes down to creating better software faster, empowering development and operations teams and delivering value to customers. However, there really isn’t a standard approach to DevOps.

    Should we standardize DevOps to introduce automation, avoid confusion and speed up the process? Will standardizing DevOps foster or disrupt innovation?

    In this episode of DevOps Unbound, hosts Alan Shimel and Mitch Ashley are joined by Jayne Groll from the DevOps Institute, Paul Bruce from Tricentis and Sarah Baker from Airbnb to discuss the pros and cons of standardizing DevOps, the challenges of standardization and possible solutions. The video is below, followed by a transcript of the converstation.

    Alan Shimel: Hey, everyone, welcome to another DevOps Unbound. If this is your first time catching a DevOps Unbound, welcome. DevOps Unbound is a biweekly video series where we talk about relevant topics in DevOps. In addition to the biweekly show, we do, it’s every four to six weeks, a live roundtable show where we invite the audience to participate and drive the discussion with online questions and comments and so forth, so we open it up to a live audience. Unfortunately, this show is not one of our live roundtables, it is prerecorded, but we have a great panel and I think you’re gonna enjoy it.

    I’m gonna get into today’s topic in a second, but before we do, let me introduce you to today’s panel. First of all, I wanna introduce a business partner of mine and my friend, Jayne Groll. Jayne, why don’t you introduce yourself to the audience, if you don’t mind?

    Jayne Groll: Thanks, Alan. Hi, everyone. I’m Jayne Groll, I’m CEO of The DevOps Institute, we’re a global member association and a certification body around topics related to DevOps. I’m really, really excited to be here and I’m hope everyone listening joins us at DevOps Institute and becomes a member.

    Shimel: Fantastic. Welcome, Jayne. Joining Jayne, I’m happy to have Paul Bruce. Hey, Paul, welcome, and if you wouldn’t mind, you know, introducing yourself?

    Paul Bruce: Yeah, hey, Alan. Good to be back. My name is Paul. In my full time job, I work with Tricentis in a number of different areas. I’m historically a performance and reliability nerd. In my off time, I organize a number of events, help to co-organize volunteer things like DevOps Days Boston, just did o11yfest this year about observability, we had that conversation, I think, with Christine Yen a couple months ago.

    Shimel: Good stuff. Mm-hmm.

    Bruce: And generally, I’m a people advocate. I had to pull DevOps out of my LinkedIn title because there were too many recruiters that I don’t need, because I’ve got a pretty good job. But also, because people advocate really describes what I care the most about, right? People are some of the hardest part of the DevOps people, process, and technology, really, software. So, I really focus my time on that.

    Shimel: That’s great to have you back on, too, Paul—good stuff. Next, we have a first time guest on DevOps Unbound today, a new member of the band, Sarah Baker. Sarah, welcome to DevOps Unbound, if you wouldn’t mind introducing yourself?

    Sarah Baker: Thank you. Wonderful. Welcome. My name is Sarah Baker, my pronouns are she and her. I’ve been working in Operations my entire career and I’ve moved into DevOps as something I always—I needed a name for it. I always wanted the people part of Ops and technology and DevOps was that. And I’ve been doing that as soon as I learned the term. And I’ve been moved and started working with Paul Bruce in the IEEE work group 2675, who is trying to create a standard for DevOps.

    Shimel: Fantastic.

    Baker: I work for—and today, I work as the Manager of Biztech in Airbnb.

    Shimel: Thank you, and thanks for joining us. That sounds like a great place for you to do this. And then the last member of our panel today is my co-host and another business partner, a long-time friend as well, Mitch Ashley. Mitch, if you wouldn’t mind introducing yourself?

    Mitch Ashley: You bet. Always good to have a good panel on with you, Alan. Mitch Ashley, I’m CEO of Accelerated Strategies, an analyst firm that’s focused on DevOps, and also on cloud native, cyber security, and digital transformation. I come to DevOps both as a practitioner and a vendor leveraging it, so very interested in hearing the perspective of folks on our topic today. So, thanks for joining us, everybody, too.

    And by the way, our DevOps Unbound is sponsored by Tricentis. I think you may have mentioned that, right, Alan?

    Shimel: No, I think I didn’t, Mitch, but thanks for picking it up for me. [Laughter]

    Groll: [Laughter]

    Ashley: I was trying to give you credit where credit may not be due.

    Shimel: Yeah, no, I don’t wanna take credit when I messed up. Yeah, DevOps Unbound is sponsored by Tricentis, and many thanks to them for their sponsorship. It makes all of this happen.

    So, let’s turn to the topic at hand today, guys. You know, when I first started DevOps.com eight years ago, I met Jayne maybe a year, within a year of that or a year and a half of that. One of the interesting things about DevOps is, there was no manifesto. There was no hard definition of what is DevOps and what is not DevOps, you know, contrary.

    And ever since then, it’s been a double-edged sword. In some ways, it’s helped DevOps grow, it’s helped DevOps stay current over the last 8 to 10 years as the world has changed, DevOps has changed along with it. On the other hand, though, we’re still dealing with the, “So, what is DevOps?” Right? “What exactly is DevOps and what exactly is not DevOps?” which is sometimes harder than what is DevOps.

    And as we sit here now, August, 2021, there really still is not a quote-unquote standard for DevOps. There is no standard DevOps. It is what you want it to be, right? As I think Andrew Clay Shafer said, “The DevOps you get is the DevOps you deserve,” right? But have we outgrown that stage? You know, that seems like a terrible twos stage of DevOps to some; to others, it’s what kept it cool. Has DevOps matured? Do we need standardization? Will it be something that kills the goose that lays the golden eggs?

    We’re gonna discuss that today, and I’m interested in all of your views. Jayne, as the CEO of DevOps Institute, how many people have taken certified DevOps classes and certifications with DevOps Institute? It’s gotta be tens of thousands.

    Groll: Yeah, about 25,000 so far. So, it’s a pretty large community.

    Shimel: Mm-hmm.

    Groll: And if you don’t mind, I wanna kind of just lay the stage, because I’m really interested in the standardization initiative. So, you know, I had a privilege of seeing, going to DevOps Days in 2012 in California. So, if you can imagine, it was in an old, dusty data warehouse, right, and it was at the very, very early stages. And so, one of the reasons DevOps Institute emerged was because there was a lot of really cool things here culturally, from an automation perspective, right, doing things faster, collaboration.

    And so, we started up DevOps Institute because we wanted to make sure the humans were represented. And I love that Paul and Sarah in particular both represented people. The problem with that is, at that point, it was very, very open, it was very kind of organic. You know, it was really a group of passionate people that were trying to just change the way IT operates, right, from a people, process, and technology perspective.

    What happened after that, though, is that there’s so much noise about DevOps that if I were an enterprise CIO right now, my head would explode, right? Now, is there one right way to do DevOps? No. Is it only gonna get you there with automation? No. You know, is there a very, very strong human element—absolutely.

    So, it’s a double-edged sword, Alan, as you said, is that we wanna be able to kind of scale down, right, some of the common language, some of the common definitions. I always say I’m married to a CPA, they have generally accepted accounting principles; maybe someday, we have generally accepted IT principles. But how do we distill the noise, right, and everyone having a different interpretation of how to do DevOps and what it is compared to, let’s get past the, “what is it?” We’ve spent, what, 10 years trying to figure out what it is, to, “how do we do this?” Right?

    Bruce: Mm-hmm.

    Groll: And it isn’t just one roadway that takes you there. So, I think it’s a challenge. I mean, we introduced foundational certifications around DevSecOps and SRE and DevOps Foundation and DevOps Engineering, really, to create kind of a common vocabulary more than the, “here’s the single way to introduce CI/CD.”

    So, I don’t know if that helps kinda set the stage, but I think it’s a really big challenge right now that, if we standardize it, we run into the risk of what happened with ITIL where it couldn’t keep pace, right, and it became religious. I come from the ITIL space, right, so it’s like, open chapter 1, verse 3 and sing a hymn before you introduce change management to how do we then, on the other end of the spectrum, it’s so open and so undefined that it’s really complicated for legacy, I call them heritage organizations, to be able to move from this step to this step.

    Bruce: Mm-hmm.

    Shimel: The church of ITIL. Paul, what’s your feeling on that?

    Bruce: Well, everybody’s on a journey, right? Your personal journey, your professional career, whatever, maybe you go do a walkabout on a particular topic to learn more about that. And so, we started this venture, there was an early round of, “Who wants to be involved in something like this?” in 2016. I answered a call from Bob Aiello and Lynn Carter, who were kind of forming this idea of, there’s a bunch of people who really care deeply who have practitioner practical experience in the field. And the early part of this process was just learning, kinda level setting on what we have done, right?

    Jayne mentioned that it’s hard, maybe, to have accepted IT standards, even though there are standards, right, that not every organization applies the same way. I don’t think that invalidates some of the general principles that we know to be true, which is, you know, you ship broken software, you hurt people, you hurt yourself, right? But those are high level. How do we break this apart and start to make sense of the world, as you said, the heritage, Jayne, you said the heritage organizations—what is so wrong, what’s going on that we have these kind of security problems, these performance problems, this inability to be competitive in terms of acceleration and stuff.

    And so, I think the purpose of a standard is not necessarily to force people to do something a certain way. I think it’s simply just kind of like, if you’ve ever had the Christmas ornaments or just ornaments box that has the insert that allows for things to be put in careful places and also work together as a unit, right, to provide a normative, not a prescriptive standard, but a normative standard to say, “Look, these processes that you already know? Well, you already followed these from, let’s say, 12207, right?” These processes around supply acquisition, knowledge management, human resources? Right, human resourcing in DevOps is a big problem, at least in the Boston area. Try to hire an SRE—there’s only about 15,000 to 20,000 in the United States, legitimately. There’s a reason for that demand.

    So, how do we think about the processes we already know and start to say, how are these things different because there are some accepted principles and practices around DevOps? Now, the practices are not things that you would ever wanna dictate in a standard. This is not the same granularity level as some other standards that dictate how to encode time formats. That’s very important at that level. But the level that we were working on was how to level set across the things that, especially organizations in high compliance and high risk industries, right, risk-averse industries—how do they take the practices and processes that they know from a process standard and start to go, “I understand how to plug, now, what the DevOps principles are into the standard to encourage both of those practices in a more predictable manner?”

    So, when we did all this work—it’s taken years, right, of a lot of learning collaboration between a whole host of people I don’t have even time to list out, but a lot of people from a lot of various different aspects of software have a lot of experience in those aspects. You know, it took synthesis and refactoring, and I was up nights and weekends just rewriting some of the statements, you know? And each of these, it’s a line to 12207, so there’s multiple processes, process declarations like quality management, quality assurance, verification and validation.

    Like I said, these project enabling processes and then these technical processes, and each of those process sections have outcomes, activities, and tasks. Things that are likely to occur in this area, right, as well as, regardless of how you do this, right, not dictating what the DevOps looks like, it’s outcomes of these things that are auditable, that not compliance but conformance. That you can confirm at various levels to these outcomes to say, if it’s important to get this right, when you hit the piñata, what comes out should be candy, not garbage, right?

    So, I’ll pause there, because I wanna give Sarah a chance to kinda provide perspective, because she’s also been working a lot with us, for all those years. [Laughter]

    Baker: I think I counted 27 people on the final author list for the IEEE.

    Bruce: Yeah.

    Baker: And it was many, many weeks of arguing, reading together the exact language. And I agree very much with some parts of what Paul says, and I wanna step back and talk a little bit about how I see, you know, what, to me, was the big shifts. And so, the way we wrote the doc was to kinda look at the 12207 and say, “How does DevOps change it? How has it changed the game? What are the perspectives that you need to have in mind in order to get the outcomes that Paul’s talking about, there?”

    And so, when we were writing it, we were writing it to that. How is this different, and to what extent do you wanna consider these areas? It’s a framework of thinking. At its largest level, it’s a framework of, for me, the value chain of delivery of software. And it’s not—and it uses many of the concepts that come out of learnings of industrial engineering, way back in the ‘40s, ‘50s, ‘60s. But it had never really come into a lot of the thinking of software, because software is different. And the more I was working and kind of digging into what are the concepts underneath DevOps, I came quite aligned with a lot of industrial engineering concepts about how things flow and how things move back and what the peaceful aspects are in that.

    And so, that—actually, if you read through the standard, you’ll see a lot of those flow pieces and all of the pieces that you then say, “Oh, it’s the feedback loops, yeah, lots of feedback. Collaboration, it’s all there.” And it’s just applying a lot of those learnings into software engineering, to me. And it was stuff I was like, “Oh, it’s so wonderful to have this.”

    And the other thing, one of the big learnings that I think I brought into the conversation is how—and Paul will back me up on this—how security for a lot of us changed slightly as we started walking our way through the 2675 work. The terms of risk became a very interesting concept that flowed through the document more than I would have expected.

    Bruce: Mm-hmm.

    Baker: And so, there was some learning within the totality of our team as we wrote this. It was quite fascinating.

    Ashley: I’m really fascinated to hear from both of you that have been working on this, because it’s not something I’ve been involved in. I sorta have a mixed history with standards, because I’ve worked in areas like networking and things like that where standards are very beneficial or really fundamental, but I’ve also learned standards are kind of what you’re gonna do, not how you’re gonna do it. Because we ran a test lab that, even though it says we’re gonna do least cost routing in a network device this way, people implement it differently and they don’t always work together. So, it’s not a nirvana, but it’s also not a pariah, either.

    Bruce: Mm-hmm.

    Ashley: So, what I wrestle with here is that, I think some of the thinking—and Jayne can speak to this, but innovation happens so quickly now. So many things are created without standards; maybe they evolve into standards, maybe they don’t. And it doesn’t bother me that there’s lots of noise around DevOps, because we’ve all seen the cycles, the hype cycles, right? If it’s worthwhile, everyone and their brother, sister, cousin, uncle will all jump on the bandwidth and call what they’re doing fill in the blank—it’s AI, it’s DevOps, it’s whatever. That’s just part of our industry. And it’ll either fizzle—you know, value stream management, is it a real thing? We’ll see. It’ll fizzle or it’ll happen, right, if it’s a real thing. And DevOps has proven itself not only is it a real thing, but other parts of the organization now see an opportunity to play, to participate, to become part of the software creation process.

    Bruce: Mm-hmm.

    Ashley: And I think that’s what’s so powerful about DevOps—it’s not about a technology, it’s about how we create software. And if you were gonna start out, you know, Jayne, when you went to that meeting in 2012 when you said, “We’re gonna go create a standard for completely doing software differently because we have cloud and we have the ability to automate and we were gonna change the software architecture,” you couldn’t have known how to do that. But being the industry would’ve, you know, the antibodies would’ve crawled all over all of us and stopped it. So, I think there’s a lot of power in the innovative, organic nature of it.

    And I don’t want DevOps to turn into ITIL, [Laughter] because that’s sort of taken on a life of its own, and now it’s trying to catch up and it’s done some good things, too. So, I wrestle with trying to constrain it when I think it’s real power is the innovation behind what we’re doing.

    Bruce: Yeah, so, before I—

    Baker: If I could take a moment—

    Bruce: – yeah, go ahead.

    Baker: – I’d like to take a moment and call out something. Part of the problem with ITIL is like, it’s ITIL. And, you know, a gazillion managers said, “ITIL, let us get a hammer and hit you over the head with it.” And DevOps, fortunately doesn’t have that problem. It has, you know, a little fuzzier in its definition, but the great thing about DevOps is that it has that sort of fuzzy edges. You can’t, it’s really hard to beat someone over the head with it. You can try. I’ve seen it happen, you know? Everybody’s a DevOps engineer now, but it’s not necessary.

    And what people talk about is not that, but the work, you know? It’s not, “We’re conforming with ITIL,” it’s like, “We’re doing DevOps.” The doing part is the important part, not the compliance part. So, when you say, when you hear people talk about it, they talk about it differently, and that’s the good thing.

    I use ITIL, I just don’t tell anybody the word.

    Jayne Groll: Which is a shame. It’s such a shame because, you know, I come from the ITIL space, and in the early days, this was not what the intent was to be. It was very much like DevOps in terms of, “Let’s help IT grow up,” right, in terms of some things.

    And, you know, to what you’re all saying, you’re absolutely right. A framework, whether it’s a standard, is a guideline, right? It helps you with the journey, as Paul said. And so, if I wanna kinda check, check, check—you know, I’ve worked with some of the ISO standards, right? So, in the ITSM space, there was ISO 20,000, 27,000 for security, right? And it basically, like, in the one or service management says, “You should record all your changes.” It doesn’t say how to record it, it doesn’t—it’s a really great practice, you should do this.

    The problem, sometimes, with standards—and I’m sure you know this and it’s a risk—the pure intention is pure. The ability to weaponize it, right, from the auditors and from others is a real risk, right? Because we’ve seen that with other standards as well, where it becomes more about the compliance than it is about how having it being a guiding light. So, I think there’s always a risk there.

    And then the other risk is, you know, think about observability, right? So, observability has been trending, what, for a year, maybe two, right? Four—okay, but really mainstreaming, like, talking about observability as kind of a mainstream practice, right? And I will share with you, Mitch, to your point, when we launched DevOps Institute in 2015, we were not welcomed with open arms, right? We were vilified for trying to put some boundaries around this.

    Now, you know, move forward seven years and I think we’ve overcome a lot of those and we have some that were detractors or really great supporters. But I think they were concerned that it would become weaponized or commoditized or whatever.

    So, I’m just gonna say one last thing because I think it’s important. Commoditization of knowledge, which, this is kind of in support of the standard, right? Commoditization of knowledge where we make sure it’s available to everyone, some people see that as a negative—it’s not. What would happen if the whole world, right—every IT organization, every IT professional decided to take this standard and use it as a guiding light, according to the needs of their organization? They weren’t worried about the audit, they got trained, they shared knowledge—wouldn’t that be amazing? But that’s commoditization.

    So, I think the risk of good versus evil on initiatives like this is real, but I also think that distilling it to everybody, kind of like accountants have done, right, is important because IT needs to grow up.

    Bruce: Yeah, well—

    Ashley: Well, and if you look at the accounting standards, they don’t tell you how to do it, they tell you what to do.

    Groll: Right.

    Ashley: It isn’t prescriptive in the how very much, so it’s very much like an IEEE standard or whatever.

    Bruce: Yep. Well, first off, I forgot to mention when we first started—I speak as an individual contributor. If it isn’t abundantly clear, [Laughter] I don’t speak for the IEEE, and I don’t speak for the other people who have spent years contributing to this meaningfully.

    So, when I say certification processes inherit all the exact same things you just mentioned as problems—weaponizing, actually low ROI maybe in some cases—we see these deficiencies and these outcomes that aren’t so great. And if you’re somebody who’s just gonna sit back and say, “I’m not willing to hold myself accountable” to stand up and say, “What does this thing actually mean like a real engineer should, you know, to start to break apart the problem and see what are the components, how does this thing work and how do I want it to work? How does it work best for the people around me as well?” If you’re not willing to do that, then I would call you the nay-sayer, you know what I mean? Like, not any one in particular, but that would be a nay-saying, like, let’s avoid accountability, let’s avoid doing what we know needs to be improved?

    Continuous improvement is a huge element that is all throughout the entire standard. It’s one of the things that’s identified as some of the core principles in an ISO study that was done before we started in on this standard to see what are the common themes of people, when they’re really feeling like there is this DevOps mindset, this culture, these practices—what do they mean by it?

    And a number of things came out. One was a high degree of automation, right? Okay, well, that’s very tactical. No matter how you do it, right—high degree of automation. Duh, right? How about effective communication and collaboration? How about shifting things and continuous everything? The notion of, that these things are not this one time and then three years later, you get to come back. No, no, no. If it’s a good idea now, maybe don’t bite off a three-year apple. Maybe take a bite, but know that you started in, there’s a continuous improvement process.

    I can say, we mentioned earlier about a holy war that might exist when you start getting into what is DevOps and what is not DevOps. Like, I started—the best way I can describe to people, because like I say, half of my day is spent on and off of Slack with people who are actually doing, working this out in a highly statistical, large distribution across the country, you know, and sometimes outside the U.S., too, just time zone supply.

    But I can say, for sure, after seeing the complete garbage Dumpster fire where nobody is willing to stand up and say, “Hey, aren’t these things common and standard?” And oh, by the way, not vendors that have something to push, right? I mean, that’s, I think, Jayne, where you were talking about maybe observability is now a thing. You know, the only reason why it’s a thing for the most part is because it’s in our face now because all the vendors are hash tagging the crap out of it.

    Same thing happened with DevOps five, six years ago—everybody had to get on the bandwagon. I remember CEOs way back then going, “What is this DevOps thing?” Oh, man. You know, just talk to some of your engineers.

    And what I can say, right, I have developed at least an internal personal perspective on what is not DevOps. So, if I can borrow the last 30 seconds of the mic for a second, here are some things I wrote as notes as I’m going back over the standard, re-reading it, going what I violently agree with from both others and myself, we did not have a chance to see this before it went live many times, right?

    So, what I got from one of the higher order sections in Section 5 was this feeling of, like, what is not DevOps. And those things are burnout. DevOps is not burnout. You know, you’ve probably been burnt out if you’ve worked in DevOps before, so where is this coming from? Why is this the case? It’s not burnout, it’s not no help. You don’t get any help, go do this thing, you know? It’s not heroics. It’s not superheroes in capes, right? Single points of failure, as I call them. It’s not cliques—which, by cliques, I mean power silos. Huh-uh, there is no such thing as The DevOps Department, people. There’s no rogue decisions. There’s traceability in decisions. There’s accountability in decisions.

    Leadership thrash—not easy to, if you’re really adopting this DevOps mindset and way of thinking about how to do things better, leadership thrash doesn’t really fit in. Toil and debt, right? One of my biggest things is, you know, I seek to eradicate toil, which is not easy. [Laughter] Just reducing it a little is nice, but it’s, and it’s probably pragmatic to say so, but really eradicating toil from other people’s plates and from your own, that’s a challenge, right? That’s kind of a life goal. And if we do this stuff together, right, if we say these are not the things we want, the question is how do we move towards something that isn’t those things, right, and that is closer to where we all align and agree, like, this is a better way of delivering software and doing it faster, right?

    So, anyway, I’ll pause there.

    Ashley: You know, one of the things I’d love to hear from both Sarah and Paul is, there’s always sort of that, “So what?” answer—question, right? “If we did this, what is the result? What’s the impact of it?” And I mean that in a positive way, I’m not being critical.

    Bruce: Yep.

    Ashley: If this standard was widely adopted, how would it improve? How would it—what things are we wanting to improve and change from where we are today? Can you describe that in any way to kinda give myself and others maybe an idea about that?

    Bruce: I just did. People already implemented it.

    Baker: Well, at the base, there’s the vocabulary, yeah.

    Bruce: Sorry, people are—

    Baker: At the base, that is part of it. Sorry. Paul and I always get [Cross talk].

    Shimel: Sarah, go ahead. Paul spoke—you go.

    Bruce: Yeah, yeah.

    Baker: Vocabulary is that first piece, making sure we’re all talking about the same framework. And so that, when we’re exchanging ideas, how did you do it, how did you do it—you know, not any one way to do it is gonna it, but knowing what your options are and talking about it with others and trying something out and figuring out if it works or not in your environment is one way to get everybody on the same playing field. But if you’re not talking about the same thing, you can’t do that.

    So, it’s having the ability for a large corpus of options to apply to your situation. To me, that’s one of the biggest things that it provides, and it also gives you ways of interacting with the rest of the business that is not IT, and kind of, “Oh, this isn’t—it’s not just IT. You’re a stakeholder, you’re a customer.” And it includes all of those pieces for the collaboration and really helps support it.

    So, to me, that’s what the standard brings. It widens the organization’s perspective a lot, and allows that cooperation to seep into the organization across all of these different pieces. Because to me, that’s how it started as DevOps, DevSecOps, DevOps Observation Ops. I mean, it grows because that’s part of its DNA is to include.

    Bruce: Yeah.

    Baker: And so, it’s very natural that it has done that and it includes other parts of the organization into that basic thought processes. I totally could see DevOps marketing security—I mean, you see all that. That’s what’s, to me, the real advantage of thinking this way is that it includes the entire org.

    Groll: Well, and first of all, utmost respect to Paul, Sarah, and the other 25 people that are working on this, because this is a gargantuan task, right? Trying to encapsulate something that creates a common framework, that has the purest intention and also, you know, if you think about the heart of why DevOps emerged in the first place, it emerged because we were not collaborating together, right?

    So, you know, in the early days of IT—I always say I’ve been in IT longer than I really want to admit to—you know, there were 25 people that sat on the same floor, in the same office building, and we all knew each other and we went to happy hour. And then, you know, the tree grew and there were lots of branches and other things. So, you know, giving a central source of truth that everybody can kind of internalize, process, speak the same language—you know, IT, we have so many different languages, we’re like countries that are butt up right next to each other.

    And I said, I have so much respect, because this is a gargantuan task. And Sarah, I agree with what you said, the purpose is really to take this need for collaboration and optimizing automation, right, so making automation essentially members of your team, right, and then taking that out into the business because every business is a technology organization, it’s—I’m sure you’re aware of the risks. You know, we’re not telling you anything that you’re not aware of, but as I said, I just have so much respect. Because it’s not gonna be an easy road, right? There are so many different opinions from vendors and from everyone who’s involved in this space that are going to have an opinion or whatever. And I think, you know, that’s something that everybody’s gonna have to deal with.

    Again, the only thing I would suggest is build it in a way that it’s nimble—dare I use the word agile, so that—

    Bruce: So, this is already done, right?

    Groll: Yeah.

    Bruce: Like, this is not a draft, this is not an initiative. This has already been done for the past four years and is now an official standard. So, the good news is, to your point, I think, about suggestions about how to do this, we are working on the second version of this draft already.

    As soon as it was out, even before it was out, we knew there were things that we just couldn’t—we couldn’t spend the time properly addressing. Like I said before, there was a lot of refactoring, but there was a lot of careful avoidance of not already repeating what was already in a good security standard over here, or in a good risk management thing, or one of the folks that worked with us, Tafline Ramos, works at the ISO, right? And what is it, 29119, right, verification and validation, the processes—that was already stuff that’s already been, and great thinking and not slow, you know? Can fully be put into a modern, unicorn sneeze rainbows and fart sprinkles type approach as well as the large Fortune 100.

    So, just to say, this is already—we’ve already put a ton of, it’s already out there, and the easiest way is, I mean, some people might be wondering, “Oh, yeah, but it’s a standard, so now I gotta pay for it?” Some standards, you do; some standards, you don’t. This one, IEEE, they cover their costs with the standards. The easiest way, if you wanted to get a free copy, become part of the new, the next version of this, right? See what we’ve done, poke holes in it, have collaboration, let’s work on it together, because that’s the point of this is to bring a framework of how we are working together in a more effective manner.

    Jayne, I’m really sorry I cut you off.

    Groll: No, no, you didn’t cut me off. Just a cautionary tale. One of the reasons ITIL kind of lost a lot of its momentum—and I’ll be very frank, I owned an ITIL training company for 15 years and I was a chief evangelist, but it took 8 years between version 3 and version 4. And so, it wasn’t built, it was a monolith.

    Bruce: Mm-hmm.

    Groll: And I think that was—you know, in the meantime, lots of other things happened, and I think there’s a cautionary tale. I’m not suggesting you’re looking at eight years, please don’t misunderstand, but this market is so—

    Bruce: No, it’s probably about three, right?

    Groll: Yeah, this market’s pretty fast. Sorry.

    Bruce: Our target is about three, between where we officially started and now it’s out and the next revision, at most, would be another three, right, that’s our target. It could be earlier or later than that.

    Think about, we’re all citizens of the United States here, right? Or anybody in Canada?

    Shimel: Is that a HIPAA violation to answer?

    Bruce: Yeah, right.

    Shimel: Just kidding, just kidding, just kidding.

    Groll: [Laughter]

    Ashley: I’m not showing you my vaccine card.

    Bruce: I ask because, I ask because—

    Shimel: I didn’t wanna go there, but go ahead.

    Bruce: – we all know what the U.S. Constitution is and where it came from.

    Shimel: Mm-hmm.

    Bruce: Do we think that it was perfect and never has to be revised? Absolutely not. That’s what the Amendments are for. And arguably, I people wanna go back to the original version, there are some serious problems with that original version. Same thing with ITIL, same thing—remember with, I think you might have heard about The Agile Manifesto. You know, that was a drunken party with a bunch of white dudes, okay?

    Groll: I know. [Laughter]

    Bruce: So, yeah, there were some good ideas that were encoded in there, but do they not have to be revised and worked out? Even Dave Thomas says agile is dead, long live agile. Like, what people have taken it to is not the point.

    So, the goal of this is to really get a full perspective. To what Sarah was saying, it’s not just—I’ve talked with a lot of the DevOps Days, various different people from DevOps Days, from a number of different, like, The DevOps Enterprise Summit and stuff, and there are some people out there that are like, “No, DevOps is just about developers and operations and it’s about just these things, and if you start getting biz in there—no, no.” And it’s like, what a narrow perspective, because you know what, you had a good idea and then you screwed it up by not including other people, by not realizing there are meta learnings that come out of what you locally did—maybe, arguably, you did well—that apply broadly. And when they do apply broadly, they bring us back to the same premise, which is, we’re all in this together, right? We all win when we all win. As Tim O’Reilly might say, provide more value than you consume, right?

    So, that’s where we intend on taking this. It’s not to turn into a bunch of agile consultants again or ITIL consultants, right?

    Ashley: [Laughter]

    Groll: Framework growers, that’s what we call it.

    Shimel: Yep. Guys, I gotta pull the plug on ya, I’m sorry, guys, and ladies. We are out of time. I think a great way to end this, though, is—Sarah, Paul, where can people get more information on the standard from the IEEE?

    Bruce: Sure. Google it, Google IEEE 2675, you’ll get to that page if you wanna buy a copy.

    Shimel: 2675.

    Bruce: I think without being a member, it’s like 99 bucks—so, look, you know, if you wanna buy it for yourself—

    Shimel: It’s not breaking the bank.

    Bruce: You probably also have, in your organization already somebody’s a member, your Risk and Compliance are probably already members to IEEE.

    Baker: Yeah.

    Bruce: And again, like I said, the best way to get a free copy is to come work with us on what does the next standard mean. It’s not a huge effort and commitment like Sarah and I have put in. [Laughter]

    Baker: [Laughter]

    Bruce: You can dip your toes in, see what makes sense, what works for you, and we love to—we include people in that effort.

    Shimel: Great. Well, Paul, Sarah, Jayne—thanks for joining us on our panel today. Mitchell, as usual, great job. This is another edition of DevOps Unbound in the books, check it out. Go check out the IEEE standard. We’ll be back in two weeks with a fresh show and a fresh topic. Until then, this is Alan Shimel, be strong, be well—Tech Strong. Take care, everyone. Bye bye.

    [End of Audio]
  • Sentry Integrates Code Observability Tool with GitHub, GitLab

    Sentry Integrates Code Observability Tool with GitHub, GitLab

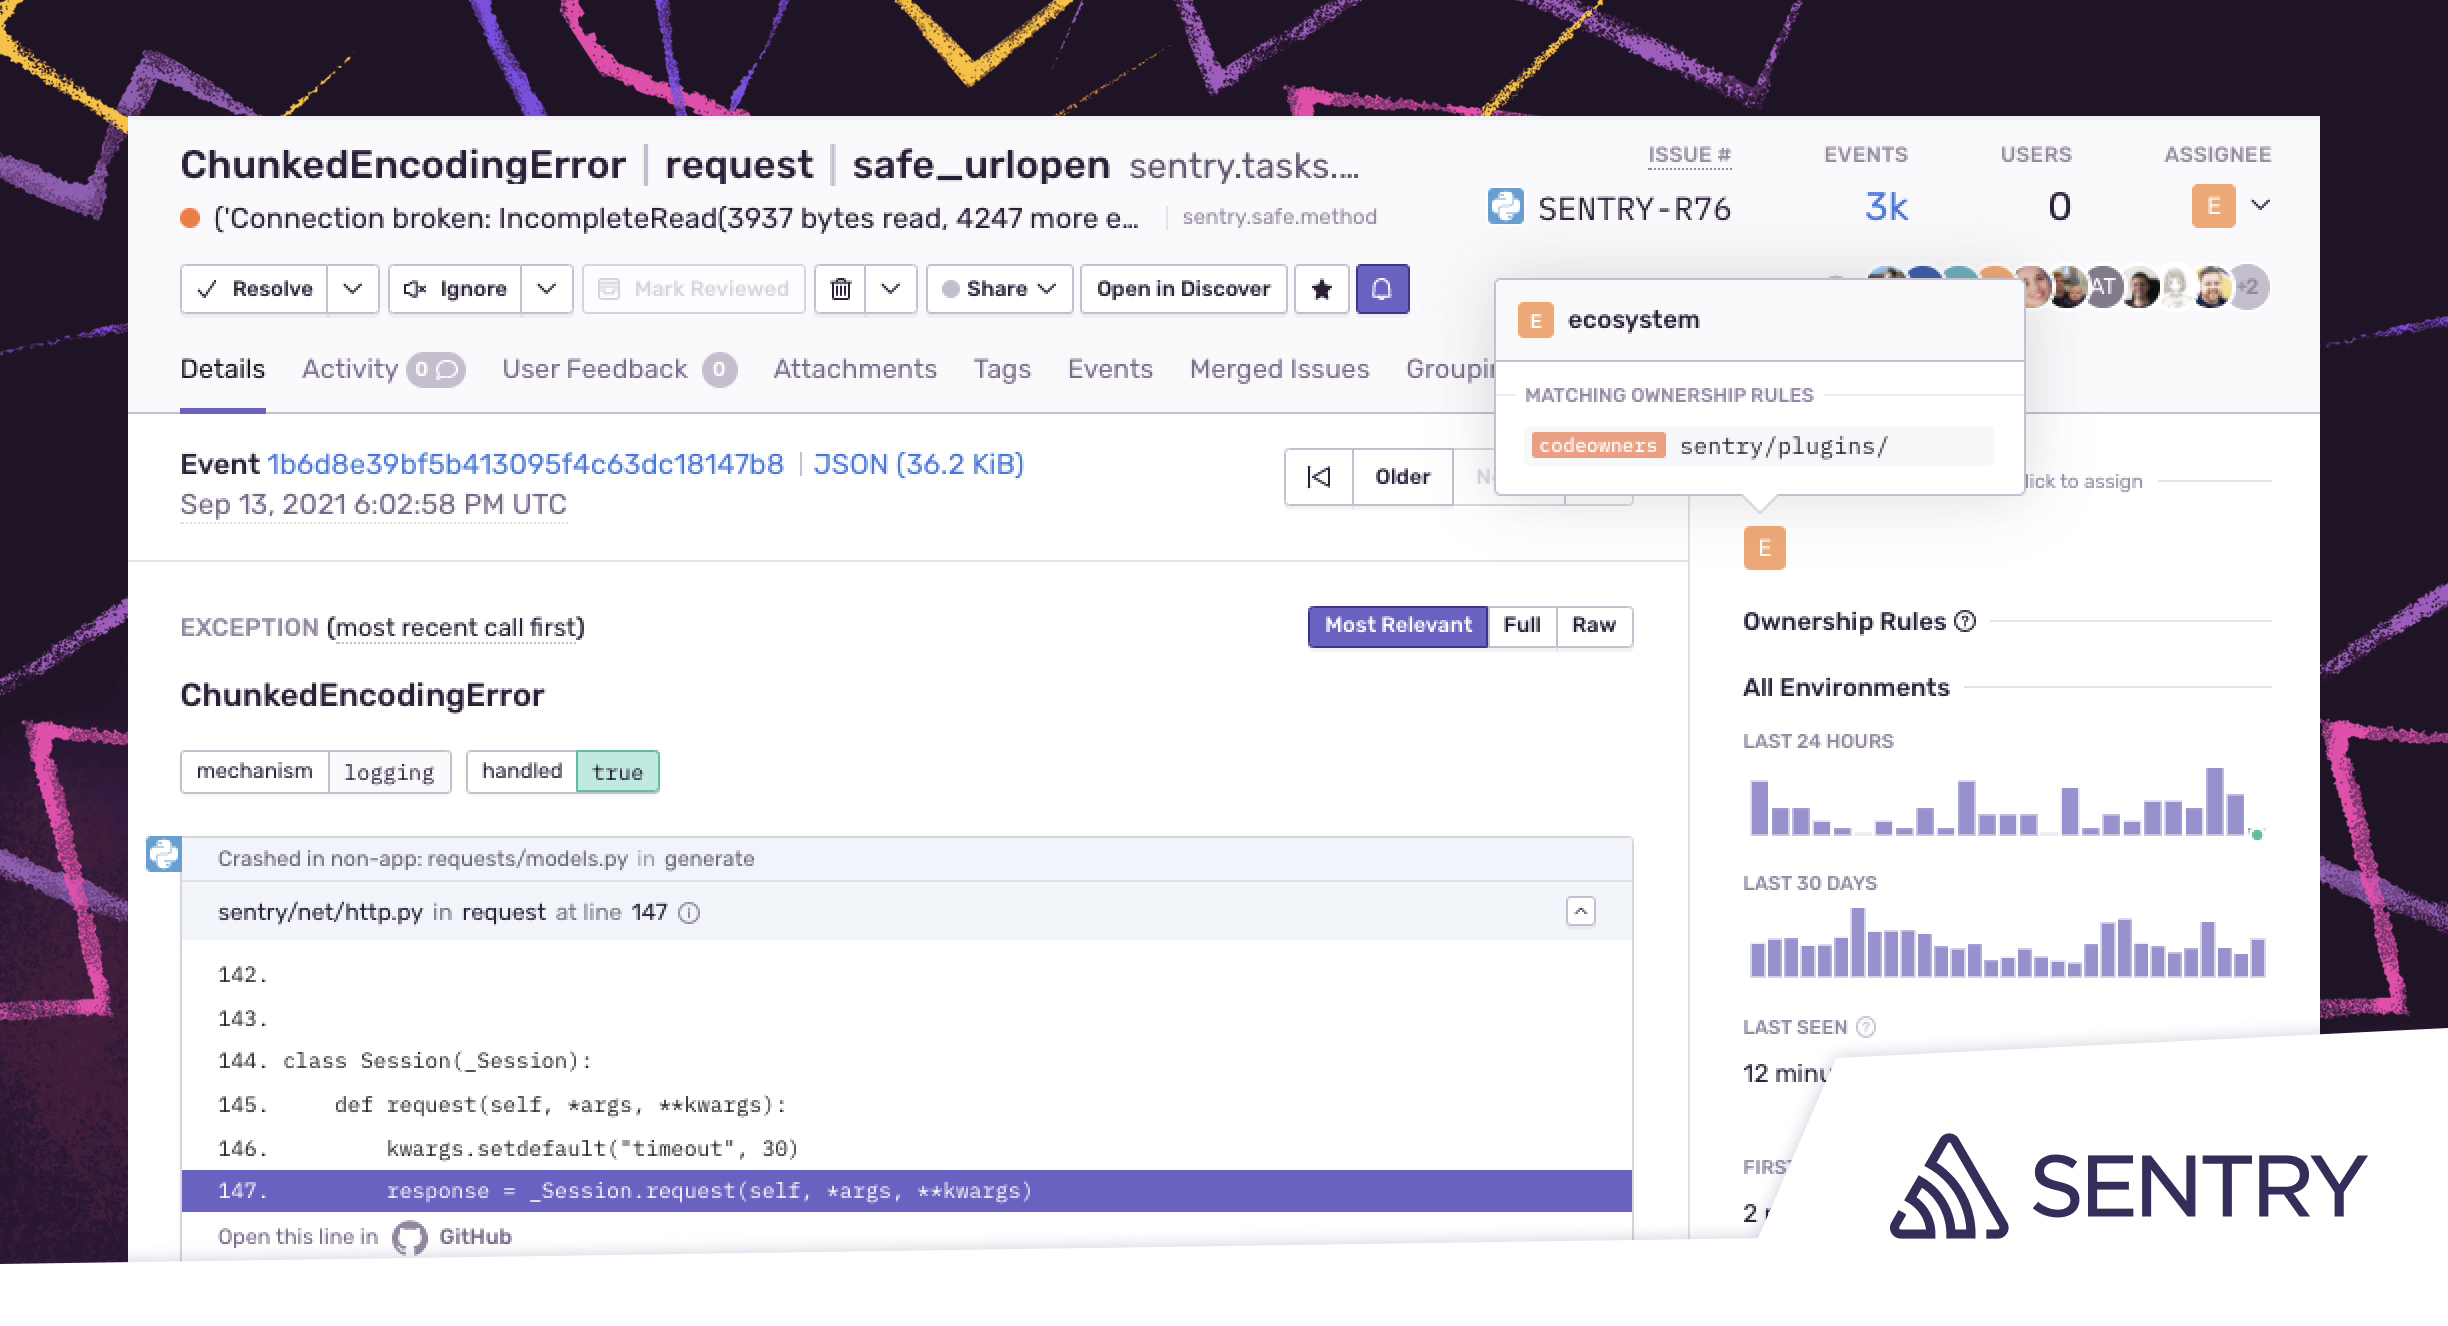
    Sentry this week extended its namesake observability platform for code to provide tighter integration with the DevOps platforms provided by GitHub and GitLab.

    Application development project managers can now assign issues to DevOps teams by integrating directly with the CODEOWNERS file in GitHub or GitLab. Error messages, for example, can now be automatically routed to individuals or teams that own the code via notifications in Slack.

    IT teams can now also identify and prioritize issues based on user impact by setting alerts based on when an issue exceeds a certain percentage of user sessions within a specific amount of time.

    Sentry CEO Milin Desai said that the percentage-based approach to alerts reduces the overall noise being generated in a way that enables DevOps teams to better prioritize their remediation efforts.

    Finally, Sentry has added an integration with the Okta identity management platform to make it possible to automatically provision and de-provision users and teams using the system for cross-domain identity management.

    As more responsibility for managing the application environment shifts left toward developers, there needs to be a way to streamline communications between developers and the rest of the IT operations team, noted Desai. Most developers today already spend less than one-third of their time writing code.

    The Sentry platform is already used by more than 75,000 organizations to enable developers to better observe and analyze code behavior. The company is now moving to bridge the divide between developers and site reliability engineers (SREs) by streamlining communications and workflows, noted Desai.

    As the responsibility for managing applications shifts left, developers don’t necessarily want to use the same tools that IT operations teams have relied on for years. Most developers want to be able to troubleshoot their applications with minimal interaction with IT operations teams.

    Historically, IT operations teams have relied on application performance management (APM) platforms to manage IT operations. Those platforms are now evolving into observability platforms that promise to provide more context by correlating events as they occur across both applications and IT infrastructure platforms. That approach, however, typically requires developers to insert agent software into their applications. Once inserted, that agent software needs to be maintained and updated, added Desai.

    The Sentry approach provides developers with a tool for collecting data from an application in a way that consumes just tens of kilobytes of memory after being embedded directly within an application. That approach eliminates the need to rely on much larger agent software to achieve observability of application code. Developers can then diagnose and possibly remediate issues in code without ever having to create a ticket asking a DevOps team to investigate an issue.

    Regardless of how developers go about instrumenting their applications, most everyone in IT agrees that the current state of observability needs to improve. The issue now is determining how best to achieve that goal in a way the benefits both the DevOps team and the developers that are now being asked to not just write code but also manage the entire application life cycle.

  • Empowering Teams to Make Mission: Impossible Possible

    Empowering Teams to Make Mission: Impossible Possible

    “Your mission, should you choose to accept it….”

    That’s the way the original Mission: Impossible TV show and, later, the movie series drew us in. The bad guy’s operation was explained. The goal was clearly defined; infiltrate and destroy. And although the task at hand was extremely difficult and fraught with unknowns, the team of good guys was briefed and everyone understood what they were doing and why. Cut to the good guys succeeding despite the odds being stacked against them.

    For most of us in product development, I think we’ve all faced—or are facing—our own impossible mission. We’re all working on “urgent” projects against some pretty tough odds. Except, unlike the old TV show, we often lack a clear goal. Sure, we’ve got our best team members on it—but does everyone understand why we’re doing what we’re doing? What, exactly, is our mission?

    No Dossier, No Chance

    In the frantic rush to “digitally transform” by churning out new products and features, the mission (if there ever was one) is often lost. Without context, developers can feel like order takers instead of outcome producers. This dynamic is a ticking time bomb; not just in terms of value delivery and business success, but for developer happiness, too. With a worldwide developer shortage and, more importantly, the fact that 80% of developers are reporting burnout, something needs to change. And fast.

    Improving the software developer experience must be a priority. And a clear mission is a great place to start. When we’re not mission-driven, our chances of being innovative, experimenting with new ways of work and empowering ourselves to be at our best are severely limited. 

    Liberated Mercenaries 

    By adopting a mission-oriented approach, development teams gain purpose. Bringing them in on the business problem that needs solving can motivate them and stimulate their creative thinking. And the cherry on top? We can even help reduce their workloads by removing meaningless blackhole tasks. We begin cultivating a work environment that helps realize the “joy;” part of one of Gene Kim’s Five Ideals. 

    For those overseeing DevOps or other continuous improvement initiatives, we can improve our odds by creating our own Mission: Impossible-like teams. To cite John Doer, venture capitalist, we can build teams of missionaries instead of mercenaries. Folks who are motivated, passionate and outcome-driven. Those galvanized by the excitement of knowing that their efforts will impact the business in a big way will inspire greatness. 

    It is the leader’s role to articulate the mission. When practitioners are empowered to use their creativity for problem-solving, innovation is unleashed and there is little room for misguided, wasteful activities.

    Preparing your Mission Dossier

    You are not alone if your answers to the following are no better now than they were five years ago:

    • Are we prioritizing our customers’ problems first?
    • Are we enabling customers to pull value rather than pushing what we believe is value?
    • Are we providing abundant opportunities for customer feedback and pivoting with learnings from failures?
    • Are we routinely surprising and delighting our customers with exceptional value?

    These are the kinds of questions that indicate how well we understand our mission. If we are aligned with customers, then, by definition, we are aligned with the business since businesses only exist to serve customers.

    So then, how do we articulate the mission so our teams clearly understand their purpose? Here are three steps to get you started.

    Step One—OKRs

    We must emphasize our focus on solving problems for our customers, both internal and external. The objectives must be clearly stated, as they were for Mr. Phelps. And, likewise, we must communicate the sense of urgency that this mission encompasses for the fleeting window of opportunity that exists before customers seek alternative solutions. 

    One highly effective approach is to employ objectives and key results (OKRs) and an OKR tree so that everyone, from the trenches to executive leadership can have line-of-sight to the purpose of their work and their role in the mission. Since DevOps Enterprise Summit 2020 in Europe, OKRs have emerged as a hot topic as leaders seek to translate urgent corporate objectives into meaningful goals for their business and technology teams.

    Step Two—Focus on Flow of Customer Value

    We must set the stage for the successful delivery of customer value. Our processes must be aligned with real customer needs while simultaneously capable of delivery excellence. The best way to do so has been proven out for over 40 years now, i.e.: adopting a continuous improvement approach to the activities which make up the value stream from customer request to fulfillment. 

    That means capturing customer needs via our OKRs and accelerating the flow of work across the value stream against those OKRs. To do that, we must have a means to systematically and continuously remove impediments to flow across all key stages, before and after development

    This approach encourages everyone—top-down, bottom-up—to become single-minded and obsessive about our mission.

    Step Three—Tracking The Mission

    With the mission clear and the teams aligned, we must also be prepared to react and preempt uncertainty. No mission runs perfectly. But we can put literal measures in place to identify danger ahead. Combining team performance metrics, such as DORA, with higher-level value stream management (VSM) metrics that focus on the flow of business value across the whole system can help everyone in the field and in the control room communicate effectively. For instance, if work upstream is holding our developers back from cracking the code, VSM metrics can help direct leadership to send support into the business analysis room.

    With mission alignment and means of communication, accepting a mission becomes enticing for everyone involved and the chances of success improve dramatically. 

  • DevOps World: Forget Doc, it’s All About Dev

    DevOps World: Forget Doc, it’s All About Dev

    This year for DevOps World, we’re heading back to the future. Doc Brown won’t be there with his souped-up time machine, but plenty of devs will. As the world is coming to realize, developers are keeping everything running, from the apps we use on a daily basis to check the weather, bank online or order food to the self-parking features on autonomous cars and artificial intelligence that’s augmenting human intelligence. Software and technology are the future, which means the future starts with the creative mind of the developer. 

    The theme of this year’s DevOps World show is “Building the Future of Software, Together.” For developers, this cannot ring more true: Across the globe, dev teams are working to code new software pipelines that will power the world’s next great innovations. We’ve already seen voyages into space and breakthrough life-saving medicines this year—what more do developers have in store for us?

    As we look ahead to DevOps World 2021 on Sept. 28 to 30, we are putting the focus on developers by offering a number of sessions to help sharpen their skills and prepare them to build the future of software. In particular, we are looking at some of the recent challenges that have been affecting code, including cybersecurity, scalability and CI/CD best practices. 

    On the security front, we’ve seen a number of cyberattacks dominate news headlines this year. As a result, companies are hyper-focused on securing their software pipelines and ensuring business and customer data are safe. Developers now need to double as the first line of defense for their organizations, ensuring their code and pipelines are as secure as possible. We’ve geared a number of sessions towards helping developers sharpen their security chops—from CloudBees customer success stories to tips for building more secure code. 

    As DevOps professionals know, software today is about continuous everything. We’ve designed a number of sessions to share best practices for CI/CD, progressive delivery and balancing speed, innovation and safety. Imagine if the DeLorean didn’t need the plutonium and just ran continuously—that’s what we’re hoping developers will learn and take away from these sessions!

    Lastly, scalability has always been a hot topic in tech. Startups continue to pop up everywhere and as these companies grow, they need to scale accordingly. We want developers to be scaling pros when they need to be, so we have a number of sessions (including keynote presentations) on scalability. 

    DevOps World is the event for developers looking to sharpen their skills, learn new abilities and network with other dev professionals. As we look to build the future of software together, the people making the magic behind the code will be driving changes and innovation, and we want to celebrate that.  While Doc Brown may be a fun character who goes back to the future, it’s dev where the future truly is. Register for DevOps World now! 

  • Transposit Survey Shows DevOps’ Impact on CIO, CTO Relationship

    Transposit Survey Shows DevOps’ Impact on CIO, CTO Relationship

    A survey of 415 CIOs and CTOs conducted by Transposit, a DevOps process orchestration platform provider, finds that as organizations continue to adopt DevOps processes more widely, friction between these types of senior IT leaders is rising within many organizations.

    As a C-level role, ‘CTO’ first gained traction in the wake of the dot com boom. In more recent years, many traditional enterprises added CTOs alongside CIOs as they realized how dependent the organization had become on software. In the wake of the COVID-19 pandemic, there is now more focus than ever on digital business transformation initiatives that are dependent on the timely delivery of software.

    Transposit CEO Divanny Lamas said that as more organizations’ structures revolve around product teams, there are a lot more CTOs. In some cases, CIOs are reporting to CTOs.

    The majority of organizations surveyed have both roles. A full 83% of CIOs said there is also a CTO at their organization, while 86% of CTOs said there is also a CIO. Just under a quarter of respondents (24%) said they perform both roles.

    At the same time, 98% of survey respondents reported increased focus on digital transformation within their organization in the past three years, with three-quarters (75%) noting that focus has increased since the start of the pandemic. A full 85% report their budget has increased over the last three years.

    Not surprisingly, 92% of respondents said that their responsibilities have changed in the last three years, with over half (56%) reporting their role changed significantly. Both are now graded according to key performance indicators (KPIs) related to managing revenue, with 66.3% of CIOs and 78% of CTOs saying their position is now either directly involved in or required to lead a business strategy.

    But only 34%, or just over a third, said that ownership of most aspects of digital transformation initiatives is a shared responsibility between the CIO and CTO. Specifically, just under a third (32%) noted ownership of software development in their organization is a shared responsibility. A full 88% of respondents apply DevOps practices, and 83.4% believe that DevOps is important to digital transformation at their organization. Almost all (98%) plan to expand their DevOps practice, and 83% already have a plan in place to do so.

    Lamas says software engineering-first principles are changing not just how applications are built but also how IT teams are structured in a way that advances innovation.

    More than a third (35%) of respondents said ownership of software operations developed in-house is a shared responsibility in their organization, while 28% said ownership of managing SaaS or operating commercial off-the-shelf (COTS) software in their organization is a shared responsibility. A third (33%) also noted ownership of the technology for the external customer experience in their organization is a shared responsibility.

    A full 95% of survey respondents also confirmed that the performance of their team is measured by key performance indicators (KPIs) related to revenue, specifically revenue growth (75%), rate of innovation (60%) and uptime (54%).

    It’s too early to say how the relationship between CIOs and CTOs will evolve, but the one thing is clear: The pressure for these roles to collaborate more effectively is on the rise.

  • 3 Ways to Prevent Developer Burnout

    3 Ways to Prevent Developer Burnout

    Without developers, software companies wouldn’t exist—and yet, the experience of these experts can be far from ideal. A recent report from Haystack found that nearly 80% of developers report being burned out and the pandemic isn’t even one of the primary factors. Despite similar job requirements, the experience of developers significantly varies across the industry, adding complexity to an already challenging job. Conflicting coding styles, communication styles and requirements from different teams conspire to make the development process inefficient and difficult and leave developers feeling overwhelmed. Between different organizations and even teams within the same organization, the differences in team culture and educational opportunities can lead to radically different job experiences for the same job title. To retain talented developers in the workforce and maximize their potential, the collective developer experience needs to be improved through a developer-first and inclusive culture and better access to professional development for developers at every level.

    Build a Strong Culture of Documentation, Communication and Knowledge Sharing

    One of the biggest challenges team leaders encounter is how to communicate key information between team members. Many developers are incredibly skilled at their trade but aren’t properly trained or given the time to work on sharing that information with either colleagues or end users. Having skilled technical writers means that the team can provide consistent, clear information about the software—and this is crucial for company success. Having technical writers on the team improves communication and efficiency and enables developers to more quickly and easily locate the resources and support that they need to perform their tasks

    The developer’s goal is to innovate and build successful and maintainable systems. Achieving this requires good team processes and a solid system of documentation. Without user-facing documentation, adoption will suffer as users struggle to get things done with the system. Similarly, without documentation of the individual components, knowledge cannot be shared between teams and so the teams working on the application cannot collaborate effectively. A positive culture around documentation and investment in best practices by all contributors, including developers, makes a huge difference in how successful an organization can be.

    Welcome Employees with Comprehensive and Constructive Onboarding

    Strong communication is especially vital during the onboarding process; it’s one of the most important periods for developers early in their careers. Getting developers up to speed in a new team quickly is crucial—and streamlining education beginning during onboarding can make a big difference. Onboarding is a golden opportunity to bring new developers into the cultural fold and enable them to contribute to the team quickly. Doing so also reduces the risk of losing developers from the team.

    Prioritize an Inclusive and Supportive Culture at all Levels

    The experience of software developers is greatly influenced by the culture of the company they work for. The values of a company and the way that departments interact make a big impact on developers—and it’s not always a positive one. Opportunities for career development, promotions, mentorship programs and training are critical for all employees, but especially those in fields with the potential for high turnover or burnout like developers. Providing developers with resources to further their own understanding and mastery of the job—such as access to a budget for attending conferences and further study—is a critical investment for their success. Organizations both large and small must take initiative to ensure developers see a path forward for themselves at their current company and within the industry—or risk losing their talented developers entirely. 

    While developers’ experiences vary across the industry, between departments and even smaller internal teams, there is inherent value in improving communication, investment and culture on a micro and macro scale. To attract and retain highly skilled and innovative developers and ensure success for teams and companies as a whole, executive leadership must work with their developers to find a cohesive system and create an experience that works for everyone. Like any other specialized professional in a complex trade, developers are invaluable to their teams and community; advocating for the improvement of their work experience throughout their careers is the best way for tech companies to keep developers creating software that improves our world.