Category: DevOps in the Cloud

  • AWS Expands Breadth, Depth of DevOps Services Portfolio

    AWS Expands Breadth, Depth of DevOps Services Portfolio

    Amazon Web Services (AWS) today launched a bevy of cloud services, including a preview of Amazon DevOps Guru, that collectively promise to make it much easier to deploy and manage cloud applications.

    Announced during the online AWS re:Invent conference, Amazon DevOps Guru is a fully managed service that employs machine learning algorithms to automatically detecting operational issues and recommend specific responses that will be delivered via a notification. Through a single console, IT teams will also be able to visualize their operational data by summarizing relevant data from multiple AWS and third-party data sources, including PagerDuty and Atlassian.

    AWS also unfurled AWS Proton, a service to automate the development and deployment of microservices-based applications built using containers and the AWS Lambda serverless computing framework. Available also in preview, AWS Proton is an application management service that enables IT teams to define reusable application components as “stacks” that can be combined with a set of curated application stacks for security, architecture and tools defined by AWS. This service then automates the provisioning of infrastructure as code, the setting up of continuous integration/continuous delivery pipelines and the setting of monitoring tools.

    AWS CEO Andy Jassy told conference attendees that in effect, AWS will be managing DevOps processes on behalf of developers.

    At the same time, AWS is launching Amazon Elastic Container Service (Amazon ECS) Anywhere, which allows IT teams to use Amazon ECS to orchestrate containers in their own data centers, and Amazon Elastic Kubernetes Service (Amazon EKS) Anywhere, which provides the ability to run EKS on the distribution of Kubernetes that AWS employs in local data centers. There is also now an Amazon Elastic Container Registry (Amazon ECR) Public service for sharing container images.

    At the same time, AWS previewed Amazon Aurora Serverless v2, which will make it possible to scale instances of MySQL databases instantly using the AWS serverless computing framework. Support for PostgreSQL databases is planned for next year.

    AWS also announced it has added a Microsoft SQL Server-compatibility layer to its PostgreSQL database to make it easier to migrate Windows applications to an open source database. The company will also open-source that capability, dubbed Babblefish, as part of an effort to encourage the development of compatibility layers for other databases. PostgreSQL already provides compatibility with Oracle RDBMS applications.

    Jassy chided providers of these proprietary database platforms for changing licensing terms when organizations deploy these databases on public clouds other than their own. Those moves have only created additional demand to migrate faster to open source databases, noted Jassy.

    Finally, AWS is adding a slew of infrastructure options, including Mac instances (EC2 Mac instances) for Amazon Elastic Compute Cloud (Amazon EC2). Built on Mac mini computers, the service will make it possible for developers to more cost-effectively build MacOS applications.

    In addition, AWS is adding 1U and 2U servers to its AWS Outposts portfolio for deploying infrastructure in on-premises IT environments. Those offerings expand AWS Outposts beyond rack-based systems.

    The company is adding AWS Graviton2-powered C6gn instances to deliver 100Gbps networking performance for Arm processors it designed. Those instances offer 40% better price performance over comparable current-generation x86-based instances, according to the company. There is also now M5zn instances of Intel Xeon Scalable processors that offer 45% better compute performance per core than current M5 instances, according to the company.

    AWS is also adding G4ad Graphics Processing Unit (GPU) instances based on processors from AMD and revealed its intention to build its own GPUs next year. The company also plans to add an Amazon EC2 instance based on up to eight Habana GAUDI accelerators from Intel to deliver up to 40% better price performance than current GPU-based EC2 instances, according to the company.

    Overall, Jassy said AWS grew 26% year over year to achieve a $46 billion run rate. As the number of services provided by the company continues to expand, maintaining that growth rate at a time when applications are moving into the cloud faster than ever looks easily achievable.

  • Mattermost Offers DevOps Command Center in the Cloud

    Mattermost Offers DevOps Command Center in the Cloud

    Mattermost today launched Mattermost Cloud, a software-as-a-service (SaaS) platform for managing DevOps workflows using pre-built playbooks that comes integrated with a wide variety of third-party developer tools.

    Chandar Venkataraman, executive vice president and chief product officer for Mattermost, said Mattermost Cloud enables IT teams to take advantage of a single-tenant DevOps platform that they don’t have to maintain in a way that forces developers to give up their preferred tools.

    In contrast, other DevOps platforms that are managed as a service require developers to make use of a narrow range of tools provided by the platform vendor, he said.

    Built on top of an instance of Kubernetes, the single-tenant capability also ensures that any data or artifacts stored on the platform remain private. The Mattermost Cloud Professional edition, available today, provides a full set of collaboration and DevOps features, while the Mattermost Cloud Enterprise edition, currently in beta, adds dedicated single-tenant cloud infrastructure, enterprise-grade secure network topology and strict data residency options.

    By building the platform on Kubernetes, he noted, it becomes much easier to scale the Mattermost Cloud platform up and down as required.

    Mattermost Cloud is essentially a DevOps command center that provides single pane-of-glass pre-built workflows that address most common DevOps processes. IT teams can add their own custom workflows as their DevOps processes mature, Venkataraman said, noting plugins for Jira, Opsgenie, PagerDuty, GitLab, GitHub and Jenkins are already available.

    The cloud platform also includes a pre-built best-practices incident management playbook to enable DevOps teams to address issues as they arise rather than trying to resolve them using a legacy ticket-based approach to IT service management (ITSM), he added.

    Venkataraman noted Mattermost doesn’t expect DevOps processes to supplant existing ITSM platforms based on ITIL-frameworks. However, many DevOps teams are looking for ways to resolve incidents within their existing workflows using, for example, a messaging platform versus a workflow designed for IT support staff.

    In general, Venkataraman said, many organizations that are relatively new to DevOps don’t want to manage the underlying platform. At the same time, he noted there are also many IT organizations that want to allocate more resources to writing code versus managing a DevOps platform.

    Each IT organization will need to decide when it makes sense to stand up their own platform for managing DevOps workflows and playbooks instead of building and maintaining their own control plane. Many of those IT teams are already making use of artifact repositories and continuous integration/continuous delivery (CI/CD) platforms that are accessed via the cloud, so a DevOps command center is only one more logical extension.

    Just as importantly, isolating the DevOps command center from the rest of the underlying DevOps platforms ultimately makes it easier for IT teams to switch out tools and platforms over time as they best see fit. The challenge now may be in finding a way to decouple workflows that are deeply intertwined with a specific platform.

  • ZeroNorth Adds Security Defect Density Dashboard

    ZeroNorth Adds Security Defect Density Dashboard

    ZeroNorth today announced it has added a Defect Density Dashboard to its software-as-a-service (SaaS) platform for managing and orchestrating application security scans.

    Company CEO John Worrall said Defect Density Dashboard borrows a concept employed to measure software quality and applies it specifically to application security. The dashboard surfaces the number of application security defects per thousand lines of code discovered during scans of code made using software composition analysis (SCA) and software application security testing (SAST) tools.

    That metric will create a key performance indicator that application security champions within DevOps teams and chief information security officers (CISO) can use to quantitatively measure the progress being made toward improving overall application security, he said.

    As organizations begin to adopt best DevSecOps practices Worral said one of the challenges IT leaders face is showing the board of directors that the level of investment being made is delivering measurable results. The Defect Density metric applies a concept that is already widely employed by quality assurance teams in manufacturing and other vertical industries to software development, he noted.

    As a provider of a SaaS platform for orchestrating security scans across multiple third-party tools, Worral said ZeroNorth is in the unique position of being able to normalize all the data generated by the tools.

    The Defect Density Dashboard also makes it easier to identify specific areas of weakness such as larger numbers of SQL injection vulnerabilities that would indicate a need to make additional training available to software development teams, he added, noting that approach allows the application security advocate to be viewed as an ally versus someone who merely criticizes the efforts of a software development team.

    Encouraging developers to scan their code before they make a commit is, of course, at the heart of any effort to shift more responsibility for application security to the left. ZeroNorth has been making a case for a platform that makes it easier to implement multiple scans across a DevOps workflow using different tools. That approach makes it more likely that a vulnerability that isn’t discovered by one tool is uncovered by another.

    The challenge, of course, is making sure developers scan their code often. There is a natural tendency to delay a scan in the name of productivity. However, the larger the base of code that needs to be scanned, the longer it takes to complete those scans. Most developers would be well-advised to scan smaller amounts of code more often.

    Regardless of the approach to scanning, developers should expect to be evaluated based on the number of vulnerabilities that are inadvertently introduced into their code. Cybersecurity teams can no longer keep pace with the rate at which application code is being deployed and updated. As such, many organizations have launched a concerted effort to eliminate as many vulnerabilities as possible before code gets deployed in a production environment. It may never be possible to eliminate 100% of vulnerabilities, but at the very least the most common exploits that cybercriminals actively scan for when looking to compromise an application can be greatly reduced.

  • Achieve Cloud Resilience Through Systematic (and Chaotic) Testing

    Achieve Cloud Resilience Through Systematic (and Chaotic) Testing

    Constantly testing the cloud in systematic and chaotic ways will help companies avoid cloud failures in a time when downtime means disconnect

    Professionals fortunate enough to shelter in place and work from home can thank cloud for their ability to shift over so seamlessly during the COVID-19 pandemic.

    Imagine a lockdown without the cloud. Availability and uptime of grocery order systems would depend on a company’s on-prem data centers. Streaming services would stutter and stall during peak hours (after dinnertime and other high-demand times. Critical personal and professional interactions would be limited to voice calls instead of rich collaboration apps, video conferencing or dynamic social media. Many companies would simply just be closed to business, unable to respond to market changes and consumers.

    Now imagine a COVID-19-induced work-from-home scenario with downtime in the cloud. Teams working remotely would fall apart. Deliveries would be scrambled and lost. More importantly, emergency services would see bigger surges with fewer tools to manage them. Medical research teams around the globe currently sharing coronavirus research and data would lose contact with each other, delaying and slowing efforts to treat and cure the COVID-19 virus.

    It may seem that the cloud was built just in time to help with our current predicament. But the concept and foundational systems of cloud computing go back more than 50 years. Popular, practical cloud applications developed more rapidly in the past 20 years, starting with the early iterations of Salesforce.com and more recently with web-based enterprise applications such as Google’s G Suite and Microsoft’s Office 365. It’s the simplicity of these relatively newer tools that have led to their broad adoption. But this surface layer masks a mind-bogglingly complex undergirding that must be fully understood and tested to be maintained.

    Clouds are strained right now. IBM endured a cloud outage of roughly two hours on June 9. Network monitoring company ThousandEyes told tech news site Fierce Telecom that the global nature of the outage suggested a control-plane issue rather than a physical failure such as a fiber cut or router failure. Microsoft’s Azure Cloud Data Center capacity in Europe has shown signs of stress as companies shift to remote work and usage of its communication and collaboration platforms, including Teams balloons. To relieve that stress, Microsoft restricted access to free and trial accounts. Google Cloud’s Kubernetes platform and networking services on parts of the U.S. East Coast went dark for a few hours on June 29.

    To avoid downtime due to cloud failure, companies must build resilience into their cloud structure by testing it in continuous and chaotic ways.

    Conventional testing fundamentally ensures that key applications have been migrated or set up in the cloud and are working properly. This is a great and proven way to ensure that cloud systems meet design considerations and do not change based on application performance. However, conventional testing does not probe for unexpected situations. To do that, advanced operations turn to chaos testing, a technique pioneered by Netflix during its own migration to the cloud starting in 2011. Chaos testing creates turbulent situations that will bring points of failure to light and influence design. Modern cloud systems bring hardware and software together in such complex and fluid ways that standard testing will never suffice. By engaging in systematic and chaotic testing, companies can develop greater resilience in the cloud and through their entire technology systems.

    To achieve resilience, IT must find vulnerabilities not revealed in normal “happy path” testing scenarios. Seeking resilience provides a glimpse into a systems’ reliability and recoverability by executing a carefully planned set of disasters. Such a disaster sequence could include:

    1. Pulling down the network connection for 10 seconds.
    2. Taking a service or server offline.
    3. Choking middleware and watching for anomalies.

    Enterprises just embarking on their migration to cloud must first study and choose a service model that fits best. Firms looking to migrate a whole workload to the cloud should choose the infrastructure-as-a-service (IaaS) option, which allow teams to rapidly orchestrate their test environments on the cloud and quickly set up systems for storage, backup and recovery.

    Organizations already in the cloud or partly migrated must take time to understand their cloud service models. This could prompt the question: Is this model right for my organization in the years ahead?

    While operating in the cloud, these companies can start planning testing scenarios to gauge their systems’ resiliency. In doing so, companies should set an objective and time window for running the tests. Then, the results of these tests help inform the requirement design phase of their cloud setup.

    With all systems and applications in a virtual cloud context, future digital transformations will become more fluid. Properly tested clouds also handle demand spikes more readily and will handle the viral adoption of an application or a rapid location switch or expansion of workforces.

    To become resilient, companies must create resilient IT systems. These systems will rely partly or wholly on cloud infrastructure. Cloud infrastructure grows more resilient through constant, systematic, and chaotic testing. Consistent, creative testing has its own value that allows businesses themselves to become more flexible and resilient enterprises.

  • New AWS Services Optimize App Development Process

    New AWS Services Optimize App Development Process

    Amazon Web Services (AWS) is always busy introducing new services, enhancing existing ones and, quite often, driving trends. However, the cloud services provider has upped its game even more in recent months.

    In the first half of 2020, AWS announced an astonishing number of developments that enable technology interoperability, simplifying legacy feature removal, creating greater flexibility and time-savings for developers and putting new capabilities at users’ fingertips.

    AWS and ARM Power

    You are going to be hearing a lot about ARM processor architecture and not just because the chipmaker is being acquired by Nvidia, the leading maker of GPUs.

    Developed in the 1980s, ARM processors are finally hitting their stride as companies are embracing ARM-based chips. ARM-based processors combine high-performance RISC designs, lower manufacturing costs and reduced power consumption, making them ideal for portable devices such as smartphones, tablets and even laptops. More and more companies are designing processors that implement ARM architecture, including Apple, AppliedMicro, Broadcom, Qualcomm and Samsung Electronics. This year, Apple brought ARM chips into the desktop world with tailored extensions such as a built-in security enclave, a motion co-processor and a neural engine.

    AWS is among those embracing ARM architecture, which has led to introducing an array of robust services that will benefit developers and end users alike. Case in point: This summer, AWS announced the general availability of its sixth generation of Amazon Elastic Compute Cloud (Amazon EC2) instances, including general-purpose (M6g), compute-optimized (C6g) and memory-optimized (R6g) instances. Powered by AWS-designed, ARM-based Graviton2 processors, they deliver up to 40% better price/performance over comparable current-generation x86-based instances.

    They also offer 50% more NVMe SSD storage GB/vCPU over comparable x86-based instances. The local SSD storage works well for apps that require high-speed, low latency storage, as well as for temporary storage of data such as batch and log processing, and high-speed caches and scratch files.

    They’re ideal for workloads ranging from application servers, microservices and high-performance computing to CPU-based machine learning inference, electronic design automation and gaming. Numerous organizations have already successfully adopted ARM-powered instances and are realizing price/performance benefits.

    The AWS Graviton-based instances are supported by a broad ecosystem of operating systems and services from independent software vendors (ISVs) as well as AWS. They can be purchased as on-demand, reserved, or spot instances; covered by savings plans or as dedicated hosts/instances, and support up to 19 Gbps Elastic Block Store (EBS) bandwidth.

    The AWS Graviton2 processor itself, released in late 2019, deserves recognition, too. Compared to first-generation ARM-powered Graviton processors, they provide twice as fast floating-point performance per core for scientific and high-performance computing workloads. They also offer optimized instructions for faster machine learning inference, always-on fully encrypted DDR4 memory and 50% faster per core encryption performance to further enhance security.

    A number of AWS services, such as Amazon Elastic Load Balancing, Amazon ElastiCache and Amazon Elastic Map Reduce, have realized superior price/performance in testing and will be moving into production on Graviton2-based instances.

    Better, Easier Artifact Management

    AWS isn’t the only organization opting for ARM. As many others prepare to make a move, AWS is doing its part to facilitate the transition. That includes deploying services that streamline various aspects of the app development process, in keeping with the efficiencies and increased performance offered by ARM-based chips.

    One that we’re most excited about is AWS CodeArtifact. This fully managed software artifact repository service eliminates the need for setting up, operating and scaling the infrastructure required for artifact management. It works with commonly used package managers and tools such as Maven and Gradle (Java), npm/yarn (JavaScript) and pip/twine (Python), so it can easily be integrated into existing development workflows.

    AWS CodeArtifact can be used for creating centralized repositories for sharing software packages approved for use across development teams. Its integration with AWS Identity and Access Management (IAM) enables access control. Its support for AWS CloudTrail provides visibility into which packages are in use and where they can easily be updated or removed.

    AWS Making Containerization Easier

    Using containers to modernize existing apps make them portable, increases development agility and reduces operational costs. The problem is that the process requires numerous manual tasks that are time-consuming and error-prone, and slow down modernization efforts.

    That’s why we think another recently deployed AWS service will have a positive impact on the app development process. AWS App2Container is a command-line tool that helps containerize existing apps running on-premises, in Amazon EC2 or in other clouds with no code changes required.

    App2Container discovers apps running on a server, identifies their dependencies and generates relevant artifacts for seamless deployment to Amazon ECS and Amazon EKS. It also provides integration with AWS CodeBuild and AWS CodeDeploy for a repeatable way to build and deploy containerized applications.

    AWS App2Container generates artifacts such as Dockerfiles, container images in Amazon Elastic Container Registry (ECR), ECS Task definitions, Kubernetes deployment YAML, templates to set up a build/release pipeline in AWS CodePipeline and more.

    It can also be used to containerize ASP.NET (.NET 3.5+) web apps running in IIS 7.5+ on Windows and Java apps running on Linux.

    Code Review and Optimization

    Another handy tool that debuted this summer is Amazon CodeGuru. Powered by machine learning, this set of tools automatically reviews code for bugs and suggests potential optimizations. It includes two components:

    • Amazon CodeGuru Profiler—Helps developers find an app’s most expensive lines of code and then recommends how to improve the code to save money.
    • Amazon CodeGuru Reviewer—Helps improve code quality by using machine learning to identify critical issues and hard-to-find bugs during development.

    Do-It-Yourself Development

    One more recently released AWS service we want to mention is Amazon Honeycode. This one has the potential to be a big time-saver for customers. The fully managed, low-code/no-code development tool makes it easy to build powerful mobile and web apps quickly with no programming required.

    Customers can use a simple visual app builder to create highly interactive web and mobile apps, backed by an AWS-built database to perform tasks such as tracking data over time and notifying users of changes. They can get started creating apps in minutes and build applications for up to 20 users for free. After that, they pay per user and for the consumed storage capacity.

    What’s Next With AWS Is What’s Now

    AWS is continually developing and deploying services that make app development easier and more cost-efficient. You can put these new services to work to innovate more, get to market quicker, generate significant cost savings and much more.

  • Red Hat Automates More Operating System Tasks

    Red Hat Automates More Operating System Tasks

    Red Hat today announced an update to Red Hat Enterprise Linux (RHEL) that automates a wide range of manual tasks.

    Scott McBrien, a principal product manager for Red Hat, said RHEL 8.3, available in a few weeks, expands the Red Hat System Roles capability that provides a prescriptive and automated means of managing operating system configurations. Red Hat System Role now addresses kernel and log settings, identity management, certificate management and Network-Bound Disk Encryption (NBDE), as well as deployments of SAP HANA databases and SAP NetWeaver middleware. Red Hat has also updated Tuned, a set of pre-configured performance profiles it makes available.

    In addition, RHEL 8.3 provides an update to Application Streams, a set of developer frameworks, databases, container tools and other resources that now adds support for Node.js 14, Ruby 2.7 and other current versions of tools and languages. Red Hat is now committed to streaming support for updates to the frameworks include in Application Streams versus only making updates available each time the entire platform is updated, said McBrien. That approach is intended to make it possible for developers to embrace new capabilities faster while maintaining support for previous versions of frameworks, said McBrien.

    Red Hat is also furthering its effort to encourage organizations that have standardized on RHEL to embrace its tools for building and managing container applications. Updated container images for Buildah, a tool for building container images and Skopeo, a tool for moving container images across storage platform, have been added along with version 2.0 of Podman, a tool for managing containers and images that adds a REST application programming interface (API) that is compatible with Docker Container Engine.

    Red Hat is making the cases for a more modular approach to deploying tools for building and maintaining containers as an alternative to a more monolithic approach pursued by Docker Inc., said McBrien.

    Finally, Red Hat has added Secure Content Automation Protocol (SCAP) profiles for the Center for Internet Security (CIS) Benchmark and the Health Insurance Portability and Accountability Act (HIPAA).

    RHEL and the Red Hat OpenShift application development and deployment platform are at the core of the hybrid cloud computing strategy being advanced by Red Hat and its parent company, IBM. According to a Red Hat Enterprise Open Source Report, 63% of organizations surveyed have a hybrid cloud architecture today, with more than half of those who do not have one in place planning to implement one in the next two years.

    Beyond bundling developer tools with RHEL to reduce the number of IT vendors, an organization needs to engage, McBrien said Red Hat is committed to automating as many low-level IT tasks as possible. IT teams should be able to deploy operating systems in the cloud just as easily as they might in an on-premises IT environment, he noted.

    It may be a little while yet before every manual IT task becomes automated, but with each new update to the operating system the number of those rote tasks that IT administrators need to devote time to continues to diminish.

  • Application Modernization Video with IBM’s Rosalind Radcliffe

    Application Modernization Video with IBM’s Rosalind Radcliffe

    Application modernization is the process of updating existing legacy applications and modernizing their infrastructure, architecture and features, by using modern technology stacks. Monolithic applications are difficult to update and expensive to scale.

    In response to today’s business requirements of growth and innovation, enterprises must deliver new applications in an agile fashion while minimizing risk. Many have turned to a hybrid or multicloud strategy where choice and flexibility are foundational.

    In this interview, Rosalind Radcliffe, distinguished engineer at IBM, explains the benefits of modernizing applications and how IBM provides all essential components to update your legacy applications.

    Rosalind will take a deeper look at application modernization during her session at IBM DevOps Virtual Summit. During the virtual event, attendees will learn how to keep their applications running smoothly with automation and data-driven solutions that can reduce mean time to resolution and explore IBM solutions to help innovate hybrid environments, disrupt cloud native development and transform existing mainframe infrastructures. The free virtual event will take place on Oct. 29 at 10 a.m. ET.

    For more information and to register, please visit the IBM DevOps Virtual Summit website.

  • From ‘Cloud Zombies’ to Multi-Cloud Experts

    From ‘Cloud Zombies’ to Multi-Cloud Experts

    A significant risk associated with cloud migration is overspending. For years, zombie-like obedience to AWS has resulted in price lock and escalating fees at many organizations – this is a tale for fighting the cloud zombies.

    Cloud costs around data egress or application bandwidth are often not transparent and thus highly unpredictable. Complicating this problem is the need to rapidly develop and scale large application ecosystems, leading to snap judgments by project engineers to buy tools. Or, cloud purchasing decisions fall to the CFO, who may not be qualified to understand technical nuances. Without cloud spending forethought, it’s easy to enter unsavory pricing commitments.

    However, all of this is changing. As cloud service providers (CSPs) mature their offerings, competitors have risen to take on AWS, unlocking more consumer choice throughout the cloud landscape. In a multi-cloud world, cloud economists are leveraging lift and shift capabilities to optimize performances. Ironically, companies are also seeing cost benefits in retaining some on-premises servers.

    I recently spoke with Scott Leatherman, chief transformation officer at Virtana, to get his take on preventing cloud cost escalation and how IT should streamline multi-cloud environments to stem the cloud budget.

    Zombies in the Cloud

    When the cloud arrived, it promised high performance at a low cost. Companies were happy to offload on-premises servers for the ease of cloud arrangements. For years, there was a “zombie-like loyalty” to cloud platforms, said Leatherman.

    Not much was thought about costs rising in parallel with the astronomical growth of the web, mobile and IoT. Executives penned long-term pricing contracts without a second thought. Then eventually, reality hit. And it came with a hefty price tag.

    Spooky Cloud Expenses

    As cloud-enabled businesses took off, they encountered many hidden fees. To name a few:

    • Egress: Fees for moving data in and out of the cloud.
    • Application: Fees for moving applications to new instances.
    • Workloads: Mounting costs for increasing bandwidth and workloads.

    These and other add-ons could quickly raise a cloud bill from $200 to $200,0000 a month. Complicating this was the fact that many large organizations purchased multi-year cloud subscriptions locked at a specific price.

    Counterintuitively, such cost-savings guarantees are “completely backward,” Leatherman said. As computing power increases exponentially per Moore’s Law, servers become cheaper to maintain.

    “You’ve literally committed yourself to something that is depreciating in cost,” he said. Yet, those savings don’t trickle down to consumers and SLAs have remained pretty flat. “What’s the most frustrating thing for me is that the best way to run this business is to lock people in.”

    The Zombies Become Aware

    In the wake of COVID-spurred digital transformation, cloud zombies are waking up to slash the budget, finding cost-effectiveness in multi-cloud strategies. Some companies are even reaffirming ties with on-premises servers.

    If performance isn’t worth the cost, it defeats the benefits of moving to the cloud entirely. So, how can we smartly optimize our environments for quality performance with leaner financial margins? Leatherman shared some steps to become cloud-smart:

    1. Baseline Your Footprint

    The first step toward reducing cloud costs is maintaining a baseline of all cloud dependencies and private data centers. This should cover a deep cost and performance analysis.

    “You need a baseline in your data center—what can I move? what should I move?” said Leatherman. Unless you have a baseline of what your data center is doing (both private and public), you can never understand what resources should move to the cloud. Powerful apps for monitoring the public cloud could help audit architecture.

    2. Optimize, Optimize, Optimize

    Only after mapping topologies can you can begin to optimize performance. Since usage differs depending on the season, cloud optimization should respond to yearlong application usage trends. For example, ERP software may pull significantly more requests at the end of the quarter and e-commerce spikes during the holidays.

    Organizations should ensure the elastic cloud truly scales to application needs, but only when needed. Ensure systems of orchestration and routing function properly, and diligently search for hidden fees. “The cost that sneaks up on you in the elastic cloud always comes up,” said Leatherman.

    Heavy computation processes, such as machine learning over big data, will require enormous server consumption. For resource-intensive scenarios, Leatherman recommended keeping code lean. Whereas CPU relies on the laws of physics, “application developers are only limited by creativity,” he said.

    Application developers should whenever possible optimize code to avoid redundancies. Doing so yields a positive environmental impact, too—eliminating operational inefficiencies can decrease cloud server usage, which reduces carbon footprint.

    3. Lift and Shift

    GCP, Azure, Oracle and other CSPs mature, the zombie-like loyalty to AWS is fading. “Now that there is parity across cloud vendors, things are changing,” he noted. “The flexibility in the marketplace is really dynamic.”

    In a multi-cloud world, organizations can leverage a hybrid cloud and “lift and shift” toward the best cost optimizations for their specific needs. This is where maintaining a strong baseline will help continually test cost efficiencies among cloud competitors.

    4. Refine Your Tool Procurement Process

    Another solution involves scrutinizing your cloud procurement process and the personnel involved. As mentioned above, new cloud tooling purchasing may occur at the DevOps level or large contracts may be escalated to the CFO office.

    Unfortunately, neither side is in an ideal situation to make smart financial decisions—one faces an urgency to deliver and the other can’t see the trees from the forest (and especially not the termites eating the valuable wood). Many believe a new role is required—The Other CFO—to help optimize the cloud stack.

    5. Retain and Optimize Private Data Centers

    By now, most enterprises are accustomed to having both a data center and a cloud center team. Leatherman argued that ultimately these two teams must work together to avoid outages and reduce the exponential costs of moving to the cloud.

    From a security perspective, there are still significant advantages to maintaining on-premises private clouds and data centers. By leveraging private assets, you aid data protection efforts and have increased control. “Datacenters have value,” he said. “Unless you started there, no one will be 100% cloud.”

    Although cloud migration seems inevitable, through software automation and Moore’s law there is value in on-premises. As a result, Leatherman predicts a rise in private cloud data center optimization and management services by third parties.

    6. AI for Cloud Cost Awareness: DevFinOps

    Finally, AI soon may be available to automatically scan for cloud cost impacts before applications are even deployed.

    Most DevOps teams use container security scanning or automated compliance validation as part of their DevSecOps process. Leatherman suggests future DevOps tooling will similarly evolve to display automated notices that estimate cloud costs for your actions in real-time.

    For example, as engineers are pushing code, a popup could display server utilizations and a cost impact breakdown. Or, inline code validation suggestions could find redundancy to decrease waste. Perhaps we’ll need a new abbreviation for this Developer + Finance + Operation focus—DevFinOps, anyone?

    Such an AI would likely not negate the need for a cloud economist to help manage multi-cloud complexity. “We’ll still need them,” said Leatherman.

    Surprises in a Multi-Cloud World

    COVID–19 is accelerating deployments tagged for much shorter timeframes, forcing many more instances to public clouds. Businesses need to get performance up and meet their SLAs. To reduce expenditures, they must quickly lift and shift to the most performant and cost-efficient environments.

    The gravity is apparent, yet hasty moves now could be disastrous for security and data privacy in the future. Besides rising cloud costs, there are other risks associated with the cloud that increase exponentially with multi-cloud environments. “It’s not just the financial spend, but the security and risk that goes along with it,” Leatherman said. “It becomes really scary how many people have access.”

    Not only must cloud spending decisions shift left, but security must arise earlier in the development cycle as well. Compliance with regulations such as GDPR or HIPPA should also influence how teams manage data between clouds.

    The Cloud is Relatively New

    An IBM-endorsed study found enterprises are only 20% of the way through their cloud journey. Many enterprises are still just at the beginning of their cloud transformations, and 90% plan to expand their cloud footprint in the next year.

    The cloud journey is quite long, and many have quite a way to go. Knowing this, cloud economics will only rise in importance. As I recently covered, cloud expertise is now superior to a university degree.

    Current forces, like the COVID–19 crisis, will no doubt continue to “drive people to the cloud,” said Leatherman. While responding to the imperative to deliver more and higher speeds, it’s essential to be smart, leverage existing assets, and optimize cloud usage at every level possible. “It shouldn’t just be cloud-first,” he said. “It should be cloud-smart.”

  • DevOps’ Data Storage Problem

    DevOps’ Data Storage Problem

    The technology sector has always been about problem-solving. When the value of big data was finally embraced, thanks to new analysis capabilities developed in the late nineties and early aughts, the industry adapted its mindset toward storage by investing in on-premises data centers to help store the data that would drive better business decisions. When this rise of data accelerated software development and deployment, creating organizational silos between developers and operations, the industry responded by creating DevOps to improve collaboration.

    Now DevOps has revolutionized the way companies do work by eliminating silos, increasing agility and creating greater visibility, resulting in faster deployments and better service overall. These new work styles have only increased the amount of data produced and the necessity to access it anytime, anywhere has made migrating to the cloud the only real viable solution to any successful DevOps team. Unfortunately, this has spawned a new challenge for the technology industry to solve: the cloud.

    Data and the Cloud Predicament

    Early DevOps adopters quickly leveraged the benefits of the cloud in increasing collaboration brought on by improved data accessibility. However, these early adopters typically entered agreements with the big three cloud vendors that offered increased storage capacity and a seemingly more flexible and accessible format. In most cases, these agreements provide instant gratification, but as DevOps expands over time new pain points are discovered as service and egress fees pile up and teams are forced to either increase budgets to accommodate storage needs or risk meeting limits and data loss.

    This situation created a cloud storage predicament: Companies either pay for more cloud storage than they’ll ever need or have to choose what data was kept and what was deleted. These unsustainable vendor agreements introduce financial pain points for scaling up or scaling down storage space, outweighing the benefits of keeping all of the valuable data being produced and collected day-to-day. As a result, most are stuck thinking about how much and what to store instead of using all of its data to drive the business forward.

    This form of vendor lock-in is a detriment to DevOps teams that rely on seemingly endless amounts of data to experiment, conduct maintenance and develop and deploy new applications.

    Accelerating DevOps With a Bottomless Mindset

    An IDC report recently indicated that the amount of data stored is now expected to hit 59 zettabytes this year alone, with the next three years of creation and consumption almost eclipsing that of the previous 30 years combined. And while DevOps has certainly contributed to this spike, the reality of our digital worlds is that data is king, and a company’s ability to seamlessly store, access and leverage it is what will set it apart from the competition.

    The problem with this growth is finding ways to sustainably store this data in the cloud, particularly when teams are handcuffed to existing storage agreements that are draining budgets. This starts with DevOps teams rethinking their approach. Instead of thinking of cloud storage and accessibility as a recurring cycle of bills and service limit notifications, cloud strategies need to focus on the ability to only pay for the space needed at any given time without the worry of additional fees for accessing archived data. Need to scale up storage capacity? Great! Add as much as you’d like. Need to scale down for a particular reason? Don’t stress over unused real estate just sitting in your vendor’s data center. Need to access archived data at a moment’s notice? Don’t hesitate out of fear of a knee-buckling egress fee.

    With this shift, DevOps teams can move away from conserving, archiving and destroying data toward gathering and utilizing all of it to drive the data-driven insights required in today’s digital economy. This change in mindset toward a “bottomless” cloud removes constraints and enables the ability to innovate at a faster and more sustainable rate.

    Unlocking DevOps Innovation

    Too often people think of DevOps and data management as being separate entities, but as software and application development evolves to include capabilities such as predictive analytics, it’s clear that a marriage between the two entities is needed. By rethinking its data strategy and embracing a bottomless approach, DevOps teams can unlock even greater efficiencies, leading to the next revolution in technology innovation.

  • Winning DevOps in the Finance Industry

    Winning DevOps in the Finance Industry

    DevOps is making its impact on almost every software-powered company these days. Companies in the finance domain, however, have been perhaps the slowest to embrace DevOps because of concerns regarding governance, security, compliance and regulatory regulations. But it is safe to say that they are currently leading the digital innovation in this era of cloud-native technology.

    Why DevOps for the Finance Industry?

    Higher customer engagement and continuous transactions make the finance industry one of the busiest and naturally requires uninterrupted infrastructure. DevOps implementation helps companies develop fast, fail fast and learn fast so they can fulfill customer expectations and deliver features faster to market than their competitors. Technology in the finance sector has not evolved much, as many companies have assumed it is too risky to embrace DevOps because of the amount of legacy code and old methodologies still in practice. As a result, digital innovation has lagged.

    Challenges of Implementing DevOps in Finance

    Unlike other industries, regulated industries imply several challenges:

    • Strong restrictions on secured networks.
    • Fine-grained audit trails.
    • Strong ACLs models.
    • Full lifecycle governance.
    • Integration with third parties.

    Security and compliance are top concerns in financial companies, and DevOps practices are, in fact, viewed as risk factors to security. Plus, the increased frequency of software releases in DevOps is seen as a threat to governance and regulatory controls.

    Is the Needle Moving Toward DevOps?

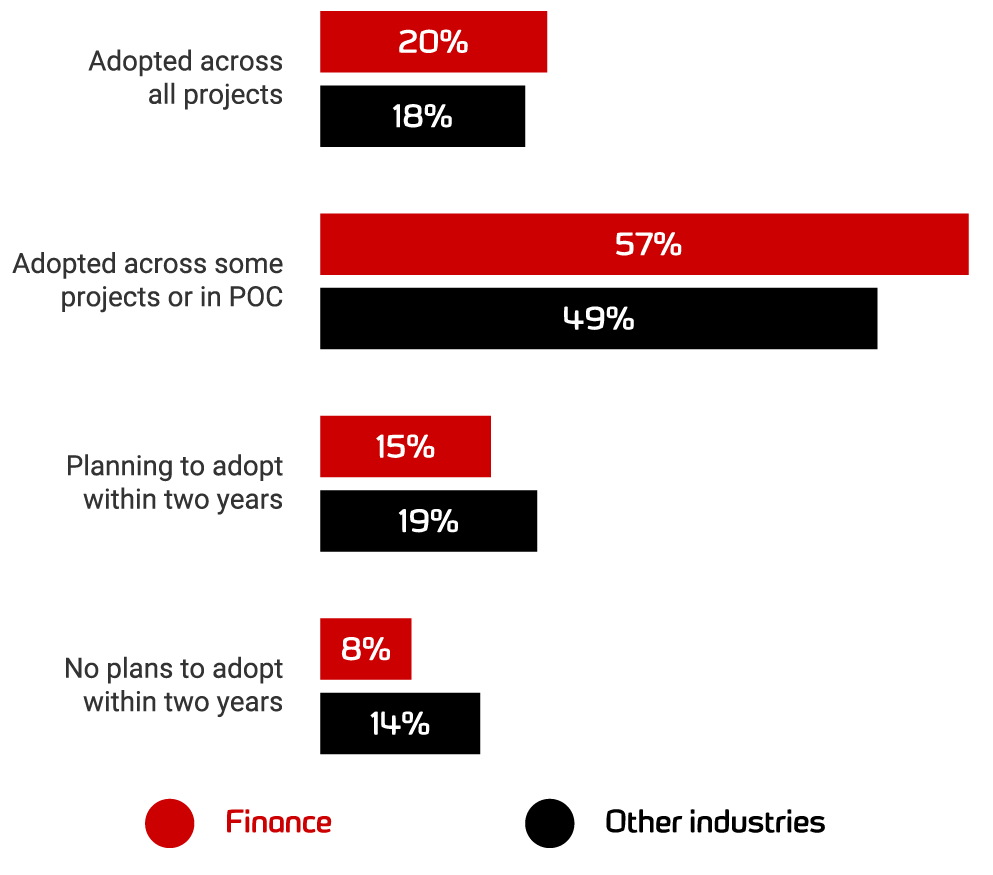
    According to the “2020 State of Database DevOps report“ by Redgate, financial services organizations report the highest levels of database DevOps adoption this year, with proportionally higher rates than any other sector. That shows financial sector maturity in terms of digital innovation. 

    Image source credit: Redgate

    Case Studies of Financial Companies and Their DevOps Journey

    Barclays DevOps Adoption

    In 2015, Barclays announced it was adopting DevOps for its digital transformation journey. Barclays processes payments that equate to around 30% of the UK’s gross domestic product. The developers’ morale and quality of code increased because of DevOps and the leadership team at Barclays credited DevOps with significantly reducing the complexity of its codes, which has allowed the company to reduce delivery risk and ultimately, improve the quality of services.

    DevOps the Lunar Way

    Lunar Way’s journey shows you don’t have to be big to use Kubernetes. The company started its cloud-native DevOps journey by splitting its massive monolith application into smaller microservices. To spin up these microservices, Lunar Way used Ansible, Terraform and Jenkins and to deploy these microservices as a whole unit. 

    Then Lunar Way started to experience scaling issues with microservices and didn’t experience any of the microservices benefits. 

    The company started looking for ways to move past this complexity by shifting its focus from machine-oriented to application-oriented architecture. It chose Kubernetes as the abstraction layer along with AWS, not worrying about where the containers are running, and this is how it was able to manage and unlock the velocity of microservices. Lunar Way also chose Kubernetes from a security perspective and to specify how the applications should run. Now the company runs around 80+ microservices in production with the help of Kubernetes. Watch and learn how Lunar Way did it: “Two years in production with Kubernetes.”

    Italy’s Biggest Bank Embraces DevOps

    A conventional bank running its real business on such a young technology? No way, are you kidding me? Nope, I am not kidding. 

    Italy’s banking group, Intesa Sanpaolo, has made this transition. Banks still run their ATM networks on 30-year-old mainframe technology, so embracing the hottest trend and tech is nearly unbelievable. 

    Even though ING, the banking and financial corporation, changed the way the banks were seen by upgrading itself with Kubernetes and DevOps practices very early in the game, there was still a stigma attached to adopting Kubernetes in highly regulated and controlled environments including health care and financial services. The bank’s engineering team came up with an initiative strategy in 2018 to throw away the old way of thinking and started embracing microservices, container architecture and migration from monolithic to multi-tier applications. Today, the bank runs more than 3,000 applications. Of those, more than 120 are now running in production using the new microservices architecture, including two of the 10 most business-critical for the bank. 

    HSBC Going the DevOps Way

    HSBC is changing the way typical banking works with cloud-native technology and DevOps, as an early user of Google’s Cloud Services Platform to provide core banking services to its business customers. 

    HSBC plans to build its all-new business banking service to run on a Kubernetes-managed container infrastructure using Google’s toolset. HSBC also has excellent partnerships with AWS and Microsoft, favoring the multi-cloud strategy. The company’s engineering team believes that moving to a container model under the umbrella of Kubernetes is significant because it means the environment is similar across different clouds. HSBC also hired people from outside of the banking sector because it wanted to change its culture from within. HSBC is said to have invested $10 million so far in its DevOps initiative.

    Capital One’s Agile to DevOps Journey

    Capital One’s Agile journey started in late 2011, with just two teams, which expanded slowly as more teams were trained in Agile development. The developers at Capital One were following the Scaled Agile Framework (SAFe). Initially, since the teams were new to the automation methodologies, integration testing, security testing, unit and performance testing were all done outside of development sprints by separate test teams. Later, once they understood how important it is to have a collaborative culture, they integrated testing into the dedicated DevOps teams and automated it well. Then slowly, they moved all testing into development sprints, adopting a culture of DevOps and uniformity and wiring integration, security and performance testing into a continuous delivery pipeline. As of 2016, the company had more than 700 Agile teams following continuous delivery.

    DevOps at Bank of America

    Bank of America is one of the world’s biggest financial institutions following DevOps practices, and its digital enterprise operations support nearly 4,300 retail financial centers and approximately 16,600 ATMs worldwide. The award-winning digital bank has nearly 38 million active users and approximately 29 million mobile users.

    Automating Security and Compliance

    As DevOps continues to evolve and become mainstream, it will continue to be of interest for many senior managers across financial services. The above case studies show they are already making DevOps a priority. But security and compliance remain barriers slowing the innovation in the financial companies. 

    Organizations should start small and keep security high priority, first using continuous integration and then adding continuous delivery and deployment using the available tools in the market. Over time, the more a company automates, the higher return on investment it can achieve.

    Automating security permissions and controls will help financial companies remove some of their most common software barriers and get their releases out quicker than before, while still maintaining the necessary governance and compliance. 

    Take a Step Forward

    Financial services companies need complex and rigorous software development processes to meet intense corporate and regulatory requirements. Yet, they are expected to release software faster than ever to meet expectations and beat the competition. By starting small and keeping security and compliance in mind, DevOps in finance can be achieved with great success.