Tag: Sysdig

  • Sysdig Launches Wireshark Foundation

    Sysdig Launches Wireshark Foundation

    Sysdig this week announced there is now a Wireshark Foundation that will oversee future development of the widely used open source traffic protocol analyzer.

    Gerald Combs, who is now director of open source projects at Sysdig, along with Loris Degioanni, CTO of Sysdig, launched Wireshark in 2006 to enable teams to monitor network traffic, learn protocols and packet basics and troubleshoot network problems. There are more than 2,000 contributors and Wireshark has been downloaded more than 60 million times in the last five years alone.

    The Wireshark Foundation will provide a framework for long-term stewardship and sustainability. The foundation will be led by Sheri Najafi as executive director, and Janice Spampinato, Hansang Bae, Najafi, Combs and Degioanni will serve on the board.
    Combs said rather than donating Wireshark to an existing foundation, it was decided to set one up to formalize many of the community processes that have evolved over the past two decades.

    Degioanni said the foundation will also ensure Wireshark remains relevant long after its creators eventually retire. Wireshark has a graphical user interface (GUI) that provides IT teams with an easy-to-understand traffic protocol analyzer. However, as applications become more distributed, additional types of IT professionals, including DevOps teams, are analyzing network traffic. Similarly, cybersecurity teams are using these tools to help track down the source of anomalous activity.

    It’s not clear whether network operations (NetOps) and DevOps workflows are merging, but the level of collaboration has increased. As networking increasingly becomes software-defined, it’s clear that developers will employ application programming interfaces (APIs) to manage networks as code in much the same way they do infrastructure in the public cloud. Most of those networking APIs are comparatively low-level, but with the rise of services meshes, it’s clear networking services are becoming more accessible.

    The biggest challenge is distinct cultures that have arisen around networking and application development. IT organizations will need to decide whether to provide development teams with the ability to programmatically invoke networking services on their own or through a self-service portal managed by a NetOps team. Regardless of who is responsible for managing the network going forward, the divide between DevOps and NetOps is already starting to narrow. The biggest challenge is simply finding a common language to express core concepts that eliminates any sense of fiefdom that might exist between them. After all, any conflict that arises can usually be attributed to a simple failure to communicate.

    In the meantime, in the age of edge computing, network latency issues are becoming even more challenging. An application based on microservices architecture is especially sensitive to network latency issues that are difficult to troubleshoot over an extended network. Tools that make those issues more obvious are crucial.

  • Sysdig Open Source is Extended to Secure Cloud Services

    New integration enables any Falco plugin to be used for Sysdig OSS

    VALENCIA, SPAIN, (KubeCon + CloudNativeCon Europe), May 16, 2022 — Sysdig, the unified container and cloud security leader, announced that Sysdig open source, the incident response standard for containers, has been extended to the cloud. Using system calls, Sysdig open source (Sysdig OSS) traditionally offers deep observability into running applications, as well as file system access and network activity, which speeds incident response and troubleshooting. Teams can quickly filter information from Sysdig OSS and take action. With the announcement of this new integration, these capabilities have been extended beyond containers to any cloud environment.

    The complexity of cloud-native applications – with countless components and variables – makes it extremely difficult for security analysts and system administrators to quickly triage alerts and debug problems. Sysdig OSS captures process, file system, and network activity in real time and with a high degree of granularity. The tool, which has nearly two million downloads and 6,850 GitHub stars, surfaces everything from executed commands and file system activity to network activity. Sysdig OSS then offers advanced filtering and troubleshooting capabilities, supporting root cause analysis for security and performance issues.

    Using a new plugin framework – originally developed by the open source community for the CNCF project Falco – Sysdig extends the number of sources Sysdig OSS can be connected with to anything that generates logs or events, including Azure, Google, and AWS CloudTrail logs. Going forward, every plugin developed for Falco can also be leveraged by Sysdig OSS. Using one tool, like Sysdig OSS, to observe events from the entire cloud-native environment streamlines investigations. Using a different tool for each environment adds complexity, which makes it massively harder to troubleshoot.

    Learn more about this framework in the Sysdig OSS 0.29 new release blog

    Sysdig’s Commitment to Open Source

    Sysdig was founded as an open source company and Sysdig Secure and Sysdig Monitor were both built on an open source foundation to address the security challenges of modern cloud applications. Both projects were created by Sysdig to leverage deep visibility as a foundation for security, and they have become standards for container and cloud threat detection and incident response. Falco, which was contributed to the CNCF in 2018, is now an incubation-level hosted project with more than 45 million downloads.

    Sysdig OSS and Falco can be used together as a powerful open source solution to reduce risk at runtime. Sysdig OSS acts as a flight recorder, capturing a detailed record for inspection. Falco acts as a security camera, continuously detecting unexpected behavior, configuration changes, intrusions, and data theft in real time. Teams can use Sysdig OSS and Falco together to detect and respond to threats.

    “If you want to see what is going on inside an application, Sysdig OSS gives you that record,” said Loris Degioanni, Founder and CTO of Sysdig. “Sysdig open source was the inspiration for Falco. While Falco will monitor and alert based on your policies, Sysdig open source will tell you what happened at a particular time, before and after the event. Having the ability to use both open source tools in the cloud is extremely powerful.”

    Resources

    ●  Read the New Release of Sysdig Open Source Leverages Falco Plugins.

    ●  Find Sysdig OSS on GitHub.

    ●  Join the Sysdig OSS Slack community.

    About Sysdig
    Sysdig is driving the standard for cloud and container security. The company pioneered cloud-native runtime threat detection and response by creating Falco and Sysdig as open source standards and key building blocks of the Sysdig platform. With the platform, teams can find and prioritize software vulnerabilities, detect and respond to threats, and manage cloud configurations, permissions and compliance. From containers and Kubernetes to cloud services, teams get a single view of risk from source to run, with no blind spots, no guesswork, no black boxes. The largest and most innovative companies around the world rely on Sysdig.

    Media Contact
    Amanda McKinney Smith
    amanda.smith@sysdig.com
    703-473-4051

  • Shift Left is Only Part of Secure Software Delivery

    Shift Left is Only Part of Secure Software Delivery

    We’re living in the age of accelerated consumption and delivery. You can get a seemingly infinite selection of products delivered to your door within two days, for free, from thousands of miles away. You can access an endless variety of services online within mere seconds: Movies, music, games, education and even health care. These modern marvels are afforded to us by relatively recent advances in software development, delivery and operations. 

    Among those advances are the adoption of DevOps practices, continuous integration and continuous deployment (CI/CD) pipelines, and automating everything from infrastructure provisioning to testing and quality assurance. These advances enable developers to deliver software faster and think about security earlier in design and development to ship safer software.

    What is Shift Left” and Why Does it Matter?

    “Shift left” is a philosophy for addressing the pitfalls of traditional waterfall-style development. In waterfall, a number of IT teams work over the course of many weeks or months, culminating in a big and beautiful software release. Of course, people make mistakes, forget things, and maybe don’t communicate well with each other. When it turns out that application elements don’t interoperate well, the teams frantically attempt to fix what’s possible and jettison what isn’t, with a very serious deadline staring them in the face. Products inevitably ship late, still somewhat broken, and with security bolted on as an afterthought.

    To shift left means to introduce security process and tooling earlier into the design and development phases. Security should be just as critical as functionality and quality. It’s a great idea because discovering a critical, build-failing vulnerability in a critical dependency after you’ve built dozens of functionalities on top of it hurts a lot more than if it’s found before you build anything at all. Maybe fixing the problem is as simple as using a newer version of a dependency, but now you have to make sure everything you’ve customized still works as intended.

    There are a number of forms of application security testing (AST) that aim to detect code-level issues early in the systems development life cycle (SDLC). Two common types of AST when shifting left are software composition analysis (SCA) and static application security testing (SAST). Put simply: SAST tests the custom code your developers write; SCA tests dependencies you include in code. 

    Assessing the security of modern applications requires both testing types. If you believe shift left means not only finding problems but also fixing them, then developer-friendly tooling is necessary. Exactly what that means can be subjective depending on developer workflows in the organization, but at the very least, developers need self-service, seamless integration into their existing CI/CD toolchains and actionable results. Because most developers aren’t security experts, security findings must prioritize the riskiest problems, point to the source of the issue and provide contextualized fixes, rather than making the developer hunt for them on their own. 

    Augmenting AST With Runtime Intelligence

    One challenge with doing a lot of early testing—especially security testing—is that the more you test, the more findings you discover. Unfortunately, some of the results will be false positives and others may be true positives that pose a relatively low risk. Development teams with a high degree of security expertise must sift through and vet findings to prioritize flaws that are severe and actionable, but such practitioners are in short supply and this type of work is tedious.

    Addressing the pitfalls of security testing isn’t simple, and it involves gathering as much contextual information as possible to begin to reason about the risk associated with each finding, usually expressed by what exploitable code is actually exercised. 

    Reasoning about vulnerability risk is not easy. We try to rank the criticality of issues to decide on an action. We can split the problem into two parts: 

    • The context of the vulnerability itself includes metrics of severity, like the CVSS score, and threat intelligence, like whether exploits are publicly available or attacks are prevalent in the wild. This information is readily available from scanning tools and third-party sources like NVD, MITRE and CISA.
    • The afflicted asset’s environmental context, however, is specific to your application and your infrastructure. Only your organization can really fill this part in. For example, is the impacted application protected by mitigating security controls? Is it exposed to the internet? Does the vulnerable component even get used at all? This is difficult or impossible to know until the application is running in its intended production environment. 

    Shift left is a way forward for modern cybersecurity, but the approach can be vastly enriched by pulling in runtime intelligence. This helps to prioritize what to fix first, removes friction, saves cycles of numerous IT teams and reduces your organization’s vulnerability risk.

    What Happens After Release?

    The whole point of shift left is to release secure software faster, but what happens next? Your flawless, beautiful code is delighting your customers with its stunning feature set and impressive performance. Then, on some idle Friday afternoon, right before what should have been a long holiday weekend, you get hit with a horrendous zero-day that you could never have predicted even if you tried. 

    When that happens, you need to respond by quickly identifying all of the affected workloads running in your environment and prioritizing them for remediation. You may need to take those workloads offline to patch immediately, limit network access to them, or otherwise mitigate the problem if a patch is either unavailable or taking too long to deploy. The point is that in real life, shift left is only one part of a successful security program, and the protective, detective, and remediation activities for your production environments on the right are also critically important to your organization’s safety and success.

    Conclusion

    Shift left alone was never going to solve all security problems, but it does create foundations for reliable, fast and secure software delivery pipelines. Security and development teams alike often suffer from a deluge of noise and few useful signals. What they really need are consistent and prescriptive ways to make sound decisions about risk. Gathering context from multiple sources through multiple layers of the stack, including runtime signals, substantially improves the quality of the information that DevSecOps teams receive from their tools and must act on.


    Effi Goldstein, director of products at Snyk, co-authored this article. Check out Sysdig and Snyk’s 2022 Container Security Trends: Expert Panel Livestream for more information. 

  • 4 Ways to Combat the DevOps and Security Workforce Shortage

    4 Ways to Combat the DevOps and Security Workforce Shortage

    Most people are painfully aware that security breaches have increased in recent years, while at the same time becoming much more sophisticated in their approach. Additionally, ever-expanding application environments and continuously evolving workloads have created more opportunities than ever for attackers. What’s not so apparent to those outside of the tech bubble: The world is dangerously ill-equipped to handle the magnitude of these threats.

    Organizations may want to meet this challenge with armies of skilled technologists primed to maintain secure operations. But the reality is there is a major shortage of capable DevOps experts, especially ones with cybersecurity skills. This creates major problems for all organizations operating in modern cloud and container environments. 

    According to the cybersecurity advocacy group (ISC)2, this skills gap has noticeable, meaningful consequences for DevOps and security teams. Responses collected from more than 4,500 cybersecurity professionals around the world indicate just how severe the problem is. More than 30% of respondents said they regularly experience misconfigured applications, 29% feel that their teams are too slow to patch critical systems and 27% are unable to maintain necessary awareness of all threats active against their IT infrastructures. 

    It is clear that cybersecurity teams are not staffed to meet current—and anticipated future—demands, processes are not managed, assessment is not addressed and monitoring is incomplete. Yet, this is not just a matter of hiring more people to perform these tasks. The necessary people needed to keep DevOps environments safe simply do not exist as the role has changed faster than the workforce. 

    Time is a critical factor in security, and there can be no waiting around for a solution to appear. DevOps leaders and CISOs must do something, and fast. Fortunately, they can mitigate the burden of this skills shortage and continue moving forward with their transition to the cloud, containers and Kubernetes by taking these steps:

    1. Employ Automation

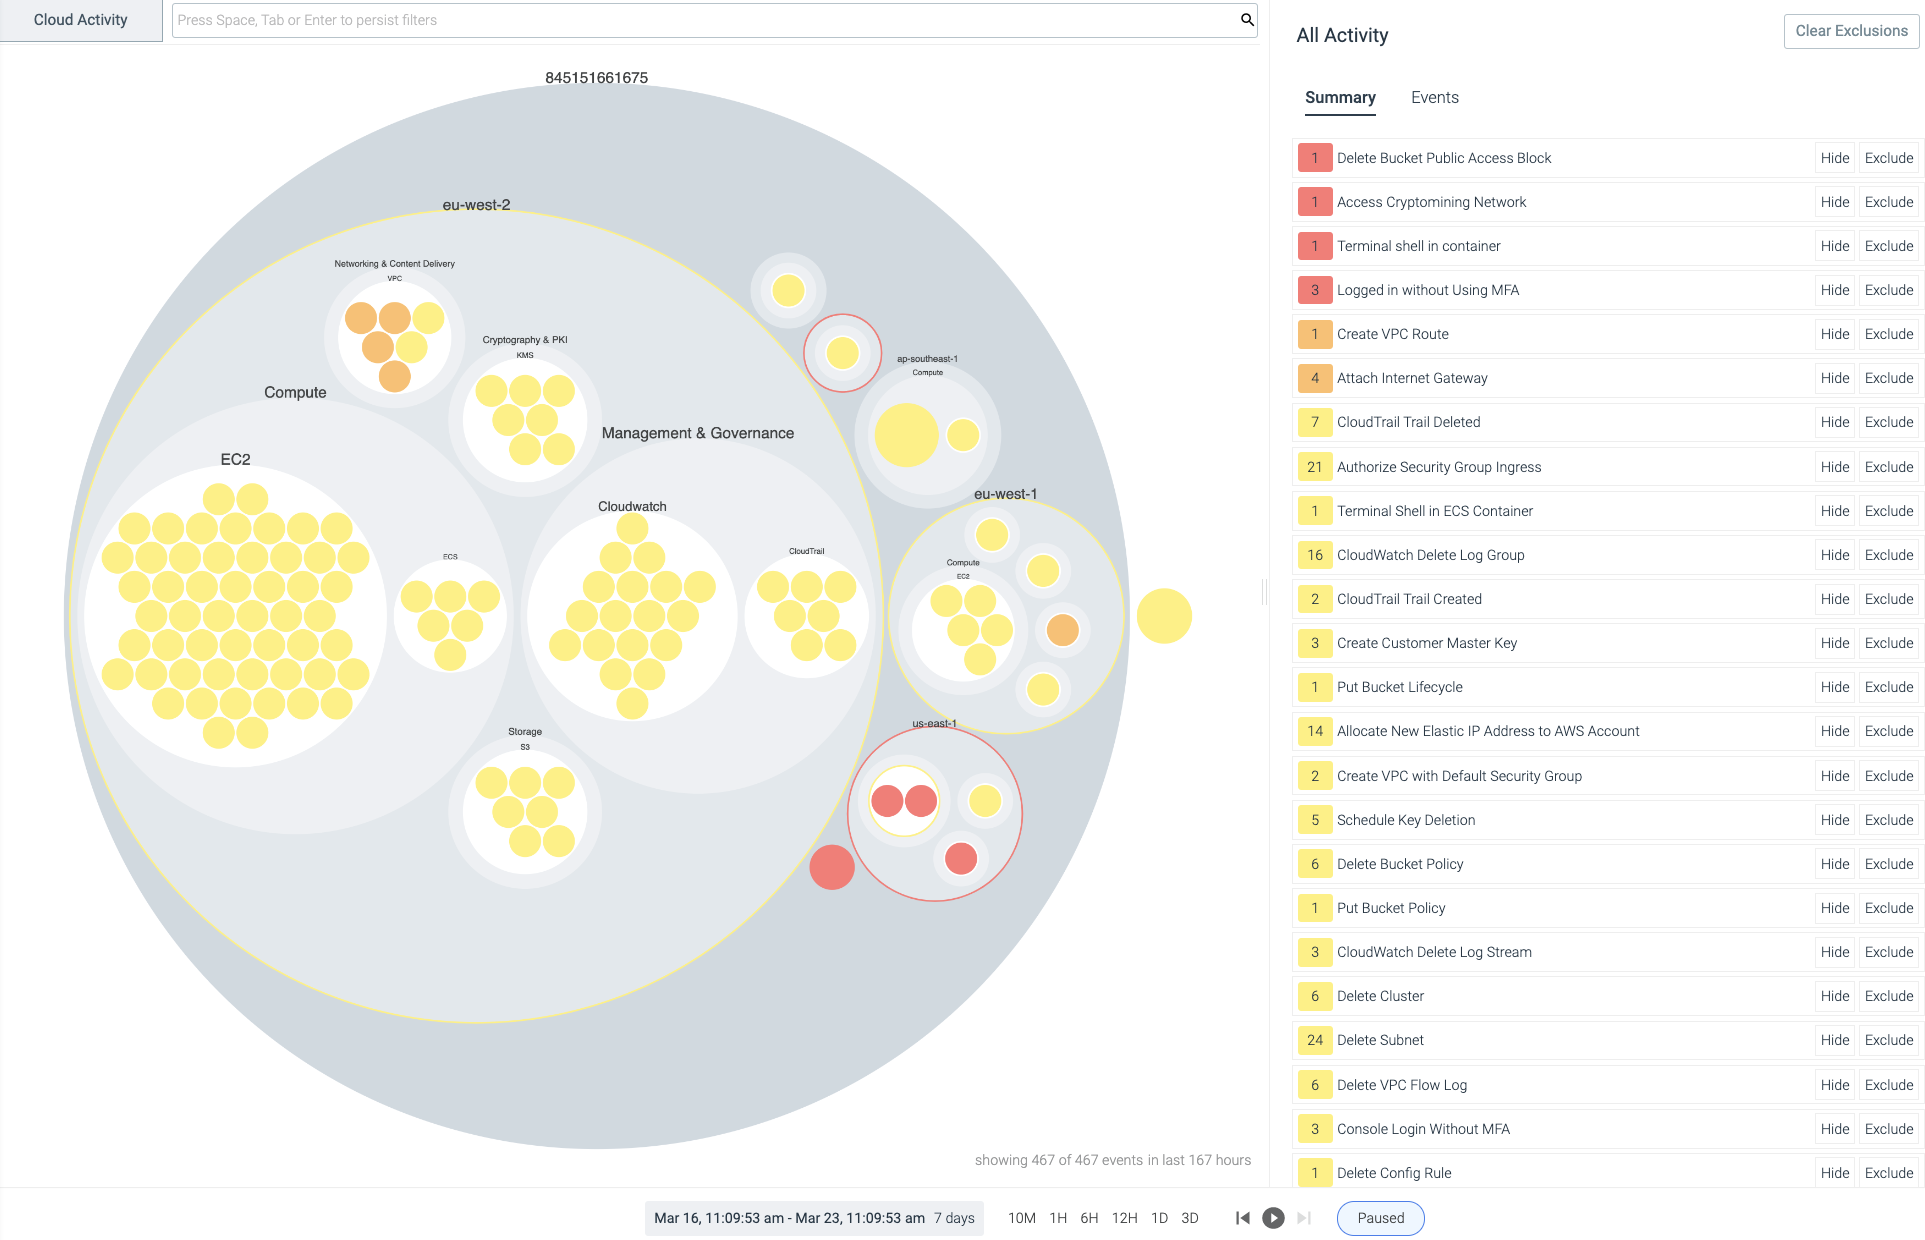
    Security and DevOps teams have to validate that security controls are actually working as intended, but also that they aren’t slowing down development efforts. Many enterprises perform manual checks to determine this, but that’s simply not scalable. Automation is the only way to do this effectively. Companies need tools that can analyze cloud activity without manual processes to understand if things are operating as expected, even in the largest deployments.

    The equalizing factor that combines speed, agility and security is found in automation. With an automated approach, cloud activity can be analyzed and interpreted and DevOps and security teams can be alerted about abnormal behavior within their cloud and container environments. This helps to address vulnerabilities and issues before they are exploited, reduce friction in the development process and ensure safe deployment. 

    For starters, DevOps teams should leverage security tools to automatically build and customize policies. The right tools, some of which can be found in open source frameworks like Falco, are built to adapt to container life cycles and integrations. DevOps teams can rely on these tools to enforce policies and to alert on issues that result from anomalous behaviors that could indicate a threat. 

    Inherent in the automation approach is the shared responsibility concept; security of cloud and container activity is put squarely into the domain of the cloud customer. They are free to operate as needed, but no organization can ignore the modern demands of speed or the necessary requirements of security. This requires that DevOps teams recognize and adapt to the needs of security oversight while security teams must act on their remit while not slowing down the development and delivery processes.

    2. Train People for the Task at Hand

    If the right people don’t exist, it’s up to security and DevOps teams to create them. Organizational training is the key to adding people with the right skills, and every organization should be looking to develop the right candidates into qualified DevOps and security experts. 

    Many of these people already can be found working as application developers or within a security function. You may find individuals who are early in their careers, looking to enhance their skill set and eager to participate in on-the-job training. Every organization should encourage mentoring by more experienced staff, but also should have formalized training programs in place to bring people up to speed on the unique needs of DevOps security. 

    Some colleges now offer specialized cybersecurity degrees or certifications. Coding schools, like the Eleven Fifty Academy in Indianapolis, for example, train students on the most current cybersecurity practices and can be a great source of talent. The United States military also offers some of the most sophisticated technology training and is also fertile ground for recruiting highly skilled security and DevOps players.

    3. Think Globally

    There is no single, prescribed way to attack or hack cloud and container environments. Approaches are diverse, and that’s why the talent responsible for security also should champion diversity. One way to do this is to look beyond your own borders for talent. As the world has embraced remote work over the past two years of the COVID-19 pandemic, more organizations than ever are equipped to bring on workers from across the globe to help them solve security and DevOps issues. 

    Think more broadly about where you can find talent and hire people who can prove their capability through tests and work samples. Not only does this deepen the pool of potential workers, but it also helps you bring new people into the fold who have different perspectives and approaches that could enhance the work you’re already doing. 

    Nearly half of the employees at the company I work for sit outside of the United States. This has drastically increased the talent pool for us. With a bit of diligence, the major barrier to hiring globally—the time difference—isn’t an issue, and you might even find it makes you more efficient.

    4. Rely on Proven Solutions

    Finally, use commercially available products to support your DevOps security needs. Building it yourself is always an option, but when it comes to security, that approach may take more time than you have; a luxury you cannot afford. 

    SaaS products are most reliable and effective in this regard, as they will scale and adapt as your team’s needs change. These tools are purpose-built for the shared responsibility model so they reduce distractions and allow you and your team to focus just on the necessary security and speed-related tasks that are important to helping you achieve your goals. Review sites, the ability to trial them and the perspectives of developer communities will also be extraordinarily helpful in guiding you to making the best decision for your organization. 

    Managing security and DevOps is never easy. With aggressive timetables and delivery deadlines, it’s easy to let the discipline required for security slip. And what makes it even harder is that we cannot hire enough people to take care of these needs. Yet, with a combination of innovative training, new perspectives on hiring and effective use of technology, any enterprise can overcome these limitations.  

  • Sysdig Adds Cloud Access Controls to DevSecOps Platform

    Sysdig Adds Cloud Access Controls to DevSecOps Platform

    Sysdig announced today that it is adding a Cloud Infrastructure Entitlements Management (CIEM) capability to its Secure DevOps platform as part of an effort to better enforce least-privilege access within the context of a larger zero-trust approach to cybersecurity.

    Nick Fisher, vice president of product marketing for Sysdig, said this addition to the company’s core DevSecOps platform for securing cloud services will prevent organizations from inadvertently providing individuals with excessive permissions that result in cybercriminals gaining widespread access to applications and systems when the credentials those individuals have are compromised.

    A recent report from the Sysdig Threat Team found that nearly 80% of users have excessive entitlements due to overly permissive policies. Similarly, Gartner forecasted that 75% of security failures will result from inadequate management of identities, access and privileges by 2023, up from 50% last year.

    The CIEM offering from Sysdig enables cybersecurity and IT operations teams to resolve that issue across multiple clouds in under two minutes once installed, said Fisher. The Sysdig platform achieves that goal by making it possible to leverage templates as a set of infrastructure-as-code (IaC) tools that enable DevOps teams to integrate security within their existing workflows.

    CIEM also simplifies access control auditing by making it easier to discover who in the organization has permission to access cloud infrastructure services. As part of that capability, Sysdig also provides out-of-the-box compliance policies and access to reports that can be generated on-demand to surface a detailed audit trail of all cloud permission changes.

    Finally, CIEM will generate an alert any time someone is denied permission to access a cloud resource, noted Fisher. That capability provides cybersecurity teams with an opportunity to then review what permissions might need to be granted or whether a bad actor is attempting to compromise a cloud environment.

    Most of the cloud security issues that organizations encounter can be traced back to developers that have misconfigured one cloud resource in a way that allows cybercriminals to access, for example, a port that has been left open. CIEM extends the Sysdig platform so that, in addition to scanning for vulnerabilities and misconfigurations, it can detect and respond to attacks across containers and virtual machines deployed in a cloud environment.

    Thanks, in part, to recent high-profile breaches of software supply chains, there’s a lot more focus on cloud security as the rate at which applications are being deployed on these platforms steadily increases. While the cloud platforms themselves are fundamentally secure, the challenge most organizations are encountering is they have immature processes in place for securing the workloads running in the cloud.

    Of course, being able to limit access to those cloud resources is only the first step toward implementing a set of DevSecOps best practices to ensure the integrity of the cloud platforms being employed. Unfortunately, too many developers still tend to assume the cloud service provider is taking steps to secure workloads on their behalf. In reality, cloud service providers have adopted a shared responsibility model that, from their perspective, limits their cybersecurity responsibility to the core infrastructure they provide. It’s up to the DevOps team responsible for the workloads running on those platforms to figure out how to secure the rest of that IT environment.

  • Learning from Loris Degioanni: Cloud-Native Days with Kubernetes Virtual Summit

    Learning from Loris Degioanni: Cloud-Native Days with Kubernetes Virtual Summit

    Keeping up with information can be challenging. With all these changes, you’re probably left wondering, “who can guide me through all this information?” Fortunately, Cloud-Native Days with Kubernetes is focused on giving attendees the tools they need to become proficient in cloud-native technologies. At the virtual summit, attendees can tune into our expert-led featured sessions and learn how to leverage cloud native technologies to move faster and more securely.

    Cloud-native technologies are quickly becoming an integral part of IT environments as organizations continuously accelerate their development efforts to meet business demands. Because of this, it’s incredibly valuable to learn from industry specialists changing the IT world as we know it. And who better to learn from than the industry thought leaders and doers in the cloud-native space? Through sessions touching on topics like security and observability, our featured tech titans will give you a better understanding of cloud native and its impact on the IT landscape.

    Today, the CI/CD pipeline is mainly built on open source tools – Kubernetes, Jenkins, GitLab, etc. Security has traditionally been closed, but it’s now clear the pace of innovation cannot be constrained by proprietary development models. Keynote speaker Loris Degioanni, CTO and founder of Sysdig, will discuss key practices needed for a secure cloud and container environment, including: what is required to increase security, visibility and simplicity in the cloud, lessons learned from major attacks like Kaseya and SolarWinds, ways to leverage Secure DevOps to not only ‘shift left,’ but also ‘roll right’ for detection and response, and how open source is the key ingredient to see all your signals in a constantly changing landscape.

    In his article, “Open Source is Taking Over Security,” published last year on The New Stack, Loris Degioanni elaborates on this idea that open source is essential to maintaining high security, stating, “I argue that, despite having lower penetration of open source, security is the industry that benefits the most from an open source approach. I also argue that open source will gradually take over and become the standard way to do security.” To understand this further, Loris breaks it up into a few key questions: Why is open source the best way to do security? and, Will open source become the standard way to do security?

    Let’s start with the most important question: Why is open source the best way to do security? Loris is adamant that open source is the key ingredient to security because of one thing – speed of innovation. Loris points out that the rise of widely adopted and open computing platforms like Kubernetes have had a big impact on how distributed, coordinated ecosystems can beat out a ‘behind closed doors’ single vendor 100% of the time. Loris writes, “On one hand, Kubernetes and cloud native have such a fast innovation pace that it’s hard for a vendor to keep up by itself. On the other hand, thanks to Kubernetes, for the first time we have a completely open platform to run our applications, where security can be natively integrated rather than being bolted on top.” 

    Open source also increases the speed of innovation because it empowers end users to work with vendors. Any user, regardless of size and level of sophistication, Loris says, can provide feedback in a tight loop and they can also contribute. So why is this relevant to security? As Loris explains, “The intrinsically fragmented nature of vulnerabilities and threats makes this bazaar-oriented approach to contributing very effective.”

    This brings us to Loris’s second question: will open source become the standard way to do security? Not only does Loris say yes, open source will become the standard way to do security, but in fact there is no escaping this. Using a metaphor of bad guys vs. good guys to describe cybersecurity battles, Loris says, “the army of the bad guys is big, smart, and aggressive. And the deck is stacked in their favor.” 

    So how do the good guys win in this scenario? Loris says the best chance at this is, “working together, as a team, leveraging each other’s strength, making sure that no energy is wasted.” Rather than having competing standards upheld by a variety of vendors, Loris is adamant that “a much better approach consists of leveraging a common set of standards that are deeply integrated in the platform, owned by the community, driven by consensus, on top of which all of the players can confidently innovate.”

    Much like Loris’s approach to open source, innovation and security are also valuable key practices at Cloud-Native Days with Kubernetes. Life moves fast. Innovation cannot afford to be slowed down, especially now. So begin your cloud-native information journey by tuning into our expert-led sessions, gathering your questions and learning from our talented speakers August 4 and 5 at 9 a.m. ET.

  • Sysdig Announces Intent to Acquire Apolicy for Infrastructure as Code Security with Auto Remediation

    Policy as code based on Open Policy Agent (OPA) strengthens existing cloud and Kubernetes security in the Sysdig Secure DevOps Platform

    San Francisco, CA, July 20, 2021 — Sysdig, Inc., the secure DevOps leader, announced intent to acquire Apolicy to shift security further left and expand the Sysdig offering to include Infrastructure as code (IaC) security. Sysdig customers secure the DevOps cycle from build through production. Apolicy complements these capabilities by strengthening cloud and Kubernetes security with compliance and governance enforcement via policy as code, auto-remediation of drift to close the loop from production to source, and faster issue resolution with risk-based prioritization.

    Cloud Teams Adopting Secure DevOps to Manage Security Risk
    The pandemic has caused a massive shift towards doing things online, which puts pressure on teams delivering applications in the cloud. Modern apps are built as containerized microservices using a DevOps approach to accelerate delivery. Teams are adopting secure DevOps as they transform security processes to adapt. This includes cloud configuration risk management, scanning images at build time, detecting and responding to threats at runtime, and continuously validating compliance with regulatory standards.

    Automating Cloud and Kubernetes Security with IaC security The trend of Infrastructure-as-Code (IaC) and GitOps continues to gain broad mindshare with cloud platform teams as a way to achieve complete operational control of infrastructure. As teams codify infrastructure using IaC tools like Terraform, CloudFormation etc, it can be easy to overlook security. Misconfigurations in the cloud are common, evident by many high profile cloud breaches. Adopting IaC principles for building infrastructure can improve reliability by improving consistency and reducing human error. Checking for security as configurations are defined ‘shifts security further left’, allowing teams to identify and resolve issues before infrastructure is deployed.

    The goal of IaC security is to automate an organization’s cloud and Kubernetes security controls. With IaC security, teams can consistently enforce compliance and governance by applying policies as code to validate both configuration files and production environments and ensure they are identical. When runtime deviations occur, they can be discovered and automatically remediated directly at the source to ensure they don’t happen again. By integrating IaC security into the secure DevOps workflows, teams can shift security further left, improving security and reducing alert fatigue for security teams.

    Blog from CEO Suresh Vasudevan: Sysdig and Apolicy Join Forces To Help Customers Secure Infrastructure As Code and Automate Remediation.

    IaC Security Benefits with Apolicy Acquisition for Sysdig’s Customers:

    • Enforce compliance and governance via policy as code from source to production: Apolicy provides the ability to apply consistent policies and best practices across multiple IaC, cloud and Kubernetes environments. Customers can now bridge the gap between developers, DevOps and security teams with a unified view of security requirements using policy as code. Automating compliance by enforcing OPA-based policies via Kubernetes admission controller puts the control back in the hands of the user.
    • Auto-remediate drift and close the loop from production to source: With the addition of Apolicy, customers can now detect runtime drift and instantly map it back to the IaC configuration (source) file. This dramatically increases developer productivity by auto-remediating the IaC configuration source with a simple pull-request and allows for enforcing policy consistently across teams.
    • Fix issues faster with risk-based prioritization: Consolidating alerts by identifying the production instances that are affected by the IaC error and prioritizing IaC fixes based on application context, allows users to prioritize remediation efforts. Rich application context makes it easy to identify owners who can fix misconfigurations.

    The Apolicy team, including the founders Maor Goldberg, CEO, Eran Leib, VP Product Management, and Shlomi Wexler, VP R&D will join the Sysdig team. The Apolicy product offering will be incorporated as part of the Sysdig Secure DevOps Platform.

    The Sysdig Secure DevOps Platform uniquely addresses the challenges of securing containers, Kubernetes, and public cloud infrastructure. Sysdig is trusted by hundreds of leading enterprises, including Worldpay by FIS, Yahoo Japan, IBM, and JW Player to confidently run modern cloud applications while managing security risks and meeting compliance requirements.

    “Most breaches are caused by configuration errors. Our customers want a single platform that detects configuration errors pre-deployment and identifies drift in production,” said Suresh Vasudevan, Chief Executive Officer, Sysdig. “With Apolicy, only Sysdig delivers a secure DevOps workflow for infrastructure and workloads and automatically closes the loop from production to source by fixing issues identified at runtime.”

    “We founded Apolicy with the purpose of securing Kubernetes from source to production through risk identification, remediation, and policy enforcement,” said Maor Goldberg, Chief Executive Officer, Apolicy. “We are excited to join forces with Sysdig and combine the best security capabilities in the market for cloud and containers together with our infrastructure and posture security. Together we will bring customers one end-to-end cloud native security platform that is built on open source.”

    “We were very excited to be the first to support Maor and the Apolicy team in late 2019 as they set out to disrupt the cloud-native application protection space. We are equally excited today to see the next step in Apolicy’s evolution as it combines with Sysdig, and look forward to the future success of the combined company,” said Tal Slobodkin, Managing Partner at StageOne Ventures.

  • Sysdig Adds CSPM Module to DevSecOps Platform

    Sysdig Adds CSPM Module to DevSecOps Platform

    Sysdig today announced it added a cloud security posture management (CSPM) module to its Sysdig Secure DevOps Platform for monitoring application performance and security to enable IT teams to continuously detect threats.

    Pawan Shankar, director of product marketing for Sysdig, said this CSPM capability is based on an open source Cloud Custodian tool that enables IT teams to define rules for accessing cloud infrastructure. In addition, the tool enables IT teams to collect utilization metrics that could be used to turn cloud resources off when they are not being employed. IT teams can now also automatically discover all cloud services being employed, including identifying which ones are misconfigured or might have compliance and regulatory issues that need to be addressed, via a software-as-a-service (SaaS) platform.

    The overall goal is to help reduce the friction that organizations encounter today as they embrace DevSecOps best practices, added Shankar.

    Sysdig is making its CSPM offering available for free, for one account, to encourage DevOps teams to make use of a CSPM capability along with Sysdig’s open source Falco threat detection capabilities. Sysdig today also announced that it extended its implementation of Falco to consume audit logs created on the Google Cloud Platform (GCP). Sysdig donated Falco to the Cloud Native Computing Foundation in 2018. More recently, Sysdig also contributed a sysdig kernel module, along with libraries for the Falco security platform for Kubernetes, that runs in the extended Berkeley Packet Filter (eBPF) microkernel to further improve Linux security.

    The free tier includes a daily check against CIS benchmarks as well as support for inline scanning of up to 250 container images per month running on either the Fargate or Elastic Container Registry (ECR) services provided by Amazon Web Services (AWS).

    Sysdig has been making a case for the convergence of traditional IT monitoring functions and security for several years now. In the wake of some recent high-profile breaches involving software supply chains, the company is betting that more DevOps teams will soon be revisiting how their software supply chains are managed at a time when it’s become easier for malware to move laterally across an entire IT environment. In fact, Sysdig cited research that estimates that malware moving laterally through an organization is involved in 70% of cyberattacks.

    Of course, with the rise of applications based on microservices, the average IT environment is about to become a lot more integrated, which naturally makes it easier for malware to move laterally. IT organizations now require greater visibility across an entire potential attack chain to combat those threats, Shankar noted.

    As DevSecOps continues to evolve, the relationship between developers and cybersecurity teams is also clearly evolving. Now that developers are being held more accountable for cybersecurity, many of them are gravitating toward tools that can be easily integrated within the context of a larger DevOps toolchain.

    It remains to be seen exactly how security tools will be integrated within those tool chains, but for DevOps teams that already rely on Sysdig to monitor their IT environments, the ability to access a raft of additional security services is only a few mouse clicks away.