Category: News

  • Virtual Instruments Changes Name to Virtana to Drive AIOps

    Virtual Instruments Changes Name to Virtana to Drive AIOps

    With the formal launch of a software-as-a-service (SaaS) to monitor cloud platforms and optimize cloud, Virtual Instruments today renamed itself Virtana.

    The company’s CloudWisdom platform is based on technology Virtana gained via the acquisition of Metricly earlier this year. In addition to being integrated with existing on-premises offerings from Virtana, CloudWisdom has been expanded to include a self-service option. Downloadable trial versions are also available.
    Virtana CEO Philippe Vincent said the name change reflects a transformation from being simply a provider of storage I/O performance testing tools to becoming a provider of an IT operations management platform infused with artificial intelligence (AIOps). As part of that effort, the CloudWisdom offering represents the first time Virtana has extended the reach of its offerings beyond on-premises IT environments, he said.

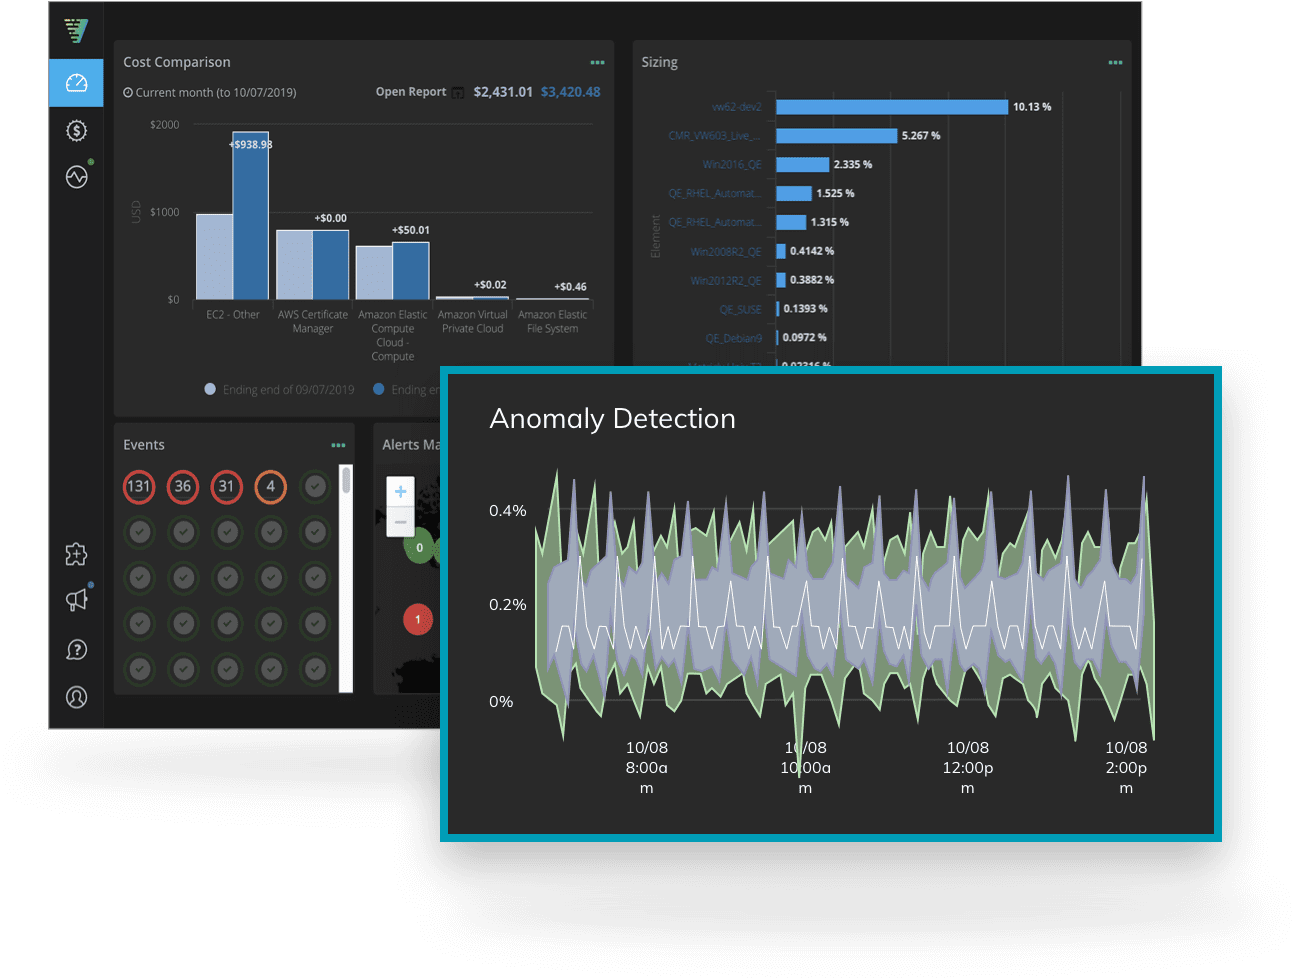
    CloudWisdom will differentiate itself, Vincent said, because it combines cloud monitoring with built-in tools for optimizing cloud costs. Rival offerings require IT organizations to acquire two separate services, he noted. The CloudWisdom platform monitoring capabilities span databases, messaging platforms and containers, as well as cloud infrastructure services from Amazon Web Services (AWS) and Microsoft.

    In general, Vincent said IT organizations are moving away from a reactive approach to managing IT to a more proactive approach that will require increased reliance on automation. As IT environments become more complex, too many IT organizations are trying to compensate by overprovisioning IT infrastructure resources to make sure application performance doesn’t deteriorate or applications crash. That approach not only drives IT costs higher, he said, but it also makes those costs unpredictable.

    To address that issue, Virtana is combining CloudWisdom with an AIOps platform designed to be equally applicable in legacy IT service management (ITSM) and emerging DevOps environments. Organizations that have adopted DevOps will be at the forefront of the transition to AIOps because of the inherent fluidity and velocity of those environments, Vincent noted. Machine learning algorithms coupled with real-time monitoring, big data analytics, workflow engines and automation frameworks will enable IT teams to streamline ITSM and DevOps processes to become more efficient. The opportunity for Virtana is to disrupt a highly fractured monitoring category by leveraging AIOps to unify monitoring at an unprecedented level of scale and scope, he added.

    Virtana is not the only IT management platform provider that has identified the same opportunity; much larger incumbent providers of these platforms and a raft of startups are moving in the same AIOps direction. Vincent said Virtana will differentiate itself by pursuing a more application-centric approach to delivering on the promise of AIOps.

    It’s too early to say to what degree IT operations can be automated using AI. There’s general agreement that AI will play a significant role in automating IT, and the more standardized the IT environment is, the easier it is to accomplish. The challenge is, most IT environments today are still anything but standardized.

    — Mike Vizard

  • Anaxi Adds Reporting Capabilities to ALM Tool

    Anaxi Adds Reporting Capabilities to ALM Tool

    Anaxi today announced it has added reporting capabilities to its namesake application lifecycle management (ALM) tool that make it possible to update stakeholders about the status of software development projects residing in repositories such as GitHub and Bitbucket Cloud as well as project management applications such as Jira.

    Company CEO Marc Verstaen said reporting capabilities will make it easier to employ Anaxi to, for example, keep business leaders apprised of updates to software development initiatives by enabling IT leaders to generate a report similar to how business leaders today employ a business intelligence (BI) application to share sales forecasts.

    The Anaxi tool is designed to provide IT leaders with a single tool for tracking progress being made across multiple DevOps platforms. Verstaen said as more organizations begin to realize they are really software companies, interest in software delivery management tools is on the rise. The reporting challenge IT leaders face is the information they need to create a holistic report lies in multiple repositories because of the inherently fragmented nature of the DevOps tool chain, he said.

    To make it easier to adopt Anaxi, the ALM tool Data employs the same credentials organizations have created to access GitHub, Bitbucket and Jira. The Anaxi app connects directly to a user’s GitHub or Bitbucket repositories and Jira projects to ensure data privacy and security. Any action performed on the Anaxi applications is written back on GitHub, Bitbucket and Jira to maintain consistency across projects involving multiple team members.

    At its core, Anaxi is pulling metadata from DevOps tools to apply analytics to track individual developer productivity and team performance. IT leaders can, for example, analyze how much code has been added and removed, refactoring and code churn on a weekly basis. Anaxi can be used either in place of a project management application or as a complement to an existing project management tool to make analytics more accessible.

    The primary goal is to make it easier for IT leaders to identify DevOps bottlenecks and prioritize projects in a way that advances business goals. Too many organizations are writing more code than ever only to discover projects are being held up because a single component on which every other module depends is behind schedule. Many of the developers writing that code could have been working on other projects if IT leaders had been made aware of changes that needed to be made to the schedule based on the anticipated delay to another project. Anaxi essentially applies predictive analytics to software development projects to determine based on past histories the likelihood of a deadline being met, Verstaen said.

    Armed with that intelligence, IT leaders can either proactively reallocate how resources or allocated or inform business stakeholders to changes in delivery schedules. In either case, Versaten says the goal is to enable IT leaders to avert any software development crisis that might arise.

    The Anaxi app is free to use by teams of up to 10 members. Teams of more than 10 users will be required to adopt a premium plan priced at $19 per month per user.

    — Mike Vizard

  • OpenLegacy Partners With Compuware to Advance DevOps on Mainframes

    OpenLegacy Partners With Compuware to Advance DevOps on Mainframes

    OpenLegacy has allied with Compuware to make it easier to build and debug microservices-based applications employing REST application programming interfaces (APIs) to access data residing on mainframes.

    Zeev Avidan, chief product officer for OpenLegacy, said the company’s namesake platform analyzes mainframe environments to create microservices-based APIs written in Java without requiring any changes to the legacy environment. That approach not only minimizes disruption to the mainframe environment, but it also eliminates the need to rely on enterprise service bus (ESB) platforms and legacy web services interfaces to access mainframe data, he said.

    The alliance with Compuware now makes it easier access the OpenLegacy platform from within Topaz Workbench, a set of tools from Compuware that are used to apply DevOps practices to applications that either run on a mainframe or need to access data residing on a mainframe.

    Avidan said it is becoming increasingly common for organizations to want to build and deploy applications that need to access mainframe data as part of various digital business transformation initiatives. The challenge they face is that most legacy monolithic applications running on a mainframe don’t have an API to invoke. OpenLegacy provides a framework for generating those APIs, which in turn makes it easier to incorporate mainframes within the context of a larger DevOps process. The alliance with Compuware furthers an ongoing effort by the two companies to foster the adoption of best DevOps processes in mainframe environments, he said.

    Legacy waterfall-based application development processes are still relevant in mainframe environments, he added, but it’s also clear organizations want to apply DevOps processes to applications spanning hybrid environments that include mainframes. The majority of data in many enterprise IT environments is created on a mainframe. Rather than being forced to copy that data, API platforms such as OpenLegacy make that data more accessible where it resides. Once the APIs are in place, it becomes practical for DevOps teams to create software development kits (SDKs) to access various applications running on mainframes, Avidan said.

    Organizations that have invested in mainframes generally are interested in agile development methodologies that enable them to derive more value from those investments. The challenge they face is finding a way to make that data available in a way that doesn’t disrupt the mission-critical applications running on the mainframe, he said. Over time, IT organizations running mainframes will adapt their processes to incorporate best DevOps practices, but the level of disruption they can embrace in pursuit of that goal has to be minimized, Avidan noted, adding it would be unreasonable to expect that level of cultural change to occur overnight.

    Despite ongoing predictions about the eventual demise of the mainframe, the number of workloads running on the venerable platform continues to increase, thanks in part to the ability to run Linux on a mainframe. What many organizations that opt to run Linux on a mainframe don’t always initially appreciate is the degree to which that decision also opens the door to transforming their internal IT culture, regardless of whether they are ready.

    — Mike Vizard

  • Render Taps Manifold to Expand Cloud Services for Developers

    Render Taps Manifold to Expand Cloud Services for Developers

    The rate at which DevOps teams that rely on cloud services from Render will be able to discover new tools is about to increase significantly, thanks to Render’s new alliance with Manifold, a provider of a marketplace-as-a-service platform.

    Render already offers logging, monitoring and other DevOps tools, and will use the Manifold technology to create its own marketplace. Render CEO Anurag Goel said the partnership will provide his company with a platform that enables instant access without having to navigate as many configuration steps because Manifold has automated those processes.

    Goel said Render has been growing at a rate of 50% per month by focusing on the needs of developers, a strategy that has resulted in more than 100 million http requests a week on the Render platform. That approach has allowed the company to differentiate its cloud platform from much larger rivals such as Amazon Web Services, Microsoft Azure and Google Cloud Platform, which are not as focused on the developer experience, he said.

    Manifold CEO Jevon MacDonald said Manifold has focused its efforts on building a marketplace that allows smaller cloud service providers to offer tools and applications with a user experience that rivals any of the marketplaces provided by the big three cloud service providers but without having to build and maintain that marketplace themselves. Manifold also works with each provider of tools and applications on the marketplace to automate the configuration process, he said.

    Over time, marketplaces have proven to be critical for cloud service providers because they provide the foundation on which developer ecosystems are created. The easier a cloud service provider makes it for DevOps teams to discover new tools and applications, the larger that ecosystem tends to become.

    Obviously, AWS, Microsoft and Google have massive DevOps ecosystems in comparison to Render. However, with the rise of cloud-native platforms such as Kubernetes, it will become much easier for DevOps teams to build applications on one cloud platform and deploy them on another. To attract developers of cloud-native applications, Render has built a containerized platform as an alternative to legacy platform-as-a-service (PaaS) environment.

    Render is betting that cross-platform strategy for building applications becomes more commonplace, more developers will opt to build applications on cloud platforms specifically focused on providing a superior developer experience. Current Render customers include smaller startups such as 99designs, Gatsby and Indie Hackers by Stripe.

    As developers start to shift toward cloud-native technologies, it remains to be seen how many DevOps teams will be willing to consider alternative cloud platforms. The major cloud service providers have built business models around providing as little support as possible. While it may not be possible for cloud service providers to support each DevOps team with an expensive support contract, there does appear to be plenty of room for cloud service providers to create a richer developer experience that goes beyond a basic one-size-fits-all approach.

    — Mike Vizard

  • Continuous Delivery Foundation Momentum Picks Up

    Continuous Delivery Foundation Momentum Picks Up

    The Continuous Delivery Foundation (CDF) this week revealed that it now includes 33 member organizations, including now JPM Chase, eBay, Dell Boomi, Cycloid, White Source, the Association of DevOps Professionals and the DevOps Institute.

    Founded by CapitalOne, CircleCI, Cloudbees, Google, Huawei, IBM, jFrog, Netflix and Salesforce in March the CDF is committed to promoting the adoption of open source continuous integration/continuous deployment (CI/CD) tools and platforms. Dan Lopez, CDF program manager, said the CDF plans to launch technical committees soon that address areas of CI/CD interest, including cybersecurity, software supply chains, software delivery management and machine learning algorithms in IT operations (MLOps).

    The CDF is not focused on promoting one open source CI/CD platform over another as much as it is fostering cross-engineering whenever feasible. As such, Lopez said the CDF is trying to advance adoption of the open source Jenkins and Jenkins X CI/CD platforms as well as the Spinnaker platform from Netflix. As other open source technologies are presented to the CDF, a technical oversight committee will evaluate them for inclusion, he said.

    At present, the membership of the CDF falls into three broad categories: companies that build tools and platforms, companies that leverage those technologies to deliver products and services and end user organizations such as JP Morgan Chase, eBay and CapitalOne.

    Lopez said the next goal is to expand the reach of the CDF beyond the U.S. and Europe to create a global CI/CD community. It’s not clear how many CI/CD platform providers will join the CDF. However, as membership in the CDF increases, pressure to join continues to mount.

    In the meantime, DevOps teams should expect collaboration between vendors to accelerate the pace of innovation across the entire DevOps life cycle. Vendors will be able to more easily identify areas to collaborate on that don’t provide much in the way of differentiation and yet are critical to advancing DevOps adoption.

    While a lot of progress has been made in terms of CI use, CD has proven to be an especially thorny challenge for most organizations. That’s become a significant challenge as organizations build applications at a faster rate and in many cases are still being deployed manually in production environments. Via the CDF, vendors are hoping to promote adoption of best practices across the entire DevOps toolchain as they gear up to introduce additional products and services that assume a strong CI/CD foundation is in place.

    It’s not clear to what degree the CDF will be able to accomplish that mission, given that most of the CI/CD issue organizations encounter are more cultural than technical. At the very least, however, organizations struggling with these issues should find solace among other like-minded souls wrestling with the same issues.

    — Mike Vizard

  • Red Hat Unveils Ansible Platform

    Red Hat Unveils Ansible Platform

    At the AnsibleFest 2019 conference, Red Hat this week announced the general availability of the Red Hat Ansible Automation Platform that combines several IT automation technologies into a single subscription.

    Built on top of Red Hat Ansible Engine, the platform also includes Red Hat Ansible Tower, a management console, and Red Hat Network Automation, an instance of Ansible designed to automate the management of network resources.

    Red Hat is also providing access to a software-as-a-service (SaaS) analytics application that enables IT teams to monitor how deeply Ansible has been adopted within any IT environment. That application also provides access to Ansible Content Collections, a packaging format that streamlines the management, distribution and consumption of Ansible content, and Automation Hub, a repository for certified content packaged using Ansible Content Collections.

    Richard Henshall, product manager for Red Hat Ansible Automation, said with this offering Red Hat is trying to make it easier for enterprise IT organizations to implement Ansible at scale. Most of the time the Ansible framework is adopted from the bottom up within an IT organization. Red Hat Ansible Automation is intended to make it easier for enterprise IT organizations to centrally deploy and manage all their instances of Ansible, he said.

    Although it’s not possible to know how many instances of the open source IT automation framework have been installed, Henshall noted there are already more than 4 million Ansible nodes that are tied to a paid support subscription from Red Hat. Most of those instances involve organizations that have adopted a declarative IT automation framework as part of their overall DevOps strategy, he said. While IT organizations don’t necessarily have embrace DevOps to employ Ansible, Henshall said there is a strong correlation.

    Much of that success can be tied to the fact that as a declarative framework Ansible doesn’t require IT operations teams to learn how to program to manage IT operations at scale. That approach has allowed IT teams to adopt the open source framework to meet the demands for more agile approaches to managing IT infrastructure stemming from developers who have embraced best DevOps practices.

    In addition, IT infrastructure vendors such as Cisco Systems, NetApp and F5 Networks have begun to embed Ansible within their server, storage and networking platforms. As those vendors sell the latest edition of their offerings, the number of IT organizations exposed to Ansible should begin to substantially increase.

    Henshall said the biggest issue now is expanding the scope of Ansible deployments. Most organizations initially wind up using Ansible to automate disaster recovery before moving on automate additional existing processes. Red Hat is now trying to encourage those teams to create new processes that previously would not have been possible without an IT automation framework, he said.

    Ansible may not be a de facto standard in the enterprise just yet, but it’s well on its way. Of course, there are still many IT professionals for one reason or another still tend to resist relying on IT automation frameworks. There are also several rival IT automation frameworks that have been embraced by DevOps teams. But when it comes IT automation, it’s clear Ansible is starting to emerge as the path of least resistance.

    — Mike Vizard

  • DevSecOps Becomes a Higher Cloud-Native Priority

    DevSecOps Becomes a Higher Cloud-Native Priority

    At the Cloud Native Security Summit, Enterprise Strategy Group (ESG) today revealed the results of a survey of 600 senior IT leaders that finds organizations are looking at DevSecOps as a way to address the complexities of managing and securing cloud-native applications.

    According to the survey results, 43% of respondents said their biggest challenge with cloud-native applications is maintaining consistency across disparate infrastructures. As a result, the same number of respondents said DevSecOps automation as their highest cloud security priority.

    Commissioned by Capsule8, Obsidian and Signal Sciences, the survey also finds 90% of respondents are concerned about not having visibility into misconfigured cloud services, server workloads, network security or privileged accounts. Another 83% are worried about the misuse of privileged accounts by insiders.

    Two-thirds (66%) say IT is more complex than it was two years ago, with more than a third (35%) citing the need to manage multiple cybersecurity controls as a major source of that complexity.

    Doug Cahill, a senior analyst and group director at ESG, said it’s clear that as organizations embrace best DevOps practices to build and deploy cloud-native applications, those processes now are being extended to include security controls as part of the quality assurance process. Rather than bolting on security, Cahill said, more organizations are building cybersecurity controls into their software from the ground up.

    Capsule8 CEO John Viega noted much of that shift is being driven by necessity. When applications were deployed mainly in on-premises IT environments, it was easier to secure the environment by deploying appliances. Now organizations need to secure applications on infrastructure they don’t control as part of a shared responsibility model that often spans multiple cloud service providers. The cloud may be more agile and less expensive, but Viega noted it’s not uncommon for hundreds of cloud accounts to have been set up by individuals in the same organization, each with very different levels of cybersecurity expertise.

    Obsidian Security CTO Ben Johnson added the rate at which cloud-native applications are being deployed and updated is overwhelming the ability of cybersecurity teams to keep pace. In fact, many organizations are still underestimating the scope of the cloud-native cybersecurity challenge they face.

    Finally, Hala Al-Adwan, vice president of technology for Signal Sciences, observed as organizations embrace DevSecOps, cybersecurity professionals still will play a key role in terms of their consulting expertise. However, responsibility for implementing cybersecurity will continue to shift left toward DevOps teams. The challenge those teams will face is the need to replace legacy cybersecurity infrastructure designed for cybersecurity administrators with programmable tools that fit neatly within a continuous integration/continuous deployment environment, said Al-Adwan.

    It’s not clear precisely when a desire to embrace DevSecOps will result in more secure applications. In theory, cloud-native applications should be a lot more secure than legacy monolithic applications. However, the degree to which higher levels of security will motivate organizations to replace monolithic applications remains to be seen.

    In the meantime, cultural issues associated with embracing DevSecOps will abound. There are simply not enough cybersecurity professionals available to participate in every application development scrum session. The real issue now is finding a way to embed that knowledge into an application development process operating at industrial scale.

    — Mike Vizard

  • New Relic Extends Observability Reach and Scope

    New Relic Extends Observability Reach and Scope

    At its FUTURESTACK 2019 event in New York today, New Relic announced it has extended the New Relic One Observability Platform to add support for its new Logs, Traces, Metrics and AI module offerings.

    Ken Gavranovic, general manager and senior vice president of products for New Relic, said his company is committed to extending the breadth of a programmable platform to address DevOps requirements flexibly, rather than forcing IT teams to stitch together multiple tools to monitor their applications.

    As part of the effort, New Relic also is making it possible for customers to build applications using the data New Relic stores in its cloud platform using a framework based on React and GraphQL. The company is also making available a series of open source monitoring applications that organizations can customize in less than an hour using templates it provides.

    New Relic also announced the availability of New Relic Logs, a log management service intended to make it easier for operations teams to correlate log data across application and infrastructure sources. The module will enable teams to run ad hoc searches that return queries in milliseconds without having to switch to another tool.

    At the same time, New Relic announced the availability of New Relic Traces and New Relic Metrics, to help DevOps teams more easily identify dependencies across the IT environment. The goal is to make it possible for teams to understand all the upstream and downstream events occurring across a distributed IT environment using a single platform, said Gavranovic.

    For example, DevOps teams will be able to monitor a serverless computing framework from within New Relic in addition to turning on a feature flagging tool that has been integrated via application programming interfaces (APIs).

    Finally, New Relic AI, available in beta, will bring artificial intelligence (AI) to the platform in the form of machine learning algorithms and predictive analytics to correlate, aggregate and prioritize incident data automatically across multiple tools to reduce alert fatigue and improve mean time to resolution. New Relic AI is already integrated with PagerDuty, Slack and other tools to enable organizations to slipstream this capability into their existing workflows, said Gavranovic.

    By taking that approach, organizations can embrace New Relic as an open platform by organizations regardless of their current level of IT maturity, he added.

    New Relic is clearly betting a single integrated tool for monitoring the entire IT environment will be preferable to integrating a wide range of disparate tools. Gavranovic believes that approach will have even more appeal as organizations embrace microservices to build and deploy applications. Given all the dependencies that exist between all those microservices, monitoring tools will need to reach across applications and infrastructure to enable DevOps teams to discover and monitor all those dependencies in near real-time.

    Naturally, New Relic is not the only provider of monitoring tools with similar ambitions. It is, however, a lot further along in terms of turning monitoring tools into an actual platform.

    — Mike Vizard

  • GitLab Outlines Scope of DevOps Ambitions

    GitLab Outlines Scope of DevOps Ambitions

    At the GitLab Commit event in New York today, GitLab launched an ambitious effort to extend the scope of its DevOps platform to provide a view into the software development life cycle for not just developers but also designers, product managers and business leaders.

    Fresh off raising an additional $268 million in funding, GitLab now plans to create different ways to view a common pool of metadata and metrics generated by the GitLab DevOps platform.

    It may be a while before GitLab can deliver on that promise, but the core concept builds on the dashboards the company already has built for IT operations and cybersecurity teams. Rather than requiring each team participating in the software development process to acquire a separate platform, GitLab should be viewed as a DevOps platform delivered as a single application that can now be applied to everyone, said Mark Pundsack, vice president of product strategy for GitLab, in speaking with conference attendees.

    As part of that commitment, Pundsack noted GitLab is expanding its DevSecOps capabilities to include auto remediation. The scanning capabilities built into GitLab will be extended not only to detect issues based on the cybersecurity policies of an organization, but also, when allowed, automatically remediate routine issues, Pundsack said, adding GitLab also will automatically roll back applications if necessary. Once in place, GitLab will have pushed application cybersecurity much further left than anyone might have expected when DevSecOps was first broached as a concept, he said.

    At the conference, GitLab demonstrated a pipeline graph capability that will provide a foundation for many of these promised offerings. GitLab already can be employed to accomplish tasks such as code quality scanning, container scanning, dependency scanning and licensing dependencies.

    All these features are an extension of GitLab’s existing strategy that aims to rationalize the number of tools organizations need to stitch together to drive a set of best DevOps processes. However, other DevOps platform providers have similar ambitions.

    Thanks to its latest round of funding, GitLab—which also announced its plans to go public next year—is now valued at $2.75 billion. The company has not released any revenue results but does claim to support more than 100,000 organizations using its platform, including Ask Media Group, Charter Communications, Delta Air Lines, Goldman Sachs, Ticketmaster and Nvidia. GitLab also claims to have more than 4,800 active contributors to its open core platform. The company now has more than 800 employees in more than 55 countries across the globe, and there currently are 222 open GitLab jobs posted.

    It remains to be seen how much $268 million will enable GitLab to fend off rivals such as GitHub, which was acquired by Microsoft, and CloudBees, which has built a large DevOps community around the open source Jenkins continuous integration/continuous deployment (CI/CD) platform. Whatever the outcome of this arms race, the massive amount of funding pouring into the platforms soon should take DevOps platforms to places many might not have ever imagined possible.

    — Mike Vizard

  • Eclipse Foundation Delivers on Jakarta EE Promise

    Eclipse Foundation Delivers on Jakarta EE Promise

    The Eclipse Foundation today announced the general availability of Jakarta Enterprise Edition (EE) 8 Full Platform and Web Profile specifications and associated technology compatibility kits (TCKs).

    Announced during the JakartaOne Livestream virtual conference, Jakarta EE 8 is the follow-on open source platform to JavaEE that provides a foundation for building cloud-native applications using a familiar Java construct.

    Mike Milinkovich, executive director of the Eclipse Foundation, said the availability of Jakarta EE 8 represents a milestone in that it is the first official release of a full Jakarta platform since Oracle agreed to give up control of Java EE to the Eclipse Foundation.

    Its specifications are fully compatible with Java EE 8 specifications and include the same application programming interfaces (APIs) and an instance of Javadoc using the same javax namespace. Its TCKs are based on, and fully compatible with, all Java EE 8 TCKs. Jakarta EE 8 will not require any changes to Java EE 8 applications or their use of javax APIs. The specifications were developed under the Jakarta EE Specification Process, which replaces the Java Community Process (JCP) for Java EE.

    The Eclipse Foundation is announcing the certification of Eclipse GlassFish 5.1, an open source compatible implementation of the Jakarta EE 8 Platform. Eclipse GlassFish 5.1 is fully tested under the open source-licensed Jakarta EE 8 TCKs for the Full Platform and Web Profiles.

    IBM today also announced that Open Liberty, an open source implementation of the WebSphere Liberty application server, has been fully certified as being compatible with Jakarta EE 8 profiles. All vendors in the Jakarta EE Working Group, including Fujitsu, IBM, Oracle, Payara, Red Hat and Tomitribe, have committed to certifying their Java EE 8-compatible implementations.

    Milinkovich said Jakarta EE 8 should drive a wave of innovation as more than 10 million developers who already know Java employ the platform to build cloud-native microservices that can be deployed using containers on Kubernetes platforms. In fact, he said, the number of cloud-native applications based on microservices that will be built and deployed in the enterprise will soon accelerate. As that transition occurs, the number of organizations embracing best DevOps processes to manage those applications also should significantly increase because the rate at which Jakarta applications will be built will be faster than Java applications historically have been built.

    Collectively, Milinkovic also noted that despite the rise of rival programming languages, these and other forthcoming efforts will drive a resurgence in interest in Java programming languages that will ensure Java’s continued dominance of enterprise IT environments for many years to come.

    Of course, the primary reason IT vendors are excited is they no longer need to pay royalties to Oracle. It’s not clear how much of those savings might be passed on to IT organizations. What is apparent is that organizations that are required to employ open source technologies whenever possible are going to be a lot happier now that Jakarta EE 8 has finally arrived.

    — Mike Vizard