Welcome to The Long View—where we peruse the news of the week and strip it to the essentials. Let’s work out what really matters.
This week: The EU wants to put servers in orbit, a GDPR penalty for Discord, and Amazon has the hatchet out. (more…)

Welcome to The Long View—where we peruse the news of the week and strip it to the essentials. Let’s work out what really matters.
This week: The EU wants to put servers in orbit, a GDPR penalty for Discord, and Amazon has the hatchet out. (more…)

We are excited to announce the finalists for the DevOps Dozen² Awards 2022, celebrating the greatest innovators and their achievements in the DevOps space. These individuals and companies have taken an active role in the DevOps community, demonstrating their leadership and commitment to the improvement of our industry in the past year.
Congratulations to every one of the finalists. All of your hard work and dedication are greatly appreciated.
Without further ado, here are the finalists for the DevOps Dozen² Awards 2022:
1. Best DevOps Industry Implementation
2. Best DevOps Survey/Analysis/Research
3. Best DevOps-Related Video Series (video)
4. Best DevOps-Related Audio Podcast Series
5. Best DevOps Book/eBook of the Year
6. Top DevOps Evangelist
7. Best DevOps Transformation (non-vendor)
8. Best DevOps Event of the Year
9. Most Innovative DevOps Open Source Project
10. DevOps Executive of the Year (non-vendor)
11. Best DevOps Presentation of the Year
12. Best DevOps.com Article of the Year
1. Best End-to-End DevOps Tool/Service
2. Best DevOps Repo/GitOps Tool/Service
3. Best CI/CD Tool
4. Best Value Stream Management Tool
5. Best Observability Solution
6. Best DevSecOps Solution
7. Best Testing Service/Tool
8. Best Kubernetes Platform/Service
9. Best Cloud-Native Security Solution/Service
10. Best DevOps for Mainframe Solution
11. Best DevOps for DataOps/Database Solution
12. Best New DevOps Tool/Service Provider
Finalists were picked by the judges and based on which entry had the most nominations. All finalists will receive a badge to display on their website and social media with a link to the voting/survey site.
Voting for the winners in all 24 categories is now open to the public. To vote for the leaders, tools and companies you think are truly deserving of an award for their exceptional service to the DevOps community, please visit the DevOps Dozen² website.
Winners will be chosen from among the finalists, with general public voting weighted for 40% of the final score and our judges’ selections for 60% of the final score. The deadline for public voting is December 31 at 5:00 p.m. ET.
The winners will be announced at the Predict 2023 Virtual Summit on January 12, 2023, and will receive both digital badges and physical trophies celebrating their achievements.
Thanks to everyone who has supported the DevOps Dozen² Awards by nominating candidates and voting. Good luck to all the finalists!

Atlassian today added a range of capabilities to its Jira project management application that make it easier to manage software development projects, including a toolchain page that simplifies tool discovery for any given project.
In addition, Atlassian is including a Discover tab on that page that makes it possible to track activities and set priorities by providing more context around the goals for any given project.
Atlassian said it also plans to add scope change insights later this month and, in the first quarter of 2023, auto-detection of stuck issues will be added to an existing ability to predict when application development projects will be completed.

The company has also added a pull request activities feed to the Code tab in Jira to make it easier to compare and contrast issues, identify anomalies and discover opportunities to move work forward along with a Code insights view for tracking branch, commit, pull request and deploy activities.
The Releases tab in Jira now surfaces feature flag status alongside development, build and deployment statuses. There’s also an ability to automatically generate release notes in the Confluence wiki application provided by Atlassian. Finally, in 2023, Atlassian is committing to making available a dark mode option for running Jira that some DevOps teams prefer.
Suzie Prince, head of product for DevOps at Atlassian, said all these Jira updates are extensions of an Open DevOps initiative the company launched earlier this year that integrated Jira with a wide range of DevOps tools. The goal is to make it simpler for DevOps teams to track project progress without necessarily having to deploy, for example, a separate analytics application. As part of that effort, Atlassian also revealed Jira has been integrated with Compass, an extensible catalog launched earlier this year for tracking software components and is available in beta.
In effect, Atlassian is making a case for Jira to become a software development project tracking hub by automatically pulling data from various other DevOps tools. Rather than requiring a project manager to send multiple requests for updates to individual developers and manually enter data, Jira’s integrations with various tools can both pull relevant data and apply analytics in a way that makes it simpler to identify issues that are adversely impacting deadlines.
Those insights can then be shared more easily with both development teams and other stakeholders in the business that have a vested interest in making sure project deadlines are met. It can also make it simpler for application development teams to justify the need for additional resources.
Project management is, of course, one of those thankless tasks that doesn’t always get the appreciation it deserves. However, as it becomes easier to automatically collect data about the status of any given project, the task itself should become less intrusive. Hopefully, as those tasks become more automated, the friction that often exists between application development teams and project managers will also subside.

Fiberplane today announced it is making available a public beta of a namesake real-time collaboration notebook specifically designed for DevOps teams that need to quickly debug IT infrastructure.
Fiberplane CEO Micha Hernandez van Leuffen said in the wake of the COVID-19 pandemic, it’s clear that the structure of DevOps teams has permanently changed now that more members of those teams work remotely. The challenge is that the tools provided to DevOps teams to manage IT environments were not designed to foster the level of collaboration that is now required, he added.
Dashboards that were designed in a different era need to be replaced with tools that make it simpler for DevOps teams to collaboratively debug infrastructure in real-time, noted Hernandez van Leuffen.
The Fiberplane notebook achieves that goal by using the same operational transformation algorithm used in Google Docs to enable teams to easily collaborate around a document or spreadsheet. The core platform itself is built in Rust and WebAssembly (Wasm), which Hernandez van Leuffen said makes it simpler to integrate Fiberplane as a plug-in into an existing DevOps workflow. Inside a Fiberplane Notebook, DevOps teams can, for example, write and run PromQL queries and display Prometheus charts alongside other data presented via an integrated graph.
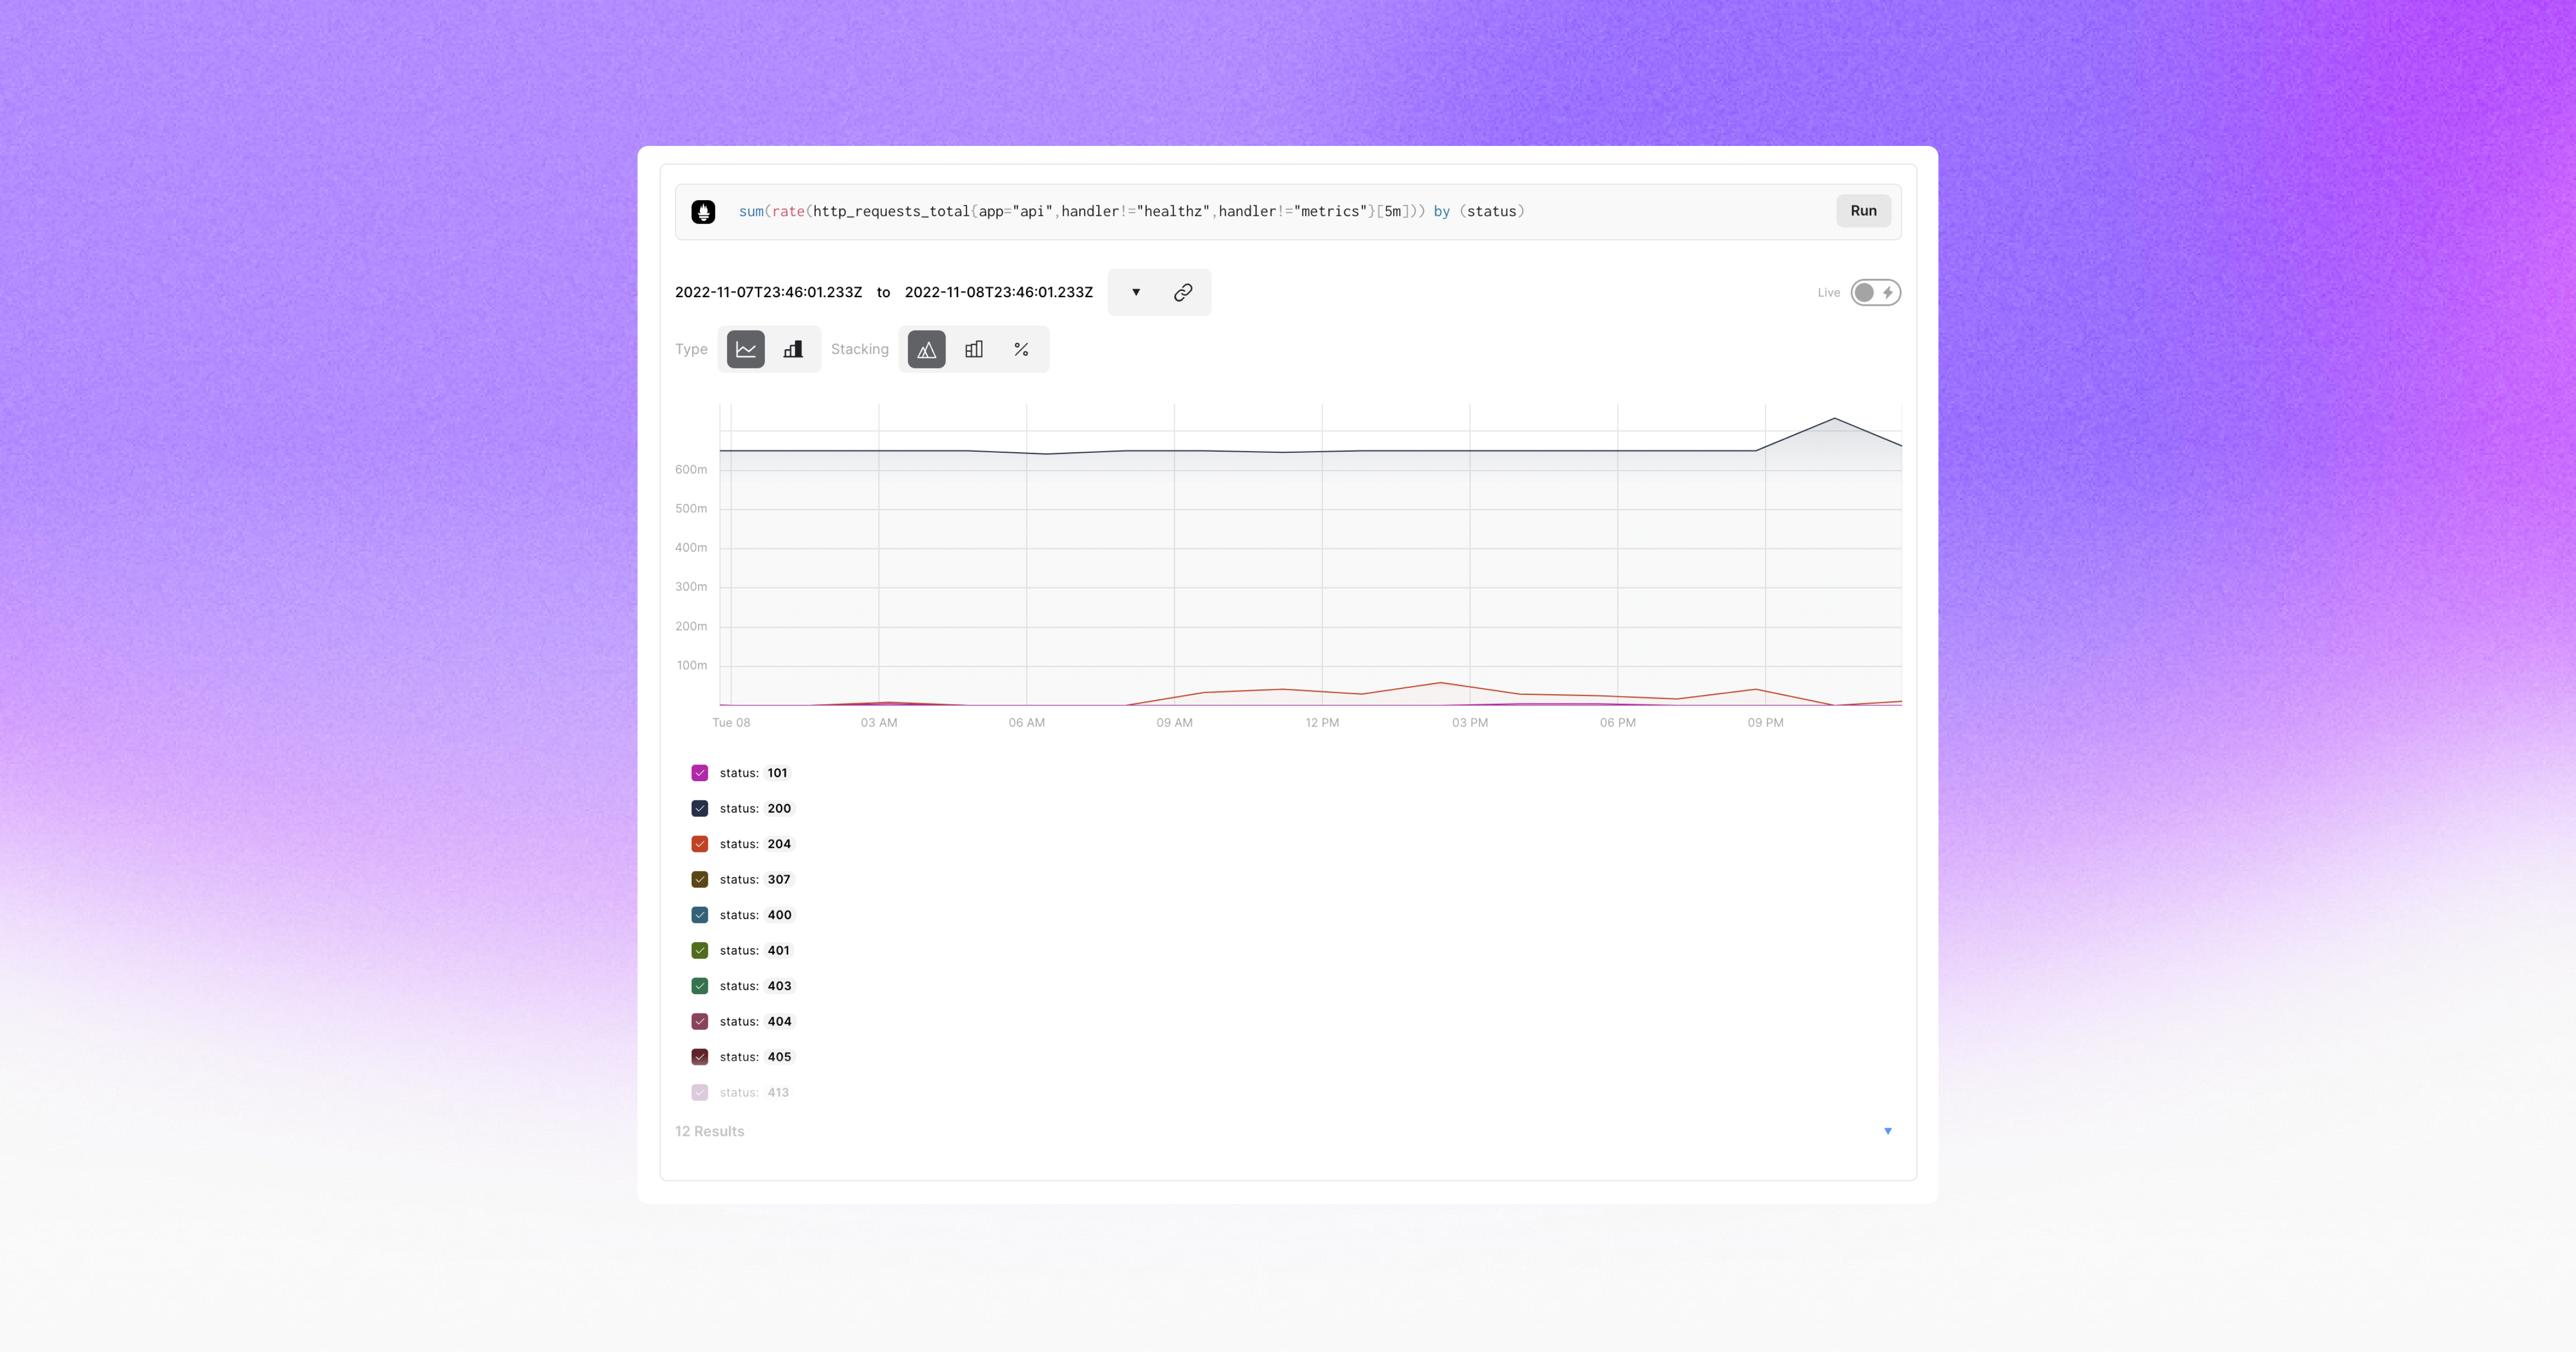
Fiberplane Notebook’s initial integrations are for Grafana Loki, Elasticsearch and Prometheus monitoring tools. It also exposes both an application programming interface (API) and command line interface (CLI) to automate notebook creation based on specific external events, such as monitoring alerts.
In effect, Fiberplane is taking the concept of notebooks used for collaboration by data science teams and applying it to DevOps workflows, said Hernandez van Leuffen. The goal is to improve DevOps teams’ productivity by reducing the amount of time it takes to resolve any issue, he added.
As IT environments become more distributed in the age of the cloud and microservices, troubleshooting issues invariably spans the responsibilities of multiple members of an IT team. Fiberplane, in effect, makes it possible to spin up a virtual war room that enables the members of an IT organization to collaborate until the issue of the moment is resolved.
The speed at which any IT issue is resolved has become a crucial metric. Given the complexity of IT environments, it’s inevitable that incidents will arise. Ideally, IT teams would discover those issues before they disrupt the business. However, in reality, the metrics organizations use to evaluate the effectiveness of a DevOps team are, unfairly or not, how quickly IT issues are resolved once they are discovered. The longer it takes for a distributed DevOps team to marshal its resources the more likely it becomes that team will be perceived as being inefficient—regardless of what level of application availability is actually achieved.
Savvy DevOps teams, of course, have implemented a wide range of incident management best practices that create a level of muscle memory for responding to a wide range of issues. The trouble is there will always be unforeseen issues that arise. DevOps teams, as a result, need to find ways to quickly focus on an issue that, for one reason or another, were simply too unpredictable to anticipate; they need to expect the unexpected.

At the SAP TechEd 2022 conference, SAP SE today announced it has added a low-code platform, dubbed SAP Build, to its portfolio to make it simpler for organizations to build custom applications.
Sebastian Schrötel, vice president and head of low-code/no-code solutions for SAP, said SAP Build is designed to make the company’s low-code tools more accessible to a wider range of developers, including so-called citizen developers that generally don’t have a lot of programming expertise.
The goal is to make it possible to monitor, analyze and automate processes by leveraging more than 500 templates available within SAP Build. The goal is to make it possible to not only build applications faster but also deploy them via a single click, said Schrötel.

The company’s approach to building custom applications separates its core applications from code developed by others by running pristine instances of SAP enterprise resource planning (ERP) applications in a separate cloud, known as the SAP digital core. A custom application is then deployed in a separate cloud and accesses SAP data via application programming interface (API). That approach enables SAP to update its ERP environment without worrying about breaking custom extensions.
Of course, not every organization has transitioned to that model, so there are still plenty of instances of SAP software running in on-premises IT environments extended using code written in Java or the proprietary ABAP programming language. Over time, SAP is hoping that custom code will either be retired in favor of a process it has added to its ERP platform or by a more modern instance of that process running with a custom application deployed on a separate SAP cloud platform.
SAP also has partnerships with providers of low-code platforms like Mendix and OutSystems that organizations can employ to build applications, but with the launch of SAP Build, the company is making a more concerted effort to encourage organizations to adopt the low-code platform it developed.
While it’s not clear how eagerly low-code tools are embraced by citizen developers versus professional developers, the one thing that is certain is the pace of application development is accelerating. In many instances, professional developers are embracing low-code platforms as an alternative to procedural code to reduce expanding application development backlogs brought on by digital business transformation initiatives. In other instances, professional developers are employing low-code tools to collaborate more easily with end users as they build and deploy the applications that drive those processes.
Regardless of the motivation, the impact this accelerated rate of application development will have on DevOps teams is profound. Not only do these applications have to be deployed in production environments, but DevOps teams must also secure and maintain a much larger application portfolio. As a result, the need to automate DevOps workflows will become more pronounced than it already is.
Oxeye today disclosed that it has discovered a critical vulnerability in the open source Backstage software used to build developer portals. Backstage was originally created by Spotify.
A 1.5.1 update to the Backstage platform remediated a sandbox escape vulnerability that can occur via a third-party Scaffolder plug-in that could be used to conduct unauthenticated remote code execution (RCE).
Oxeye CTO Ron Vider said Oxeye worked with Spotify to responsibly disclose the issue and enabled a patch to be created prior to the disclosure of the vulnerability, which Spotify gave a 9.8 out of 10 severity rating.

Backstage is now being advanced under the auspices of the Cloud Native Computing Foundation (CNCF), but is already widely used by organizations such as American Airlines, Netflix, Splunk, Fidelity Investments, Epic Games and Palo Alto Networks, as well as by Spotify.
The vulnerability is another example of a potential template-based attack through which run shell commands can be manipulated to inject malware into an application development environment.
In general, separating the logic from the presentation layer as much as possible can greatly reduce exposure to the most dangerous template-based attacks.
Vider said Oxyeye is focusing its vulnerability research on cloud-native platforms such as Backstage that are generally being used to build modern applications based on a microservices architecture. It’s not clear to what degree organizations have transitioned away from more monolithic approaches to building applications, but it’s clear that a much larger percentage of applications are now being constructed using microservices.
Cybercriminals, of course, are targeting these platforms as part of a sustained effort to compromise software supply chains in the hope that the malware they inject will find its way into multiple downstream applications. Those attacks, in turn, are convincing more organizations to embrace DevSecOps best practices to better ensure the integrity of their software supply chains. The challenge is many of those attacks are being aimed at open source software projects that don’t always have enough resources to quickly develop a patch in the event a zero-day vulnerability is disclosed.
While it’s impossible to know the extent to which cybercriminals are already exploiting vulnerabilities in DevOps platforms, the level of cybersecurity scrutiny being applied has dramatically increased in the wake of a series of high-profile breaches. The Biden administration has even gone so far as to issue an executive order requiring federal agencies to better secure their software supply chains. As a result, DevOps teams should expect there to be a lot more DevOps platform vulnerability disclosures in the months ahead, and that those vulnerabilities will require immediate patching.
Like it or not, software supply chains are going to become more secure. The only thing left to be determined is the level of pain that will be experienced as more vulnerabilities are discovered in the DevOps platforms that were used to construct them.

DevOps.com is now providing a weekly DevOps jobs report to highlight career opportunities for DevOps professionals as part of an effort to better serve our audience.
Our goal in these challenging economic times is to make it easier for DevOps professionals to advance their careers.
Of course, the pool of available DevOps talent is still relatively constrained, so when one DevOps professional takes on a new role it tends to create an opportunity for others.
The five job postings shared this week are selected based on the company looking to hire, the vertical industry segment and, naturally, the pay scale being offered.
We’re also committed to providing additional insights into the state of the DevOps job market. In the meantime, for your consideration:
Dice.com
ApTask
Remote
DevOps Architect
$160,000 to $200,000
SimplyHired
FluentStream
Remote
DevOps Engineer
$150,000 to $200,000
The College Board
Remote
Senior DevOps Engineer
$144,000 to $150,000
ZipRecuiter
Ushur
Santa Clara, CA.
Senior DevOps Engineer
$130,000 to $140,000
Indeed
Element 84, Inc.
Remote
Senior DevOps Engineer
$119,000 to $140,000

Aqua Security this week claimed it is the first software supply chain security platform provider to meet the attestation requirements as defined by an executive order issued to federal agencies last year by the Biden administration.
A supplementary memo issued by the Biden administration required federal agencies to collect compliance attestation letters for all software they use by September 14, 2023. Those attestation letters need to confirm that the software development environments they employ are secure, that sources of code are trusted and that code vulnerabilities have been remediated, provenance for data and code is being tracked using a software bill of materials (SBOM) and that these processes are being consistently maintained.
Eilon Elhadad, senior director of supply chain security for Aqua Security, said Aqua Security was able to meet those requirements within 100 days of the issuance of that memo. The Aqua Security platform for securing software supply chains is based on a platform it gained with the acquisition late last year of Argon, a provider of a set of tools that provides an agentless approach to integrating with continuous integration/continuous delivery (CI/CD) platforms that maps the development environment. Armed with those insights, it then becomes possible to prioritize and automate the remediation of vulnerabilities based on security best practices and compliance rules, noted Elhadad.
The Argon platform also includes code-tampering detection technology that performs validity checks to make sure the integrity of the build process has not been compromised.

Naturally, there’s plenty of time for other security platform providers to comply with the requirements set forth in Biden’s executive order. However, software development teams are also in a race against time. In the wake of a series of high-profile breaches, it’s become apparent how vulnerable software supply chains really are. Cybercriminals have increased their efforts to compromise developer credentials so they can embed malware in software components and activate them downstream if future application incorporate that component, noted Elhadad.
It’s not clear how closely enterprise IT organizations are tracking the efforts of the U.S. government to secure its software supply chain, but any entity that builds software used by any of those agencies will be impacted. Advocates of DevSecOps best practices within enterprise IT organizations will undoubtedly use the Biden administration’s requirements to define a minimum baseline for securing software supply chains.
In the meantime, a new front has clearly been opened in the cybersecurity war. The more applications are targeted, the greater the impetus for shifting responsibility further left toward application development teams becomes. The challenge is not just scanning the code being written by developers, but also making sure the software build created by development teams has not been compromised by bad actors that have inserted themselves into the process, noted Elhadad.
Given the magnitude of the effort required, it’s not likely that every software supply chain will be secured any time soon. However, the responsibility for securing those software supply chains is weighing more heavily on DevOps teams.

At the VMware Explore 2022 Europe conference, Hewlett Packard Enterprise and VMware, Inc. this week extended their alliance to integrate instances of the VMware Cloud platform into the managed HPE GreenLake service.
Hang Tan, chief strategy officer for HPE, said for the first time HPE is managing the entire VMware Cloud stack in addition to its servers and storage platforms via a service that is based on a consumption pricing model. The goal is to reduce the total cost of IT by not requiring IT teams to overprovision IT infrastructure resources to run VMware Cloud, he said.
Previously, IT teams could have deployed VMware Cloud on the HPE GreenLake service in a more disaggregated fashion, but that would have required separate billing processes, added Tan.
Many organizations are currently revisiting their IT strategies during increasingly challenging economic times, noted Tan. The managed HPE GreenLake service enables IT teams to devote more of their internal IT resources to building and deploying applications rather than managing IT infrastructure, he added.
It’s not clear how many organizations are transitioning toward a subscription model for consuming on-premises IT infrastructure, but in the cloud era it’s apparent that more of them are comfortable consuming IT as a service. HPE reported that the HPE GreenLake service supports more than 120,000 users accessing more than one exabyte of data worldwide. Among the top 100 HPE customers, nearly 80% have already adopted the HPE GreenLake platform, the company claims.
The challenge many organizations face is they still need to deploy and update application workloads in on-premises IT environments for both performance reasons and to meet various compliance mandates. The HPE GreenLake service is an effort to bring a cloud operating model to on-premises IT environments running not just VMware Cloud but also a wide range of other rival software stacks that HPE already supports.
Naturally, organizations that have embraced DevOps workflows would need to align the way they build and deploy applications to a managed service. IT teams that find that challenging, however, could opt for a self-service edition of the HPE GreenLake service that provides IT teams with more control over the underlying infrastructure being consumed as a service, noted Tan.
Regardless of approach, it’s apparent that some type of as-a-service approach to consuming IT infrastructure is being more widely employed across what are becoming highly distributed computing environments. Each organization will need to determine for itself to what degree treating IT more as an operating versus capital expense makes the most economic sense.
However, there’s no doubt that infrastructure cycles are generally going to be less disruptive when they are included as part of a multi-year services agreement. IT teams may also find it easier to take advantage of ongoing artificial intelligence (AI) advances when IT environments are managed on their behalf by a vendor.
One way or another, the way IT infrastructure is managed is continuing to evolve at a time when organizations are starting to focus more of their efforts on applications that are becoming more difficult to build, deploy, secure and maintain.

At the VMware Explore 2022 Europe conference, IBM this week announced an IBM Cloud for VMware-as-a-Service offering that integrates instances of VMware Cloud with the infrastructure-as-a-service (IaaS) platform managed by IBM in the cloud.
Rohit Badlaney, vice president of product management and strategy for IBM Cloud, said now that VMware Cloud can be consumed as a subscription service, it’s now possible for IBM to integrate it with its cloud platform to create a fully managed service. Previously, IT organizations would have had to separately license VMware Cloud and deploy it on IBM Cloud themselves, he noted.
In general, Badlaney said IBM is focused on working with organizations in highly regulated industries that need to run complex workloads in the cloud. IBM is not interested in competing against other cloud service providers to run workloads on commodity infrastructure, he added.
The majority of applications that run in the cloud today consume a narrow range of memory and storage resources. The IBM cloud is clearly more focused on providing higher-margin services to complement the cloud infrastructure it makes available via its data centers. Less clear is to what degree monolithic applications running in on-premises IT environments are being lifted and shifted to the cloud. While there is clearly a segment of organizations that no longer want to operate their own data centers, the bulk of applications continue to run in on-premises IT environments. The reasons for this include everything from performance requirements and security concerns to regulatory compliance issues.
However, since most on-premises applications run on VMware virtual machines, much of the focus on cloud migration has revolved around platforms that would not require IT teams to refactor applications to run on a different virtual machine platform. IBM is also betting that, given the current state of the global economy, more organizations will soon be opting to not manage their own data centers. Cloud platforms managed by a third party would enable those organizations to focus more of their own internal IT efforts on application development and deployment.
Each organization will need to determine for itself whether to treat IT as an operating versus a capital expense, depending on which approach makes the most economic sense. Organizations that have embraced DevOps workflows would need to align the way they build and deploy applications to a managed service.
In theory, of course, a managed cloud computing service makes IT teams more agile and efficient. Less IT infrastructure winds up being overprovisioned by developers that can programmatically spin up resources on demand. Of course, there are a lot of IT stacks other than VMware Cloud that can be deployed in the cloud. IBM, for example, makes available the Red Hat OpenShift platform to run cloud-native applications on Kubernetes clusters. IBM has not yet committed to offering the VMware Tanzu platform for running those types of applications.
Not every application is going to wind up running in the cloud, but what is certain is that application environments are becoming more complex to manage in the next era of cloud computing.