Category: Features

  • DevOps Dozen² Awards 2023 Nominations Now Open

    DevOps Dozen² Awards 2023 Nominations Now Open

    We are excited to announce that the DevOps Dozen² 2023 nominations are now open. Now in its ninth year, the DevOps Dozen once again highlights the leading innovators in the DevOps world. 

    As we’ve done the last three years, there are actually 24 award categories. Twelve are aimed at the many great commercial DevOps solution categories in the market. The other twelve are aimed at the vibrant community and open source ecosystem which powers the DevOps movement. 

    As in years past, the selection process has two tiers. Nominations for finalists are open now and will close on October 20, 2023. We will announce the finalists on November 13, 2023. After the finalists are announced, open voting will be conducted to determine the winners in each category. Public voting accounts for 40% of the weighted final count, with 60% coming from the votes of this year’s panel of judges.

    This year’s judges are myself, Alan Shimel, CEO of Techstrong Group, Mitchell Ashley, CTO of Techstrong Group, Sharon Florentine, managing editor of DevOps.com, and John Willis, DevOps luminary and author. As we’ve done in past years, we are asking the 12 companies that receive commercial category nominations to pay a nominal fee to cut down on spam submissions and help cover the cost of tracking the nominations, trophies and other administrative expenses. Community awards remain free to nominate but spamming nominations will result in disqualification.

    We have not changed the categories from last year, though we did consider adding a category for AI in DevOps. Perhaps next year. Without further ado, here are the 24 categories for the DevOps Dozen awards:

    DevOps Dozen Tools and Services Awards

    • Best End-to-End DevOps Tool/Service
      Consolidation in the DevOps space has led to a greater selection of platforms offering end-to-end solutions. This award honors the platform with the most diverse and robust solution for DevOps teams.
    • Best DevOps Repo/GitOps Tool/Service
      GitOps has become an integral part of the DevOps toolbox. This award is presented to the most outstanding code repository/Git/GitOps tool.
    • Best CI/CD Tool
      This award recognizes the best CI/CD tool that helps teams to deliver quality code faster.
    • Best Value Stream Management Tool
      Value stream management has come into its own as an important tool for measuring the business value of DevOps and application development. This award recognizes the value stream management tool that most effectively helps organizations visualize the value stream, track metrics and measure improvement.
    • Best Observability Solution
      This award recognizes the best observability solution for understanding the performance of individual components, systems and entire applications.
    • Best DevSecOps Solution
      This award honors the best DevSecOps solution, which enables security to be included earlier in and continuously throughout the SDLC.
    • Best Testing Tool/Service
      Testing is a mainstay in the DevOps toolchain. This award recognizes the best testing tool for ensuring the quality of code.
    • Best Kubernetes Platform/Service
      The adoption of containers has paved the way for an entire solutions ecosystem. Kubernetes is perhaps the most widely recognized and utilized tool for container orchestration. There are many platforms and services that offer Kubernetes-based solutions. This award honors the best Kubernetes platform/service available.
    • Best Cloud-Native Security Solution/Service
      The cloud-native movement has taken the IT world by storm due to the depth and breadth of the solutions available and the benefits of building applications and services specifically for cloud-native environments. This award recognizes the best cloud-native tools, solutions and services.
    • Best DevOps for Mainframe Solution
      Despite their age, mainframes are a mainstay in the IT world, and a variety of solutions are available for enabling DevOps practices in mainframe and hybrid environments. This award recognizes the best of them.
    • Best DevOps for DataOps/Database Solution
      Databases often have been left out of the DevOps conversation, but that is changing  as the concept of DataOps is gaining greater traction. This award recognizes the best solution in the database and DataOps space.
    • Best New DevOps Tool/Service Provider
      This award recognizes the best new service provider or tool that has brought innovation to the DevOps space in the past year (must be less than 24 months old).

    DevOps Dozen Community Awards

    • Best DevOps Industry Implementation
      This award honors organizations that have successfully adopted and implemented DevOps principles and practices.
    • Best DevOps Survey/Analysis/Research
      This award recognizes research that has significantly and positively impacted the DevOps community.
    • Best DevOps-Related Video Series (video)
      This category highlights the most entertaining, educational and inspirational DevOps video series—those with the most engaging and highest-quality content.
    • Best DevOps-Related Audio Podcast Series
      Which is your favorite DevOps podcast from this year? This category celebrates the many great DevOps podcasts driving discussions about everything from CI/CD and testing to DevSecOps, Kubernetes, containers and more.
    • Best DevOps Book/eBook of the Year
      Each year sees a plethora of well-crafted DevOps-related books and ebooks. This category highlights the most popular and  most-read of the year.
    • Top DevOps Evangelist
      This category is one of our favorites! There are so many great evangelists who spread the DevOps gospel, but we want to know who does it best. Nominees can work within the DevOps space or outside of it.
    • Best DevOps Transformation (non-vendor)
      In a year marked by continued digital transformation, we want to know which organizations stood out in their efforts to transform their business through DevOps.
    • Best DevOps Event of the Year
      Virtual events became the norm throughout  the pandemic. But as more people crave face-to-face interaction, in-person events have slowly made a comeback. Which DevOps event stands out from the crowd?
    • Most Innovative DevOps Open Source Project
      Open source projects are meant to promote innovation and increase efficiency, velocity and quality. While there are many great open source projects out there, the best ones are those that create a community of people who work on and with the technology and support each other.
    • DevOps Executive of the Year (non-vendor)
      This category celebrates excellence among DevOps leaders at the C-suite (or equivalent) level.
    • Best DevOps Presentation of the Year
      This category recognizes the best DevOps-themed presentation from the many (virtual) conferences that took place this year.
    • Best DevOps.com Article of the Year
      This category celebrates excellence among DevOps leaders at the C-suite (or equivalent) level.

    Good luck to everyone nominating for the DevOps Dozen² Awards 2023. We will update finalists on November 13.

  • Should You Measure Developer Productivity?

    Should You Measure Developer Productivity?

    A recent McKinsey article entitled ‘Yes, you can measure software developer productivity‘ has got the software developer community talking. And the general consensus is they’re not happy.

    Most software developers are not enthusiastic about the prospect of having their individual performance metrics monitored. “Anyone who attempts to measure software in some sort of scientific way is just doing the wrong thing,” said YouTube personality ThePrimeTime. Dave Farley of Continuous Delivery even goes as far as to call the McKinsey report “harmful dribble.”

    This debate arises as developer productivity engineering (DPE) is gaining traction as a means to improve developer performances and, perhaps, in response to employment landscape shifts like the Great Resignation, which saw developers and DevOps pros leaving their roles. Companies like Spotify, LinkedIn, Netflix and others are also investing in internal developer platforms (IDPs) to increase developer productivity and satisfaction amid a limited talent supply.

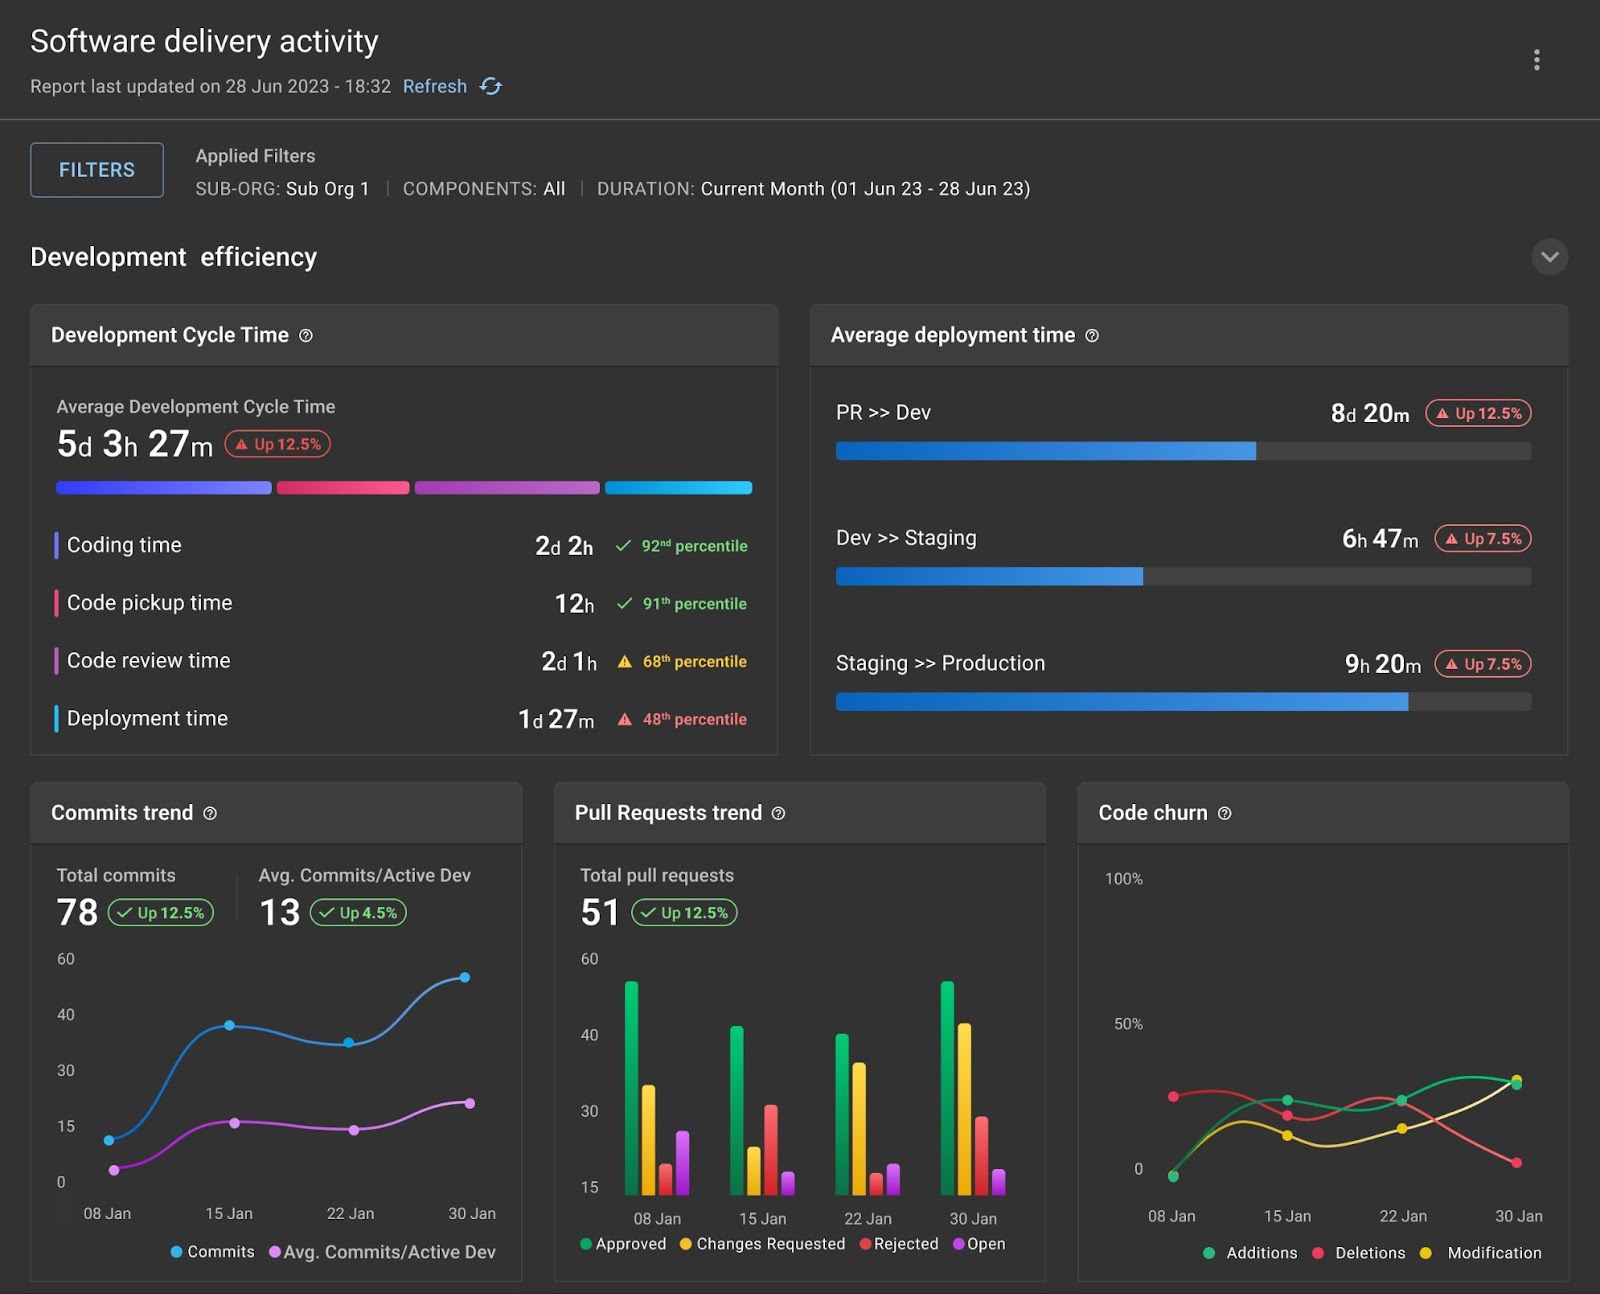
    Alongside these ambitions, much has been written about how managers can measure developer productivity in terms of qualitative metrics, like developer satisfaction, as well as quantitative metrics, like number of commits or story points, deployment frequency or failure rates. But can tracking such metrics deliver tangible results? Or do they go too far?

    Below, we’ll consider whether you can actually measure software developer productivity. But more than that, we’ll evaluate whether this is a meaningful tactic with desirable outcomes.

    Ways to Measure Development Productivity: DORA

    First, let’s look at some of the standard techniques to measure development productivity. The DORA metrics, produced by the DevOps Research and Assessment (DORA) team at Google after years of research, identified four key metrics:

    1. Deployment frequency: How often you ship changes.
    2. Lead time for changes: The time between a commit and it reaching production.
    3. Change failure rate: The percent of releases that fail; downtime, worsened service or rollbacks.
    4. Time to restore service: The average time it takes to respond to an issue, also known as mean-time-to-recovery.

    These metrics could be helpful indicators of a software development team’s overall agility and health. They can signal bottlenecks in the CI/CD process or highlight where too much time is spent remediating issues, encouraging positive changes. Solving these root causes could all improve a team’s productivity.

    Going Beyond DORA: SPACE

    DORA also added reliability to the list. That’s understandable, given the interest in building reliable systems. But things start to get a little more complex when SPACE enters the equation.

    Proposed in a 2021 paper by GitHub researchers, SPACE augments DORA with the following attributes:

    • Satisfaction and well-being
    • Performance
    • Activity
    • Communication and collaboration
    • Efficiency and flow

    Metrics like satisfaction or communication and collaboration are pretty subjective. Plus, it can be challenging to gather this data and encourage engineers to speak honestly in surveys. Measuring the activity of individual members, like the number of issued closed or pull requests made, isn’t exactly tied to end value and could even produce a negative psychological effect.

    “Consequently, teams can become fixated on them, as seemingly positive changes are relatively easy to achieve,” wrote James Walker. He adds that SPACE still doesn’t tell you why measurements have value—furthermore, it lacks actionable information and might be tricky to implement, given developer pushback against performance analysis systems.

    Opportunity-Focused Metrics

    The McKinsey report adds to the mix what it calls “opportunity-focused productivity metrics,” which include inner/outer loop time spent, a Developer Velocity Index benchmark, contribution analysis and a talent capability score. (It’s not totally clear how these metrics can be computed). It then organizes all these metrics into a framework that further segments measurements into system, team and individual levels.

    McKinsey's framework for measuring developer productivity

    While some believe in the framework’s legitimacy, many commentators don’t see the practicality of implementing such a framework in practice. “Introducing the kind of framework that McKinsey is proposing is wrong-headed and certain to backfire,” wrote the PragmaticEngineer.com. “The report is so absurd and naive that it makes no sense to critique it in detail,” wrote Ken Beck.

    Things to Avoid With Developer Productivity Metrics

    Apparently, developers are very weary of being measured. And given the recent backlash, it seems like overreliance on productivity metrics could negatively impact the engineering culture. So, engineering leadership should be careful when implementing these sorts of tactics. Here are some anti-patterns to consider.

    Don’t make it about individual performances. Metrics like DORA have become standards for measuring the efficiency of software teams, but they shouldn’t be applied at the individual level. “Measuring software development in terms of individual developer productivity is a terrible idea,” said Dave Farley. Technology development is more of a collaborative process; performance metrics should reflect how the team operates.

    Don’t measure developer productivity in isolation. On that note, performance metrics shouldn’t be judged in isolation. Issues with failures, for example, often depend on contexts outside of an individual developer’s control. At the same time, it can be hard to correlate individual developer contributions to end customer satisfaction.

    Don’t create an opportunity to gamify productivity systems. Leadership shouldn’t directly tie a developer’s salary, reputation or position to whether or not they hit certain metrics. If productivity systems carry this much weight, they could become gamefied.

    Don’t put in more effort than it’s worth. In tech, where there’s hype, there’s money to be made—and a host of vendors ready to hawk monitoring tools. What’s more, to enact these productivity measurement enhancements, McKinsey noted that “most companies’ tech stacks will require potentially extensive reconfiguration.” Devoting many engineering resources to monitor engineers just seems like a big pill to swallow.

    Don’t put too much faith in metrics. Lastly, metrics only show one side of the picture. They are only data points and can’t always depict what it’s really like on the ground. Furthermore, qualitative responses also might be skewed due to reluctance to speak up.

    Remember Goodhart’s Law and Focus On Quality

    Personally, I believe that measuring things like developer productivity, efficiency, experience and satisfaction does have some merit for some businesses. Most teams are now working asynchronously, and metrics help leaders take the pulse of a team’s performance, even if they are all remote workers.

    It’s also nothing new. Leadership has been attempting to measure developer productivity for years. But, these metrics often lack context and come with many caveats to consider. Thus, they shouldn’t be given a huge seat at the table.

    I like this ‘law’ from British economist Charles Goodhart, which is colloquially summarized as “when a measure becomes a target, it ceases to be a good measure.” In other words, when you start working for the metrics, the engineering culture and overall code quality might decline. This matters, since a separate study found that increases in code quality tend to be followed by an increase in developer productivity.

    So, focus first on establishing code quality and, hopefully, productivity will flow.

  • Five Great DevOps Job Opportunities

    Five Great DevOps Job Opportunities

    DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted to better serve our audience.

    Our goal in these challenging economic times is to make it easier for DevOps professionals to advance their careers.

    Of course, the pool of available DevOps talent is still relatively constrained, so when one DevOps professional takes on a new role it tends to create an opportunity for others.

    The five job postings shared this week are selected based on the company looking to hire, the vertical industry segment and, naturally, the pay scale being offered.

    We’re also committed to providing additional insights into the state of the DevOps job market. In the meantime, for your consideration:

    CareerBuilder.com

    The DarkStar Group
    Fairfax, Virginia
    AWS DevOps Engineer (Security Clearance)
    $250,000

    Indeed.com

    Dutch Bros. Coffee
    Grants Pass, Oregon
    Senior DevOps Engineer
    $139,473 to $161,688

    LinkedIn

    Claravine
    Remote
    DevOps Engineer
    $105,000 to $115,00

    SimplyHired.com

    Motorola Solutions
    New York, New York
    Infrastructure Operations Engineer
    $93,620 to $180,000

    Dice.com

    Scholastic Inc.
    New York, New York
    Associate DevOps Engineer
    $58,500 to $93,500

  • DevOps is Making Gains on Mainframe Platforms

    DevOps is Making Gains on Mainframe Platforms

    A survey of 800 executive and technical professionals conducted by BMC found close to two-thirds (62%) are employing DevOps workflows to build and deploy applications.

    In addition, the survey also finds that just under a third of respondents (32%) are applying artificial intelligence to IT operations (AIOps) across all platforms.

    John McKenny, senior vice president and general manager of intelligent Z optimization and transformation at BMC, said the survey shows that organizations continue to invest in mainframe applications alongside distributed computing environments.

    In fact, 61% of respondents noted that data volume on mainframes increased in the last year, with 56% reporting an increase in the number of databases running. Well over a third of respondents (35%) also reported increased interest in taking advantage of cloud technologies to handle, for example, storage and data protection.

    Overall, the survey found that 94% of respondents have a positive perception of the mainframe, with nearly two-thirds (63%) reporting increased mainframe investments over the past year.

    Compliance and security lead the list of priorities for mainframe organizations, with 61% of respondents citing these as top issues, followed by cost optimization (49%), enhancing automation (41%) and data recovery (40%).

    In general, organizations with mainframes are adopting modern application development tools such as VS Code to attract a younger generation of developers. It’s critical to continue to attract developers to mainframe platforms that continue to run the most mission-critical applications in the enterprise, said McKenny. Many of those applications are being modernized using DevOps tools and practices rather than being moved to another platform, he added.

    He added that the appetite for using generative artificial intelligence (AI) to write code for mainframe applications is less clear because of intellectual property concerns. Most organizations are not going to want to expose their mainframe code to a general-purpose large language model (LLM) that drives a public generative AI platform, but there will be a role for private LLMs that are trained using code that has been validated, noted McKenny.

    Regardless of how generative AI evolves, there’s still much work to be done to further the adoption of DevOps best practices in mainframe environments. Each organization will determine how stringently to apply those practices based on the frequency at which applications running on mainframes need to be updated. In most cases, organizations with mainframes will use a mix of waterfall and DevOps-based approaches to building and deploying applications for many years. The decision as to which approach to employ will, naturally, have as much to do with culture as it does the rate at which the application needs to be built and deployed to drive, for example, a digital business transformation initiative.

    The days when mainframes were managed in isolation from the rest of a distributed computing environment are slowly coming to an end. A mainframe is, arguably, just another node for deploying applications. The challenge and the opportunity now is getting the right DevOps tools in the hands of the IT team managing heterogeneous IT environments, including mainframes.

  • Summit Highlights Open Source Software Security Progress

    Summit Highlights Open Source Software Security Progress

    More than a year after the Open Source Security Foundation (OpenSSF) summit kicked off an initiative to better secure open source software-based software supply chains, a lot of progress has been made—but much work remains to be done.

    The OpenSSF this week hosted a Secure Open Source Software (SOSS) Summit 2023 event in Washington, D.C., during which it made available a Secure Open Source Software Vision Brief 2023. The brief describes the various efforts being made to improve open source software security, including, for example, providing maintainers of open source software projects with free DevSecOps tools.

    This week, the Cybersecurity and Infrastructure Security Agency (CISA) also published an Open Source Software Security Roadmap that defines its role in providing more visibility into how open source is being used and the associated risks.

    However, it’s not clear how much maintainers of these projects are embracing DevSecOps workflows. Many projects are led by a handful of maintainers that often lack the time and skills required to ensure the components they employ have not, for example, been compromised by malware that might find its way into downstream applications.

    Sonatype CTO Brian Fox said the focus of the summit’s participants will be on education and securing public code repositories. While there is a lot of focus on maintainers, he added that there is not enough attention to all the organizations that have not updated open source components within a software build with known vulnerabilities. Many IT teams are reluctant to upgrade components for fear of breaking applications with complex dependencies, but the amount of code that is potentially insecure is massive. “There’s a huge mountain to climb,” he said.

    The challenge is determining which code to upgrade first in a way that will have the most impact in terms of improving application security, added Fox.

    Shawn Ahmed, chief product officer for CloudBees, also noted that organizations should evaluate the DevSecOps processes being applied by maintainers of open source software projects. CloudBees, for example, reviews the plugins provided by the open source community for the Jenkins continuous integration/continuous delivery (CI/CD) platform for vulnerabilities every month, he noted.

    It’s also critical for organizations that consume open source software to contribute code to improve the security of open source software, added Ahmed. Too many organizations are focused on open source software security without devoting resources that would help resolve the issue. he added. “We need to make sure open source software is not a vulnerability threat,” said Ahmed.

    Moran Ashkenazi, chief strategy officer (CSO) and vice president of security engineering for JFrog, said on the plus side, there is a lot more awareness of open source software security issues since the disclosure of a zero-day vulnerability in the Log4j shell tool widely used to manage logs in Java applications. But added that this issue is not going to be resolved overnight. “That was a wakeup call,” she said.

    Tapabrata Pal, vice president of architecture for Fidelity Investments, noted that the fundamental problem is that cybercriminals have become more adept at injecting malware into software supply chains, so no one knows whether their application environments might be compromised. “It’s a serious issue,” he said.

    It’s not known whether the open source software that many developers routinely incorporate into their applications might contain vulnerabilities that could be exploited, but the level of technical debt that has accrued over the last several decades is considerable. The issue is finding a way to address it without becoming overwhelmed by the enormity of the task.

  • CloudBees CEO: State of Software Development is a Disaster

    CloudBees CEO: State of Software Development is a Disaster

    CloudBees CEO Anuj Kapur told attendees at a DevOps World event today that with developers spending only 30% of their time writing code the current state of software development in enterprise IT organizations is a disaster.

    After more than 14 years of effort, the promise of DevOps—in terms of being able to accelerate the rate at which applications are being deployed—remains largely academic, said Kapur. In fact, the effort to shift more responsibility for application security further left toward developers has only increased the amount of cognitive load and reduced the amount of time available to write code, he noted.

    However, with the rise of generative artificial intelligence (AI), an inflection point that will dramatically increase the velocity at which applications are being built and deployed has arrived, said Kapur. The challenge will be achieving that goal without increasing the cognitive load on developers. That cognitive overload results in 70% of developers’ time not being productive within organizations that often hire thousands of developers, he noted.

    Despite all the DevOps issues that need to be addressed, AI advances promise improvement. The overall DevOps market is still relatively young, given the current level of adoption, said Kapur. “We continue to believe the market is early,” he said.

    Today, CloudBees took the wraps off the first major update to the open source Jenkins continuous integration/continuous delivery (CI/CD) platform to have been made in the past several years. At the same time, the company also unveiled a DevSecOps platform based on Kubernetes that is optimized for building and deploying cloud-native applications based on portable Tekton pipelines. That latter platform provides the foundation through which CloudBees will, in the months ahead, apply generative AI to software engineering to, for example, create unit tests on the fly and automate rollbacks.

    In addition, DevSecOps capabilities will be extended all the way out to the integrated development environments (IDE) to reduce the cognitive load of developers.

    The overall goal is to reduce the number of manual processes that create bottlenecks that make it challenging to manage DevOps at scale.

    Criticism of the level of developer productivity enabled by DevOps compared to other development approaches needs to be tempered, said Tapabrata Pal, vice president of architecture for Fidelity Investments, because it still represents a significant advance. There is still clearly too much toil, but the issues that impede the pace at which developers can effectively write code tend to be more cultural than technical, he added.

    Organizations are not inclined to automatically trust the code created by developers, so consequently, there is still a lot of friction in the DevOps process, noted Pal.

    In theory, advances in AI should reduce that friction, but it’s still early days in terms of the large language models (LLMs) that drive generative AI platforms and their ability to create reliable code, he added. That should improve as LLMs are specifically trained using high-quality code, but in the meantime, the pace at which substandard code might be generated could overwhelm DevOps processes until AI is applied there as well, said Pal.

    Thomas Haver, master software engineer for M&T Bank, added that while assisted AI technologies will have a major impact, it’s not reasonable to expect large organizations to absorb them overnight. Patience will be required to ensure advances are made in ways that are both secure and sustainable, he added. In some cases, organizations may opt to build their own LLMs to achieve that goal, noted Haver. “You should not expect to change on a dime,” he said. “It will take time to see the fruits of our labor.”

    While many DevOps challenges need to be resolved, the benefits continue to outweigh the cost and effort required to succeed. The hope is that, with the help of AI, the return on those investments will continue to accrue.

  • Google De-Recruits 100s of Recruiters ¦ ARM Valued at $45½B in IPO

    Google De-Recruits 100s of Recruiters ¦ ARM Valued at $45½B in IPO

    Welcome to The Long View—where we peruse the news of the week and strip it to the essentials. Let’s work out what really matters.

    This week: Google fires hundreds of recruiters, and ARM gets a sky-high valuation. (more…)

  • ngrok Adds Load Balancing to Programmable Network Service

    ngrok Adds Load Balancing to Programmable Network Service

    ngrok today added a global server load balancing capability to its service for managing ingress via an application programming interface (API).

    Alan Shreve, ngrok CEO, said the ngrok Global Server Load Balancing (GSLB) service reduces latency and increases overall resiliency by automatically rerouting traffic across a global network of points-of-presence ngrok manages.

    The overall goal is to provide a higher level of abstraction for managing network operations (NetOps) that can be programmatically invoked. NetOps takes the place of what are essentially the equivalent of Assembly programming tools to provision networking equipment, he added. The long arc of computing is moving toward higher levels of abstraction to make IT capabilities more accessible, noted Shreve.

    That approach eliminates the need for IT teams to assign network operations teams to manage appliances in favor of a service that also provides a demilitarized zone (DMZ) via a service that accesses reverse proxies and firewalls, noted Shreve. The ngrok service ensures unauthorized requests are instantly blocked.

    The ngrok service provides a programmable approach to managing network services that makes it simpler for DevOps teams to invoke them. Instead of waiting for a network operations team to provision networking equipment, an API makes it possible to integrate the provisioning of networking services within the context of a larger DevOps workflow.

    One of the challenges that IT teams continue to encounter is that while virtual machines can be spun up in minutes, the provisioning of network services can require anywhere from minutes to days, depending on the age of the networking equipment. The ngrok service doesn’t eliminate the need for network professionals, but it does make it simpler for them to collaborate with application development and deployment teams, said Shreve.

    It’s not clear if NetOps teams will one day simply become an extension of a DevOps team, but as applications become more distributed, the need to minimize network latency is becoming more critical. A service like ngrok makes it simpler for DevOps teams to ensure the appropriate level of bandwidth is available so distributed application performance doesn’t slow to a crawl.

    Of course, the bigger challenge will be bridging the cultural divide that currently exists between many NetOps and DevOps teams. Both groups have their own distinct nomenclature for describing services that, in many cases, the other simply doesn’t comprehend. As distributed application development accelerates, each organization will need to determine how to demolish those silos so both teams can more easily achieve a common goal.

    In the meantime, IT leaders might to reconsider their strategy as networking services become increasingly programmable via APIs. Most modern networking equipment today is software-defined in the sense that network operations teams have access to graphical tools to provision networking equipment. However, as APIs become more accessible, the need for those graphical tools may not be nearly as high as it is today as networking becomes just another service to be managed as code.

  • CloudBees Unfurls Dual CI/CD Strategy at DevOps World Event

    CloudBees Unfurls Dual CI/CD Strategy at DevOps World Event

    During a DevOps World event, CloudBees took the wraps off the first major update to the open source Jenkins continuous integration/continuous delivery (CI/CD) platform made in the past several years.

    At the same time, the company also unveiled a proprietary DevSecOps platform based on Kubernetes that is optimized for building and deploying cloud-native applications based on portable Tekton pipelines.

    Shawn Ahmed, chief product officer for CloudBees, said the updates to Jenkins make it possible to horizontally scale Jenkins controllers while at the same time ensuring high availability. The latest update also provides a workspace caching mechanism to simplify sharing them across multiple jobs in a way that significantly reduces the amount of compute and storage resources consumed, he added.

    CloudBees also added a Baseline capability to the Jenkins repository to improve startup times without causing build storms.
    Collectively, those capabilities will increase the number of jobs that can be simultaneously executed to improve overall productivity, said Ahmed.

    CloudBees has also added a Pipeline Explorer tool in the cloud-based edition of Jenkins that enables DevOps teams to visually debug and troubleshoot pipeline jobs. That tool will also provide the foundations for self-healing and artificial intelligence (AI) capabilities that CloudBees plans to add to the Jenkins platform later this year and into 2024, added Ahmed. For example, AI tools will surface suggestions on how to fix a problem in a pipeline, he noted.

    The DevSecOps platform, meanwhile, leverages Tekton pipelines to provide DevOps teams with more granular control over how pipelines can be orchestrated, said Ahmed. It also provides access to GitHub Actions-style domain-specific language (DSL), support for feature flagging, security, compliance, pipeline orchestration capabilities, analytics and value stream management (VSM) tools that can be deployed by an internal IT team or accessed via a single or multi-tenant managed cloud service.

    Those built-in capabilities will make it simpler for platform engineering teams to centrally manage building and deployment of cloud-native applications by enabling developers to self-service their own engineering requirements via an internal developer platform (IDP), said Ahmed. The overall goal is to provide a more integrated approach that breaks down software engineering silos that exist in many existing DevOps workflows, said Ahmed.

    Each DevOps team will need to decide for themselves to what degree to move forward using Jenkins to build and deploy applications versus opting for a more modern alternative in the form of the DevSecOps platform. CloudBees, however, is committed to providing plug-ins and integrations across both platforms to enable DevOps teams to protect their investment in existing tooling, noted Ahmed.

    The status of Jenkins X, an open source CI/CD platform based on Kubernetes that CloudBees previously donated to the Cloud Delivery Foundation (CDF), is not immediately clear. Regardless of the approach, however, there is a clear opportunity to revamp DevOps workflows by upgrading Jenkins or switching to a more modern platform such as DevSecOps. The challenge, as always, is determining the pace at which any such transition might be made.

  • JFrog Launches New Channel Partner Program

    JFrog Launches New Channel Partner Program

    At JFrog’s swampUP event in San Jose, California, the company launched its Global Channel Partner Program. The program, led by Kelly Hartman, VP of alliances and partners, is JFrog’s first formal program to work with the channel to bring its DevOps and DevSecOps solutions to market.

    Rather than the traditional pyramid model, Hartman, who was formerly at AWS, has designed a flatter program; partners can choose to work with JFrog in a co-selling arrangement, as a traditional reseller or as part of JFrog’s government sales partners. Partners can choose which type of relationship they want to use on a case-by-case, deal-by-deal basis. This gives them lots of flexibility.

    This program is a sign of JFrog’s continuing evolution from a startup to a public company. Several of the founding channel partners in the program weren’t surprised at the announcement; the feeling was, as Mike King of IT Methods said, “They have been knocking on this door for some time.” Hartman added that the goal was not to make JFrog a 100%-channel company. Rather, the aim is to have as much business run through the partners as JFrog’s customers want while keeping the emphasis on the JFrog customer base.

    The program is primarily aimed at DevOps consultants worldwide, rather than the larger integrators, JFrog said. The DevOps consultant market is broadly fragmented, and made up of numerous sized companies – from one to two-person operations all the way up to 1,000+-person organizations, such as IT Methods.

    Hartman said she is learning from her past experience at AWS and other organizations. She has not crafted a traditional program with tiers and marketing development funds; instead, much of what partners need is built into a self-service portal, including a campaign in a box and social media kits.

    IT Methods is an ideal partner for JFrog, King said. They offer a fully-managed SaaS, single-tenant platform allowing their customers to manage their DevOps environments. IT Methods supports more than 45 DevOps tools and its major clients are large enterprises. They have offered JFrog via their platform for six years, but welcome the formal partner program and accompanying certification offered for SMEs. King said he was pleasantly surprised at the JFrog program’s maturity, considering it is a new program. He added that joint lead generation and closing capability and partner enablement offerings would put JFrog “at the head of the class.”

    The JFrog channel partner program joins their existing technology partner and cloud partner programs. In fact, Hartman said they are working with their cloud provider partners to source new channel partners. 

    It was an exciting new development in what promises to be a gangbuster swampUP here in San Jose. More developments will follow.