Category: Enterprise DevOps

  • There are Few Enough Silver Bullets

    There are Few Enough Silver Bullets

    I was working through this week’s blog this morning, and it was laser-focused on a narrow topic. I had examples of why too much of a good thing is bad, how absolutism about methodology is hurting the majority of organizations out there, and how to get past this issue to keep improving what IT does for the organization.

    And I was nearly done when I decided that there are far too many areas of IT that suffer from absolutism, so I’d offer general symptoms and steps that work to get out of any of them.

    What do I mean by ‘absolutism’? Well, it used to be—and, in a couple of areas, still is—true that people would say, “We are an X shop.” And mean it. If you were a Cisco shop in the 1990s or 2000s, that is all you bought. Competitors were not allowed; nor was consideration of competitors. This applies to methodologies as well as product categories. In fact, today it applies to various methodologies more than products.

    And it’s bad for the organization, no matter where it comes from. While with vendors, it streamlines purchasing and offers the (in)famous “single throat to choke”, it also causes inefficiencies in costs (from your perspective, they are a monopoly, and some large vendors gained infamy by trying to take advantage of that fact), and causes people to do things in the least efficient way because that’s what the chosen methodology/solution requires.

    Sometimes, we manage to do the dance and avoid “One True Way”—take the move to cloud and continuation to multi-cloud, for example. While cloud vendors do not offer customers much leeway in pricing or priority (we customers are all cattle, not kittens), multi-cloud still offers us the opportunity to use the cheapest or best-suited cloud vendor without much drama.

    Many times, we are not so effective at avoiding the idea of a silver bullet. Take Agile. If there was a One True Ring of this decade in IT, I’d want it to be containers, but it would actually be Agile. Most IT departments zealously guard that Agile is the One True Way. Early-stage new product development is astoundingly well suited to Agile, and we needed it—if just for that part. Late-stage product maintenance, where changes are not feature-laden monuments to systems complexity, are also really well-suited to Agile and we should be happy to have it. In between? Large updates that can span data centers—or even continents—with a geographically dispersed workforce and hundreds (or more) of hours of development to get one sub-feature completed? Not really a great fit for Agile, and while many of us have said that for years, here is hoping things are changing. As I’ve said before, as maligned as waterfall was, it did the job for decades and handles large complex projects well. Maybe we need a replacement more in line with the times; one that incorporates what we’ve learned from Agile. I’d love that, actually. But what we don’t need is “We’re an Agile shop.” It is less useful than when it was said about products (at least if you only chose a single product, you got single sourcing and streamlined purchasing. With methodologies, you don’t even get that).

    Note: Agile is an example, not the point of the post. Avoid “One True Way” across your organization. Root it out and examine it. Sometimes, a single solution with a single specialized skillset is the perfect answer—at least for now. Far too often, “We are an X shop” is someone’s preference codified into corporate policy.

    To get past One True Way, you have to be there showing its weaknesses to management. There is some skill overlap when allowing multiple approaches or products, but if management starts prattling about that, simply point out the number of development and/or CI/CD environments the org is currently supporting. To show the overhead, track hours spent. Staff shortages have been endemic to IT for years. Make certain you know how much time is spent in overhead for the product or process, and try to map that to what could have been achieved with that time. It’s not perfect, but it will be illustrative. And don’t stop. Do your work, but point out every time that One True Way makes the job harder or more expensive.

    You are nailing it. Don’t let things like Agile keep you from churning out great apps for the company. I’ve been on teams where the time spent in process overhead was dragging down the ability to deliver quality. Fight that. Keep kicking it, and use the best tools/processes for the job.

  • Saying Goodbye to Legacy Systems

    Saying Goodbye to Legacy Systems

    Are you still using a rotary phone, tube television or Rolodex? Probably not. But if you were, you’d still be using newer technology than what many enterprises still rely on every day to drive mission-critical applications that we use every day when shopping, banking or hundreds of other normal tasks. 

    At least two-thirds of large enterprises are running mainframe-based apps that date back 10 to 20 years and more than 25% of businesses feature applications that are between 20 or 30 years old. Today, businesses are often running and maintaining legacy applications built on traditional databases while simultaneously building microservices-based apps to accelerate new services and innovations. The mantra “If it ain’t broke, don’t fix it” certainly applies here; and while there are many reasons organizations continue to rely on mainframes and legacy systems, there are also many organizations that want to begin modernization initiatives but don’t know where to start.

    However, the past few years saw a wave of new digital-first companies in all industries putting pressure on legacy systems-based businesses—from retail to finance to manufacturing to technology. The COVID-19 pandemic accelerated many organizations’ modernization plans and made clear that for those that wanted or needed to modernize to stay competitive, avoiding the problem just wasn’t an option. Companies found that if they weren’t proactive about modernizing, the cost of being reactive when they needed to update and evolve was exorbitant.  

    Accelerating IT modernization initiatives can be a major challenge: Safely modernizing those legacy apps and mainframe systems and the critical data in them can seem impossible, but it can be done. Companies like Kroger, for example, have already made that jump and there’s a lot to learn from them. Here are three things that can help any enterprise on their journey to say goodbye to mainframes and legacy systems:

    You Need a Frictionless Path for Legacy Apps

    Many modern solutions are only focused on greenfield applications and helping newer born-in-the-cloud companies and projects; however, the reality is most Fortune 1000 companies have a lot of existing applications they can’t afford to ignore or completely rebuild all at once. Supporting existing applications with standard interfaces like Postgres while delivering the scalability and resiliency to support modern applications is critical to providing a bridge from where companies have been to where they are trying to go. Distributed SQL databases provide a seamless path forward to modernize existing apps while supporting new and current initiatives. 

    Embrace Automation

    It’s time to stop relying on complex code or fragile systems with bolted-on third-party tools. Being able to rely on intelligence and automation in the data layer for distribution, resiliency and availability is critical to minimizing changes and impacts on current applications. Doing so will reduce risk, offload legacy app tasks and ensure systems have the intelligence to work properly. With a distributed SQL database, you can deliver a single logical database that appears to applications like a monolithic, single-server database but with the underlying intelligence to allow it to stretch across hybrid, private and public clouds. 

    Finding Flexibility and Becoming Future-Proof

    To avoid being tied to specific systems or architectures, it’s time to adopt a future-proof mindset. Businesses can achieve this through:

    • Multi-cloud/hybrid cloud: With a distributed SQL database, you can deliver a single logical database that looks like a monolithic, single-server database but with the intelligence to stretch across hybrid, private and public clouds—providing the flexibility to be deployed wherever the application is needed or is best served.
    • Any hardware: No two data centers look alike and there are a wide variety of hardware needs, from bare metal to VMs and containers. The right modern distributed database provides ultimate flexibility in where the data layer can be installed to match whatever hardware and configurations are already in use. 
    • Any deployment: Existing organizations have a wide variety of environments and deployment types, from single data centers to two or more private data centers to more and more hybrid environments that span on-premises and public clouds. A modern distributed database provides the freedom to support a wide range of deployment options, including synchronous replication, geo-partitioning and cross-cluster asynchronous replication.  
    • Open source freedom: While many databases provide some open source components, there are still a few 100% open source solutions committed to the Apache 2.0 license. Users can benefit from the full set of enterprise features and capabilities in these open source solutions as well as benefit from the security and transparency that comes with a 100%-open source solution. 

    It’s time to update the old adage, “If it ain’t broke, don’t fix it” to “If it ain’t fixed, it could be broke,” with regard to modernizing legacy systems. If you’re considering starting a modernization journey, save time, resources and money now to make upgrades that might later be costly, time-consuming and overwhelming for your internal teams. 

  • Catchpoint Enables Experimentation by Automating Web App Testing

    Catchpoint Enables Experimentation by Automating Web App Testing

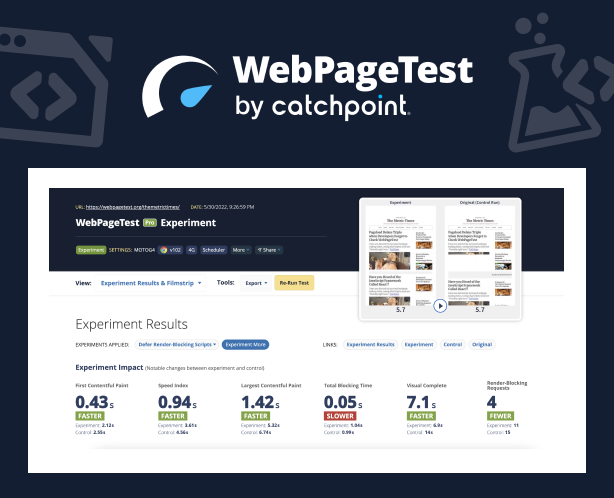
    Catchpoint this week expanded its open source WebPageTest performance testing suite of tools to enable IT teams to run instant tests that surface suggestions for improving overall web application and site performance.

    In addition, Catchpoint is now providing support for private tests, bulk tests and priority testing capabilities within the WebPageTest tool suite.

    Tim Kadlec, director of engineering for WebPageTest, said the goal is to make it easier for both developers and DevOps teams to experiment with how changes to applications and websites could improve performance using a capability that has now been added to the core suite.

    Identifying opportunities to improve performance typically requires tediously constructing manual tests over a period of weeks, noted Kadlec. Much of that effort is experimental in the sense that no one knows for sure if the tests being constructed will have a material impact on performance.

    The Opportunities and Experiments capability provides teams with a low-code tool for building tests based on a set of best practices that Catchpoint has defined. That approach makes it simpler to automatically generate and test tweaks that, for example, eliminate blocking scripts, optimize image rendering and minimize layout shifts. The result is optimization tests that show how their applications and websites could benefit from specific, actionable improvements without having to change any of the code that has already been deployed, said Kadlec.

    That’s a critical capability because it will encourage a level of experimentation that previously IT teams shied away from, simply because the amount of effort required to achieve an uncertain outcome was too high.

    It’s not precisely clear who is conducting these types of tests, as more responsibility for testing applications continues to shift left toward developers. The latest additions to WebPageTest make it easier for developers to conduct those tests without necessarily requiring help from a DevOps team, noted Kadlec.

    While there has always been a tremendous amount of focus on web application and site performance, the attention level has risen across organizations in the digital business transformation era. Many of the processes being implemented via web applications are extremely latency-sensitive. As more of those applications become routinely tested, the overall level of application performance should steadily improve.

    At the same time, the number of web applications and websites that most organizations are supporting also continues to expand. Most of those organizations are looking for ways to test applications without necessarily having to expand the size of the testing team or significantly increase the amount of time spent on testing.

    Regardless of the approach, it is apparent that testing is becoming more automated. The goal is not so much to eliminate the need for dedicated testing teams, but reduce the number of rote tasks that contribute to test avoidance in the interest of saving time. In theory, the more tests run—and the earlier they are run—the fewer issues that DevOps teams will need to deal with later.

  • The APIs You Really Don’t Know About

    The APIs You Really Don’t Know About

    A few years ago, we were rightly warned about the amount of exposure our APIs created. A massive attack surface that often used “security by obscurity” as its primary method of protection. We’ve come a long way since then, building secrets, tokens, RBAC and even more into our API interfaces.

    We’re still behind in getting comprehensive lists of APIs, but this bit is getting better as time moves on. Increasingly, both API management and DevSecOps markets are helping to catalog new APIs, and both the API management and application and API protection markets are helping to protect APIs that are unknown by tracking calls moving through the network. By using proxies, it is relatively easy to capture calls to APIs and report the list of APIs (and sometimes much more; about parameters and data transport, for example) to security or operations staff.

    In summary. the API management and security market has been doing great work, searching out the various APIs that are active in our systems, and cataloging new APIs as they are created. This gives us a comfortable and complete look at our current API environment and how it is protected. Most of these tools help protect what isn’t currently well protected.

    If only that really were all of the APIs in our networks. Unfortunately, that’s not the case. Because the ones not in this “complete list” can be the most insidious. As always, it is what you don’t know that poses the biggest risk.

    You see, there are APIs that are not currently maintained and are not currently actively accessed. Say you have an application that you installed from a third party—open source or purchased, either one—and then stopped accessing. Well, it is still sitting out there. The APIs are available—not necessarily documented and not necessarily secured. For security staff, this is how nightmares begin.

    Historically, we could count on these interfaces to be private. Those days are long gone in the hybrid environment. They might be private, but the definition of “private” is much looser than it has historically been and if there is a route from the internet to the API, it’s not private, and for well-known applications, is a time-bomb.

    This is another reason to clear out old versions and/or redundant installations of things like web servers and databases. Don’t make excuses—just upgrade them to the most recent version or remove them entirely. You can do this by merging what they do with a newer/better-protected installation or by just stopping them and fixing the apps that this impacts. “Turn it off and see what breaks” is admittedly a risky step, but sometimes will prove necessary to lock down the environment. If you don’t know what is using it, I’d argue your security risks are larger than an unprotected API hanging about, but that’s a topic for another blog.

    Meanwhile, keep rocking it. There is so much in your purview that we have to discuss what you don’t know about in the domain you are the specialist in. That’s not a weakness in you, that’s a statement about how much crap is tossed on your plate while making the org more competitive. And you’re dealing with it. So smile, keep kicking and lock down the scary bits.


  • 3xFAIL: IPv6 Fails | Fintech Fails | Firefox Fails

    3xFAIL: IPv6 Fails | Fintech Fails | Firefox Fails

    Welcome to The Long View—where we peruse the news of the week and strip it to the essentials. Let’s work out what really matters.

    This week: IPv6 gets stabbed in the back, Fintech firms’ valuations are falling, and the latest browser war seems to be over—Firefox lost. (more…)

  • JFrog Aims to Push DevOps to the Edge

    JFrog Aims to Push DevOps to the Edge

    At its swampUP event, JFrog launched a JFrog Connect platform for updating, managing, monitoring and securing remote Linux and internet of things (IoT) devices.

    The JFrog Connect platform is based on a lightweight agent JFrog gained last year with the acquisition of Upswift and that has now been integrated with the JFrog Artifactory repository. DevOps teams can now use a low-code tool to build flow logic that is integrated with a Git repository in addition to triggering a rollback to ensure a device returns to its previous known software state when necessary.

    DevOps teams will also be able to connect to a wide range of Linux-based IoT devices from anywhere in the world and then manage and monitor them in real-time by name, description or tags.

    JFrog CTO Yoav Landman said in the near future, DevOps teams will find themselves building and deploying applications that will not only be deployed on fleets of endpoints at the network edge, but also will be continuously updated.

    Historically, those endpoints have been managed mainly by operations technology (OT) teams, but it will soon be up to DevOps teams to automate the management of those platforms down to an individual container using the lightweight agent created by Upswift, he said.

    The number of application workloads being deployed on edge computing platforms is rising sharply as organizations seek to process and analyze data closer to the point where it is being created and consumed. In fact, that shift is at the core of digital business transformation initiatives that depend on edge computing platforms and devices running, for example, IoT applications that process data in near-real-time.

    The challenge today is in many cases organizations lack the ability to consistently deploy software on edge computing platforms, which results in the creation of a hodgepodge of homegrown tools to manually deploy software on edge computing platforms. There is a clear need to raise the DevOps bar to address edge computing requirements, said Landman.

    It’s too early to say just how much software will be deployed on the edge, but there may come a day when there is more software at the edge than there is in the cloud. In the meantime, the line between edge computing and cloud computing continues to blur. Many more DevOps teams will soon find themselves managing thousands of distributed endpoints from a central cloud.

    In the meantime, DevOps teams should expect to find themselves working more closely with OT teams that generally have a significantly different culture. Many of those OT teams are just now coming to terms with the implications of connecting endpoints to the internet. The need to continuously update the software on those platforms is not typically the first issue that comes to mind for them. Today much of the software running on edge computing platforms is rarely updated. In the future, however, that software is likely to be updated at a rate that many OT teams are not ready to envision much less manage.

  • Broadcom Acquires VMware to Expand Software Portfolio

    Broadcom Acquires VMware to Expand Software Portfolio

    Broadcom today pulled the trigger on an acquisition of VMware for $61 billion in cash and stock that could dramatically expand its software portfolio.

    Tom Krause, president of the Broadcom Software Group, told investors that the Broadcom infrastructure software group will become part of VMware once the deal closes. The deal, however, includes a 40-day “go shop” option for VMware to court another suitor who might be willing to acquire VMware at a higher price.

    Should the deal close, Broadcom is committed to melding its portfolio of DevOps, AIOps and security offerings with the VMware portfolio, said Krause. Broadcom acquired CA Technologies in 2018 and the enterprise division of Symantec in 2019.

    Krause said Broadcom plans to invest in the core VMware vSphere, vSAN and vRealize management software platforms that drive the most revenue for VMware today. Broadcom is also committed to increasing VMware earnings from $4.7 billion to $8.5 billion within the next three years. The primary driver of that growth will be savings generated by eliminating duplicate functions in the combined company and a forecasted increase in the volume of workload running on VMware platforms, said Krause. There are currently 300,000 vSphere customers that are increasing the number of workloads they are deploying both in the cloud and in on-premises IT environments, he noted.

    Broadcom is also committed to shifting as many customers as possible away from perpetual software licenses to subscriptions that generate more consistent recurring revenues, added Krause. VMware today reported revenue for the first quarter of fiscal 2023 was $3.09 billion, an increase of 3% from the first quarter of fiscal 2022. Subscription and software-as-a-service applications accounted for 29% of total revenue for the quarter. Subscription and SaaS revenue for the first quarter was $899 million, an increase of 21% year-over-year.

    Dan Kirsch, principal analyst and managing director for Techstrong Research, an arm of the parent company of devopsy.kinsta.cloud, said given the size of the deal, many existing VMware customers are naturally going to be nervous. The primary concern will be the degree to which Broadcom might attempt to increase licensing fees to meet its financial goals, he noted.

    The acquisition of VMware comes at a time when the number of workloads being deployed in the cloud is far outpacing the rate at which workloads are being deployed in on-premises IT environments. The bulk of those workloads run on non-VMware-based hypervisors. However, many of the workloads that run on VMware today in a data center are being shifted to the cloud. VMware has also invested in building a Tanzu platform for building and deploying cloud-native applications on Kubernetes clusters.

    Broadcom is committed to investing in research and development across the combined software portfolio, said Krause.

    It remains to be seen how much of the VMware employee base will remain with the combined company. It’s not uncommon for there to be a ‘brain drain’ in the wake of a major merger, noted Kirsch.

    Whether or not the deal closes, a lot of IT teams will, at the very least, be reviewing their VMware software portfolio in the weeks ahead as the new Broadcom-VMware entity evolves. In fact, it’s likely that the acquisition of VMware will set off a wave of mergers and acquisitions during what appears to be an economic downturn. That means regular reviews of vendor relationships will soon be the order of the day for a wide range of IT organizations.

  • Go Language is Popular? | VMware Sells to Broadcom? | Unlimited PTO?

    Go Language is Popular? | VMware Sells to Broadcom? | Unlimited PTO?

    Welcome to The Long View—where we peruse the news of the week and strip it to the essentials. Let’s work out what really matters.

    This week: Golang goes from zero to hero, will Broadcom buy VMware? And limitless vacation is still a Thing. (more…)

  • The Scanner We Really Need

    The Scanner We Really Need

    IT has scanners for everything. And by everything, I mean everything. We scan source code for vulnerabilities and data leaks. We scan apps for vulnerabilities. We scan the network for holes. We scan our cards for access … Okay, that last one doesn’t fit, but you get the idea.

    Know what we don’t scan for (and what I propose we start scanning for immediately)? Secrets. Oh, there are apps that include finding secrets as part of their feature set—but only a part—and they only scan for secrets within their domain. What we really need is something all-encompassing. Secrets have a way of turning up everywhere—Git, flat files, databases, source code, email … If it can store text, your secrets are probably in there. The larger the organization, the more true this is.

    Way back in the day, I started working at a company that had mainframe admin credentials stored in a flat file on the network. I am not an InfoSec employee, but I can smell insecurity easily enough and I told them to knock it off.

    I am not mentioning the company by name because this is not indicative of their practices today, nor am I mentioning my position or the market, because anyone interested could then use my LinkedIn profile to figure out who it was.

    In my role there, I had the authority to tell them to knock it off, but they handed me a ready response: “Our network is secure, so we don’t have to worry about it. And we monitor the file … some …”

    The same type of mentality seems to permeate IT today. Security by obscurity is alive and well with regard to secrets, and yet we as an industry know (from hard-earned experience) that it is largely a myth.

    So, we need a tool that can access all the places that secrets might be hiding and ferret them out—I’m thinking like a simple UI that takes a secret and searches for it in all of the configured places—would be perfect. Well, almost perfect. Iteration 2.0 would report on what is accessing the secret in that location.

    Get secrets management. Several markets offer secrets management as part of a toolset, you might even own a product that can do it for you. Then, given the search tool and a good secrets management solution, you could search out all instances and replace access to them. Until iteration 2.0 comes out, you could replace them in a test environment and see what breaks—though we also have the hard-earned experience to know that this isn’t foolproof, so you’ll want to heavily document the change for that odd thing that breaks 20 months from now.

    This is not that difficult a product to design and build; finding where each secret is accessed from would be the hardest part. But that’s still doable with our current dev tools. One of you should build it and get rich.

    But meanwhile, as always, keep rocking it. Secrets stored in not-so-secret locations or not, you’re keeping the company running day in and day out. That makes you the stars of business. Keep up the good work.

  • Could Buying VMware Bring Broadcom Hybrid Cloud Bona Fides?

    Could Buying VMware Bring Broadcom Hybrid Cloud Bona Fides?

    Rumors are swirling that Broadcom wants to buy its way into the growing hybrid cloud market by acquiring VMware. The deal won’t come cheap—after news of the potential deal surfaced, VMware’s market cap soared to around $50 billion. Yes, billion with a ‘B’.

    As interest rates increase and investors reevaluate many of the lofty software company valuations, I expect to hear many more acquisition rumors. During this time of uncertainty, cash-flush vendors are going to be on the hunt for software vendors that can provide a technology platform, have large partner ecosystems and that also produce reliable revenue.

    Why the Acquisition Makes Sense for Broadcom

    Broadcom has a nice, solid business producing semiconductors for smartphone makers as well as storage and networking devices used in large data centers. However, like many hardware companies, the business has been desperately trying to break into the software industry. Why? There’s a semiconductor shortage and the company is in the right market at the right time. However, the company’s leadership knows that market conditions change. Software margins are significantly higher than hardware deals, and R&D and manufacturing costs for semiconductors are notoriously high.

    VMware has grown to become a large cloud technology platform, not just a virtualization offering. If Broadcom is able to successfully close on this deal, it will instantly own one of the largest cloud software platforms in the industry. In addition to acquiring large enterprise customers, the VMware partner ecosystem is important. For example, I believe that the NVIDIA partnership will be a profitable one for VMware. The two companies have been working together to create a platform to support AI-based applications for the data center, cloud and at the edge.

    In a time when some cloud businesses are experiencing wild fluctuations because of their lack of profitability, the VMware business model is solid. However, these fundamentals are also why the company is ripe for acquisition. In its fiscal year 2022, the company reported $12.85 billion in revenue and $6.33 billion in subscription and SaaS licensing revenue. Free cash flow for fiscal year 2022 was nearly $4 billion.

    Let’s quickly contrast VMware to the cloud data warehouse Snowflake (NYSE: SNOW). Snowflake’s market capitalization is around $40 billion and within the last year was well over $120 billion. Meanwhile, the company’s revenue is around $1.2 billion and it is struggling to find a path to profitability. If you were hunting to acquire a software business during a time when financial indicators are flashing red, which business model would you prefer?

    Broadcom’s Strategy: Become a Software Company

    I mentioned that Broadcom is desperate to gain relevance in the software industry. Why do I say this? The company’s recent acquisitions showed a clear pattern emerging—Broadcom has been trying to acquire its way into software.

    In 2018 the company acquired CA Technologies for nearly $19 billion. The following year, Broadcom acquired Symantec’s enterprise cybersecurity business for $10.7 billion. In addition, there were rumors that Broadcom was planning to acquire SAS Institute, the privately held analytics vendor, for somewhere around $15 billion to $20 billion. Those talks fell through when the SAS Institute’s aging co-founders and majority stakeholders announced a plan to go public in 2024.

    This M&A strategy might seem strange to many, but Broadcom originally tried growing through the acquisition of companies similar to itself. In 2018, the company made an offer of $117 billion to acquire chip producer Qualcomm. Broadcom later withdrew the bid when it became clear that the Trump administration pushed hard to prevent the deal, citing national security concerns.

    Although this latest deal would face governmental review and the Biden administration previously voiced concerns over tech mega-mergers and monopolies, we have not seen the administration prevent similar deals.

    The Path Won’t be Easy: Three Strategies for Success

    The market is full of cautionary tales of software vendors that were acquired only to be slowly destroyed. A successful acquisition would require Broadcom to tread lightly and maintain the elements that have made VMware the company that it is today. Below are three priorities that Broadcom should focus on if the deal is completed.

    Keep VMware independent: It is critical that VMware does not show favoritism toward one chip maker. VMware’s largest customers use chips from Intel as well as other manufacturers. If Broadcom tries to steer VMware toward its own chips exclusively, the backlash could quickly undercut the value of the acquisition. In addition, it’s my belief that the hybrid and multi-cloud models are here to stay (rather than a single cloud approach). Customers expect vendors to work with each other and are reluctant to accept single stack proprietary approaches. 

    Find innovative DNA and facilitate business unit collaboration opportunities: Hock Tan, Broadcom’s CEO, is very well respected in the industry; however, the company is not known for software innovation. Although I expect VMware to remain a standalone business unit (similar to CA’s current position within Broadcom’s ecosystem), it will be important to foster innovation. Broadcom should accelerate VMware investments, like Project Monterey and the NVIDIA partnership, while looking for new investment opportunities. Perhaps Broadcom could provide VMware with custom chips to help accelerate Project Monterey, but this sort of line-of-business collaborative innovation hasn’t been the model for Broadcom’s other software acquisitions. It should be.

    Nurture the partnership network: The next phase for the VMware partner ecosystem will require partners to understand the company’s vision for the future. What will the acquisition mean for partners? Will they have access to more solution selling that combines VMware and Broadcom technologies? How can existing Broadcom partners join the VMware partnership ecosystem? That will be another big question.

    It will be extremely interesting to see how this plays out. We’ll definitely be keeping an eye on this potential merger of two heavyweights!