Category: DevOps Toolbox

  • F5 Looks to Streamline Application Networking

    F5 Looks to Streamline Application Networking

    At its AppWorld 2024 conference this week, F5 announced a software-as-a-service (SaaS) edition of its NGINX application networking portfolio, which are now all available under a single enterprise license.

    Shawn Wormke, general manager for NGINX, said NGINX One will eliminate much of the friction enterprise IT teams currently encounter when implementing NGINX Plus, NGINX Open Source, NGINX Unit, NGINX Gateway Fabric and the Kubernetes Ingress Controller the company provides.

    As part of that effort, F5 is also now making available a unified console across its application networking portfolio that promises to streamline the management of the F5 application networking portfolio.

    Currently available under an early access program, NGINX One creates an as-a-service platform through which enterprise IT organizations can invoke and pay for these capabilities on an as-needed basis, said Wormke. The overall goal is to reduce the total cost of application networking by eliminating the need for IT teams to integrate the various elements of NGINX One on their own, he added.

    In general, application networking has become more complex with the rise of cloud-native applications based on microservices. By reducing the cognitive load required to network those applications, it becomes simpler to make network operations a more natural extension of DevOps workflows, noted Wormke.

    Most organizations have some level of experience with application networking using proxy servers, but as application environments have become more complex, the need for gateways and ingress controllers to provide these capabilities at scale has become more apparent. As a result, more IT organizations are starting to revisit how they are structured. There may always be a need for dedicated networking specialists to manage the physical network underlay, but as other networking services become more integrated with DevOps workflows, responsibility for some networking services is starting to shift further left toward DevOps teams that will either deploy these capabilities themselves or take advantage of a SaaS platform such as NGINX One. The overall goal is to be able to dynamically provision application networking services without having to wait for a network administrator to provision them.

    There are, of course, a lot of approaches to application networking that are now emerging. Regardless of how application networking evolves, however, the rigidity that has characterized the delivery of network services for decades should finally start to fade away. Today, outside of a cloud computing environment, it’s still common for IT teams to provision virtual machines or Kubernetes pods in hours only to wait days or even weeks for network connectivity to be provisioned. As IT environments become more hybrid and more workloads are pushed to the edge, there is a clear need for a more agile approach.

    Each organization will need to decide how best to approach application networking across legacy monolithic applications, microservices and event-driven applications at a time when IT environments have become much more complex to manage. The challenge, as always, is reducing as much friction as possible without unduly raising the total cost of IT to a point where it becomes unsustainable.

  • Kobiton Open Sources Test Script Generation Tool

    Kobiton Open Sources Test Script Generation Tool

    Kobiton today announced it is open sourcing a script generation tool for the Appium automation framework that automates the running of test scripts.

    The overall goal is to make the tool, which makes it simpler to create more testing scripts, more widely available and, ultimately, lead to higher-quality applications being deployed.

    Kobiton CTO Frank Moyer said the tool makes it possible to generate tests from a test case that has been captured in a Node.js format. Rather than having to hire hundreds of testers to create those scripts manually, it’s now possible to automate those tasks using an open source tool, he added.

    On average, Kobiton claims the tool it developed can write a 30-step script in 10 minutes, whereas a manual approach could take as long as four hours to construct a similar test.

    Once created, those test scripts can automatically be executed using the Appium framework. The output from that tool can also be used on other testing platforms, including Sauce Labs, BrowserStack and LambdaTest or integrated with low-code testing platforms from Perfecto and Tricentis.

    It’s no secret that the quality of any given application tends to vary widely, not just between organizations but also within them. Most of those issues can be traced back to a lack of testing that usually occurs because there isn’t enough time. As deadlines near, one of the first places organizations look to make up for delays is the time available for testing. The hope is that whatever issues arise will be addressed via the next update. Of course, when the update falls behind schedule, the testing process is again cut back.

    Ideally, application development projects would not be allowed to go forward without adequate testing, but given business pressures, they often do. The only way to limit the impact of application development delays is to reduce the time required to create and run tests. The more automated that process becomes, the less time there will be spent on manually running routine tests. In fact, hopefully, there might even be enough time to run more complex tests to uncover issues that might adversely impact the user experience in ways no one might have otherwise considered.

    One way or another, the quality of the applications being deployed needs to improve if for no other reason than end users have options. Most end users will never give a mobile application a second chance if the initial experience doesn’t meet expectations. At the same time, application security regulations are only going to become more stringent. The tolerance for known vulnerabilities discovered after an application has been deployed is falling. Many organizations will find themselves subject to fines being levied simply because there was not enough adequate testing baked into the software supply chain.

    In fact, application security should, in the final analysis, be an element of a large quality assurance process that begins with adequate testing.

  • Survey Surfaces Raft of Ongoing Agile Development Challenges

    Survey Surfaces Raft of Ongoing Agile Development Challenges

    A survey of 788 software development professionals finds 71% are using agile development methodologies within their software development life cycle (SDLC) but only 44% said it is working very well (11%) or somewhat well (33%) in the enterprise.

    Conducted by Digital.ai, the survey identifies end-to-end visibility and traceability from business initiative through deployment as the top opportunity for improvement (44%), followed by an ability to measure cycle time, wait time and bottlenecks (34%), continuous testing (29%) and identification and measurement of technological risk (28%).

    Nearly half (46%) identified too many systems as a primary reason Agile was not scaling, followed by siloed teams (37%), culture clash (34%), inconsistent adoption (30%) and the inability to measure business value (28%).

    Despite these issues, nearly two-thirds (63%) said they have visibility into their Agile pipeline, with 55% claiming they have complete visibility. However, only 36% said DevOps teams currently work together as one team to accelerate innovation and deployment of high-quality and more reliable software. At the same time, only two-thirds (66%) claimed at least 50% of their applications were delivered on time and “with quality.”

    Joyce Tompsett, general manager of the State of Agile project at Digital.ai, said the survey makes it clear many organizations are still trying to strike the right balance when it comes to developing software. For example, the survey finds the top two reasons organizations adopt Agile (tied at 41%) are to accelerate time to market and prioritize delivery and measure customer/business value. Most software development teams are being evaluated both based on velocity (33%) and the value delivered (29%), the survey finds.

    The survey also identifies customer satisfaction (43%), time to delivery (39%) and competitive advantage (34%) as their top priorities for 2024.

    In general, the survey finds that 33% of respondents reported business leaders and executives are actively leading and participating in company-wide agile transformation. However, more (41%) said there was not enough leadership participation. Well over a third (37%) said business teams simply don’t understand what Agile is or what it can do. More than a quarter (27%) said there is not enough training.

    Not surprisingly, the most widely adopted methodology is Scrum (63%) with the Scaled Agile Framework (SAFe) being the most widely used (26%). Another 22% don’t have a mandated framework, while 12% said they have created their own.

    The debate over what precisely constitutes agile development is, of course, ongoing. Each organization tends to adopt the elements of the framework that make the most sense for them, so the actual state of adoption from one organization to the next will vary widely. The one thing that is certain is the more complex the IT environment, the more challenging it can be to embrace agile development.

    And there continues to be lots of room for improvement. If only two-thirds of organizations are delivering half (50%) of their applications on time with an acceptable level of quality, it means there are more projects that are failing to meet that standard than many software development teams might care to admit.

    As more organizations become more dependent on software, however, tolerance for that level of failure will only continue to decline as businesses and leaders lose patience with application development practices that do not live up to expectations.

  • OpenText Extends Tool for Auditing Source Code Using Machine Learning

    OpenText Extends Tool for Auditing Source Code Using Machine Learning

    OpenText this week updated a static analysis tool it provides to audit code using machine learning algorithms to provide deeper insights into on-premises IT environments.

    Announced at the OpenText Security Summit 2024 conference, the latest generation of Fortify Audit provides additional artificial intelligence (AI) models capable of learning the unique attributes of custom source code.

    The latest version of Fortify Audit Assistant also adds the ability to detect drift in a model and, if necessary, automatically refresh it. OpenText is now committing to refreshing those models every quarter.

    The discriminant AI model from OpenText enables machine learning algorithms to learn how humans conducted an application audit to then run similar tests on other applications. Previously, Fortify Audit relied on the same core model to audit both on-premises and software-as-a-service (SaaS) applications based on data collected by OpenText. Fortify Audit Assistant now provides support for more than 30 language-specific models to improve testing performance.

    Dylan Thomas, senior director for Fortify engineering and product for OpenText Cybersecurity, said this capability ensures that any sensitive data never leaves an on-premises IT environment.

    The overall goal is to streamline the number of alerts that would otherwise overwhelm a DevSecOps team trying to identify the root cause of an issue, he added. For example, Fortify Audit Assistant will identify test code that is not vulnerable because it was never deployed in an actual production environment. That approach makes it easier for DevOps teams to prioritize which vulnerabilities to fix first in their source code using a lightweight AI model that still enables them to deeply scan source code, noted Thomas.

    Historically, DevSecOps teams need to make a trade-off between lightweight approaches and deep scans of source code that is no longer required, he added.

    As regulations pertaining to software supply chain security become more stringent the number of development teams that will be subject to some type of audit is only going to increase. The cost of failing an audit will also inevitably increase as regulatory bodies look to make examples of organizations that are not properly securing their software supply chains.

    It’s not clear how aggressively organizations are embracing best DevSecOps practices to address myriad software supply chain security issues that were highlighted in an executive order issued by the Biden administration to Federal agencies. However, with the rise of AI and other forms of automation, it should become simpler to identify more vulnerabilities before they wind up being exploited in a production environment.

    There will always, of course, be a need to secure production environments because there’s always a probability mistakes will be made. However, given the lax practices many organizations have employed to build and deploy applications, it’s probable the number of vulnerabilities that exist in production environments today is beyond counting. In many cases, the better part of valor might be to replace many of those applications entirely with ones built using DevSecOps best practices.

    Regardless of the path to better application security chose the one thing that is certain is cybercriminals are only going to become even more adept at discovering those vulnerabilities.

  • Salesforce Adds Ability to Apply Custom Security Policies to APIs

    Salesforce Adds Ability to Apply Custom Security Policies to APIs

    Salesforce today added the ability to customize security policies for application programming interfaces (APIs) to the Mulesoft Anypoint API management platform.

    Gerry Egan, vice president of product management for Mulesoft at Salesforce, said this capability makes it possible for organizations to use an Anypoint Flex Gateway Policy Development Kit to streamline development of custom API security policies that can be implemented as code.

    In addition to providing integrations with integrated development environments (IDEs), the Anypoint Flex Gateway Policy Development Kit also provides test policies that can be employed to ensure API security.

    That approach makes it simpler to ensure APIs are secure as they are being built and deployed within the context of an automated DevOps workflow versus having to rely entirely on a separate API security platform, he noted.

    The Mulesoft Anypoint Gateway already comes with security policies that DevSecOps teams can readily implement. Salesforce is now adding the ability to apply custom policies that DevOps teams can apply as it becomes apparent cyberattacks against APIs are becoming more sophisticated, noted Egan. Those policies can, for example, be used to remove sensitive data or replace it with a token, he added.

    Responsibility for API security is often not well established in many organizations, but as more accountability for API security shifts left toward DevSecOps teams, there is growing interest in addressing the issue as code when APIs are developed and deployed. While cybersecurity teams are responsible for maintaining cybersecurity after APIs are deployed, few of them have any insight into how an API is crafted. That’s a significant issue because cybercriminals have become more adept at both exfiltrating data via external facing APIs in addition to manipulating the underlying business logic to compromise a digital process, noted Egan.

    The Mulesoft Anypoint Gateway automates the process of building and applying security policies to APIs as part of the software development life cycle (SDLC) in a way that minimizes any impact on developer productivity, he added. That approach provides the added benefit of reducing the level of cognitive load developers would otherwise experience if they had to manually create software policies, said Egan.

    In general, most APIs are internally facing, but it’s not uncommon for them to suddenly be exposed to the internet as application use cases evolve. The best way to ensure API security is at the point of creation. Providing developers with API security tools gives them an opportunity to address security issues at the beginning of the application development process.

    There have already been several cybersecurity breaches involving APIs in the past year. It may only be a matter of time before there are additional breaches that could prove catastrophic. Regardless of the size of the API breach, the application development team that created and deployed the API in the first place is ultimately going to be held accountable for fixing it. The challenge is to find the simplest way to eliminate the issue in the first place at a time when the number of APIs being built and deployed only continues to explode.

  • Graylog Makes Free API Security Tool Available to Developers

    Graylog Makes Free API Security Tool Available to Developers

    Graylog this week made available a free version of its platform for securing application programming interfaces (APIs), intended to encourage developers to adopt best practices to secure them.

    The free version of Graylog API Security has all the capabilities of the paid version but is limited to 16GB of local rolling storage on a single node with a one-year renewable license.

    Graylog CEO Andy Grolnick said the goal is to make it simple for developers to use this edition of the platform as they are building APIs. As applications are deployed in a production environment, the expectation is organizations will then need to access the version of the platform that is designed to scale, he added.

    Based on technology Graylog gained with the acquisition of an API security platform originally developed by Resurface.io, this free version of Graylog’s API security platform is trying to help bridge the divide between the application development teams that create APIs and the cybersecurity teams tasked with protecting them, said Grolnick.

    Capabilities of the platform include API classification, discovery, risk scoring, an ability to capture API request and response payloads and continuous monitoring of API and threat signatures in real-time. Collectively, these capabilities enable Graylog API Security to provide high-fidelity alerts using a data lake that is embedded in the platform, noted Grolnick.

    That approach enables Graylog API Security to capture all API requests and response details to distinguish valid API traffic from malicious activity involving, for example, data exfiltration hiding under valid response codes.

    In addition, Graylog API Security automatically surfaces remediation guidance for developers who typically lack cybersecurity expertise.

    API security has become a major DevSecOps issue because cybercriminals are increasingly targeting APIs to steal data. As more externally facing APIs are deployed, the overall size of the attack surface that needs to be defended increases exponentially.

    A recent survey conducted by Enterprise Strategy Group (ESG) on behalf of Graylog found more than three-quarters of respondents (76%) have an average of 26 APIs per application. Most respondents are using open APIs for public consumption (67%) or are connecting applications with partners (64%).

    In general, most of those APIs are internally facing, but it’s not uncommon for those APIs to suddenly be exposed to the internet as use cases for applications evolve. The challenge is that few cybersecurity teams have visibility into APIs that, when manipulated by malicious actors, can expose code or provide a mechanism through which business processes can be compromised. This issue often exists because, in many organizations, it’s still not clear who is actually responsible for API security.

    Arguably, the best way to ensure API security is at the point of creation. Providing developers with API security tools gives them a chance to do the right thing from the beginning of the application development process, said Grolnick.

    There have already been several cybersecurity breaches involving APIs in the past year. It may only be a matter of time before there are additional breaches that could prove catastrophic. Regardless of the size of the API breach, the application development team that created and deployed the API in the first place is ultimately going to be held accountable for fixing it.

  • OX Security Optimizes DevSecOps to Improve Application Security

    OX Security Optimizes DevSecOps to Improve Application Security

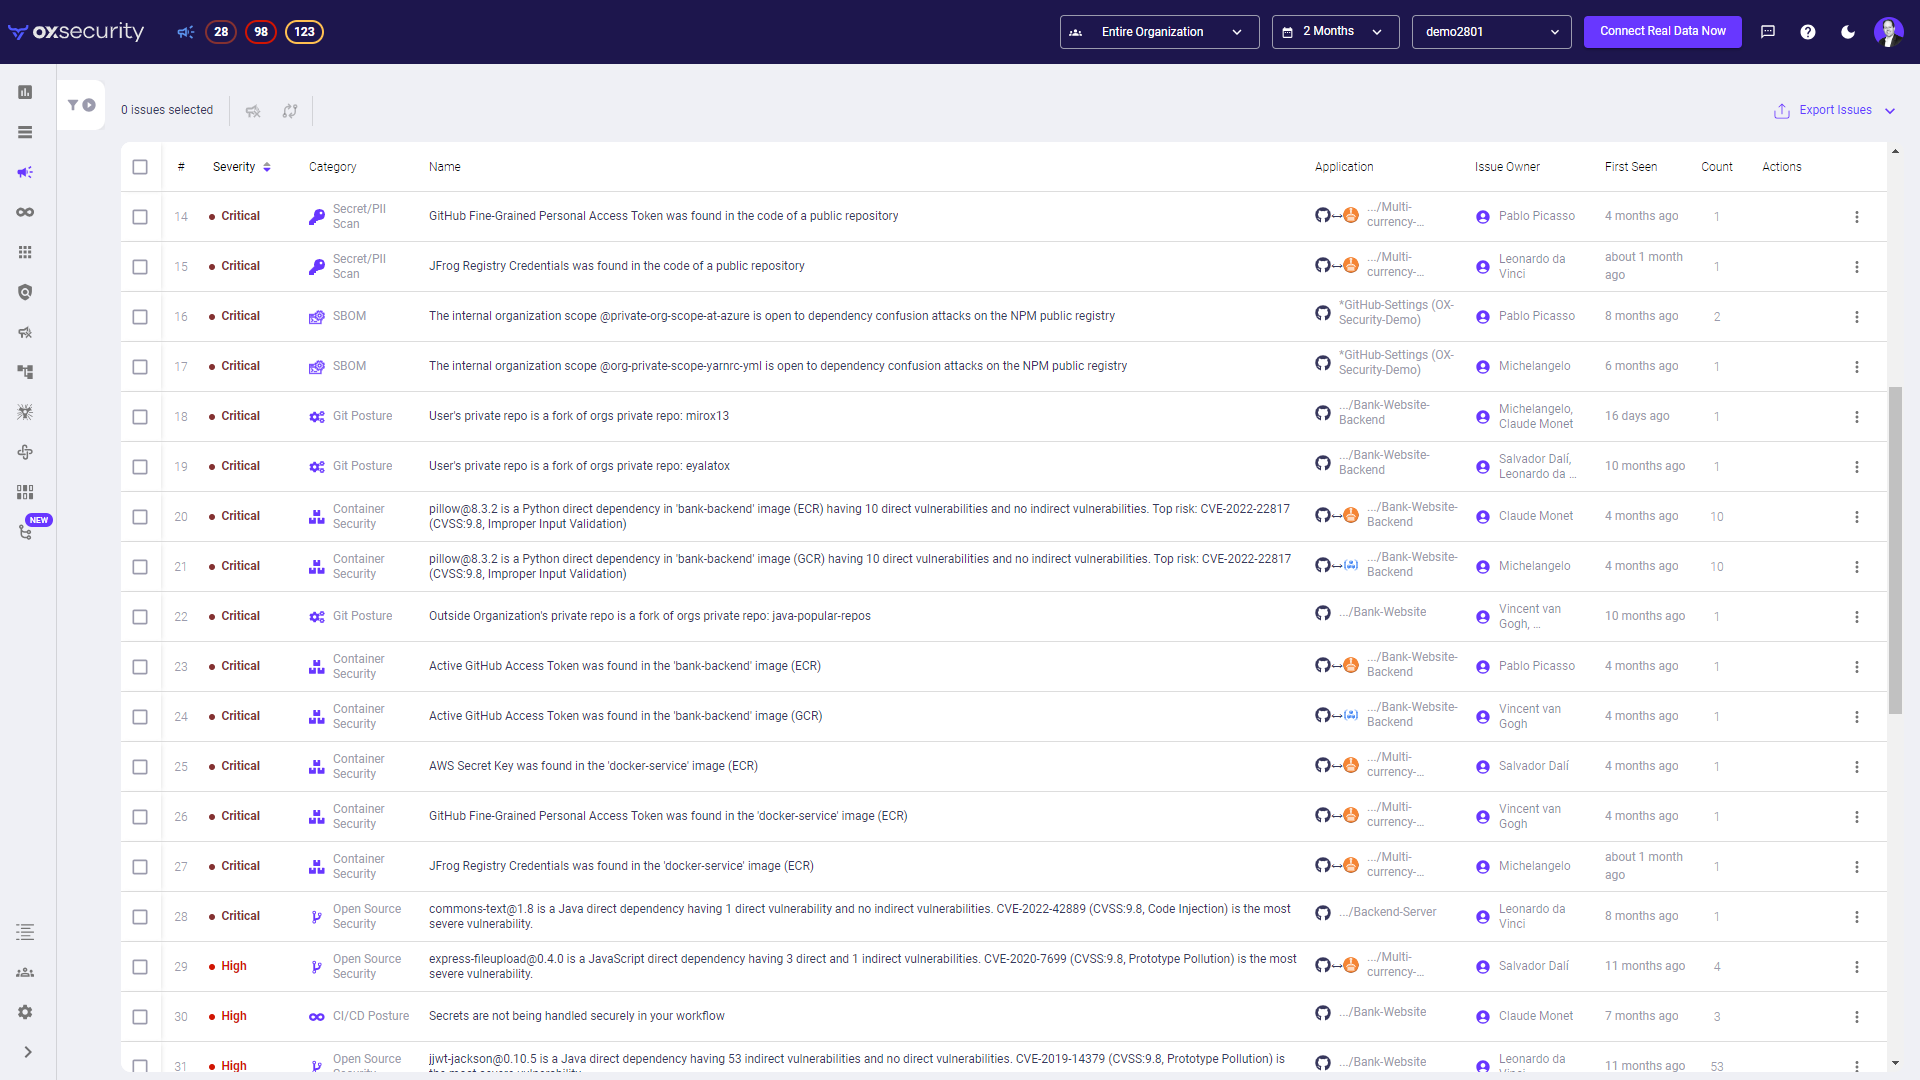
    OX Security this week updated its application security posture management (ASPM) platform to enable DevSecOps teams to instantly identify applications running in production environments that are running code that could be potentially exploited.

    The ASPM platform from OX Security leverages large language models (LLMs) to identify vulnerabilities. The latest version adds an ability to confine the number of alerts generated to instances of code that can actually be exploited.

    OX Security CEO Neatsun Ziv said that approach reduces the number of alerts that would otherwise be generated by 99% to enable DevSecOps teams to focus their limited resources on the 1% of alerts that represent an actual risk to the business. OX Security achieves that goal in part because its scanners are integrated with source control, continuous integration/continuous delivery (CI/CD) platforms, registries and cloud computing environments.

    The overall goal is to reduce the amount of manual effort currently required to consistently maintain DevSecOps best practices.
    The primary reason many vulnerabilities are never addressed is that DevSecOps teams are simply overwhelmed by alerts. Most of the alerts generated by a cybersecurity team are not immediately relevant because either the vulnerability is not present in the application running in a production environment or the application doesn’t connect to the internet.

    The OX Security platform makes it possible to identify application security issues that need to be prioritized because it has been confirmed a vulnerability exists that can be exploited, said Ziv.

    No matter how precise the alert process becomes, a DevSecOps team will still need to manage it, added Ziv. However, as the alerts generated become more relevant, it should become easier to bridge the historic divide between application developers and cybersecurity teams. Too many developers routinely ignore vulnerabilities identified by cybersecurity teams simply because previous efforts to identify the actual severity they represent have ultimately been a waste of their time.

    The challenge just about any organization encounters when trying to better secure their software supply chains is, not surprisingly, getting application developers to buy into the DevSecOps process. Most developers are going to actively resist any approach to remediating vulnerabilities that takes time away from building new applications. Most of them only allocate about 10% of their time or less to remediating vulnerabilities. As such, it’s incumbent on a DevSecOps team to find ways to address application security issues in ways that don’t adversely impact developer productivity.

    Organizations could mandate that vulnerabilities be remediated. In fact, there is a growing body of regulations that will require organizations to do just that unless they can prove the vulnerability in question cannot be exploited. The only way to effectively make that case will be to rely more on automation to document that the code running in a production environment is actually secure.

    In the meantime, developers should expect to see their code scrutinized more than ever. Of course, the better part of valor is to ensure that as many vulnerabilities as possible are never introduced.

  • Cycode Discloses GitHub Actions Vulnerability in Google Bazel Project

    Cycode Discloses GitHub Actions Vulnerability in Google Bazel Project

    Cycode today revealed it discovered a command injection vulnerability in the way the GitHub Actions continuous integration/continuous delivery (CI/CD) platform was used to update the open source Bazel project that many organizations employ to build and test software.

    The vulnerability, now remediated, could have been used to create a backdoor through which malicious code could have been inserted into a codebase that is managed by Google.

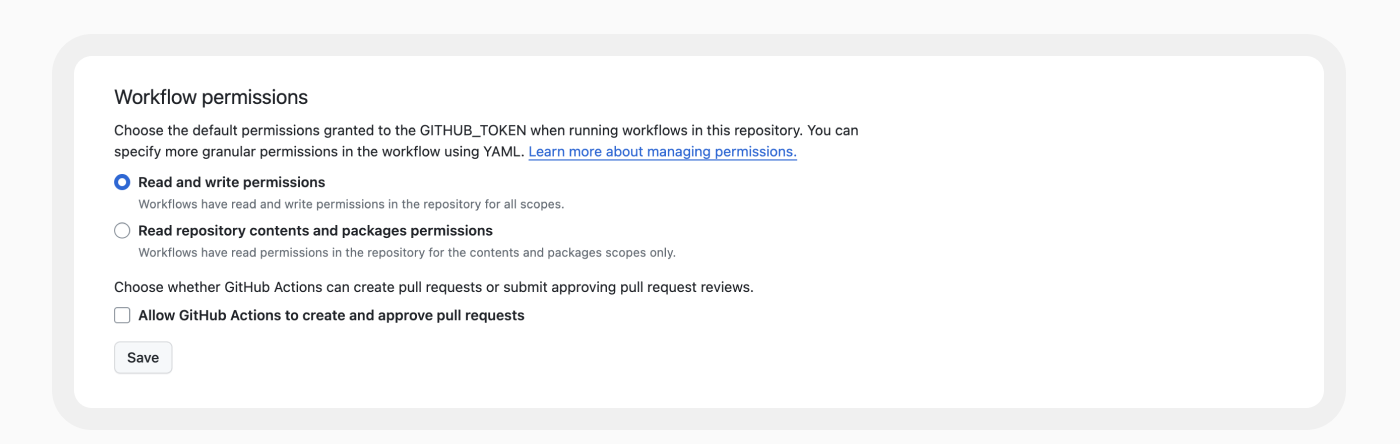
    Cycode researchers shared their discovery with Google, which has since updated the way it employs GitHub Actions to manage the Bazel codebase. Specifically, Google updated the base permissions to embrace least privilege principles to resolve the vulnerability discovered by Cycode.

    The vulnerability was discovered using RAVEN, an open source tool for scanning CI/CD platforms for vulnerabilities that Cycode makes available.

    Elad Pticha, senior security researcher for Cycode, said the vulnerability is the latest example of an instance of an open repository for building software that has been shown to be potentially vulnerable to an attack on a software supply chain that could theoretically impact any number of downstream applications and projects, including Kubernetes, Angular and platforms and services provided by Uber and LinkedIn.

    A Custom Actions capability that enables application development teams to create their own workflows presents any cybercriminal attempting to compromise of software supply chain with a tempting target, noted Pticha. A few changes to lines of code in a workflow can translate into thousands or even millions of lines of code, many of which an organization may never detect. Out of 3.4 million workflows examined by Cycode, nearly all (99%) make use of one or more Custom Action.

    Cycode has previously identified dozens of vulnerabilities in open source projects by mainly focusing on vulnerabilities within workflows. This latest research shows those vulnerabilities extend to indirect dependencies, such as Custom Actions, noted Pticha.

    Each DevOps team should review its own workflows for similar vulnerabilities at a time when more cybercriminals than ever are intent on compromising software supply chains. While many organizations have embraced DevSecOps workflows to improve application security, there is a natural tendency to overlook vulnerabilities that might exist in the workflows used to build and deploy software. The challenge is that DevSecOps workflows are still immature. A recent survey of 500 U.S. CISOs, AppSec directors and DevSecOps team members conducted by Cycode found 78% admitted application security attack surfaces are unmanageable, with 90% acknowledging relationships between their security and development teams need to improve.

    It’s not apparent if the vulnerability discovered by Cycode was actually ever exploited, but as most cybersecurity professionals know, if it can be imagined, someone has tried it. As such, any organization that uses Bazel might be well-advised to conduct a code review.

    In the meantime, it’s already apparent that regulations pertaining to securing software supply chains are only going to become more stringent in the months ahead. In the wake of the executive order from the Biden administration requiring federal agencies to lock down their software supply chains, it’s now only a matter of time before similar requirements are baked into legislation and various other regulations are implemented. The challenge and the opportunity now is to get ahead of this issue before a mandate with a hard deadline that can’t be ignored winds up disrupting the entire software development life cycle.

  • Azure Cost Optimization: A Complete Guide

    Azure Cost Optimization: A Complete Guide

    Microsoft Azure is one of the “big three” cloud providers, and is a primary part of IT expenditure for many companies. Azure cost optimization is a strategy that involves managing and controlling Azure costs to ensure efficient usage and spending. It requires a thorough understanding of where and how your resources are being used, as well as insight into the various pricing options available.

    Azure cost optimization involves implementing best practices related to managing cloud costs, such as turning off resources when not in use, choosing the right-sized resources, taking advantage of Azure discounts and more. By optimizing these aspects, you can ensure that you are only paying for the resources you need and are using them efficiently.

    Azure cost optimization is an ongoing strategy that involves constant monitoring and adjustments as your usage and needs evolve. This means that you need to be proactive and vigilant in your cost management efforts, regularly reviewing your usage patterns and making adjustments as necessary.

    Why is Azure Cost Optimization Important?

    As organizations migrate more and more of their workloads to the cloud, the costs associated with Azure usage can quickly escalate if not properly managed. This can lead to budget overruns and decreased profitability.

    By leveraging Azure cost optimization strategies, businesses can gain greater control over their Azure spending. This not only helps in reducing costs but also enables businesses to more accurately predict their future cloud spending. This can be a major advantage when it comes to financial planning and budgeting.

    Moreover, Azure cost optimization can also lead to improved operational efficiency. By ensuring that resources are used efficiently, businesses can avoid wasted spend and focus their resources on the tasks that truly add value to their operations. This can lead to increased productivity and better overall performance.

    Azure Cost Optimization Tools

    Azure provides several free tools designed to help customers optimize their cloud spending. These tools provide insights into your usage patterns, help you identify potential cost savings, and guide you in implementing best practices for cost management.

    Azure Cost Management and Billing

    Azure Cost Management and Billing provides detailed insights into your Azure spending. It allows you to track your spending by resource, location, service, and more, enabling you to identify where your money is going.

    With Azure Cost Management and Billing, you can set up budgets to control your spending and set up alerts to notify you when you’re nearing your budget limits. You can also analyze your spending trends over time, which can be useful for forecasting future costs.

    Azure Advisor

    Azure Advisor provides personalized recommendations based on your usage and configurations, helping you optimize your resources for cost, performance, security and reliability.

    Azure Advisor can identify unused or underutilized resources you can shut down or resize to save money. It also provides recommendations for purchasing reserved instances or using Azure Hybrid Benefit, which can lead to significant cost savings.

    Azure Pricing Calculator

    The Azure Pricing Calculator is a tool for estimating the cost of Azure services before you use them. You can input your expected resource usage, and the calculator will provide an estimate of the costs.

    This tool can be especially useful when you’re planning a new workload or considering a migration to Azure. By understanding the potential costs upfront, you can make more informed decisions and avoid surprises.

    Azure Monitor

    Azure Monitor is a comprehensive service that provides insights into your application performance, infrastructure, and network. While primarily used for performance monitoring, it can also provide valuable insights for cost optimization.

    For example, Azure Monitor can help you identify overutilized or underutilized resources, enabling you to make adjustments to optimize your costs. It can also help you track your resource usage over time, providing insights into your spending patterns.

    Azure Resource Graph

    Lastly, Azure Resource Graph is a service that enables you to explore your Azure resources at scale. It provides a unified view of your resources across all your subscriptions, making it easier to manage and optimize your resources.

    With Azure Resource Graph, you can quickly identify resources that are not in use or are underutilized, allowing you to reduce unnecessary spending. It also enables you to visualize your resource usage, helping you understand your spending patterns better.

    6 Strategies for Azure Cost Optimization

    Now that we are familiar with the basics of cost optimization on Azure and the tools the platform provides, let’s review some strategies that can help you optimize and reduce costs in Azure.

    1. Right-Sizing Azure Resources

    One of the simplest yet most impactful strategies for Azure cost optimization is to right-size your Azure resources. This involves matching your business requirements with the appropriate Azure resources in terms of type, size and quantity.

    Too often, organizations over-provision their Azure resources, which leads to unnecessary expenditures. By right-sizing, you ensure that you’re only paying for what you need. This can be achieved by closely monitoring your Azure resources usage, identifying any underutilized resources, and scaling them back accordingly.

    Remember, Azure provides a range of resource types, each with its own set of capabilities and costs. Always cross-verify whether the selected resource is the most cost-effective one for your specific use case. For instance, if your application doesn’t require high compute power, choosing a lower-tier virtual machine could significantly reduce your costs.

    2. Utilizing Azure Budgets and Alerts

    Azure Budgets and Alerts are powerful tools for cost management. They provide you with the ability to set a budget for your Azure spending and receive alerts when your spending approaches or exceeds your budget.

    Setting up an Azure budget is a proactive approach to cost management. It allows you to allocate your finances effectively and avoid any unexpected charges. Furthermore, with Azure alerts, you can instantly get notified when your consumption is nearing your budget. This gives you ample time to adjust your usage or increase your budget, preventing any service disruptions due to overspending.

    Moreover, Azure Budgets and Alerts are highly customizable. You can create multiple budgets for different scopes (like management groups, subscriptions, or resource groups), set your alert conditions, and even automate actions based on these alerts using Azure Logic Apps.

    3. Tagging and Resource Organization

    Azure tagging and resource organization is another crucial strategy for Azure cost optimization. Tags are user-defined key-value pairs that you can assign to your Azure resources. They help you categorize and manage your resources based on your business needs.

    By effectively tagging your Azure resources, you can gain visibility into your resource consumption at a granular level. This can help you identify any high-cost resources, track your spending by project, department or environment, and make informed decisions about cost optimization.

    Organizing your resources into logical groups can also simplify management and governance. For instance, you can group your resources based on their life cycle or purpose and apply consistent policies and access controls across the group. This not only improves security and compliance but also helps in identifying any redundant resources that can be eliminated to save costs.

    4. Utilizing Storage Tiers Based on Usage Requirements

    Another effective strategy for Azure cost optimization is to utilize different storage tiers based on your usage requirements. Azure Storage provides three access tiers – hot, cool and archive, each designed for different types of data.

    The Hot tier is for data that is frequently accessed and requires low latency. It has higher storage costs but lower access costs. The Cool tier is for infrequently accessed data, offering lower storage costs but higher access costs. Finally, the Archive tier is the most cost-effective solution for long-term retention of rarely accessed data.

    By carefully analyzing your data usage patterns and selecting the right storage tier, you can significantly reduce your Azure storage costs. Moreover, Azure offers automatic tiering options like blob-level tiering and life cycle management policies, which can further optimize your storage costs based on your data lif ecycle.

    5. Leveraging Azure Hybrid Benefit

    If you’re an existing Microsoft customer, leveraging Azure Hybrid Benefit can be a game-changer for your Azure cost optimization. Azure Hybrid Benefit allows you to bring your on-premises Windows Server and SQL Server licenses with software assurance to Azure, offering significant cost savings.

    With Azure Hybrid Benefit, you can run Windows Server and SQL Server workloads on Azure at a reduced rate, providing substantial savings as compared to pay-as-you-go prices. Furthermore, Azure is the only cloud provider that offers such benefits, making it an ideal choice for businesses looking to optimize their cloud costs while leveraging their existing Microsoft investments. Azure Hybrid Benefit is starting to support software from other companies, including Oracle and Red Hat.

    6. Regularly Reviewing and Optimizing Subscriptions

    Lastly, regularly reviewing and optimizing your Azure subscriptions is a must for Azure cost optimization. This involves keeping track of your Azure usage and costs, identifying any inefficiencies and making necessary adjustments.

    Azure provides several tools like Azure Cost Management and Azure Advisor that can help you gain insights into your Azure spending and offer personalized recommendations for cost optimization. For instance, Azure Advisor can identify idle resources that can be shut down to save costs or suggest reserved instances for predictable workloads to avail discounts.

    Moreover, consider exploring Azure Cost Management Power BI App for advanced reporting and analysis of your Azure spend. It offers a rich set of visuals and filters that can help you uncover deep insights into your cost data and drive cost efficiency.

    In conclusion, while Azure offers a plethora of services and capabilities, managing costs effectively requires strategic planning and continuous monitoring. By implementing the above strategies, you can ensure that you’re making the most out of your Azure investments while keeping your costs under control.

  • Dynatrace Extends Data Reach and Scope of Observability Platform

    Dynatrace Extends Data Reach and Scope of Observability Platform

    At its Perform 2024 event today, Dynatrace unfurled a Dynatrace OpenPipeline that makes it possible to apply analytics to multiple types of data sources in real time.

    The company also unveiled a Data Observability offering that can be used to vet the quality and lineage of data being exposed to the Davis artificial intelligence (AI) engine at the core of the Dynatrace observability platform to reduce false positives that otherwise might generate an alert in addition to helping reduce the volume of data that might need to be stored.

    Finally, Dynatrace announced it is starting today extending the reach of its observability platform to the large language models (LLMs) that are used to create generative AI platforms. That capability will, for example, make it simpler to monitor the consumption of tokens that are used to provide access to these models.

    Steve Tack, senior vice president for product for Dynatrace, said Dynatrace OpenPipeline will enable organizations to streamline the collection of data in a way that will enable them to apply observability more broadly by applying stream processing algorithms to petabytes of data.

    Scheduled to be available in 90 days, the Dynatrace OpenPipeline capability enables IT teams to ingest and route observability, security, and business events data from any source and in any format at the point of ingestion, including unstructured data that is automatically converted into a usable format. That data can then be enriched to enable deeper analytics.

    It also provides IT teams with more control over which data they analyze, store or exclude from analytics, which in turn helps reduce the total cost of observability, noted Tack.

    Finally, it presents IT teams with the ability to apply more customizable security and privacy controls to how that data is employed, he added.

    Dynatrace is pursuing a multimodal approach to AI that spans predictive, causal and generative models. Collectively, that approach makes it simpler to identify the root cause of issues, identify anomalies that might disrupt services and streamline incident management by, for example, providing summarizations of events in a natural language format.

    It’s not clear how broadly observability will be applied beyond the data collected to manage DevOps workflows and other IT processes, but it’s clear there is a high correlation between IT events and business outcomes as organizations become more dependent on software. As AI becomes more pervasively employed, it should become simpler to apply analytics to a much wider range of types of data to surface the relationship between IT events and business processes. In effect, Dynatrace is making it simpler to apply best data engineering practices to collect, manage and analyze that data, noted Tack.

    In the meantime, DevOps teams should revisit how their pipelines are currently constructed to make it simpler to capture all relevant data. As critical as telemetry data collected from the DevOps platform is to ensure application development and delivery occurs as fast as possible, that data is only one factor in a larger equation. The challenge and the opportunity now is determining how best to apply AI to correlate it all.