Category: Continuous Delivery

Continuous delivery is a software engineering discipline that allows organizations to consistently develop and release quality software at a rapid pace. It is achieved by automating the software development lifecycle, enabling tasks such as development, testing and release to occur concurrently and continuously.

  • 5 Tips for Securing DevOps: What You Wish You Knew Sooner

    5 Tips for Securing DevOps: What You Wish You Knew Sooner

    Foundations and frameworks, concrete and steel—not exciting. But that’s the foundation and framing of pretty much every modern building. Everything else that is part of a building–flooring, wiring, lighting, room placement and so on—is made possible by the foundation and the framework. If you want DevOps to succeed in your organization, you have to start by building a solid foundation and a framework, including security. What’s below is a suggested approach to the concrete and steel of DevOps.

    Three Foundational Needs

    1. Leadership and Governance
    Someone has to make the decisions, be responsible for leading the team(s), give direction and provide operational governance. Securing DevOps is not just about compliance with a set of security concepts; it’s also about setting the right tone for the workplace. Leadership and governance are key enablers of development success.

    The pressure to deploy software faster and more often is real—but so are the security, regulatory and many other concerns around automation that may uncover bugs or defects in software before it gets pushed to production. In an environment where there’s pressure to release code faster, how does one balance these competing priorities? What’s more important: Speed or quality? This tension between speed and quality remains one of the main challenges faced by organizations adopting DevOps practices today.

    Organizational leadership and governance regarding people and data must be in place to keep people working on the right things, keep up morale, provide direction about project prioritization and budget the right tools for getting the job done.

    An important subcategory of governance is data classification. Where does the data reside? Over which channels does it flow? What kind of data is it? Classifying the data has long-term implications for resource procurement such as what storage to use and if it needs to be encrypted, how stringent access control for the environments needs to be and interoperability of the various technologies.

    2. Regulatory Compliance
    It wasn’t too long ago that if a business remained only national, then there weren’t necessarily many regulatory requirements. Presently, if a business has a website (and who doesn’t?), then international and cross-border data transfer is a given unless one takes the course of geo-restriction, which in itself can be a major undertaking with repercussions.

    Determine regulatory needs. From where do people or other services access the data? What cross-border transfer is involved? To paraphrase the late 1960s-1980s public service announcement, “It’s 10:00 p.m. – do you know where your data is?” Design and implement accordingly.

    3. Risk Management
    One cornerstone of technology management is that it’s all about risk. If there’s a serious incident such as data intrusion or theft, what will the cost be to the organization and was the company part of the problem (e.g., negligence)?

    What are the technical vulnerabilities, threats and risks presented by the product or service? What kinds of testing (e.g., regression, penetration, vulnerability, CTI) would it take to assess and address the risks? What does the patch cadence look like?

    On the personnel side, what are the risks of key players leaving? What’s the morale of the team regarding aspects such as culture and pay? What’s being done to address those risks? Included are third-party, contractual, and privacy risks (remember data classification above?).

    NPM packages are a growing trend as an avenue of exploitation; uptime is a common requirement for meeting obligations, and privacy is considered by many to be more than a privilege but a human right, and not something to take lightly.

    Two Framing Activities

    The foundation activities undergird the entire structure of DevOps, but also consider what shapes the structure.

    1. Software Development Life Cycle (SDLC)
    The SDLC is vital. Without it, where do all personnel (team, contractors, consultants) know how to proceed with designing and implementing the product? What model is used, and who’s responsible for what? It’s all here in the SDLC. Of course, things like references for API architecture specifics and corollary application documentation would make one feel like wandering in the Library of Congress (and make developers want to burn it down like the ancient Egyptian Library of Alexandria!).

    Speaking of APIs: Due to the enormous rise of API use in all industries, including health care and retail, any use of APIs must be part of the SDLC.

    Not only are APIs on the rise for public use and interaction, but microservices use within an org has increased drastically. APIs are necessary internally and externally for businesses to reach, maintain and accelerate the speed of innovation, so including them as critical resources is crucial. The average API usage per company increased by 221%, so attending to that ecosystem by ensuring proper activities, especially security, are included is needed for developers.

    The SDLC is there to make workflow and production consistent (and concomitantly easier) by codifying what needs to be done for both company and customer, not to make work more difficult by presenting nauseating tedium. Like any corporate policy, it needs to remain useful, while not watered down.

    Here are a few specific aspects to include:

    ● Threat modeling in some form needs to be included. It doesn’t have to be a magnanimous effort, but the realities of threats will play a major part in development.
    ● Testing. Regression, stress, pentest, security – these and others will help guide what kind of testing environment one will need and lead to any need to increase items such as capacity and scalability.
    ● Secure coding. If it’s being done, take steps to improve. If it’s not being done, just get started. It’s always hard to go back and fix insecure code, but it’s a necessity due to the many risks and regulations involved in providing software to the public.

    2. Training
    Training is required because businesses have to adapt as technological changes create new opportunities that lead to continuously changing customer demands.

    Training is everywhere! There’s no one right place or right approach – just get training and change as needed (specifics should be handed down by leadership).

    On a strict and lowball budget? One option is OWASP membership (which costs $50 per person per year) and includes several types of AppSec and DevSecOps training. That small investment can help raise the level of clean and secure coding, threat and security consciousness and professional reputation.

    Setting the Course and Always in Motion

    An issue with setting any course in business is that it’s semi-permanent. A DevOps model put in place becomes part of the foundation, which can make one reticent to commit. The only way to prove the chosen methods is to set them in stone and do them consistently for a long time. Aspects of the model may change over time, but once that foundation is put in place, it takes an enormous amount of work, time and money to change it. The change wouldn’t be a remodel, but a reconstruction, so the model takes proper consideration at the outset to chart the right course.

    While DevOps needs a solid foundation, it’s an always-in-motion model. There are new technologies, new people, business changes, customer demands and societal and cultural shifts. These concepts can be included in calculations, but what those changes will be is incalculable. Hire and train the right people and the necessary steps and adjustments will be possible.

  • Fiberplane Notebook Tool Fosters DevOps Collaboration

    Fiberplane Notebook Tool Fosters DevOps Collaboration

    Fiberplane today announced it is making available a public beta of a namesake real-time collaboration notebook specifically designed for DevOps teams that need to quickly debug IT infrastructure.

    Fiberplane CEO Micha Hernandez van Leuffen said in the wake of the COVID-19 pandemic, it’s clear that the structure of DevOps teams has permanently changed now that more members of those teams work remotely. The challenge is that the tools provided to DevOps teams to manage IT environments were not designed to foster the level of collaboration that is now required, he added.

    Dashboards that were designed in a different era need to be replaced with tools that make it simpler for DevOps teams to collaboratively debug infrastructure in real-time, noted Hernandez van Leuffen.

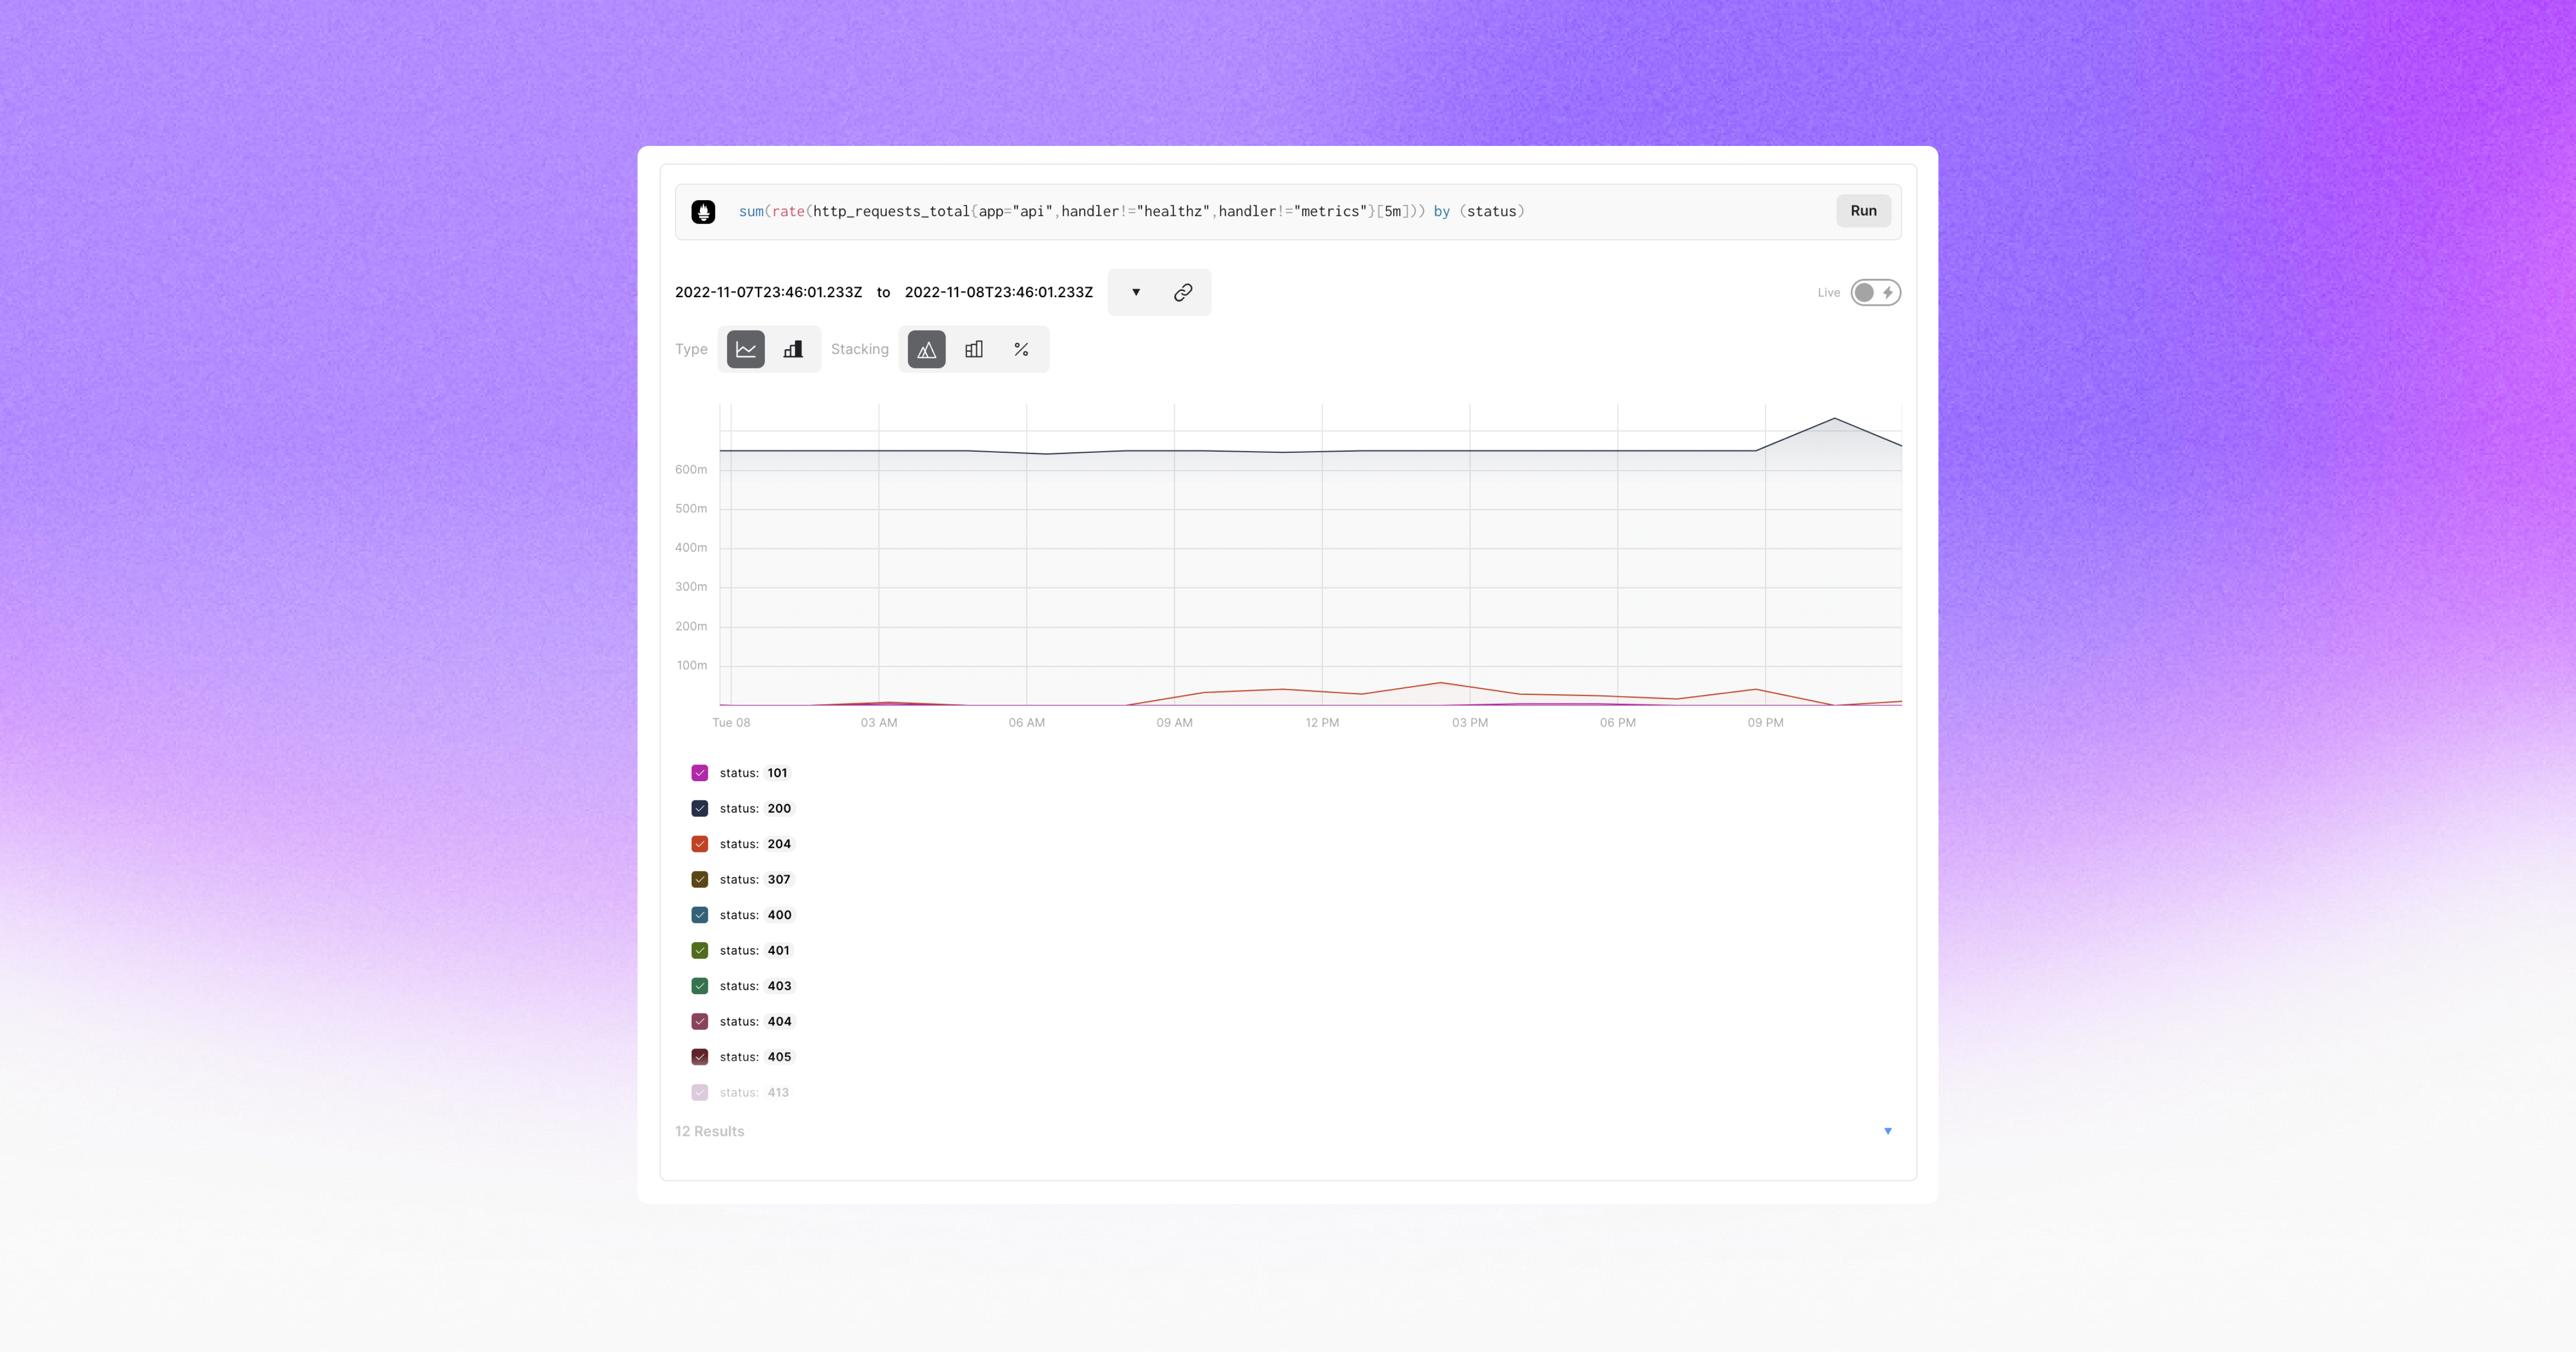
    The Fiberplane notebook achieves that goal by using the same operational transformation algorithm used in Google Docs to enable teams to easily collaborate around a document or spreadsheet. The core platform itself is built in Rust and WebAssembly (Wasm), which Hernandez van Leuffen said makes it simpler to integrate Fiberplane as a plug-in into an existing DevOps workflow. Inside a Fiberplane Notebook, DevOps teams can, for example, write and run PromQL queries and display Prometheus charts alongside other data presented via an integrated graph.

    Fiberplane Notebook’s initial integrations are for Grafana Loki, Elasticsearch and Prometheus monitoring tools. It also exposes both an application programming interface (API) and command line interface (CLI) to automate notebook creation based on specific external events, such as monitoring alerts.

    In effect, Fiberplane is taking the concept of notebooks used for collaboration by data science teams and applying it to DevOps workflows, said Hernandez van Leuffen. The goal is to improve DevOps teams’ productivity by reducing the amount of time it takes to resolve any issue, he added.

    As IT environments become more distributed in the age of the cloud and microservices, troubleshooting issues invariably spans the responsibilities of multiple members of an IT team. Fiberplane, in effect, makes it possible to spin up a virtual war room that enables the members of an IT organization to collaborate until the issue of the moment is resolved.

    The speed at which any IT issue is resolved has become a crucial metric. Given the complexity of IT environments, it’s inevitable that incidents will arise. Ideally, IT teams would discover those issues before they disrupt the business. However, in reality, the metrics organizations use to evaluate the effectiveness of a DevOps team are, unfairly or not, how quickly IT issues are resolved once they are discovered. The longer it takes for a distributed DevOps team to marshal its resources the more likely it becomes that team will be perceived as being inefficient—regardless of what level of application availability is actually achieved.

    Savvy DevOps teams, of course, have implemented a wide range of incident management best practices that create a level of muscle memory for responding to a wide range of issues. The trouble is there will always be unforeseen issues that arise. DevOps teams, as a result, need to find ways to quickly focus on an issue that, for one reason or another, were simply too unpredictable to anticipate; they need to expect the unexpected.

  • SAP Adds Low-Code Platform to Build Custom Apps Faster

    SAP Adds Low-Code Platform to Build Custom Apps Faster

    At the SAP TechEd 2022 conference, SAP SE today announced it has added a low-code platform, dubbed SAP Build, to its portfolio to make it simpler for organizations to build custom applications.

    Sebastian Schrötel, vice president and head of low-code/no-code solutions for SAP, said SAP Build is designed to make the company’s low-code tools more accessible to a wider range of developers, including so-called citizen developers that generally don’t have a lot of programming expertise.

    The goal is to make it possible to monitor, analyze and automate processes by leveraging more than 500 templates available within SAP Build. The goal is to make it possible to not only build applications faster but also deploy them via a single click, said Schrötel.

    The company’s approach to building custom applications separates its core applications from code developed by others by running pristine instances of SAP enterprise resource planning (ERP) applications in a separate cloud, known as the SAP digital core. A custom application is then deployed in a separate cloud and accesses SAP data via application programming interface (API). That approach enables SAP to update its ERP environment without worrying about breaking custom extensions.

    Of course, not every organization has transitioned to that model, so there are still plenty of instances of SAP software running in on-premises IT environments extended using code written in Java or the proprietary ABAP programming language. Over time, SAP is hoping that custom code will either be retired in favor of a process it has added to its ERP platform or by a more modern instance of that process running with a custom application deployed on a separate SAP cloud platform.

    SAP also has partnerships with providers of low-code platforms like Mendix and OutSystems that organizations can employ to build applications, but with the launch of SAP Build, the company is making a more concerted effort to encourage organizations to adopt the low-code platform it developed.

    While it’s not clear how eagerly low-code tools are embraced by citizen developers versus professional developers, the one thing that is certain is the pace of application development is accelerating. In many instances, professional developers are embracing low-code platforms as an alternative to procedural code to reduce expanding application development backlogs brought on by digital business transformation initiatives. In other instances, professional developers are employing low-code tools to collaborate more easily with end users as they build and deploy the applications that drive those processes.

    Regardless of the motivation, the impact this accelerated rate of application development will have on DevOps teams is profound. Not only do these applications have to be deployed in production environments, but DevOps teams must also secure and maintain a much larger application portfolio. As a result, the need to automate DevOps workflows will become more pronounced than it already is.

  • Why IT Teams Need Continuous Improvement

    Why IT Teams Need Continuous Improvement

    In the dynamic world of software delivery, an ‘if it’s not broke don’t fix it’ philosophy won’t get you very far—even when your software and systems are working as planned. 

    Software is more complex than ever and innovation is exploding across markets. To keep up with constant innovation from your competition in a global marketplace, you should always be thinking about how to improve your products and services. 

    The teams and organizations focused on continuous improvement simply outperform those who settle for the status quo and fear the unknown. Let’s look at why continuous improvement is important in IT organizations; how to avoid common mistakes when measuring success and tips for getting started. But first, let’s define what continuous improvement is.

    Defining Continuous Improvement

    Continuous improvement is incrementally improving a project or process several times based on feedback. Feedback can come from various sources, including users and automated testing.

    Advantages of Continuous Improvement

    Making small changes over time offers many benefits when compared to a “big bang” change. Often, a “big bang” change is made with little to no feedback until it is almost too late. 

    By making smaller changes, a team can try something, listen to feedback and adjust. If a change is poorly received by end users, little time was spent working on it, so it can more quickly be completely reworked or scrapped altogether. This encourages experimentation with the safety net of knowing nothing is permanent.  

    Think of it like swimming from one end of a murky lake to another. You could dive underwater and not come up until you hit land and, hopefully, you are in the right place. Or, you could periodically pop your head above water, check your bearings and adjust course.  

    Who Benefits?

    Today, it’s hard to imagine a situation where IT teams wouldn’t benefit from adopting a continuous improvement methodology.  Any IT team whose responsibilities include writing software and delivering it to users benefits from continuous improvement. Smaller, incremental changes generally mean a smaller risk of something going wrong. Making a small change to a piece of software or tweaking the software delivery pipeline to shave 30 seconds off the time it takes for each deployment environment adds up over time.

    What do IT Leaders Get Wrong?

    Continuous improvement is all about incremental changes over time to streamline workflows and cut back on waste. In the moment, those changes and improvements can be very subtle, making them harder to justify. When IT leaders don’t look at the big picture, it’s easy to miss how these small changes contribute to overall improvement.  

    For example, let’s say a team is completely focused on measuring deployment time. But the first fully automated deployment to production took just as long as a manual deployment. With a proper feedback loop, the team sees that it took just as long because there were a few misconfigured items. The next deployment takes less time, but only by a few minutes. 

    Each subsequent deployment takes less and less time. But it took several months and multiple attempts to go from two-hour manual deployments to 15-minute automated deployments. With an intensive focus on deployment time, this may not seem like a significant improvement given how long it took to get there. However, in this scenario, the team was so focused on deployment time that it missed other important measurements, such as the number of emergency fixes created after the team started automating the deployment. 

    If they examined those numbers before automation, they would have realized that they pushed out a handful of emergency fixes after a manual deployment—but, almost overnight, those emergency fixes stopped after introducing automation. Critical measurements and improvements like these are easily overlooked when leadership focuses too narrowly and avoids the “big picture” view.

    Getting Started

    When working in IT, there are many problems to solve with a finite number of people and limited time to fix them. It’s tempting to try and solve the problems at the same time. After all, you are only making small changes. 

    However, for real change to occur, you must make several small changes over time. Pick one or two problems to solve and focus on them until you reach a good stopping point; then, move on to the next problem.

    Also, know what and where to measure. With data in hand, you can take an informed approach to designing improvements. Never settle for thinking there are no further improvements because, inevitably, you will be proven wrong when your competition does it better and faster. 

    Ensure that your organization or team is dedicated to lifelong learning, perhaps by experimenting with chaos engineering to see how the system responds. This will spark important conversations and justification for improvement, as well as invaluable feedback. 

    Every IT organization benefits from adopting continuous improvement and will find that it promotes innovation and helps maintain a competitive advantage. It is easy to take too narrow a view of the small changes. But with a high-level, strategic view of continuous improvement, leadership will see the benefits. 

  • Codenotary Automates SBOM Creation

    Codenotary Automates SBOM Creation

    Codenotary today launched a tool that enables an application to automatically generate a software bill of materials (SBOM) by adding a single line to its source code.

    Codenotary CEO Moshe Bar said TrueSBOM makes it possible to self-report the components used to construct applications to any organization that uses them for the first time. In contrast, existing SBOMs only provide a snapshot of the components of an application at the time it was initially created, he added.

    IT organizations are being asked to trust application providers that all the modules specified in the SBOM are the only components being used. Codenotary is making a case for an approach that enables the organization consuming that software to spin up an SBOM in real-time on demand.

    From a DevSecOps perspective, adding a single line of code to the application to enable TrueSBOM should also eliminate the need to create and maintain separate text files to generate an SBOM.

    Awareness of the need for SBOMs has skyrocketed since the Biden administration’s executive order made it clear that federal agencies would require them from any software provider starting next year. Many enterprise IT organizations are likely to follow suit as part of a larger effort to better secure software supply chains in the wake of a series of high-profile cybersecurity breaches.

    That approach also makes it a lot simpler for organizations to accurately pinpoint where components are actually running any time a new zero-day vulnerability is discovered, added Bar.

    Priced at $1,450 per application stack per year, there are also lower-cost instances of TrueSBOM available for applications based on either a serverless framework or using the portable WebAssembly (Wasm) format.

    Most internal DevOps teams already have a good handle on what software components are being employed with the applications they deploy, said Bar. The issue is that the organizations that use that software can’t easily verify what components are being employed, he added. That’s problematic because an organization may have decided to prohibit deployment of a specific software component because of a known vulnerability. Rather than trust a text file created by the provider of an application, TrueSBOM allows the user of an application to maintain control over their software environment, noted Bar.

    It’s not yet clear how most organizations will operationalize SBOMs now that more of them are being created. Ideally, organizations should be able to approve only software that has components that have been verified to be secure. Armed with those insights, over time, it should become simpler to start reducing security technical debt with more secure applications, added Bar.

    The challenge, of course, is that the Codenotary solution requires the addition of one line of code to an application. However, as SBOM mandates become more stringent, the number of application providers that are anxious to comply with rules for securing software supply chains should increase. The issue now is finding a way for both the developer and consumer of that software to streamline a verification process that, in its current form, is too cumbersome to effectively manage.

  • Building Higher-Quality Software With Open Source CD

    Building Higher-Quality Software With Open Source CD

    Business is accelerating, and experience– for customers, partners and employees–is everything. This means nearly all applications need to be enhanced with new features, security updates and bug fixes on ever-shorter cycles. But isn’t rushing new code into production, especially in cloud environments, a recipe for mistakes, security vulnerabilities and user frustration? Not if the right approach is taken.

    Continuous delivery (CD) enables development teams to rapidly and regularly deploy software updates into production systems without jeopardizing user experience or creating security risks. Battle-tested open source CD orchestration solutions, including Spinnaker and Argo, provide a cost-effective way to deliver secure, high-quality software at massive scale to multi-cloud and Kubernetes environments.

    What is Continuous Delivery (CD)?

    Most software development teams suffer from quality issues related to outages, tracking down bugs and security vulnerabilities, complex upgrades, release rollbacks and more. According to a 2020 report by the Consortium for Information & Software Quality™ (CISQ™), software quality suffers as companies rush to add more value at greater speeds. In 2020, the cost to companies was $2.08 trillion in the U.S. alone.

    CD relies on a framework of stakeholder collaboration, process automation and continual and rigorous risk assessment and feedback to ensure a smooth, high-volume flow of high-quality code is deployed to production systems. When done right, CD reduces software development risks by enabling development teams to deploy changes such as new features, configurations, bug fixes and even experiments into production safely, quickly and sustainably. It also reduces costs associated with software deployments, failed releases and customer frustration and attrition.

    With effective CD workflows in place, development teams gain confidence and are more productive, delivering better products faster while eliminating the frustration of missed release dates, management wrath and the blame game associated with software bugs and vulnerabilities making it into production.

    Open Source CD Solutions

    Prior to the rise of open source CD solutions, companies often relied on point automation using scripts. These could improve efficiency a bit, but when companies moved from the monolithic architecture of a mainframe or on-premises servers to a microservices-based production environment, the scripts could not be easily adapted or scaled to cope with the more complex environment. This led to the formulation of continuous delivery orchestration solutions that could ensure code updates would flow to their destination in a repeatable, orderly manner.

    Two highly popular open source CD solutions have emerged, Spinnaker and Argo. Spinnaker was developed by Netflix and extended by Google, Microsoft and Pivotal. It was made available on GitHub in 2015. Spinnaker creates a “paved road” for application delivery, with guardrails to ensure only valid infrastructure and configurations reach production. It facilitates the creation of pipelines that represent a software delivery process. These pipelines can be triggered in a variety of ways, including manually, via a cron expression, at the completion of a Jenkins Job or other pipeline and other methods. Spinnaker also provides cluster management, as well as visibility into an application’s cloud footprint, letting users resize, delete, disable and even manually deploy new server groups using strategies like blue-green deployments.

    Argo CD, a container-native deployment engine for Kubernetes, supports CD pipelines, enabling the automated deployment of applications within Kubernetes. Introduced in 2018, Argo CD utilizes the Argo GitOps Engine, an open source library that implements core GitOps features. It allows users to manage, automate and audit the software deployment with Git as the source of truth. Features of Argo CD include drift detection, the analysis of the health of application resources and a real-time view of application activity.

    As open source software, both solutions offer all the benefits that the open source model offers, including low start-up costs, rapid and continual innovation and paid support when it becomes necessary.

    A CD Automation Success Story

    Symphony provides a cloud-based collaboration platform for financial institutions that are highly regulated and render services to millions of customers, so the solution must meet rigorous standards for security and regulatory compliance. The company wanted to enable a multi-tenant system to improve performance and reduce the cost of operations for each client. However, the existing software delivery system created bottlenecks in integration testing, long triage times and manual handovers of releases to site reliability engineering (SRE). The ever-growing number of delivery pipelines and software delivery environments also increased infrastructure costs and the burden on human resources, making it difficult to deliver features faster and ensure compliance at scale.

    Symphony determined it needed a completely new CD solution supporting infrastructure and software delivery workflows that they could retrofit into their existing platform. The solution needed to support infrastructure-as-code, pipeline-as-code and configuration-as-code, while providing visibility, auditability and faster approval processes. Symphony opted for a CD solution that harnessed the power of both Spinnaker and Argo to automate the entire end-to-end CD process, including pipelines for infrastructure, deployment, testing and promotion to production deployments. With the solution, Symphony was able to slash the time required to onboard new environments by 98%–just 10 minutes to get the infrastructure and platform ready for the client. This also allowed for fast and frequent changes.

    With automated CD in place, the company enjoyed significant cost optimization through automation. It was also able to increase security and compliance through automatic policy checks that continually enforced compliance across the stages of each pipeline–without compromising delivery speed.

    Getting Started

    As you review potential CD solutions, ensure they can deliver the required level of:

    • Ease of setup and configuration
    • Visibility and collaboration
    • DevOps tools integration and extensibility
    • Built-in deployment environment support
    • Security and governance
    • Workflow flexibility
    • Performance, uptime and scalability

    Get an Expert Assessment

    While the benefits of a CD solution are enormous, deploying one is not trivial. It pays to make good choices to get it right the first time. A professional assessment of your existing environment and processes can help you in several ways, including:

    • Exposing your current silos
    • Identifying the bottlenecks in your software delivery process that can be automated
    • Identifying productivity improvement opportunities for everyone involved in the delivery journey
    • Giving you the insights you need to make an informed decision about your CD solution.
    • Providing advice on best practices that can transcend the deployment process to the next level of efficiency and quality

    If your company requires the rapid delivery of secure, high-quality software releases, the time to deploy a continuous delivery solution is now.

  • GitHub Previews Free CI/CD Migration Tool Due in 2023

    GitHub Previews Free CI/CD Migration Tool Due in 2023

    At its GitHub Universe event, GitHub today unveiled a bevy of updates to its cloud service, including a forthcoming set of migration tools. The tools will automate migrations from legacy continuous integration/continuous delivery (CI/CD) platform to GitHub Actions.

    GitHub Actions Importer is already being used by a small group of enterprise IT organizations to migrate workflows and template the GitHub CI/CD platform.

    Damian Brady, senior manager for developer advocacy at GitHub, told conference attendees that these free tools will become more broadly available in 2023. GitHub Actions Importer will be distributed as a Docker container that manifests itself as an extension of the GitHub command line interface (CLI).

    One of the biggest challenges the company has faced in driving adoption of its platforms is that many DevOps teams don’t want to rebuild the templates and workflows they are already using on their existing CI/CD platform, he noted.

    Other GitHub Actions extensions include native integration with software development tools for building internet-of-things (IoT) applications and support for personal access tokens (PATs) that enable more granular control over permissions and repository access.

    Other security capabilities include expanded access to audit log events in the enterprise edition of GitHub, an ability for maintainers of open source repositories to privately share vulnerability reports and support for Ruby as one of the programming languages now supported by a CodeQL tool for discovering vulnerabilities.

    Additional extensions to existing services for developers also were previewed, including an ability to interact with the GitHub Copilot tool for automating code writing using voice commands. Dubbed “Hey, GitHub!” the tool is available as an experiment being advanced by the GitHub Next research team.

    Finally, the company previewed enhancements to code search-and-view capabilities in the Codespaces tool that will now be made available for free for up to 60 hours per month to developers.

    GitHub claims its CI/CD platform is now being used to process 10 million builds a day, most of which are employing code accessed via its repository. It’s not clear how that compares to other CI/CD platforms, but it’s apparent the GitHub Actions CI/CD platform has gained a significant amount of traction as GitHub continues to make a case for creating tighter integrations between its repository and CI/CD platform. GitHub is also clearly signaling it will spend a lot more time wooing organizations that already have a legacy CI/CD platform installed.

    In the meantime, the next era of DevOps has arrived as workloads become both more complex to build and deploy across highly distributed computing environments. Many of the CI/CD platforms that organizations deployed are now straining under the weight of multiple customizations and extensions that have been made over the years. Each DevOps teams will need to decide whether maintaining those platforms makes the most technical and economic sense or if they should migrate to a more modern platform.

    Regardless of what they decide, one thing that is certain is that DevOps teams won’t be getting larger, so the need to invest in higher levels of automation has become pressing.

  • CloudBees Demos Orchestration Capabilities of ReleaseIQ Platform

    CloudBees Demos Orchestration Capabilities of ReleaseIQ Platform

    At the online DevOps World 2022 event today, CloudBees demonstrated for the first time the capabilities of the application release management platform it gained last month through the acquisition of ReleaseIQ.

    Shawn Ahmed, chief marketing officer and interim chief product officer at CloudBees, told conference attendees that the ReleaseIQ platform will provide application development teams with visibility into precisely how their code is making it into production environments.

    Armed with those insights, it then becomes possible to understand exactly how the way commits are made during a build process are, for example, creating a workflow bottleneck, he added.

    The ReleaseIQ platform is designed to enable DevOps teams to both create and maintain pipelines using a no-code tool. That enables greater transparency into workflows via dashboards that also provide optimization recommendations.

    CloudBees already provides a Flow orchestration engine within its continuous delivery platform. However, ReleaseIQ provides a similar capability across multiple continuous integration/continuous delivery (CI/CD) platforms using a SaaS platform that is more accessible. ReleaseIQ can also be integrated with multiple platforms including CloudBees CI, Jenkins, CircleCI, GitLab, Bamboo, ArgoCD and others.

    Naturally, the current level of DevOps maturity varies widely by organization. However, as more organizations realize how much they depend on software to drive digital business transformation processes, the need to further automate application development and delivery becomes more apparent. While CI is widely used today, the number of organizations that have consistently implemented CD to automate application release management is still fairly limited. The underlying infrastructure that software is deployed on typically has a unique set of application programming interfaces (APIs) that each CD platform needs to support. Platforms such as ReleaseIQ provide a higher level of abstraction that simplifies managing the pipelines that deliver software.

    CloudBees is essentially positioning ReleaseIQ as the orchestration engine for both unifying pipeline management and, ultimately, enabling value stream management across increasingly complex application development environments. It may take a while to fully realize that ambition, but with the acquisition of ReleaseIQ, the company is now pursuing a more cloud-centric approach toward enabling DevOps teams to, for example, more easily reuse pipelines.

    DevOps teams, of course, have created a lot of scripts over the years to provide orchestration capabilities. The issue is that those scripts tend to be brittle in the sense they don’t scale especially well over time. They also tend to be poorly documented and challenging to maintain if the script writer leaves the organization. It’s not uncommon for new members of a DevOps team to replace a script with one they wrote simply because they’re more familiar with how it’s constructed.

    More than a decade after the launch of the Jenkins CI/CD platform, there are still plenty of manual DevOps processes that should be more automated. A no-code orchestration platform may prove to be a significant step toward automating a wide range of tasks that consume more time than they should.

  • OutSystems Acquires Ionic to Further Automate App Development

    OutSystems Acquires Ionic to Further Automate App Development

    OutSystems this week revealed it has acquired Ionic, a provider of an open source framework that provides developers with a higher level of abstraction for building and deploying mobile and desktop applications.

    OutSystems CTO Patrick Jean said Ionic will accelerate the company’s ongoing efforts to extend the reach of its platform for building low-code applications without developers having to worry about, for example, the screen size of the device an application is deployed on it because the framework automatically right-sizes it. Ionic, in effect, will provide an extension to the platform that OutSystems already uses to automate the building and deployment of low-code applications, he added.

    In addition to its namesake user interface (UI) framework for building mobile applications that can run on multiple platforms, the Ionic portfolio also includes a tool for natively deploying web applications, dubbed Capacitor, and a toolchain for building web component-based design systems, dubbed Stencil. Collectively, these tools are used today by more than five million developers.
    OutSystems plans to extend the capabilities of these tools to make it simpler to deploy applications on both mobile devices and desktop systems, said Jean. The overall goal is to reduce the cognitive load that developers currently carry when they need to build and deploy applications that run on multiple platforms, he added.

    That capability will prove critical as more individuals beyond professional developers become involved in building, deploying and updating applications, noted Jean. In fact, many of those developers are likely to be business people that only develop applications on a part-time basis, he added.

    The percentage of applications being built using low-code tools has increased dramatically. Professional developers have embraced these tools and platforms alongside so-called citizen developers that are using them to build applications, as well. As the backlog of applications that needs to be built steadily increases, low-code platforms have played a crucial role in enabling developers to keep pace with the demand for new applications.

    Less clear is the impact these low-code applications are having on DevOps workflows. On one hand, there are clearly more applications that need to be deployed than ever. At the same time, many of the DevOps and data modeling processes that once required, for example, a dedicated continuous integration/continuous delivery (CI/CD) platform are being embedded in the platforms provided by the vendors that create low-code tools.

    Regardless of how low-code applications are deployed, the one thing that is certain is the pace of digital business transformation is being greatly accelerated by these tools and platforms. DevOps teams will soon need to put guardrails in place that enable developers with a wide range of experience and skillsets to securely deploy and update applications.

    On the plus side, DevOps teams should also expect it to become easier to automate the delivery of low-code applications at levels of unprecedented scale. In fact, the issue going forward may not be whether IT can keep up with the needs of the business but whether the business can keep pace with the rate of innovation now being enabled.

  • SRE Survey Reveals Major Technical and Cultural Challenges

    SRE Survey Reveals Major Technical and Cultural Challenges

    Catchpoint, in partnership with Blameless, today published an annual survey of 559 site reliability engineers (SREs) that found 59% of respondents didn’t view tool sprawl to be a major concern. Another 40% said tool sprawl is a moderate (33%) to serious problem (8%).

    More than half of respondents said they build as much as 30% of the tools they use themselves, with more than half (54%) noting their organization tracks three or more different types of telemetry data to drive observability. The top three types of telemetry data collected are infrastructure (62%), application (58%) and network monitoring (55%) and, on average, the survey suggested the median toil level of SREs dropped 5% year-over-year.

    Just under half of respondents (46%) also noted they saw no or low value from artificial intelligence for IT operations (AIOps) compared to 30% that have seen moderate to high value. Another 25% are still unsure.

    Finally, the survey concluded that organizations that have adopted a “just culture”—where organizations ensure that incident reporting is not met with punitive measures—are 500% more likely to be Elite performers in terms of the DevOps Research and Assessment (DORA) metrics defined by Google.

    Leo Vasilou, director of product marketing for Catchpoint, said that the survey results provided some insights into the challenges SREs face as they strike a balance between trying to achieve DevOps goals and the fact that hiring has become more constrained during an economic downturn.

    That stress, however, has less to do with managing toolchains than it does ensuring that applications driving critical business processes are consistently available, he noted.

    SREs have emerged as a distinct DevOps function in recent years, focused almost exclusively on programmatically managing the dependencies that exist between a wide range of applications and the underlying infrastructure upon which they depend. Optimizing applications in the cloud-native era has become more challenging because the number of dependencies that exist between the microservices that make up a modern distributed computing environment continues to exponentially increase. In many cases, applications are continually added to IT environments without a commensurate increase in the overall size of the SRE team.

    Regardless of the economic climate, hiring and retaining SREs remains a challenge given the demand for IT professionals with those skills. Of course, there is no formal SRE certificate that is widely recognized so who qualifies to be an SRE tends to vary from one organization to the next. The one thing that is generally agreed upon is that SRE automate a wide range of tasks that would otherwise require multiple IT administrators to perform. Glassdoor also reports that, on average, an SRE makes north of about $125,000, which ranks among the highest salary level within any IT organization.

    Each organization, depending on their geographic region, would need to determine how many IT administrators they could replace if they hired an SRE. That doesn’t mean IT administrators that rely on a wide range of graphical tools to manage IT tasks are going away any time soon, but as DevOps continues to evolve, the dynamics between SRE and IT administrators also will continue to evolve.