Author: Mike Vizard

  • Virtual Instruments Aims to Meld DevOps, ITSM Worlds

    Virtual Instruments Aims to Meld DevOps, ITSM Worlds

    Virtual Instruments today announced additions to an IT management platform that leverage machine learning algorithms to identify application drift and dynamically right-size virtual machines.

    Tim Van Ash, senior vice president of products for Virtual Instruments, said version 6.2 of the company’s VirtualWisdom platform is part of an ongoing campaign to meld the traditional world of IT service management with best DevOps practices using an AIOps platform. As part of that effort, Virtual Instruments last month acquired Metricly, a provider of tools for monitoring cloud costs in real-time.

    The latest update to that platform also adds tools to monitors, reports, forecasts and alarms against the capacity consumption rate of any application, while a capacity forecast alarm now allows IT teams to specify how many days, weeks or months they wish to be notified prior to potential capacity exhaustion occurring on any one node or cluster.

    Finally, Virtual Wisdom 6.2 provides access to updated VirtualWisdom Proactive Dashboards that provide access to Smart Charts, through which the AIOps platform now supports annotation, linking and smart naming in addition to topology views that are specific to a set of IT infrastructure or an application.

    Van Ash said the Virtual Instruments approach to AIOps is that it allows IT teams to respond to changing application conditions in real-time and set granular limits on how much capacity can be consumed by any particular application. For example, IT teams can ensure that specific applications are given a Platinum-level preference that prevents any other application from consuming resources allocated to that application, he said.

    In general, Van Ash said Virtual Instruments is pursuing an application-centric approach to AIOps that will make it easier for IT organizations to optimize IT infrastructure capacity dynamically. Rather being overly focused on utilization rates and tracking events, AIOps platforms need to be able to address the entire IT life cycle as it relates to the value that IT environment has to the business, he said, noting today many DevOps teams are building and deploying applications with little regard or actual control over the service levels those applications need to achieve and maintain. The goal, he said, is to provide a single platform through which DevOps and IT operational teams steeped in legacy IT service management (ITSM) models such as ServiceNow can collaboratively achieve a common set of goals.

    A day of reckoning is coming for proponents of DevOps and IT teams that have built sprawling IT environments employing ITIL-based processes. Those ITIL-based processes are not especially flexible, but they have been employed successfully to roll out applications at scale consistently. Advancements in AIOps should go a long way to bring the two schools of IT management together by making it easier to bend the available IT infrastructure resources to the will of multiple application developers trying to share a common pool of resources.

    In the meantime, no one should expect AI to solve their problems magically overnight. It takes a while for algorithms to solve all their IT headaches. However, the days when the relationship between developers and IT operations teams could be described as mostly contentious soon may be coming to a merciful end.

    — Mike Vizard

  • GitHub Enterprise Server Update Extends Enterprise Push

    GitHub Enterprise Server Update Extends Enterprise Push

    GitHub has expanded its push into the enterprise with the 2.18 release of GitHub Enterprise Server, which includes a bevy of updates intended to make administrators’ lives easier.

    Mario Rodriguez, head of product for GitHub Enterprise, said the enterprise edition of GitHub is seeing triple-digit growth as large companies more aggressively embrace DevOps tools and processes that already have proven themselves to be effective when building and deploying large-scale web applications.

    To make it easier for administrators of those environments accessing either an on-premises edition or software-as-a-service (SaaS) version of GitHub Enterprise Server, the latest edition enables administrators to employ an issue-transfer capability to delete an issue in one repository and move it along with its associated metadata to a new repository in a single step.

    Other additions to GitHub Enterprise Server include an assignable commenters capability that allows maintainers with write access to assign an issue or pull request to anyone who has commented on it, regardless of their organization membership or repository permissions.

    If an issue or pull request belongs to a milestone, the name of the milestone now also will display on the project card and in the project card details sidebar. An issue or pull request from milestones can be added or removed using the details sidebar, and project cards can be organized by milestones using the search bar.

    GitHub is now also providing administrators with repository templates that allow them to own or have write access to a template repository. That capability allows anyone with access to the repository to generate a new repository with the same directory structure and files. If an administrator creates a user-owned repository, they also now will be able to watch it for updates automatically. However, forks no longer will be automatically watched, even for those granted push access.

    Rodriguez said GitHub is also starting to extend the scope of its platform to address best DevSecOps processes. Expanded dependency graph support adds security alerts to projects that rely on “yarn.lock” files. Those alerts help developers stay on top of vulnerabilities that impact their dependencies, which Rodriguez said is critical because security issues these days can wipe out all the productivity gains previously made in a DevOps process.

    An expanded audit logs capability allows administrators to see changes to settings for organizations and repositories, in addition to seeing when PAT and SSH are being used to access information and when there’s been a change in organization and repository membership.

    In general, Rodriguez said GitHub Enterprise Server, which gets updated once a quarter, provides 95% of the GitHub repository capabilities accessed by more than 40 million developers to share code and download open source software. Enterprise IT organizations clearly want to replicate the GitHub developer experience behind a firewall to ensure no one is inadvertently accessing proprietary software that provides them with a competitive advantage. The challenge, of course, is not so much setting up the repository as much as it is defining all the DevOps processes that need to revolve around it.

    — Mike Vizard

  • VMware Starts to Make DevSecOps Case

    VMware Starts to Make DevSecOps Case

    VMware, at the VMworld 2019 conference this week, strengthened its case for an application-centric approach to cybersecurity via updates to VMware AppDefense along with acquiring Intrinsic, a provider of a set of tools for securing serverless computing frameworks.

    VMware AppDefense layers a distributed service layered on top of the Platinum Edition of VMware Sphere platform that enables organizations to create a framework for whitelisting interactions between applications. Updates to the VMware AppDefense now enable organizations to run vulnerability reports across an entire application and virtual infrastructure stack along with support for integrity checks for the Windows operating system kernel.

    At the same time, VMware vSphere Platinum has now gained visibility and anomaly detection with automated reputation analysis for processes and network behaviors on a per-virtual machine basis. That capability is enabled by a collaboration with Kenna Security to feed risk-based data vulnerability metrics into the VMware AppDefense App Verification Cloud service.

    Additional capabilities include being able to initiate remediation actions based on the potential severity of a vulnerability, such as killing processes and network connections, and the ability to initiate remediation actions via the VMware NSX network virtualization overlay.

    At the same time, VMware also revealed that a future version of VMware AppDefense would also incorporate the technology that Intrinsic developed for securing serverless computing frameworks.

    Tom Corn, senior vice president and general manager for security products, said that move represents the first effort to extend the reach of AppDefense to include cloud-native computing environments. VMware AppDefense, coupled with an endpoint security service VMware is about to gain with the acquisition of Carbon Black, are at the core of its DevSecOps strategy, and rather than thinking in terms of endpoints at devices, the company will employ Carbon Black to secure applications as though they are the endpoint, he said.

    In some cases, Corn noted, that will require organizations to embed a lightweight agent within their applications. However, in many cases, platforms such as vSphere or Workspace ONE software will serve as the enforcement point because they already will have the Carbon Black agent software embedded. The Carbon Black agent also will be integrated with VMware Secure State, a real-time security and configuration monitoring service.

    The goal is to reduce the number of conflicting agent software strewn across an enterprise by various silos of cybersecurity technologies that don’t do much more than increase the operational cost of cybersecurity, said Corn. VMware is pursuing a more proactive approach focused on securing the entire application environment. That approach includes the web application firewall the company gained by acquiring Avi Networks earlier this year, he said.

    VMware already had a multiyear technology alliance with Carbon Black, so it has a good chance of achieving this goal soon once the acquisition is completed. In addition, as part of its DevSecOps strategy, AppDefense is already integrated with a variety of continuous integration/continuous deployment (CI/CD) platforms, Corn said.

    It may be a while before VMware fully delivers on that DevSecOps promise, but at the very least the DevSecOps dialogue in the enterprise is about to be elevated significantly.

    — Mike Vizard

  • Atomist Takes on Application Drift Management

    Atomist Takes on Application Drift Management

    Atomist today announced it is extending the capabilities of its software delivery automation platform to include drift management tools that make it easier to identify changes to code.

    Now in beta, that capability is based on an open source project dubbed Org Visualizer, which makes it possible to clone an entire project hosted in a GitHub repository via a single click and then visually inspect it.

    DevOps teams also can leverage a built-in Policy Manager to capture and track changes in code, define custom policies that automatically apply updates and automated actions and generate progress reports showing how close they are to achieving a target policy goal.

    Atomist CEO Rod Johnson said the reporting tools provide a visual representation of what’s occurring within an organization’s codebase to make it easier to identify both overly complex dependencies and vulnerabilities.

    The drift management tools are built on the software delivery machine (SDM) concept that lies at the heart of the company’s core platform, Johnson said. The Atomist platform is based on a domain model for software delivery constructed around an application programming interface (API) server and GraphQL, an open source data query and manipulation language. That approach eliminates the need to master, for example, complex YAML files to deliver software. The addition of the visualization tools not only make it easier to see what’s going on in the development environments, but they also make it easier to identify areas where technical debt in the form of bugs and vulnerabilities is building within an application development project, he noted.

    The sooner those issues are addressed, the more probable it becomes that DevOps teams will deploy reliable, secure code, rather than needing to update it or roll back the entire application, Johnson added.

    Although the Atomist platform is capable of working in any application environment, there’s a high correlation between organizations that have embraced microservices-based on containers and organizations looking to automate software delivery using the Atomist platform, Johnson said. Organizations that embrace microservices based on containers typically have a frequent need to update codebases in production environments, he noted, adding many organizations don’t know the impact that microservices updates have on the rest of the production environment.

    In general, there’s been a lot of DevOps progress when it comes to automating continuous integration within the context of application development project. However, automating the delivery of software has proven to be a more elusive goal. As the rate and amount of code being developed continues to accelerate, it’s now only a matter of time before software delivery automation becomes a more pressing issue. Manual deployment processes prone to errors only serve to aggravate application development and deployment backlog at a time when business leaders are demanding IT teams become more agile.

    At the very least, tools that enable DevOps teams to visualize the scope of the challenge ahead should help frame a realistic conversation about what’s truly achievable, given the current state of the codebase.

    — Mike Vizard

  • DevOps Deeper Dive: VMware Transformed

    DevOps Deeper Dive: VMware Transformed

    At the VMworld 2019 conference this week, VMware in no uncertain teams made it clear it wants to become a major DevOps force.

    Following the acquisition of sister company Pivotal Software last week, VMware is moving to build out an application development framework for building and deploying cloud-native applications based on Kubernetes. That effort coincides with ongoing investments in its vRealize Suite of management tools, through which VMware is committed to automating IT operations across both on-premises IT environments and public cloud computing environments.

    To advance those twin goals, VMware this week launched a series of Tanzu management tools for managing any distribution of Kubernetes while at the same time launching VMware hybrid cloud platform, which combines everything—from vRealize automation tools to the monitoring tools from Wavefront by VMware—to create a central console through which all of IT can be managed.

    [su_box title=”The VMware DevOps Timeline”]

    • October 2015 – Dell Acquires VMware along with EMC
    • April 2017 – VMware acquires Wavefront monitoring service
    • August 2017 – VMware shifts public cloud strategy via Amazon Web Services (AWS) alliance; VMware and sister company Pivotal Software unveil Kubernetes distribution
    • November 2017 – VMware Launches VRealize Management Suite
    • February 2018 – VMware acquires CloudCoreo to gain cloud configuration tools
    • August 2018 – VMware acquires CloudHealth Technologies to gain governance tools; VMware launches AppDefense to provide a zero-trust framework
    • November 2018 – VMware acquires Heptio for Kubernetes expertise
    • December 2018 – Dell acquires all VMware outstanding shares
    • May 2019 – VMware Acquires Bitnami for application packaging tools
    • July 2019 – VMware Acquires Avi Networks to gain Web Application Firewall (WAF); VMware Acquires Bitfusion for machine learning algorithms and GPU virtualization software
    • August 2019 – VMware Acquires Pivotal Software; VMware Acquires Carbon Black; VMware Launches Tanzu Platform to manage Kubernetes; VMware Unveils Hybrid Cloud Platform

    [/su_box]

    After deciding to launch a series of services through which it manages instances of its software on public clouds such as Amazon Web Services (AWS) and local servers from sister company Dell EMC, VMware has been slowly expanding its reach into the realm of applications. The most significant element of that thrust to date has been its acquisition of Pivotal, a provider of the widely used Spring framework based on Java and a platform-as-a-service (PaaS) environment based on open source software from the Cloud Foundry Foundation (CFF).

    The CFF is in the process of migrating the application development environment created for Cloud Foundry to Kubernetes, a cloud-native container orchestration engine being developed under the auspices of the Cloud Native Computing Foundation (CNCF). Both the CFF and the CNCF are arms of the Linux Foundation. The rise of Kubernetes has resulted in many organizations shifting their application development strategies to a platform capable of supporting multiple application development environments.

    Prior to announcing the deal to be acquired by VMware, Pivotal cut its revenue forecast for fiscal 2020 by $40 to $50 million.

    VMware DevOps
    VMware CEO Pat Gelsinger

    Pivotal Software spun out of VMware in 2013, so to a certain degree VMware’s move to acquire Pivotal represents something of a homecoming that last week was valued at $2.7 billion. Pivotal currently has about 350 customers, many of which are hosting a distribution of the Cloud Foundry PaaS on VMware platforms. VMware also tapped Pivotal to jointly develop a curated instance of Kubernetes, dubbed Pivotal Container Service (PKS), that is optimized for VMware platform. As part of that effort, VMware is also developing an instance of VMware vSphere that will run Kubernetes natively.

    At the VMworld 2019 conference, VMware CEO Pat Gelsinger made it clear VMware plans to leverage Kubernetes to bridge the historical divide between developers and IT operations teams. In fact, he told attendees Kubernetes was the most important technology to emerge since the virtual machine was created. As part of that effort, Gelsinger noted that the acquisition of Pivotal coupled with the recent acquisition of Bitnami, a provider of tools for packaging applications, means there are now more 5 million developers participating in the VMware ecosystem.

    VMware is clearly hoping the developer ecosystem will expand as VMware makes it easier to launch virtual machines on every major public cloud as well as on-premises IT environments. VMware has faced a major challenge over the last several years as DevOps teams have bypassed internal IT teams to deploy applications on cloud services based on alternative virtual machines by AWS or Microsoft. Thanks to the inherent portability of Kubernetes, VMware is hoping organizations will now deploy cloud-native applications on VMware platforms. It remains to be seen, however, to what degree DevOps teams will embrace VMware on public clouds versus continuing to employ those virtual machines.

    When it comes to cloud-native computing, VMware is clearly playing catchup. VMware has 250 PKS customers today, while rivals such as Red Hat (now an arm of IBM) have already redeployed their application development and deployment platforms on Kubernetes as an alternative to the Cloud Foundry PaaS. On the plus side, VMware now claims to be the third-largest contributor to Kubernetes, thanks in part to its acquisition of Heptio, a provider of Kubernetes tools.

    In the meantime, there’s no question VMware is at the forefront of developing tools for automating the management and securing of IT infrastructure running its virtual machine software. Less clear is to what degree VMware will be able to translate that success to also unify application development and IT operations across multiple platforms a truly meaningful DevOps way, rather than merely bundling a suite of disparate tools together at a discount.

    — Mike Vizard

  • DORA Report: DevOps Maturity Levels Rise

    DORA Report: DevOps Maturity Levels Rise

    The annual DORA report on DevOps shows a marked increase among Elite performers compared to last year

    The DevOps Research and Assessment (DORA) arm of Google Cloud today published the results of an annual survey that suggests there have been marked gains in the level of DevOps maturity.

    The “2019 Accelerate State of DevOps Report,” an annual global survey of 31,000 IT professionals, finds 20% of the respondents now consider their organizations to be “Elite” DevOps performers, up from a comparatively paltry 7% a year ago.

    The Elite group reported their organizations routinely make multiple code deployments per day. By comparison, low performers reported deploying code somewhere between once per month and once per six months. The normalized annual deployment numbers range from 1,460 deploys per 365 days for the highest performers to seven deploys per year for low performers. Effectively, Elite performers deploy code 208 times more frequently than low performers, according to the DORA report.

    The report also finds Elite performers need less than a day of lead time to make a change to an application, compared to 2,555 hours for low performers, and Elite performers reported a change failure rate of 0% to 15%, compared to 46% to 60% for low performers. Finally, elite performers are able to recover from an incident 2,604 times faster than low performers.

    Nicole Forsgren, DORA Lead, Research and Strategy at Google Cloud, said the study makes it clear DevOps best practices are now crossing the proverbial chasm in IT. Organizations that are furthest along in making that transition tend to set up “communities of practice” within their organizations through which DevOps best practices are shared across teams, she noted. The DORA report also makes it clear elite performers automate and integrate tools more frequently into their toolchains on almost all dimensions.

    Forsgren said the study also makes it clear that the practice of slowing down the rate at which code is developed to achieve higher-quality application deployments is not nearly as effective as employing lighter-weight change processes to lower the amount of code getting deployed at any one time. Slowing down the rate at which code is developed and deployed is not a good strategy, she said, because as the amount of code that needs to get deployed at any time increases, reliance on heavyweight processes to deploy that code usually results in more errors being made. A lighter-weight approach provides the added benefit of reducing the amount of technical debt any organization is likely to incur at any stage of the DevOps process.

    The increased rate at which organizations are embracing best DevOps practices naturally coincides with the rise of more complex cloud-native applications. Most of those applications are being built using microservices that create a lot of dependencies within that application environment, with different development teams often working in isolation on specific microservices. The only way to manage that level of complexityeffectively is to embrace DevOps processes, noted Forsgren.

    In fact, the DORA report finds Elite performers are 24 times more likely to have met all cloud characteristics as defined by the National Institute for Standards and Technology (NIST) than low performers. Organizations that meet all essential cloud characteristics are 2.6 times more likely to be able to estimate the cost to operate software accurately. They also are twice as likely to be able to identify their most operationally expensive applications easily, and 1.65 times as likely to stay under their software operation budget, the study finds.

    Clearly, best DevOps practices is one of those rare IT gifts that simply keeps on giving.

    — Mike Vizard

  • Splunk to Acquire SignalFx to Gain APM Platform

    Splunk to Acquire SignalFx to Gain APM Platform

    Splunk today announced it will acquire SignalFx as part of an effort to extend its reach beyond IT operational analytics and into the realm of application performance management (APM).

    Valued at approximately $1.05 billion, the deal to acquire an APM platform delivered as a software-as-a-service (SaaS) offering will expand and accelerate Splunk’s overall transition to a recurring revenue model based on cloud services, said Splunk CEO Doug Merritt during a call with industry analysts.

    Splunk is currently on pace to generate over $300 million per year from the cloud version of its IT operational analytics platform. Splunk revenues for the second quarter were $517 million, up 33% year over year, with software generating $350 million of that total. However, as Splunk transitions to more of a subscription-based pricing model, the company has some financial management challenges. GAAP operating loss for the company’s second quarter was $87 million. However, non-GAAP operating income was $47 million, even though operating cash flow was negative $129 million. That cash-flow issue is a direct result of the transition away from a perpetual software license model based on the volume of data consumed by the Splunk platform. Overall, Merritt said Splunk is firing on all cylinders and is still on track to have 20,000 customers by the end of its fiscal year.

    Merritt said once the deal is approved, sometime in the second half of fiscal 2020, SignalFx will provide a complementary set of services for monitoring legacy monolithic applications as well as cloud-native applications based on containers, Kubernetes and serverless computing frameworks. There are very few customers at this point who have not adopted cloud-native technologies, but for now they remain a small percentage of the overall number of application workloads being managed, he added.

    The goal is to provide a suite of services that will enable IT teams to investigate, analyze, monitor and act on data in real-time, said Merritt.

    Splunk is already widely employed by internal IT operations teams, many of whom already rely on a complementary APM platform. Splunk clearly expects organizations will prefer to acquire an IT operational analytics platform and an APM service from the same vendor. However, competition between APM platform providers is already fierce. That said, Splunk appears to be counting on increased demand for real-time application monitoring to differentiate SignalFx from rivals.

    It’s not clear to what degree Splunk might converge the various services now being provided separately by both companies. It’s also not clear how or whether this deal will accelerate acquisitions of the remaining independent APM platform providers.

    In the meantime, Merritt said SignalFx and Splunk’s earlier acquisition of VictorOps, provider of incident management platform based on best DevOps practices, will expand the amount of visibility Splunk has with application development teams.

    Ultimately, acquisitions of smaller, DevOps-oriented companies by vendors that today are still more closely identified with legacy ITIL-based IT processes, such as Splunk, are only like to increase. What will be interesting to watch is whether the tools and services being acquired by those companies wind up being the DevOps tail that wags the proverbial ITIL dog.

    — Mike Vizard

  • Puppet Aims to Automate Vulnerability Remediation

    Puppet Aims to Automate Vulnerability Remediation

    Puppet today unveiled Puppet Remediate software, which makes it easier to prioritize and remediate software vulnerabilities automatically.

    Matt Waxman, vice president of products for Puppet, said Puppet Remediate builds on existing automation capabilities in the Puppet platform to make it easier for DevOps teams to focus on addressing vulnerabilities. Most existing approaches to addressing vulnerabilities rely on manual processes that often result in vulnerabilities not being addressed in an especially timely manner, he said.

    To accelerate that process, Puppet Remediate identifies vulnerabilities based on their potential severity and then gives DevOps teams the option to automatically remediate all known instances of that vulnerability, said Waxman. Puppet Remediate combines infrastructure data with vulnerability data gathered in real-time from Tenable, Qualys and Rapid7 to prioritize vulnerabilities.

    Puppet Remediate will not automatically remediate a vulnerability without the express approval of the DevOps team. That’s critical because in many instances the patch being applied still needs to be tested and vetted by the DevOps team, noted Waxman. Once approved, Puppet Remediate includes four pre-built tasks that allow DevOps teams to address more than 80% of the typical remediation workloads—importance because once a vulnerability is discovered, it’s not uncommon to find that same mistake has been made across many other software modules that have already been built and deployed.

    Deployed using Docker containers, Puppet Remediate relies on an agentless approach to vulnerability remediation that adds minimal overhead to either a Linux or Windows application environment, Waxman said. He added the goal is to make it easier for developers or cybersecurity teams to deploy Puppet Remediate on any platform.

    Waxman said the primary goal is to help organizations embrace best DevSecOps processes. In the absence of automation, the amount of time allocated to addressing vulnerabilities manually within existing applications often gets short shrift as developers race to meet deadlines for new applications. The irony, of course, is that each new application only serves to increase the number of potential vulnerabilities that need to be addressed. To restore order to vulnerability remediation process, Puppet is making the case for applying a proven IT automation framework to application security management.

    It may take a while for organizations to fully embrace automated application vulnerability remediation, but it would seem that, given the chronic shortage of cybersecurity professionals, adoption of these types of platforms is all but inevitable. There simply are not enough skilled cybersecurity professionals available to participate in every aspect of the application development and deployment process.

    At the very least, automated vulnerability remediation tools should inform developers of the mistakes being made most often. Over time, the number of instances of those vulnerabilities being discovered should decline as developers realize they are addressing the same issue repeatedly. Once that becomes obvious, hopefully that long-awaited teachable moment that eliminates that particular vulnerability from the application environment is finally at hand.

    — Mike Vizard

  • Catchpoint Expands Network Monitoring Service Reach

    Catchpoint Expands Network Monitoring Service Reach

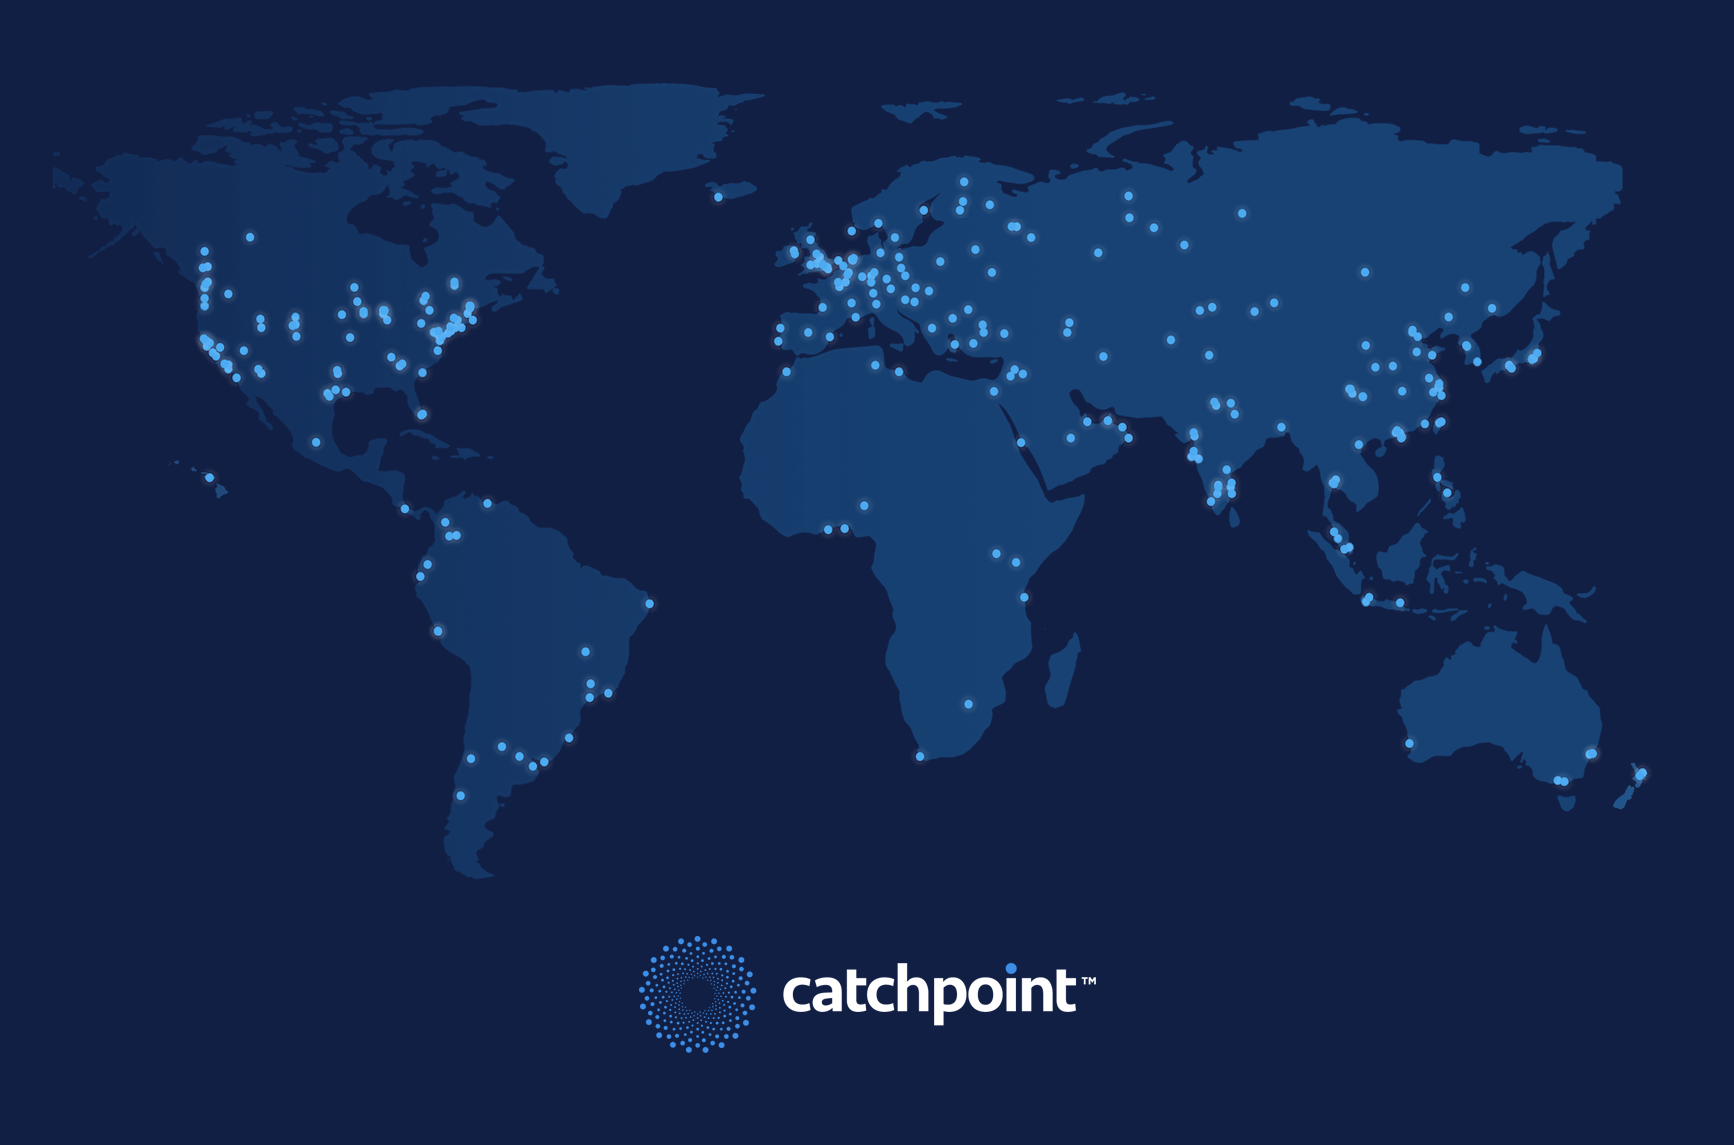
    Catchpoint has expanded the number of locations worldwide from which it is gathering telemetry data for its networking monitoring service to more than 825 sites.

    Drit Suljoti, chief product officer for Catchpoint, said as applications continue to become more distributed, the worlds of DevOps and network operations (NetOps) converge. DevOps teams need more visibility into how network latency issues anywhere in the world are impacting the digital experiences of their end users, said Suljoti.

    The Catchpoint monitoring service now extends to 200 cities worldwide, including 140 nodes in mainland China. In addition to monitoring critical backbone locations, Catchpoint has placed nodes in 133 public cloud locations and is now offering a free and seamless migration for companies looking to adopt a next-generation digital experience management (DEM) platform in place of Gomez and Keynote services from Dynatrace that recently were retired, said Suljoti.

    In much the same way DevOps teams rely on a variety of tools to monitor applications, they also need access to a service that continuously monitors the networks on which those applications depend, Suljoti said. That requirement has become more critical as the number of latency-sensitive applications such as those based on microservices increases, noted Suljoti. As organizations depend on those applications to drive a variety of digital business processes, visibility into how the network is impacting the application experience of end users can easily degrade, he added.

    Most organizations already have tools to monitor network performance within their own data center. However, creating the monitoring framework required to identify network performance issues across a global wide area network (WAN) would be cost-prohibitive for most organizations. When it comes to deploying applications that span multiple WANs, most DevOps teams are essentially blind.

    It’s still not clear within many organizations who is responsible for monitoring WAN services. Historically, NetOps teams have held this responsibility. However, Suljoti said that as DevOps processes continue to expand and mature, there is a more collaborative approach emerging that incorporates network monitoring tools within testing frameworks that organizations create within the context of a continuous integration/continuous deployment (CI/CD) process.

    In the meantime, pressure on existing WAN networks will only increase. In the absence of 5G services, the number of applications competing for access to bandwidth increases. Many organizations have no idea whether network service providers are really meeting the commitments they agreed to as part of the service level agreement (SLA) provided. As more application performance issues get traced back to the underlying network, frustration with the quality of network services is only going to mount. Before they can call network service providers to account, DevOps teams will need access to analytics that clearly show service level commitments are not being met.

    Of course, that may only elicit an apology from the network service provider. At the very least, however, DevOps teams will be able to make a much more informed decision concerning how they want to route application traffic going forward.

    — Mike Vizard

  • Virtual Instruments Acquires Metricly to Monitor Cloud Costs

    Virtual Instruments Acquires Metricly to Monitor Cloud Costs

    Virtual Instruments has acquired Metricly, a provider of a software-as-a-service (SaaS) application that help organizations to optimize the deployment of cloud application workloads.

    Tim Van Ash, senior vice president of products at Virtual Instruments, said Metricly employs machine learning algorithms to identify opportunities to improve performance and reduce costs. Those capabilities complement an existing VirtualWisdom platform from Virtual Instruments to apply machine learning algorithms to optimize IT operations, otherwise known as AIOps.

    Virtual Instruments focused exclusively on enhancing storage I/O performance before extending the reach of its portfolio to include server performance. With the acquisition of Metricly, the company is further extending the portfolio to span hybrid cloud computing environments, said Van Ash.

    Metricly, formerly known as Netuitive, provides analytics tools that are focused on helping organizations contain cloud costs.

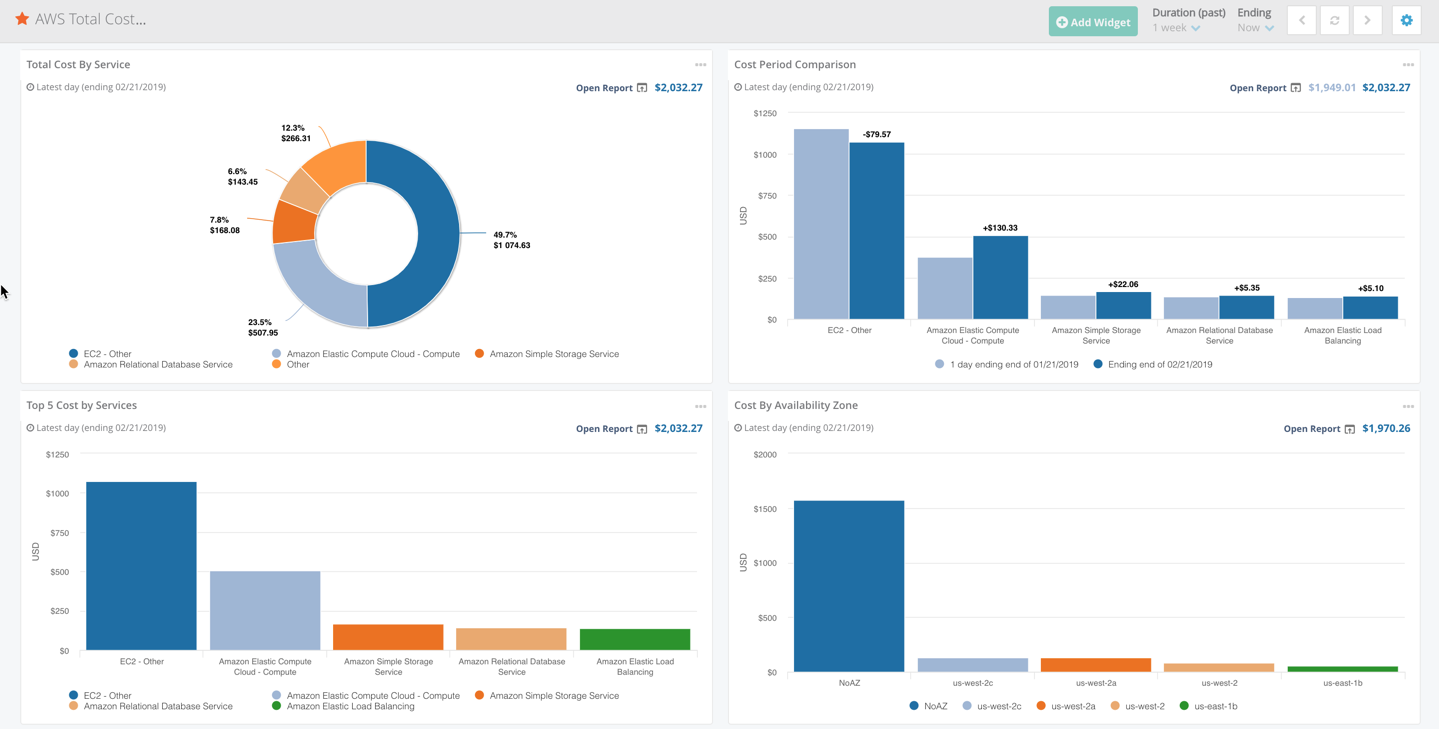
    Metricly CEO Bob Farzami said the company’s tools increasingly are being incorporated via application programming interfaces (APIs) into DevOps processes to provide visibility into costs, as the number of applications deployed in the cloud expands and increases. The acquisition of Metricly adds more than 50 integrations to open source DevOps technologies to the Virtual Instruments monitoring portfolio, which spans databases, messaging platforms, containers and cloud infrastructure services such as AWS Lambda, EC2, ECS, ASG, EMR, Microsoft Azure VMs and Load Balancer.

    Those integrations are critical because as the number of services being made available on AWS increases, the visibility organizations have into their real cloud costs becomes more difficult to both discern and limit, said Farzami. There are already hundreds of cloud services on AWS. Cloud service providers often count on organizations to forget how many instances of, for example, virtual machines they have spun up, only to be presented with an unexpected bill at the end of the month. Those issues will be further exacerbated as organizations more aggressively employ multiple cloud platforms.

    Many organizations are also seeing cloud costs rise over time as the volume of data being dynamically accessed by stateful applications increases. Once those costs reach a certain level, those organizations are realizing it costs less to repatriate those applications back on into on-premises IT environments. Metricly provides a mechanism through which organizations gain more visibility into their cloud costs in real-time, but also identify when specific cost thresholds are about to be reached.

    It will be at least somewhere between five to 10 years before even the majority of application workloads are running in the cloud. Today, after more than 10 years, only about 20% of application workloads are running in public clouds. There are a whole host of reasons organizations still prefer on-premises IT environments, ranging from regulatory requirements and performance to cybersecurity and simple inertia. Wherever workloads wind up being deployed, however, the one thing DevOps teams can count on going forward is that someone in the finance organization soon will be asking more pointed questions about how much it costs to run that workload.

    — Mike Vizard