Author: Mike Vizard

  • Five Great DevOps Job Opportunities

    Five Great DevOps Job Opportunities

    DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience.

    Our goal in these challenging economic times is to make it just that much easier for DevOps professionals to advance their careers.

    Of course, the pool of available DevOps talent is still relatively constrained, so when one DevOps professional takes on a new role it tends to create an opportunity for others.

    The five job postings shared this week are selected based on the company looking to hire, the vertical industry segment and naturally, the pay scale being offered.

    We’re also committed to providing additional insights into the state of the DevOps job market. In the meantime, for your consideration:

    Dice.com

    Oscar Technology
    Remote
    DevOps Engineer- Go Language
    $120,000 to $180,000

    LinkedIn

    Proprio
    Seattle, Wash
    Senior ML-DevOps Engineer
    $120,000 to $170,000

    SimplyHired

    DISH
    Littleton, Col.
    Senior DevOps Engineer
    $106,210 to $143,750.

    Indeed.com

    RumbleOn
    Irving, Tex.
    DevOps Engineer
    $115,000 to $135,000

    Monster.com

    PROLIM Corp.
    Washington, D.C.
    AWS DevOps Engineer
    $90,000 to $110,000

  • Dell Launches Project Frontier Initiative to Advance Edge Computing

    Dell Launches Project Frontier Initiative to Advance Edge Computing

    Dell Technologies this week launched Project Frontier initiative that promises to make deploying software at the edge simpler using integrated platforms that will be available in 2023.

    Announced at a Dell Technologies Summit event, Project Frontier will create an integrated edge computing platform for vertical industry segments such as manufacturing and retail.

    Dell CEO Michael Dell told conference attendees these platforms will help customers simplify, optimize and scale their edge applications in a secure way.

    The offerings can be centrally managed either by an internal IT operations team or via managed services that Dell provides to simplify onboarding and ensure zero-trust security. The overall goal is to reduce the number of instances that might require IT personnel in the field to configure and update them.

    According to a 2022 IDC survey, 42% of businesses say the most challenging aspect of edge deployments is putting together an entire edge solution. To address that challenge, Dell is also launching a Dell Edge Design Program through which it will collaborate with customers to further advance edge computing solutions.

    Through its Dell Validated Design program, the company is already building edge computing platforms for specific customers, but the goal now is to make it simpler to deploy edge computing platforms at scale.

    The number of application workloads being deployed on edge computing platforms is rising sharply as organizations seek to process and analyze data closer to the point where it is created and consumed. In fact, that shift is at the core of many digital business transformation initiatives that depend on edge computing platforms and devices running, for example, internet of things (IoT) applications to process data in near-real-time.

    A major issue—and one that remains largely unsolved, in many cases—is that organizations lack the ability to consistently deploy software on edge computing platforms. That results in a hodgepodge of homegrown tools deploying software on a wide range of edge computing platforms using manual processes that don’t scale well.

    It’s too early to say just how much software will ultimately be deployed on the edge, but there may come a day when there is more software at the edge than there is in the cloud. Of course, the real challenge will be unifying the management of DevOps processes, regardless of where any given piece of software might be deployed. In fact, Dell is betting that as edge computing continues to evolve, the line between edge computing and cloud computing will continue to blur until they are little more than natural extensions of each other.

    Dell, of course, is not the only IT vendor that views edge computing as the next trillion-dollar IT opportunity. There is already no shortage of options. The issue will be determining which IT vendor has the most robust edge computing ecosystem. In the meantime, DevOps teams would be well-advised to revisit DevOps workflows now with an eye toward making sure they can truly scale. After all, as edge computing platforms continue to proliferate, their ability to build, deploy, update and secure software is about to be put to the ultimate test.

  • Microsoft Expands DevOps Portfolio in the Cloud

    Microsoft Expands DevOps Portfolio in the Cloud

    At the Ignite conference this week, Microsoft launched a slew of updates to its DevOps portfolio as part of an effort to make it simpler to build, manage and secure cloud applications.

    Microsoft is adding Azure Deployment Environments, available in preview, that enable developer teams to invoke a set of best practices to quickly spin up application infrastructure using project-based templates.

    Microsoft is also making generally available Visual Studio Image for Dev Box, a self-service environment for accessing workstations on the Microsoft Azure cloud. Those images make it simpler to access Visual Studio functions and complimentary tools. Microsoft has also made generally available the latest version of the Visual Studio 2022 application development platform.

    In addition, Microsoft has signed an agreement with Postman to collaborate on integration that promises to accelerate the development of application programming interfaces (APIs) starting with the ability to both import and export APIs from Azure API management into Postman.

    Microsoft is also making generally available a predictive tool that employs machine learning algorithms to automatically scale virtual machines on Azure. In addition, updates to the Azure Monitor Log service now make it possible to ingest logs at a fifth of current costs and archive them for up to seven years. ​​​​​​​Microsoft is also now providing tools to migrate from legacy log agents to the Azure Monitor Agent (AMA) and has added Java profiling with a Java Flight Recorder (JFR) tool that collects data from a Java virtual machine and Java applications.

    In terms of managing application environments, Microsoft has now extended the reach of Azure Automanage to now include servers managed via the company’s Arc management platform, in addition to virtual machines running on the Azure cloud. Other capabilities added to Azure Automange include enhanced backup settings and different auditing modes for the compute server baselines and the ability to specify custom Log Analytics Workspaces and Azure tags to identify resources based on settings.

    Microsoft is also previewing an enhanced Azure remote support service through which Microsoft personnel will collect logs and commands to help resolve issues.

    Finally, in terms of securing applications, a GitHub Advanced Security for Azure DevOps tool that, now available in private preview, promises to make it simpler to identify and fix exposed secrets and vulnerable open source dependencies across the software life cycle using a CodeQL code scanner.

    At the same time, Microsoft is making available Microsoft Defender for DevOps to better secure code created to configure clouds. In addition, it will also enable DevOps teams to better prioritize their remediation efforts across multi-pipeline DevOps environments spanning multiple clouds. Microsoft Defender for DevOps is available in preview and supports GitHub and Azure DevOps with future support for other DevOps platforms planned.

    Another security addition available in preview is Microsoft Defender Cloud Security Posture Management (CSPM), which promises to provide contextual risk-based information via attack path analysis surfaced using a cloud security graph service to identify the most exploitable cloud resources. Microsoft has also made generally available a multi-cloud security framework for Microsoft Defender for Cloud to help organizations adopt DevSecOps best practices.

    Microsoft is also previewing support for agentless scanning for Microsoft Defender for Servers and an expansion of Microsoft Defender for Containers that adds support for Amazon Web Services Elastic Container Registry.

    Microsoft CEO Satya Nadella told conference attendees that Microsoft is making a concerted effort to natively embed security capabilities within its platforms to reduce the total cost of security. Many of the tools DevOps teams rely on today don’t integrate well, which is challenging at a time when application environments are becoming more dynamic as more cloud-native applications are deployed.

    It’s too early to say how much better security will entice organizations to opt for one cloud platform versus another. But it is almost certain that cloud service providers will be expected to contribute to securing software supply chains.

  • Google Looks to Secure Software Supply Chains

    Google Looks to Secure Software Supply Chains

    At the Google Cloud Next ’22 conference, Google today launched a managed Software Delivery Shield (SDS) service to enable DevOps team to store, manage and secure the build artifacts in Artifact Registry. At its core, SDS is based on a trust-based policy engine to establish, maintain and verify a chain of trust across the software supply chain.

    In addition, Google has updated its container analysis tool to include vulnerability scanning for Maven and Go containers along with preview support for non-containerized Maven packages.

    The managed Software Delivery Shield service spans a range of Google runtimes environments, including Google Kubernetes Engine (GKE), Cloud Code, Cloud Build, Cloud Deploy, Artifact Registry and Binary Authorization. Cloud Build also now officially supports Supply chain Levels for Software Artifacts (SLSA) Level 3 best practices by default in addition to generating authenticated and non-falsifiable build provenance for both containerized applications and non-containerized Maven and Python packages.

    GKE, in preview now, provides detailed assessments, assigns severity ratings and surfaces the security posture of the clusters and workloads, including insights into operating system vulnerabilities, workload configurations and other actionable insights. Log data can now also be captured while security event information can be routed to, for example, a security information and event management (SIEM) platform.

    The Google Cloud Run serverless platform can also, in preview, display software supply chain security insights such as SLSA build-level compliance, build provenance and vulnerabilities found in running services.

    At the same time, Google is also making available in preview Cloud Workstations, which provide fully managed secure development environments on Google Cloud that can be accessed via a browser. Built-in security capabilities include virtual private cloud (VPC) controls, no local storage of source code, private ingress/egress, forced image updates and identity access management (IAM) policies.

    Finally, the Cloud Code plug-in for integrated development environments (IDEs) now includes a preview of Source Protect to give developers real-time security feedback in the form of vulnerability dependencies and license reporting as they write code.
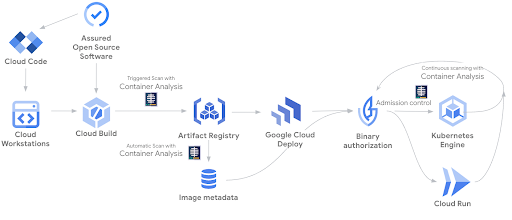
    Collectively, Google claimed it now provides more than 250 curated packages across Java and Python with verified provenance. It also automatically generates a software bill of materials (SBOM) to create an inventory of all components and dependencies.

    Historically, cloud service providers have been advocating a shared responsibility approach to cloud security that required organizations to not only secure their applications but also the way cloud infrastructure is provisioned. The challenge is developers generally provision cloud infrastructure themselves even though they generally have limited cybersecurity expertise. Too many developers assume the underlying cloud infrastructure is more secure than it actually is.

    Now, cloud service providers are extending the security services they provide at a time when organizations are making security a bigger factor in determining where to build and deploy applications.

    Sunil Putti, vice president and general manager for Google Cloud Platform, said Google is attempting to make cybersecurity invisible to developers in the sense that guardrails will automatically be embedded within the platform.

    The issue is that cloud computing environments are becoming more complex as new classes of cloud-native applications are deployed alongside legacy monolithic applications. Complexity, as always, is the enemy of cybersecurity.

  • GitLab Allies With Google to Improve Developer Productivity

    GitLab Allies With Google to Improve Developer Productivity

    GitLab Inc., in collaboration with Google, today launched an open source Cloud Seed tool that makes it simpler for DevOps teams to consume Google Cloud Platform (GCP) resources.

    The Cloud Seed tool, announced at the virtual Google Cloud Next ’22 conference, is integrated within the GitLab web UI to make it simpler for developers to consume Google cloud resources—such as Cloud Run for building and deploying containerized applications—and the managed Cloud SQL database service.

    Nima Badiey, global vice president of alliances for GitLab, said the goal is to reduce friction that would otherwise be created by requiring developers to write code to consume these services using a set of lower-level application programming interfaces (APIs).

    That self-service approach not only improves productivity but provides the added benefit of reducing the odds those services might be misconfigured in a way that creates a cybersecurity vulnerability, he added.

    As it seeks to gain ground on Amazon Web Services (AWS) and Microsoft, Google has a vested interest in working with providers of DevOps platforms to make it simpler for developers to consume cloud resources. The challenge is that developers often make mistakes when they programmatically invoke cloud services. Those resulting misconfigurations are all too often not discovered and remediated until after there has been some type of cybersecurity incident.

    In the wake of a series of high-profile breaches of software supply chains, there is a lot more focus on security. The challenge, of course, is finding a way to ensure application development platforms are as secure as possible without slowing down the rate at which software is developed and deployed. Achieving that goal requires the right mix of policies, training and systems, said Badiey.

    Most organizations are trying to strike a balance between the need for greater security and their need to attract and retain developer talent. In theory, the rise of DevSecOps best practices is pushing more responsibility for security further left toward developers. However, most developers have little to no cybersecurity expertise, so it’s clear more guardrails need to be built into DevOps tools and platforms to prevent cybersecurity mistakes from being made.

    It’s not clear how much improved developer productivity and greater security will drive organizations toward one cloud platform versus another, but in an age where many more organizations now routinely employ two or more cloud platforms, it could make a significant difference. Developers don’t especially enjoy remediating applications after they are deployed in a production environment because they have generally already moved on to other projects. IT operations and cybersecurity professionals are also likely to nudge developers toward platforms that create the least amount of operational overhead for them.

    Regardless, one thing that is certain is compliance requirements are about to become stricter for all concerned as scrutiny of software supply chains intensifies in the months ahead. The issue now is how to proactively address those requirements before they become a much larger issue.

  • Allstacks Adds Alert Capability to VSM Platform

    Allstacks Adds Alert Capability to VSM Platform

    Allstacks has added an alert capability to its software-as-a-service (SaaS) value stream management platform that automatically notifies DevOps teams when software project goals and deadlines are likely to be missed.

    The core Allstacks platform employs machine learning algorithms and artificial intelligence (AI) models to keep track of pull requests, commits and card changes via a set of dashboards that are designed to be accessible to anyone in an organization.

    The Allstacks Alerts capability makes it possible to notify those stakeholders via email or Slack any time a specific indicator, such as a pull request, has been open for four days, which would suggest risks of delays have increased. Support for Microsoft Teams will be added early next year.

    Adam Dahlgren, senior vice president of product for Allstacks, said the goal is to leverage the advanced analytics built into the platform to surface thoughtful observability insights versus simply firing off a series of generic alerts that lack any context.

    Value stream management (VSM) platforms such as Allstacks automatically take technical metrics collected via DevOps tools and correlate them to key performance indicators (KPIs) defined by business leaders. The concept of value stream management traces its lineage back to lean manufacturing methods, which called for each step of a manufacturing process to be continuously measured. As software development has evolved from being a craft to a highly-automated process using DevOps best practices, an appreciation for the value of monitoring the impact of missed software development deadlines on the business has grown as organizations realize how dependent they are on software.

    In fact, many organizations are discovering there is a clear disconnect between their business goals and software development processes. Business leaders are especially anxious to understand how a software development project delay might impact future revenue projections at a time when economic conditions are the most uncertain they’ve been in recent memory.

    VSM platforms also make it possible to track KPIs spanning multiple software development projects; the hope is that doing so will make it easier to see where resources should be reassigned as various bottlenecks are encountered. In the long term, Allstacks is also working toward adding scenario planning tools to make it easier for IT and business leaders to model “what-if” scenarios, added Dahlgren.

    It’s not clear how much organizations are willing to invest in VSM platforms, but the need for them is becoming more acute. The challenge many organizations still face is making sure they have the tools in place to collect the appropriate technical metrics. A SaaS-based platform should make it simpler to achieve that goal and to apply algorithms to what can quickly become a large corpus of data.

    Of course, it’s still early days as far as the adoption of VSM platforms are concerned. But there’s no doubt the divide between application development teams and the rest of the business is continuing to narrow. Less clear is to what degree that increased visibility will lead to a higher degree of empathy between dev teams and the business.

  • BMC Survey Surfaces DevOps Mainframe Progress

    BMC Survey Surfaces DevOps Mainframe Progress

    A global survey of 1,000 executives and IT professionals that rely on mainframes found 70% are now employing DevOps processes to build and deploy applications on the venerable platform, with 60% of those respondents now deploying applications faster. A full 80% of respondents also wanted to deploy mainframe applications faster, according to the survey.

    The survey also found that integration of IT processes across mainframes and distributed computing environments has increased, with well over half (57%) now sharing platform operations roles. A total of 44% reported site reliability engineering (SRE) as a shared role that spans both platforms.

    Applications developed in-house are being delivered faster than a year ago, reinforcing the mainframe’s business value, with 76% realizing value in under 12 months.

    More than half of respondents (53%) said their organizations is also implementing DevSecOps practices in a way that spans all those platforms. The top priority for organizations that have mainframes is security and compliance (67%), the survey also found.

    Nearly a third have also adopted artificial intelligence for IT operations (AIOps) across mainframes and distributed computing platforms. Survey respondents that have adopted both mainframe AIOps and DevOps reported they are gaining visibility into service issues 70% faster, with 41% improving uptime and availability, according to the survey.

    Finally, the survey found 95% of respondents still had a positive perception of the mainframe as a platform for running applications, with 62% reporting transaction volumes on the mainframe are increasing. More than half (55%) also noted workload volatility and unpredictability is increasing. A similar percentage (55%) also reported more than half of their data is on a mainframe.

    John McKenny, senior vice president and general manager for Intelligent Z mainframe optimization and transformation at BMC, said IT teams in a downturn are, as usual, trying get the most out of their existing investments. The thing that is changing most is the mainframe is now becoming more integrated with distributed computing environments as IT teams strive to achieve that goal, he added.

    In general, there’s still much work to be done in terms of furthering adoption of DevOps best practices in mainframe environments, noted McKenny. Each organization will most likely determine at what level to apply those practices based on the frequency at which applications running on mainframes need to be updated. There are still plenty of applications running on mainframes that might not need to be updated for many years, but as organizations embrace digital business transformation initiatives, the need to update mainframe applications more frequently has increased, noted McKenny.

    Regardless of the type of application deployed, it’s apparent that the days when mainframes were managed in isolation from the rest of a distributed computing environment are slowly coming to an end. A mainframe is, arguably, just another node for deploying applications. The one major difference is that, as platforms are considered, the mainframe is a lot more secure, said McKenny.

    The challenge and the opportunity now, of course, is as much about changing attitudes toward the mainframe as it is making the right DevOps tools available to the IT teams tasked with managing heterogeneous IT environments.

  • Endor Labs Applies Graph Analysis to Secure Software Supply Chains

    Endor Labs Applies Graph Analysis to Secure Software Supply Chains

    Endor Labs exited stealth mode today to launch a platform that applies graph analysis to identify the depth of dependencies that exist within an application.

    Fresh from raising $25 million in funding, Endor Labs CEO Varun Badhwar said the Dependency Lifecycle Management Platform makes it simpler for organizations to manage dependencies within applications that can involve tens of thousands of components.

    Existing software composition analysis (SCA) tools are not able to as accurately identify the dependencies between software components because they generate too many false positives, he added.

    To address that problem, the Dependency Lifecycle Management Platform provides the equivalent of a credit risk score for each component employed with an application environment, said Badhwar.

    Designed to run out-of-band within a continuous integration process, the Dependency Lifecycle Management Platform is currently being made available via a private beta program.

    On average, bout 80% of an application is made up of open source components that developers downloaded from a repository. The challenge is that many of those components have known vulnerabilities. The Dependency Lifecycle Management Platform makes it simpler to both identify those vulnerabilities during the build process and find components that might be impacted by a newly discovered zero-day vulnerability, said Badhwar.

    Overall, the Dependency Lifecycle Management Platform improves the productivity of both application development and cybersecurity teams by streamlining vulnerability management, he added.

    Having a full understanding of their dependency graph also lets customers generate and analyze accurate software bills of materials (SBOMs) as applications are dynamically updated, noted Badhwar.

    In the wake of a series of high-profile breaches, there has been increased focus on software supply chains. The challenge is most developers don’t have a lot of cybersecurity expertise and, even when provided with tools to identify vulnerabilities, there are simply too many alerts generated. In the absence of any context, most of those alerts simply wind up being ignored. In the meantime, the rate at which new applications are being deployed and updated isn’t slowing down, especially as more organizations embrace cloud-native applications that make it easier to rip and replace software components.

    It’s going to take years for organizations to implement DevSecOps best practices to teach developers how to build more secure applications, but that journey needs to begin with tools that make it simpler for developers to address issues before applications are deployed. The best way to combat application vulnerabilities is to make sure they don’t manifest themselves in code in the first place. Based on the number of vulnerabilities that continue to find their way into application environments, it’s apparent that the current processes being used to build applications are fundamentally broken.

    At this juncture, it will take years to fix the application development and deployment process, but as more secure applications eventually replace millions of insecure applications the overall security posture of organizations will steadily improve. The issue now is finding ways to achieve that goal before another known vulnerability leads to another major security crisis.

  • Five Great DevOps Job Opportunities

    Five Great DevOps Job Opportunities

    DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience.

    Our goal in these challenging economic times is to make it easier for DevOps professionals to advance their careers.

    Of course, the pool of available DevOps talent is still relatively constrained, so when one DevOps professional takes on a new role it tends to create an opportunity for others.

    The five job postings shared this week are selected based on the company looking to hire, the vertical industry segment and, naturally, the pay scale being offered.

    We’re also committed to providing additional insights into the state of the DevOps job market. In the meantime, for your consideration:

    Indeed.com

    Harnham
    Remote
    Senior DevOps Engineer
    $160,000 to $180,000

    Monster.com

    Riley Consulting Services
    Folsom, CA.
    Senior Full-Stack .Net Developer
    $150,000 to $180,000

    LinkedIn

    Flowhub
    Remote
    Senior DevOps Engineer
    $140,000 to $160,000

    Dice.com

    Northrup Grumman
    Aurora, Col.
    Senior Principal DevOps Engineering Lead
    $120,000 to $180,000

    SimplyHired.com

    OBMedia
    Remote
    Senior DevOps Engineer
    $120,000 to $160,000

  • ServiceNow Acquires Era Software to Unify Observability

    ServiceNow Acquires Era Software to Unify Observability

    ServiceNow today announced it has agreed to acquire Era Software as part of an effort to add support for log data to the Lightstep observability platform the company acquired last year.

    Ben Sigelman, general manager for the Lightstep business unit at ServiceNow, said rather than reinventing the same log management capability that Era Software already has, it makes more sense to integrate that capability with the Lightstep platform that collects metrics and traces.

    The integration of those two platforms will then make it possible to unify observability rather than requiring DevOps teams to navigate two separate silos, he added.

    As observability continues to evolve and mature, the most immediate goal is to make it simpler to navigate the alert storm that inevitably ensues any time there is a disruption, said Sigelman. The alert storms generally occur after there has been a change made, but unraveling how exactly that change impacted an IT environment is challenging, he noted.

    An observability platform reduces the time and effort necessary to achieve that goal by surfacing a set of statistics that guide DevOps teams through that process, added Sigelman. The challenge, of course, has always been finding an efficient means of storing all the telemetry data that’s generated. In fact, as organizations start to deploy microservices-based cloud-native applications, many of them are starting to see the amount of telemetry data increase exponentially.

    Era Software uses an object storage system to index and analyze log data collected from cloud applications, Kubernetes and IT infrastructure platforms. The company has also made available in beta an Era Streams tool that reduces the volume of observability data collected without sacrificing fidelity by dynamically reconfiguring data pipelines in real-time.

    Once the acquisition is completed, log data analytics will then be shared with the IT service management (ITSM) tools that ServiceNow provides alongside the Lightstep observability platform. The goal is to make it easier to correlate those IT events with their potential impact on the business, said Sigelman.

    Era Software CEO Todd Persen said the long-term 10-year goal is to get to the point where issues are both automatically detected and remediated. In the meantime, the amount of context switching that IT teams encounter can be sharply reduced via a unified observability platform.

    There is, of course, no shortage of unified observability platforms these days. DevOps teams have also been relying on legacy monitoring tools that track specific metrics for years. The issue is that those legacy monitoring tools only track a narrow range of pre-determined metrics. As IT environments become more complex, the need to launch more open-ended queries to determine the root cause of IT disruption has become more pronounced.

    It may be some time before observability platforms are widely adopted, but the need for them is generally apparent to anyone managing a modern IT environment. Less clear is the degree to which observability platforms will remove the need for legacy monitoring tools; however, right now the focus should be on gaining as much visibility and transparency as possible into what are still opaque IT environments.