Author: Mike Vizard

  • Cisco Streamlines Licensing Options for IT Operations Platform

    Cisco Streamlines Licensing Options for IT Operations Platform

    Cisco has reduced the number of licensing options for its Intersight operations platform to two as part of an effort to make the software-as-a-service (SaaS) platform for managing on-premises and cloud computing environments more accessible.

    In addition, Cisco has added a Cisco UCS X-series Modular System to its portfolio based on a two-socket server configured with 4th Gen Intel Xeon Scalable processors and an instance of Intersight that has been extended to make it possible to apply policies that limit energy consumption.

    Mahesh Natarajan, senior director of product management of cloud and compute for Cisco, said Intersight is a complement to the management platform the company already bundles with its Unified Compute Systems (UCS) platforms for on-premises IT environments.

    Essentials enables management of server profiles/policies, managing firmware updates and proactive health monitoring and security advisories along with many other capabilities. The Advantage option adds low-code/no-code orchestration, more advanced server operations, multi-domain visibility and third-party integration with, for example, third-party IT service management (ITSM) platforms.

    In the wake of the COVID-19 pandemic, there’s been a shift toward cloud-based platforms that make it simpler for IT teams to centrally manage multiple IT environments from anywhere. Cisco Intersight, in addition to supporting Cisco servers, has been integrated with cloud services from Amazon Web Services (AWS), Google and Microsoft to achieve that goal.

    In fact, as the management of IT continues to converge across multiple platforms, the concept of a data center has become something of a misnomer, said Natarajan. Integrated application workloads are now routinely distributed across on-premises and cloud computing platforms that are simpler to manage using a consistent set of policies, he added.

    A SaaS platform also provides the added benefit of reducing the total cost of IT because the need to deploy management platforms for each environment is sharply reduced, noted Natarajan.

    Very few organizations are running all their application workloads in one environment, so the need to reduce costs by finding more efficient ways to manage IT operations is becoming a more pressing issue. Most IT teams are trying to limit the number of full-time employees they might otherwise hire by trying to improve the overall productivity of the teams they do have.

    Of course, centralizing the management of IT is as much a cultural challenge as it is technical. Each IT team that deploys a workload on a platform has a natural bias toward using the management framework made available by the platform provider. Each of those platform providers is now extending its reach as part of an effort to become the one control plane that rules them all. Cloud service providers, for example, are extending the reach of their management frameworks into both local data centers and edge computing environments.

    Regardless of preferences, the cost of licensing multiple management platforms can quickly become prohibitive, especially if they provide redundant capabilities. Organizations looking to reduce the total cost of IT would much rather reduce licensing costs than lay off the IT staff that drive a wide range of digital processes. The challenge, as always, is getting everyone in the IT organization to agree on what that one management platform should be.

  • New Relic Adds Module to Surface Code Metrics

    New Relic Adds Module to Surface Code Metrics

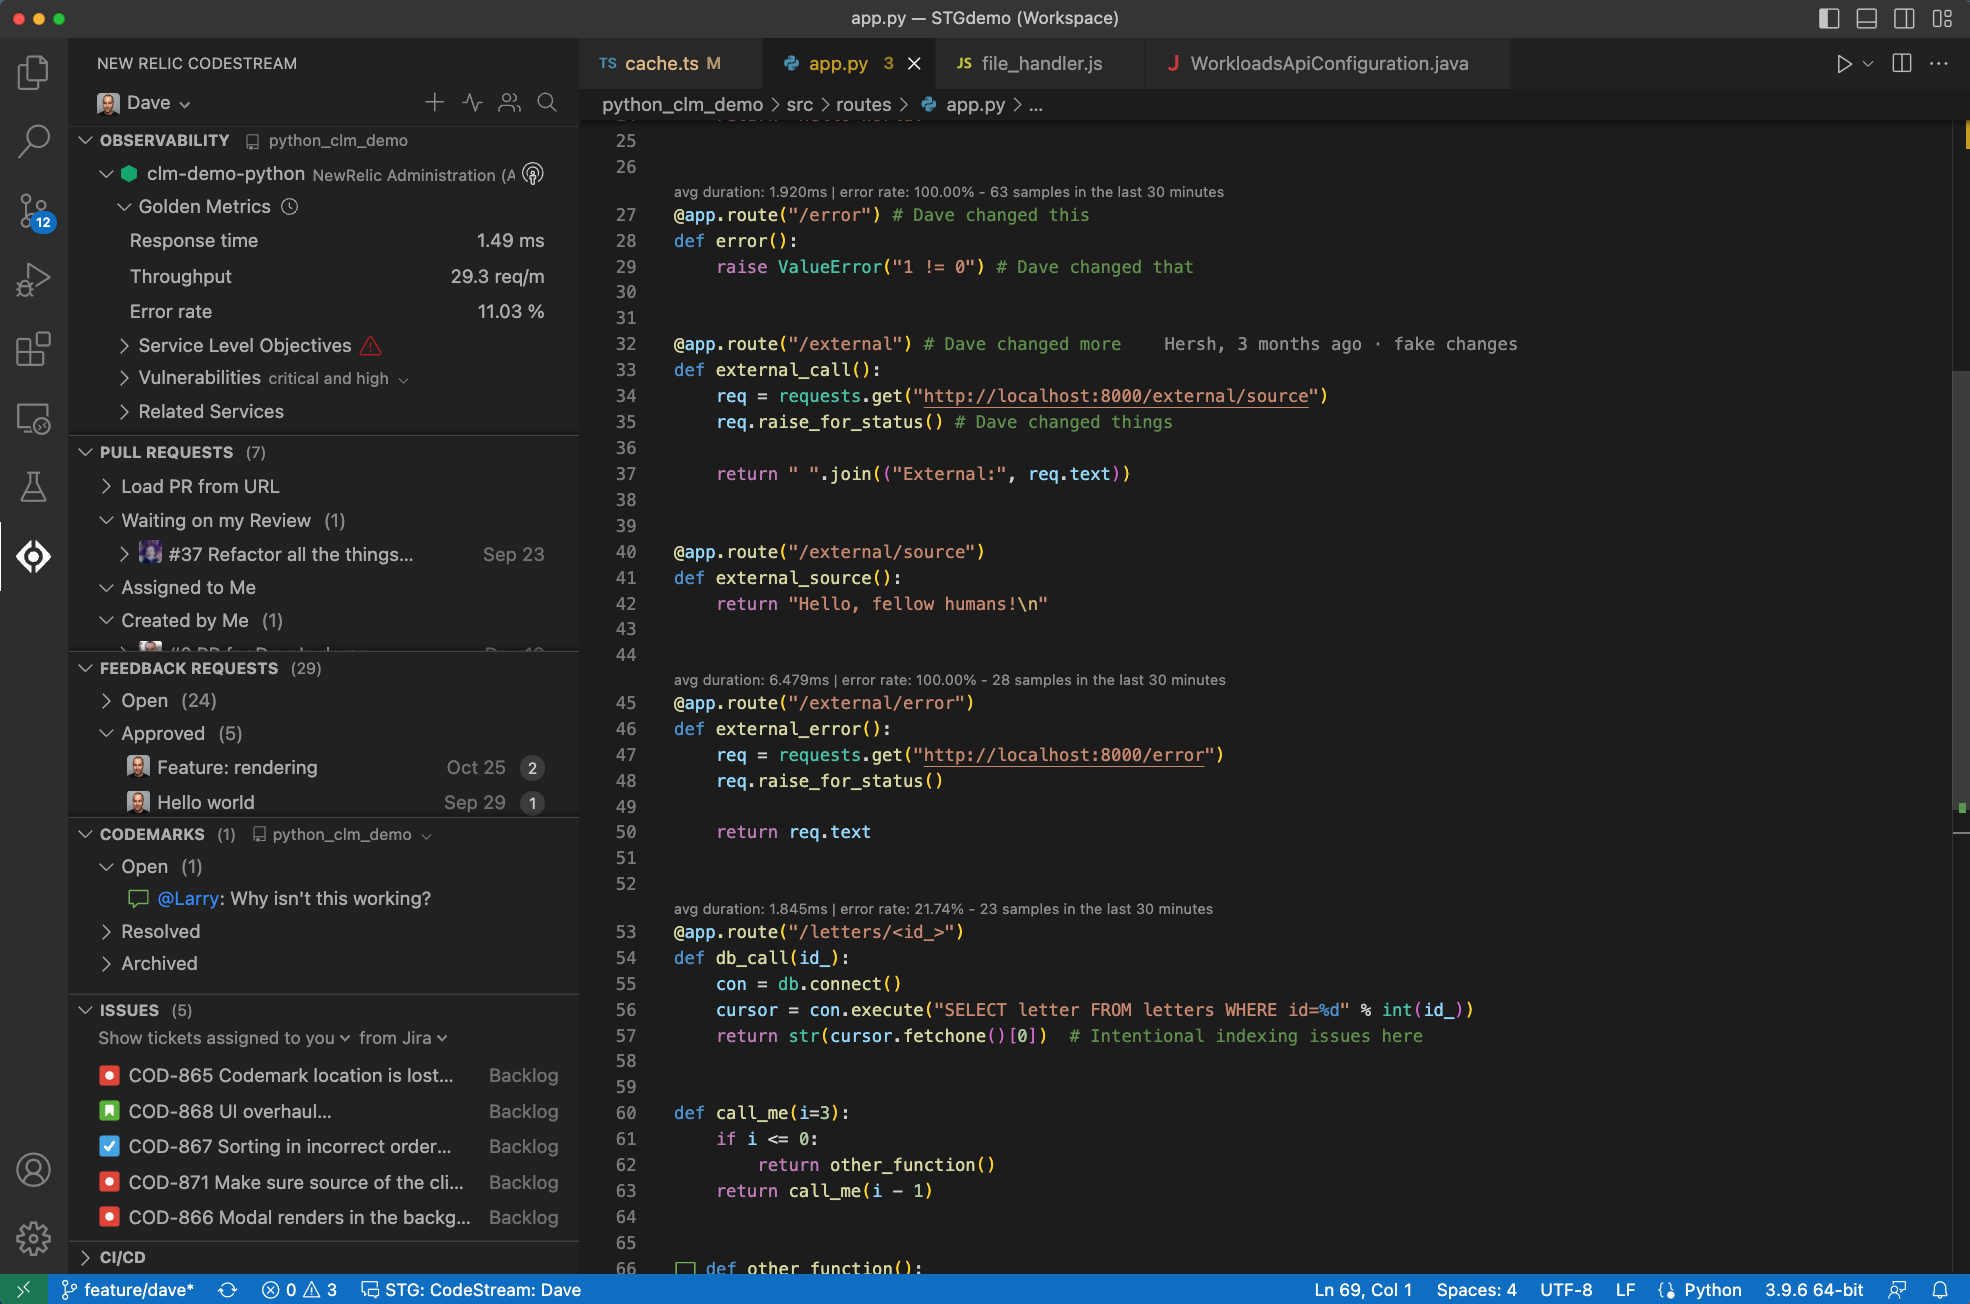
    New Relic today added a free CodeStream module to its observability platform to give developers access to metrics and telemetry data that will enable them to write higher-quality code faster.

    Peter Pezaris, group vice president and general manager of strategy and experience for New Relic, said this capability is part of an effort to shift observability left toward developers to optimize code as it is written and after it is deployed.

    CodeStream surfaces metrics and telemetry data within the integrated development environment (IDE) developers use to write software. Telemetry metrics are displayed as a line of text above the code or in the debugging tool used to troubleshoot an application. Alternatively, developers can view metrics via an observability panel at the service level. They can also view performance metrics such as error rates and response times for related services.

    That approach eliminates the need to wait for IT operations teams to surface issues that usually don’t manifest until long after the code in question was originally developed, noted Pezaris.

    The overall goal is to provide development teams with frictionless access to observability data at every stage of the software development life cycle, he added. That analysis capability will result in faster mean-time-to-detection (MTTD), mean-time-to-resolution (MTTR) and, ultimately, shorter development cycles, said Pezaris.

    Organizations should also be able to reduce technical debt faster by making it easier to identify issues that, for example, adversely impact application performance, he noted. That activity can be especially challenging because developers often inherit code written by someone else that often lacks clear documentation. CodeStream makes it simpler to onboard a developer to any application modernization initiative that has been launched to reduce technical debt, said Pezaris.

    A recent New Relic survey found only 27% of respondents have achieved full-stack observability, and only 5% claimed they have a mature observability practice in place. A third (33%) of respondents also said they still primarily detect outages manually or based on complaints, the survey found.

    On the plus side, the survey also found nearly three-quarters of respondents said C-suite executives in their organization are advocates of observability, and more than three-quarters of respondents (78%) saw observability as a key enabler for achieving core business goals. However, more than half (52%) of respondents said they experienced high-business-impact outages once per week or more, and 29% said they take more than an hour to resolve those outages.

    A full 82% of respondents said they use four or more tools to monitor the health of their systems. Only 7% said their telemetry data is entirely unified and only 13% said the visualization or dashboarding of that data is entirely unified. Nearly half of the respondents (47%) said they would prefer to have a single, consolidated observability platform, but only 2% said they currently used one tool for observability.

    Regardless of the approach to observability, it is clear that development and IT operations teams need to be looking at the same metrics and telemetry data at the same time to collaborate effectively.

  • Zenhub Brings Issues Management to Project Management Platform

    Zenhub Brings Issues Management to Project Management Platform

    Zenhub today announced it is adding an issue management module that makes it simpler for stakeholders to collaborate with developers on application development projects without having to log into a GitHub repository.

    Fresh from raising an additional $10 million in capital, Zenhub co-founder Aaron Upright said Zenhub Issues is a plug-in for a project management application the company developed for GitHub environments to better streamline software development life cycles. The issue is that many application stakeholders, such as marketers, are not especially pre-disposed to logging into a repository for managing software components, he said.

    Zenhub Issues provides an alternative means for collaborating with developers that doesn’t require stakeholders to log into GitHub, he said. In addition, organizations no longer need to acquire additional GitHub licenses for those users, noted Upright. Many of those end users wind up with read-and-write access to software components, which creates unnecessary cybersecurity risks should their credentials be compromised, he noted.

    In some cases, organizations will also be able to eliminate the need for the project management applications many of those stakeholders have adopted because they can track issues via Zenhub Issues, he added.

    Many organizations’ entire business strategies now revolve around accelerating the rate at which software development projects can be completed. Many elements of those projects, however, can’t go forward until a specific component upon which it depends is completed, so project management has become a critical function. Investors are holding business leaders more accountable for software delivery timetables that have direct implications on revenue generation, so that pressure naturally falls on DevOps teams.

    It’s not surprising that there aren’t a wider range of end users of project management applications as various stakeholders seek to keep closer tabs on how updates to schedule impact their planning cycle. Everyone from the sales team to the board of directors now wants more visibility into the rate at which software development projects are being completed. The challenge DevOps teams face is that software development is an inexact science. Application development projects can just as easily fall behind schedule as they can leap ahead depending on how well code is written.

    Regardless of how application development projects are managed, the relationship between DevOps teams and the rest of the organization has fundamentally changed. Unfortunately, expectations are not always realistically aligned with available development resources. A project management application that is widely employed across an organization should make that apparent to all interested stakeholders. In theory, at least, that should result in either the hiring of additional developers or a reassessment of the business strategy.

    One way or another, project management applications designed for managing software development projects now play a pivotal role in business planning. The challenge is finding a way to populate those applications with the data needed without requiring developers to help enter data that can already be easily pulled from the DevOps tools and platforms. Otherwise, instead of being viewed as a benefit, the entire project management process becomes one more tedious task that development teams are not going to prioritize over writing code.

  • IT Teams Need to Do More With Increased Budgets

    IT Teams Need to Do More With Increased Budgets

    A survey of 600 C-suite and IT decision-makers published today found the majority of organizations are trying to make increased IT budgets stretch even further as costs rise and the number of workloads deployed continues to increase steadily.

    Conducted by SoftwareOne Holding AG, a provider of software and IT services, the survey found 93% of respondents expected IT budgets to increase, with 83% planning to invest more in application modernization. However, 83% also noted they are under pressure to stretch budgets even further as part of an effort to increase agility (46%), improve customer experience (45%) and improve security to support remote workforces (45%). A full 92% said they would be increasing investments in security.

    The core issue that IT leaders are wrestling with appears to stem from increased cloud costs. The survey found the primary causes of those increased costs are inflation-related price hikes passed along by cloud service providers (41%), workloads exceeding planned capacity (40%), transformation initiatives that are cloud-dependent (40%), fewer cloud discounts (37%), lack of visibility into and management of cloud costs (34%), overprovisioning (34%), repercussions from previous lift and shift efforts (34%) and shadow IT (30%).

    Craig Thomson, senior vice president of cloud and application services at SoftwareOne, said that technical debt is having a significant downstream impact across organizations. For example, the survey found 72% of respondents reported that digital transformation initiatives are falling behind, with 38% noting the accumulation of this debt stems from rushed cloud migrations throughout the pandemic. Just under a third (31%) failed to optimize workloads before commencing the migration. More than a third (38%) admitted their organization miscalculated the cloud budget.

    Progress is being made, however, with 45% of respondents reporting they have improved transparency and control of cloud costs. A full 80% planned to increase their investment in financial operations (FinOps) to achieve this, and 39% said they would use cloud-native tools to reduce licensing costs.

    Those efforts suggested IT leaders are being very deliberate in their approaches to reining in costs while at the same time embracing best practices, said Thomson. IT leaders have finally started to realize the cloud is not so much a destination for workloads as much as it is an operating model, he added.

    The challenge is that cloud computing environments are becoming more complex to manage as organizations deploy cloud-native applications on Kubernetes clusters and serverless computing frameworks deployed alongside legacy monolithic applications that were lifted and shifted to the cloud. Organizations will need to invest more in automation to make up for an IT talent gap that prevents organizations from accelerating the rate at which they can build and deploy cloud applications, noted Thomson.

    On the plus side, it appears organizations are willing to allocate budgets to achieve their IT goals. The issue is that, as more organizations become more dependent on software, they are asking IT teams to do even more with the resources at hand. The degree to which that can be achieved, of course, is almost wholly dependent on how much of the technical debt that already exists in the cloud can be retired.

  • Survey: More Cybersecurity Pros Embedded in DevOps Teams

    Survey: More Cybersecurity Pros Embedded in DevOps Teams

    A survey of 2,500 C-level executives published today by Palo Alto Networks found 81% of organizations have embedded cybersecurity professionals within their DevOps teams.

    Despite the presence of those cybersecurity professionals, however, the survey also suggested there is much work to do in terms of optimizing DevSecOps workflows. A full 90% of organizations cannot detect, contain and resolve cybersecurity threats within an hour, the survey found.

    Bob West, chief security officer for Palo Alto Networks, said most of the challenges associated with DevSecOps are directly related to persistent cloud security issues. More than three-quarters of organizations (78%) said they had distributed responsibility for cloud security, but almost half (47%) said a majority of their workforce still does not understand their security responsibilities.

    In many cases, developers with little to no cybersecurity expertise are responsible for provisioning cloud infrastructure. As a result, misconfigurations that create security issues are commonplace, noted West. That’s especially problematic because three-quarters of organizations (75%) are deploying new or updated code to production weekly, with almost 40% committing new code daily, the survey found. Given that developers far outnumber cybersecurity professionals in most organizations, it remains challenging to ensure application code is secure, noted West.

    In addition to improving the overall state of cloud security, organizations need to focus on fundamentals such as training developers to be more mindful of cybersecurity issues, he added. Most developers never had any formal cybersecurity training, so it’s up to organizations to make sure that particular skills gap is closed, he noted. In addition, organizations need to make sure they have a robust set of patch management processes in place alongside a capability to manage permissions and entitlements, added West.

    Overall, the survey found organizations are using more than 30 security tools, on average, including six to 10 dedicated to cloud security. More than three-quarters of respondents (76%) said relying on multiple security tools created blind spots that affected their ability to prioritize risk and prevent threats. A full 80% said they would benefit from a centralized security solution that sits across all of their cloud accounts and services.

    One way or another, a rising tide of regulations focused on improving the security of software supply chains will force organizations to improve cloud security, said West. The survey showed there is a strong commitment in terms of making cybersecurity professionals an integral part of a DevOps workflow. The issue is that there are still a raft of training and process issues that need to be addressed at a time when cybercriminals are becoming increasingly adept at compromising applications both as they are developed and after they are deployed.

    Of course, training and modifying processes take time. DevSecOps is as much about changing culture as it is about acquiring new tools. DevOps teams are still highly committed to building and deploying applications as quickly as possible. The challenge is finding a way to insert a set of cybersecurity gates within those workflows without slowing down the pace at which applications are developed.

  • AWS Delivers on Latest Graviton3 Price/Performance Promise

    AWS Delivers on Latest Graviton3 Price/Performance Promise

    Amazon Web Services (AWS) has expanded the number of virtual machines based on the latest generation of its Graviton processors to include instances that support DDR-5 memory.

    The latest Amazon EC2 instance types, dubbed M7g and R7g, that are now generally available are based on the AWS Graviton3 processors developed using an architecture created by Arm. Previously, these instances were only available as part of a technology preview program.

    Rahul Kulkarni, director of product management at AWS, said these latest offerings take advantage of DDR-5 memory to provide 25% better performance than the previous sixth generation of Graviton instances. DDR5 memory increases the amount of bandwidth available by 50%, he noted.

    Graviton processors now provide the lowest-priced instance of virtual machines in addition to the best performance and overall price/performance across the AWS portfolio, Kulkarni added.

    AWS is making a case for employing its AWS Graviton processors for general-purpose workloads as more IT teams are being tasked with reducing costs as the overall number of applications being deployed in the cloud continues to increase. In fact, all of the top Fortune 50 companies have already deployed workloads on Graviton processors, noted Kulkarni.

    While it’s not clear how many applications are being developed to run natively on Arm processors, the process of refactoring existing applications to run on Arm processors is not as intensive for most applications as it was when previously moving applications from one class of processors to another.

    In addition, Kulkarni noted AWS has committed to providing a full range of DevOps services, including a continuous integration/continuous delivery (CI/CD) platform, to help facilitate any transition to Graviton processors.

    There are, of course, multiple strategies for containing cloud costs that range from committing to consuming a specified amount of compute resources annually at discounted rates to relying more on spot instances that are available for limited amounts of time. Regardless of approach, the days when developers were allowed to invoke cloud resources at will appear to have come to an end as enterprise IT organizations become more aware of the total cost of IT. As a result, many of them are adopting financial operations (FinOps) best practices to maximize the utilization of cloud infrastructure resources.

    AWS, like most cloud service providers, gives organizations a wide range of processor options. However, it’s apparent that AWS views Arm processors in the form of Graviton to be the most efficient from both a price and performance perspective. It’s not clear how quickly organizations are embracing Graviton in the cloud given the dominance of x86-based platforms, but it’s apparent there is now a clear alternative for general-purpose workloads. If fact, the more data-intensive those workloads become, the greater the interest in more efficient processor architectures.

    Of course, x86 platforms are not going away anytime soon. But as more Arm-based processors find their way into the enterprise, DevOps workflows will only become more challenging to manage.

  • Five Great DevOps Job Opportunities

    Five Great DevOps Job Opportunities

    DevOps.com is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience.

    Our goal in these challenging economic times is to make it easier for DevOps professionals to advance their careers. Of course, the pool of available DevOps talent is still relatively constrained, so when one DevOps professional takes on a new role, it creates an opportunity for others.

    The five job postings shared this week are selected based on the company looking to hire, the vertical industry segment and, naturally, the pay scale offered.

    We’re also committed to providing additional insights into the state of the DevOps job market. In the meantime, for your consideration:

    Monster.com

    REPS & Co.
    Remote
    Senior Software Engineer
    $120,000

    Dice.com

    AIT Global
    Jersey City, New Jersey
    DevOps Engineer
    $120,000 to $130,000

    Indeed.com

    Southwest Airlines
    Dallas, Texas
    Cloud DevOps Engineer
    $118,600

    SimplyHired

    Portrait Displays
    Pleasanton, California
    DevOps Engineer
    $110,000 to $140,000

    LinkedIn

    Peraton
    Chantilly, Virginia
    DevOps Engineer
    $72,500 to $181,300

  • Report Identifies Top 10 Open Source Software Risks

    Report Identifies Top 10 Open Source Software Risks

    Endor Labs, a provider of a platform for managing open source software, published a report that classifies the top 10 open source software risks of 2023. The company published the list as part of an effort to better educate application development teams about issues that can lead to software supply chain compromises. That list includes:

    Known Vulnerabilities: A version of a software component may contain vulnerable code that is accidentally introduced by its developers. When vulnerability details are publicly disclosed, there may not be a patch readily available.

    Unmaintained Software: A software component may not be actively developed or maintained anymore, resulting in patches for functional and non-functional bugs not being provided in a timely manner—if they’re provided at all.

    Name Confusion Attacks: Attackers may create components whose name resembles the names of legitimate open source or system components. This is also known as typosquatting. Bad actors might also attempt to mimic trustworthy authors (brandjacking) or play with common naming patterns in different languages or ecosystems (combosquatting).

    Compromise of Legitimate Package: Attackers may compromise resources that are part of an existing, legitimate project or associated distribution infrastructure to inject malicious code into software components.

    Outdated Software: A project may use an old, outdated version of a software component even though a newer, more secure version exists.

    Untracked Dependencies: Developers may not be aware of a dependency on a component because it is part of another upstream module they employed.

    License Risks: A software component or project may not have a license at all, may have one that is incompatible with the component’s or project’s intended use or whose requirements are not or cannot be met.

    Immature Software: An open source project may not apply development best practices such as having a standard versioning scheme or lacking a regression test suite, review guidelines or documentation.

    Unapproved Changes: A software component may change without giving developers the chance to notice, review or approve such changes because the download link points to an unversioned resource, a versioned resource has been modified or tampered with or due to an insecure data transfer.

    Unknown Origin: Details about the source code, build process or the distribution process of a software component may be unknown or non-verifiable.

    Endor Labs CEO Varun Badhwar said organizations need more visibility in the potential operational risks that come with increased reliance on open source software. That doesn’t mean organizations should use less open source software, but there are issues that many development teams may not always appreciate. A recent analysis of nearly 2,000 software packages published by Endor Labs, for example, found 95% of all application vulnerabilities can be traced back to a transitive dependency created when a developer employed an open source component.

    Regardless of the root cause, responsibility for application security continues to be pushed left toward application developers. The challenge is it’s not possible to achieve that goal without first knowing what issues developers and the DevSecOps teams that support them need to be focused on. Perfect application security is, of course, unattainable, but any reduction in the number of vulnerabilities littering the software landscape will go a long way toward reducing the current level of stress developers and DevOps teams experience.

  • Checkly Adds Monitoring-as-Code to Testing Platform

    Checkly Adds Monitoring-as-Code to Testing Platform

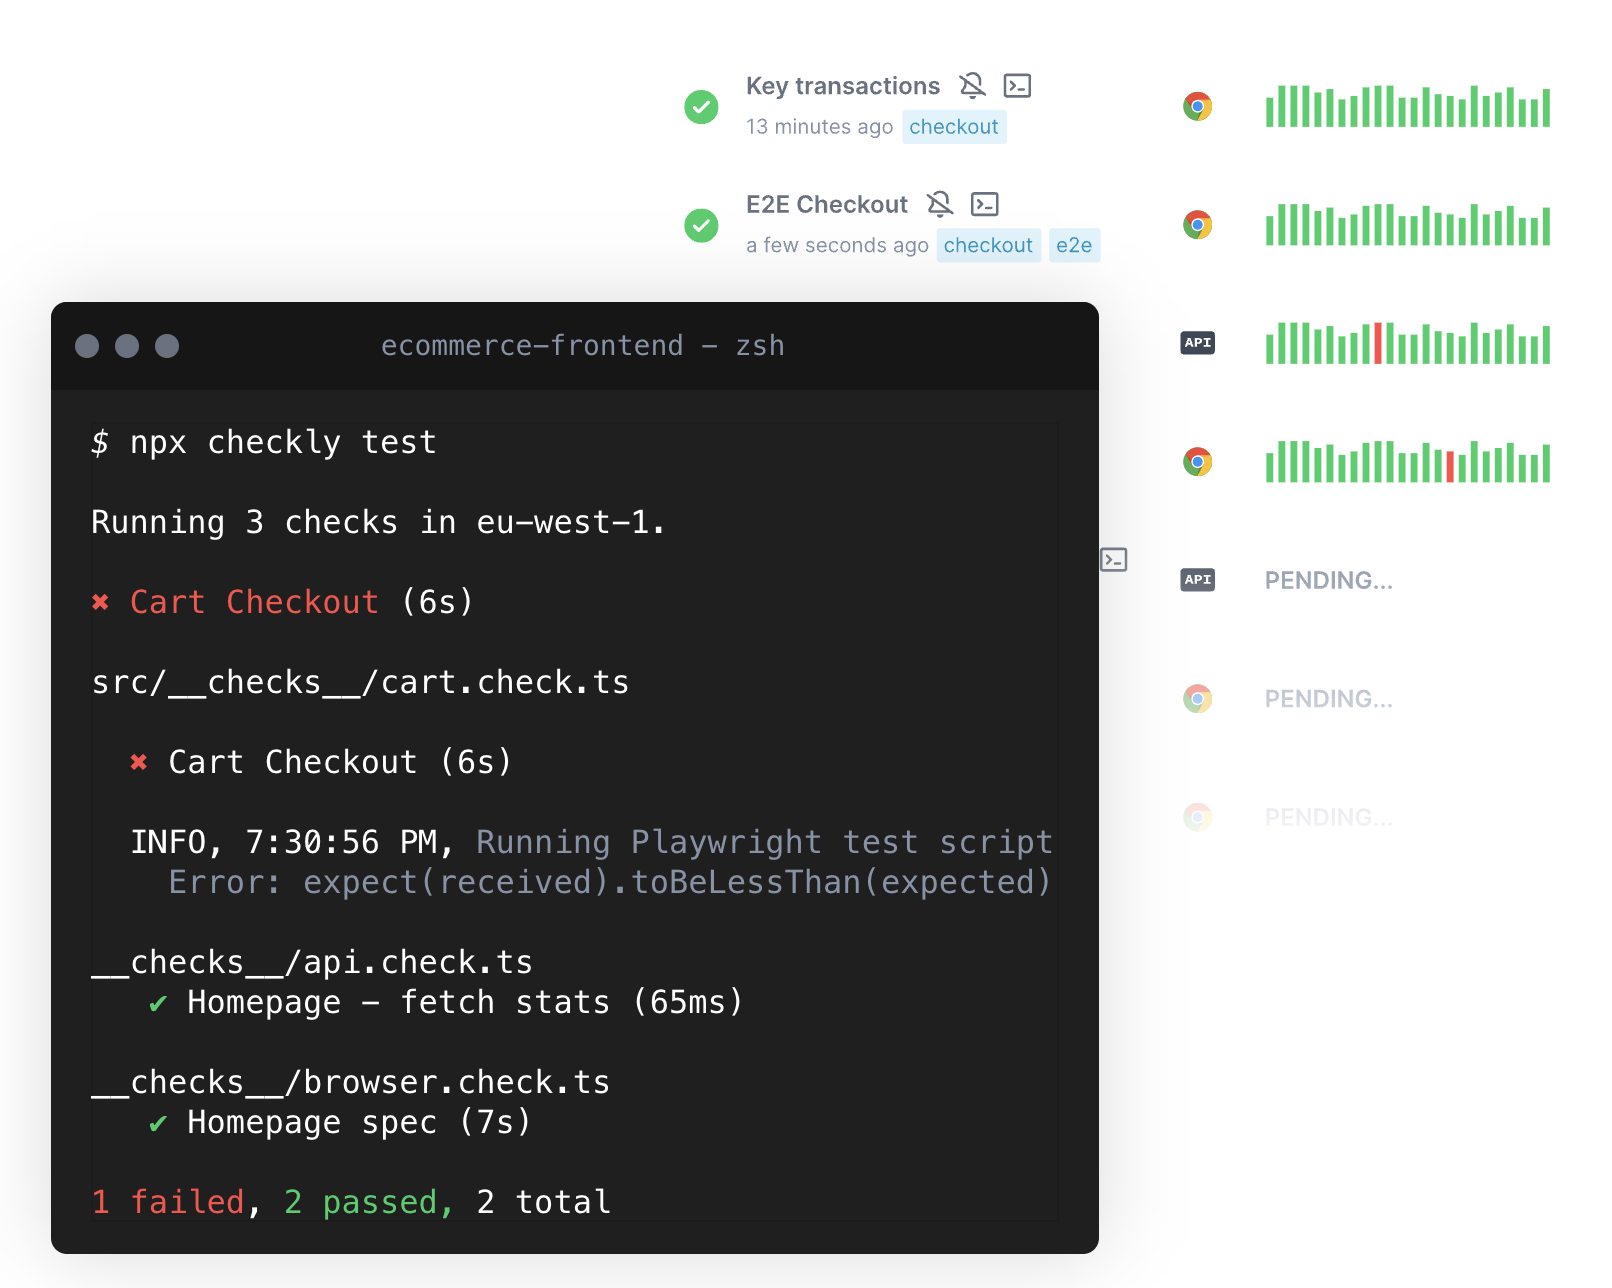
    Checkly this week added a monitoring-as-code (MaC) workflow capability to its software-as-a-service (SaaS) platform that is used to create synthetic tests for applications.

    The Checkly platform spins up browsers to test and can now monitor how applications are performing at both the user interface and application programming interface (API) level. That capability, currently available in beta, is enabled via a command line interface (CLI) for accessing an instance of TypeScript to invoke MaC workflows.

    Checkly CEO Hannes Lenke said that integrated approach enables application development teams to observe applications in as little as 60 seconds without instrumenting them with agent software.

    As part of that effort, Checkly also made generally available Playwright Test, a testing platform for web applications that spins up modern browsers on demand in addition to updating its public dashboards and adding an analytics API.

    Finally, the Checkly SaaS platform has passed a SOC 2 Type II security audit.

    Lenke said the overall goal is to make it simpler for developers to discover and remediate issues as they assume more responsibility for the ongoing management of applications.

    It’s not clear whether developers are taking over responsibility for testing and monitoring applications, but as more responsibility for applications shifts left, organizations are looking to give developers the tools they will require to succeed. That doesn’t mean IT operations teams won’t need to continue to monitor IT environments, but developers do need integrated tools that give them enough meaningful context to address them as they write code. Synthetic testing tools also enable developers to address many routine issues long before they might be discovered by a dedicated testing team that should be focused on ensuring the overall quality of the user experience.

    Regardless of the approach to testing and monitoring, Lenke noted that the silos that make up the software development life cycle are becoming more tightly integrated in modern application development environments. The primary objective is to make it possible for organizations to accelerate application development without compromising quality, he added.

    Of course, the more testing that occurs early in the application development process, the fewer issues a DevOps team should encounter after an application has been deployed in a production environment. The issue is that, historically, much of that testing occurs late in the application development process. Each time a project falls behind schedule, there is naturally a greater temptation to reduce the amount of time spent on testing to ensure the on-time delivery of an application. Providing developers with tools for testing and monitoring applications as they are being built should ensure that the proper level of testing is occurring before an application is deployed.

    There will, however, never be a perfect application. Over time, DevOps teams will discover that every application is impacted by drift to varying degrees as updates are made and the underlying infrastructure is upgraded. The most critical issue is reducing the number of potential issues overworked DevOps teams may need to address later on by ensuring the code being deployed is of the highest quality possible.

  • Sysdig Launches Wireshark Foundation

    Sysdig Launches Wireshark Foundation

    Sysdig this week announced there is now a Wireshark Foundation that will oversee future development of the widely used open source traffic protocol analyzer.

    Gerald Combs, who is now director of open source projects at Sysdig, along with Loris Degioanni, CTO of Sysdig, launched Wireshark in 2006 to enable teams to monitor network traffic, learn protocols and packet basics and troubleshoot network problems. There are more than 2,000 contributors and Wireshark has been downloaded more than 60 million times in the last five years alone.

    The Wireshark Foundation will provide a framework for long-term stewardship and sustainability. The foundation will be led by Sheri Najafi as executive director, and Janice Spampinato, Hansang Bae, Najafi, Combs and Degioanni will serve on the board.
    Combs said rather than donating Wireshark to an existing foundation, it was decided to set one up to formalize many of the community processes that have evolved over the past two decades.

    Degioanni said the foundation will also ensure Wireshark remains relevant long after its creators eventually retire. Wireshark has a graphical user interface (GUI) that provides IT teams with an easy-to-understand traffic protocol analyzer. However, as applications become more distributed, additional types of IT professionals, including DevOps teams, are analyzing network traffic. Similarly, cybersecurity teams are using these tools to help track down the source of anomalous activity.

    It’s not clear whether network operations (NetOps) and DevOps workflows are merging, but the level of collaboration has increased. As networking increasingly becomes software-defined, it’s clear that developers will employ application programming interfaces (APIs) to manage networks as code in much the same way they do infrastructure in the public cloud. Most of those networking APIs are comparatively low-level, but with the rise of services meshes, it’s clear networking services are becoming more accessible.

    The biggest challenge is distinct cultures that have arisen around networking and application development. IT organizations will need to decide whether to provide development teams with the ability to programmatically invoke networking services on their own or through a self-service portal managed by a NetOps team. Regardless of who is responsible for managing the network going forward, the divide between DevOps and NetOps is already starting to narrow. The biggest challenge is simply finding a common language to express core concepts that eliminates any sense of fiefdom that might exist between them. After all, any conflict that arises can usually be attributed to a simple failure to communicate.

    In the meantime, in the age of edge computing, network latency issues are becoming even more challenging. An application based on microservices architecture is especially sensitive to network latency issues that are difficult to troubleshoot over an extended network. Tools that make those issues more obvious are crucial.