Tag: vulnerability remediation

  • Rezilion Launches Vulnerability Prioritization Platform

    Rezilion Launches Vulnerability Prioritization Platform

    Rezilion today announced general availability of a platform that enables DevOps teams to better prioritize remediation efforts by identifying which vulnerabilities both run in memory and actually impact a class or function that can be executed.

    Liran Tancman, Rezilion CEO, said the biggest DevSecOps challenge organizations face today is that the bulk of vulnerabilities that developers are tasked with remediating don’t constitute a significant cybersecurity threat.

    Rezilion has created a searchable proprietary next-generation vulnerability database (NGVDB) that identifies which issues impact specific classes and functions. That capability enables DevOps teams to de-prioritize close to 95% of software vulnerabilities, said Tancman.

    In addition, the Rezilion platform will surface remediation suggestions that lower the amount of disruption and/or cost, he said. A fully-automated remediation capability, for example, will automatically upgrade and test vulnerable software components and packages within a continuous integration (CI) pipeline that were found to be exploitable. In the longer term, Rezilion is also working toward surfacing remediation suggestions that might be addressed using an alternative to patching, said Tancman.

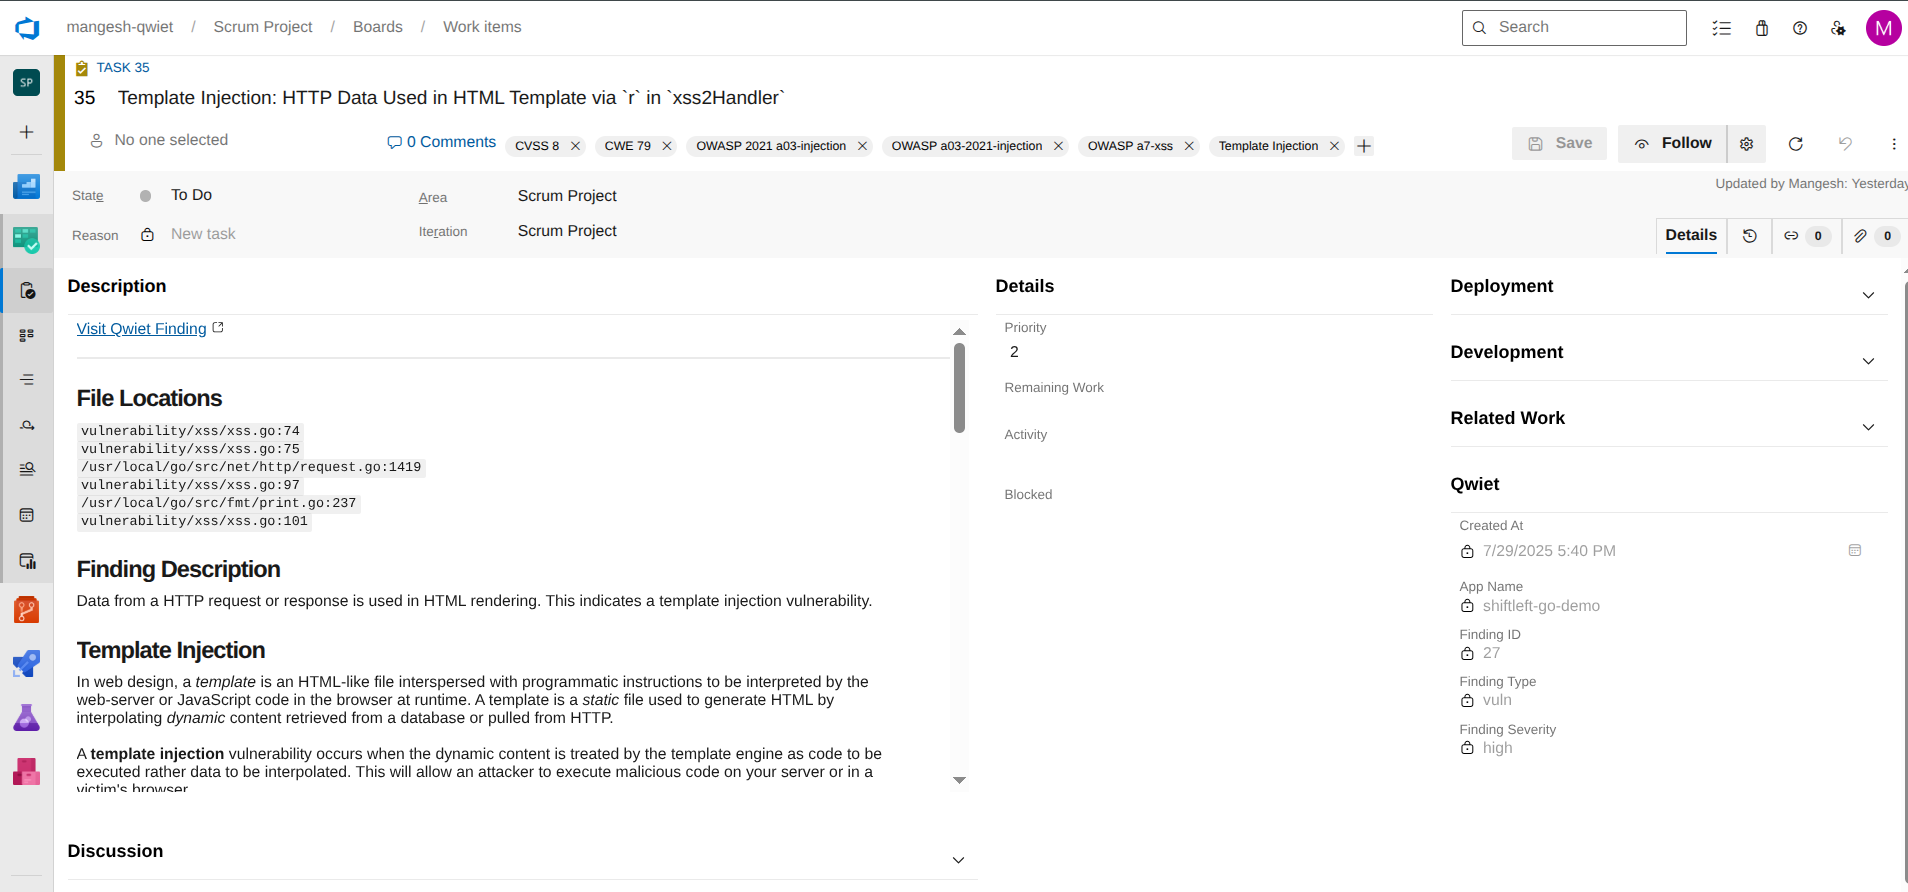
    The Rezlion platform is also integrated with IT service management platforms such as ServiceNow and project management tools such as Jira to make it easier to address vulnerabilities as part of existing workflows, he added.

    Most developers today are simply overwhelmed by the number of vulnerabilities that cybersecurity teams routinely ask them to patch, noted Tancman. The goal should be to enable developers to focus their limited time and effort on remediating the vulnerabilities that truly matter to ensure application security, he said.

    In addition, developers need to have more confidence in the fact that the patch they are being asked to make won’t break their existing applications, added Tancman.

    Vulnerability prioritization is, of course, at the heart of the long-standing divide that exists between DevOps and cybersecurity professionals. Spreadsheets filled with long lists of vulnerabilities are regularly created, but there is usually no context provided in terms of how severe a threat any given vulnerability poses. As a result, developers would allocate a small portion of their time to applying patches that are prioritized based on intuition and level of complexity rather than severity.

    Naturally, developers are going to allocate most of their time to creating new applications and features. For any DevSecOps initiative to succeed, it’s critical to ensure optimal use of the time allocated to remediation. Cybersecurity teams will continue to compile lists of vulnerabilities, but that list can now be triaged in a way that causes the least amount of friction.

    In the wake of a series of high-profile security breaches, there is now more focus than ever on securing software supply chains. The challenge is to find a way to better secure applications both before and after they are deployed in a production environment. There will always be vulnerabilities that are discovered after an application has been deployed. However, just because a vulnerability exists, that doesn’t mean it’s exploitable. The trouble with application security today is that, all too often, remediation efforts turn out to be a waste of time.

  • Vulcan Cyber Research Reveals Most Enterprise Cybersecurity Teams Lack the Ability to Remediate Risk

    Benchmark study finds most cybersecurity organizations lack the tooling and resources to deliver enterprise cyber hygiene

    TEL AVIV, Israel — May 12, 2021 — Vulcan Cyber®, developers of the industry’s only risk and vulnerability remediation platform, today released the results of its latest vulnerability remediation maturity research project. A survey of more than 100 enterprise security executives across North America and EMEA found that most enterprise cybersecurity and vulnerability management organizations lack the ability to drive remediation initiatives, to reduce risk and achieve acceptable levels of cyber hygiene. Vulcan Cyber is using the benchmark data from this research to provide cybersecurity leaders with a free vulnerability remediation maturity self-assessment service.

    Conducted by Pulse, the Vulcan Cyber vulnerability remediation maturity survey examines the maturity of enterprise vulnerability remediation programs while seeking to identify where shortcomings exist within respondents’ cyber hygiene efforts. According to the findings, 56% of organizations lack the ability to remediate vulnerabilities with speed and at the scale necessary to protect business from exploits and hackers. Immature cybersecurity teams typically react to vulnerabilities on a case-by-case basis. Additionally, nearly 80% of respondents do not have the proper tooling to proactively orchestrate and automate vulnerability remediation.

    “Enterprises must work to get ahead of the relentless barrage of known security vulnerabilities that increasingly threaten business. Development, IT operations and security teams should be able to coordinate and measure their efforts to remediate vulnerabilities quickly and at scale,” said Yaniv Bar-Dayan, Vulcan Cyber CEO and co-founder. “To be effective, it takes the right people, processes and tools. If anyone is lacking, it is close to impossible to drive meaningful remediation outcomes. It is no small task to get fix done so we are doing all we can to make vulnerability scanning and vulnerability prioritization freely available to all cybersecurity teams.”

    Key findings from the Vulcan Cyber study include:

    • Only 21% of enterprises have the proper tooling to proactively manage and automate vulnerability remediation. While only one-third (34%) of respondents reported having a defined, effective process for detecting and responding to vulnerabilities, one-third (33%) lack an effective or comprehensive process entirely.
    • Forty-four percent of survey respondents only rely on the criticality of a vulnerability and the available bandwidth of IT and security teams to determine how quickly to remediate a vulnerability—and less than one-quarter (21%) are proactively remediating as quickly as possible.
    • Nearly one-third (31%) of respondents admitted their organizations do not prioritize vulnerabilities at all. The most mature organizations use a combination of inputs from CVSS scores, threat intelligence, and risk to business assets to prioritize vulnerabilities, but this was only 26% of enterprises.
    • Forty-six percent of survey respondents either don’t measure vulnerability risk at all, or rely on “gut feel.”

    “As organizations become more mature in their vulnerability remediation efforts, it is possible to become substantially more efficient, while increasing the scale of cyber hygiene coverage,” said Bar-Dayan. “It requires all stakeholders – security, IT operations, engineering, and business unit owners – to align objectives and orchestrate tooling to create optimized and automated remediation workflows. We are working to change the economics of risk operations and vastly improve enterprise cyber hygiene.”

    Vulcan Cyber has made it easy for organizations to assess their vulnerability remediation maturity levels using its new security self-assessment tool. For additional guidance on how to benchmark current practices and outcomes against using the Vulcan Vulnerability Remediation Maturity Model, read the Vulcan Cyber eBook titled, The Four Levels of Mature Vulnerability Remediation.

    For more information about Vulcan Cyber, please visit https://vulcan.io/ to request a demo, or try Remedy Cloud today. In addition, Vulcan Free is now available as the industry’s only free vulnerability prioritization tool. Apply for Vulcan Free access today.

    About Vulcan Cyber

    Vulcan Cyber has developed the industry’s first risk and vulnerability remediation platform, built to help businesses reduce cyber risk through measurable cloud and application security. The Vulcan platform orchestrates and tracks the remediation lifecycle from scan to fix by prioritizing vulnerabilities, curating and delivering the best remedies, and automating processes and fixes through the last mile of remediation. Vulcan Cyber helps IT security teams collaborate and “get fix done” at scale. Vulcan Cyber is proud to offer Remedy Cloud and Vulcan Free as freemium SaaS solutions for businesses of all sizes. The unique capability of the Vulcan Cyber platform has garnered Vulcan Cyber recognition as a 2019 Gartner Cool Vendor and as a 2020 RSA Conference Innovation Sandbox finalist. https://vulcan.io