Tag: target

  • Five Great DevOps Job Opportunities

    Five Great DevOps Job Opportunities

    devopsy.kinsta.cloud is now providing a weekly DevOps jobs report through which opportunities for DevOps professionals will be highlighted as part of an effort to better serve our audience.

    Our goal in these challenging economic times is to make it easier for DevOps professionals to advance their careers.

    Of course, the pool of available DevOps talent is still relatively constrained so when one DevOps professional takes on a new role it tends to create an opportunity for others.

    The five job postings shared this week are selected based on the company looking to hire, the vertical industry segment and, naturally, the pay scale being offered.

    We’re also committed to providing additional insights into the state of the DevOps job market. In the meantime, for your consideration:

    LinkedIn

    CapitalOne

    Annapolis

    Director of Software Engineering – Risk Management and Compliance

    $190,000

    Dice.com

    Nigel Frank International

    Remote

    Senior Azure DevOps Consultant

    $165,000 per year.

    Indeed.com

    ROM Technologies

    Brookfield, Conn.

    DevOps Engineer

    $120,000 per year.

    SimplyHired

    Comcast

    Philadelphia, Penn.

    Senior Engineer Cloud Infrastructure

    $109,932 – $164,898.

    Monster.com

    Target

    Remote

    Lead Engineer – High Performance Distributed Computing

    $105,800 – $190,500

  • DevOpsDays MSP 2015: Minneapolis is a Tech Hub?

    DevOpsDays MSP 2015: Minneapolis is a Tech Hub?

    I stopped in the Minneapolis Airport to make a connection earlier this year. I never spent much time thinking about Minneapolis given its reputation for snow and ice. I hadn’t ever planned to go there nor had I explicitly made plans to avoid it. That was until the lineup for devopsdays MSP came out.
    I remembered seeing videos from the previous year and being mildly surprised they had such a seasoned lineup. When the speakers were announced I wasn’t expecting to see such a solid group of presenters taking the stage again. I like going to events in cities with a thriving tech industry. It always makes for a good hallway track when a lot of sharp folks are in the area and can easily attend. So what were all these people doing in Minneapolis?
    It ends up a lot of tech heavy companies are in the area. Target, US Bank, Cargill, General Mills, Best Buy, Land O’ Lakes, and 3M are among them. None of these are pure tech companies like I would expect to find around San Francisco, but any company that’s competitive these days is probably leveraging a lot of technology in an effort to better serve their customers and keep things running smoothly behind the scenes. If you know anything about what I’ve been doing with CookieOps it should be no surprise I was thrilled to see technology applied to traditional business models so enthusiastically.
    Target not only sponsored the event but had employees show up in force, fully engaged. 2nd place highlight for this event was discussing devOps, agile, and lean principles with Mary and Tom Poppendieck, authors of Lean Software Development: An Agile Toolkit, along with a group of folks from Target. Mary’s talk, “The New New Software Game” focused on techniques that make it possible for small teams to deploy small changes to large systems very rapidly and very safely. More specifically, this was a talk on how to break monolithic systems into micro services. I really appreciated how her talk highlighted human interaction and how it incorporates with technology.
    Getting to listen to Mary and Tom talk shop with Target was incredible. They mentioned the shelf life of software on more than one occasion, and I may have gotten a little light headed when Mary used a cookie company as an example of a manufacturing process that’s deeply concerned with time to market.
    The top highlight of the event for me had to be Daniel Willis’s ignite talk, “Sports Stats 101: Putting the R in Sports”. As a mathematician and a father I think getting kids into technology early is one of the best things we can do for them. When I saw Daniel was giving a talk on baseball stats in R at the age of 12 I had no choice but to make plans for Minneapolis. Daniel didn’t disappoint either, cracking standard deviation jokes in his bow tie in front of a crowd of about 400 people.
    Colleen Velo’s talk, “Rolling Your Own vs SaaS” covered the tradeoffs between internally coding solutions, using open source software, and running infrastructure in the public cloud. Bloom Health, another Minneapolis business, is in the high risk environment of healthcare. I found Colleen’s perspective and experience on this subject to be extremely relevant given the new security challenges we’re facing in our industry and the trouble that higher risk sectors are having with innovation as a result of it. I wasn’t surprised to hear Bloom is moving to SaltStack giving the risk associated with the industry where they operate.
    I also encourage you to take a look at Josh Zimmerman’s presentation on “Why You Should Care about DevOps in the Public Sector”. Public sector IT employees face a different set of problems with respect to structure, motivation, and funding. DevOps has moved from startups towards the enterprise, but there’s still a lot of good these practices can do to solve problems in the public sector where much of the resistance can be attributed to the need for a cultural change. Josh and I had a chance to talk about the cultural perspective of libraries, and how they’re viewed as places to keep books instead of places to keep information. I try to check out a library when I’m in a new town and see if they have anything interesting in the archives. This trip landed me in the Minneapolis Central Library where I was able to look at an early edition of Walden that included signed letters from Henry David Thoreau. There’s a lot of good stuff at the Hennepin County Central Library including a Dunn Bros Coffee on the first floor, a Teen Tech Center sponsored by Best Buy, art exhibits, and even a sound proof piano room. I stayed in Special Collections the entire time  I was there, but if you’re in Minneapolis it’s definitely worth stopping by.

    thoreau
    I really appreciated Jason Clifford ignite on GameOps, volunteering it as an Open Space, and coaching a group of us through a few rounds of The Resistance at the evening reception, which was sponsored by Target. Games like The Resistance and Werewolf help us learn how to interact and reinforce the low trust commensalism environment I’ve spent a good bit of time promoting this year and will be presenting this October at Lean Agile Scotland. If table top gaming isn’t low trust commensalism I don’t know what is. You literally have to share a table.

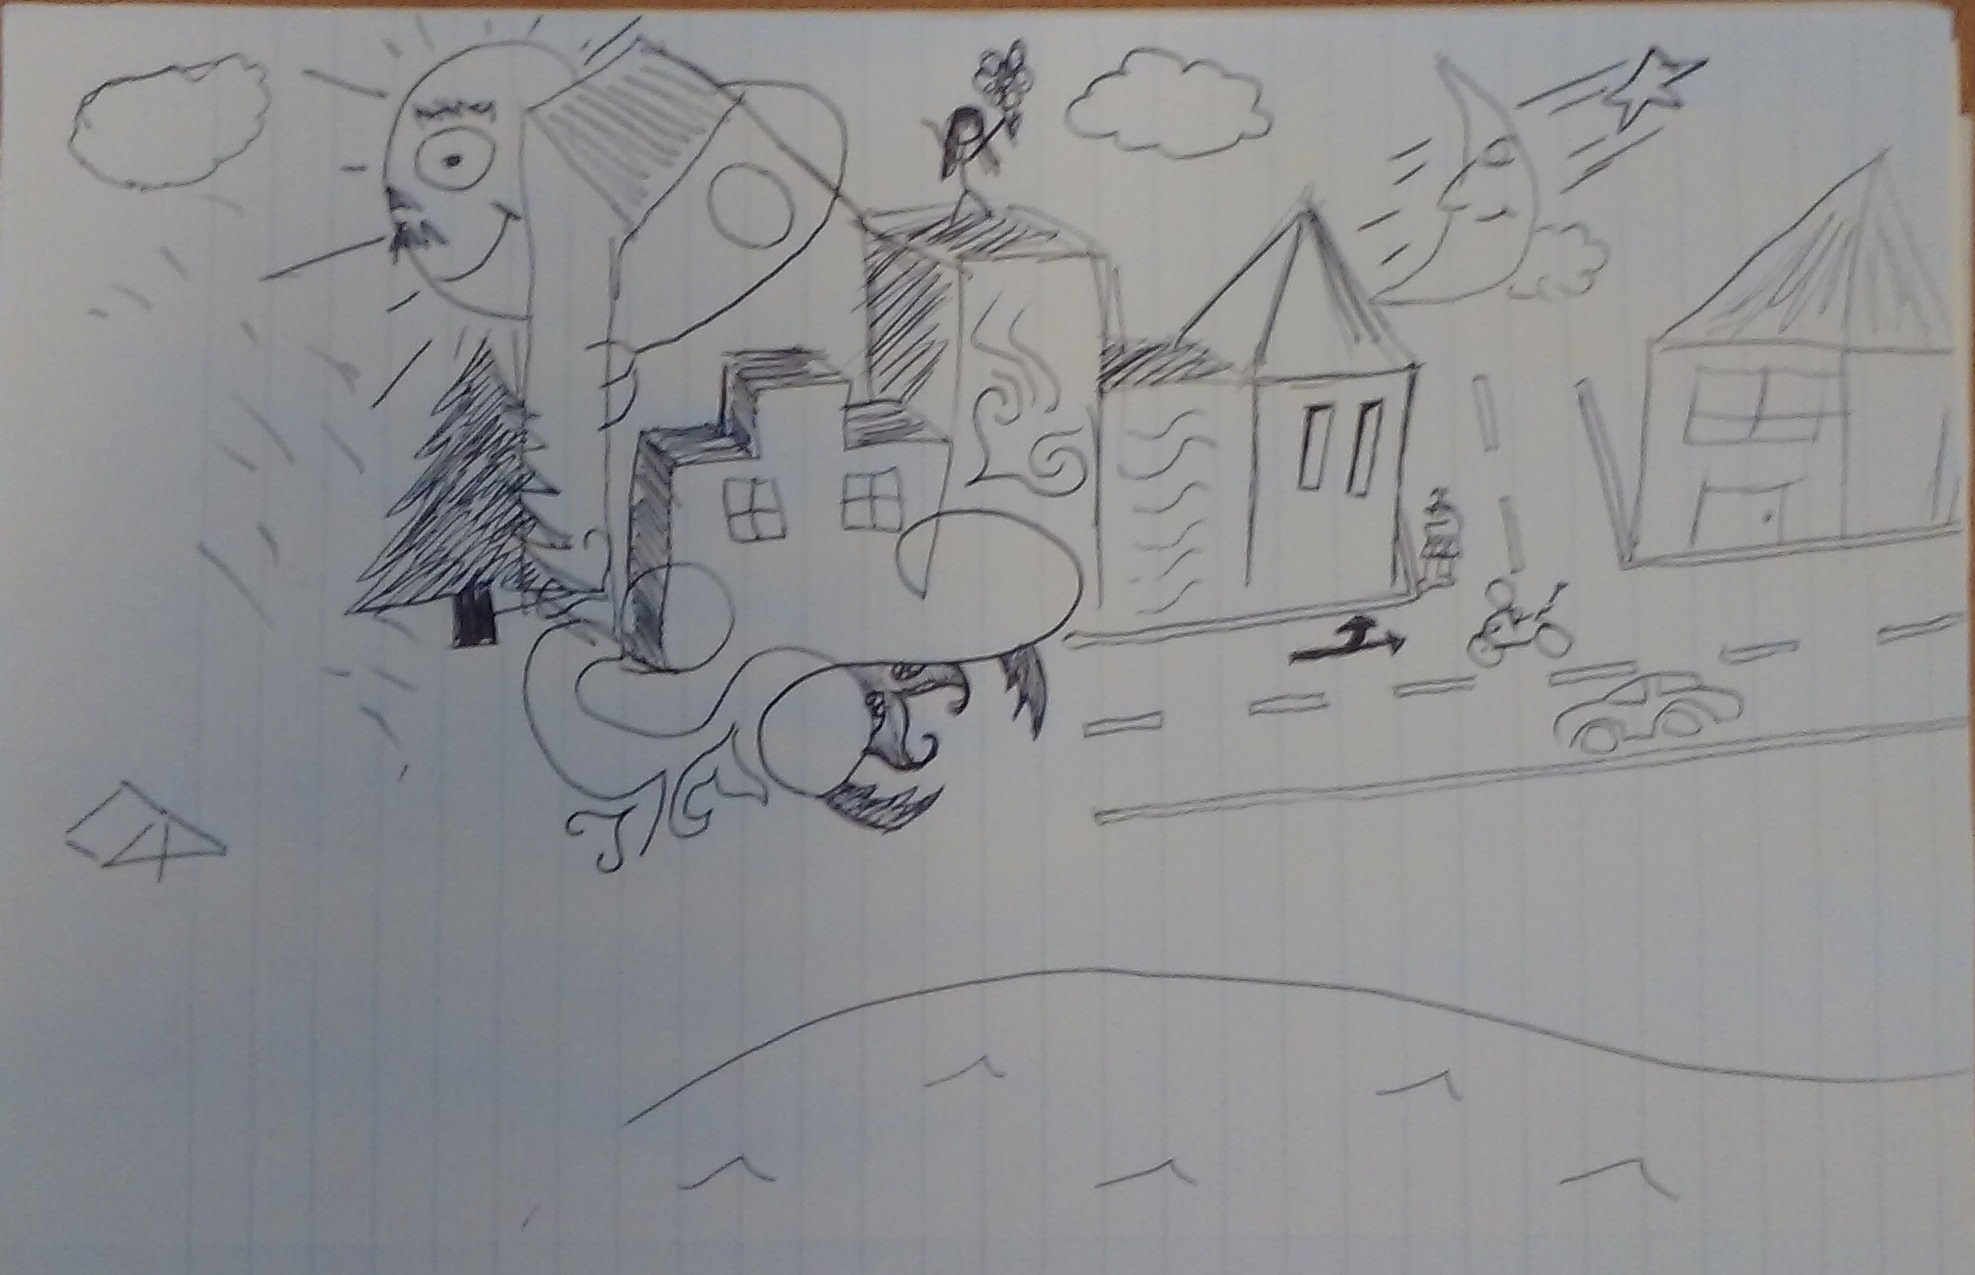
    I also introduced the group to The Drawing Game during the open space. You start with a random doodle on a blank page and pass the paper and pen around to each person so they can add something to the picture. We made it around our open space twice before stopping and ended up with the picture below. This game is a life saver for any group stuck waiting to eat, especially if there are kids with you. A spare place mat and a pen borrowed from the staff have warded off more toddler meltdowns for me than I can count. It’s still fun for older kids and adults too, even if you’re just watching the scene unfold.

    drawingGame

    So how did all this awesomeness end up in Minneapolis? As far as devopsdays MSP is concerned I’d give a lot of the credit to Bridget Kromhout. It’s obvious she puts a lot of time into the devOps community at large and hasn’t forgotten to help build a strong community in her own backyard. The food, shirts, event communications, AV, and even the slides and videos on the website for the event can all be traced back to her and the rest of the amazing staff. Bridget promised an awesome event while in New York but I was skeptical she might be partial when she started talking about the wonderful warm weather in Minneapolis. I can confirm first hand it doesn’t snow year round in Minneapolis, and devopsdays MSP happens during the perfect time of year for a visit.
    We’re only two weeks out from devopsdays Pittsburgh, and I’m looking forward to attending the event, visiting this town for the first time, and meeting some new faces while visiting with some more familiar ones. My expectations are pretty high thanks to Minneapolis, Bridget, and the entire MSP crew. Is Pittsburgh a tech hub too?

  • 2014 – The year of identity security breaches

    2014 – The year of identity security breaches

    There’s no doubt that 2014 will be remembered in the IT industry as a year of major security breaches.

    The year started with virtually every US resident worrying whether they’d been affected by the Target breach, and ended with the massive security breach of Sony and their film “The Interview.” And was, all along the way, peppered with other notable breaches.

    The interesting theme, with all of the major security breaches, was that they were almost all related to compromised credentials. As we know, having the right privileged user management is one of the top ways to protect your network, you don’t want to share same hacker-limelight that Sony did.

    But just for posterity, here’s a review of some of the top security breaches, and how they happened:

    Target

    What is considered the “biggest retail hack in history,” shook nearly every US resident in early 2014 as credit cards from 1,797 stores were compromised around Thanksgiving 2013. The hackers plotted against the company while Target was installing new security software. The repercussions were severe. Target reportedly spent $61 million on legal damages instigated by the breach, and profits fell by 46% in the holiday shopping season.

    Suggested read: http://www.businessweek.com/articles/2014-03-13/target-missed-alarms-in-epic-hack-of-credit-card-data

    Sony

    Although the investigation into what occurred is still on-going, early accounts point to compromised user credentials (or even perhaps an inside actor providing credentials) being leveraged to access, gather and exfiltrate data. We know, of course, that the attackers gained a tremendous amount of data including unreleased films, personal emails, HR data, and other confidential documents. Bummer for Sony. The WSJ estimates the breach cost them $100 million.

    Suggested read: http://techcrunch.com/2014/12/16/hack-sony-twice-shame-on-sony/

    Celebrity iCloud Photo Hacking

    While this particular breach was extra-sensationalized because of all of the celebrities involved, the Celebrity iCloud hack boiled down to plain old identity theft. Hackers identified email address, passwords, and the like and started gaining access to the iCloud data. Once in, they were able to copy all of the files. When celebrities realized they couldn’t login to their iCloud accounts, they naturally reset their passwords and were able to continue. Most of them didn’t even know they had been compromised.

    Suggested read: http://www.cnn.com/2014/09/02/showbiz/hacked-nude-photos-five-things/

    eBay

    In late May, eBay notified its customers: it had been compromised. Credentials for employees with access to their critical systems were compromised, is appears, several months prior to their detection. Financial information, which was coyly stored separately, was not hacked. Lucky for eBay.

    Suggested read: http://www.forbes.com/sites/gordonkelly/2014/05/21/ebay-suffers-massive-security-breach-all-users-must-their-change-passwords/

    Home Depot

    Over 56 million credit cards and 53 email addresses were stolen after a third party vendor’s employee’s credentials were stolen. This allowed hackers to gain access to the Home Depot network and make off with the confidential data. This breach was reminiscent of the Target breach in which another third party vendor (HVAC provider) was compromised and that subsequently led to Target’s compromise.

    Suggested read: http://www.usatoday.com/story/money/business/2014/11/06/home-depot-hackers-stolen-data/18613167/

    As you can see, the common thread to these security breaches is compromised credentials. Hackers realize the power of admin credentials in leveraging open systems. And, because many companies do an inadequate job of protecting their systems—despite patching, hardening, and firewalls—user admin access becomes an easy hacker target.

    How can we stop this seemingly simple vector of breaches? Protect your credentials with good user management. Just patching isn’t going to get us there. At Jumpcloud we spend a lot of time looking at this, and ensure that security and user credentials are watched with close vigilance and best-practice security to keep hackers out. Drop me a comment if you have any other thoughts on this topic.