Tag: security orchestration

  • Orchestration Emerges as Crucial DevSecOps Enabler in 2021

    Orchestration Emerges as Crucial DevSecOps Enabler in 2021

    As DevSecOps best practices continue to evolve and mature in 2021, security orchestration is emerging as a cornerstone of a solid defense-in-depth approach to application security.

    DevSecOps assumes organizations will shift responsibility for application security further left toward developers. If this assumption is correct, then developers clearly need access to a range of code analysis tools to achieve that goal. The challenge they face is incorporating tools from multiple vendors within a DevSecOps workflow. At different points in the development process, it may make sense to employ a static application security tool (SAST) versus a dynamic application security tool (DAST) that stress-tests the application just before it is deployed.

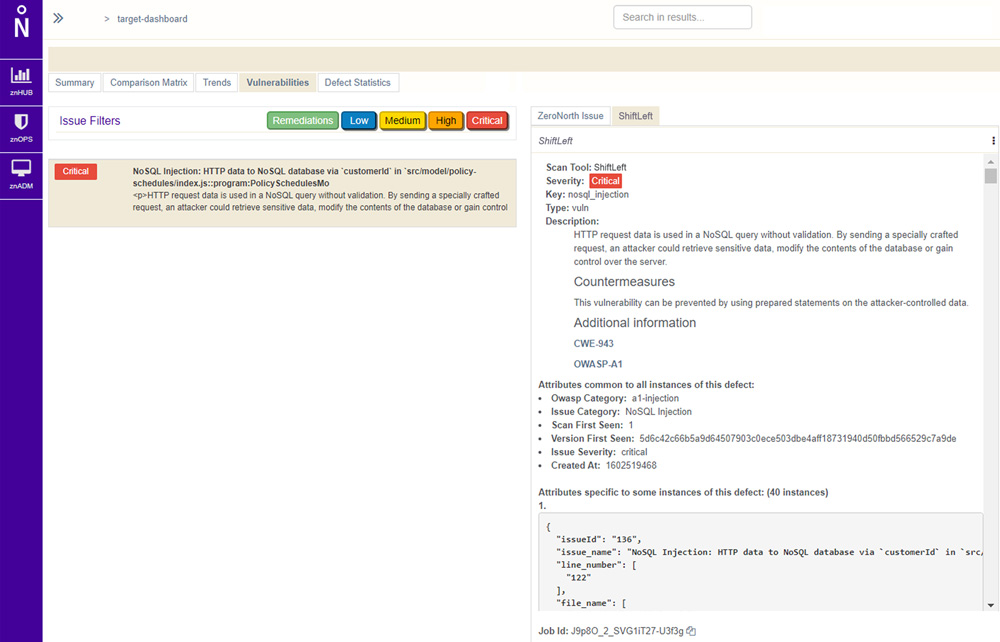
    Not surprisingly, providers of these tools are starting to align with security orchestration engine providers. ZeroNorth, for example, recently added ShiftLeft, a provider of a SAST tool, to the list of security tools that can be orchestrated via its software-as-a-service (SaaS) platform.

    Joanne Godfrey, director of product marketing for ZeroNorth, said organizations that have embraced DevSecOps are standardizing on two to three security tools. This mitigates the risk of becoming overly dependent on a single tool to discover vulnerabilities, Godfrey said. No single security tool can uncover every possible vulnerability in a timely manner, so DevOps teams must work to integrate multiple security tools into their workflows.

    Developers need tools capable of identifying vulnerabilities as they write code. They should also construct tests to proactively flag vulnerabilities before those are incorporated into a larger build. New vulnerabilities, however, are discovered all the time and it’s not uncommon for a container build deemed safe yesterday to suddenly need an update as quickly as possible. DevOps teams also need to secure the runtimes and hosts on which application builds are deployed, which typically requires more collaboration with the security teams usually responsible for managing platform security and DevSecOps.

    Despite this need to collaborate closely, the cultural divide between DevOps and cybersecurity teams is often wide. While there’s a lot of interest in DevSecOps best practices, developers don’t always prioritize application security when there are delivery deadlines to be met. This often results in security issues being addressed late in the application development process or, worse, addressed after the fact as part of an update delivered after an application has been deployed in a production environment.

    As application development accelerates, it’s imperative that the current divide between DevOps and security teams is bridged. Short-handed cybersecurity teams simply can’t keep pace with the rate at which applications are being built, deployed and updated. The need to shift more application security responsibility left toward developers increases daily.

    The challenge now is, rather than simply delivering an empty DevSecOps sermon, IT leaders need to practice what they preach and provide developers with the tools and processes required to secure their applications.

  • You have to crawl before you walk…

    You have to crawl before you walk…

    In previous posts I have explained what Security Policy Orchestration is, why DevOps folks should care, and how it can help facilitate the cultural change necessary for organizations to reap the long-term benefits of the cloud and virtualization. In this post, I’ll provide a few examples of how Security Policy Orchestration can create some “quick wins” – wins that create common ground between Security, Dev and Ops, and set the stage for higher profile wins with significant business impact.

    As infrastructure becomes increasingly complex it gets harder to decipher. In software we call this Readability – it determines our ability to support the code over time and to ensure security. The same concept applies to networks – the more complex they are, the harder it is to use them, maintain them and ensure security.

    The primary value of Security Policy Orchestration is providing a holistic view of the infrastructure. It “sees” the entire network and creates an index, which enables network administrators to perform quick queries across their environment providing “needle-in-a-haystack” search capabilities. While it might seem obvious, gaining visibility into the environment is a very powerful tool that can deliver huge benefits, especially when the environment is complex and subject to constant changes.

    Let me give you a few use cases:

     Audits:  As my security brethren know, preparing for an audit can take weeks (if not months).   However, once the network infrastructure is indexed, meaning you have structured records of the network elements (devices, interfaces, routes, security rules…), the kind of documentation required for security audits for PCI, SOX, NERC, and other regulations is literally a few mouse clicks away. Imagine finding all applications flows involved in a PCI flow in one click, or, even better, through a REST API call.

    Many of Tufin’s large enterprise customers report that their internal audit requirements are more stringent and time consuming than external compliance mandates, and require customized reporting, which they often have to script themselves.  Policy Orchestration solutions enable them to be much more agile – to the point where security no longer becomes a “showstopper.“

    A successful and effective audit (one that actually improves security) requires a collaborative approach across Dev and infrastructure – having the needed data at hand ensures agility, which is crucial for embedding this into the continuous process.

    Server Migration: Many enterprises and service providers are currently tasked with server migrations to virtual data centers or cloud environments. The challenge they face is identifying the talkers, connections and protocols that are needed to maintain connectivity and business continuity.  Firewall policies are often the best place to find this information because their important role in “attaching applications to the network”. However, it’s a labor intense task. Even if you have only 10 firewalls, with a few hundred rules and a thousand objects, identifying the flows is going to take a while. Now multiply that by 100 migrations per month – it’s virtually impossible.

    However, once you automate the process, it becomes quite easy.  With change automation in place, all you have to do is click “Find”, or, even better, call an API, and you will know the flows immediately.

    Application Deployment: As most devopsy.kinsta.cloud readers are (likely) well aware, when an Application team needs a connection opened to say, an LDAP database, they open a ticket with a business request:  “I need to connect server A to LDAP database B.”

    It’s the network guy (or gals) job to translate that request into a set of IP addresses that plot a secure, efficient network path that connects the database to the application. A week or so later, the requisite changes are made, and voilà, the application can leverage the LDAP database.  Or not, and then the network team needs to re-trace its steps and figure out what the problem is.

    The above process, in many organizations, is a loose one, usually conducted via email, and between people who don’t often traverse the same orbit.

    Add human error into the equation – a mistyped or incorrectly documented IP address, and you end up with re-dos, which everyone hates because they are time consuming and in complex network environments can be impossible to trouble shoot manually.

    Ask any network manager – reducing (if not eliminating) re-do’s is an impressive feat that offers substantial efficiency gains.   It’s also worth noting that without automation it is really, really hard to properly risk assess proposed changes.  In worst-case scenarios, an insecure network connection becomes apparent after something bad has happened.  But why wait for something bad to happen before innovating?  Bring security into your next network virtualization initiative at its onset – I promise you, you won’t be sorry.

    DevOps folks are likely familiar with the idea of abstraction, but it is still a relatively new concept in network security circles.   When applied to network change management, Abstraction separates business logic from the technology underpinnings of network infrastructure, and allows Operations teams to translate higher-level application language into terms they can use to enable underlying network services.   In scenarios like the above, the ability to automate this process can not only deliver huge efficiencies and create a much more collaborative dynamic between application, network and security teams.

    Hopefully, these examples build the case for how Security Policy Orchestration can be leveraged to deliver some quick wins.  Of course, organizations that commit to deeper and wider change reap greater benefits.  However, as my Co-founder, Tufin CEO Ruvi Kitov likes to say, you have to crawl before you walk, and walk before you run.  So in my next post, I’m going to explore why security people are so weary of automation, and how to get around that, in hopes that Security, Dev and Ops teams can all walk together.

  • What is Security Policy Orchestration and Why Should DevOps Teams Care?

    What is Security Policy Orchestration and Why Should DevOps Teams Care?

    After attending the DevOps day I wrote about in my last post, I wanted to take a minute to explain exactly what Security Policy Orchestration actually is so we can begin to understand how the two concepts overlap.

    Simply put, Security Policy Orchestration is intelligent network change automation. It goes beyond simple task automation by truly understanding the network through simulation and analytics. It also gives security people an extra level of governance and control, which is so critical to assure security and business continuity.

    Security Policy Orchestration reflects the growing relevance that managed security policies are having on IT systems.   In network security lingo, security policies are firewall policies, but can also apply to Access Control Lists (ACLs), router and load balancer configurations.  Managing security policies is an arduous task that requires automation, and Security Policy Orchestration has emerged in response to numerous factors happening in tandem – mainly, that:

    • Business agility is gaining importance as a key competitive factor. This is creating an increased demand for automation across IT and, specifically at the network layer.
    • IT organizations are pressured to match the speed, convenience and self-service provisioning the cloud environment offers for internal application deployment.
    • Enterprise networks are growing larger and more complex with numerous traffic routing and shaping technologies to service multiple data centers.
    • The widespread use of stateful and next-gen firewalls for external and internal network segmentation has significantly increased the size of the enterprise firewall estate, forcing security policies to morph into complex rule sets that map how business is conducted over the network.

    The collective impact of these developments on network and security operations tasks is having a profound impact on people, processes and technology, including DevOps groups, who like their Security Operations (SecOps) brethren, are under pressure to roll out services faster.

    Security Policy Orchestration helps to alleviate that pressure, enabling SecOps teams to keep up with the demands of the business while ensuring security and preventing an outage or a breach.  Being able to automatically generate, provision and synchronize Security Policy changes across a growing set of systems – with security, compliance and governance concerns accounted for – means that security will not become a bottleneck that slows down DevOps teams.

    While Security Policy Orchestration evolved out of network security operations, its benefits transcend security.  Even though it will remain a SecOps function, its impact on DevOps is only going to increase, especially as Network and Security Operations continue to converge.  However, the fundamental enabler of Security Policy Orchestration is automation.

    As a result, there is significant common ground between DevOps and SecOps when it comes to automating application connectivity. This may not have been an issue for you yet, but my introduction to DevOps came from my experiences helping Tufin customers automate application connectivity.  It’s a subject that is extremely germane to DevOps teams, and a topic that I plan to explore in depth in this blog because those of us leading the Orchestration charge within SecOps are kindred spirits with DevOps evangelists.  

    Contrary to popular belief, Security Policy Orchestration wasn’t created to restrict a company but to free it and help DevOps teams to accomplish its vision at the lowest IT risk level possible.  After all, there is no such thing as bulletproof security where the Internet is concerned.

    Instead, security folks focus on reducing risk, which puts us in a much better position to add value to the business.  Plus,  since so many of today’s biggest threats (i.e. APTs, for example) are network-based, introducing the tenets of Security Policy Orchestration  – which literally automates best security practices into change processes – is in the mutual best interest of both SecOps and DevOps teams. 

    In my next post, I plan to dig into more detail on the stakes Security, Dev and Ops all share to make IT work faster, better and safer, and propose a few ways in which SecOps and DevOps teams can collaborate to gain some quick wins.

  • Why Baking Security Into the DevOps Framework is Vital to Its Success

    Why Baking Security Into the DevOps Framework is Vital to Its Success

    I attended my first official DevOps conference in Israel in September 2013.  But I was initially introduced to DevOps by my customers – firewall and network managers who, through their efforts to automate  security policy management, found themselves dealing with a new and like-minded set of IT stakeholders  –  DevOps teams.

    They said DevOps was also all about automation – automation that allowed IT to increase their business contributions by enabling new applications and other IT services to be rolled out faster with greater control and efficiency.  

    Conceptually, it was clear to me that the DevOps value proposition is just as relevant to Security as it is to Operations and Development groups, especially since Security teams apply automation with the same fervor as DevOps.  

    In fact, using automation to accelerate IT has caught hold in the network security world to fuel a new movement and class of solutions, called Security Policy Orchestration.  As the CTO of Tufin, a Security Policy Orchestration company, I could not help but recognize the synergies.  I was (and still am) intrigued by DevOps, so when I heard about the conference, I decided to go.

    And I am so glad I did.

    The alignment between DevOps and Security Policy Orchestration is obvious. They both champion the use of automation to accelerate the pace of business. We Security Policy Orchestration folks are just coming at it from a different area within the organization.  Kindred spirits, right?

    In theory, absolutely, but in reality…not so much.

    The conference as a whole was great.  It completely validated my theories regarding the synergies between Security Policy Orchestration and DevOp.  But what surprised me was that security was a topic that was not being discussed at all at the conference.   Maybe a hat-tip to application security, but network security was not even on the DevOps radar, at least not at this particular conference.

    It needs to be.  For DevOps, to really be able to move the needle, we have to work together.  If history has taught us anything, it’s that when new applications and services are not created or rolled out with security in mind, at some point we will have to go back and retrofit it back in.

    Envision the typical experience:   the development team builds a new application, brings IT Operations in to implement it.  Once that is done, IT Ops prides itself on all the corkscrewing it took to make the application work on the actual infrastructure.  Except for once the app is in production, it doesn’t work.  The troubleshooting begins.  Invariably, issues of network connectivity come up.  Solving them requires app, dev and security managers to break down the cultural and organizational barriers that exist within their organizations to work together to ensure the application is architected correctly into the network.  This starts and the process of change requests between AppDev and IT to get the app up and running. 

    If that process is not automated, it can take months longer than it needs to resolve everything.   Not to mention any company subject to PCI has to consider terms like secure zoning, a concept that is not second nature to DevOps folks.   If PCI is not an issue, there are plenty of other internal and regulatory mandates and security –related considerations that, if for no other reason than common sense, can exponentially reduce the chances of a company ending up in the headlines due to an APT.    

    These are just a couple of many scenarios that can be avoided if development, IT and security work together from the get go.

    The net/net is that Dev and ops have the same goal but they are siloed, which is slowing down the pace of business – inhibiting it.  Collaboration is not some warm and fuzzy team-building thing – it is a fundamental business requirement.

    And that’s why I am so excited to have the opportunity to do this blog.  I think I can add a unique perspective on how DevOps and Security can work together to reach our common goals.

    My next post will explain will dig into what Security Policy Orchestration actually is, so we can begin to tease out the similarities and determine how to build on that to true alignment and partnership. 

    Stay tuned as the drama unfolds! This should be fun….