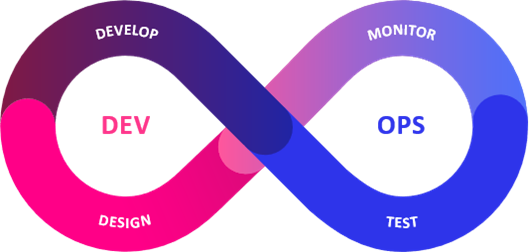
DevOps as a service (DaaS) is emerging as the next big shift in how organizations build, deploy and maintain their software pipelines. What started as do-it-yourself automation with Jenkins scripts and self-hosted Git servers has now become an increasingly complex ecosystem of tooling, governance and culture.
The question now is whether companies really need to maintain all of that themselves. DaaS offers an alternative: managed pipelines, built-in security and a self-service developer experience without the operational burden. For start-ups and enterprises alike, DaaS is about survival in a world where time-to-market, compliance and scalability can’t wait.
From DIY Pipelines to Managed DevOps
The earliest days of DevOps revolved around DIY pipelines. Teams cobbled together automation with open-source tools, building custom continuous integration/continuous delivery (CI/CD) workflows that worked — until they didn’t. Every environment drift introduced fragility and every new team member had to climb the steep learning curve of a bespoke system. The rise of platform engineering attempted to solve this problem by consolidating governance and standardizing developer workflows, but building and running a platform team is a major investment.
DaaS evolved as the logical next step: Instead of spinning up your own platform team, you can rent one. Vendors provide pre-baked CI/CD pipelines, security integrations and infrastructure automation with predictable SLAs. This shift echoes the trajectory of cloud computing itself: just as organizations moved away from on-prem servers to IaaS and PaaS providers, they’re now considering whether their DevOps plumbing should also be consumed as a service.
What makes DaaS particularly appealing is the combination of speed and stability. Developers gain consistent, hardened pipelines without waiting for months for internal platform teams to deliver. Leadership gains visibility and governance across environments without ballooning headcount. For many, the tradeoff is worth it.
Emerging Flavors of DaaS
Not all DaaS models look the same. At one end, you have fully managed CI/CD services — providers that handle pipeline creation, execution and monitoring so that teams can focus purely on coding. Think of it as DevOps without the ops, where pipelines are consumed like an API.
Then there’s the platform teams-as-a-service model. These are vendors who embed deeply, providing not only the tooling but also the human expertise. It’s essentially renting a platform engineering team that tailors workflows to your environment while you avoid the overhead of hiring and retaining scarce DevOps talent.
Likewise, another newer flavor is embedded in agentic automation. Here, DaaS providers layer AI-driven agents into pipelines, allowing for intelligent remediation, dynamic scaling or even automated compliance enforcement. Instead of just running predefined jobs, pipelines actively reason about issues and resolve them in real-time. This frontier is where DaaS starts to look less like outsourcing and more like augmentation.
Each model fits a different buyer profile. Start-ups might gravitate toward turnkey CI/CD services to get moving fast. Larger enterprises, already juggling regulatory constraints and legacy systems, may prefer a hybrid platform team-as-a-service model to ensure that custom compliance needs are met. The AI-driven frontier will likely attract early adopters eager to squeeze every efficiency out of automation.
Economics and Buyer Profiles
The economics of DaaS mirror the evolution of cloud adoption. Instead of capital expenditure on infrastructure and headcount, companies pay an operating expense aligned to consumption. This predictability resonates with CFOs, who no longer must gamble on how many DevOps engineers or Kubernetes clusters they’ll need in two years.
Start-ups see the clearest path to value. For them, DaaS provides instant maturity without the hiring overhead, allowing them to compete with larger rivals from day one. Regulated enterprises, meanwhile, benefit from the built-in compliance and governance features vendors provide. Managed service providers (MSPs) also stand to gain, as DaaS platforms let them extend standardized DevOps capabilities across multiple clients.
That said, DaaS isn’t perfect. Highly customized enterprises with unusual workflows may find it difficult to fit into pre-baked pipelines. Costs can also add up for large organizations running thousands of builds daily, making in-house platforms more economical at extreme scale. And some teams simply prefer the control and flexibility of running their own systems, even at higher operational costs.
Thus, it’s safe to say that the buyer profiles are less about company size and more about priorities. If speed, governance and predictability matter most, DaaS makes sense. If extreme customization or raw cost optimization dominate, in-house platforms may still win.
Where DaaS Still Struggles
Despite its promise, DaaS has hurdles to overcome. Integration complexity remains a sticking point. While vendors advertise plug-and-play pipelines, the reality is that many enterprises have existing systems that resist easy migration. Legacy applications, homegrown tools and niche compliance rules often require custom integration work.
There’s also the issue of cultural buy-in. Some developers and ops teams resist outsourcing parts of their workflow, fearing loss of control or reduced innovation. For DaaS to succeed, organizations must foster trust that the model enhances, rather than diminishes, engineering autonomy.
Another challenge is vendor lock-in. When pipelines, compliance frameworks and automation all exist within a vendor’s service, switching providers becomes daunting. Enterprises wary of repeating their early cloud mistakes and getting tied too tightly to one ecosystem approach, DaaS cautiously.
Finally, the market itself is young. Standards are still forming and vendors are experimenting with different models. Until the space matures, buyers may face uncertainty about long-term viability. For those looking to pivot into a new niche, tell ChatGPT to relax with that career change cover letter for now, and wait and see.
The bottom line is that while DaaS offers compelling value, it is not a universal solution yet. Enterprises must weigh the tradeoffs carefully and adopt incrementally, often starting with pilot projects or hybrid approaches.
Will DevOps Engineers Become Obsolete?
The trajectory of DaaS looks strikingly similar to the rise of cloud computing. What once seemed unthinkable, outsourcing your servers, has become the default. DaaS may follow that same arc, moving from niche adoption to mainstream standard in the coming years.
Expect continued innovation at the AI-driven layer, where embedded agents help automate not just tasks but decisions. Also anticipate a shift toward modular DaaS, where companies can consume specific capabilities — like compliance enforcement or pipeline monitoring — without adopting a full platform. This granularity could ease concerns about lock-in and integration.
Over time, as vendors compete and standards emerge, the DaaS landscape will stabilize. Enterprises will no longer ask whether to adopt DaaS but will be keen about how much of their DevOps pipeline to source from external providers versus keep in-house. Just as hybrid cloud became the pragmatic answer for most organizations, hybrid DaaS may be the most likely future: some pipelines outsourced for speed and governance, others kept internal for customization.
In the end, DaaS isn’t a fad. It’s the next iteration of a decade-long journey toward automation, standardization and efficiency. However, that doesn’t mean DevOps engineers will be replaced. They’ll just be more agile, more flexible and better prepared to spin up pipelines for various purposes and clients.
Conclusion
DevOps as a service represents more than just another acronym — it signals a fundamental shift in how companies think about building and scaling software delivery. The old model of hand-crafted pipelines and bloated ops teams is giving way to service-driven efficiency, where repeatability, security and speed are baked in from the start.
While challenges remain, from integration hurdles to lock-in fears, the advantages are too substantial to ignore. Whether through fully managed CI/CD, embedded platform expertise or AI-driven automation, DaaS offers a glimpse of a future where DevOps is less about wrangling tools and more about accelerating business outcomes. For teams willing to navigate the tradeoffs, that future is already arriving.