Tag: Contrast Security

  • Contrast Security Adds API Support to Security Platform

    Contrast Security Adds API Support to Security Platform

    Contrast Security has fully extended its vulnerability scanning and runtime application self-protection (RASP) platform to now include application programming interfaces (APIs).

    Company CTO Jeff Williams said the Contrast Secure Code Platform embeds agents directly into code to detect vulnerabilities using a combination of integrated static and dynamic application security testing tools. That approach makes it simple to embed vulnerability scanning and exploit prevention capabilities within a DevOps workflow as an application is built and deployed, he noted.

    In contrast, traditional approaches to application security depend on legacy platforms such as web application firewalls (WAFs) that are deployed by cybersecurity teams to protect applications in a way that doesn’t provide the same level of granular control at the API level, said Williams.
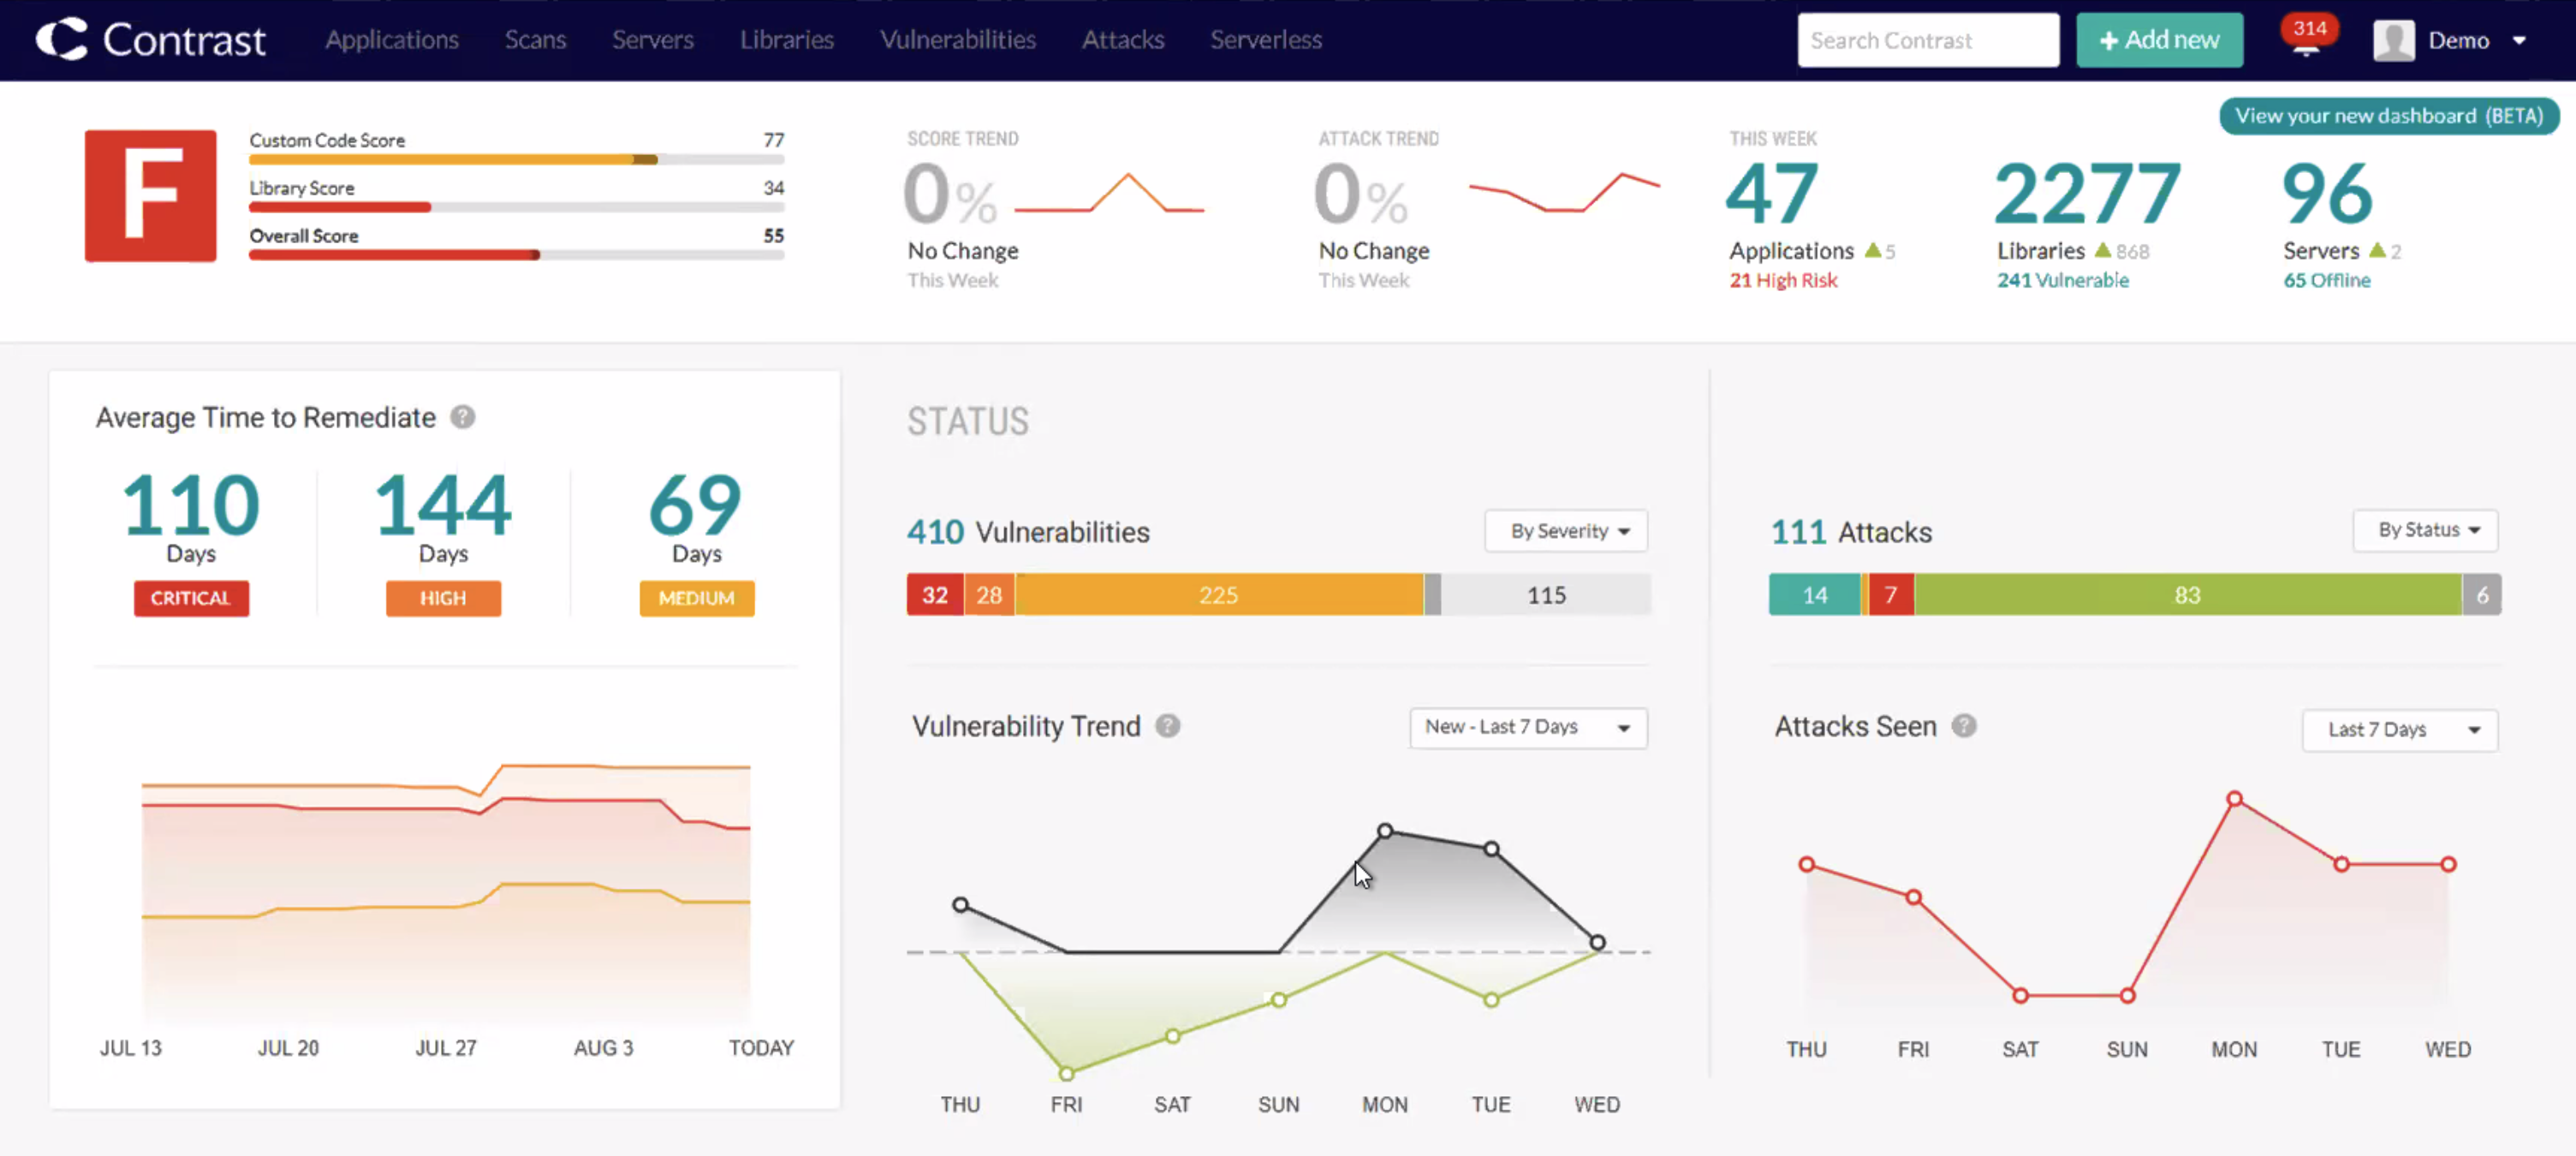
    Contrast Security claims the Contrast Secure Code Platform improves scan times by a factor of ten while fixing defects 45 times faster. It also reduces false positive alerts by being 200% more accurate, the company claims.

    As more organizations start to embrace best DevSecOps practices to better secure software supply chains, many of them are trying to achieve that goal without slowing down the rate at which applications are built and deployed. That approach, however, requires giving developers and DevOps teams the tools needed to build and deploy secure applications without requiring a lot of direct intervention on the part of a security operations team.

    In general, there is also now a lot more focus on API security as more organizations build and deploy microservices-based applications that rely on APIs to interconnect discreet components. Those APIs should be built, deployed and secured by DevOps teams before they are deployed just like any other software component, noted Williams. The current process of building applications is at its core, from a security perspective, fundamentally broken, he added.

    Application security, in general, has always been somewhat problematic. Cybersecurity teams tend to fund the tools and platforms they regularly employ. The assumption is that application development teams will invest in the tools they need to build and deploy applications. Alas, application development teams that have limited cybersecurity expertise assume that cybersecurity teams are securing both the underlying infrastructure and the applications deployed on top of it. As a result, application security is frequently underfunded.

    In the wake of a series of high-profile breaches of software supply chains there are now at least more reviews of application security being conducted. Contrast Security is making a case for securing the entire application, including the APIs, it invokes using agent software that is injected into the application at the time it is constructed.

    It’s not clear to what degree application security issues will be addressed using agent software rather than traditional cybersecurity platforms managed by security operations teams. Responsibility for application security is shifting left toward developers and the DevOps teams that support them, but as long as humans write code, mistakes will be made, said Williams

    The issue, of course, is many of the members of those teams are still focused a lot more on writing code and deploying applications than they are on cybersecurity.

  • Contrast Security Adds Free Code-Scanning Tool

    Contrast Security Adds Free Code-Scanning Tool

    Contrast Security this week made available a free security tool that enables developers to scan their code using the same core engine used by the cybersecurity team within their organization.

    Steven Phillips, vice president of product marketing for Contrast Security, said while there is no shortage of free tools for scanning code these days, the majority are not especially accurate. The scanning engine in CodeSec by Contrast Security is more than 10 times more accurate, Phillips said, because it is optimized to identify true positives versus generating a lot of false negatives, he claimed. He added that CodeSec is not just another freemium offering for developers that is a hobbled version of a commercial offering.

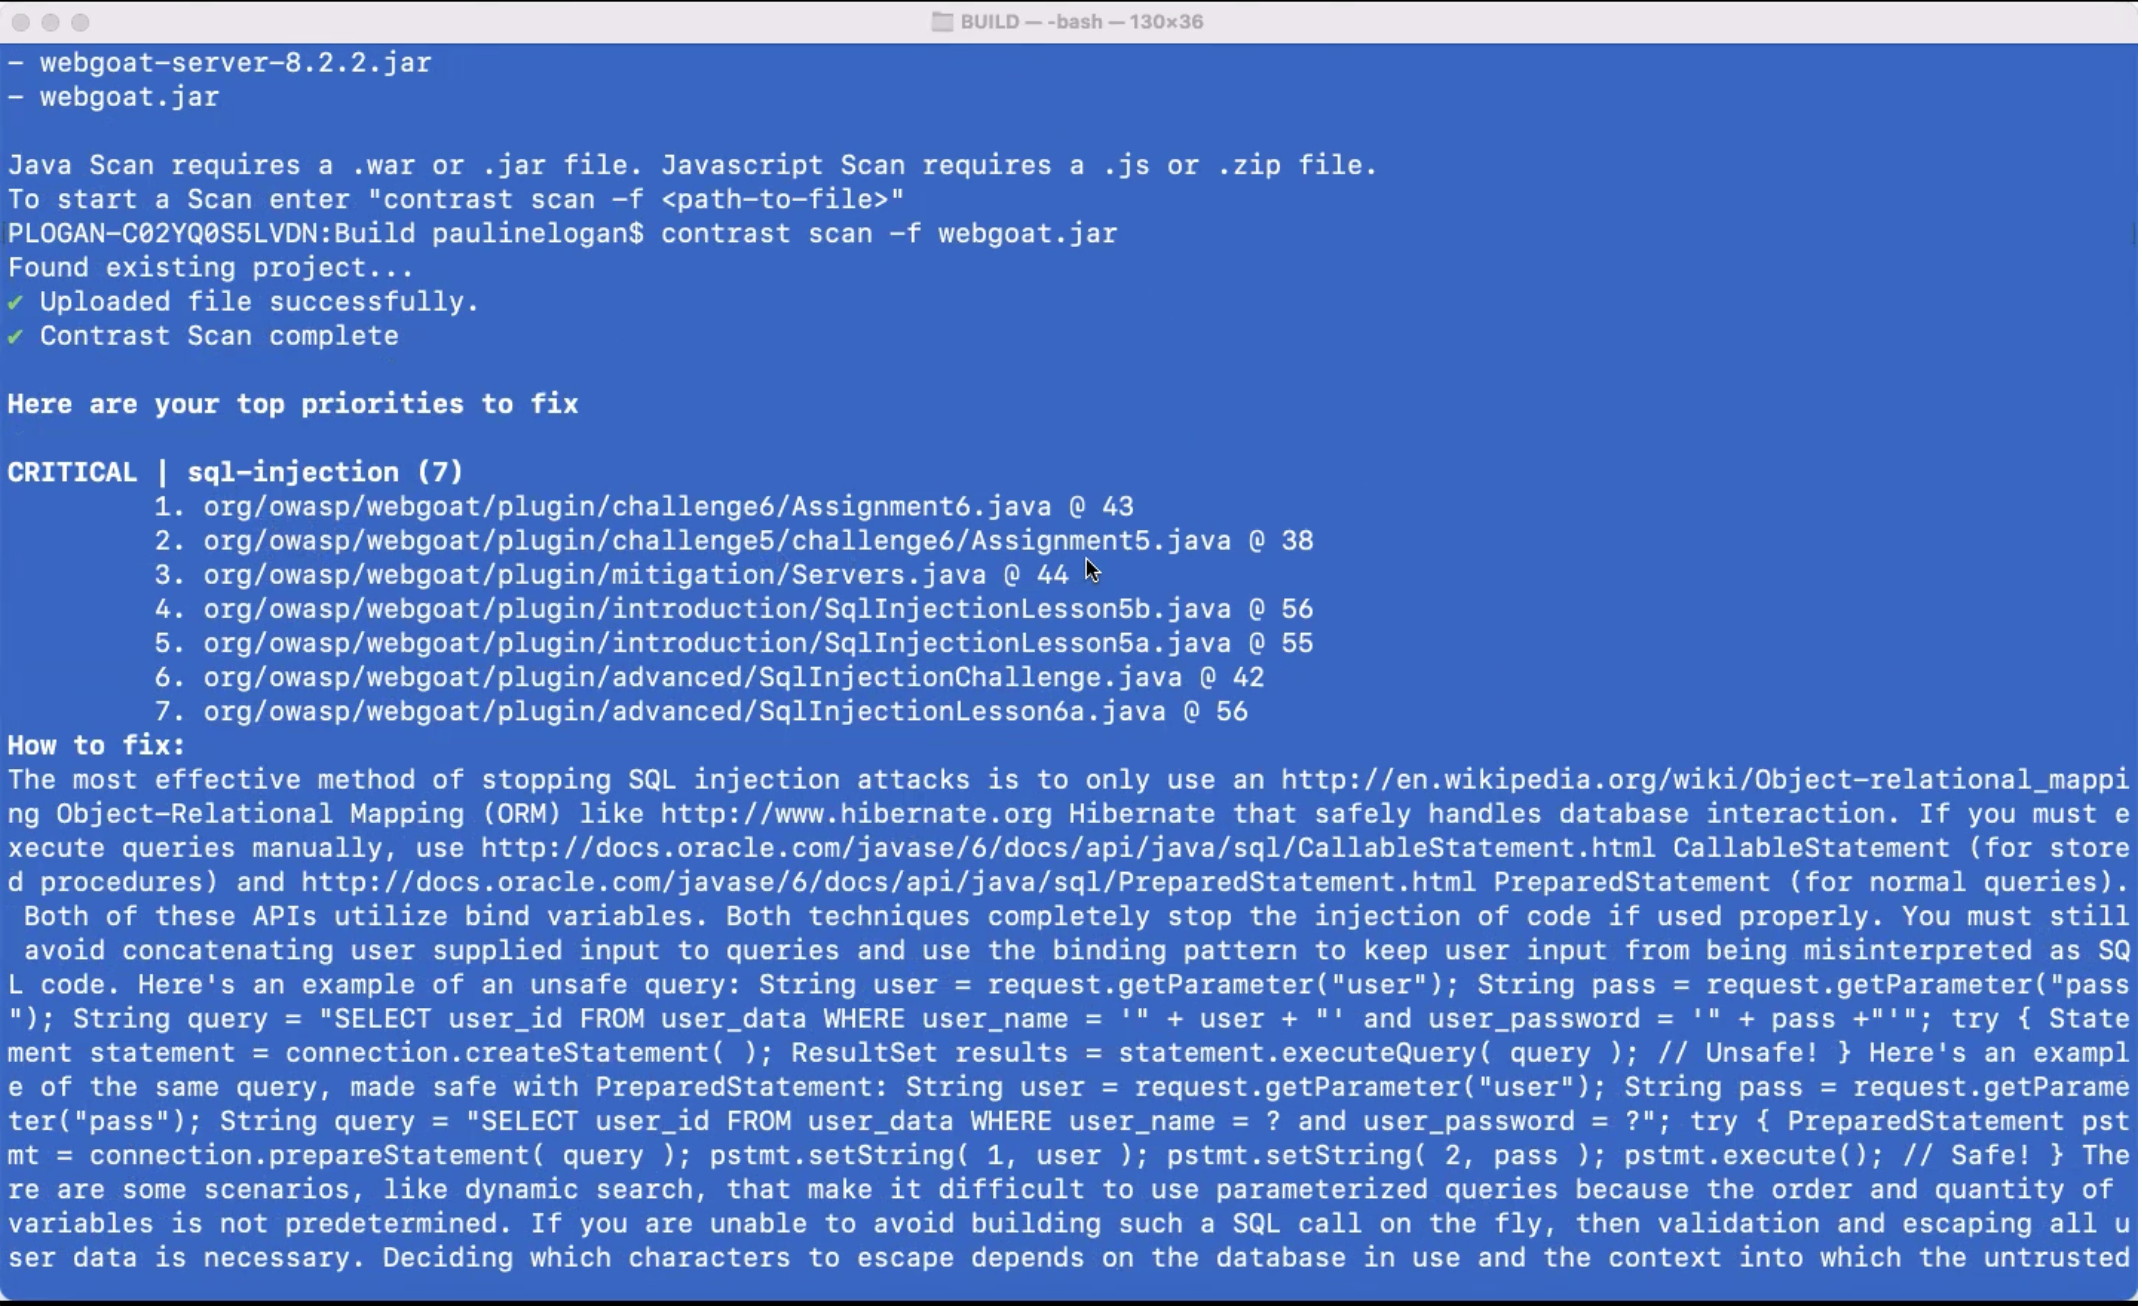
    CodeSec also differs from Contrast Security’s existing application security tool because it provides access to a command-line interface (CLI) that makes it easier to integrate within the context of a DevOps workflow. That approach makes it simpler for organizations to shift more responsibility for application security further left toward developers, noted Phillips.

    However, shifting responsibility left toward developers is not a panacea, Phillips said. The Contrast Security approach enables more collaboration between development and cybersecurity teams that are using the same scanning engine via a software-as-a-service (SaaS) platform to discover vulnerabilities, he noted.

    It’s difficult to determine just how far cybersecurity might shift left, but every vulnerability discovered by an application development team is one less for cybersecurity teams to ask developers to fix in a production environment. The challenge is making it as simple as possible for developers to discover those vulnerabilities.

    One way or another, the amount of time and effort being applied to application security has increased sharply in recent months following the disclosure of a series of high-profile breaches. Cybercriminals are now targeting software supply chains as part of an effort to compromise a wide range of downstream applications. Many of the modules that developers routinely reuse are being compromised by surreptitiously inserted malware. The fundamental challenge organizations are trying to address is how to build and deploy more secure applications without slowing down the rate at which they are built.

    Naturally, training developers to recognize security issues is a big part of the equation. However, no two developers are ever going to have the same level of cybersecurity expertise. Tools that identify vulnerabilities in ways that developers can act on are critical for advancing the adoption of DevSecOps best practices. Those tools require some level of acceptance among developers because they tend to prefer CLI tools.

    In the meantime, organizations will most likely have to scan a wide range of already-deployed applications for vulnerabilities. Applications running both inside and outside the cloud have been routinely deployed with a minimum level of scanning. The truth is that many developers have tended to view cybersecurity policies as an impediment to building and deploying applications. Unfortunately, cybercriminals now appreciate and take full advantage of the opportunity to wreak havoc.

  • Contrast Security Releases New Capabilities to Secure Enterprise Software Supply Chains

    Leading AppSec provider combines vulnerability testing for custom and third-party code across build, test, production and cloud-native environments

    Los Altos, CA, March 15, 2022 — Contrast Security (Contrast), the leader in code security that empowers developers to secure-as-they code, today announced that its Secure Code Platform now integrates software supply chain security across the development lifecycle, from the developer desktop to production systems. The new integration makes Contrast the first platform on the market that allows enterprises to identify their biggest supply chain risks and defend against them.

    As a direct response to the 2021 ransomware attack that shut down the Colonial Pipeline, President Joe Biden’s Cybersecurity Executive Order imposes strict standards for any software sold to federal agencies. More recent zero-day events such as the log injection vulnerability embedded in the popular Log4j Java library have also forced businesses in the private sector to re-evaluate the security standing of software imported, built and consumed by developers.

    “Together, open-source and custom code are the ingredients to the applications that businesses build, buy and ship,” said Jeff Williams, co-founder and CTO at Contrast Security. “Testing these software ingredients separately lacks context and leads to both false positives and false negatives. To accurately identify vulnerabilities organizations must perform security testing on the entire integrated application or API, which reveals how custom code and open-source interact.”

    Contrast integrates software composition analysis (SCA) with each of its security testing and protection solutions including its industry-leading interactive application security testing (IAST), runtime application self-protection (RASP) and Serverless Application Security solutions. Integration with Contrast’s static application security testing (SAST) solution is coming soon. The Contrast Secure Code platform helps businesses close security gaps in their software supply chain by:

    • Testing for custom and third-party code vulnerabilities simultaneously within native CI/CD pipelines and cloud-native environments.
    • Producing a comprehensive software bill of materials (SBOM) to help benchmark software supply chain risk and satisfy regulatory and compliance requests.
    • Removing the need to chase fixes for inactive libraries pulled in from code repositories by flagging libraries that are actually called at runtime.
    • Finding third party security issues in cloud-native workloads like serverless functions (e.g., AWS Lambda)
    • Protecting production applications and APIs from targeted attacks with no patching or code changes required.

    Jeff Williams, Co-Founder and CTO at Contrast is scheduled to participate in a virtual, fireside chat with Melinda Marks, Senior Analyst with ESG Research, at 2 p.m. EST on Tuesday, April 6, 2022 to discuss how recent events like Log4j have prioritized software supply chain security, the role of SBOMs and other techniques businesses need to consider to embed secure coding practices for third-party components. To register for the upcoming joint ESG Research and Contrast webinar, please visit https://www.contrastsecurity.com/webinar-esg.

    About Contrast Security

    Contrast Security secures the code that global business relies on. It is the industry’s most modern and comprehensive Code Security Platform, removing security roadblock inefficiencies and empowering enterprise developers to write and release secure application code faster. Embedding code analysis and attack prevention directly into software with instrumentation, the Contrast platform automatically detects vulnerabilities while developers write code, eliminates false positives, and provides context-specific how-to-fix guidance for easy and fast vulnerability remediation. Doing so enables application and development teams to collaborate more effectively and to innovate faster while accelerating digital transformation initiatives. This is why a growing number of the world’s largest private and public sector organizations rely on Contrast to secure their applications in development and extend protection to cloud and on-premise applications in production.

  • Contrast Security Extends DevSecOps Platform With Revolutionary Technology To Find Vulnerabilities That Matter 10x Faster

    Breakthrough pipeline-native code analysis security testing with Contrast Scan is now available with the Contrast Application Security Platform for complete coverage of the DevSecOps life cycle

    Los Altos, CA, June 10, 2021 – Contrast Security today announced the release of Contrast Scan that revolutionizes static application security testing (SAST) with pipeline-native static analysis to analyze code and detect vulnerabilities early on in the software development life cycle (SDLC). The release of Contrast Scan extends the DevSecOps capabilities of the Contrast Application Security Platform to the entire SDLC, empowering security teams to run scans up to 10x faster and remediate vulnerabilities up to 45x faster while meeting compliance requirements of an organization’s security policy.

    Incumbent legacy static approaches employ noisy rule sets to look for code quality issues. This outside-in approach generates immense volumes of security findings that become increasingly more time- and resource-intensive to manage. This is exacerbated due to the number of distracting false-positive alerts that kill productivity—upwards of 85% in many instances. For newer developer-friendly code scanning tools, application security shifts left too far, exacerbating the problem of false positives and leaving developers with no context on prioritization or how-to-fix guidance. In response, two-thirds of practitioners who rely on legacy static scanning indicate they are looking for a different approach to application security.

    Contrast Scan aims to solve these challenges with a pipeline-native approach that achieves dramatic improvements in speed, accuracy, and developer experience, accelerating digital transformation by removing inefficiencies and roadblocks that slow release cycles. Onboarding with Contrast Scan is quick and easy—requiring zero configuration and literally three clicks to get findings. Further, as Contrast Scan is integrated as part of the Contrast Application Security Platform, organizations have a unified, developer-friendly view of vulnerabilities and attacks with harmonized security profiles across SAST, interactive application security testing (IAST), runtime protection and observability, and software composition analysis (SCA), all in one DevSecOps platform.

    Key benefits of Contrast Scan include:

    • Results that matter delivered 10x faster. A breakthrough demand-driven algorithm powers the static analysis engine in Contrast Scan, enabling teams to pinpoint exploitable vulnerabilities while ignoring those that pose no risk. As a result, based on real-world scan results, Contrast Scan can shrink the amount of time to run scans by 10x. Faster scans remove DevOps security roadblocks that slow innovation, improve the efficiencies of security and development teams, and reduce the operating expenses (OpEx) of scanning.

    • 45x faster remediation times. When used in concert with the broader set of capabilities in the Contrast platform, Contrast Scan accelerates remediation times by an astounding 45x. This is achieved by enabling developers to focus on exploitable flows, prioritize routes with entry points based on runtime and production traffic analysis, and leverage actionable remediation guidance. All of this pays down security debt, which results in reduced application security risks.

    • 30% improvement in application security efficiencies. By integrating pipeline-native static analysis security testing into the Contrast Application Security Platform, application security teams can improve scan, triage, and remediation efficiencies by up to 30%. Contrast’s comprehensive DevSecOps approach bakes security into rapid-release cycles that are typical of modern application development and deployment environments. It also offers complete coverage of the DevSecOps life cycle with application tools optimized from build to production. This streamlines compliance reporting—often shrinking the time to demonstrate security policy compliance from days to minutes.  Today’s organizations should not be forced to choose between speed and security. With the addition of Contrast Scan, the Contrast Application Security Platform now offers a path to DevSecOps that allows organizations to secure any application anywhere—from a developer’s desktop, at a release gate, or in instances of production. The Contrast platform was purpose-built to deliver true DevSecOps with SCA, application security testing (AST), and exploit prevention capabilities using instrumentation across the entire SDLC.

    “Contrast Scan is a game changer for both application security and application development teams,” said Steve Wilson, Chief Product Officer at Contrast Security. “It allows teams to get unprecedented observability into their applications’ threat landscape early in the development life cycle—without all the noise of traditional static scanning tools. This means organizations’ applications will remain more secure while enabling them to maintain the agility of their development teams.” For more information on Contrast Scan, visit the Contrast Scan webpage and check out the below content.

    About Contrast Security
    Contrast Security is the leader in modernized application security, embedding code analysis and attack prevention directly into software. Contrast’s patented deep security instrumentation completely disrupts traditional application security approaches with integrated, comprehensive security observability that delivers highly accurate assessment and continuous protection of an entire application portfolio. This eliminates the need for disruptive scanning, expensive infrastructure workloads, and specialized security experts. The Contrast Application Security Platform accelerates development cycles, improves efficiencies and cost, and enables rapid scale while protecting applications from known and unknown threats.

  • Contrast Security Extends DevSecOps Platform With Revolutionary Technology To Find Vulnerabilities That Matter 10x Faster

    Breakthrough pipeline-native code analysis security testing with Contrast Scan is now available with the Contrast Application Security Platform for complete coverage of the DevSecOps life cycle

    Los Altos, CA, June 10, 2021 – Contrast Security today announced the release of Contrast Scan that revolutionizes static application security testing (SAST) with pipeline-native static analysis to analyze code and detect vulnerabilities early on in the software development life cycle (SDLC). The release of Contrast Scan extends the DevSecOps capabilities of the Contrast Application Security Platform to the entire SDLC, empowering security teams to run scans up to 10x faster and remediate vulnerabilities up to 45x faster while meeting compliance requirements of an organization’s security policy.

    Incumbent legacy static approaches employ noisy rule sets to look for code quality issues. This outside-in approach generates immense volumes of security findings that become increasingly more time- and resource-intensive to manage. This is exacerbated due to the number of distracting false-positive alerts that kill productivity—upwards of 85% in many instances. For newer developer-friendly code scanning tools, application security shifts left too far, exacerbating the problem of false positives and leaving developers with no context on prioritization or how-to-fix guidance. In response, two-thirds of practitioners who rely on legacy static scanning indicate they are looking for a different approach to application security.

    Contrast Scan aims to solve these challenges with a pipeline-native approach that achieves dramatic improvements in speed, accuracy, and developer experience, accelerating digital transformation by removing inefficiencies and roadblocks that slow release cycles. Onboarding with Contrast Scan is quick and easy—requiring zero configuration and literally three clicks to get findings. Further, as Contrast Scan is integrated as part of the Contrast Application Security Platform, organizations have a unified, developer-friendly view of vulnerabilities and attacks with harmonized security profiles across SAST, interactive application security testing (IAST), runtime protection and observability, and software composition analysis (SCA), all in one DevSecOps platform.

    Key benefits of Contrast Scan include:

    Results that matter delivered 10x faster. A breakthrough demand-driven algorithm powers the static analysis engine in Contrast Scan, enabling teams to pinpoint exploitable vulnerabilities while ignoring those that pose no risk. As a result, based on real-world scan results, Contrast Scan can shrink the amount of time to run scans by 10x. Faster scans remove DevOps security roadblocks that slow innovation, improve the efficiencies of security and development teams, and reduce the operating expenses (OpEx) of scanning.

    45x faster remediation times. When used in concert with the broader set of capabilities in the Contrast platform, Contrast Scan accelerates remediation times by an astounding 45x. This is achieved by enabling developers to focus on exploitable flows, prioritize routes with entry points based on runtime and production traffic analysis, and leverage actionable remediation guidance. All of this pays down security debt, which results in reduced application security risks.

    30% improvement in application security efficiencies. By integrating pipeline-native static analysis security testing into the Contrast Application Security Platform, application security teams can improve scan, triage, and remediation efficiencies by up to 30%. Contrast’s comprehensive DevSecOps approach bakes security into rapid-release cycles that are typical of modern application development and deployment environments. It also offers complete coverage of the DevSecOps life cycle with application tools optimized from build to production. This streamlines compliance reporting—often shrinking the time to demonstrate security policy compliance from days to minutes.

    Today’s organizations should not be forced to choose between speed and security. With the addition of Contrast Scan, the Contrast Application Security Platform now offers a path to DevSecOps that allows organizations to secure any application anywhere—from a developer’s desktop, at a release gate, or in instances of production. The Contrast platform was purpose-built to deliver true DevSecOps with SCA, application security testing (AST), and exploit prevention capabilities using instrumentation across the entire SDLC.

    “Contrast Scan is a game changer for both application security and application development teams,” said Steve Wilson, Chief Product Officer at Contrast Security. “It allows teams to get unprecedented observability into their applications’ threat landscape early in the development life cycle—without all the noise of traditional static scanning tools. This means organizations’ applications will remain more secure while enabling them to maintain the agility of their development teams.”

    About Contrast Security

    Contrast Security is the leader in modernized application security, embedding code analysis and attack prevention directly into software. Contrast’s patented deep security instrumentation completely disrupts traditional application security approaches with integrated, comprehensive security observability that delivers highly accurate assessment and continuous protection of an entire application portfolio. This eliminates the need for disruptive scanning, expensive infrastructure workloads, and specialized security experts. The Contrast Application Security Platform accelerates development cycles, improves efficiencies and cost, and enables rapid scale while protecting applications from known and unknown threats.

  • Creating Marketplace Efficiencies for the Healthcare Industries

    Creating Marketplace Efficiencies for the Healthcare Industries

    With approximately 6 million patients that visit this digital healthcare company per month to schedule and book doctor appointments, they strive to adapt, innovate, and modernize the healthcare industry by providing a frictionless healthcare experience for healthcare practitioners and for the 21st century patient. The company started out by focusing on the first step in a patient’s healthcare journey—the effective scheduling and booking of doctor appointments to help solve the ongoing access problem. The company initially focused on private healthcare practices and building a technology solution optimized for that specific use case. They experienced early success, building momentum, and critical mass. The company soon realized that there was a significant opportunity to turn its focus and expand to a larger piece of the healthcare system by addressing the changes in healthcare demands.

    To read more from the Customer Success Story, download the case study below:

    [su_button url=”https://devops.wpengine.com/wp-content/uploads/2020/08/Digital-Healthcare-Company_Final-Draft.pdf” target=”blank” background=”#ef2d3f”]Download Now[/su_button]

  • At the Intersection of Finance and Security

    At the Intersection of Finance and Security

    Envestnet | Yodlee is a leading data aggregation and data analytics platform powering dynamic, cloudbased innovation for digital financial services. More than 1,000 companies, including 13 of the 20 largest U.S. banks and hundreds of Internet services companies, subscribe to the Envestnet | Yodlee platform to power personalized financial apps and services for millions of consumers. Envestnet | Yodlee solutions help transform the speed and delivery of financial innovation, improve digital customer experiences, and drive better outcomes for clients and their customers.

    Saran Makam is the Director of Application Security at Envestnet | Yodlee, leading a team of global security professionals. Saran is responsible for managing the Application Security Program for multiple products and making sure that application security is integrated within the Software Development Life Cycle (SDLC).

    To read more about this Customer Success Story, download it here:

    [su_button url=”https://devops.wpengine.com/wp-content/uploads/2020/08/Customer-Success-Story-Yodlee030119.pdf” target=”blank” background=”#ef2d3f”]Download Now[/su_button]


  • Securing the Digital Commerce Ecosystem for Merchants, Customers, and Banks

    Securing the Digital Commerce Ecosystem for Merchants, Customers, and Banks

    Founded in 2006, GreenSky, Inc. is a leading financial technology company “Powering Commerce at the Point-of-Sale” for a growing ecosystem of merchants, consumers and banks. Their highly scalable, proprietary technology platform enables nearly 16,000 merchants to offer frictionless promotional payment options to consumers, driving increased sales volume and accelerated cash flow. Banks leverage GreenSky’s technology to provide loans to super-prime and prime credit consumers nationwide. Since their inception, over 2.4 million consumers have financed over $17 billion of commerce using GreenSky’s paperless, real-time “apply and buy” technology.

    To learn more about GreenSky, download the case study below:

    [su_button url=”https://devops.wpengine.com/wp-content/uploads/2020/08/Customer-Case-Study-Greensky.pdf” target=”blank” background=”#ef2d3f”]Download Now[/su_button]


  • Contrast Security Launches Next Generation Open Source Software Security Platform for DevOps

    Fortune 100 Financial Services Company Immediately Adopts Contrast OSS to Reduce Open Source Risk

    Contrast Security, the pioneer in enabling “self-protecting” software by embedding vulnerability analysis and exploit prevention directly into modern software, continues to re-invent application security with the launch of Contrast OSS. Contrast OSS is offered as a solution to help organizations building modern software solve the security, legal and compliance risks associated with their use of open source software (OSS).

    According to a recent RedHat report, 99% of IT leaders in surveyed enterprises see adoption of open source software as important for their organization, and a majority of organizations plan to increase their use of open source over the next 12 months. As companies around the world rely more on leveraging open source software, there is also a growing understanding of the risks that come with it. First generation tools used by these organizations to assess open source components struggle to provide effective security analysis and are not keeping up with high-velocity software development. These scan-based tools do not produce the accurate and actionable insight teams need to pinpoint true risks and quickly eliminate those risks early in the development phase. Moreover, legacy tools do not provide protection against attempts to exploit open source vulnerabilities in production applications. This leaves companies exposed to evolving threats, with poor visibility into the real risks introduced by these components.

    Created with patented security instrumentation technology, Contrast OSS is the only solution on the market that can continuously identify vulnerable open source components, determine how they are actually used by the application, and then prevent exploitation at runtime. Contrast OSS capabilities function as a solution that can work alongside Contrast Assess and Contrast Protect as part of the Contrast Security Platform. Contrast OSS provides the ability to:

    • Automatically create and maintain an organization-wide inventory of open source components mapped to applications, servers and environments.
    • Provide real-time correlation of vulnerabilities, OSS license information, and additional library metadata.
    • Continuously assess open source components for known and unknown vulnerabilities across all software development and delivery pipelines.
    • Continuously evaluate open source components for license compliance and intellectual property risk across all software development and delivery pipelines.
    • Automatically enforce custom policies and provide real-time feedback to security, compliance and development teams.
    • Prioritize and focus developer remediation efforts on critical vulnerabilities by accurately identifying whether vulnerable open source components are actually used by the application.
    • Continuously monitor production applications and block attacks on vulnerable open source to prevent runtime exploitation.
    • Maintain centralized visibility and point-of-control for all customer and open source software risk, portfolio-wide, through a single automated platform.

    This new offering by Contrast Security is already witnessing demand in market, and has recently been selected by a Fortune 100 financial services company to secure the company’s software portfolio and growing use of open source software. The Fortune 100 company selected Contrast Security to gain better visibility across their entire application stack, including all open source components introduced into their codebase by their development and digital transformation teams. With Contrast Security, the customer was looking for one platform that can deliver immediate and actionable feedback loops to developers to enable faster remediation and risk reduction procedures, while also driving down overall cost and operational complexity.

    “Contrast Security has a long and successful track record of helping organizations secure their applications,” said Surag Patel, Chief Strategy Officer, Contrast Security. “The increasing dependence on open source is undeniable and the ability for enterprises to leverage open source software without risk to the business, remains a top priority for VPs of Development, CISOs and CIOs. We are excited to offer the first complete solution that enables real-time inventory, assessment of security risk, assessment of licensing compliance risk and security exploit prevention for open source software. In an era of accelerated software delivery, customers can now embed automated controls into their software development and delivery pipelines, and monitor all of their applications and open source dependencies continuously. Leveraging the Contrast Security platform, organizations now have an embedded security solution that is built for the modern software era, without having to deploy and orchestrate multiple tools.”