There was a time when compliance meant a quarterly ritual. Someone from security would walk over with a spreadsheet, ask a few questions, tick a few boxes and disappear until the next audit cycle. The infrastructure team would scramble to prove that yes, encryption was enabled, and no, that S3 bucket was not public anymore. Everyone felt relieved, went back to shipping features and quietly hoped nothing would drift before the next review.
That model is dead; it just hasn’t been buried yet.
The problem is not that teams lack security awareness. Most engineering organizations today understand that vulnerabilities need catching early and that production environments need hardening. The problem is that compliance has historically lived outside the delivery pipeline — treated as a checkpoint rather than a continuous practice. In a world where teams deploy dozens of times a day across multi-cloud environments, a checkpoint approach is like locking the front door while the back wall is missing.
This is where security as code changes the conversation entirely.
What Security as Code Actually Means
Security as code is not just another rebrand of DevSecOps, though the two share DNA. At its core, it means treating security policies, compliance baselines and governance rules exactly the way we treat application code. They are version-controlled, peer-reviewed, tested in CI and enforced automatically at every stage of the pipeline.
Think about how infrastructure as code (IaC) transformed provisioning. Before Terraform and CloudFormation, engineers clicked through console UIs and hoped their configurations matched across environments. IaC made infrastructure reproducible, auditable and consistent. Security as code does the same thing for compliance. Instead of documenting your security posture in a wiki that nobody updates, you encode it into policy files that are evaluated every time code moves through the pipeline.
The distinction matters. When a security policy lives in a PDF, it is aspirational. When it lives in a Git repository with automated enforcement, it is operational.
Why 2026 is the Inflection Point
Several forces are converging to make security as code not just desirable but unavoidable.
First, regulatory pressure has intensified across every sector. The EU Cyber Resilience Act, DORA for financial services, updated NIST frameworks and tightening SOC 2 requirements — all demand that organizations demonstrate continuous compliance rather than point-in-time adherence. Auditors are increasingly asking not just whether controls exist but whether they are continuously monitored and enforced. A quarterly scan no longer satisfies that question.
Second, cloud-native architectures have made manual compliance impractical. When your infrastructure is ephemeral, when containers spin up and down in seconds, when Kubernetes clusters are running hundreds of pods across multiple namespaces, no human team can manually verify that every resource meets your security baseline. The attack surface changes too quickly and too often for static checklists to keep up.
Third, and perhaps most practically, engineering teams are tired of the friction. In too many organizations, security review is still the bottleneck that sits between ‘code complete’ and ‘deployed’. Developers write a feature, submit it for security review, wait three days, get feedback, fix the issues, resubmit and wait again. This does not scale, and it breeds resentment between teams that should be collaborating. Security as code eliminates this bottleneck by making the feedback loop instant and automatic.
What This Looks Like in Practice
The tooling ecosystem has matured significantly. Open Policy Agent (OPA), now a graduated CNCF project, has become the de facto engine for policy enforcement across Kubernetes, CI/CD pipelines and API gateways. Checkov scans IaC templates against hundreds of built-in policies covering CIS benchmarks, PCI-DSS, HIPAA and NIST before a single resource gets provisioned. HashiCorp Sentinel provides policy as code for Terraform workflows. AWS Config Rules, Azure Policy and GCP Organization Policies offer native guardrails within each cloud provider.
However, tooling alone is not the transformation. What matters is the workflow.
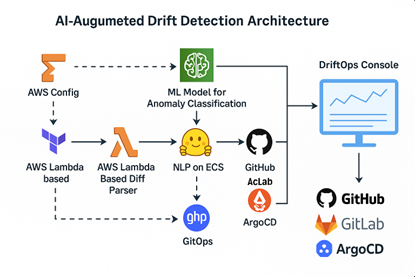
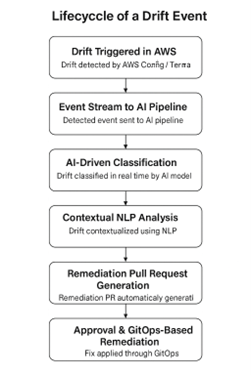
In a mature security as code implementation, a developer writes a Terraform module to provision a new database. Before that module even reaches the plan stage, Checkov evaluates it against the organization’s security policies. Is encryption at rest enabled? Is the database accessible only from private subnets? Are backup retention policies configured? If any policy fails, the pipeline stops. The developer gets immediate feedback, fixes the issue in the same commit cycle and moves forward. No tickets. No waiting. No handoffs.
At the Kubernetes layer, OPA Gatekeeper evaluates every admission request against policies defined in Rego. Want to ensure no container runs as root? That every pod has resource limits? That images only come from your approved registry? These are not suggestions in a runbook — they are constraints enforced at admission time. Non-compliant workloads simply cannot be deployed.
The compliance evidence generates itself. Every policy evaluation produces a decision log. Every failed check is recorded. Every exception is tracked with justification and approval. When audit time comes, you do not scramble to prove compliance. You export the logs.
The Cultural Shift That Makes it Work
The technical implementation is the easier part; the harder challenge is cultural.
Security as code requires security teams to think like engineers. Instead of writing policy documents that describe what should happen, they write policy code that enforces what must happen. This is a meaningful shift in skill set and mindset. Security engineers who can write Rego, who understand Terraform module patterns, who can review pull requests on policy changes — these are the practitioners who will define how compliance works in the next decade.
It also requires engineering leadership to treat security policies as first-class code. That means they go through the same review process as application code. They have tests. They have staging environments where policy changes are validated before they reach production. When a new compliance requirement emerges, the response is not a meeting and a memo. It is a pull request.
Perhaps most importantly, it requires organizations to accept that security is not a gate at the end of the pipeline. It is a property of the system, continuously verified, just like uptime and performance.
Where Teams Get it Wrong
The most common failure mode is what I call ‘tool-first, policy-later’. Teams adopt OPA or Checkov, write a handful of policies to satisfy an immediate audit requirement and then stop. The policies become stale. New services get deployed without coverage. The tooling exists but the practice atrophies.
The second failure mode is over-restriction. Teams write policies so aggressive that developers cannot get anything deployed without filing exceptions. This recreates the exact bottleneck that security as code was supposed to eliminate, just with a different approval mechanism. Good policy design requires pragmatism. Start with critical controls — encryption, network isolation, access management — and expand gradually. Not everything needs to be a hard block on day one. Some policies can start as warnings that become enforced over time as teams adjust.
The third failure is treating security as code as solely a platform team concern. If developers never see the policies, never understand why a deployment was blocked and never contribute to policy evolution, you have just moved the silo from a spreadsheet to a repository. Policies must be visible, documented and open for contribution.
What Comes Next
The direction of travel is clear. Policy-as-code adoption is accelerating. Gartner projects that by the end of 2026, a majority of software organizations will rely on internal developer platforms with embedded policy enforcement. The CNCF ecosystem continues to invest heavily in OPA and related projects. Cloud providers are expanding their native policy engines with deeper integration into deployment workflows.
However, the real shift is not about any single tool or framework; it is about the expectation. Continuous compliance is becoming a baseline expectation, not a differentiator. Organizations that still rely on periodic audits and manual reviews will find themselves unable to move at the speed their business demands, unable to satisfy increasingly stringent regulatory requirements and unable to attract engineers who expect modern security practices.
Security as code is not the future of compliance in DevOps. For the teams paying attention, it is already the present. The rest are just catching up.