Tag: application programming interface

  • RapidAPI Adds Tool to Make Building APIs Simpler

    RapidAPI Adds Tool to Make Building APIs Simpler

    RapidAPI today added a free RapidAPI Studio offering to its portfolio that makes it easier for developers to build, consume, manage and monetize application programming interfaces (APIs).

    Wade Wegner, senior vice president and head of product at RapidAPI, said RapidAPI Studio, available in beta, makes it simpler for developers to move between design and development, testing and management without losing context.

    It is also designed to be slipstreamed into developer workflows by either being accessed via a browser, as a desktop application, a macOS-native application or as an extension to the VS Code tools provided by Microsoft, added Wegner.

    That approach also makes it easier for teams of developers to collaboratively work on API projects, he noted.

    APIs are foundational to every modern application development initiative. Each microservice included in a modern application has its own API. As a result, the number of APIs—internal and external—that organizations are building and exposing has increased exponentially, especially as the number of digital business transformation initiatives continues to expand. While the bulk of APIs employed today are internally facing, the number of external-facing APIs being employed tends to rise sharply as more business processes become digitized.

    Less clear is who within the organization is responsible for managing those APIs after they have been deployed. In some cases, developers assume responsibility for them along with every other component of an application. Developers, however, tend to move on to other projects; DevOps and cybersecurity teams are being tasked with managing, securing and updating APIs. This is part of a larger effort to better secure software supply chains in the wake of a series of high-profile breaches.

    Unfortunately, documentation of those APIs has been somewhat lax within many organizations. In many cases, organizations are not even sure how many APIs have been deployed. Many organizations also discover, to their chagrin, that so-called zombie APIs previously abandoned by developers can still be exploited by cybercriminals to exfiltrate data.

    At the same time, the management of APIs is becoming more complex. Along with existing REST APIs and legacy web services based on XML, organizations are now deploying GraphQL APIs. The result is a mix of API schemas that require different levels of expertise to manage and secure.

    It’s not clear how the increased focus on securing software supply chains might impact API management. However, it’s apparent that cybercriminals are becoming more adept at discovering insecure APIs through which they can exfiltrate data. The challenge organizations face is that it’s not feasible to secure those APIs without first having a framework in place for managing them.
    One way or another, an API management crisis will soon come to a head as it becomes even simpler to build and deploy APIs. The only thing that remains to be seen is to what degree organizations will get ahead of that issue before it spins out of control altogether.

  • Kong Previews Application Connectivity Service

    Kong Previews Application Connectivity Service

    Kong Inc., at its online Kong Summit 2020 conference, unfurled Kong Konnect, a cloud service through which developers can leverage application programming interfaces (APIs) and microservices to integrate distributed applications.

    Available as a private beta, Kong Konnect promises to make it easier for developers to create complex workflows spanning API gateways, Kubernetes Ingress controllers and service mesh runtimes.

    Company CTO Marco Palladino said Kong Connect makes it possible for developers to consume integration runtimes as a service via an interface that allows them to invoke only the specific services they require.

    Scheduled to be generally available early next year, Kong Konnect is based on a ServiceHub platform that creates a single source of truth for all services via a catalog that any organization has developed. Kong Konnect also provides access to a runtime manager that enables self-service provisioning based on roles in addition to enabling IT teams to manage Kong runtimes across hybrid cloud computing environments.

    Kong Konnect also integrates the company’s API Gateway, Ingress Controller and Kong Mesh, a service mesh based on open source Envoy proxy software, and Kong Vitals, a tool for monitoring Kong services and transactions in real-time. Kong Konnect is also integrated with Insomnia to design APIs using a tool that integrates with any Git-based repository and the Kong Developer Portal, through which developers can publish their own services.

    Palladino said the goal is to provide a turnkey service that automatically provides all the Layer 4 through 7 networking services that developers require to integrate both monolithic applications running on virtual machines as well as emerging microservices-based applications running on Kubernetes clusters. Kong Konnect makes available universal service connectivity on-demand via a single API to any class of developer, he said.

    As application environments become more distributed, developers are spending more time than ever on basic connectivity issues. The company is making a case for a cloud service that unifies all those services under a common control plane it manages on behalf of developers. That service will then free up developers to spend more of their time writing code versus integrating application services, said Palladino.

    That capability will be especially critical as IT organizations begin to deploy more applications on edge computing platforms that need to be integrated with a wide array of application services running on public clouds and on-premises IT environments, added Palladino.

    It’s too early to say to what degree IT organizations may be ready to rely on a service versus continuing to manage connectivity themselves. In effect, Kong is making a case for abstracting all the underlying complexity of connectivity and networking using an API to invoke everything from a simple API gateway to a service mesh designed to integrate hundreds of microservices.

    Regardless of the path chosen, the one thing that is clear is a new application connectivity as a service era has finally arrived.

  • How API Testing Can Save You Thousands

    How API Testing Can Save You Thousands

    API testing before launch can mean the difference between a $25 cloud database bill and a $30k bill

    Usage-based billing is a popular payment model in cloud-based SaaS platforms. The idea is that you only pay for the amount of data your project uses, which is great for companies that have finite metrics on their usage amount.

    It’s like getting a glass of water from your kitchen sink. Every time you open the faucet, you know your water bill will go up a few cents (actually much less than that, but for example). So let’s say the water faucet is the cloud platform and the glass represents your API requests.

    One of the ways organizations rack up exorbitant usage-based bills is from critical mistakes in the API request code. For example, your neighbor asks for a glass of water and you fill 10 glasses, or you forget to turn the faucet off after you fill the glass. This is very similar to what can happen in usage-based billing on SaaS platforms, especially for cloud-based API requests.

    An Expensive Example of Data Requests Gone Wrong

    A crowdfunding app in Colombia known as Vaki was shocked to receive a $30,000 USD bill from Google Firebase, due to some pretty simple mistakes. The company had rushed its product to launch, then noticed the app was running incredibly slowly after a version merge.

    Vaki had two choices: either take down the website or try to debug the app in a race against the money-clock. The company chose the latter option and discovered that its API was coded in such a way that with every visitor to their site, it needed to call every document of payments to see the number of supporters of a campaign or the total collected, on every page of the app.

    In other words, the company sent more than 40 billion requests to Firestore in less than 48 hours—an immensely costly mistake, although Vaki managed to work it out with Google in the end. One problem is that Vaki worked on the code while the site was already live, when any of these tools for API testing may have helped the company find the problem before launch.

    It is very important that tech teams debug every request to servers before release. Analyze if the number of requests and data transfer make sense and if your company will support the costs of the host with a big load of traffic. Otherwise, you will just catch loops or un-optimum requests with a huge bill or with your site down.

    API Learnings From Mistakes

    While cloud-based databases such as Amazon, Google Cloud and Microsoft Azure provide a pay-per-hour model, Firebase bills based on a 100k-250k read/write/delete requests to the database. So technically if you stay within this range, your bill shouldn’t amount to more than $25.

    But this also means you need to have perfect code with no mistakes or loops. Vaki was reading every document entry in a certain collection to calculate the total collected and support values for each time a user looked at a particular view.

    In other words, if a crowdfunding campaign had 100 donations, the app would call to the database once, but the reading would equate to 100 reads twice, which means a total of 200 read requests.

    Obviously, when you hit something like 2 million views on a campaign, the read requests to the database will very quickly exceed the billions. And to Google’s credit, this isn’t a get-money schemed it cooked up because it’s very easy to stay within the target metrics.

    In Vaki’s case, it was a simple human error in the data structure that wasn’t optimized for efficiency, and eventually, the company would’ve run into other problems, such as maxed out database connections.

    How to Keep Usage-billing to a Minimum

    Hosting apps today are fairly cheap, but databases can quickly grow out of control if they aren’t optimized efficiently. When it comes to traffic flow between the different parts of your application, read and write requests are the most frequent occurrence in the entire flow.

    So even though the front end may be fast to boot, it’s your backend that needs to be checked, especially as serverless architectures don’t typically offer backend data sessions. So as the backend requires more space and processing power, your overall bill increases.

    There are a few key takeaways from all this. One is that you’ll need to re-think your approach to how your data will have an impact on the total number of reads and writes, and how much processing power is required, which basically means optimizing your code for efficiency and long-term stability.

    The other takeaway is the importance of testing your API before launch, so that you can catch the sort of flaws that Vaki experienced before the product actually goes live.

  • Camunda Extends Reach of BPM Platform

    Camunda Extends Reach of BPM Platform

    Camunda, a provider of a business process management (BPM) platform written in Java, this week added support for an open application programming interface (API) to make it easier to integrate its namesake software with applications written in Javascript/Node.js, Python and C#.

    Company CTO Daniel Mayer said at a time when many organizations are investing in digital business transformation initiatives, the latest updates to the Camunda BPM platform adds support for an OpenAPI standard advanced by The Linux Foundation to enable IT organizations to integrate business processes spanning modules created using different programming languages. In the case of Camunda, IT organizations will be able to generate a REST API client using their preferred coding language that can be integrated with the core Camunda BPM platform, he said.

    In addition, Camunda announced that version 7.13 of the Camunda BPM platform will be available in the form of a lightweight distribution, dubbed Camunda BPM Run, that can be deployed as a Docker container to create a standalone engine with no Java or application server knowledge required.

    Camunda has also added support for Camunda’s Optimize 3.0 to provide a unified view of real-time process insights from any data source and the ability to visually track changes across different versions of process models using its Cawemo tool.

    Finally, Camunda has added support for version 1.3 of the Decision Model and Notation (DMN) specification as well as version 1.2 of the Friendly Enough Expression Language (FEEL) defined by The Object Management Group.

    In the wake of the economic downturn brought on by the COVID-19 pandemic, many organizations are looking to reduce costs by streamlining business processes. The decision many of them need to make is determining to what degree they want to rely on packaged applications to achieve that goal versus a platform that enables them to create custom business processes. While many rote processes can be automated using packaged applications, Mayer said the Camunda platform makes it possible to create business processes that truly differentiate organizations from rivals. Packaged applications, in contrast, drive organizations to employ the same business processes in the same way.

    Of course, organizations can customize packaged applications. However, at that point, most of them will have embarked on an application development project that would be easier to complete using a platform designed for that purpose, he noted.

    Naturally, there are other platforms for integrating business processes that revolve around graphical user interfaces. Camunda has been making the case for an open source Java-based platform that enables developers to create and deploy custom business processes using best DevOps practices at a much lower total cost. The company also commercially makes available an enterprise edition of its platform. In total, Camunda claims there are now than 100,000 developers participating in the Camunda community.

    It’s too early to determine to what degree organizations will rely on packaged applications versus BPM platforms to drive digital business transformation initiatives. However, given the current economic climate, it’s apparent these projects have never been more urgent.

  • Survey Sees More Complex API Challenges Ahead

    Survey Sees More Complex API Challenges Ahead

    A survey of more than 10,000 developers of application programming interfaces (APIs) suggests there’s lots of room for improving the overall efficiency of API lifecycle management.

    The survey was conducted by Postman, a provider of a platform for building APIs. Respondents on average said they only spend a quarter of their time (26%) on the development of APIs. The rest of the time is consumed by debugging and manual testing (22%), automated testing (11%), designing and mocking APIs (11%), managing others (9%), documentation (7%), monitoring (6%) and publishing (4%). A full 70% said they are spending more time on manual testing and debugging than they thought they should.

    All that time spent on manual testing and debugging may be having an adverse impact on the number of APIs that can be built, tested and deployed at a time when a transition to microservices-based architectures is requiring organizations to build and support more than ever.

    According to the survey results, about a quarter of respondents (24%) work with more than 20 APIs. Well over half those employed on average (53%) are for internal use, compared to 28% employed specifically for integration and 19% that are made public.

    In terms of technologies survey respondents are most excited about for the coming year, microservices (54%), containers (46%) and serverless computing frameworks (44%) top the list.

    As far as the performance is concerned, survey respondents are evenly split. Just under half (48%) said they feel that their APIs do not break, stop working or materially change specification often enough to matter. However, 28% said these issues arise on a monthly basis, while 16% said they deal with these issues weekly. Another 3% said it was a daily challenge.

    In terms of security, survey respondents are relatively confident: Nearly three-quarters of respondents (73%) said they feel that their APIs are “very secure” or have “above-average security.” Only 2% said they felt they were not at all secure.

    It’s hard to say how secure any API is without testing it. Rebecca Johnston-Gilbert, a marketing manager for Postman, said it’s apparent more organizations are starting to address security at the design phase rather than after the API has been built and deployed. Many organizations have already adopted an API-first approach to application development that enables them to manage them in isolation from the applications they are designed to support, she said.

    Among other survey findings, 73% of survey respondents said they work on a team of 10 members or less, while a quarter (26%) work on teams with 22 to 50 members. In addition, 78% of respondents have five or fewer years of experience in developing APIs.

    In general, survey respondents said they would like to see improvements in the areas of documentation (64%), standardization (59%) and sample code (58%), which suggests consuming APIs is still not all that simple.

    There is no doubt organizations increasingly will be applying best DevOps practices to the building and maintaining APIs. The challenge organizations face is, not only do they need to build and maintain what could soon be hundreds (if not thousands) of APIs to support microservices but also those APIs will need to be a lot more resilient as the dependencies between microservices exponentially increase.

    — Mike Vizard

  • GitHub Actions Advances Automation Strategy

    GitHub Actions Advances Automation Strategy

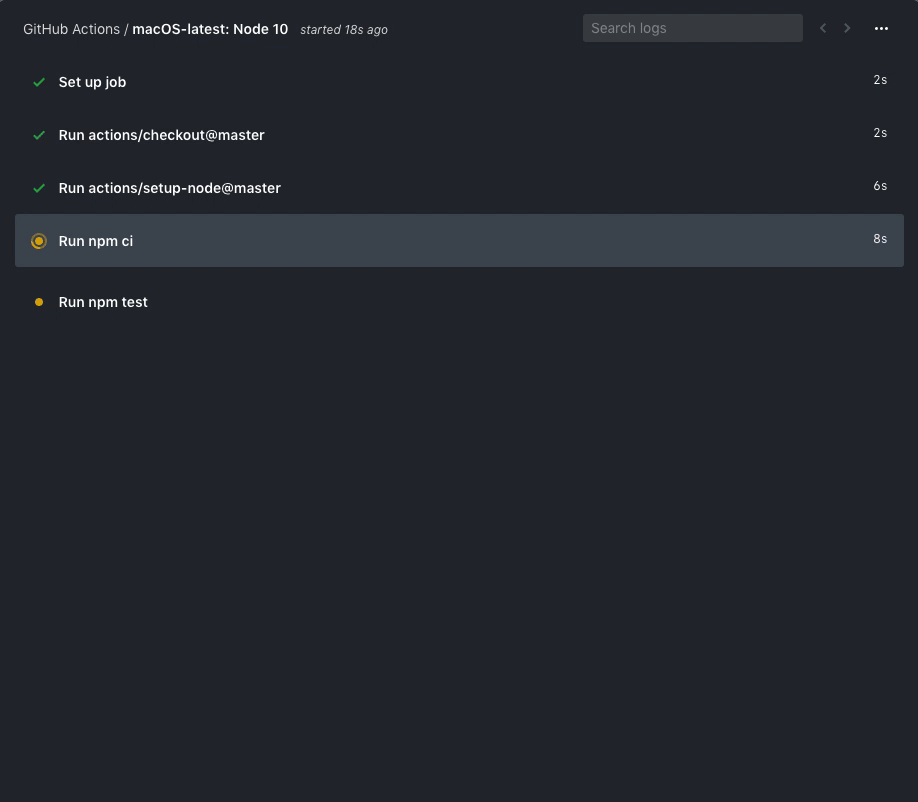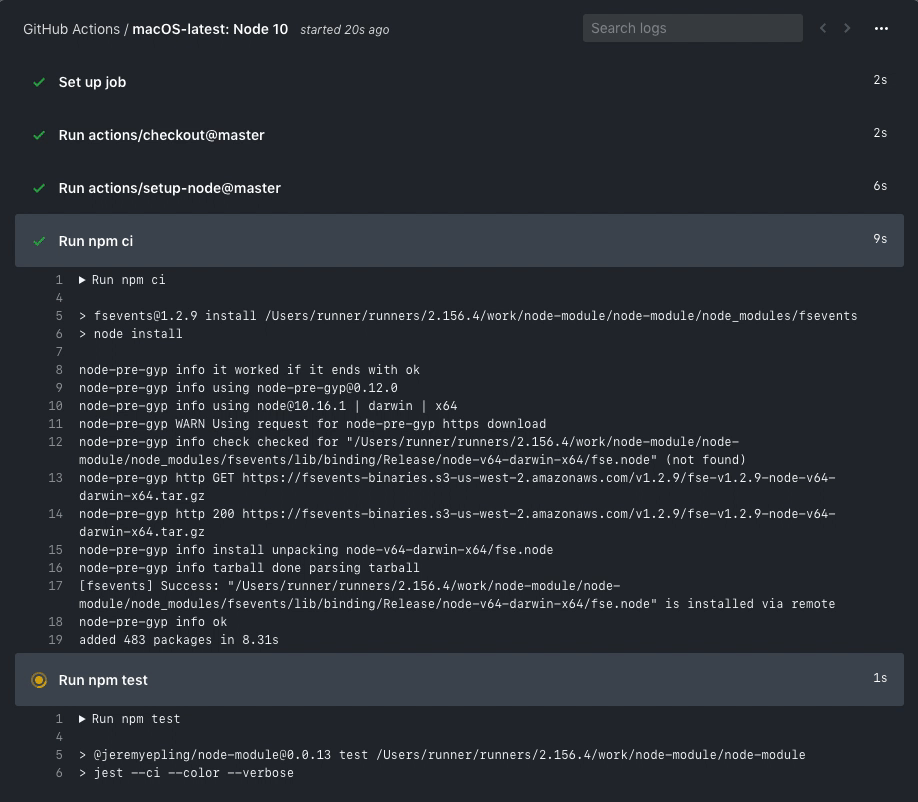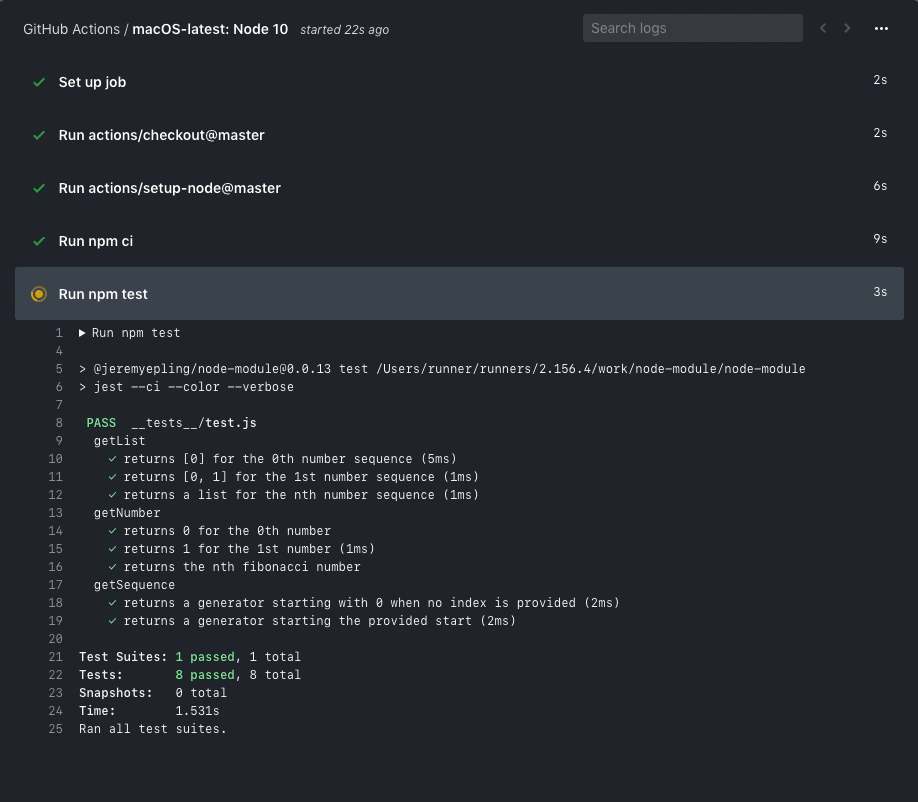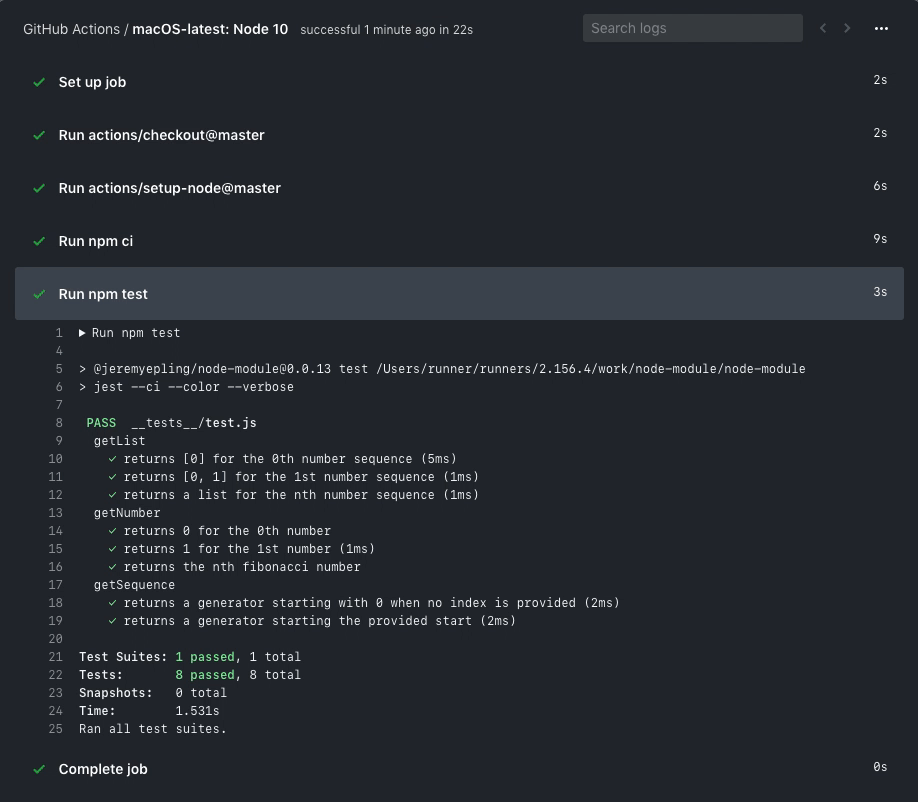
    GitHub Actions, a set of application programming interfaces (APIs) through which DevOps tools can automate workflows, is now available in beta.

    Previewed last year at the GitHub Universe event, GitHub Actions is intended to provide not only a way to automate responses to events occurring within a GitHub Repository but also share those workflows across multiple DevOps teams, said Max Schoening, senior director of product design for GitHub.

    Actions are based on YAML files, which makes it possible to write them in JavaScript or other programming languages or package them up as a set of containers. In either instance, they are designed to interact with the full GitHub API and any other public API.

    In addition, higher levels of automation enabled by GitHub Actions should make it more feasible for DevOps teams to test multiple versions of a project in parallel as workflows written in code replace manual processes, said Schoening.

    As more manual processes become automated, the number of IT teams who are intimidated by DevOps processes today should begin to decline. Organizations also should be able to apply best DevOps practices more consistently across multiple teams. Too often today the DevOps practices within the same organization tend to vary widely. Schoening also noted that given the open source history of GitHub, organizations will be able to see how workflows have been created for popular open source projects and then copy them.

    In addition, Schoening said the arm of Microsoft will continue to invest in analytics that will surface workflow recommendations that can be applied to any project regardless of the language employed or the platform on which it’s destined to be deployed.

    On one level, DevOps is all about a ruthless commitment to automation. But when automation goes wrong at scale, it can be extremely problematic. Rather than relying on “black box” approaches to automating processes, a truly open source approach to automation makes it possible for DevOps teams to see how a process is being automated and then extend it if they so choose, said Schoening. To help address the concern, GitHub Actions also provides access to live logs to provide real-time feedback as builds run, which Schoening said makes it easier for DevOps teams to debug automations created using GitHub Actions.

    It’s too early to say just how automated DevOps processes will get. There’s an emerging school of thought that contends the goal is to make it feasible for developers to spend 100% of their time writing business logic. It’s not clear whether that goal is achievable anytime soon, but progress is made with each update to continuous integration/continuous development (CD/CD) platforms. As complementary advances in machine learning algorithms and other forms of artificial intelligence (AI)—otherwise known as AIOps—occur, it’s apparent many manual DevOps processes will fall by the wayside.

    In the meantime, the workflows that make up any DevOps process should become increasingly sophisticated as advances in automation span everything from hybrid cloud computing environment to internet of things (IoT) deployments. The issue soon may not be how cumbersome any DevOps workflow is, but rather the potential limits of the imagination applied to automating them.

    — Mike Vizard

  • How to Automate an API Security Program Without Adding Staff

    How to Automate an API Security Program Without Adding Staff

    In today’s information economy, data is a primary raw material and a source of value to both providers and consumers. For many companies, entire business models are built on the exchange of information.

    Consider a ride-sharing business that owns no vehicles of its own. What the company does possess, however, is a database of private vehicle owners who are willing drivers, a roster of people who will gladly pay for a ride and an application that can instantly connect a rider with a driver via an application programming interface (API). The ride-sharing company makes its money by taking a cut of the fare.

    Another example is a company that collects and refines financial data and makes it available to investors who might want to buy stock. Companies such as E*TRADE, Merrill Lynch and Fidelity buy that investment data to make it available to their clients. APIs are at the heart of these important data exchanges.

    How Prominent are APIs?

    The information economy is synonymous with the API economy. APIs are increasingly the way business partners—internal and external—exchange and monetize data and services. APIs allow for machine-to-machine data retrieval, essentially removing barriers and accelerating access to data. There is hardly a modern application today that doesn’t provide an API to integrate with other applications and data sources. The typical mobile app today uses an average of 10 to 15 APIs to move meaningful data into and out of the app. Modern web apps called SPAs (single-page apps) do the same. APIs have proven to be so efficient and useful that many companies have begun creating new business ventures by mobilizing their data to third-party developers and the public.

    DevOps teams heartily embrace APIs to advance their ability to produce applications much more quickly. APIs, however, are largely a mystery to security teams that must ensure that this means of rapid data exchange does not create unnecessary risk and negative exposure for the company or its brand. Enterprise security teams are right to question the vulnerabilities and threats posed by APIs. Insecure APIs have led to some very serious data breaches, some of which are outlined in the Dark Reading article, “Expect API Breaches to Accelerate.”

    For example, the mobile payment app Venmo exposed sensitive details about hundreds of millions of transactions through a poorly secured API. In another case, an insecure Panera Bread API used by a mobile app exposed users’ private details through a searchable API that required no authentication to access. As a result, as many as 37 million records, which included customer personal information identifiers (PII) such as names, email addresses, physical addresses, birthdays and the last four digits of credit cards—all in plain text—were exposed. T-Mobile, McDonald’s, Symantec, Instagram and numerous other companies have suffered through significant data breaches traced back to insecure APIs. The damage is high because most APIs are designed to serve data without security in mind.

    DevOps and security teams can agree that a data breach coming from their applications is completely untenable. Thus, designing and applying a security program that spans across all APIs across all applications is an essential function in protecting data and brand. Just exactly how can this be achieved? Let’s look at the steps of automating an API security program without needing to add additional security staff.

    The Challenge of Securing APIs

    The very nature of identifying all APIs makes it a challenge to secure them. A developer can create an API in a matter of minutes and publish it on the internet with almost no resistance when using public cloud services such as Amazon, Microsoft and Google. What’s more, she can make changes to that API as often as she wants, and every change cycle presents an opportunity to introduce new risk. It’s not unusual for a developer to change her API weekly or daily.

    Let’s go back to that example of the financial services company that sells data to stock brokers. Suppose the developer makes a change to her API which unintentionally enables the brokers to see the client lists of every other broker that consumes data via the API. That would be a catastrophic breach, yet this is precisely the type of API breach suffered by the U.S. Postal Service a year ago.

    APIs today increasingly are built on serverless infrastructures such as Amazon Lambda, Azure Functions or Google Cloud Functions. Traditional firewalls, gateways and agents can’t protect this type of API built on ephemeral infrastructure. Now consider that a large enterprise might develop and/or use hundreds or even thousands of APIs. The magnitude of the challenge to secure every API becomes apparent. Manual security oversight and enforcement are simply out of the question. Automation of security assessments done on a continuous basis is the only scalable approach.

    Start With an API Security Framework

    Every organization that creates or uses APIs needs an API security framework that consists of three steps:

    1. Continuous API discovery and specification creation.
    2. Continuous API specification analysis and inspection.
    3. API policy enablement and enforcement.

    Let’s have a look at each step and its impact.

    Know What APIs Are in Use and What They Are Intended to Do

    Gathering API specifications is an important first step in defining what APIs are intended to do. However, many APIs exist without any specification. A service that creates API specs helps to deal with those APIs void of documentation. However, this spec creation service also needs to continuously monitor and discover new APIs to remedy the problem of not knowing what APIs exist and their intended function. It’s common for a developer to document what her API is designed to do initially, but updating that documentation every time she makes a change to her API is rare. To compensate, the organization needs to have an automated tool that gathers this information and notes each time an API changes, then accordingly updates the API specification.

    For example, consider an API that exists to transfer customer information between a company’s back-end server and a mobile application. The developer adds a feature or two and the API changes to support these new features, resulting in the API doing things it wasn’t originally expected to do. How would the organization know about these changes? There is a need to continuously analyze the API for such changes to understand the current state of specifications for what the API is doing.

    The organization needs to create specifications of all the APIs, especially publicly facing APIs hosted in the cloud. This service needs to operate continuously to look for changes in the APIs constantly. There are tools that can automate these various activities, including discovering new APIs and changes to existing APIs. These tools also can uncover other cloud resources and data services related to these APIs; enumerate API domains, functions and associated methods; and generate a standards-based (Swagger, OpenAPI v3) spec if one does not exist.

    Analyze the APIs for Security Threats

    The next step is to perform a security inspection on each API operation every time it changes. The security team needs to know: Does it have the right data encryption? Is proper authentication in place? What type of authorization policy is being applied? What is the API’s level of availability? What kind of data sources does it access? Knowing each API’s current security posture is critical if the organization wants to avoid a data breach.

    This API analysis needs to take place continuously and at scale since manual processes are ineffective for organizations using numerous APIs. Fortunately, there are tools and technologies that automate this process and perform tasks such as finding potential vulnerabilities within the authentication and encryption layers of the API. The tools also can generate security tasks with recommended changes for developers to remedy their respective API problems and alert security personnel when there are discrepancies between the API specification and its functional operations.

    Create and Enforce Security Policies

    No two companies have the same appetite for risk. If there’s one aspect of creating an API security program that requires a manual investment of time, it’s policy creation. Automation then can be used to enforce the policy. A security policy for APIs should start with two primary questions: Who should be able to utilize the API? And what level of sensitivity, regulatory oversight and/or privacy concerns does the API have? Based on the answers to those first two questions, you can form the basis for the security policy.

    For example, a bank has an API that provides transaction statements for a specified account. That API has access to extremely sensitive and private information for each of its customers. One customer should never be allowed to access another customer’s account statements. Therefore, the authentication, authorization, encryption and availability of that API would be set to the most restrictive security standards available to ensure data exposure is tightly controlled. Another API from this same bank may provide the current interest rates of savings and money market accounts. This is data the bank likely would share with anyone potentially interested in opening an account with them. In this case, the level of security restriction would be lowered to support a wide variety of systems, browsers, SDKs and apps to ensure this information is highly available.

    Historically, API policy enforcement for authentication, encryption and availability was often done at the network gateway layer. As applications have migrated to modern architectures such as mobile and cloud, the gateway approach has increasingly become less practical, less scalable and more restrictive. Application developers are often leveraging authentication, encryption and availability zones provided to them through SDKs and/or cloud services. In these cases, an automated service that integrates with these security services is a better approach for API policy enforcement versus traditional network gateways.

    Automation is Key

    Security teams are notoriously overworked and short-staffed. Worldwide, there’s a dire shortage of skilled security professionals available for hire, so adding additional security staff to build and execute the API security program isn’t a practical option. Bringing in consultants is expensive and can be budget-busting. Thus, automation through tools and technology is a sensible approach.

    Automation provides the benefits of saving time and money when it comes to executing the three steps outlined above. What’s more, an automated program provides consistency in the repetitive tasks necessary to discover, document and analyze the APIs in use, and enforce corporate policies to control risk.

    APIs are critically important to modern applications. DevOps people heartily embrace them, and security teams can learn their value as well once they understand how a robust and continuous API security program will benefit their organization.

    — Doug Dooley

  • Kong Applies AI to API Management

    Kong Applies AI to API Management

    Kong today announced today two offerings that rely on artificial intelligence (AI) to automate the management of application programming interfaces (APIs).

    The first offering, dubbed Kong Brain, collects data from any existing platform to auto generate documentation, which can then be used to automate the configuration of the Kong Enterprise API management platform.

    The second offering, dubbed Kong Immunity, leverages machine learning algorithms to analyze traffic patterns to first define normal traffic and then train models to automatically detect any anomalies and issue alerts when those anomalies are detected.

    Kong CTO Marco Palladino said Kong Brain is intended to make it easier to manage APIs across a modern IT environment by making it possible to continuously reconfigure APIs as new code is added to any platform connect to Kong Enterprise.

    In addition, Kong Brain makes it simpler to visually map services and their endpoints to provide deeper visibility into API traffic and the health of any given service, said Palladino.

    Kong Immunity, meanwhile, enhances the overall security of the IT environment by identifying potential threats before they proliferate across the API ecosystem, he notes.

    Available under an early access program, Kong Brain and Kong Immunity represent the first steps toward employing AI to layer a central nervous system that automates governance, security ad documentation while increasing the reliability of the overall API ecosystem, Palladino said.

    As microservices specifically and IT in general continue to evolve, the number of dependencies that will exist across the IT environment will far exceed the ability of any IT staff to manage manually. That issue will become especially acute as more organizations embrace applications based on microservices, Palladino said, because each microservice within that application has its own set of APIs that need to be managed. While Kong Enterprise can support both microservices and traditional monolithic applications, Palladino expects the proliferation of microservices across multiple cloud platforms to force the need to adopt API management platforms infused with AI.

    Obviously, the introduction of AI into IT environments will have a profound impact on API management and associated DevOps processes. While developers typically create APIs, responsibility for managing APIs has been shifting to IT operational teams. By adding AI to API management platforms such as Kong Enterprise it should become significantly easier for any enterprise to manage APIs at scale. Of course, AI models don’t work out of the proverbial box. But as the machine learning algorithms that drive those AI models become more familiar with the IT environment, the more automated the management of the APIs distributed across that IT environment becomes.

    What impact AI will have on DevOps processes remains to be seen. But it’s increasingly clear that AI will be applied across the IT operations spectrum. In theory, the more automated IT operations becomes the more resources any organization should be able to shift toward developing more applications, which naturally generates more APIs to be managed. It may take a little more time before most organizations have enough confidence in AI to make that transition. But at this point, it’s not so much a question of whether AI will be applied to IT operations as much as it is to what extent.

    — Mike Vizard

  • Axway Extends API Management Reach

    Axway Extends API Management Reach

    With application programming interfaces playing a larger role in the DevOps environment, Axway has added to its API toolkit for developers. The company expanded its AMPLIFY API management platform to include a visual tool for composing and integrating APIs and enhanced its API Manager tool so that it now can be invoked to scale resources up or down as needed. In addition, Axway unveiled API Central Service that makes it easier to integrate APIs across an ecosystem of organizations that make their services available via the AMPLIFY marketplace.

    Other new capabilities include an open-source MQTT connector for building internet of things (IoT) applications, a connector to the Microsoft Azure Cloud and tighter integration between Axway’s MFT file transfer software and the Syncplicity file synchronization software it acquired earlier this year.

    Axway also merged the Titantium SDK for building native mobile applications using JavaScript into the Core SDK for developers and is previewing the Query Builder Analytics tool, which enables users to do ad hoc query of mobile statistics. The Titanium code is based on technology developed by Appcelerator, which Axway acquired early last year.

    The announcements were made at the recent Axway SPARK 2017 conference. Vince Padua, vice president of platform and products for Axway, says these and other enhancements to the Axway API portfolio are intended to make it easier for organizations to craft microservices spanning multiple platforms. In some instances, those microservices will be crafted by developers, but Axway believes more advanced users will be stitching together microservices on their own using visual tools, says Padua.

    While most early use of APIs was driven by web-based applications facing external users, using APIs to interconnect services inside the enterprise now dwarfs the number of instances of published external APIs, he notes. The proliferation of those APIs has created a significant DevOps challenge for organizations and requires an API management platform to streamline the management of various back-end service. At the same time, Padua notes that DevOps teams working in collaboration with line-of-business units have taken over much of the API management, which previously was left up to individual developers. Now, IT organizations are trying to strike a balance between maintaining control and developer productivity, he says.

    The shift in API management responsibilities has also driven a wave of mergers and acquisitions over the last two years as API management has become embedded in mainstream application development platforms. But there’s also a fierce debate over the degree to which legacy API management platforms can support microservices. As microservices based on emerging technologies such as containers or more mature Java programming tools continue to evolve, API management is becoming more critically important. Each microservice generates its own API that needs to be maintained as each microservice gets continually updated. That requires an API management platform that can support all levels of API call activity that once would have been assumed to be unimaginable.

    — Mike Vizard