Category: Features

  • AI Native Dev: Shaping the Future of AI-First Software Development

    AI Native Dev: Shaping the Future of AI-First Software Development

    In an era where artificial intelligence is rapidly transforming the software development landscape, a new community has emerged to lead this evolution: AI Native Dev. The community is centered around the website, https://AINativeDev.io/, The site serves as a platform for a raft of different types of content and information.

    This platform is not just a repository of tools and insights though; it’s a vibrant hub for developers dedicated to reimagining software creation through an AI-first lens.

    I recently had a chance to sit down with my friend Patrick Debois, of DevOps fame who is a prominent member of this budding community. You can listen to my DevOps Chats podcast with Patrick for more color and details.

    What is AI Native Dev?

    AI Native Dev is a collaborative initiative that brings together developers, technologists and thought leaders to explore and define the principles of AI-native software development. Unlike traditional AI-assisted development, which integrates AI tools into existing workflows, AI Native Dev advocates for a foundational shift. It emphasizes building software with AI as a core component from the ground up, fundamentally altering how applications are conceived, designed, and maintained.

    The community is spearheaded by industry veterans, including Guy Podjarny, founder of Tessl and former CEO of Snyk, and Simon Maple, a seasoned developer advocate. Their combined expertise in security, development, and AI positions AI Native Dev as a leading voice in the AI-driven development movement. 

    Beyond GuyPo and Simon Maple, other members of the community include Patrick Debois, Olivier Pomel, Macey Baker and Amanda Brock. 

    Core Principles of AI Native Development

    At the heart of AI Native Dev are four guiding principles that encapsulate the ethos of AI-first software engineering: 

    1. Specification-Driven Development: Emphasizing clear, structured specifications that serve as the foundation for AI-generated code. This approach ensures that AI tools can produce accurate and contextually relevant codebases.
    2. Context-Aware Development: Leveraging AI’s ability to understand and integrate comprehensive project contexts, leading to more informed decision-making and cohesive software solutions.
    3. AI Agents as Developers: Transitioning AI from a supportive role to an active participant in software creation, where AI agents can autonomously develop and operate components of software systems.
    4. Human Oversight by Design: Ensuring that AI-driven workflows are designed with clear human oversight mechanisms, maintaining alignment with human intent and ethical standards.

    These principles are not static; AI Native Dev encourages community contributions to refine and evolve these guidelines, fostering a dynamic and inclusive development philosophy. 

    Engaging with the Community

    AI Native Dev offers multiple avenues for engagement, catering to a diverse range of interests and expertise:

    • Discord Community: A space for real-time discussions, knowledge sharing, and networking with like-minded developers passionate about AI-native development. 
    • AI Native Dev Podcast: Hosted by Guy Podjarny and Simon Maple, the podcast delves into the nuances of AI-native development, featuring conversations with industry leaders and innovators. 
    • AI Native DevCon: An annual virtual conference that showcases practical applications of AI in software development, offering insights into current trends and future directions.
    • AI Dev Tooling Landscape: A comprehensive, community-curated repository of AI tools and technologies spanning the entire software delivery lifecycle, from prototyping to deployment. 

    These platforms collectively serve as a nexus for learning, collaboration, and innovation, empowering developers to stay at the forefront of AI-native methodologies.

    The Vision Ahead

    AI Native Dev is more than a community; it’s a movement aimed at redefining the paradigms of software development in the age of AI. By fostering a culture of openness, collaboration and continuous learning, AI Native Dev aspires to equip developers with the tools, knowledge and mindset necessary to harness AI’s full potential.

    As AI continues to evolve, so too will the practices and principles of software development. AI Native Dev stands as a beacon for those ready to embrace this transformation, offering a roadmap for building software that is not only enhanced by AI but fundamentally rooted in it. 

    Join the AI Native Dev Community

    Embark on your journey into AI-native software development by exploring the resources and connecting with the community at AINativeDev.io. Whether you’re a seasoned developer or new to the field, AI Native Dev welcomes all who are eager to shape the future of software development through the lens of artificial intelligence.

  • Minimus Unfurls Service for Accessing Secure Software Artifacts

    Minimus Unfurls Service for Accessing Secure Software Artifacts

    Minimus today at the 2025 RSA Conference launched a managed service through which it ensures application development teams are provided access to a secure set of minimal container images and virtual machines.

    Company CTO John Morello said the Minimus service eliminates the possibility that developers might inadvertently download software artifacts that might be infested with malware.

    At the core of the Minimus service is an operating system the company specifically developed to make managing the orchestration of software artifacts simpler. That capability then enabled Minimus to ensure that hardened software artifacts that have been configured to minimize the overall size of the attack surface that might be presented can be integrated into DevSecOps workflows, said Morello.

    Minimus also constantly monitors threat intelligence to ensure the security of those artifacts while also providing developers with real-time insights into potential threats to reduce overall risk, he added.

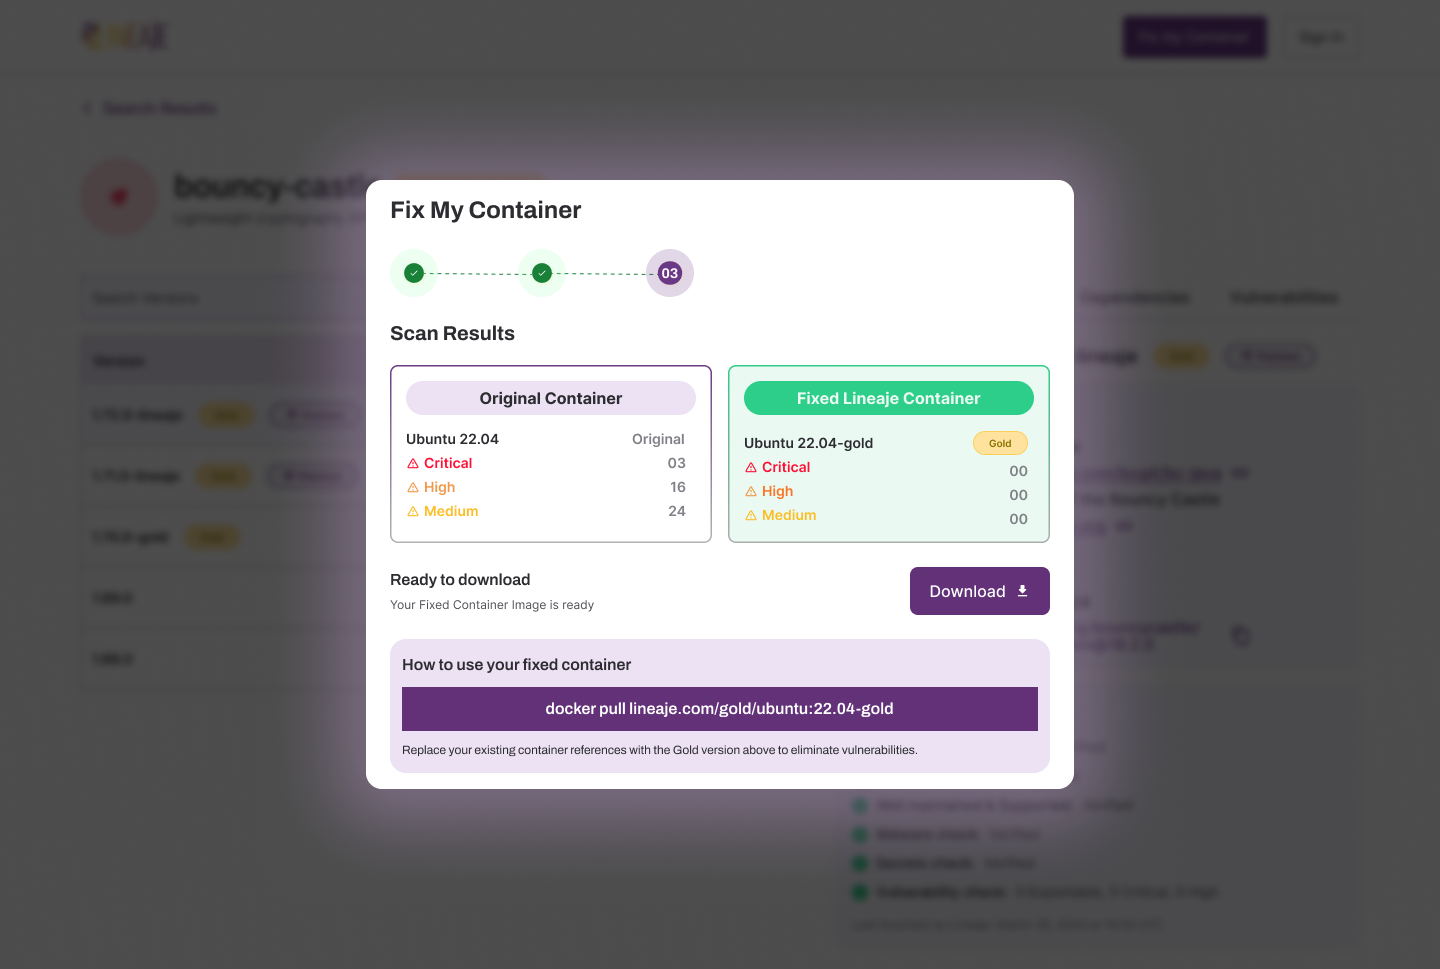
    While a lot of progress has been made in securing software supply chains, too many developers are still downloading software artifacts from insecure repositories. The Minimus service provides an alternative approach to accessing software artifacts that have been vetted by application security experts for known vulnerabilities and security weaknesses, said Morello.

    It’s not clear why more DevSecOps teams are not limiting the number of repositories that application developers can use to download software artifacts but cybercriminal syndicates have clearly become more adept at injecting malware into them as part of an effort to infect as many downstream applications as possible. Unfortunately, it might not be years before that malware is actually activated.

    DevSecOps teams have been making a concerted effort to provide application developers with scanning tools that discover vulnerabilities and malware in software artifacts. However, the success of those efforts is often limited simply because the number of alerts being generated overwhelms the ability of application developers to recognize and remediate issues based on their actual severity. The Minimus service reduces the need to run those scans by ensuring the software artifacts being used are secure in the first place, said Morello.

    It’s not clear how many application security incidents can be traced specifically back to vulnerabilities and malware in software artifacts, but most developers would prefer to not have to address an issue discovered months, sometimes even years, after an application has been deployed in a production environment. As always, an ounce of prevention is always going to be worth more than a pound of any proverbial cure.

    The challenge at this point isn’t so much finding the technologies required to secure those artifacts as much as it might be changing the culture of application developers that have for decades now routinely downloaded artifacts from public repositories without considering the application security implications.

    Hopefully, the overall state of application security will improve as more organizations move to lock down their software supply chains. In the meantime, however, DevSecOps teams rather than investing in more tooling may want to consider trying to solve the issue at the root source of the repository problem.