Category: Enterprise DevOps

  • 10 Key Features of AI Code Assistants

    10 Key Features of AI Code Assistants

    One of the most potent tools that have emerged to streamline the coding process is code assistants. Code assistants are software tools designed to assist programmers by providing suggestions and automated features that help in writing code more efficiently and accurately. They act as virtual aides, making the coding process faster, more intuitive and less prone to errors.

    Code assistants can be categorized into two types: Rule-based and AI-based. Rule-based assistants follow predefined rules and perform according to set guidelines. They are mainly used for syntax highlighting, code formatting and basic error detection. AI-based code assistants can learn from past coding patterns, predict what a programmer is trying to achieve and suggest appropriate code snippets. They are capable of understanding the context of the code and providing accurate suggestions, as well as generating entire blocks of code based on natural language instructions. Read this blog post for examples of popular AI coding assistants.

    Whether you are an experienced software developer handling complex projects or a beginner, coding assistants can automate the tedious aspects of coding, allowing you to focus more on problem-solving and innovation.

    The Growing Importance of AI in Software Development

    As software development becomes more complex and time-sensitive, the role of AI in this field has grown significantly. AI-driven code assistants represent a major shift in how software is developed. They bridge the gap between human expertise and the efficiency of automated processes. 

    AI in software development not only speeds up the coding process but also enhances the quality of the code. These tools can analyze vast amounts of code, learn from it and apply that learning to assist developers in real-time. They can adapt to different coding styles and requirements, making them versatile tools for a wide range of programming tasks. Furthermore, as software projects increase in size and complexity, AI code assistants become crucial in managing and navigating these complexities. They offer intelligent insights, detect potential issues before they become problematic, and assist in keeping large codebases clean and manageable.

    In addition to increasing efficiency, AI code assistants are instrumental in reducing the barrier to entry in software development. They make coding more accessible to people with varying levels of expertise, including those who are new to programming. This accessibility is essential in an era where the demand for software development skills is continuously rising. By providing real-time assistance and learning resources, AI code assistants are not just tools for current developers but also learning aids for future generations of programmers.

    10 Key Features to Expect from Code Assistants in 2024

    With the rapid advances in large language models (LLMs), the following features are becoming standard in coding assistants as we enter 2024.

    Advanced Contextual Understanding

    Modern code assistants are evolving to understand the context of code more intricately. Unlike simple autocomplete tools, these AI systems can analyze the broader scope of a project, recognizing patterns and offering suggestions that align with the overall architecture and design patterns. This advanced understanding not only streamlines coding but also aids in maintaining consistency throughout the codebase.

    Real-Time Code Optimization Suggestions

    AI tools can proactively recommend changes to improve performance and efficiency. For instance, a code assistant might suggest a more efficient algorithm or highlight redundant code blocks that can be simplified. This feature not only enhances code quality but also serves as a learning tool for developers, exposing them to best practices and alternative approaches.

    Enhanced Debugging Assistance

    Debugging is often a time-consuming aspect of development. In 2024, expect code assistants to revolutionize this process by offering enhanced debugging assistance. Through deep analysis, these tools automatically detect errors and anomalies, suggesting potential fixes. They can pinpoint the exact location of a bug and provide context, significantly reducing the time developers spend in the debugging phase.

    Automated Refactoring

    Refactoring is crucial for maintaining clean code, and AI-driven assistants now offer sophisticated automated refactoring capabilities. They intelligently suggest changes that improve code readability and maintainability, such as restructuring code or renaming variables for clarity. These suggestions will be particularly beneficial for managing and updating legacy code, ensuring it adheres to modern coding standards.

    Code Documentation Generation and Update

    Keeping documentation updated is a challenge. Code assistants can now automate this task by generating and updating documentation in real-time. As code changes, the documentation will reflect these updates, ensuring that it always stays in sync with the codebase. This feature will be invaluable in large teams where keeping track of changes can be daunting.

    Predictive Coding Assistance

    Moving beyond reactive suggestions, code assistants will offer predictive assistance. By analyzing coding patterns and project structures, these tools will predict a developer’s next steps and offer relevant suggestions even before they are explicitly requested. This proactive approach will speed up the development process, reducing the cognitive load on developers.

    Understanding and Responding to Developer Queries in Natural Language

    Developers can pose queries or express coding requirements in plain English, and the assistant will interpret and execute these requests. Chat-based interfaces offered by leading AI coding assistants take this one step further. This advancement will make coding more intuitive and accessible, especially for beginners or non-expert users.

    Real-Time Suggestions and Conflict Resolution in Team Projects

    Collaboration in coding projects can lead to conflicts and inconsistencies. Code assistants now offer real-time suggestions and automated conflict resolution for team projects. These tools will identify potential conflicts in merge requests and suggest optimal resolutions, enhancing team collaboration and maintaining code integrity.

    Personalized Coding Assistance Based on Past Interactions

    Personalization is becoming a significant feature of code assistants. By learning from past interactions with a developer, these tools will tailor their suggestions and support to align with individual coding styles and preferences. This adaptive learning approach ensures that the assistance provided is most relevant and efficient for each developer.

    Enhancing Accessibility of Coding for Non-Expert Users

    One of the most impactful features of code assistants is their role in democratizing coding. By simplifying complex coding concepts and automating mundane tasks, these tools will make software development more accessible to non-experts. Beginners and those learning new programming languages will find these assistants particularly useful, as they provide guidance and learning aids.

    Conclusion

    Code assistants powered by AI are becoming an integral part of the software development process. They not only make coding faster and more efficient but also reduce the chances of errors, making the resultant software more reliable. The role of code assistants is only expected to grow, bringing in more advanced and intuitive features. Whether you are a seasoned programmer or a newbie, embracing code assistants can be a game-changer for your coding journey.

  • Salesforce Adds Ability to Apply Custom Security Policies to APIs

    Salesforce Adds Ability to Apply Custom Security Policies to APIs

    Salesforce today added the ability to customize security policies for application programming interfaces (APIs) to the Mulesoft Anypoint API management platform.

    Gerry Egan, vice president of product management for Mulesoft at Salesforce, said this capability makes it possible for organizations to use an Anypoint Flex Gateway Policy Development Kit to streamline development of custom API security policies that can be implemented as code.

    In addition to providing integrations with integrated development environments (IDEs), the Anypoint Flex Gateway Policy Development Kit also provides test policies that can be employed to ensure API security.

    That approach makes it simpler to ensure APIs are secure as they are being built and deployed within the context of an automated DevOps workflow versus having to rely entirely on a separate API security platform, he noted.

    The Mulesoft Anypoint Gateway already comes with security policies that DevSecOps teams can readily implement. Salesforce is now adding the ability to apply custom policies that DevOps teams can apply as it becomes apparent cyberattacks against APIs are becoming more sophisticated, noted Egan. Those policies can, for example, be used to remove sensitive data or replace it with a token, he added.

    Responsibility for API security is often not well established in many organizations, but as more accountability for API security shifts left toward DevSecOps teams, there is growing interest in addressing the issue as code when APIs are developed and deployed. While cybersecurity teams are responsible for maintaining cybersecurity after APIs are deployed, few of them have any insight into how an API is crafted. That’s a significant issue because cybercriminals have become more adept at both exfiltrating data via external facing APIs in addition to manipulating the underlying business logic to compromise a digital process, noted Egan.

    The Mulesoft Anypoint Gateway automates the process of building and applying security policies to APIs as part of the software development life cycle (SDLC) in a way that minimizes any impact on developer productivity, he added. That approach provides the added benefit of reducing the level of cognitive load developers would otherwise experience if they had to manually create software policies, said Egan.

    In general, most APIs are internally facing, but it’s not uncommon for them to suddenly be exposed to the internet as application use cases evolve. The best way to ensure API security is at the point of creation. Providing developers with API security tools gives them an opportunity to address security issues at the beginning of the application development process.

    There have already been several cybersecurity breaches involving APIs in the past year. It may only be a matter of time before there are additional breaches that could prove catastrophic. Regardless of the size of the API breach, the application development team that created and deployed the API in the first place is ultimately going to be held accountable for fixing it. The challenge is to find the simplest way to eliminate the issue in the first place at a time when the number of APIs being built and deployed only continues to explode.

  • IBM Adds Lower-Cost Linux Mainframe to Portfolio

    IBM Adds Lower-Cost Linux Mainframe to Portfolio

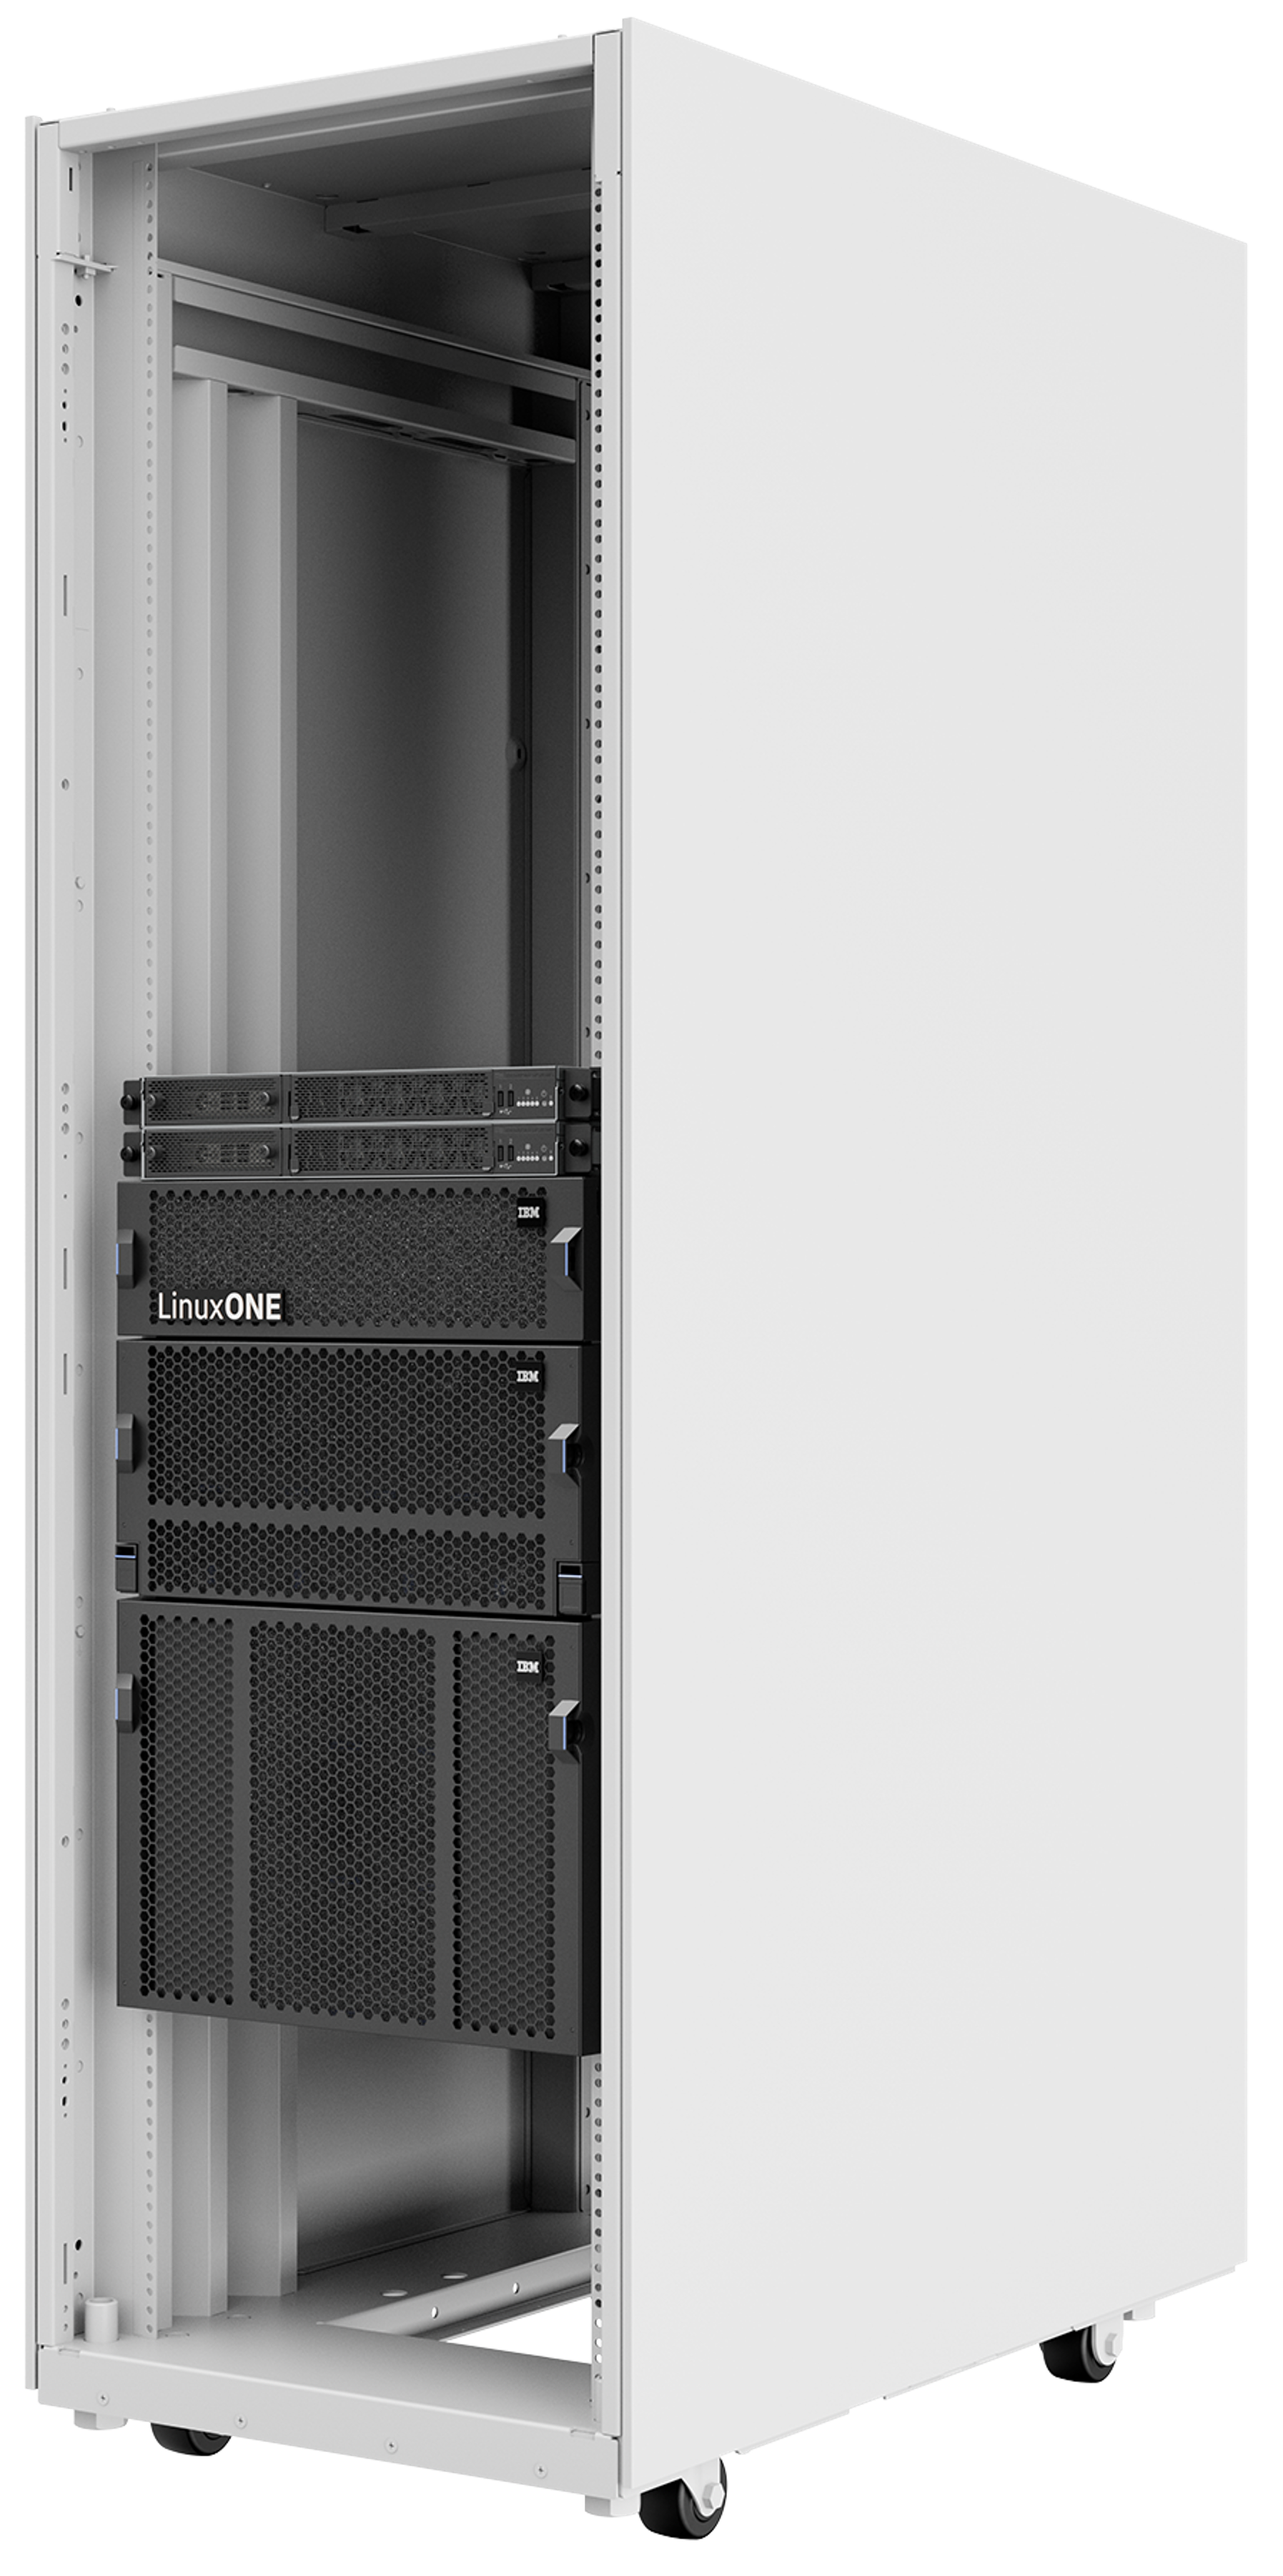
    IBM today made its most aggressive move yet in its quest to make mainframes running Linux more affordable, launching an entry-level platform starting at $135,000.

    The IBM LinuxONE 4 Express is a pre-configured rack system that is based on the same 5.2Ghz IBM Telum processor that IBM uses in its Z16 series of mainframes.

    In addition, the platform supports IBM Secure Execution, which is designed to thwart any attempt to decrypt data in the future using quantum computers.

    IBM claims organizations that move Linux workloads from x86 servers to an IBM LinuxONE 4 Express can save over 52% on their total cost of ownership over five years.

    The overall goal is to make it simpler for organizations to consolidate workloads that otherwise would need to be deployed across a distributed computing environment, she added. That approach ensures higher levels of availability for workloads that are increasingly processing massive amounts of data using two levels of physical and two levels of virtual cache in a way that consumes less energy, noted Tina Tarquinio, vice president of product Management for IBM Z and LinuxONE.

    The IBM LinuxONE 4 Express also includes an integrated accelerator for running artificial intelligence (AI) inference engines using more than 6 TFLOPs compute capacity per chip.

    IBM expects that as more organizations process sensitive data to drive AI applications, there will be increased interest in deploying applications in more secure on-premises IT environments, said Tarquinio. Mainframes provide a more cost-effective way to achieve that goal at a time when DevOps teams are embracing methodologies such as platform engineering to centralize the management of workloads, she added.

    At the same time, increased reliance on automation is making it simpler for IT teams to rely on multiple types of platforms to optimally process workloads. That capability enables IT teams to make platform decisions that are based on fit-for-purpose best principles more easily, noted Tarquinio.

    It’s not clear how many organizations will now be able to afford a mainframe when the initial cost of an x86 server is still much lower. But in the face of ongoing economic uncertainty, it seems more organizations are willing to consider all their options. The issue is that adding additional X86 servers is often viewed as the path of least resistance to increasing compute capacity.

    Naturally, each IT team will need to decide what path forward makes the most sense for them, but as workloads continue to become more data-intensive, it’s clear that infrastructure requirements are changing. The more data that needs to be processed, the more challenging it becomes to maintain service level agreements that are based on maintaining specific levels of application performance, noted Tarquinio.

    The challenge now is determining where best to run those workloads across an increasingly hybrid cloud computing environment that continues to offer more options as IT platforms evolve and expand.

  • Graylog Makes Free API Security Tool Available to Developers

    Graylog Makes Free API Security Tool Available to Developers

    Graylog this week made available a free version of its platform for securing application programming interfaces (APIs), intended to encourage developers to adopt best practices to secure them.

    The free version of Graylog API Security has all the capabilities of the paid version but is limited to 16GB of local rolling storage on a single node with a one-year renewable license.

    Graylog CEO Andy Grolnick said the goal is to make it simple for developers to use this edition of the platform as they are building APIs. As applications are deployed in a production environment, the expectation is organizations will then need to access the version of the platform that is designed to scale, he added.

    Based on technology Graylog gained with the acquisition of an API security platform originally developed by Resurface.io, this free version of Graylog’s API security platform is trying to help bridge the divide between the application development teams that create APIs and the cybersecurity teams tasked with protecting them, said Grolnick.

    Capabilities of the platform include API classification, discovery, risk scoring, an ability to capture API request and response payloads and continuous monitoring of API and threat signatures in real-time. Collectively, these capabilities enable Graylog API Security to provide high-fidelity alerts using a data lake that is embedded in the platform, noted Grolnick.

    That approach enables Graylog API Security to capture all API requests and response details to distinguish valid API traffic from malicious activity involving, for example, data exfiltration hiding under valid response codes.

    In addition, Graylog API Security automatically surfaces remediation guidance for developers who typically lack cybersecurity expertise.

    API security has become a major DevSecOps issue because cybercriminals are increasingly targeting APIs to steal data. As more externally facing APIs are deployed, the overall size of the attack surface that needs to be defended increases exponentially.

    A recent survey conducted by Enterprise Strategy Group (ESG) on behalf of Graylog found more than three-quarters of respondents (76%) have an average of 26 APIs per application. Most respondents are using open APIs for public consumption (67%) or are connecting applications with partners (64%).

    In general, most of those APIs are internally facing, but it’s not uncommon for those APIs to suddenly be exposed to the internet as use cases for applications evolve. The challenge is that few cybersecurity teams have visibility into APIs that, when manipulated by malicious actors, can expose code or provide a mechanism through which business processes can be compromised. This issue often exists because, in many organizations, it’s still not clear who is actually responsible for API security.

    Arguably, the best way to ensure API security is at the point of creation. Providing developers with API security tools gives them a chance to do the right thing from the beginning of the application development process, said Grolnick.

    There have already been several cybersecurity breaches involving APIs in the past year. It may only be a matter of time before there are additional breaches that could prove catastrophic. Regardless of the size of the API breach, the application development team that created and deployed the API in the first place is ultimately going to be held accountable for fixing it.

  • Security Across the SDLC

    Security Across the SDLC

    We’ve seen some interesting movements in the security space over the last couple of years. My focus is on application security, but one of the movements we’ve seen is the blurring of what is application and what is infrastructure security, so I do a fair amount of that also. And then, with the advent of WAAP, we have network security playing a role in AppSec… It’s a growing snowball.

    I will start with the mandatory happy declaration that DevOps no longer treats security as an annoyance. While we’re well past that, I think the shock of the whole “security is a problem, not protection” mentality that DevOps started with is still hanging with us, and some still actively believe that. But at this point, we’re well on the “Security is part of the process” trail we should be on.

    If you look at the top-level changes, static application security testing (SAST) vendors have grown to be development security, covering SAST, DAST, IAST, RASP and even a bit of data security. Meanwhile, load balancers and WAF slowly evolved into full-on web applications and API security that covers the production side with active protections for things like DDoS and DLP.

    Likewise, we’ve seen this with the growth of cloud workload protection and how the entire digital architecture is being pulled into CSPM.

    I’ve said it before – we’re in a consolidation phase. It looks like it will go even further than I thought, though. Now, we are starting to see an interesting development: WAAP vendors are starting to include some or all of DAST, SAST and RASP. Arguably, they always did some IAST because their focus was on runtime protection, but their emphasis is more on protection than test, so it will be interesting to see that bit expand also.

    And all of this includes an inconvenient fact. We don’t have any more people to do security than we ever did; in fact, we have less. That’s part of the reason that we haven’t shoved security everywhere – there aren’t people to do it. In true DevOps fashion, we have distributed the work across other teams – Dev is right there where code security and API security start, so we’ve implemented SAST and DAST bits right into the IDE, for example. Or Ops has always done some amount of security, and we’ve just upped the amount. But they don’t magically have more time, either. I’m sure you are feeling it if you are a practitioner; almost all of us are. AI promises to help with that, and in security, it will likely deliver. Another thing I’ve pointed out before is that security is one space that really does stand to gain from generative AI – in helping make more secure code, in helping make all the permutations of tests, in making rules based upon observed data and more. The time-saving benefits will deliver, in my opinion. But it’s still a lot of work, and some of it is straight-up additional work because we weren’t doing things like container security a few years ago.

    In the short term, if full SDLC security is applied, there will be more work. In the long term, the mega platform for security may well reduce this work as it limits notifications across tools. Maybe we should name the coming mega platform SecArch. Also in the long term, AI will help alleviate some of the load. Until then, buckle in. You’re not likely to get staff to cover new work. But it will be worth it. Just keep plugging along, and know when to say you just can’t add one more thing to the pile.

  • New Relic Adds Ability to Correlate IT Events to Business Processes

    New Relic Adds Ability to Correlate IT Events to Business Processes

    New Relic this week added an ability to enable DevOps teams to better understand the potential business impact any change to an IT environment might have.

    Manav Khurana, chief product officer for New Relic, said New Relic Pathpoint adds a dashboard to the company’s observability platform through which business metrics can be collected alongside telemetry data. That data is collected either via connectors provided by New Relic or via a metrics application programming interface (API) that IT teams can invoke.

    IT teams can use that API to connect to custom applications or an end-to-end business process, noted Khurana.

    All that data is then modeled alongside DevOps telemetry data to provide insights into the impact any change might have on the business in real-time, he added. That approach provides the added benefit of making it easier to strategically align the management of applications, services and infrastructure by business function, noted Khurana.

    In the near future, New Relic will also extend the natural language capabilities it is currently previewing to New Relic Pathpoint, he said.

    Longer term, New Relic is working toward making it possible to model how proposed changes to business processes will impact IT environments, added Khurana.

    Business and IT leaders intuitively understand that every business event creates a corresponding IT event, but most organizations manage those processes in isolation. New Relic Pathpoint presents an opportunity to close a divide between IT teams and the rest of the business that has plagued organizations for decades.

    It may be a while before advances in data analytics and AI eliminate that divide completely, but creating a common set of metrics for managing business and IT processes is a crucial first step.

    In the meantime, DevOps teams, in addition to accelerating the pace at which applications can be built and deployed, are being asked to employ observability platforms such as New Relic One to minimize disruption to the business. Observability has always been a core DevOps tenet, but achieving and maintaining it is challenging. Most DevOps teams today aspire to be able to maintain some level of continuous monitoring. However, as it becomes easier and less costly to instrument applications using open source agent software, interest is rising in observability platforms that simplify the investigation of anomalies indicative of an issue that could disrupt an application environment. As that shift occurs, more organizations will seek to correlate IT and business events.

    It’s still early days as far as the adoption of observability platforms is concerned, but it’s apparent that as application environments become more complex, the plethora of monitoring tools that DevOps teams rely on will need to be streamlined. It’s not uncommon for DevOps teams to have multiple monitoring tools that surface a set of predefined but often conflicting metrics. Observability platforms, however, unify logs, metrics and traces in a way that makes it simpler to launch queries to identify the root cause of an issue, hopefully before any catastrophic disruption can occur.

  • 2024 Infrastructure Tech Predictions

    2024 Infrastructure Tech Predictions

    Ganesh Srinivasan, partner at Venrock, co-authored this article.

    2023 was a rollercoaster like none other; from the death of the modern data stack sprawl to the birth of generative AI, we are only at the beginning of a new era in the ‘art of the possible.’ We guarantee 2024 won’t be a disappointment.

    With a new year approaching, it’s the perfect time for us to examine what we anticipate being the biggest developments in the year ahead. Here is what we think is going to happen in 2024:

    1. OpenAI’s Reign Challenged

    With the emerging learnings in core neural net architectures that led to the transformer and dominance by OpenAI, it is likely that their imminent release of GPT5 will be surpassed in specific performance benchmarks by a new entrant on the backs of more efficient architectures, improved multimodal capabilities, better contextual understanding of the world and enhanced transfer learning. These new models will be built on emerging research in spatial networks, graph structures and combinations of various neural networks that will lead to more efficient, versatile and powerful capabilities.

    2. Apple: The New Leader in Generative AI

    One of the most important players in the generative AI space is only starting to show their cards. 2024 will be the year Apple launches its first set of generative AI capabilities, unlocking the true potential of an AI-on-the-edge, closed architecture with full access to your personal data – showing that Apple is actually the most important company in the generative AI race.

    3. Building for Client-First

    The last decade has reflected a shift away from fat clients to server-side rendering and compute. But the world is changing back to the client. Mobile-first experiences will be required to work in offline mode. Real-time experiences require ultra-low latency transactions. Running LLMs will increasingly be required to run on the device to increase performance and reduce costs.

    4. Death of Data Infrastructure Sprawl

    The rapid growth of the data infrastructure needs of enterprises has led to an increasing sprawl of point solutions, from data catalogs, data governance, reverse extract, transform, load, and airflow alternatives to vector databases and yet another lakehouse. The pendulum will swing back to unified platforms and fewer silos to bring down the total cost of ownership and operating overhead going into 2024.

    5. Approaching the AI Winter

    Generative AI in 2023 could be best characterized as the ‘art of the possible,’ with 2024 being the true test to see if prototypes convert into production use cases. With the peak of the hype cycle likely here, 2024 will experience the stage of disillusionment where enterprises discover where generative AI can create margin-positive impact and where the costs outweigh the benefits.

    6. The Misinformation Threat

    While image and video diffusion models have unlocked a new era for digital creation and artistic expression, there’s no doubt that its dark side has not yet taken its toll. With a presidential election in the wings, diffusion models as a machine for political disinformation will emerge to become the next major disinformation weapon of choice.

    7. AI’s Real-World Breakthrough

    Coming out of the ‘field of dreams’ era for AI, 2024 will represent a breakthrough for commercial use cases in AI, particularly in the physical world. Using AI for physical world modalities will unlock our ability to change and engage with the machines and devices around us, from understanding machine telemetry for problem detection to distilling insights across thousands of real-time sensor feeds.

    8. S3: The Growing Threat to Snowflake

    AWS S3 is about to become the biggest competitor to Snowflake. With a rapidly growing ecosystem of tools emerging as the compute layers on top of S3 leverage their ultra-low costs, high availability, Availability Zone support, and new single-digit millisecond latency service, everyone’s ‘Snowflake cost problem’ is about to have a new set of attractive alternatives.

    9. The Rise of Flink and Operational Analytics

    If business analytics drove the first wave of the data infrastructure evolution, operational analytics will drive the next wave, with Apache Flink at the center of it. Enterprises will begin en masse adopting real-time and streaming capabilities to begin using data to drive operational decision making. This will create new value in areas such as logistics, financial transactions, inventory management and fraud detection.

    10. The Developer AI Stack

    Going into 2024, AI’s most significant impact in the digital world will be unlocking developer productivity. From code generation to debugging to build management, AI will unlock a new level of developer productivity that we haven’t seen since the advent of the cloud.

    If you agree, disagree or would like to share your own 2024 predictions with us, please reach out on X at @ethanjb and @gan3sh.