Category: Continuous Delivery

Continuous delivery is a software engineering discipline that allows organizations to consistently develop and release quality software at a rapid pace. It is achieved by automating the software development lifecycle, enabling tasks such as development, testing and release to occur concurrently and continuously.

  • 5 Security Threats DevOps Teams Should Know

    5 Security Threats DevOps Teams Should Know

    DevOps security, also known as DevSecOps, is a philosophy in which security practices are integrated into the DevOps process. DevOps security involves creating a ‘security-as-code’ culture with ongoing, flexible collaboration between release engineers and security teams. The DevSecOps movement, much like DevOps itself, is focused on creating new solutions for complex software development processes within an agile framework.

    DevOps security is about breaking down silos and promoting open collaboration across teams. It’s about making everyone accountable for security with the ultimate aim of improving the quality and speed of code releases. The adoption of a DevOps security model necessitates a cultural shift across the organization. It requires the integration of security into every aspect of the development and operations processes.

    DevOps Security is not just about implementing tools and technologies; it’s about changing the way we look at security. Rather than being an afterthought, security should be a key part of the ongoing conversation from the start of the project to the end.

    5 Security Threats DevOps Teams Must Know About

    As a DevOps professional, it’s crucial to be aware of the potential threats that could compromise your systems, applications, and data. Let’s take a look at the top five security threats that DevOps teams must be aware of.

    Phishing Attacks

    Phishing attacks are a common security threat that can lead to data breaches. These attacks involve cybercriminals impersonating legitimate organizations to trick individuals into revealing sensitive information, such as passwords and credit card numbers.

    Phishing attacks can be particularly damaging for DevOps teams. They can lead to unauthorized access to development systems and data, which can lead to devastating supply chain attacks. For example, an attacker could trick a team member into revealing their login credentials for a critical system, allowing the attacker to gain access and inject malware into a CI/CD pipeline.

    Code Injection

    Code injection is another common security threat that DevOps teams must be aware of. This involves the exploitation of an application by injecting malicious code. The attacker can then execute the malicious code to compromise the system or steal sensitive data.

    For DevOps teams, code injection attacks can be particularly harmful. These attacks can lead to compromised systems and applications, resulting in data breaches and significant downtime.

    Man-in-the-Middle Attacks

    Man-in-the-middle attacks are a type of security threat where the attacker intercepts and potentially alters the communication between two parties without their knowledge. This can lead to a range of damaging outcomes, including data theft, session hijacking, and even identity theft.

    For DevOps teams, man-in-the-middle attacks can be particularly problematic. These attacks can lead to compromised systems and data, and even the unauthorized alteration of code.

    Container Vulnerabilities

    Container vulnerabilities are a significant security threat for DevOps teams. Containers are a key technology in the DevOps world, allowing for the rapid and reliable deployment of applications. However, like any technology, they come with their own set of security risks.

    These vulnerabilities can range from use of insecure images, to misconfigurations and software bugs, to more serious issues like kernel exploits. If an attacker is able to exploit a container vulnerability, they could potentially gain control over the entire system.

    DDoS Attacks

    Last but not least, distributed denial-of-service (DDoS) attacks are a significant security threat that DevOps teams must be aware of. These attacks involve overwhelming a production environment with traffic, causing it to become unavailable to users.

    For DevOps teams, DDoS attacks can be particularly damaging. Not only can they lead to significant downtime, but they can also result in lost revenue and damage to the organization’s reputation.

    How to Mitigate These DevOps Security Threats

    While these security threats are concerning, there are effective strategies and techniques that can be used to mitigate them.

    Implement Email Security Practices and Tools

    To combat phishing attacks, it’s crucial to implement email security tools that can detect and block phishing attempts. These tools can help to filter out phishing emails, reducing the likelihood that team members will fall victim to these attacks.

    In addition to implementing email security, it’s also important to provide security awareness training for team members. This training should cover the basics of cybersecurity, including how to recognize and respond to phishing attempts.

    Use Input Validation and Sanitization in Applications

    To protect against code injection attacks, it’s important to use input validation and sanitization in applications. Input validation involves checking that the data provided by a user meets certain criteria before it’s processed by the application.

    Input sanitization, on the other hand, involves cleaning up the data to remove any potentially harmful elements. This can help to prevent malicious code from being executed within the application.

    Employ HTTPS and SSL/TLS Encryption for Data in Transit

    To guard against man-in-the-middle attacks, it’s important to employ HTTPS and SSL/TLS encryption for data in transit. This ensures that any data being sent between the user and the application is encrypted, making it much more difficult for an attacker to intercept and read the data.

    Regularly Scan Containers for Vulnerabilities

    To protect against container vulnerabilities, it’s crucial to regularly scan containers for vulnerabilities. This involves using tools that can analyze the containers and identify any potential security risks.

    By regularly scanning containers, DevOps teams can identify and address vulnerabilities before they can be exploited by an attacker.

    Implement Rate Limiting and Network Filtering

    Finally, to mitigate the risk of DDoS attacks, it’s important to implement rate limiting and network filtering. Rate limiting involves restricting the number of requests that a user can make to the application within a certain period of time.

    Network filtering, on the other hand, involves blocking traffic from certain IP addresses or ranges that are known to be associated with DDoS attacks. This can help to reduce the impact of a DDoS attack and protect the availability of the application.

    In conclusion, DevOps security is a crucial aspect of the DevOps process. By being aware of potential security threats and taking steps to mitigate them, DevOps teams can significantly reduce the risk of a security breach and ensure the ongoing success of their projects.
  • Survey: Widespread Inability to Remediate App Vulnerabilities

    Survey: Widespread Inability to Remediate App Vulnerabilities

    A survey of 621 IT and security professionals published this week found only 20% are confident in their ability to detect a vulnerability before an application is released.

    Conducted by the Ponemon Institute on behalf of Security Journey, a provider of cybersecurity training services for developers, the survey finds 61% struggling to remediate vulnerabilities effectively, with 55% blaming misalignment between development, security and compliance teams for delays.

    A third of respondents (33%) said teams lacked a common view of applications and assets, with 38% acknowledging they lack the ability to hold departments accountable for patching applications. Only 11% of organizations believed they patch vulnerabilities effectively in a timely manner, the survey finds.

    In the 12 months prior to the study, 54% of respondents suffered a security incident due to an unpatched vulnerability, with 51% experiencing more than eight incidents.

    Overall, half (50%) admitted they fail to test the security of their applications after they have been released. Only 36% specifically teach developers to write secure code. Just one-fifth (21%) educated developers on vulnerability remediation. Less than half (43%) have invested in training provided by a third party.

    When training is provided, 68% of respondents also admitted immediate feedback is not provided and less than half (47%) said secure coding training is customized to meet developer needs. Half (50%) of those who provided training have no formal assessment to measure knowledge gain, the survey found.

    Amy Baker, chief marketing officer and security education evangelist for Security Journey, said the survey makes it clear much work still needs to be done in terms of teaching developers how to write secure code.

    In addition, too many software development teams are overly optimistic about their ability to remediate known vulnerabilities the next time they plan to update an application, said Baker. Many developers move on to the next application simply because either the pressure to meet delivery deadlines is too intense or there is some other emerging technology, such as large language models (LLMs), that needs to be learned, she added. In fact, too many organizations are far too focused on the rate at which applications are built and deployed at the expense of cybersecurity, Baker noted.

    That’s especially problematic because cybercriminals have become much more adept at monitoring application deployments and updates, she added.

    The amount of time between when code is deployed and when cybercriminals begin scanning it for vulnerabilities is now measured in hours rather than days. Developers, unfortunately, are deploying more insecure code than ever. In fact, much of that code is insecure by design, noted Baker.

    Overall, nearly half of respondents (48%) only train developers annually, bi-annually or when an incident occurs. More than two-thirds (68%) only train developers on how to implement secure coding practices to meet compliance requirements. In effect, because developers are not taught security in school, what training they do receive is on the job, said Baker.

    Clearly, there is still much work to be done when it comes to implementing DevSecOps best practices to improve application security. In the meantime, the amount of code that needs to be patched has already reached proportions that most application development teams are never going to be able to effectively address.

  • Venafi Adds Ability to Prevent Unauthorized Code From Running

    Venafi Adds Ability to Prevent Unauthorized Code From Running

    Venafi added an ability to prevent unauthorized code from running in IT environments that make use of its machine identity management platform.

    Shivajee Samdarshi, chief product officer at Venafi, said the Stop Unauthorized Code Solution leverages the company’s CodeSign Protect offering to ensure that only authorized code can run on any given platform.

    The overall goal is to enable organizations to better secure their software supply chains using a zero-trust approach to software based on identity management and code signing to verify software comes from an approved source and complies with policy controls, he added.

    All code is signed using private digital certificates or those issued by trusted certificate authorities, said Samdarshi. Before code can execute, the security platforms an organization has in place can be configured to check that digital signature against trusted code signing certificates, he noted.

    Interest in securing software supply chains has risen sharply since the Biden administration issued an executive order requiring federal agencies to implement a range of measures, including code signing, to achieve that goal. However, securing software chains is often more challenging than organizations initially appreciate.

    In fact, a recent Venafi survey found that 70% of security and IT leaders believe that software supply chain attacks are their biggest security blind spot. Additionally, 85% believe that continuous security validation of the CI/CD pipeline is vital to reduce the risk of vulnerabilities going undetected during the software development lifecycle. A full 88% said they believe machine identity management is essential to the success of zero-trust models that are being more widely adopted across enterprise IT environments.

    Arguably, the most important thing organizations need to focus on is making sure application developers and cybersecurity professionals develop a working relationship. The biggest barrier to the adoption of DevSecOps best practices required to secure software supply chains remains largely cultural. For more years than anyone cares to admit, many developers have viewed cybersecurity more as a hindrance to application development that needs to be overcome or circumvented rather than being a core aspect of a quality assurance process. The total number of vulnerabilities that exist in applications running in production environments could likely be measured in the billions.

    Remediating all those vulnerabilities may never be practical, but at the very least, DevSecOps teams could make sure that no new code containing vulnerabilities is allowed to execute. Cybercriminals have become especially adept at inserting malware into code that they hope will find its way into any number of downstream applications before they activate it. That capability alone should help mollify cybersecurity teams that are increasingly being tasked with improving software supply chain security. The challenge is those cybersecurity teams don’t always appreciate the impact new policies can have on the pace at which applications are developed and deployed.

    Like it or not, software supply chains will generally be more secure in 2024. The only thing that remains to be determined is how much friction will be injected into DevSecOps workflows to achieve that goal.

  • Configuration-as-Code: Trends and Predictions for 2024

    Configuration-as-Code: Trends and Predictions for 2024

    Configuration-as-code, often abbreviated as CaC, is an innovative approach to managing and provisioning computing resources. It refers to the practice of handling changes, deployments and updates to software and systems via code rather than manual processes. CaC allows for a version-controlled, reproducible and automated method of managing environments, leading to more consistent and reliable systems.

    The essence of configuration-as-code is to treat system configurations the same way that software code is treated. This means that configurations are written in a code format, stored in a version control system and applied through automated processes. This approach brings several benefits, including consistency, repeatability and the ability to test changes before applying them to live environments.

    This concept is not just a theoretical approach but rather a practical tool for managing modern digital infrastructure. It’s a key component of DevOps practices, enabling teams to move faster while maintaining control and minimizing the risk of operational issues. Configuration-as-code is a critical tool for managing complex systems and achieving the highest levels of operational efficiency and reliability.

    The Evolution of CaC in Recent Years

    Over the past several years, configuration-as-code has grown from a niche concept into a mainstream practice adopted by many leading technology companies. This evolution has been driven by several factors, including the increasing complexity of digital systems, the rise of cloud computing and the broader adoption of DevOps practices.

    In the early days, system configurations were often managed manually or through ad-hoc scripts. This approach was prone to errors, hard to scale and lacked visibility into changes. As systems grew more complex, the need for a more robust, scalable, and reliable method of managing configurations became apparent. This led to the creation of configuration-as-code.

    The rise of cloud computing has been a significant driver in the adoption of configuration-as-code. With cloud platforms, resources can be provisioned and managed via APIs, making it possible to handle configurations through code. This has allowed for much greater scalability and flexibility enabling companies to manage large, complex environments more effectively.

    The adoption of DevOps practices and increasingly mature automation frameworks have also contributed to the growth of Configuration as Code. As infrastructure-as-code (IaC) becomes the norm, CaC is becoming a staple of modern DevOps practices.

    Trends in Configuration-as-Code for 2024

    Looking ahead to 2024, several trends are likely to shape the future of configuration-as-code:

    Increased Adoption of Cloud-Native Environments

    As more companies adopt cloud-native technologies, the use of configuration-as-code is set to increase. Cloud-native environments are inherently dynamic and complex, making them an ideal fit for configuration-as-code. With CaC, teams can manage these environments more effectively, ensuring consistency, scalability, and reliability. Cloud-native technologies like Kubernetes and Docker also natively support configuration-as-code, making it easier for teams to adopt this approach.

    Use of AI and Machine Learning in Configuration Management

    Artificial intelligence and machine learning are set to play a significant role in the future of configuration management. With AI and ML, teams can automate even more aspects of configuration management, reducing the risk of human errors and freeing up time for more valuable tasks. For example, AI could be used to predict the impact of configuration changes, while machine learning could help automate the process of optimizing configurations for performance and cost efficiency.

    Shift Toward Immutable Infrastructure

    Immutable infrastructure means that servers are never modified after they’re deployed. Instead, any changes are made by deploying a new server with the desired configuration. This approach reduces the risk of configuration drift and ensures a consistent environment. Configuration-as-code is a key enabler of immutable infrastructure, making it easier to manage and deploy servers in a repeatable, automated way.

    Collaboration and Democratization of CaC

    Finally, the trend towards collaboration and democratization in technology will also influence configuration-as-code. With CaC, configurations become more visible and accessible, allowing for greater collaboration between teams. This can lead to better decision-making, less siloed working, and improved overall outcomes. At the same time, configuration-as-code also enables democratization by making it easier for non-technical stakeholders to understand and participate in configuration management.

    Predictions for Configuration-as-Code in 2024

    CaC is Becoming a Cornerstone in the DevSecOps Approach

    The integration of development, security and operations—commonly known as DevSecOps—aims to embed security practices into the DevOps process. As we look towards 2024, configuration-as-code is set to become a cornerstone in the DevSecOps approach.

    By treating infrastructure as code, teams can apply the same security practices they use for application code to their infrastructure. This includes performing code reviews, using automated testing, and tracking changes to the environment. With configuration-as-code, security can shift left—being considered earlier in the development process—leading to more secure systems.

    Moreover, configuration-as-code can help bridge the gap between security and operations teams. It allows for a shared language and shared tools, fostering better collaboration and communication.

    Growth of CaC-as-a-Service

    Configuration-as-code-as-a-service is an emerging trend that is set to grow significantly by 2024. This approach allows businesses to outsource configuration management to a specialist third party, which uses configuration-as-code to automate the process. Cloud-based configuration management solutions provide advanced capabilities such as secrets management, centralized configuration management and orchestrated workflows.

    Version Control Features Specifically Designed for CaC

    Version control systems are a key component of configuration-as-code. They allow teams to track changes to their environment, revert back to previous versions if necessary, and collaborate more effectively. In 2024, we can expect to see the evolution of version control systems with features specifically designed for CaC.

    These features might include support for infrastructure-specific languages and better integration with infrastructure tools. Version control tools might also introduce improved support for collaborative configuration workflows, making it easier for teams to work together on infrastructure configuration.

    Increased Role of CaC in Managing Edge Computing Environments

    As we move into 2024, we can expect to see an increased role for configuration-as-code in managing edge computing environments. Edge computing is rapidly growing due to its ability to bring computation and data storage closer to the location where it is needed, improving response times and saving bandwidth.

    With the rise of edge computing, managing these environments becomes increasingly complex. CaC can automate the process of setting up and maintaining these environments, reducing human error and increasing efficiency. This also allows for consistency across different environments, leading to more reliable systems.

    In conclusion, the future of configuration-as-code looks promising. As we move towards 2024, we can expect to see an increased role for CaC in managing edge computing environments, its evolution as a cornerstone in the DevSecOps approach, the growth of CaC-as-a-Service, and the evolution of version control systems specifically designed for CaC. These developments promise to bring about greater efficiency, security and collaboration in the realm of infrastructure management.

  • Mobb Extends DevSecOps Reach of Tool to Generate Patches

    Mobb Extends DevSecOps Reach of Tool to Generate Patches

    Mobb today added an ability to instantly surface patches for vulnerabilities at the time when code is being committed during a DevSecOps workflow.

    Previously, the tool provided by Mobb to create validated patches based on the scan results of third-party SAST tools would only surface issues to individual developers.

    Mobb CEO Eitan Worcel said organizations can now address these issues within the context of DevSecOps workflow.

    The Mobb platform combines proprietary security research and traditional semantic analysis with generative artificial intelligence (AI) to automatically create patches for vulnerabilities. The overall goal is to make it simpler for DevSecOps teams to consistently ensure applications with known vulnerabilities are remediated before they are deployed, said Worcel.

    The Mobb approach eliminates the need for IT teams to sort through static application security testing (SAST) scans themselves. Each vulnerability typically requires at least 30 minutes to fix, so the Mobb platform improves application security while simultaneously making developers more productive.

    Historically, one of the reasons for the wide divide between application development teams and cybersecurity professionals is that many of the vulnerabilities discovered don’t actually impact applications running in production environments. Development teams then find themselves wasting time investigating vulnerabilities and, when they do determine a vulnerability is an issue, spending time developing a patch. The Mobb tool automatically creates the necessary patch, so there is less of a need to debate which vulnerabilities are worthy of the time required to create a patch.

    For decades, application development teams have been attempting to find a way to remediate vulnerabilities as quickly as possible. With increased focus on adopting DevSecOps best practices to address those vulnerabilities, more organizations are now reviewing software supply chains as part of a larger effort to improve application security.

    There will, of course, be vulnerabilities that the Mobb tool will not be able to address simply because there may not be enough affected applications to warrant pre-building a patch. Even with the most robust set of rules, it is improbable that an automated tool can, with 100% certainty, safely fix every issue. However, given the number of routine vulnerabilities present in applications, such as SQL injections, there’s plenty of opportunity to improve developer productivity by relying on patches that address common vulnerabilities.

    The process by which patches are prioritized, developed and then applied has, of course, long been a source of DevOps frustration. Anything that streamlines that process will go a long way toward improving the overall state of application security at a time when cybercriminals are becoming more adept at exploiting vulnerabilities. The challenge is finding a way to remediate vulnerabilities that developers will embrace rather than resist. The Mobb approach still provides them with control over what patches are applied but the toil involved with creating a patch in the first place has been substantially reduced.

    It’s not clear how long it might be before automated approaches to building patches might improve the overall state of application security but, as always, every journey needs to begin with a first step in the right general direction.

  • Navigating the Hybrid Cloud Maze: Overcoming Adoption Hurdles

    Navigating the Hybrid Cloud Maze: Overcoming Adoption Hurdles

    Hybrid cloud solutions mark a significant evolution in organizational IT strategy, blending on-premises infrastructure with cloud-based services. This approach offers a unique mix of control, flexibility and scalability and introduces new dimensions in IT security. Crucial for businesses adapting to dynamic market demands, the hybrid model necessitates a robust security framework to protect sensitive data across diverse platforms. By integrating the security aspect into its core, hybrid clouds cater to the strategic shift towards more agile, responsive and cost-effective IT operations, ensuring that advanced security measures are ingrained in every layer of the infrastructure. A recent report states that 72% of organizations using a hybrid approach combine public and private clouds, highlighting the growing need for comprehensive security strategies in these environments.
    The transition to a hybrid cloud model introduces a unique set of security challenges that are critical to address. These challenges include ensuring secure data transfers between on-premises and cloud environments, protecting against increased surface attacks due to the interconnected nature of hybrid systems, managing identity and access controls across diverse platforms and ensuring compliance with various regulatory standards.

    Types of Organizations Suited for Hybrid Cloud Solutions

    Hybrid cloud solutions are particularly beneficial for organizations requiring a blend of security, flexibility and scalability. Enterprises with fluctuating workloads, including e-commerce platforms that experience seasonal spikes, find hybrid clouds ideal for managing these variations efficiently. Organizations handling sensitive data, such as healthcare and financial institutions, benefit from the hybrid model’s ability to store critical data on-premises while utilizing the cloud for less sensitive operations. Start-ups and small and medium enterprises (SMEs) also find hybrid clouds appealing due to their ability to scale resources as the business grows without requiring substantial upfront infrastructure investment. Additionally, companies in sectors like retail and manufacturing, where legacy systems are prevalent, can leverage hybrid clouds to innovate without completely overhauling their existing IT setup.

    Standardized Integration Protocols

    Standardized integration protocols are fundamental in hybrid cloud environments, acting as the glue that connects disparate systems seamlessly. They ensure consistent communication and data flow between on-premises infrastructure and cloud services, which is crucial for maintaining operational efficiency and data integrity. A well-known example of such a protocol is the open data protocol (OData). OData, used for data integration, enables interoperability between different systems by providing a uniform method to query and update data. This protocol is beneficial in a hybrid cloud setup because it allows applications to access information from various sources, including on-premises databases or cloud-based storage, through a common interface. Organizations can mitigate the complexities of integrating diverse computing environments by employing standardized protocols like OData.

    Dynamic Security Strategies

    With the complexity inherent in hybrid cloud environments, dynamic security strategies are indispensable to safeguard data and applications across varied platforms. These environments blend on-premises and cloud infrastructures, each presenting its own set of security challenges. The intricate nature of these setups demands a fluid and responsive security approach that can swiftly adapt to emerging threats and the unique attributes of different infrastructure components. Continuously evolving security measures are essential to keep pace with the ever-changing threat landscape, ensuring comprehensive protection for both on-premises and cloud-based systems.
    The effectiveness of these strategies is particularly crucial in defending against incidents like distributed denial of service (DDoS) attacks, which can exploit the interconnected nature of hybrid environments. Employing advanced security solutions that offer proactive and automatic mitigation capabilities is key to minimizing potential downtime and latency issues. A well-integrated security strategy, encompassing both cloud and on-premises defenses, is vital to maintaining the integrity and availability of services across the hybrid cloud architecture. This balanced approach ensures that data and applications remain secure, irrespective of location within the hybrid cloud framework.

    Solutions for Harnessing Hybrid Cloud Benefits

    It is crucial to intertwine strategic solutions and best practices with robust security measures to maximize the advantages of hybrid cloud environments. Cost optimization, while essential, must go hand-in-hand with security considerations. Effective security management involves not just monitoring and optimizing costs but also ensuring that each investment contributes to a more robust security posture. This includes deploying resources to enhance protection against cyber threats and regularly assessing the security implications of resource allocation within hybrid environments.
    Approaching efficient resource deployment and utilization with a security-first mindset is imperative. Practices such as auto-scaling, which dynamically adjusts resources based on demand, should be integrated with security protocols to ensure that changes in resource allocation do not compromise security. This approach is crucial for maintaining operational efficiency and cost control and ensuring that the hybrid cloud environment remains resilient against evolving security threats. Embracing these practices helps organizations leverage the full benefits of hybrid cloud solutions, achieving a balance between performance, cost-effectiveness, and, most importantly, stringent security.

    The Evolving Landscape of Hybrid Cloud Architectures

    As hybrid cloud architectures evolve, security experts need to anticipate emerging threats and adapt to new technologies. The horizon for cloud security is increasingly complex, with sophisticated cyberthreats challenging traditional defenses. To stay ahead of the competition and threats, professionals must invest in continuous learning, leverage artificial intelligence and predictive analytics for threat detection, and foster a culture of security innovation. Preparing for these changes involves technology adoption and developing proactive, intelligence-driven security strategies for a resilient digital future.
  • Swimm Adds Generative AI Chat Tool for Documentation

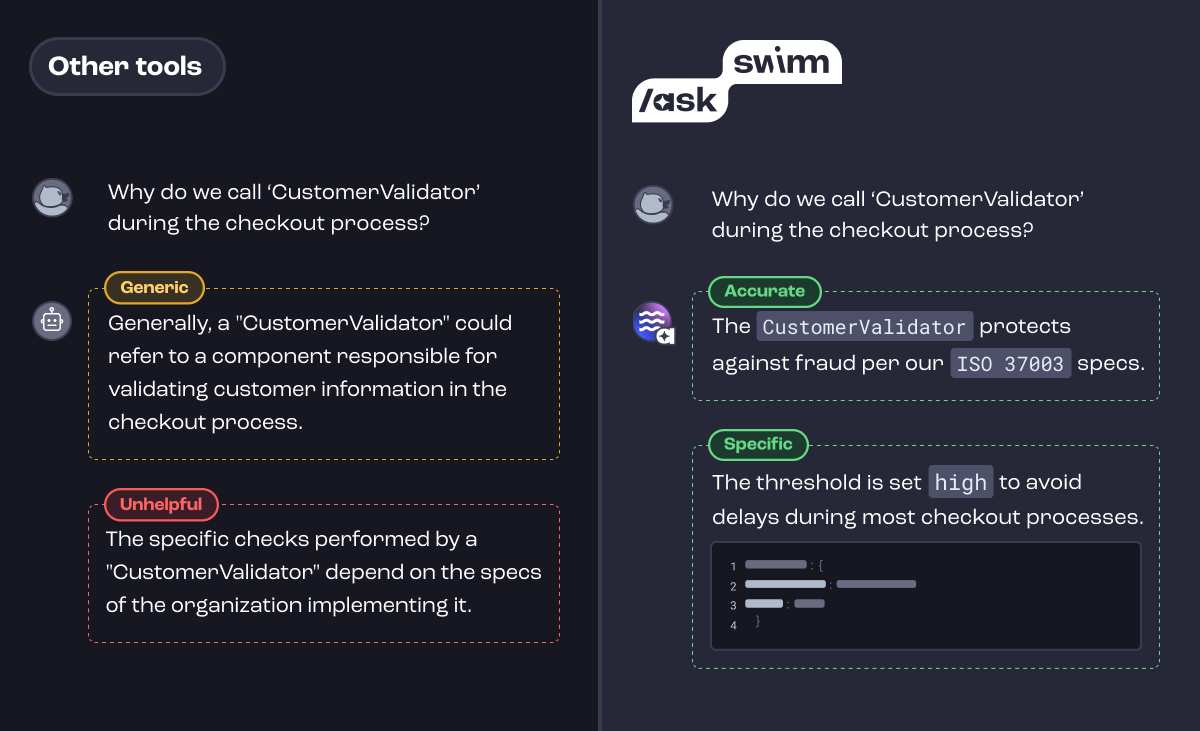
    Swimm today announced it has added a chat tool that enables developers to use natural language to surface insights into code.

    Company CEO Oren Toledano said the /ask Swimm tool makes it simpler to launch queries that enable developers to better understand how code was constructed.

    The /ask Swimm tool aggregates documentation along with other related data to surface factors that are not evident in the code itself, such as documentation of business decisions, product design considerations and decisions concerning why specific architectural choices were made. It automatically captures and updates code-related knowledge to provide a continuous feedback loop as code, documentation, files and repositories are created and updated to provide deeper insights into code that goes beyond what might have been actually documented.

    The overall goal is to provide a mechanism that enables developers to understand how and why code was constructed within the context of an integrated development environment (IDE), said Toledano.

    Swimm has previously made available a platform that uses generative AI platform to create a static analysis of documentation. That capability should make it simpler for organizations to track documentation at a time when generative AI platforms such as ChatGPT are exponentially increasing the amount of code being written. In theory, those platforms should be able to also create documentation for that code, but there will still be a need for tools to track and analyze it.

    In the longer term, Swimm plans to continue to extend its usage of generative AI to provide deeper levels of insights across entire applications and software ecosystems to address that challenge, noted Toledano.

    In the short term, however, it’s clear that AI is making developers more productive than ever. In fact, the volume of code being generated might soon overwhelm existing DevOps pipelines and workflows. Most DevOps teams will need to revamp those workflows as the pace at which more applications than ever are being developed and deployed faster than ever.

    It’s still early days as far as generative AI adoption is concerned, but it’s clear many developers are already using it to write code. How much of that code makes it into a production environment is difficult to determine, but a lot of that code is going to be of varying quality. A general-purpose AI platform such as ChatGPT was trained using code collected from all across the web. The code generated by these platforms is only as good as the examples used to train it, all of which were created by human developers who may have made mistakes, such as including code that has known vulnerabilities.

    Regardless of whether code was generated by a machine or a human, the probability that documentation will need to be analyzed as part of a code review process is always high. The challenge and the opportunity is to determine the best way to apply AI to a longstanding challenge that is now being exacerbated by the existence of AI tools that, with each passing day, are only becoming more accessible to developers.

  • Navigating the Multi-Cloud Ecosystem

    Navigating the Multi-Cloud Ecosystem

    Multi-cloud infrastructure, an approach where organizations utilize services from multiple cloud providers, is rapidly gaining traction in the tech world.

    In this article, we will unpack the concept of multi-cloud infrastructure, examining how it enables businesses to diversify their cloud ecosystems for enhanced performance, greater flexibility and improved risk management.

    Understanding the Multi-Cloud Ecosystem

    Multi-cloud environments represent a strategic approach in cloud computing where businesses utilize services from multiple cloud providers to meet diverse operational needs.

    This concept differs from hybrid cloud, which typically blends both private and public cloud infrastructures, aiming to offer a balance between the two under a single unified environment.

    In contrast, a multi-cloud strategy involves using distinct cloud services – for instance, one provider for storage, another for computing power and another for analytics – without necessarily integrating them into one cohesive system. This approach allows organizations to leverage the unique strengths and offerings of various cloud providers, thereby optimizing their IT infrastructure for efficiency, cost-effectiveness and enhanced performance.

    The Advantages of a Multi-Cloud Approach

    Adopting a multi-cloud approach brings several key benefits, the biggest among them being enhanced resilience, flexibility and the avoidance of vendor lock-in.

    By distributing resources and workloads across multiple cloud environments, businesses can mitigate risks associated with relying on a single cloud provider, such as service outages or data loss. This diversity ensures continuous operation and robust disaster recovery capabilities.

    Additionally, a multi-cloud strategy empowers organizations with the flexibility to select the best services that each cloud provider offers, tailoring their IT infrastructure to specific needs and operational demands. This tailored approach enables businesses to optimize both performance and cost. Different providers may offer competitive pricing for specific services, allowing companies to choose the most cost-effective solutions for their requirements.

    Moreover, by avoiding vendor lock-in, organizations retain the freedom to switch providers as needs evolve or as newer, more advantageous services become available. This strategic utilization of multiple clouds ultimately leads to a more efficient, agile and economically sound IT infrastructure.

    Key Challenges in Multi-Cloud

    Multi-cloud management comes with its own set of challenges, particularly in terms of complexity, data security and compliance. DevOps teams often grapple with the complexity of managing disparate cloud services, each with unique features and interfaces, making seamless integration and consistent operation a demanding task.

    Data security is another critical concern, as safeguarding sensitive information across multiple platforms requires robust and adaptable security measures. Additionally, ensuring compliance with varying regulations across different cloud environments adds another layer of complexity.

    These challenges necessitate that DevOps teams are technically proficient and adept at strategic planning and coordination to manage a multi-cloud ecosystem effectively.

    Best Practices in Multi-Cloud Deployment and Management

    When managing and deploying within a multi-cloud ecosystem, DevOps teams can greatly benefit from the following five best practices:

    1. Strategic Cloud Service Selection: Carefully assess and choose cloud services based on specific workload requirements, performance metrics and cost-effectiveness to ensure optimal deployment.
    2. Centralized Monitoring and Management: Utilize centralized tools for monitoring and managing different cloud environments to maintain consistency and control and to streamline operations.
    3. Consistent Security Posture: Apply uniform security policies and practices across all cloud platforms to protect data integrity and comply with regulatory standards.
    4. Automation: Automate repetitive and routine tasks across different clouds for efficient resource utilization, reduced errors, and faster deployment cycles.
    5. Cost Management and Optimization: Continuously monitor and manage cloud spending across platforms to avoid cost overruns, ensure efficient use of resources and follow cloud cost optimization best practices.

    Building a Multi-Cloud Strategy: A DevOps Perspective

    From a DevOps perspective, building a comprehensive multi-cloud strategy involves aligning cloud infrastructure with business objectives and core DevOps principles.

    The first step is clearly defining business goals and identifying how different cloud environments can support these objectives. This should be followed by selecting cloud services that best match the specific needs of each workload, considering factors like performance, cost and compliance requirements. Integrating continuous integration and continuous deployment (CI/CD) processes is crucial in a multi-cloud setup.

    This integration ensures software can be developed, tested and deployed rapidly and reliably across different cloud platforms. The strategy should also include implementing robust automation and monitoring tools to maintain consistency and efficiency across the cloud.

    By focusing on these elements, a DevOps team can develop a multi-cloud strategy that not only aligns with the organization’s goals but also adheres to the agile and efficient ethos of DevOps methodologies, ensuring seamless operation and scalability in the multi-cloud environment.

    Wrapping Up

    In conclusion, effectively navigating the multi-cloud ecosystem is crucial for DevOps success, as it offers unparalleled flexibility, scalability and resilience in managing diverse cloud resources. DevOps professionals are encouraged to embrace multi-cloud strategies as they enhance operational agility and open avenues for innovation and improved service delivery.

  • Implementing Data Analytics in Multi-Cloud Environments

    Implementing Data Analytics in Multi-Cloud Environments

    Multi-cloud data analytics is more intricate, demanding a nuanced approach to ensure seamless operations and accurate insights. Coordinating analytics across multiple cloud providers introduces various issues, requiring careful consideration of implementation strategy. From cost management to performance variability and data orchestration, we will explore each challenge in detail and provide actionable insights on how to effectively navigate these hurdles, ensuring fool-proof data analytics infrastructure in multi-cloud solutions.

    Interoperability and Standards

    Interoperability challenges arise in multi-cloud data analytics due to varying APIs and standards across cloud providers. The lack of uniformity in data formats and communication protocols hinders seamless collaboration and data exchange. To address this, organizations should prioritize cloud services adhering to open standards, and advocate for industry-wide interoperability initiatives. Additionally, create an abstraction layer or middleware that acts as a bridge between different cloud providers. This abstraction layer helps standardize interactions, facilitating seamless data exchange and reducing dependencies on specific provider APIs. Thus, you enhance the flexibility of your multi-cloud environment, making it easier to integrate and switch between different cloud platforms.

    Vendor Lock-In

    Organizations risk becoming overly dependent on a single vendor, limiting flexibility and making migration complex. Utilizing specialized features or tools from one provider may face difficulties transitioning to another, which restricts the ability to choose more cost-effective or suitable solutions and may result in increased switching costs. To mitigate this, a multi-cloud strategy should be adopted, favoring standardized technologies and open APIs, allowing organizations to distribute workloads across multiple cloud providers and avoid being tied to a specific vendor’s ecosystem, enhancing flexibility and strategic decision-making. Design architectures that leverage abstraction layers and avoid tightly coupling with provider-specific services. This approach ensures flexibility, allowing your organization to choose and switch between cloud providers based on performance, cost and strategic considerations while minimizing the risk of vendor lock-in.

    Cost Management

    Each provider has unique pricing models and billing mechanisms, making it difficult for organizations to accurately estimate and compare costs. The dynamic nature of data analytics workloads, coupled with data transfer expenses between clouds, contributes to the complexity of budgeting. To cope with that, implement a centralized cloud cost management tool to monitor expenses across providers. Also, regularly review and optimize resource utilization to identify underutilized or over-provisioned instances. You may leverage reserved instances or spot instances for cost-effective computing and implement automation for scaling based on demand, ensuring resources are allocated efficiently. Lastly, negotiate pricing with cloud providers and explore discount options to secure favorable terms for long-term commitments.

    Performance Variability

    As providers have unique infrastructure, network configurations and service levels, inconsistent performance levels may occur and impact the reliability and predictability of analytics results. To mitigate these consequences, conduct thorough performance testing across different cloud environments, optimize queries for specific platforms, and consider workload distribution based on provider strengths. Utilizing performance monitoring tools helps track and analyze variations, enabling timely adjustments. Choosing cloud providers based on specific performance requirements and establishing performance service level agreements (SLAs) also mitigates the impact of performance variability in multi-cloud data analytics.

    Resource Orchestration

    Due to differences in orchestration tools, APIs, and resource management mechanisms cloud providers employ, compatibility issues often take place. The heterogeneity makes it complex to ensure seamless deployment, scaling, and management of analytics workloads. Organizations may consider adopting cloud-agnostic orchestration tools and frameworks to abstract the underlying differences among cloud providers, allowing for consistent resource management. Embracing infrastructure as code (IaC) practices and automation also streamlines resource orchestration, enabling organizations to deploy and manage analytics workloads more efficiently across various cloud environments.

    Data Movement and Latency

    Varied network architectures, geographical distances, and differing data transfer mechanisms contribute to increased latency and potential performance issues. Transferring significant datasets across clouds incurs additional costs and can lead to operational inefficiencies. To avoid that, organizations should optimize data movement processes by leveraging efficient transfer protocols, considering edge computing for proximity to data sources, and strategically distributing workloads based on data location. Implementing caching strategies and utilizing content delivery networks (CDNs) can help mitigate latency challenges, ensuring a more responsive and cost-effective multi-cloud data analytics environment.

    As a Footnote

    In conclusion, the journey of implementing data analytics in multi-cloud environments presents its unique set of challenges. Embracing open standards, adopting cloud-agnostic tools and fostering a culture of continuous improvement are essential components of overcoming them. Continuous monitoring, regular updates to governance frameworks, and strategic decision-making aligned with your business specifics and objectives are keys to reaping maximum benefits from multi-cloud data analytics. You may also take advantage of cloud computing consulting to get a tailored strategy from experts.